
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Binary Analysis — Page 8 | Kitploit
Categories

Binary Analysis

Binary reverse engineering, disassembly, decompilation, and patching tools.

Kitploit recommended
Top tools

10 selected
ghidra preview#1

ghidra

GitHubnationalsecurityagency/ghidra
71.1k1 day ago
radare2 preview#2

radare2

GitHubradareorg/radare2
24.5k3h 27m ago
cutter preview#3

cutter

GitHubrizinorg/cutter
19.4k1 month ago
rizin preview#4

rizin

GitHubrizinorg/rizin
4.1k21h 46m ago
x64dbg preview#5

x64dbg

GitHubx64dbg/x64dbg
49.1k10h 45m ago
angr preview#6

angr

GitHubangr/angr
9.0k17h 35m ago
capa preview#7

capa

GitHubmandiant/capa
6.1k7 days ago
Detect-It-Easy preview#8

Detect-It-Easy

GitHubhorsicq/detect-it-easy
11.3k1 day ago
LIEF preview#9

LIEF

GitHublief-project/lief
5.5k2 days ago
ImHex preview#10

ImHex

GitHubwerwolv/imhex
54.4k20 days ago
NewestRelevanceMost popularRecently updated
1643 results
vmlinux-to-elf preview

vmlinux-to-elf

GitHubmarin-m/vmlinux-to-elf

A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)
embedded-systems-securityreverse-engineeringbinary-analysis+1
1.8k1 day ago
malware_training_vol1 preview

malware_training_vol1

GitHubhasherezade/malware_training_vol1

Materials for Windows Malware Analysis training (volume 1)

reverse-engineeringforensicsmalware-analysis+4
2.1k2 years ago
Ropper preview

Ropper

GitHubsashs/ropper

Display information about files in different file formats and find gadgets to build rop chains for different architectures (x86/x86_64, ARM/ARM64,…

payload-generationexploitationreverse-engineering+3
2.1k2 months ago
frida-scripts preview

frida-scripts

GitHub0xdea/frida-scripts

A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.
android-securityios-securitydynamic-code-analysis+3
1.6k8 days ago
goblin preview

goblin

GitHubm4b/goblin

An impish, cross-platform binary parsing crate, written in Rust
reverse-engineeringfuzzingbinary-analysis
1.5k2 days ago
EfiGuard preview

EfiGuard

GitHubmattiwatti/efiguard

Disable PatchGuard and Driver Signature Enforcement at boot time

defensive-toolsexploitationreverse-engineering+1
2.5k4 months ago
frida-gum preview

frida-gum

GitHubfrida/frida-gum

Cross-platform instrumentation and introspection library written in C

dynamic-analysis-sandboxingmemory-forensicscode-analysis+6
1.0k14h 22m ago
TinyInst preview

TinyInst

GitHubgoogleprojectzero/tinyinst

A lightweight dynamic instrumentation library
dynamic-analysis-sandboxingcode-analysisreverse-engineering+3
1.4k1 month ago
uEmu preview

uEmu

GitHubalexhude/uemu

Tiny cute emulator plugin for IDA based on unicorn.
embedded-systems-securitydynamic-analysis-sandboxingreverse-engineering+3
1.2k2 months ago
Manalyze preview

Manalyze

GitHubjusticerage/manalyze

Static analyzer for PE executables with plugin-based detection of packers, compilers, suspicious imports, cryptographic constants, and ClamAV…

static-analysisvulnerability-analysisreverse-engineering+2
1.1k2 months ago
r2frida preview

r2frida

GitHubnowsecure/r2frida

Radare2 and Frida better together.
android-securitystatic-analysisdynamic-analysis-sandboxing+8
1.4k1 day ago
Alcatraz preview

Alcatraz

GitHubweak1337/alcatraz

x64 binary obfuscator for PE files with control flow flattening, anti-disassembly, import obfuscation, and instruction mutation to hinder reverse…
reverse-engineeringbinary-analysis
2.0k3 years ago
remill preview

remill

GitHublifting-bits/remill

Library for lifting machine code to LLVM bitcode
embedded-systems-securitystatic-analysisreverse-engineering+3
1.8k2 months ago
HexRaysCodeXplorer preview

HexRaysCodeXplorer

GitHubrehints/hexrayscodexplorer

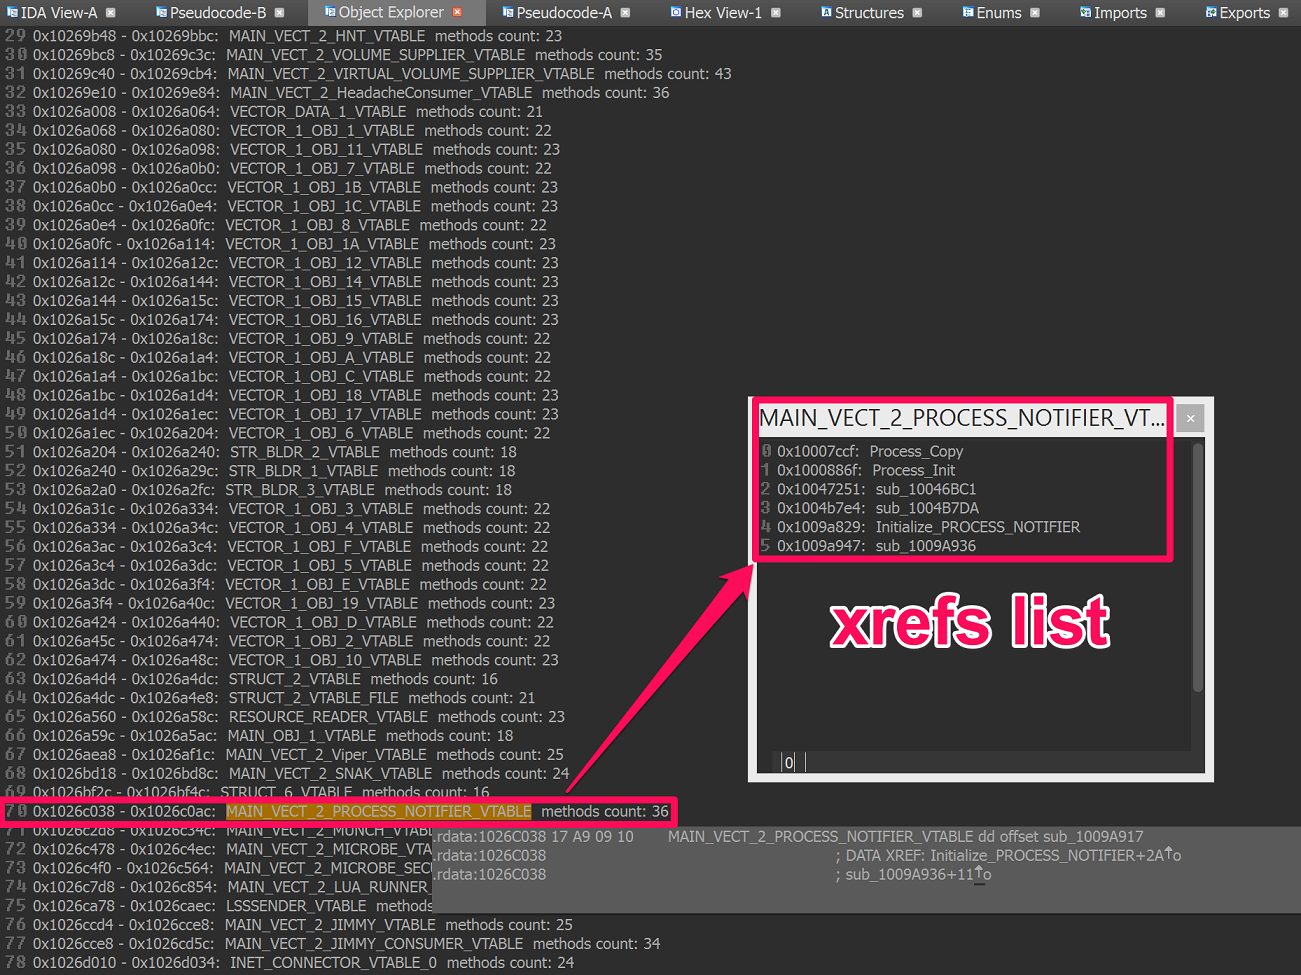
Hex-Rays Decompiler plugin for better code navigation
static-analysisreverse-engineeringdebuggers+2
2.6k11 months ago
ofrak preview

ofrak

GitHubredballoonsecurity/ofrak

Binary analysis and modification platform for unpacking, analyzing, modifying, and repacking firmware and executable formats via GUI and Python API.

embedded-systems-securityreverse-engineeringctf+2
2.1k2 months ago
apk.sh preview

apk.sh

GitHubax/apk.sh

Makes reverse engineering Android apps easier, automating repetitive tasks like pulling, decoding, rebuilding and patching an APK.


android-securitydynamic-analysis-sandboxingpayload-generation+3
3.8k9 months ago
yara-x preview

yara-x

GitHubvirustotal/yara-x

A rewrite of YARA in Rust.

defensive-toolsdisk-forensicsioc-management+14
1.2k22h 36m ago
awesome-llvm-security preview

awesome-llvm-security

GitHubgmh5225/awesome-llvm-security

Curated collection of LLVM security resources covering binary lifting, code obfuscation, static analysis, symbolic execution, sanitizers, and…


static-analysisdynamic-analysis-sandboxingcode-analysis+7
89027 days ago
Previous1…789…92Next







