
 #1
Binary reverse engineering, disassembly, decompilation, and patching tools.
Kitploit recommended
 gamozolabs/elfloader
An architecture-agnostic ELF file flattener for shellcode
 fuzztruction/fuzztruction
Fault-injection-based fuzzer that mutates generator programs to produce almost-valid inputs for targets, enabling fuzzing of complex formats and…
 nodiuus/nocturne
A bin2bin code virtualizer for x86-64 PE's
 arguslab/argus-saf
Scala-based static analysis framework for Android and Java bytecode with flow analysis, decompilation, and native code analysis via symbolic…
 ioactive/melkor_elf_fuzzer
Melkor is a very intuitive and easy-to-use ELF file format fuzzer to find functional and security bugs in ELF parsers.
 boratanrikulu/gobee
Write your BPF programs in Go, not C. gobee transpiles a Go subset to BPF C and generates typed cilium/ebpf bindings.
 armadito/armadito-av
Armadito antivirus main repository
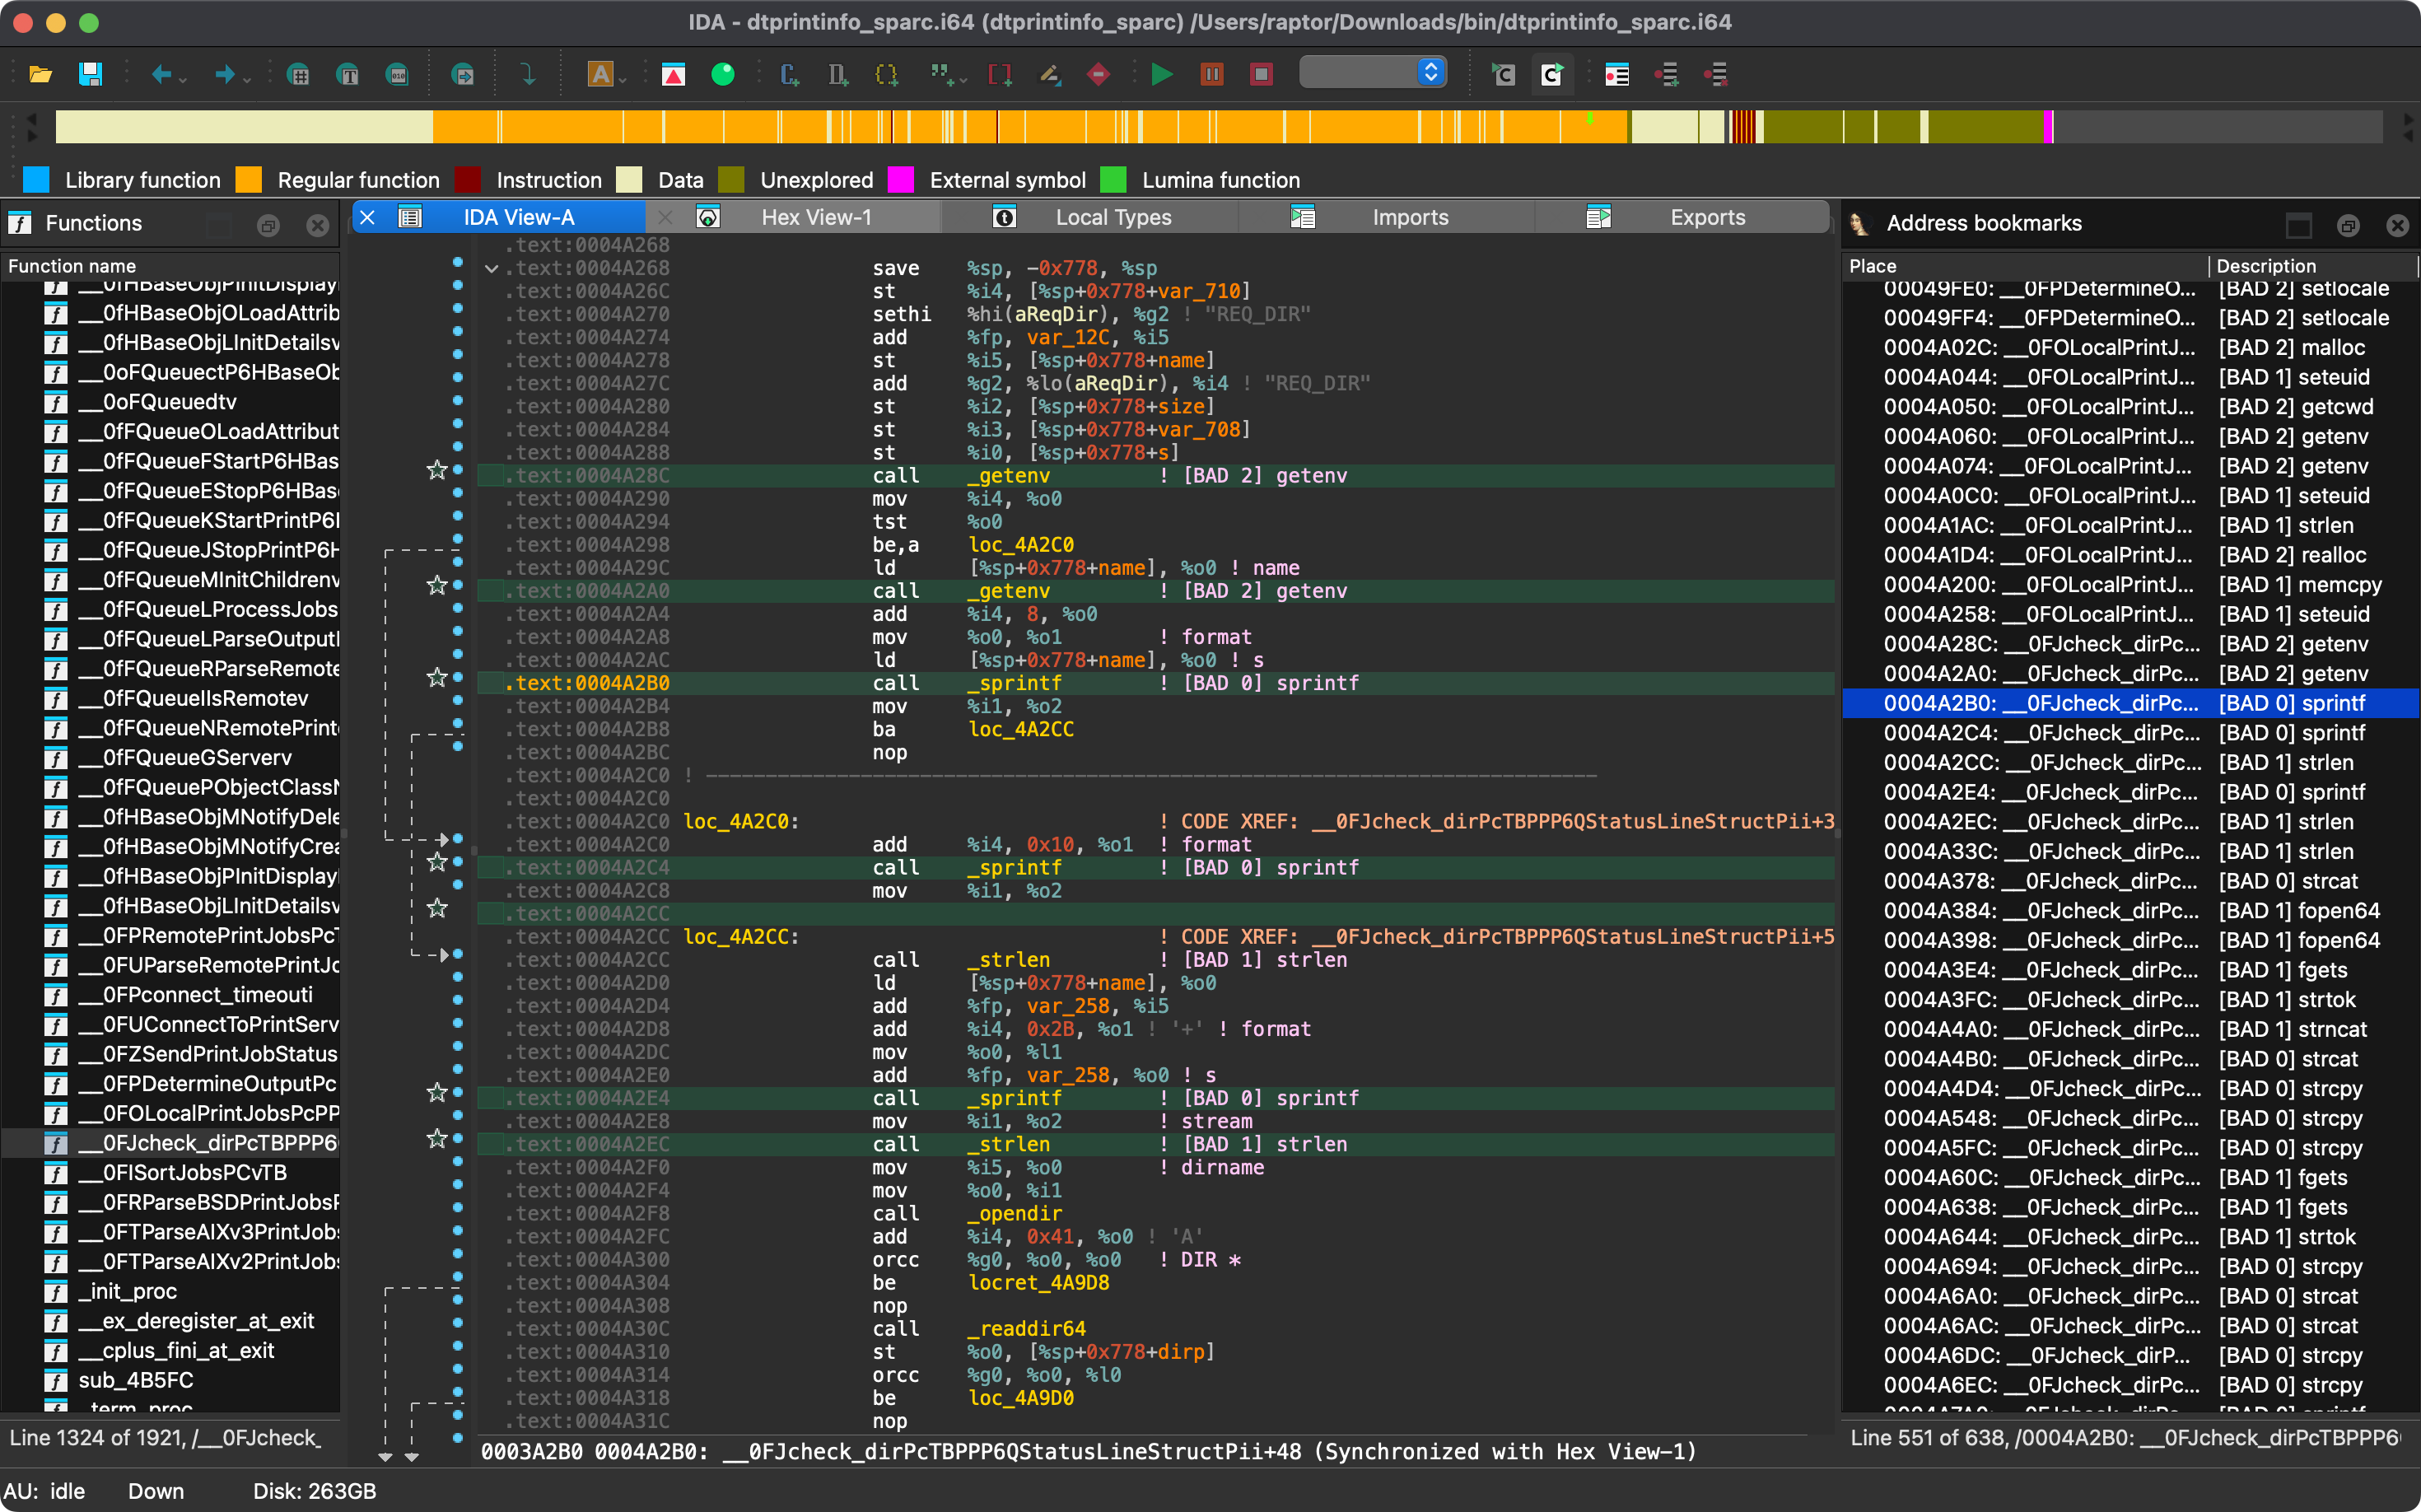 0xdea/rhabdomancer
Vulnerability research assistant that locates calls to potentially insecure API functions in a binary file.
 fboldewin/com-code-helper
Two IDAPython Scripts help you to reconstruct Microsoft COM (Component Object Model) Code
 synacktiv/lumina_server
Local server for IDA Lumina feature
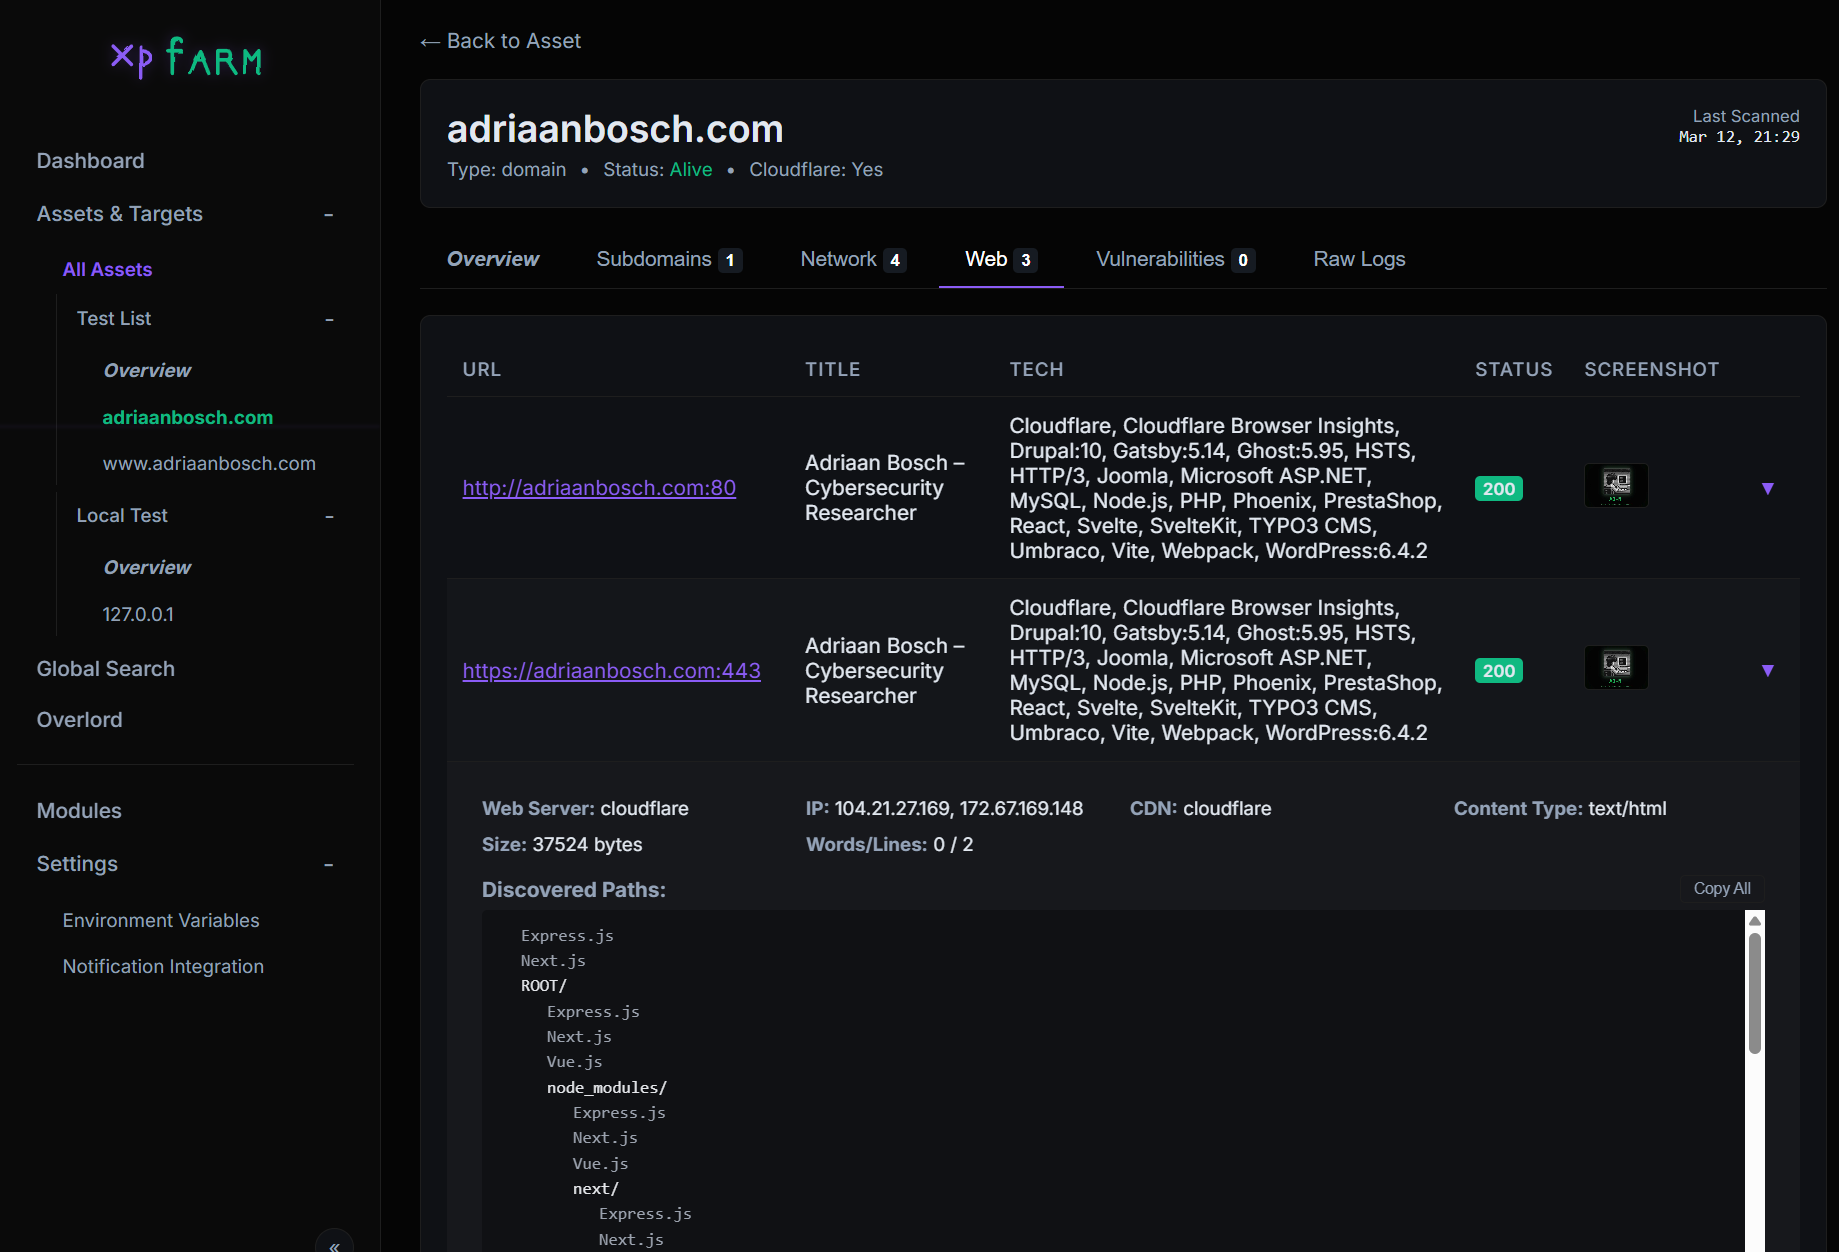 canuk40/xpfarm
Automated bug bounty & recon framework — wraps Subfinder, Naabu, Httpx, Nuclei, Nmap, CVEMap, Gowitness, Katana & more behind a unified web UI
 nazywam/autoit-ripper
Extract AutoIt scripts embedded in PE binaries
 ricardoquesada/regenerator2000
An interactive disassembler for the CPU 6502, focused on Commodore 8-bit computers. Features a TUI with modern features like x-ref, undo/redo, flow…
 mzakocs/qualcomm_baseband_scripts
Collection of scripts for reversing Qualcomm Hexagon baseband / modem firmware
 takahiroharuyama/ida_haru
scripts/plugins for IDA Pro
 mrphrazer/obfuscation_analysis
Binary Ninja plugin to analyze and simplify obfuscated code
 malwaretech/fakembr
TDL4 style rootkit to spoof read/write requests to master boot record
 wheregoes/byd-dolphin-hacking
Reverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.








