Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
nocturne — A bin2bin code virtualizer for x86-64 PE's | Kitploit

Tools/GitHubGitHub/nodiuus/nocturne
Payload GenerationExploitationReverse EngineeringShellcodePenetration TestingBinary AnalysisRed TeamingBinary Exploitation
GitHubnodiuus/nocturne

nocturne

A bin2bin code virtualizer for x86-64 PE's

View Repository
17115765 months agoReviewed by Kitploit
Share

nocturne

Named after one of my favorite games, "nocturne" is a bin2bin x86-64 PE code virtualizer and binary rewriter.

Features

  • Native Call Bridge
  • 30+ VM Handlers
  • Built-in junk code obfuscation
  • Thread-safe per-invocation VM state

Usage

To use the Nocturne virtualizer, copy and include "nocturne_sdk.hpp" from core/ into your project.

#include "nocturne_sdk.hpp"

VIRTUALIZE int secret(int x) {
	if (x % 2 == 0) {
		return x / 2;
	} else {
		return x * 3 + 1;
	}
}
VIRTUALIZE_MARK(secret);

Afterwards, run the cli executable.

cli.exe -i <input.exe> -o <output.exe>

Example:

cli.exe -i example.exe -o example_protected.exe

By default, the CLI uses auto mode.

Or, explicitly:

cli.exe -i <input.exe> -o <output.exe> --mode auto

Example:

cli.exe -i example.exe -o example_protected.exe --mode auto

To scan for markers:

cli.exe -i <input.exe> -o <output.exe> --mode markers

Example:

cli.exe -i example.exe -o example_protected.exe --mode markers

Or, if you want to virtualize specific segments of a binary without the SDK:

cli.exe -i <input.exe> -o <output.exe> --mode rva <start_rva> <end_rva>

Example:

cli.exe -i calc.exe -o calc_vmp.exe --mode rva 0x1600 0x1864

Screenshots

Before Virtualization: image

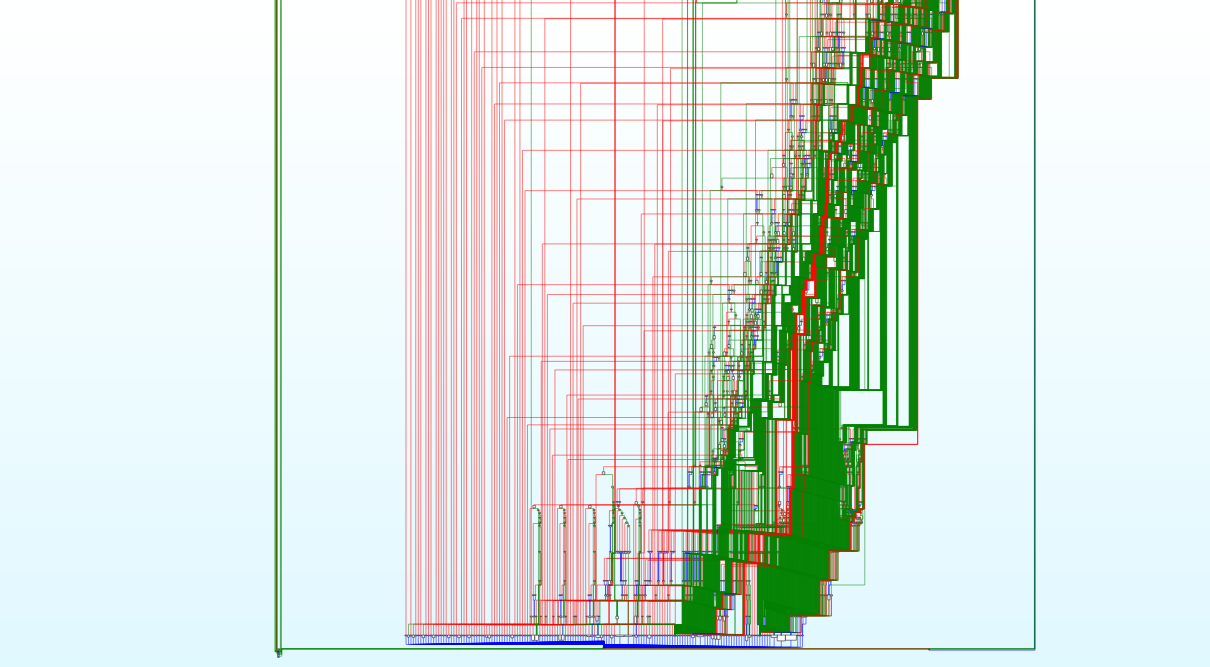
After Virtualization:

image

Obfuscated dispatcher loop: image

Dependencies

LIEF
Zydis
argparse

Disclaimer

First and foremost, this is mostly a POC project. Please don't expect it to be too stable. With that being said, I will be progressively adding more features/fixes to this as time goes on.

If there are any features / handlers you want implemented, I implore you to open an issue. I welcome any and all contributions.

License

This project is source-available, not open source.

The source code is available under the PolyForm Noncommercial License 1.0.0.

You may use, study, modify, and share this software for noncommercial purposes, subject to the license terms.

Commercial use, enterprise use, internal company use, production business use, hosted services, paid products, client work, consulting work, or organizational deployment is not permitted without a separate written license.

For commercial or enterprise licensing, contact: [email protected] / @nodiuus

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    795
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    520
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    439
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    267
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →