
 #1
Binary reverse engineering, disassembly, decompilation, and patching tools.
Kitploit recommended
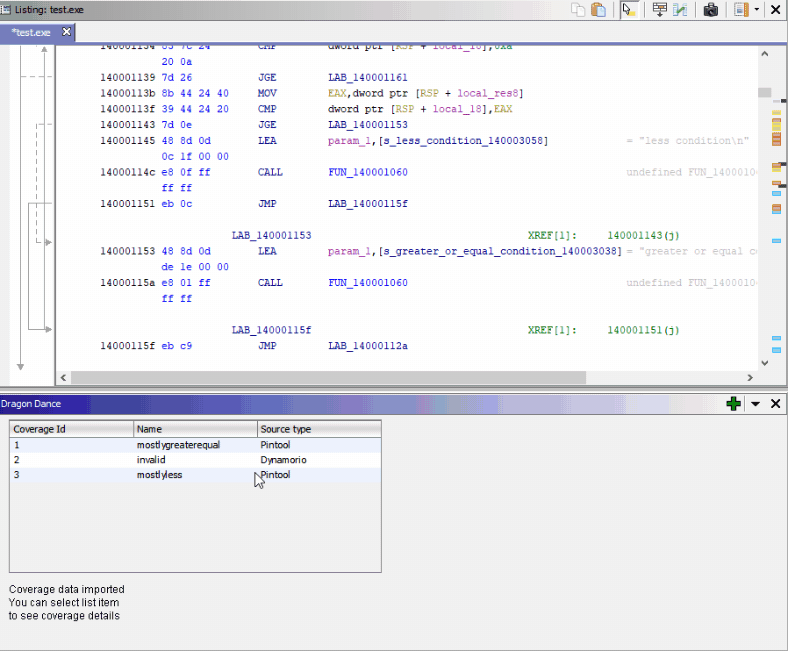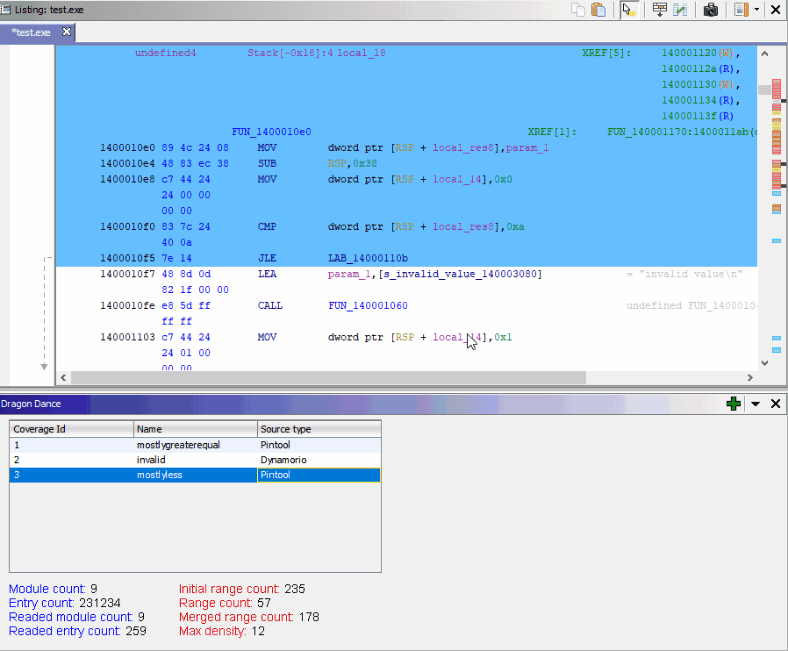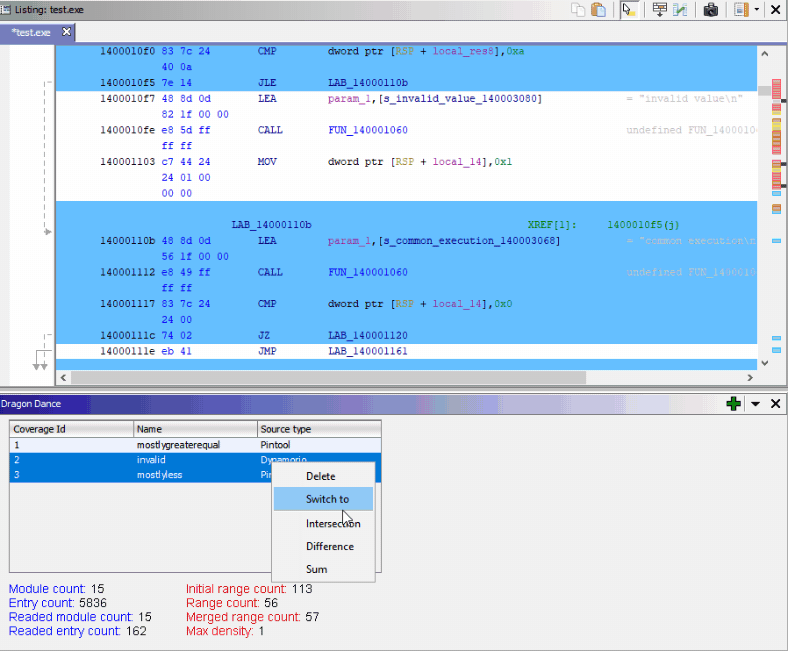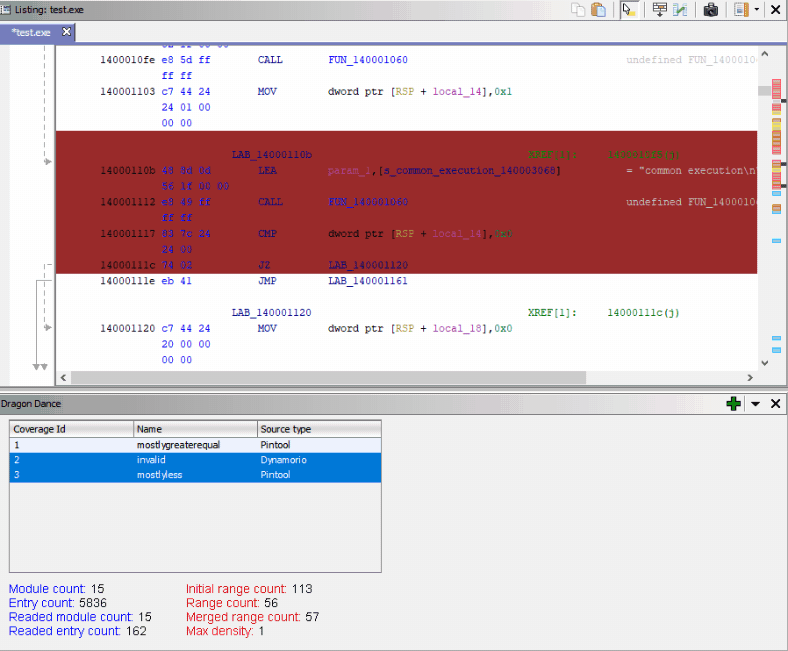
 0ffffffffh/dragondance
Binary code coverage visualizer plugin for Ghidra
 nevesnunes/z80-sans
OpenType font that disassembles Z80 instructions
 amossys/memitm
Tool to make in memory man in the middle
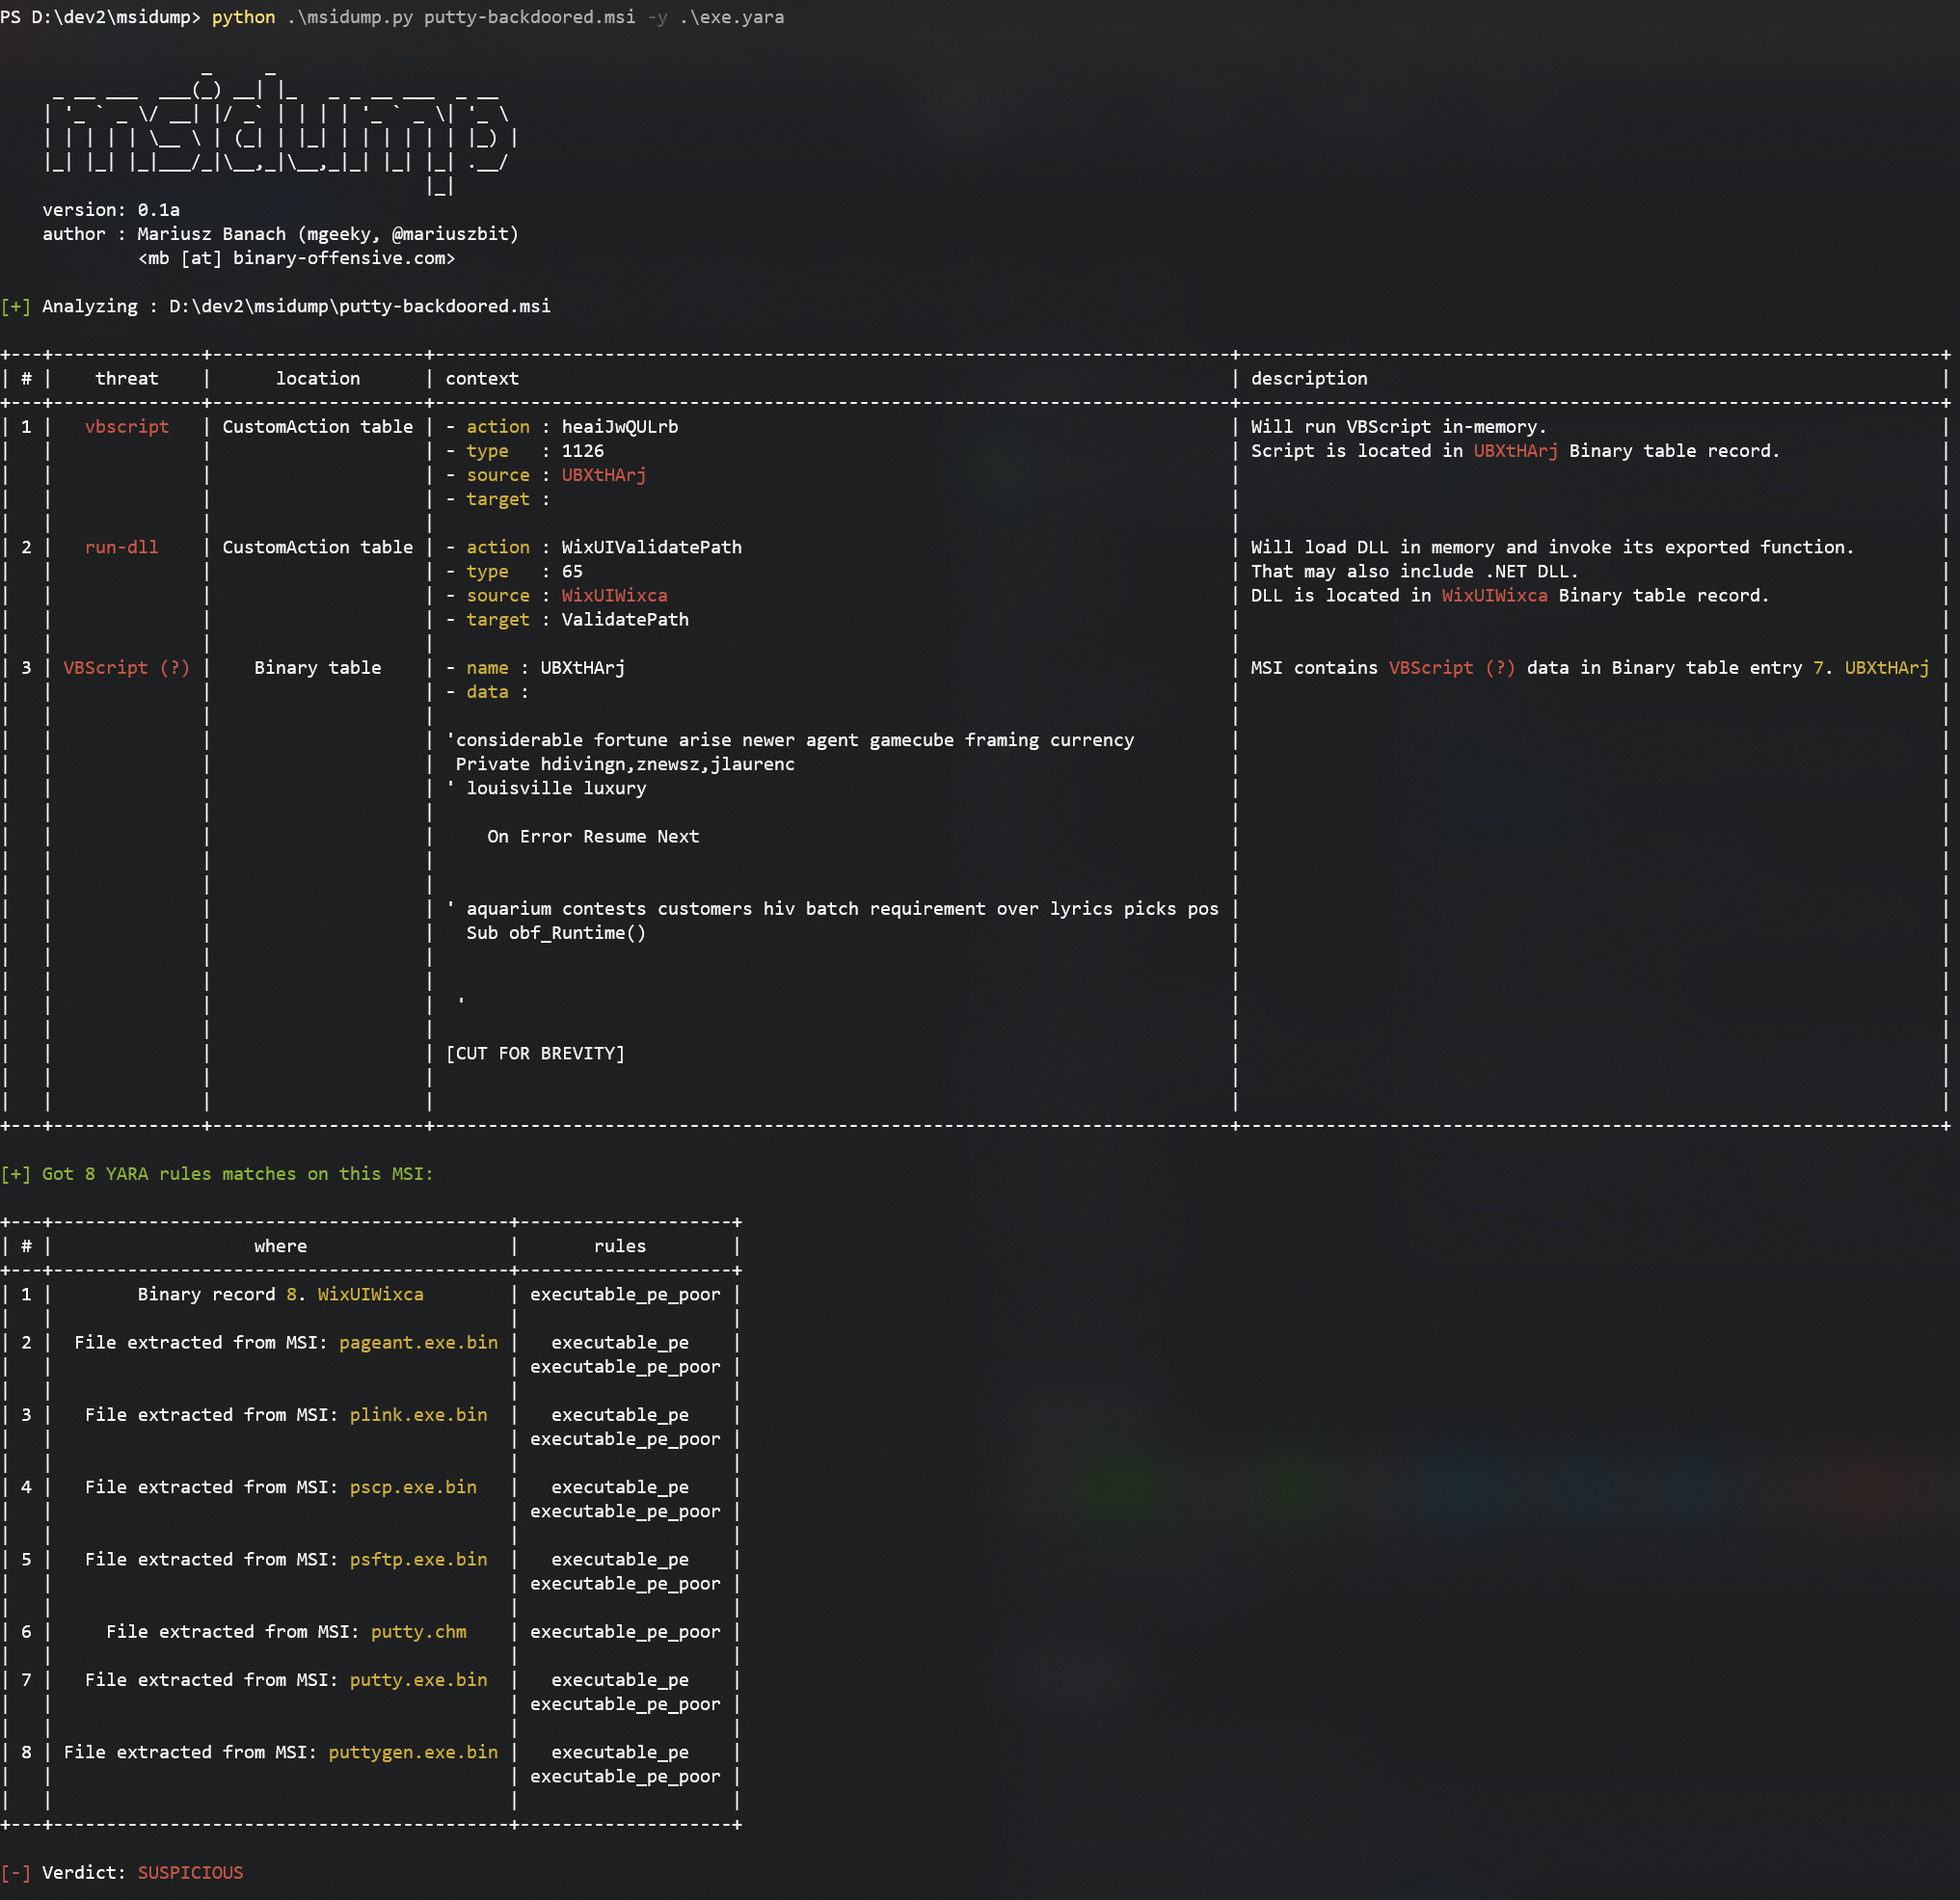 mgeeky/msidump
MSI Dump - a tool that analyzes malicious MSI installation packages, extracts files, streams, binary data and incorporates YARA scanner.
 hari-prasaanth/thick-client-pentest-checklist
A OWASP Based Checklist With 80+ Test Cases
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 nteseyes/pylane
An python vm injector with debug tools, based on gdb.
 penberg/chimera
Sandbox untrusted code with safe access to the host.
 zimawhit3/bitmancer
Nim Library for Offensive Security Development
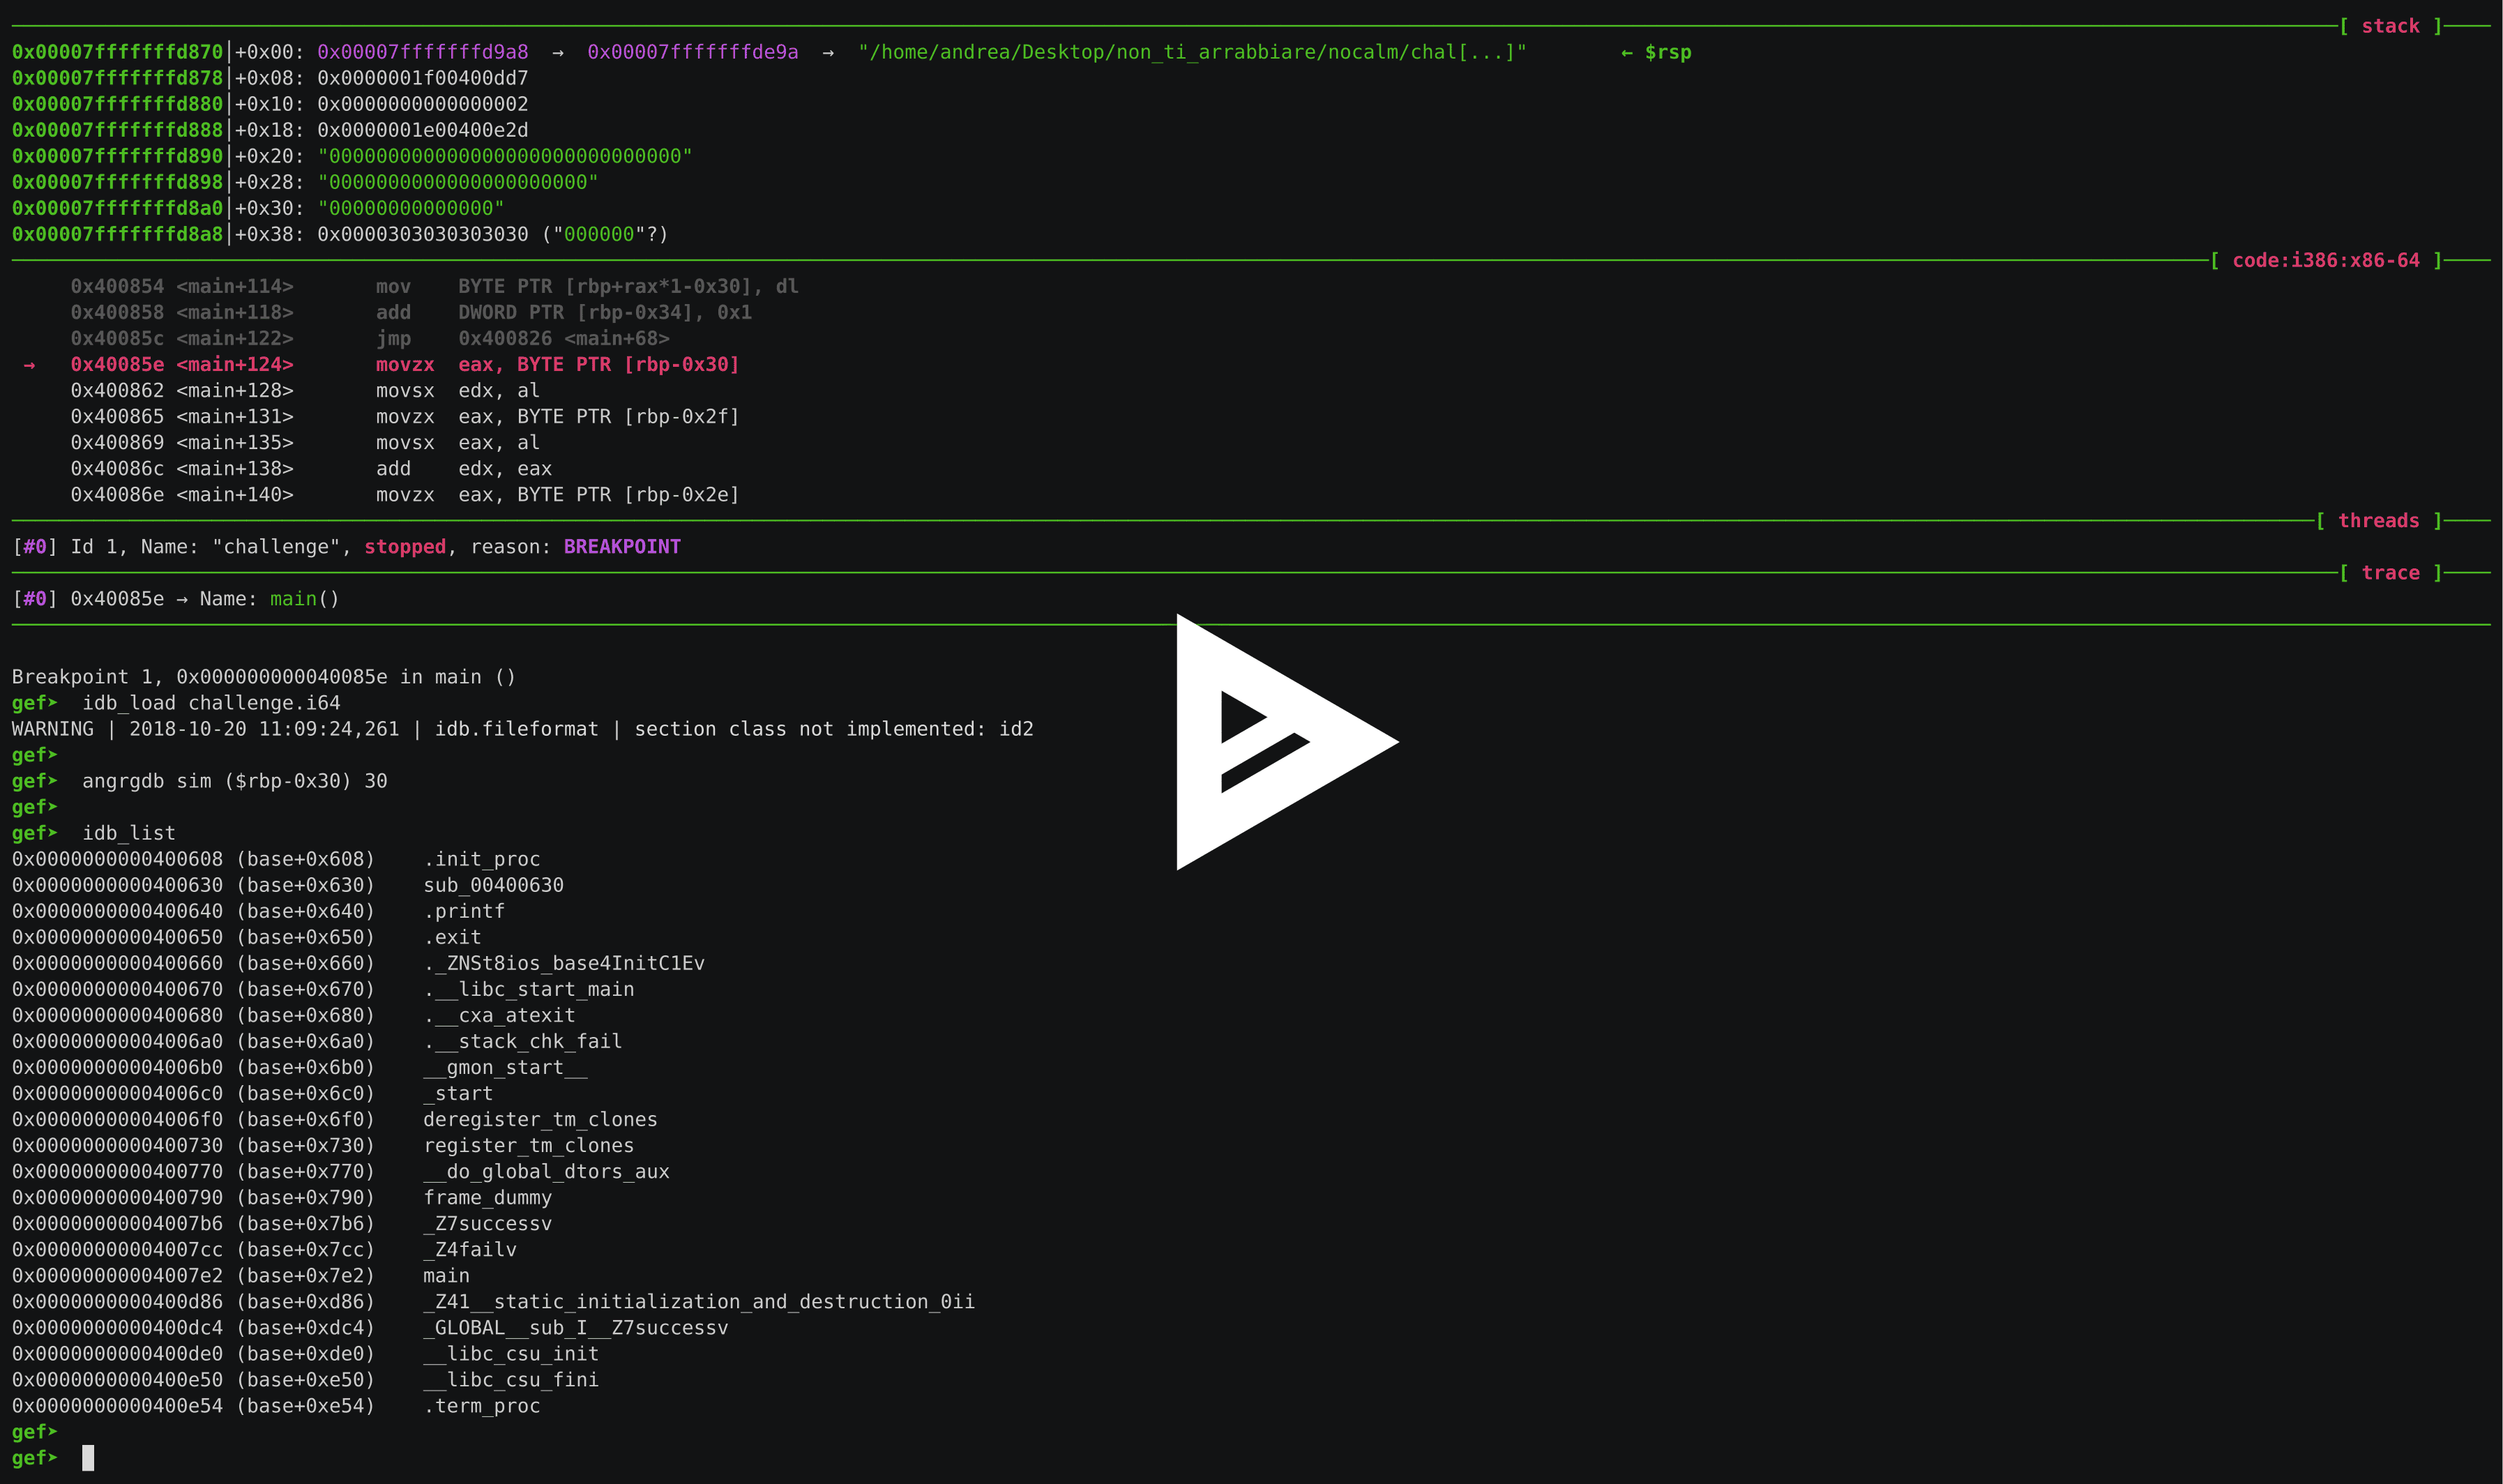 andreafioraldi/angrgdb
Use angr inside GDB. Create an angr state from the current debugger state.
 mandiant/dncil
The FLARE team's open-source library to disassemble Common Intermediate Language (CIL) instructions.
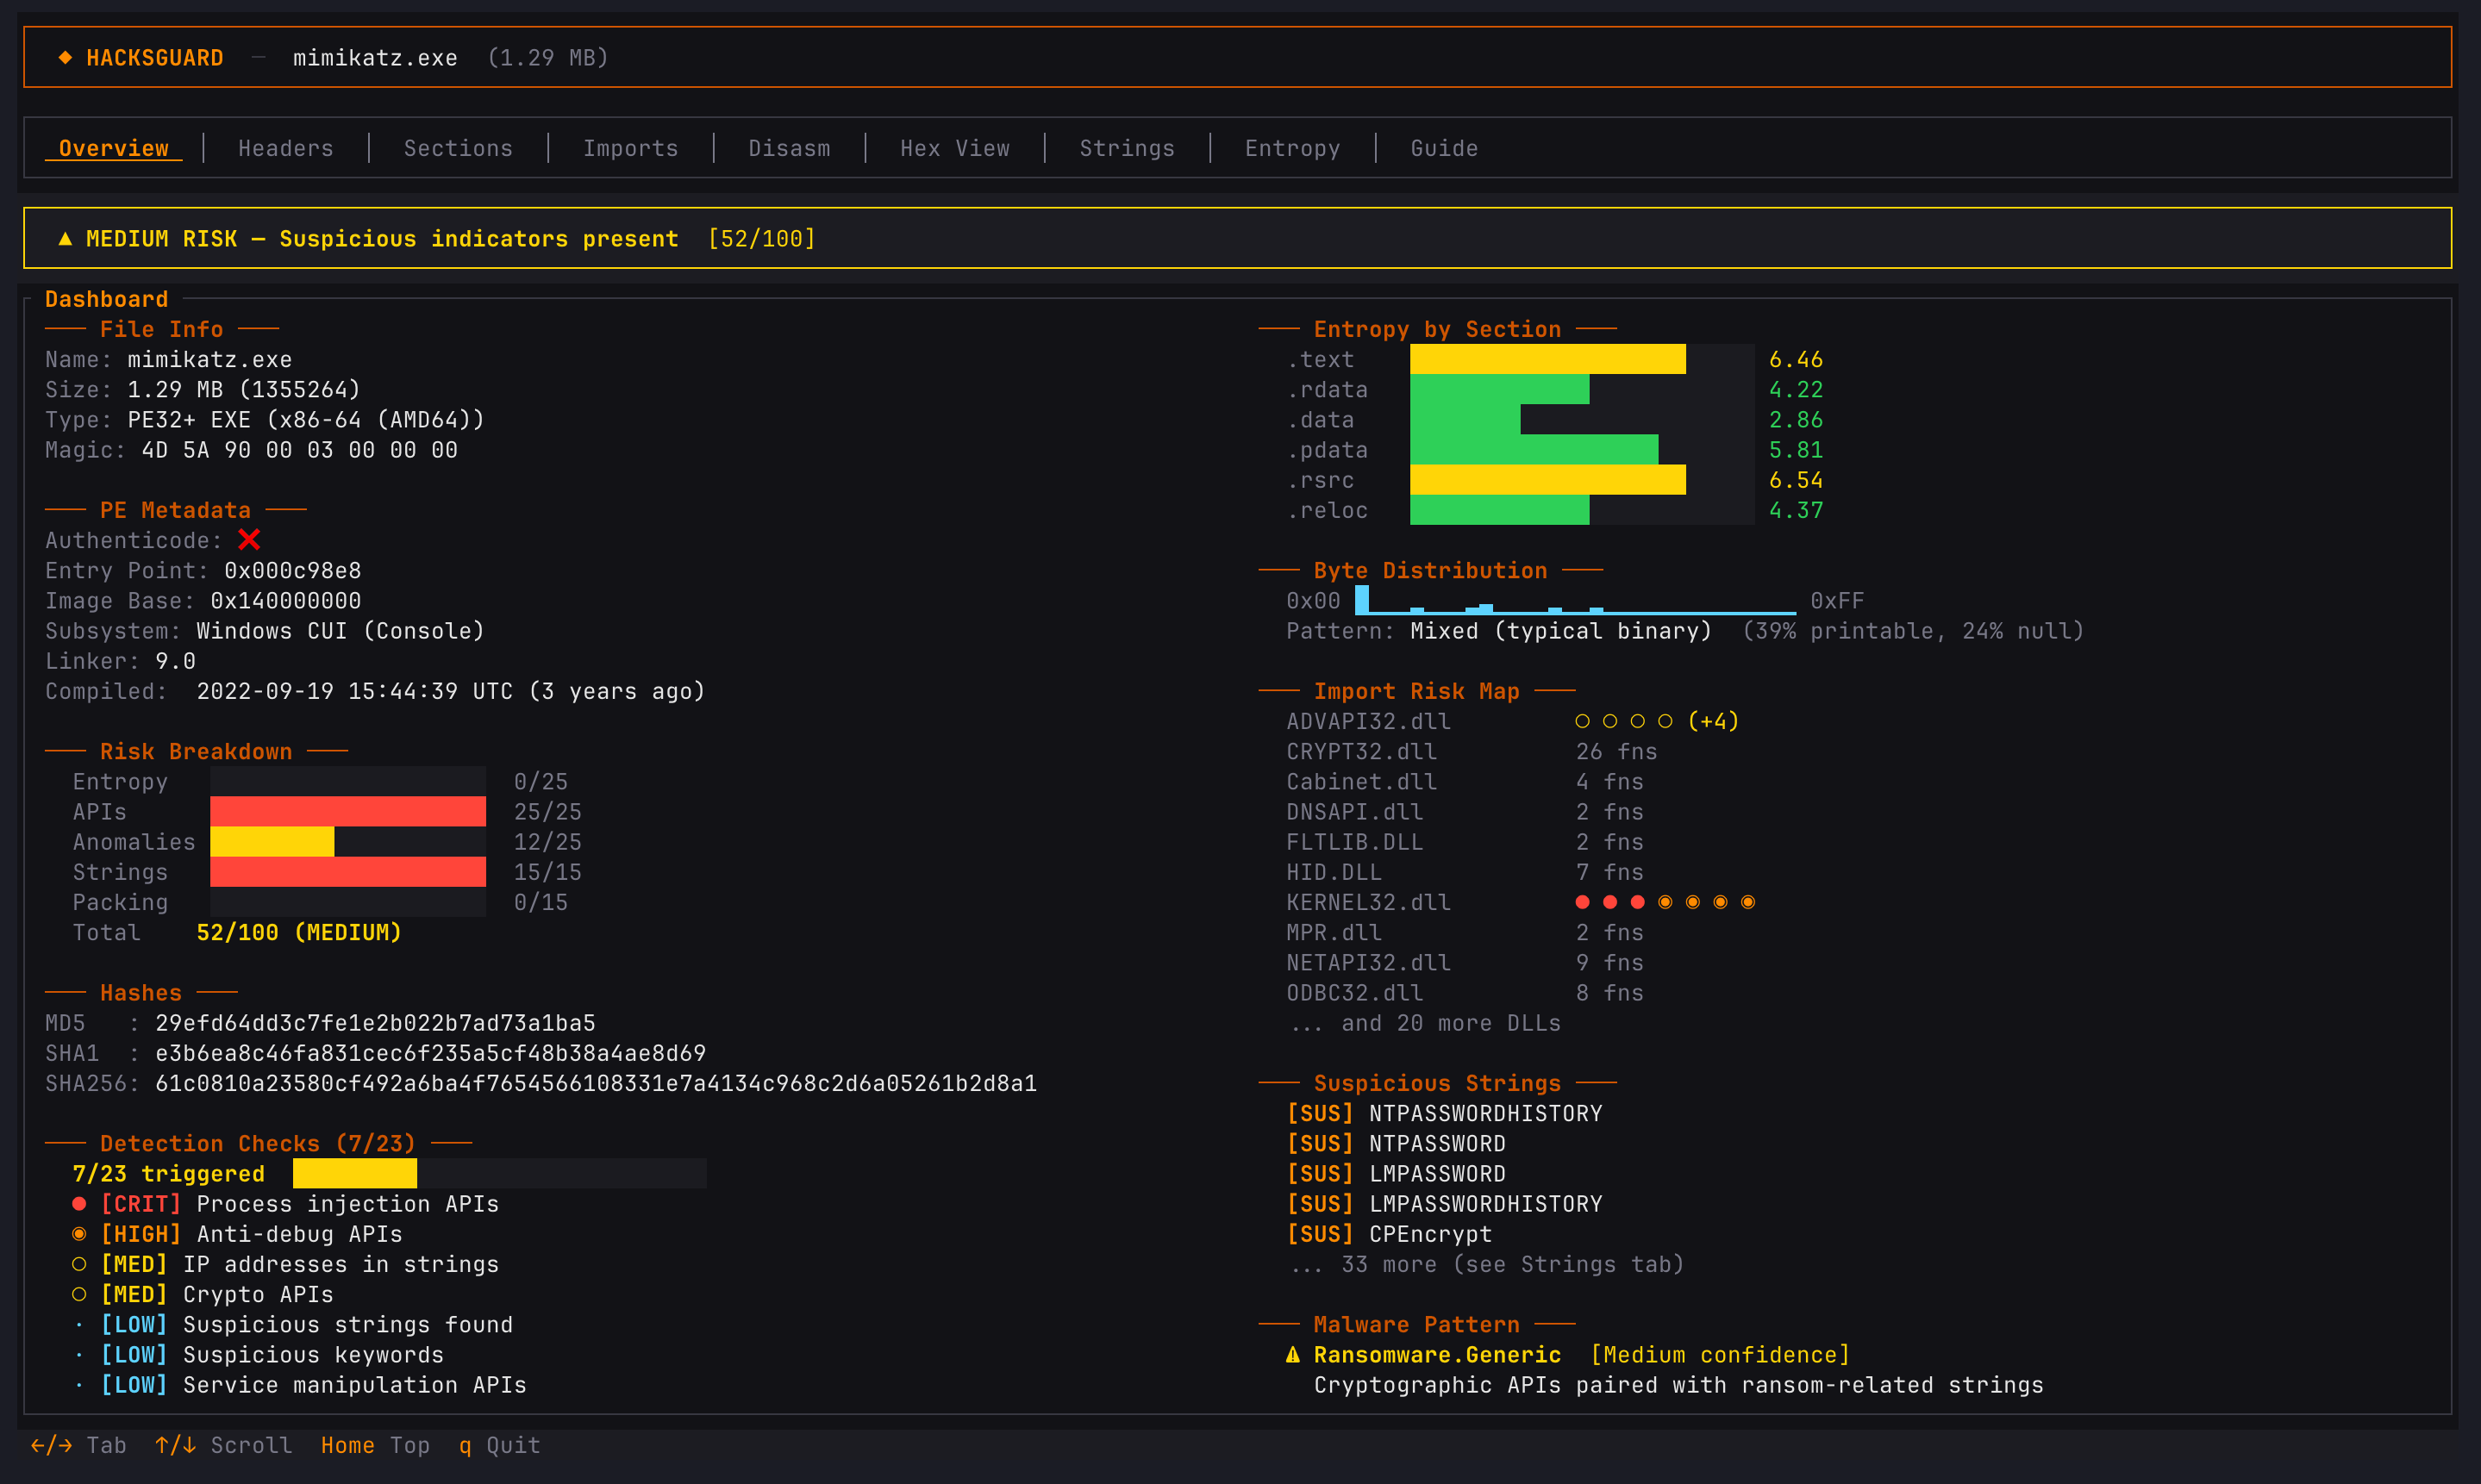 rhacknarok/hacksguard
A blazingly fast, multi-threaded TUI malware analysis tool built in Rust. Features deep PE parsing, YARA scanning, and heuristic risk scoring.
 lab52io/leakedhandlesfinder
Leaked Windows processes handles identification tool
 dnakov/r2d2
🤖🏴☠️ radare2 plugin for GPT-4 🦜. Solve crackmes automatically 🪄
 robindavid/idasec
IDA plugin for reverse-engineering and dynamic interactions with the Binsec platform
 gamozolabs/elfloader
An architecture-agnostic ELF file flattener for shellcode
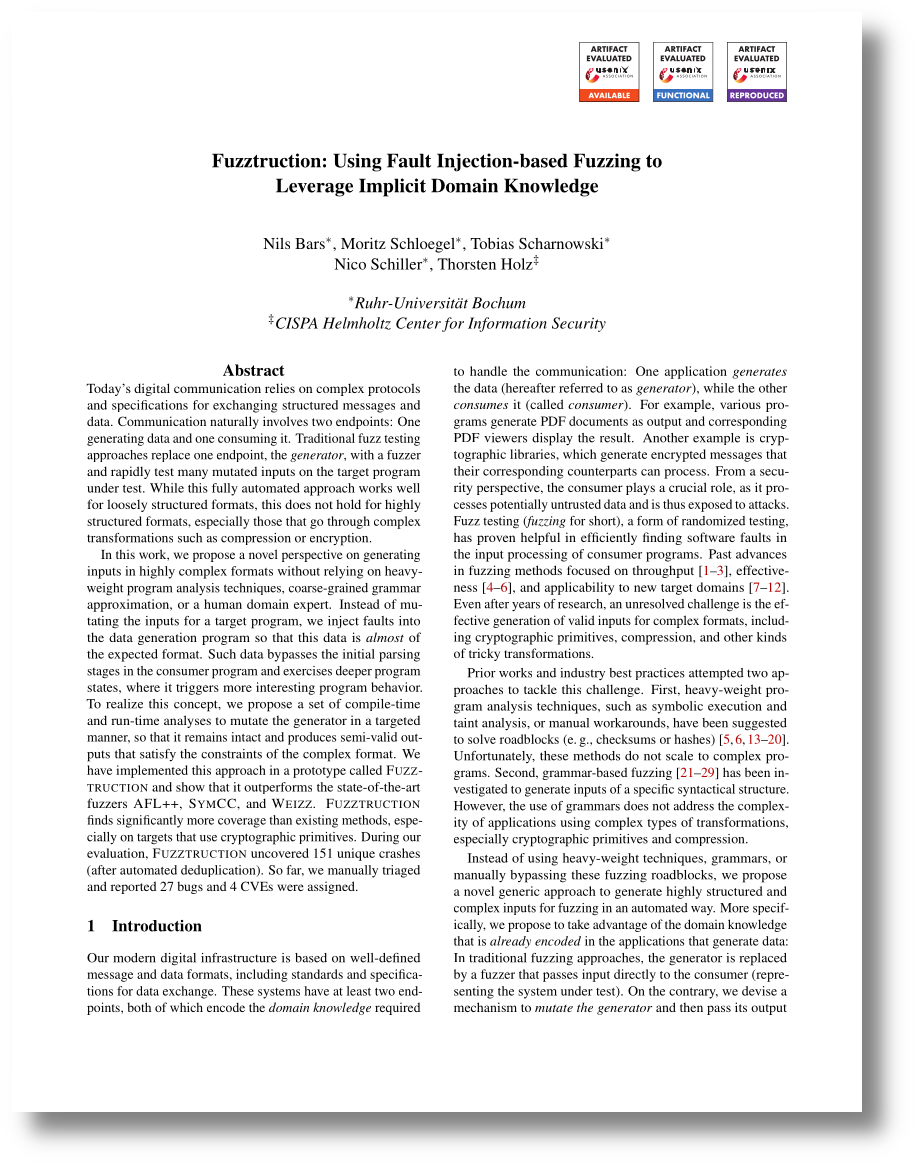 fuzztruction/fuzztruction
Fault-injection-based fuzzer that mutates generator programs to produce almost-valid inputs for targets, enabling fuzzing of complex formats and…
 jschicht/logfileparser
Parser for $LogFile on NTFS








