
 #1
 oalabs/findyara-ida
IDA python plugin to scan binary with Yara rules
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 fuzzuf/fuzzuf
Modular fuzzing framework with a DSL (HierarFlow) to compose fuzzing loops from reusable primitives. Supports AFL, libFuzzer, VUzzer, and more for…
 zx41r/awesome-reverse-engineering-and-malware-analysis
A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
 s3cur3th1ssh1t/nimgetsyscallstub
Dynamically extracts fresh syscall stubs from ntdll.dll to evade signature-based detection, with a shellcode execution template for Nim-based…
 hugsy/windbg_js_scripts
Toy scripts for playing with WinDbg JS API
 gadiluna/safe
SAFE: Self-Attentive Function Embeddings for binary similarity
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 mrphrazer/binary-cartography
Technical webinars on reverse engineering, malware analysis, and software protection.
 oalabs/frida-extract
Frida.re based RunPE (and MapViewOfSection) extraction tool
 plum-umd/redexer
The Redexer binary instrumentation framework for Dalvik bytecode
 netspooky/inhale
A malware analysis and classification tool.
 ynwarcs/cve-2025-21298
Proof of concept & details for CVE-2025-21298
 shemesh999/oregami
IDA plugins and scripts for analyzing register usage frame
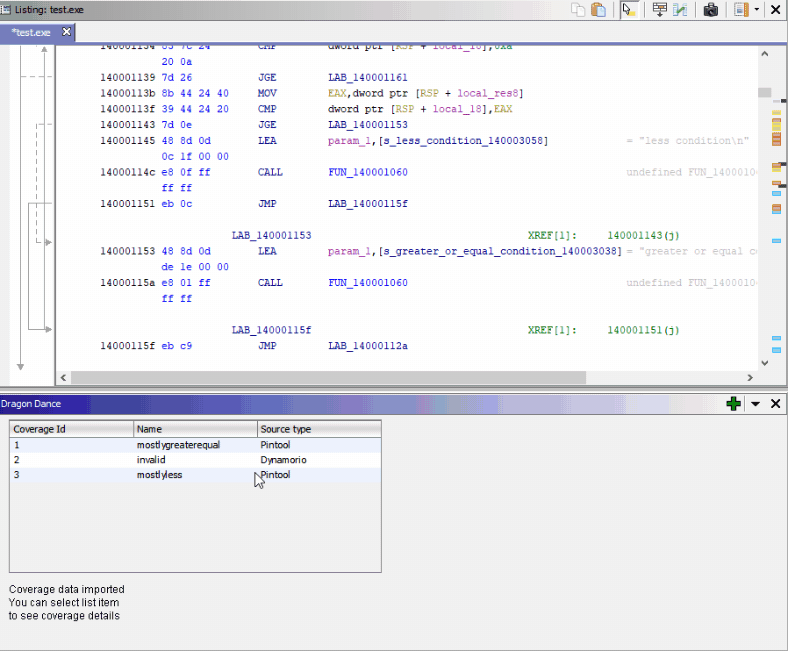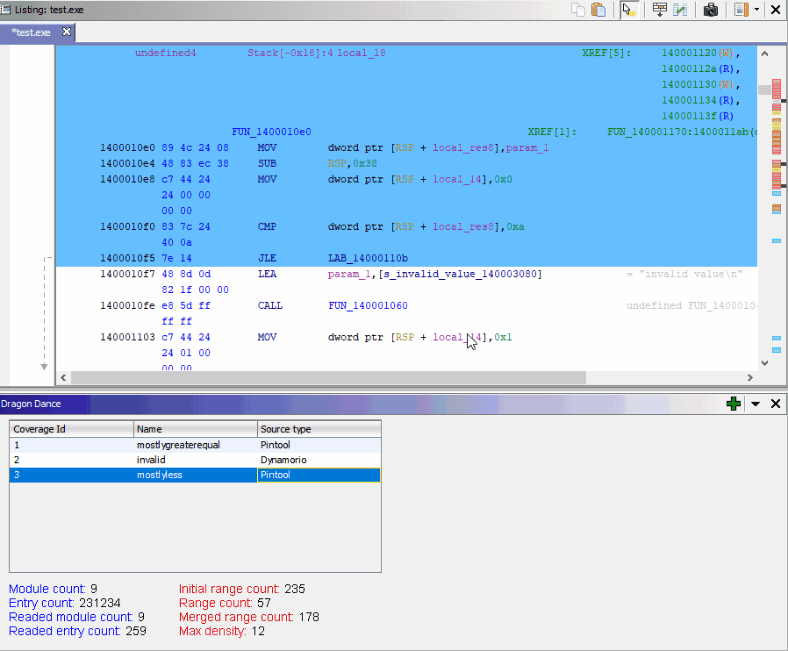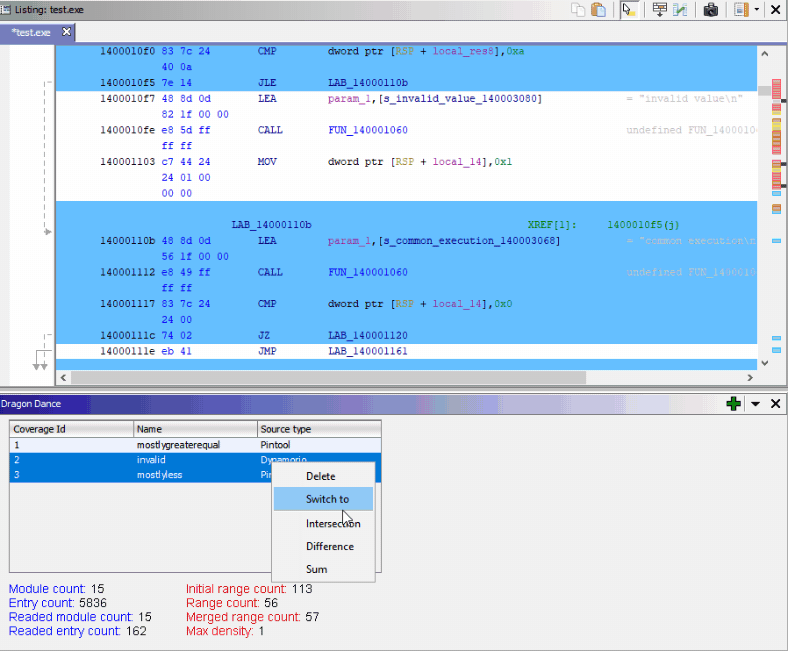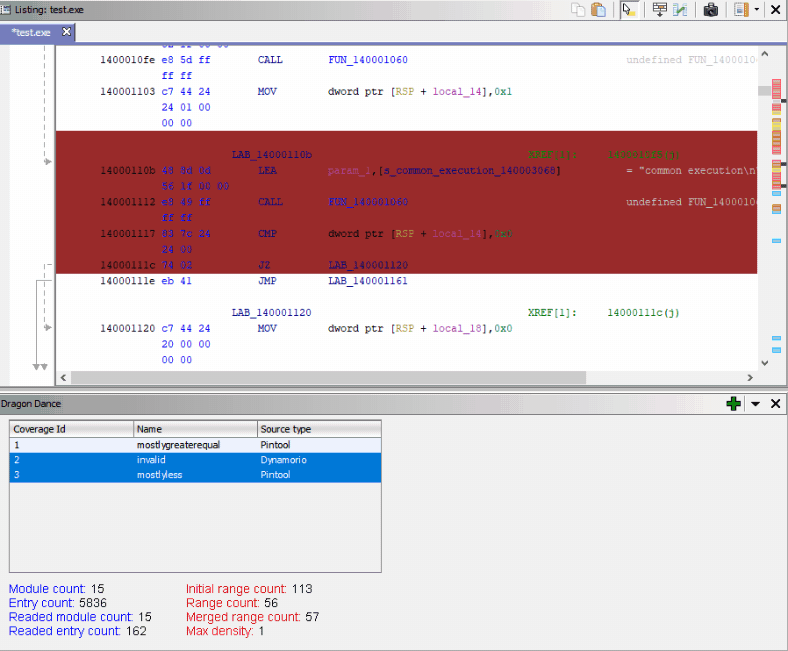 0ffffffffh/dragondance
Binary code coverage visualizer plugin for Ghidra









