Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Binary Analysis — Page 27 | Kitploit
Categories

Binary Analysis

Binary reverse engineering, disassembly, decompilation, and patching tools.

Kitploit recommended
Top tools

10 selected
ghidra preview#1

ghidra

GitHubnationalsecurityagency/ghidra
71.1k5h 31m ago
radare2 preview#2

radare2

GitHubradareorg/radare2
24.5k4h 39m ago
cutter preview#3

cutter

GitHubrizinorg/cutter
19.4k9h 23m ago
rizin preview#4

rizin

GitHubrizinorg/rizin
4.1k3 months ago
x64dbg preview#5

x64dbg

GitHubx64dbg/x64dbg
49.1k6 days ago
angr preview#6

angr

GitHubangr/angr
9.0k1 day ago
capa preview#7

capa

GitHubmandiant/capa
6.1k6 hours ago
Detect-It-Easy preview#8

Detect-It-Easy

GitHubhorsicq/detect-it-easy
11.3k6h 52m ago
LIEF preview#9

LIEF

GitHublief-project/lief
5.5k2 days ago
ImHex preview#10

ImHex

GitHubwerwolv/imhex
54.4k26 days ago
NewestRelevanceMost popularRecently updated
1662 results
cdf preview

cdf

GitHubkudelskisecurity/cdf

Automated differential fuzzing tool for cryptographic software that detects implementation errors, compliance failures, and side-channel leaks…

vulnerability-analysisfuzzingcryptography+1
1715 years ago
rePy2exe preview

rePy2exe

GitHub4w4k3/repy2exe

A Reverse Engineering Tool for py2exe applications.
static-analysisreverse-engineeringmalware-analysis+1
2089 years ago
drAFL preview

drAFL

GitHubmxmssh/drafl

AFL + DynamoRIO = fuzzing binaries with no source code on Linux
dynamic-analysis-sandboxingexploitationfuzzing+1
2497 years ago
NinjaDroid preview

NinjaDroid

GitHubrovellipaolo/ninjadroid

Ninja Reverse Engineering on Android APK packages
android-securitystatic-analysisreverse-engineering+2
2877 days ago
idamcp preview

idamcp

GitHubidamcp/idamcp

MCP server integrating IDA Pro with AI agents, featuring a stateless gateway for multi-session management, a relational SQL query engine for binary…
static-analysisdynamic-analysis-sandboxingreverse-engineering+3
1251 day ago
PortexAnalyzerGUI preview

PortexAnalyzerGUI

GitHubstruppigel/portexanalyzergui

Graphical interface for PortEx, a Portable Executable and Malware Analysis Library
static-analysishash-analysisreverse-engineering+3
14913 days ago
autoPwn preview

autoPwn

GitHubbannsec/autopwn

Automate repetitive tasks for fuzzing

exploitationfuzzingbinary-analysis
1265 years ago
FwHunt preview

FwHunt

GitHubbinarly-io/fwhunt

The Binarly Firmware Hunt (FwHunt) rule format was designed to scan for known vulnerabilities in UEFI firmware.

embedded-systems-securityvulnerability-scannersvulnerability-analysis+3
2482 years ago
scan preview

scan

GitHubatomdrift-project/scan

0-day malware detection for binaries, source & scripts (that doesn't suck)

defensive-toolsstatic-analysisvulnerability-scanners+9
22510h 53m ago
how_to_become_a_malware_analyst preview

how_to_become_a_malware_analyst

GitHubpinksawtooth/how_to_become_a_malware_analyst

Curated guide to becoming a malware analyst, covering essential knowledge, reverse engineering, analysis tools, and LLM-assisted learning with…
memory-forensicsreverse-engineeringmalware-analysis+7
2841 month ago
PolyEngine preview

PolyEngine

GitHublongwayhomie/polyengine

PolyEngine is an evasive PE packer designed for CTF challenges and low-level Windows security education. It focuses on bypassing EDR and AV…
payload-generationexploitationids-ips-evasion+6
1542 months ago
fwhunt-scan preview

fwhunt-scan

GitHubbinarly-io/fwhunt-scan

Tools for analyzing UEFI firmware and checking UEFI modules with FwHunt rules
embedded-systems-securityiot-securityvulnerability-analysis+3
2431 year ago
bread preview

bread

GitHubtheldus/bread

Injectable real-mode x86 debugger for BIOS reverse engineering and arbitrary real-mode code debugging via serial cable, with GDB integration and…

reverse-engineeringdebuggershardware-security+2
3261 year ago
malduck preview

malduck

GitHubcert-polska/malduck

🦆 Malduck is your ducky companion in malware analysis journeys
static-analysisdynamic-analysis-sandboxingreverse-engineering+3
3571 year ago
fhex preview

fhex

GitHubecho-devim/fhex

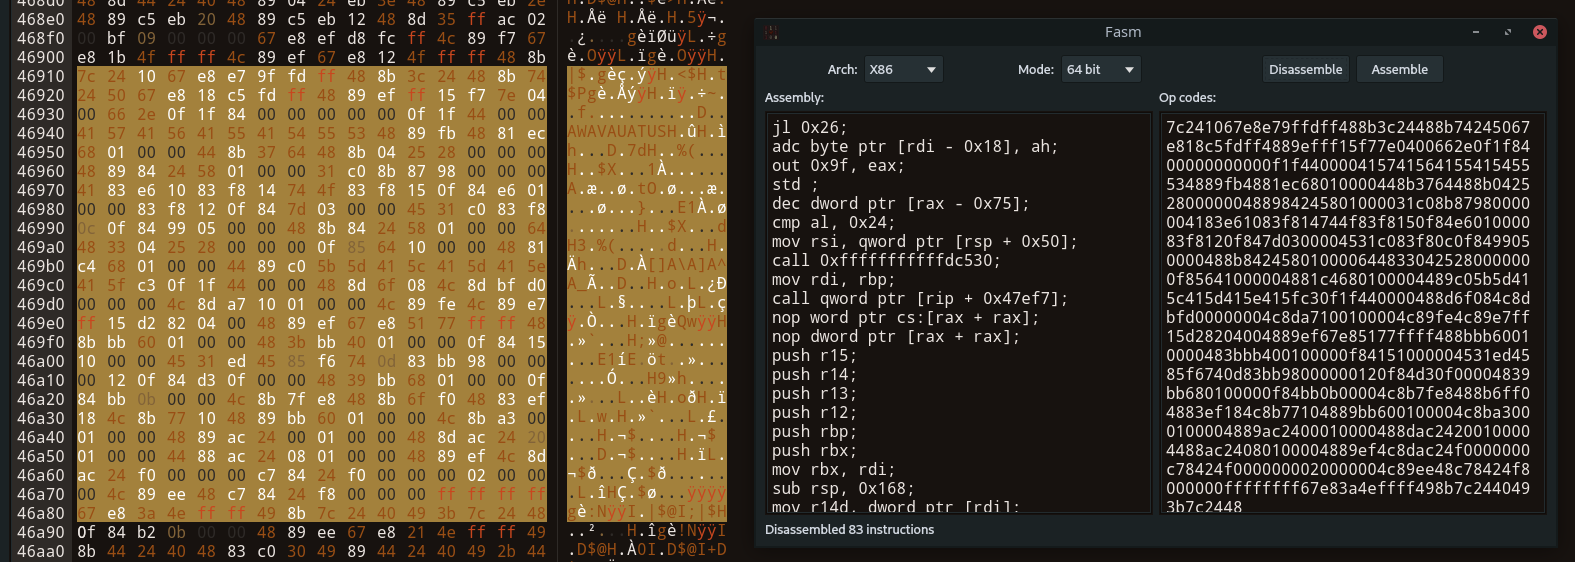
A Full-Featured HexEditor compatible with Linux/Windows/MacOS
general-purpose-utilitiesreverse-engineeringdebuggers+2
4371 year ago
REpsych preview

REpsych

GitHubbattelle/repsych

Psychological warfare in reverse engineering

reverse-engineeringsteganographybinary-analysis
21010 years ago
themida-unmutate preview

themida-unmutate

GitHubergrelet/themida-unmutate

Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.
static-analysisreverse-engineeringshellcode+3
3802 years ago
sass-king preview

sass-king

GitHubflorianmattana/sass-king

Reverse engineering NVIDIA SASS instruction dictionary, kernel audits and pattern recognition across GPU architectures.


embedded-systems-securitystatic-analysiscode-analysis+8
3175 months ago
Previous1…262728…93Next