#1
 trailofbits/rpcinvestigator
Windows RPC interface discovery and analysis tool with visual endpoint enumeration, PE parsing, symbol resolution, real-time ETW sniffing, and…
 risksense-ops/cve-2016-6366
Public repository for improvements to the EXTRABACON exploit
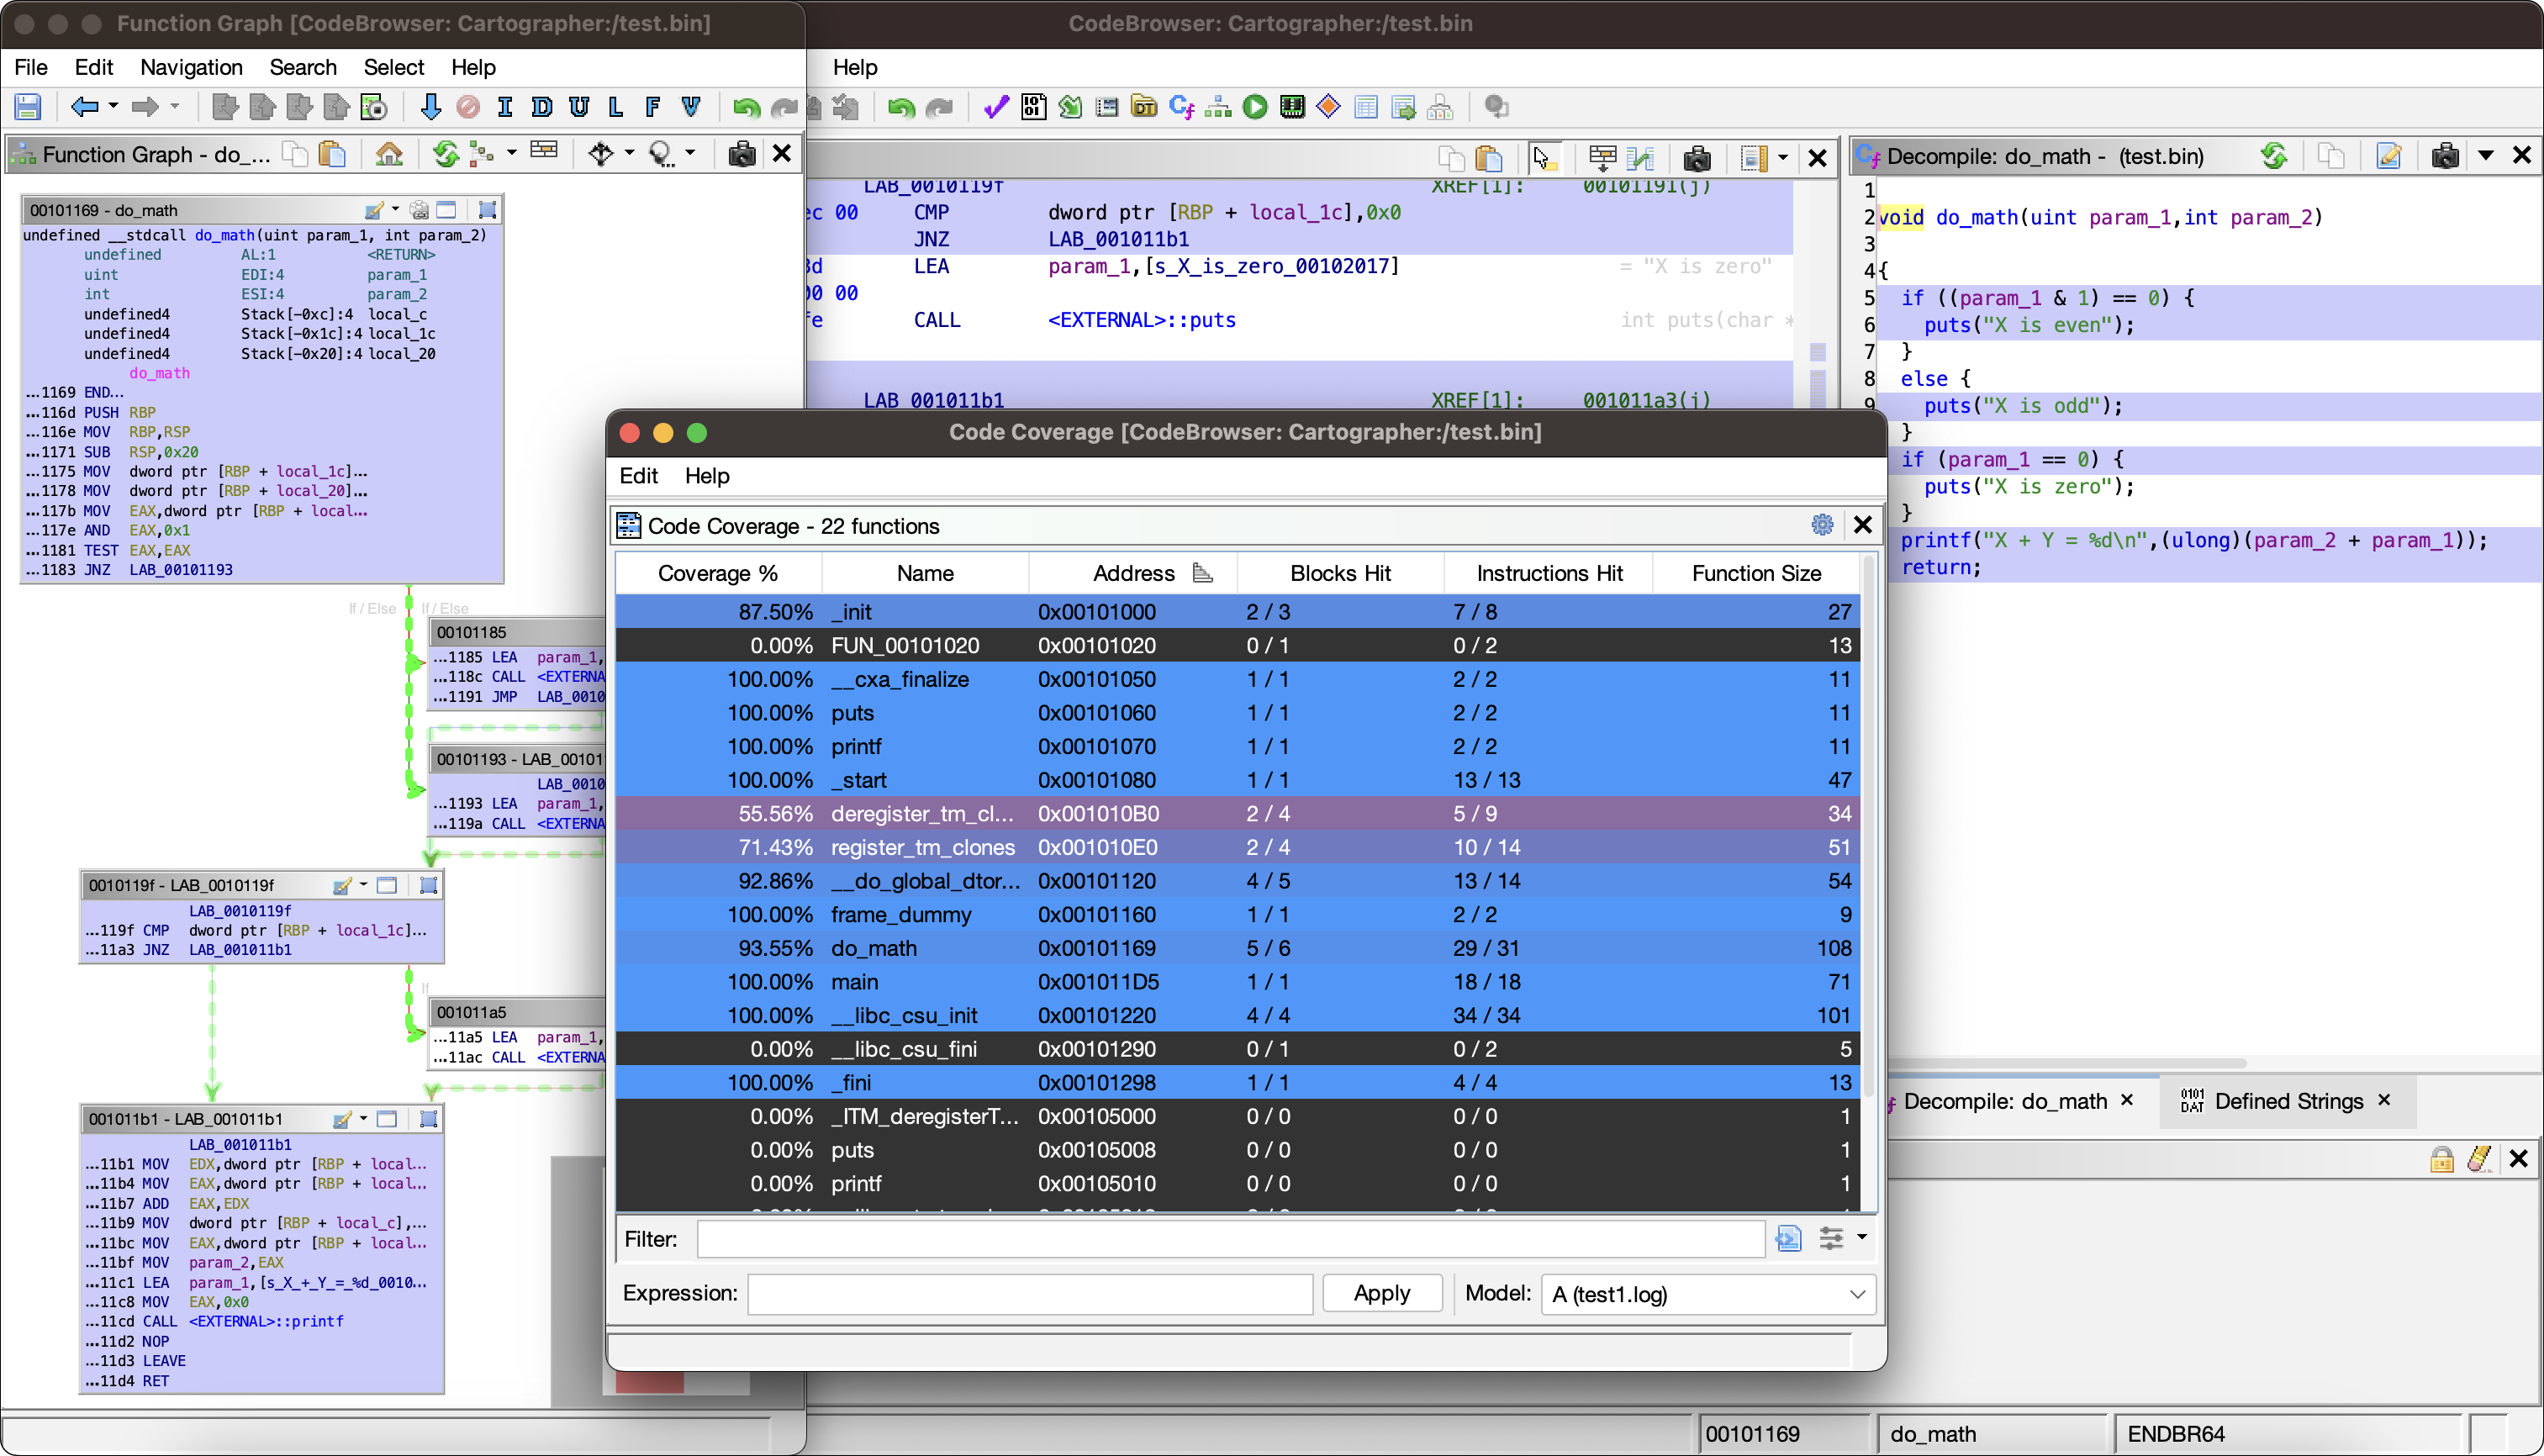 nccgroup/cartographer
Code Coverage Exploration Plugin for Ghidra
 drago-96/cve-2022-0778
Proof-of-concept exploit for CVE-2022-0778, demonstrating an infinite loop in OpenSSL's BN_mod_sqrt via a crafted X.509 certificate with non-prime…
 zznop/drow
Injects code into ELF executables post-build
 denuvosoftwaresolutions/gamba
Simplification of General Mixed Boolean-Arithmetic Expressions: GAMBA
 nccgroup/tpmgenie
TPM Genie is an I2C bus interposer for discrete Trusted Platform Modules
 yuatemycat/superghidra
Python toolkit accelerating Ghidra with a cached daemon, ARM64 P-code lifting, Z3 equivalence proofs, GPU-accelerated scanning, binary diffing, and…
 netspooky/scare
A multi-arch assembly REPL and emulator for your command line.
 delvinru/apk-info
APK full-featured parser
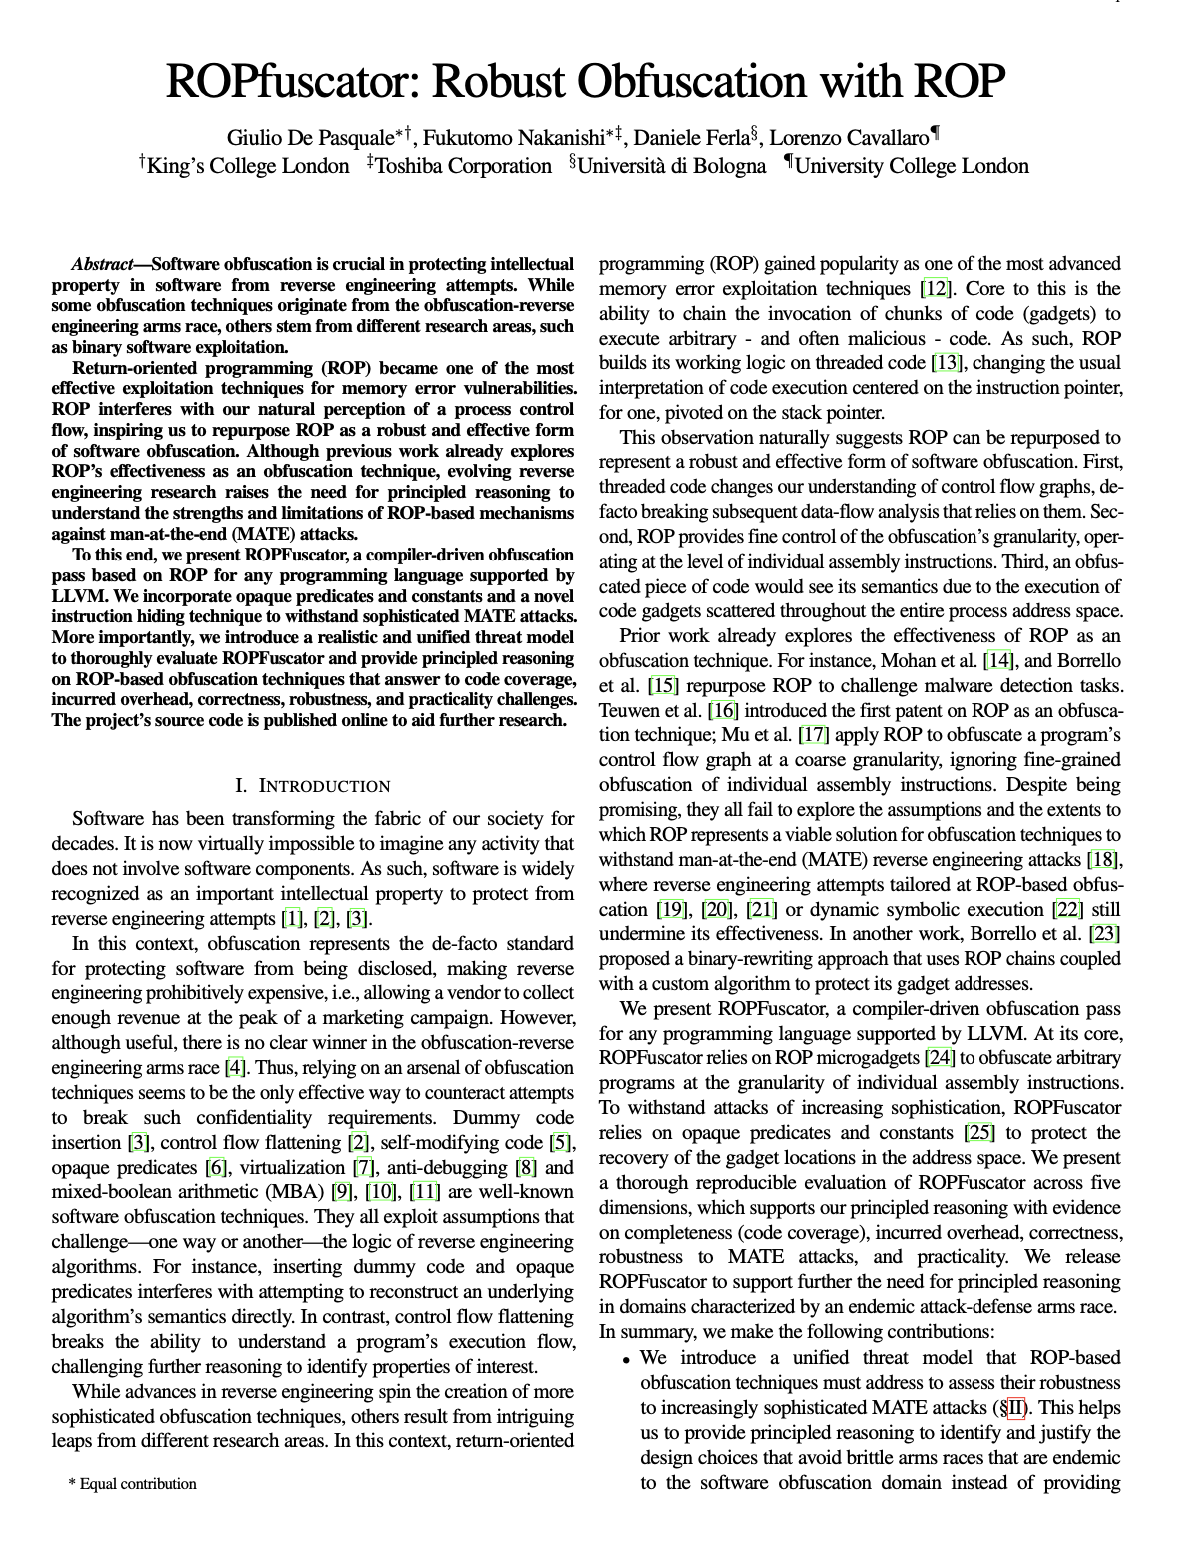 ropfuscator/ropfuscator
ROPfuscator is a fine-grained code obfuscation framework for C/C++ programs using ROP (return-oriented programming).
 felixber/findfunc
IDA Pro plugin for filtering functions by assembly patterns, byte sequences, string/name references, and size constraints, with rule-based search and…
 hdm/juniper-cve-2015-7755
Notes, binaries, and related information from analysis of the CVE-2015-7755 & CVE-2015-7756 issues within Juniper ScreenOS
 jakev/pyxamstore
Python utility for parsing Xamarin AssemblyStore blob files
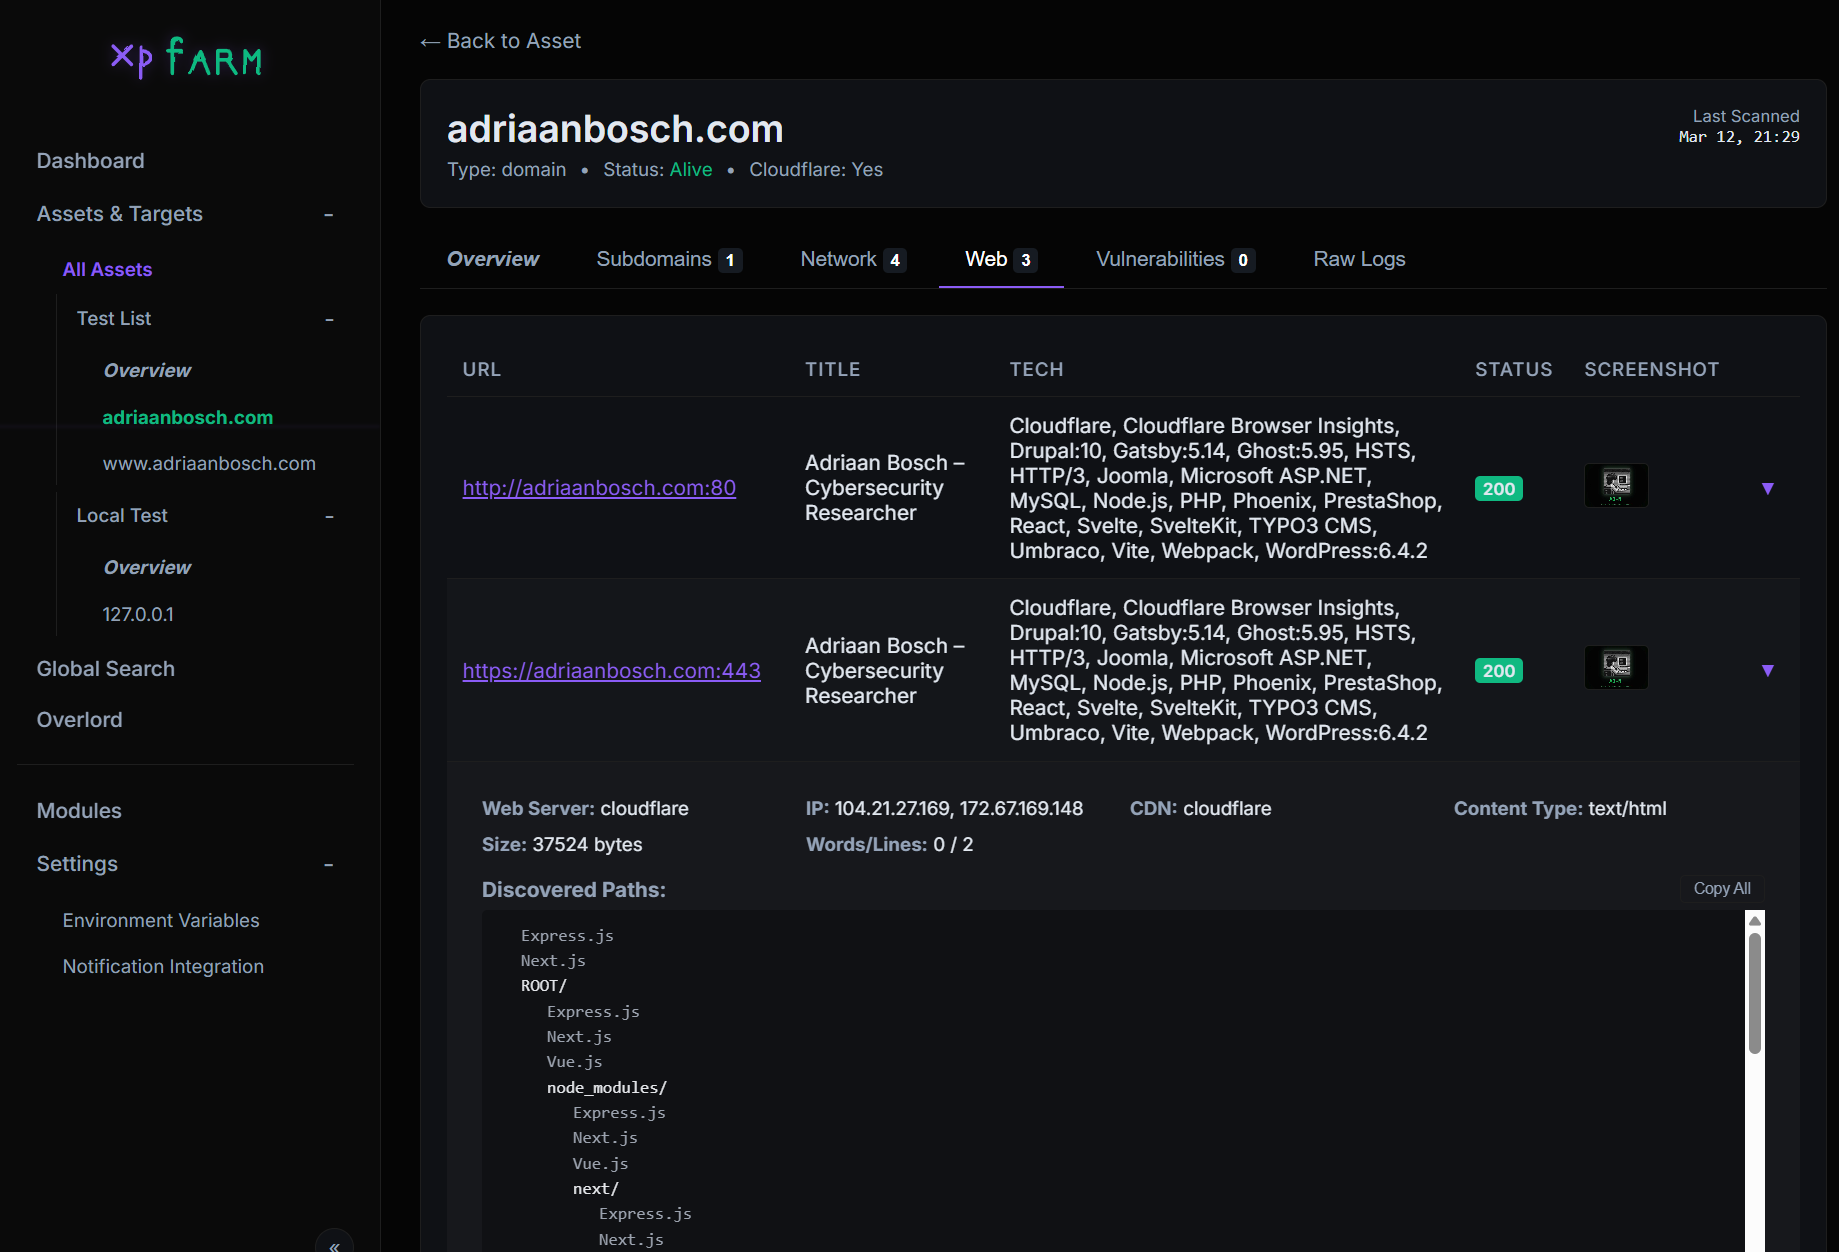 canuk40/xpfarm
Automated bug bounty & recon framework — wraps Subfinder, Naabu, Httpx, Nuclei, Nmap, CVEMap, Gowitness, Katana & more behind a unified web UI
 seemoo-lab/polypyus
Binary-only firmware historian that learns to locate functions in raw binaries by extracting known functions from similar binaries, enabling fast…
 trailofbits/mquire
Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.