
 #1
Binary reverse engineering, disassembly, decompilation, and patching tools.
Kitploit recommended
 kazu-yamamoto/pgpdump
A PGP packet visualizer
 frank2/packer-tutorial
A tutorial on how to write a packer for Windows!
 trailofbits/cobra
Coefficient-Based Reconstruction of Arithmetic — a Mixed Boolean-Arithmetic (MBA) expression simplifier for deobfuscation
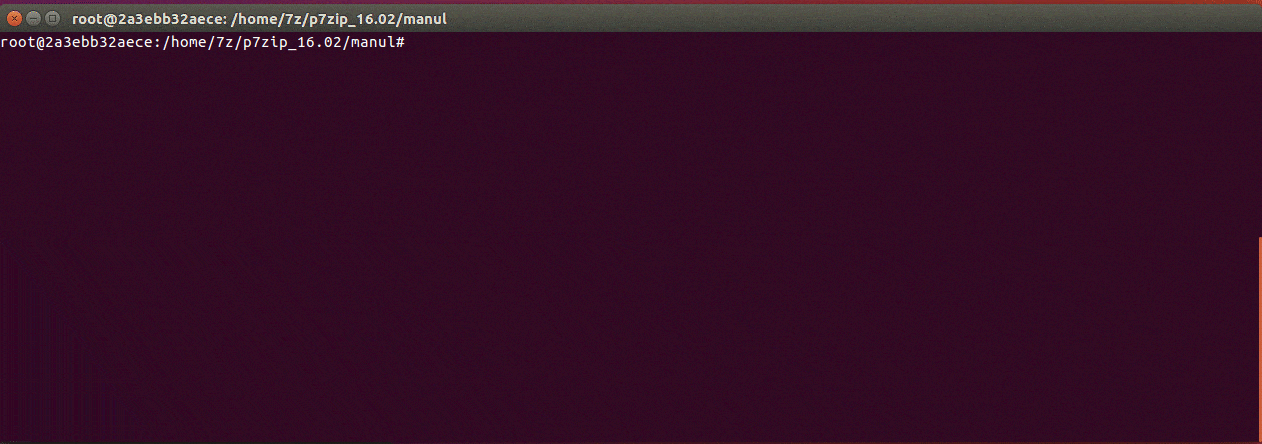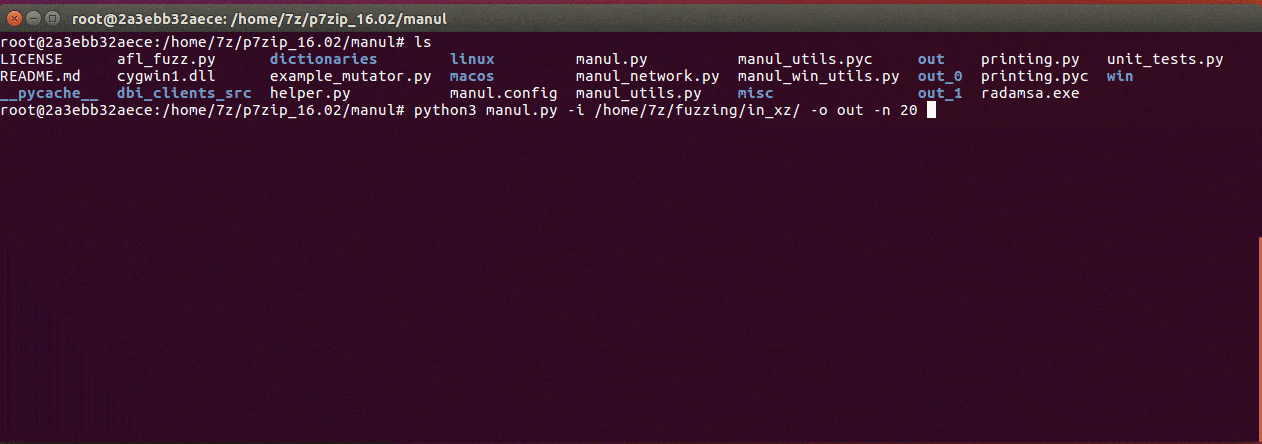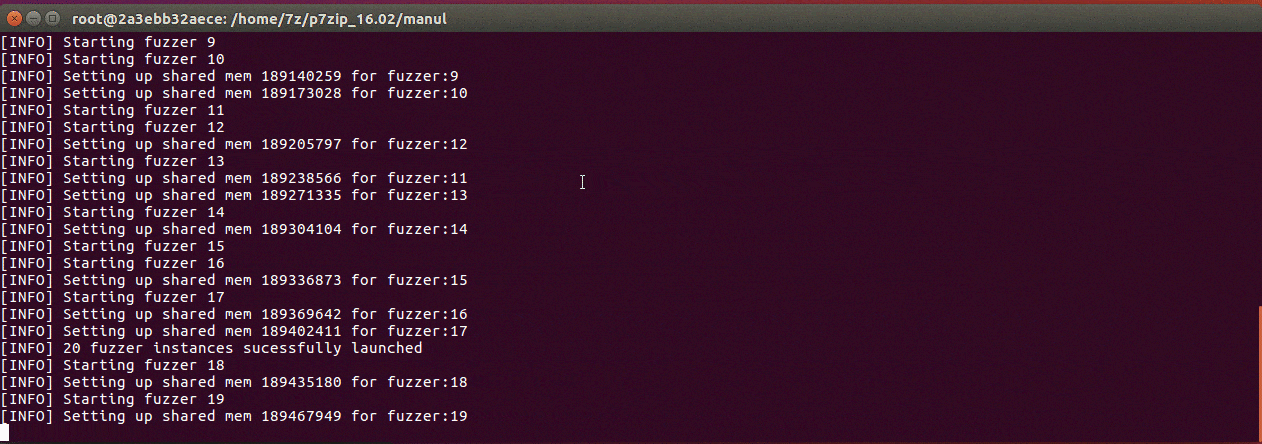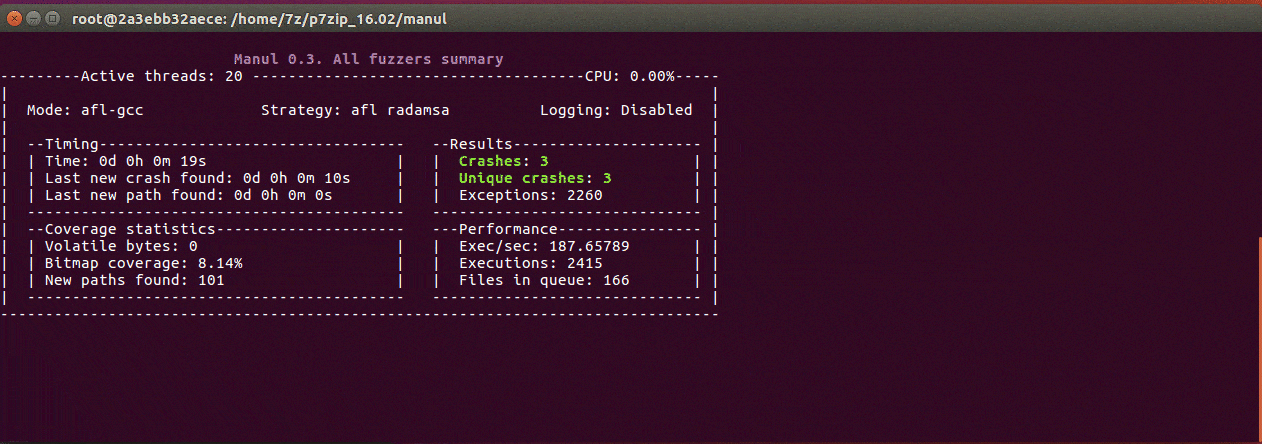 mxmssh/manul
Manul is a coverage-guided parallel fuzzer for open-source and blackbox binaries on Windows, Linux and MacOS
 matheuzsecurity/furtex
Post-exploitation and evasion research toolkit for Linux.
 mr-un1k0d3r/windows-signedbinary
Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
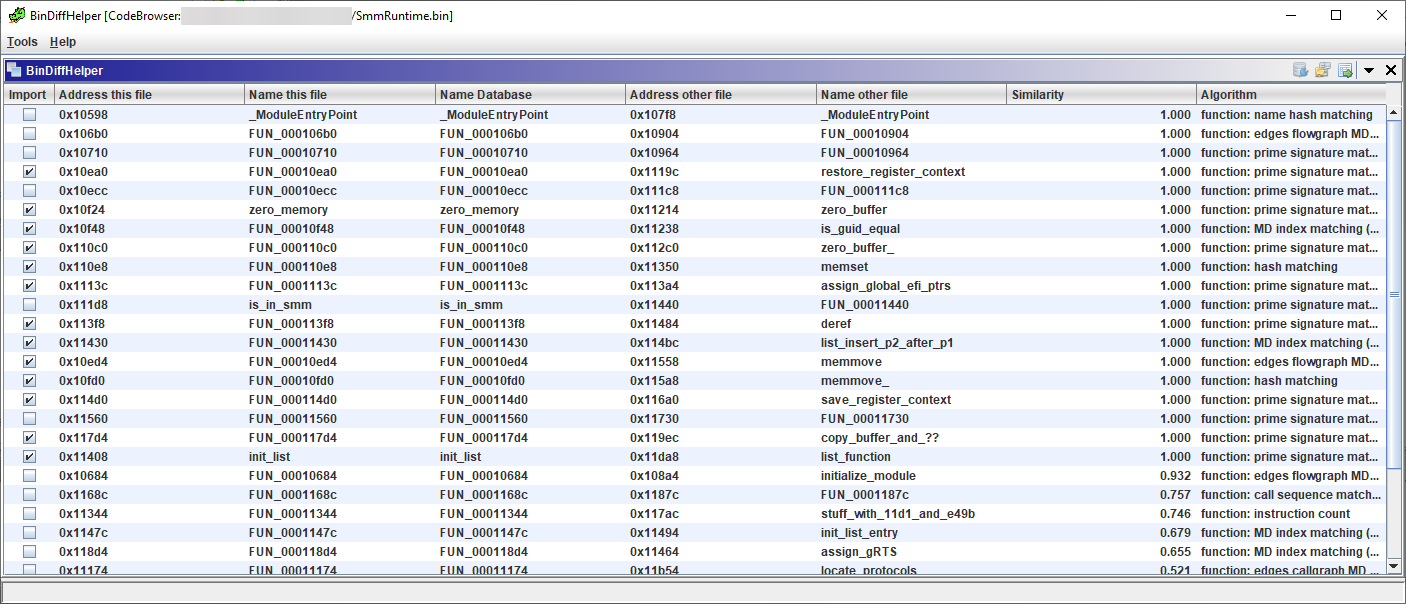 ubfx/bindiffhelper
Ghidra Extension to integrate BinDiff for function matching
 uds-se/formatfuzzer
Template-driven binary format fuzzer that generates and parses valid test inputs at high speed, with AFL++ integration for coverage-guided fuzzing.
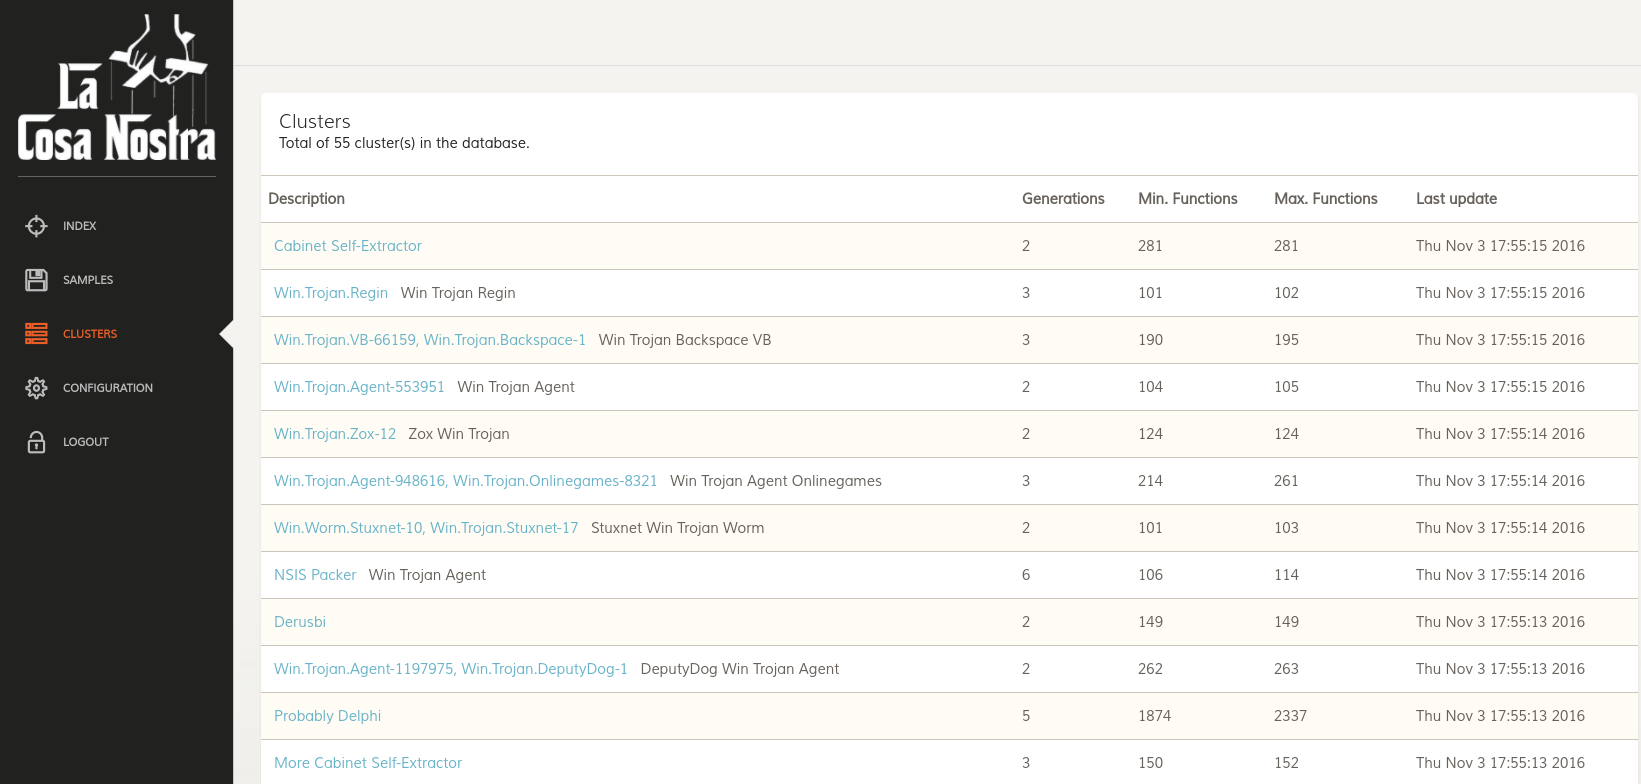 joxeankoret/cosa-nostra
Cosa Nostra, a FOSS graph based malware clusterization toolkit.
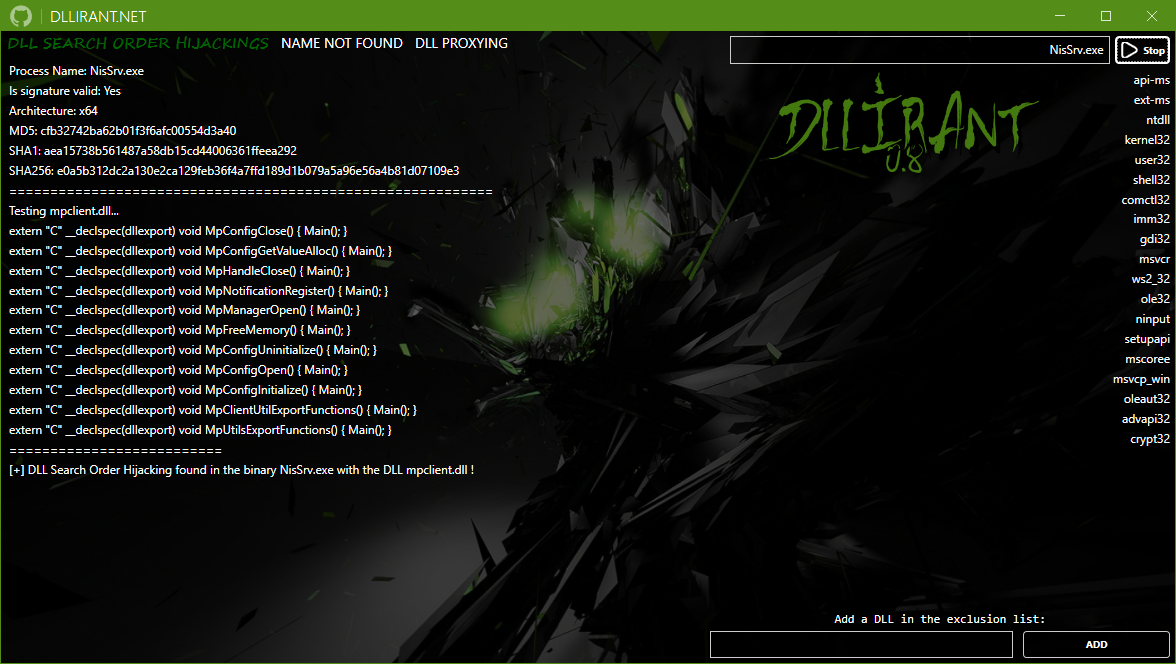 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 airbus-cyber/ghidralligator
Multi-architecture pcode emulator using Ghidra/Sleigh for AFL++ fuzzing of binaries, firmware, and embedded targets; detects memory-corruption bugs…
 nccgroup/asatools
Main repository to pull all NCC Group Cisco ASA-related tool projects.
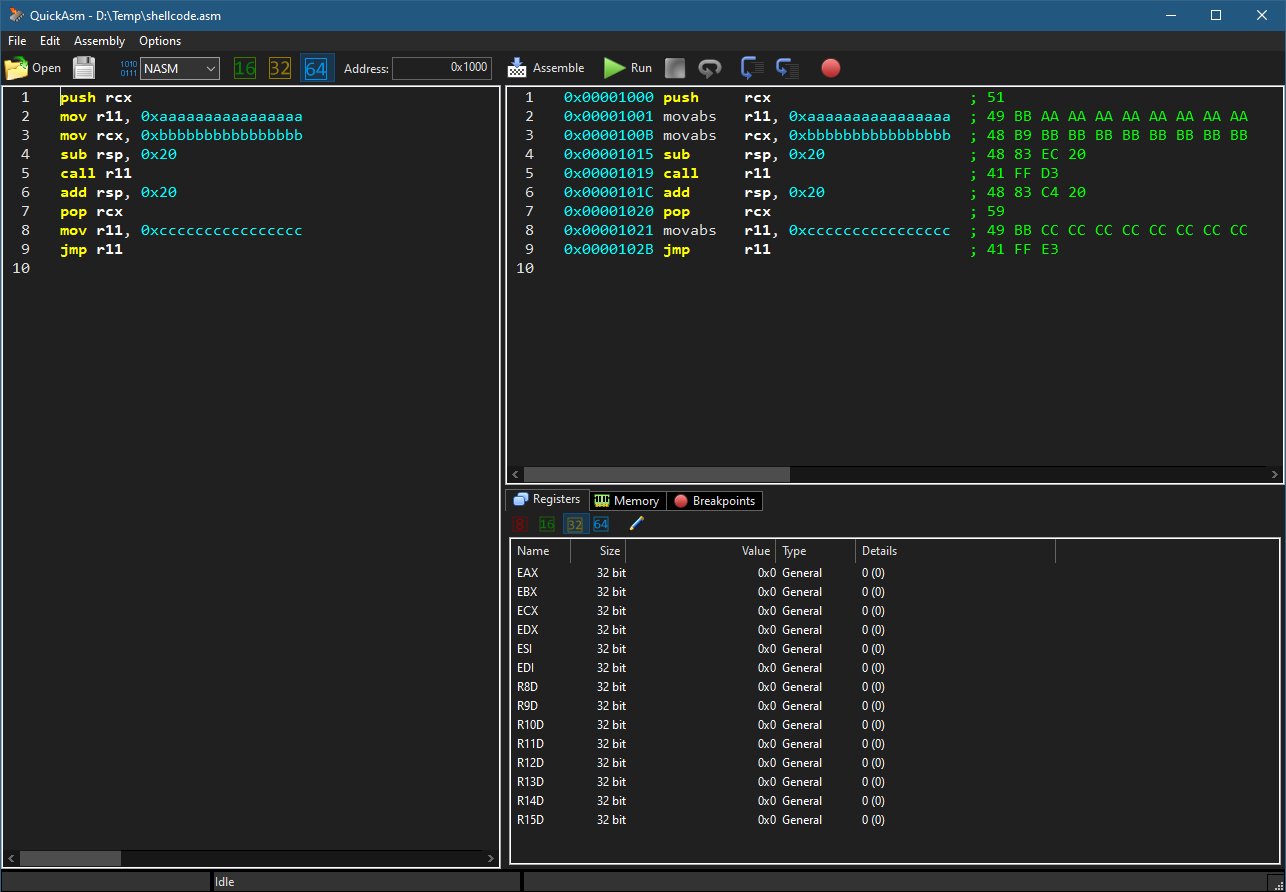 zodiacon/quickasm
Simple x86/x64 Assembler/Disassembler/Emulator
 secrary/infectpe
InfectPE - Inject custom code into PE file [This project is not maintained anymore]
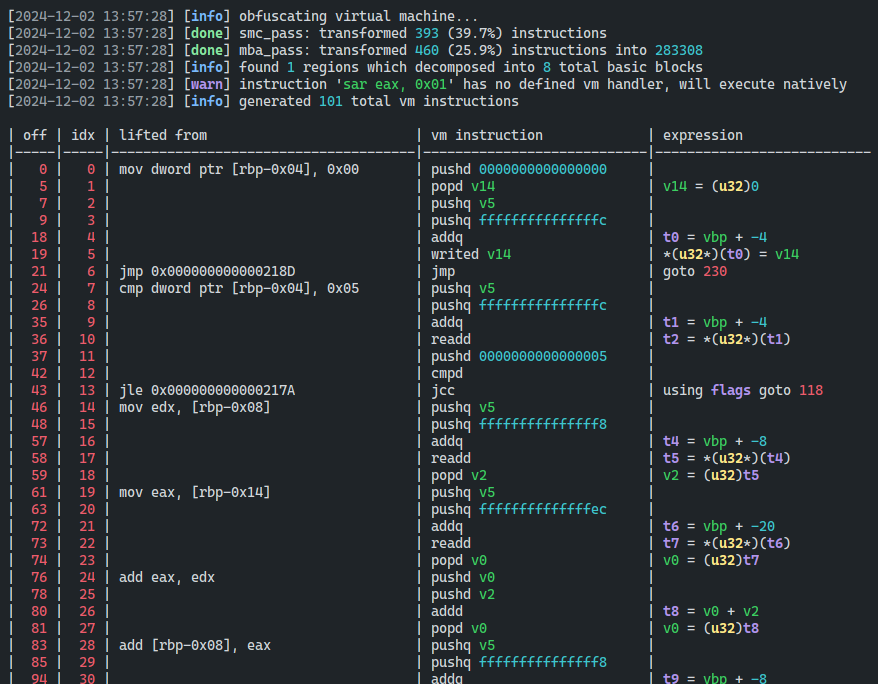 dmaivel/covirt
An x86-64 code virtualizer for VM based obfuscation
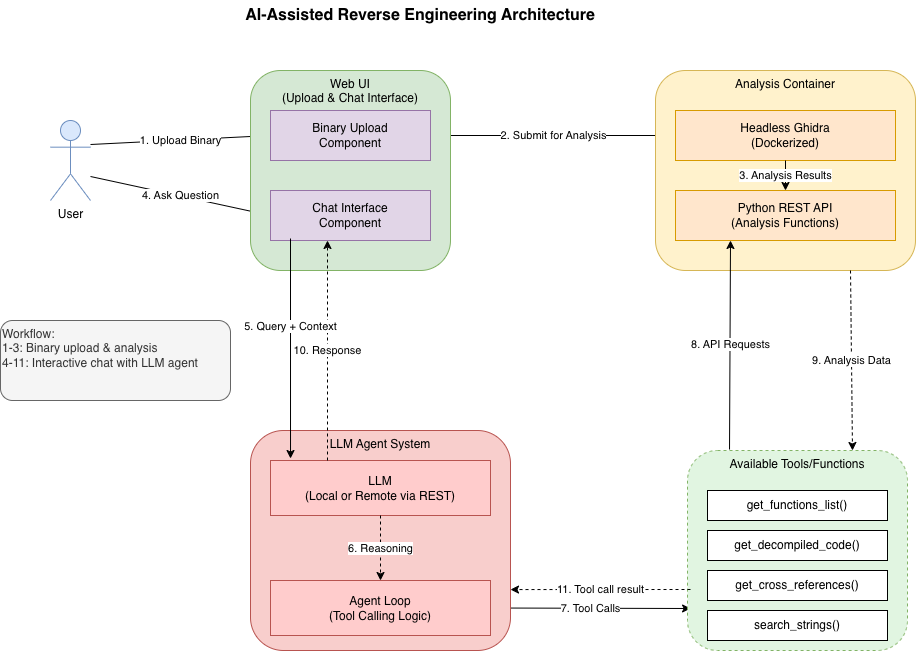 biniamf/ai-reverse-engineering
AI-Assisted Reverse Engineering with Ghidra
 cellebrite-labs/ida_kernelcache
An IDA Toolkit for analyzing iOS kernelcaches.
 kudelskisecurity/cdf
Automated differential fuzzing tool for cryptographic software that detects implementation errors, compliance failures, and side-channel leaks…








