
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Binary Analysis — Page 25 | Kitploit
Categories

Binary Analysis

Binary reverse engineering, disassembly, decompilation, and patching tools.

Kitploit recommended

Top tools

10 selected
ghidra preview#1

ghidra

GitHubnationalsecurityagency/ghidra
71.1k1h 54m ago
radare2 preview#2

radare2

GitHubradareorg/radare2
24.5k11h 12m ago
cutter preview#3

cutter

GitHubrizinorg/cutter
19.4k1 day ago
rizin preview#4

rizin

GitHubrizinorg/rizin
4.1k13 days ago
x64dbg preview#5

x64dbg

GitHubx64dbg/x64dbg
49.1k7 days ago
angr preview#6

angr

GitHubangr/angr
9.0k3h 19m ago
capa preview#7

capa

GitHubmandiant/capa
6.1k1 day ago
Detect-It-Easy preview#8

Detect-It-Easy

GitHubhorsicq/detect-it-easy
11.3k6h 21m ago
LIEF preview#9

LIEF

GitHublief-project/lief
5.5k1 day ago
ImHex preview#10

ImHex

GitHubwerwolv/imhex
54.4k28 days ago
NewestRelevanceMost popularRecently updated
1672 results
cve-2022-27255 preview

cve-2022-27255

GitHubinfobyte/cve-2022-27255

Automated firmware analysis and exploit toolkit for CVE-2022-27255, a Realtek eCos SDK SIP ALG buffer overflow affecting 30+ router models. Includes…
embedded-systems-securityiot-securityvulnerability-analysis+7
2844 years ago
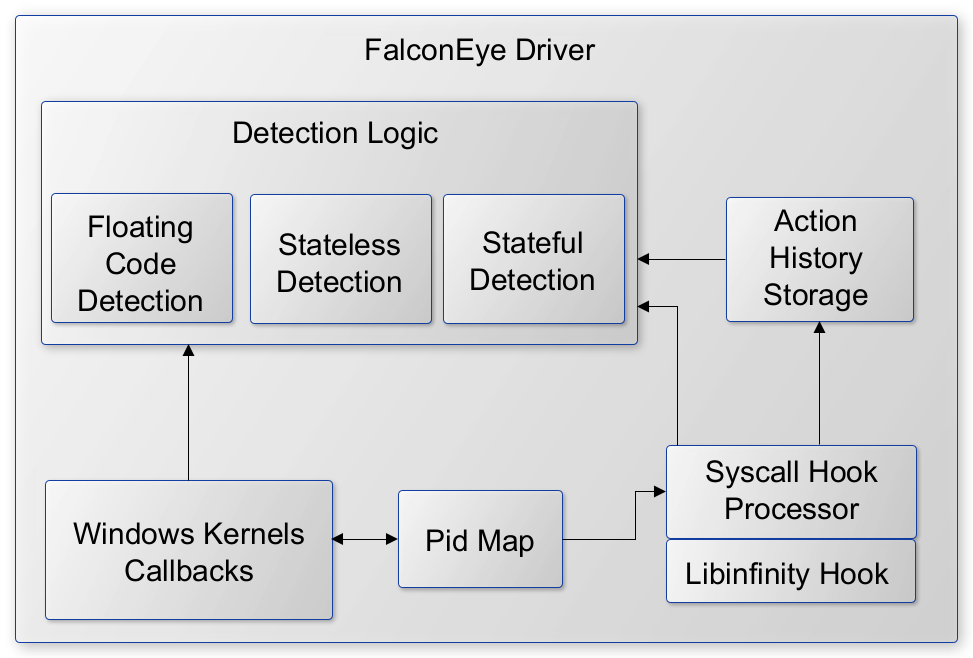
FalconEye preview

FalconEye

GitHubrajiv2790/falconeye

Kernel-mode Windows driver for real-time detection of process injection techniques, including shellcode, DLL, and reflective injection, with syscall…
defensive-toolsmalware-analysisbinary-analysis+1
3105 years ago
CVE-2023-4863 preview

CVE-2023-4863

GitHubmistymntncop/cve-2023-4863

Proof-of-concept for CVE-2023-4863, a heap buffer overflow in WebP image decoding. Demonstrates the code_lengths trigger mechanism discovered by…
vulnerability-analysiscode-analysisexploitation+2
3182 years ago
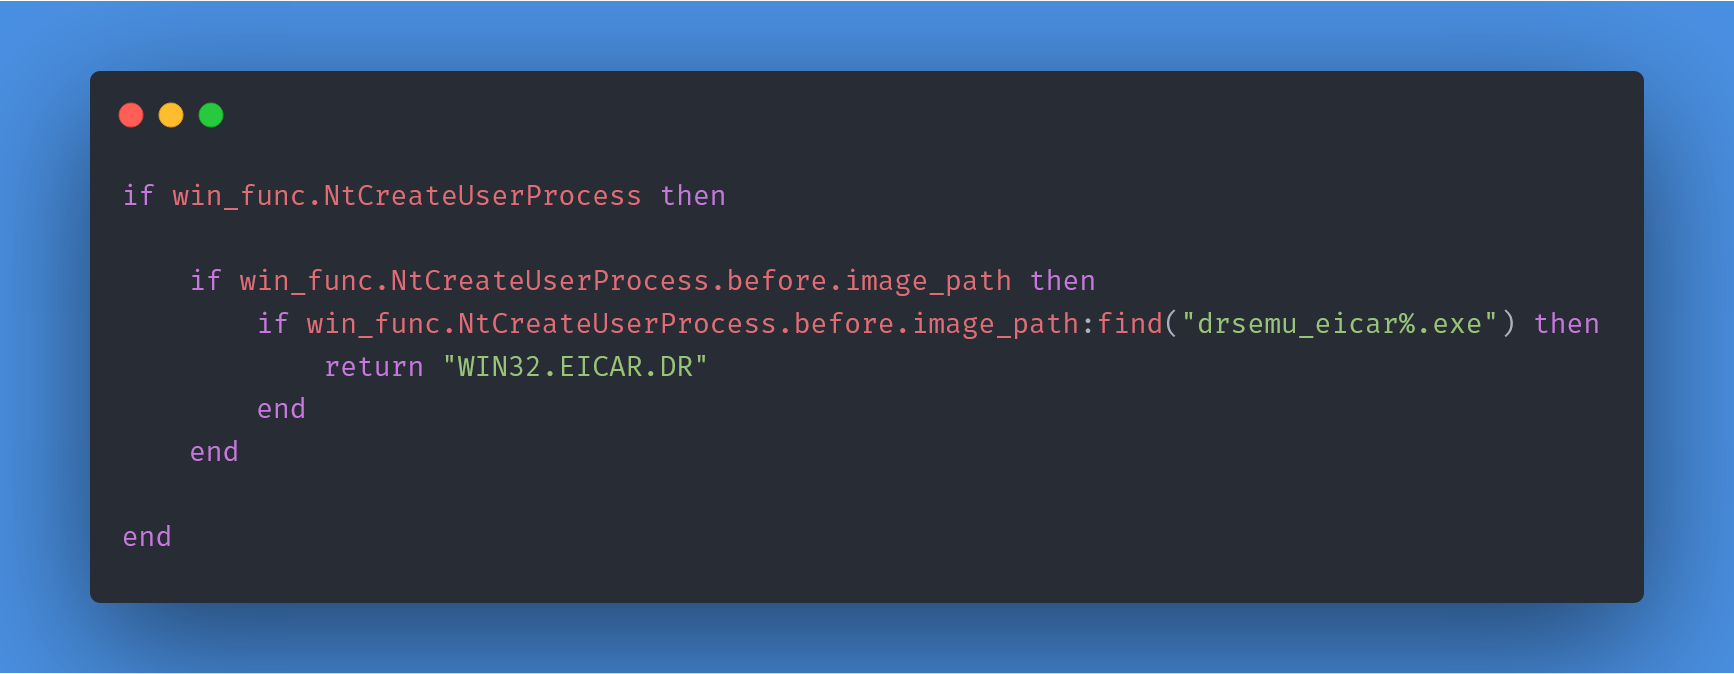
DrSemu preview

DrSemu

GitHubsecrary/drsemu

DrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior

dynamic-analysis-sandboxingreverse-engineeringmalware-analysis+1
2797 years ago
antidbg preview

antidbg

GitHubnotrequiem/antidbg

A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering
defensive-toolsstatic-analysisdynamic-analysis-sandboxing+4
3531 month ago
Reversecore_MCP preview

Reversecore_MCP

GitHubsjkim1127/reversecore_mcp

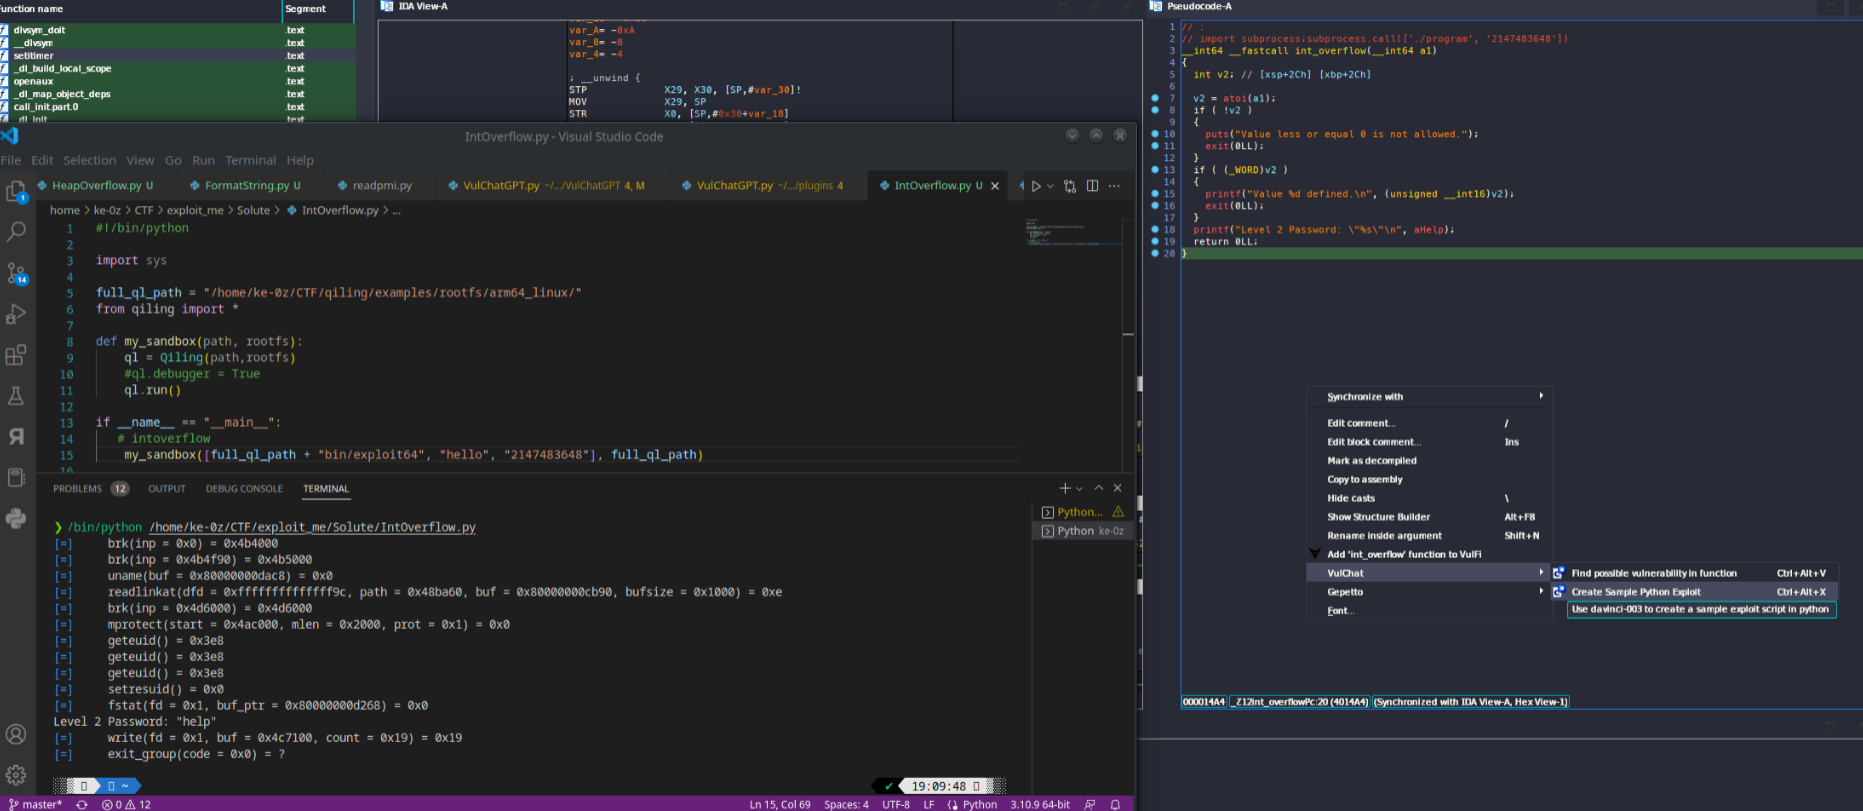
A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…
ioc-managementstatic-analysisdynamic-analysis-sandboxing+7
1852 days ago
BinAIVulHunter preview

BinAIVulHunter

GitHubke0z/binaivulhunter

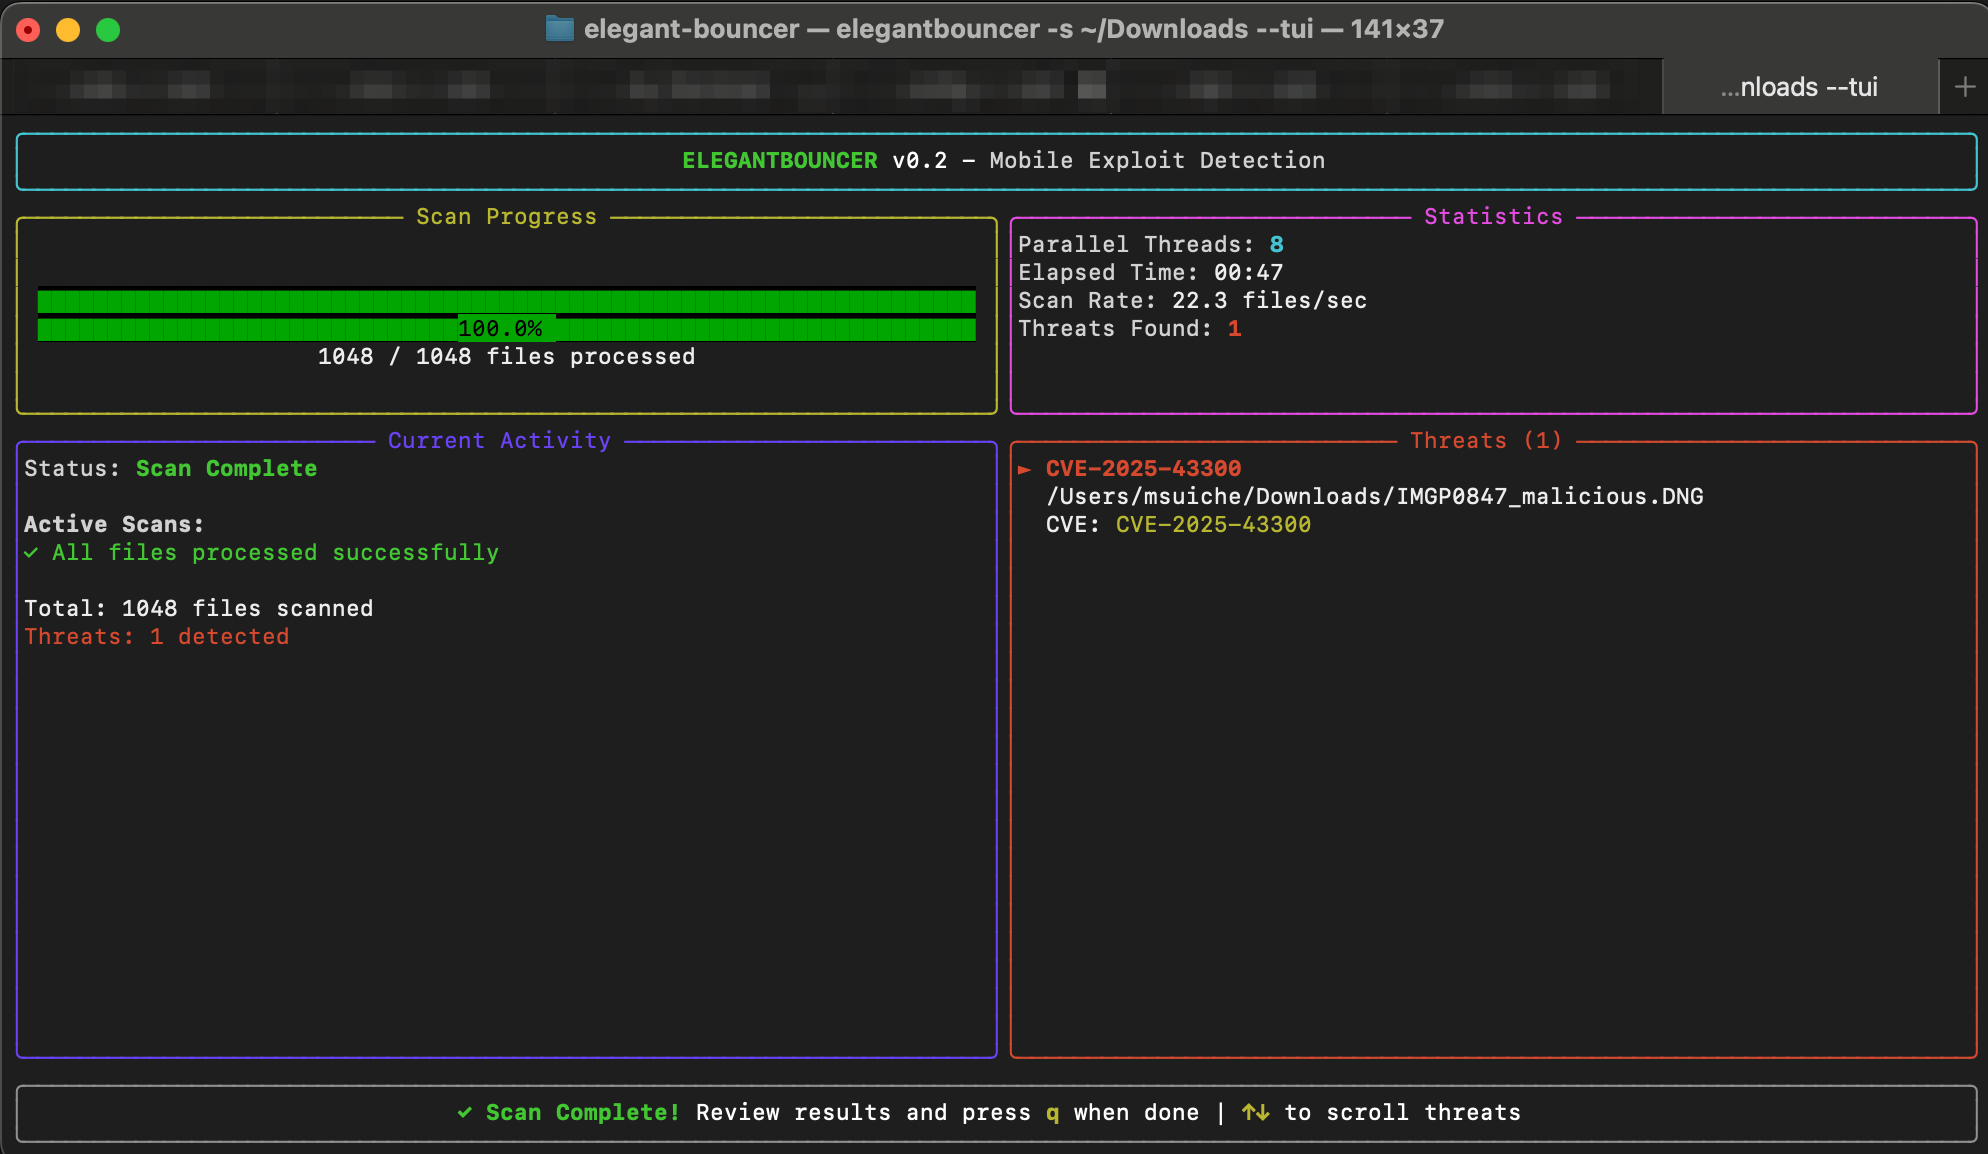
Use IDA PRO HexRays decompiler with OpenAI(ChatGPT) to find possible vulnerabilities in binaries
static-analysisvulnerability-analysiscode-analysis+4
37211 months ago
elegant-bouncer preview

elegant-bouncer

GitHubmsuiche/elegant-bouncer

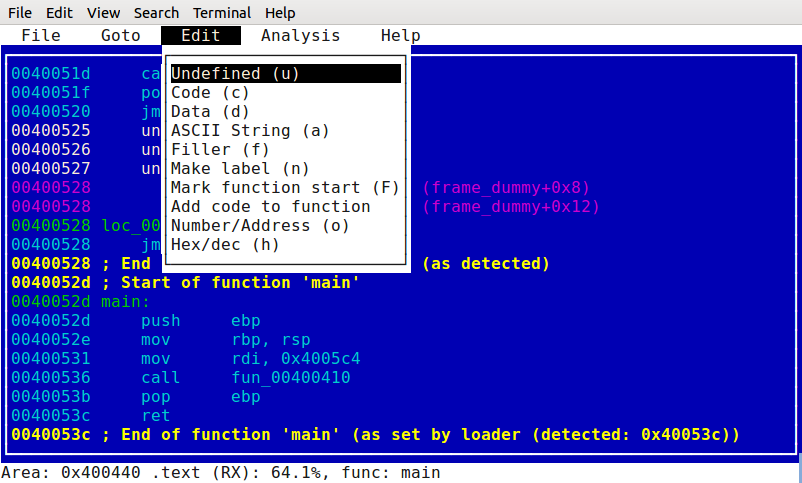
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.
ios-securityvulnerability-analysismobile-forensics+4
1778 days ago
ScratchABit preview

ScratchABit

GitHubpfalcon/scratchabit

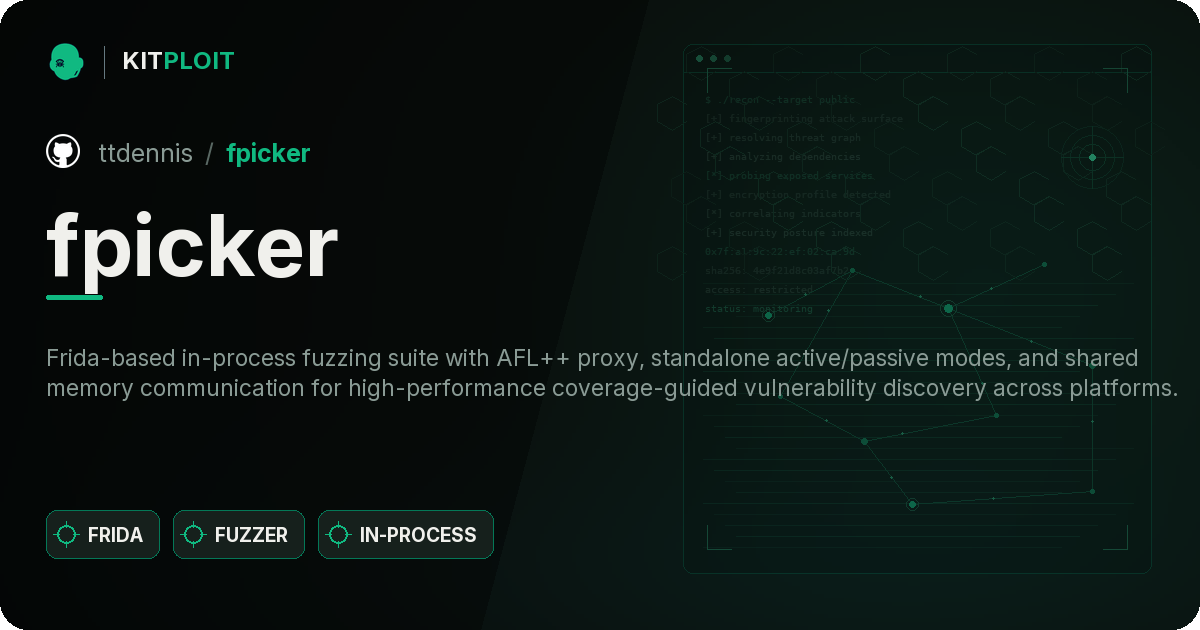
Easily retargetable and hackable interactive disassembler with IDAPython-compatible plugin API
static-analysisreverse-engineeringdebuggers+1
4135 years ago
fpicker preview

fpicker

GitHubttdennis/fpicker

Frida-based in-process fuzzing suite with AFL++ proxy, standalone active/passive modes, and shared memory communication for high-performance…
dynamic-analysis-sandboxingvulnerability-analysisexploitation+2
2961 year ago
MemoryModulePP preview

MemoryModulePP

GitHubstrivexjun/memorymodulepp

C++ library to load DLLs directly from memory without touching disk, with exception handling support, enabling stealthy code execution and evasion of…

exploitationreverse-engineeringmalware-analysis+2
2256 years ago
sleigh preview

sleigh

GitHublifting-bits/sleigh

CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
static-analysiscode-analysisdynamic-code-analysis+4
1943 days ago
quokka preview

quokka

GitHubquarkslab/quokka

Quokka: A Fast and Accurate Binary Exporter
static-analysiscode-analysisreverse-engineering+2
2231 day ago
EhTrace preview

EhTrace

GitHubk2/ehtrace

ATrace is a tool for tracing execution of binaries on Windows.

dynamic-analysis-sandboxingcode-analysisexploitation+4
24311 months ago
cerberus-re-skill preview

cerberus-re-skill

GitHubowenpawl/cerberus-re-skill

cerberus-re is a local Apple-focused reverse-engineering workbench for building a repeatable three-headed static/dynamic/instrumentation loop around…

static-analysisdynamic-analysis-sandboxingios-security+7
1802 months ago
CrimsonEDR preview

CrimsonEDR

GitHubhelixo32/crimsonedr

Simulate the behavior of AV/EDR for malware development training.

defensive-toolsdynamic-analysis-sandboxingmalware-analysis+3
5682 years ago
replica preview

replica

GitHubreb311ion/replica

Ghidra plugin that enhances reverse engineering by fixing missed disassembly, detecting functions, labeling crypto constants, and renaming functions…
static-analysisreverse-engineeringmalware-analysis+2
3156 years ago
ropr preview

ropr

GitHubben-lichtman/ropr

A blazing fast™ multithreaded ROP Gadget finder. ropper / ropgadget alternative (currently x86 only)


exploitationreverse-engineeringshellcode+1
5556 months ago
Previous1…242526…93Next







