
 #1
Binary reverse engineering, disassembly, decompilation, and patching tools.
Kitploit recommended
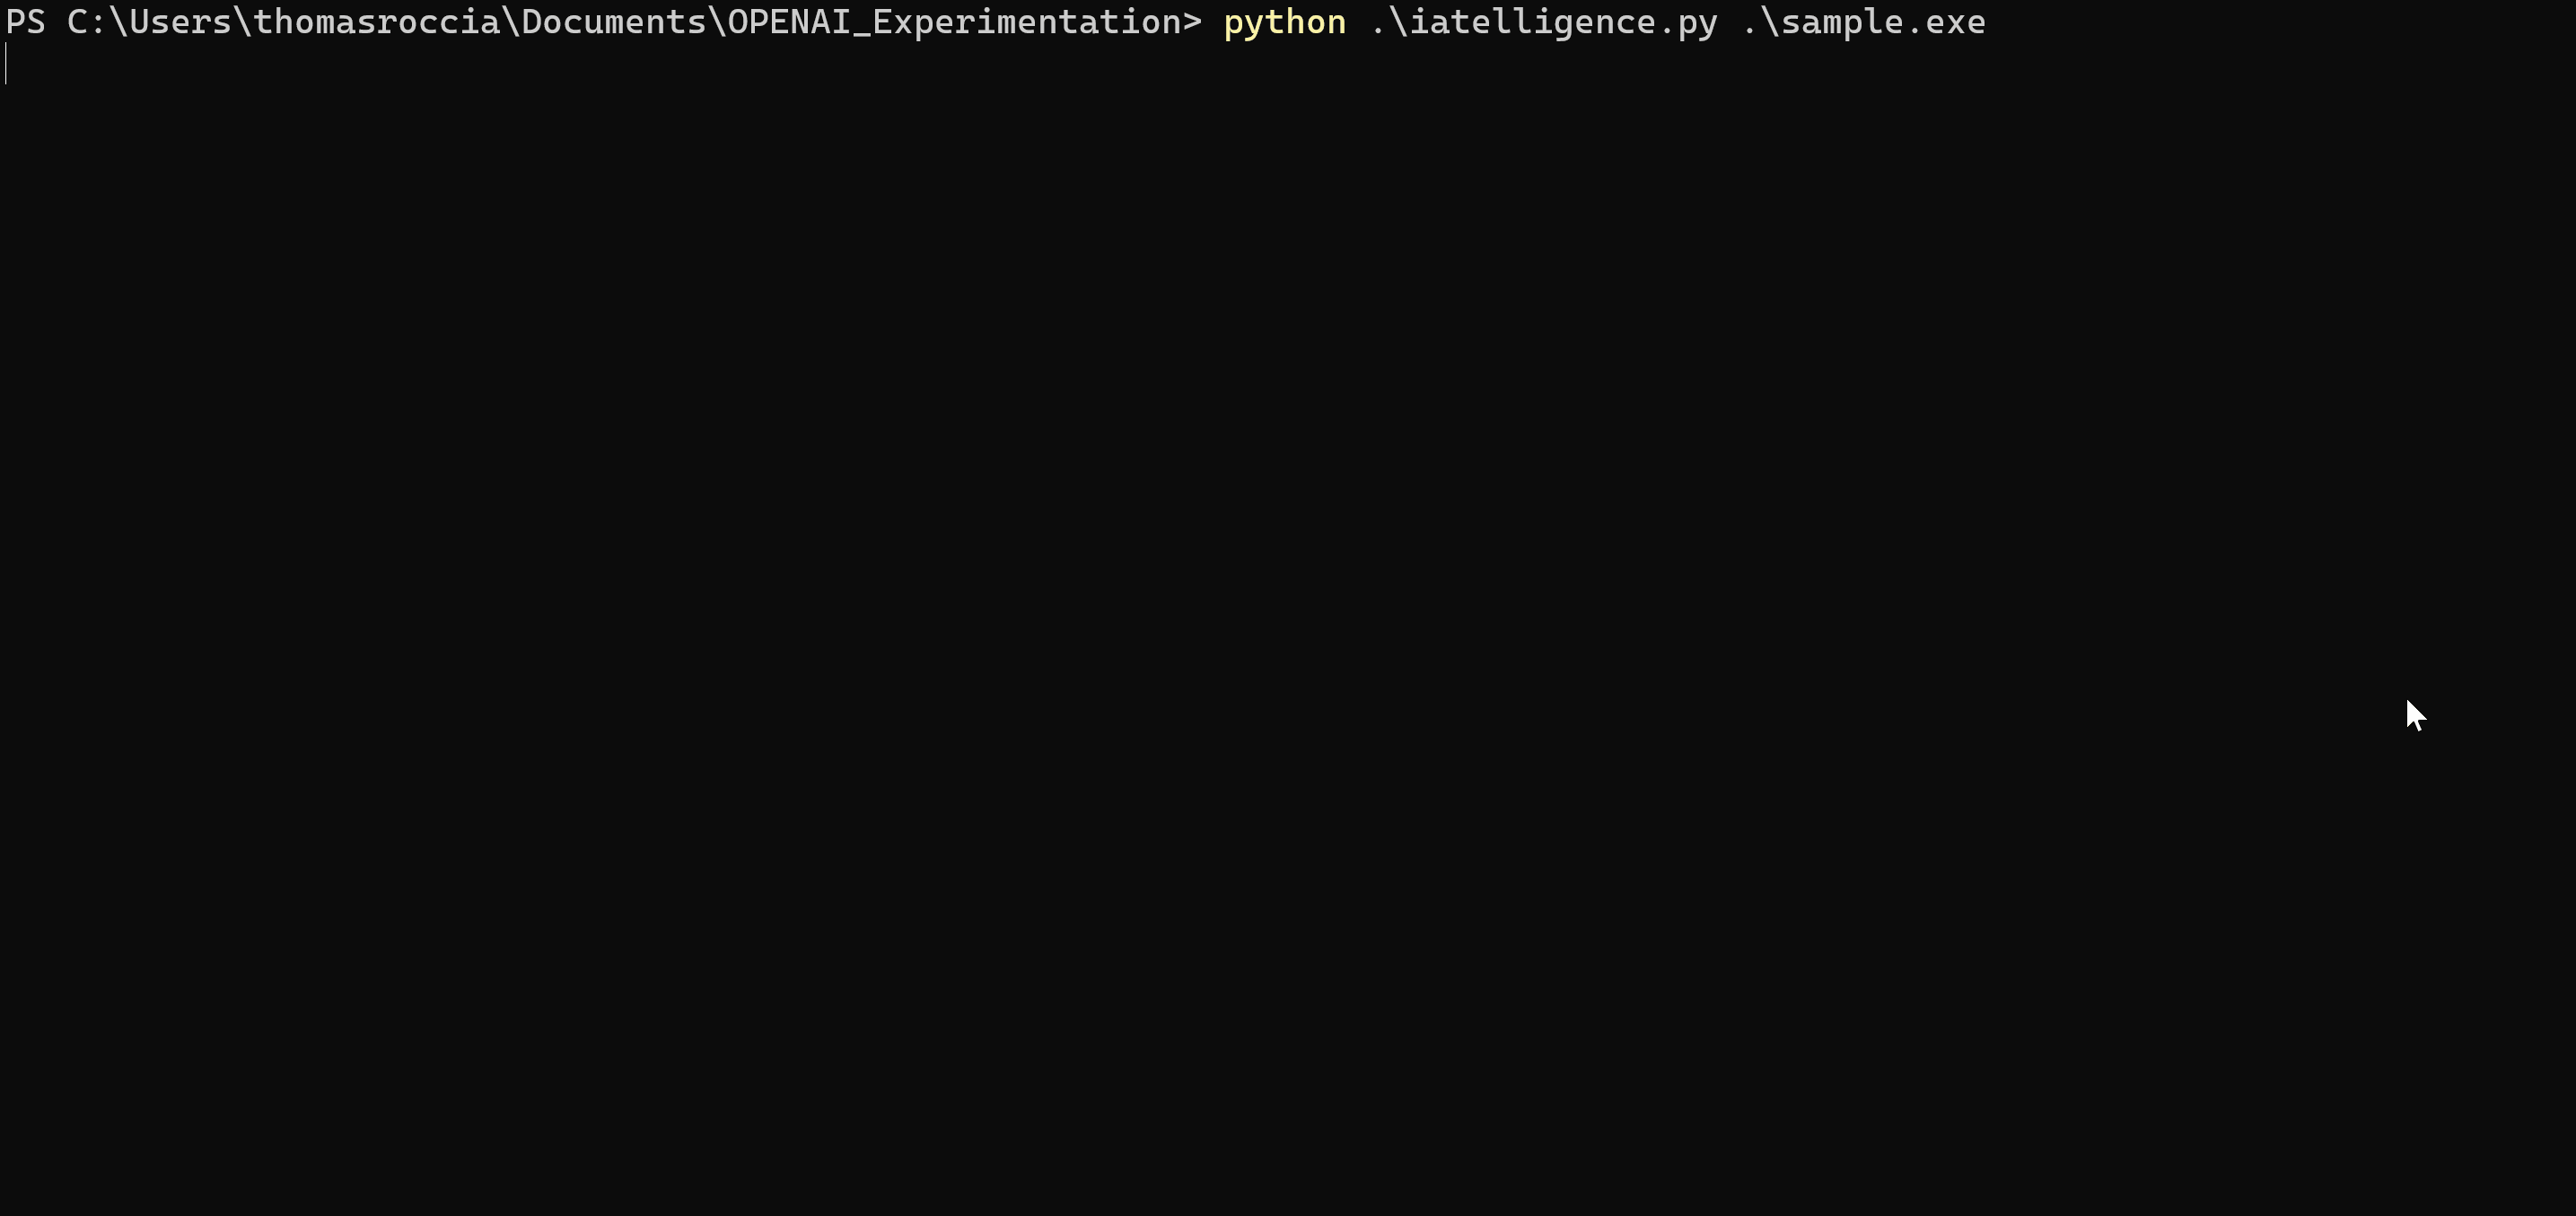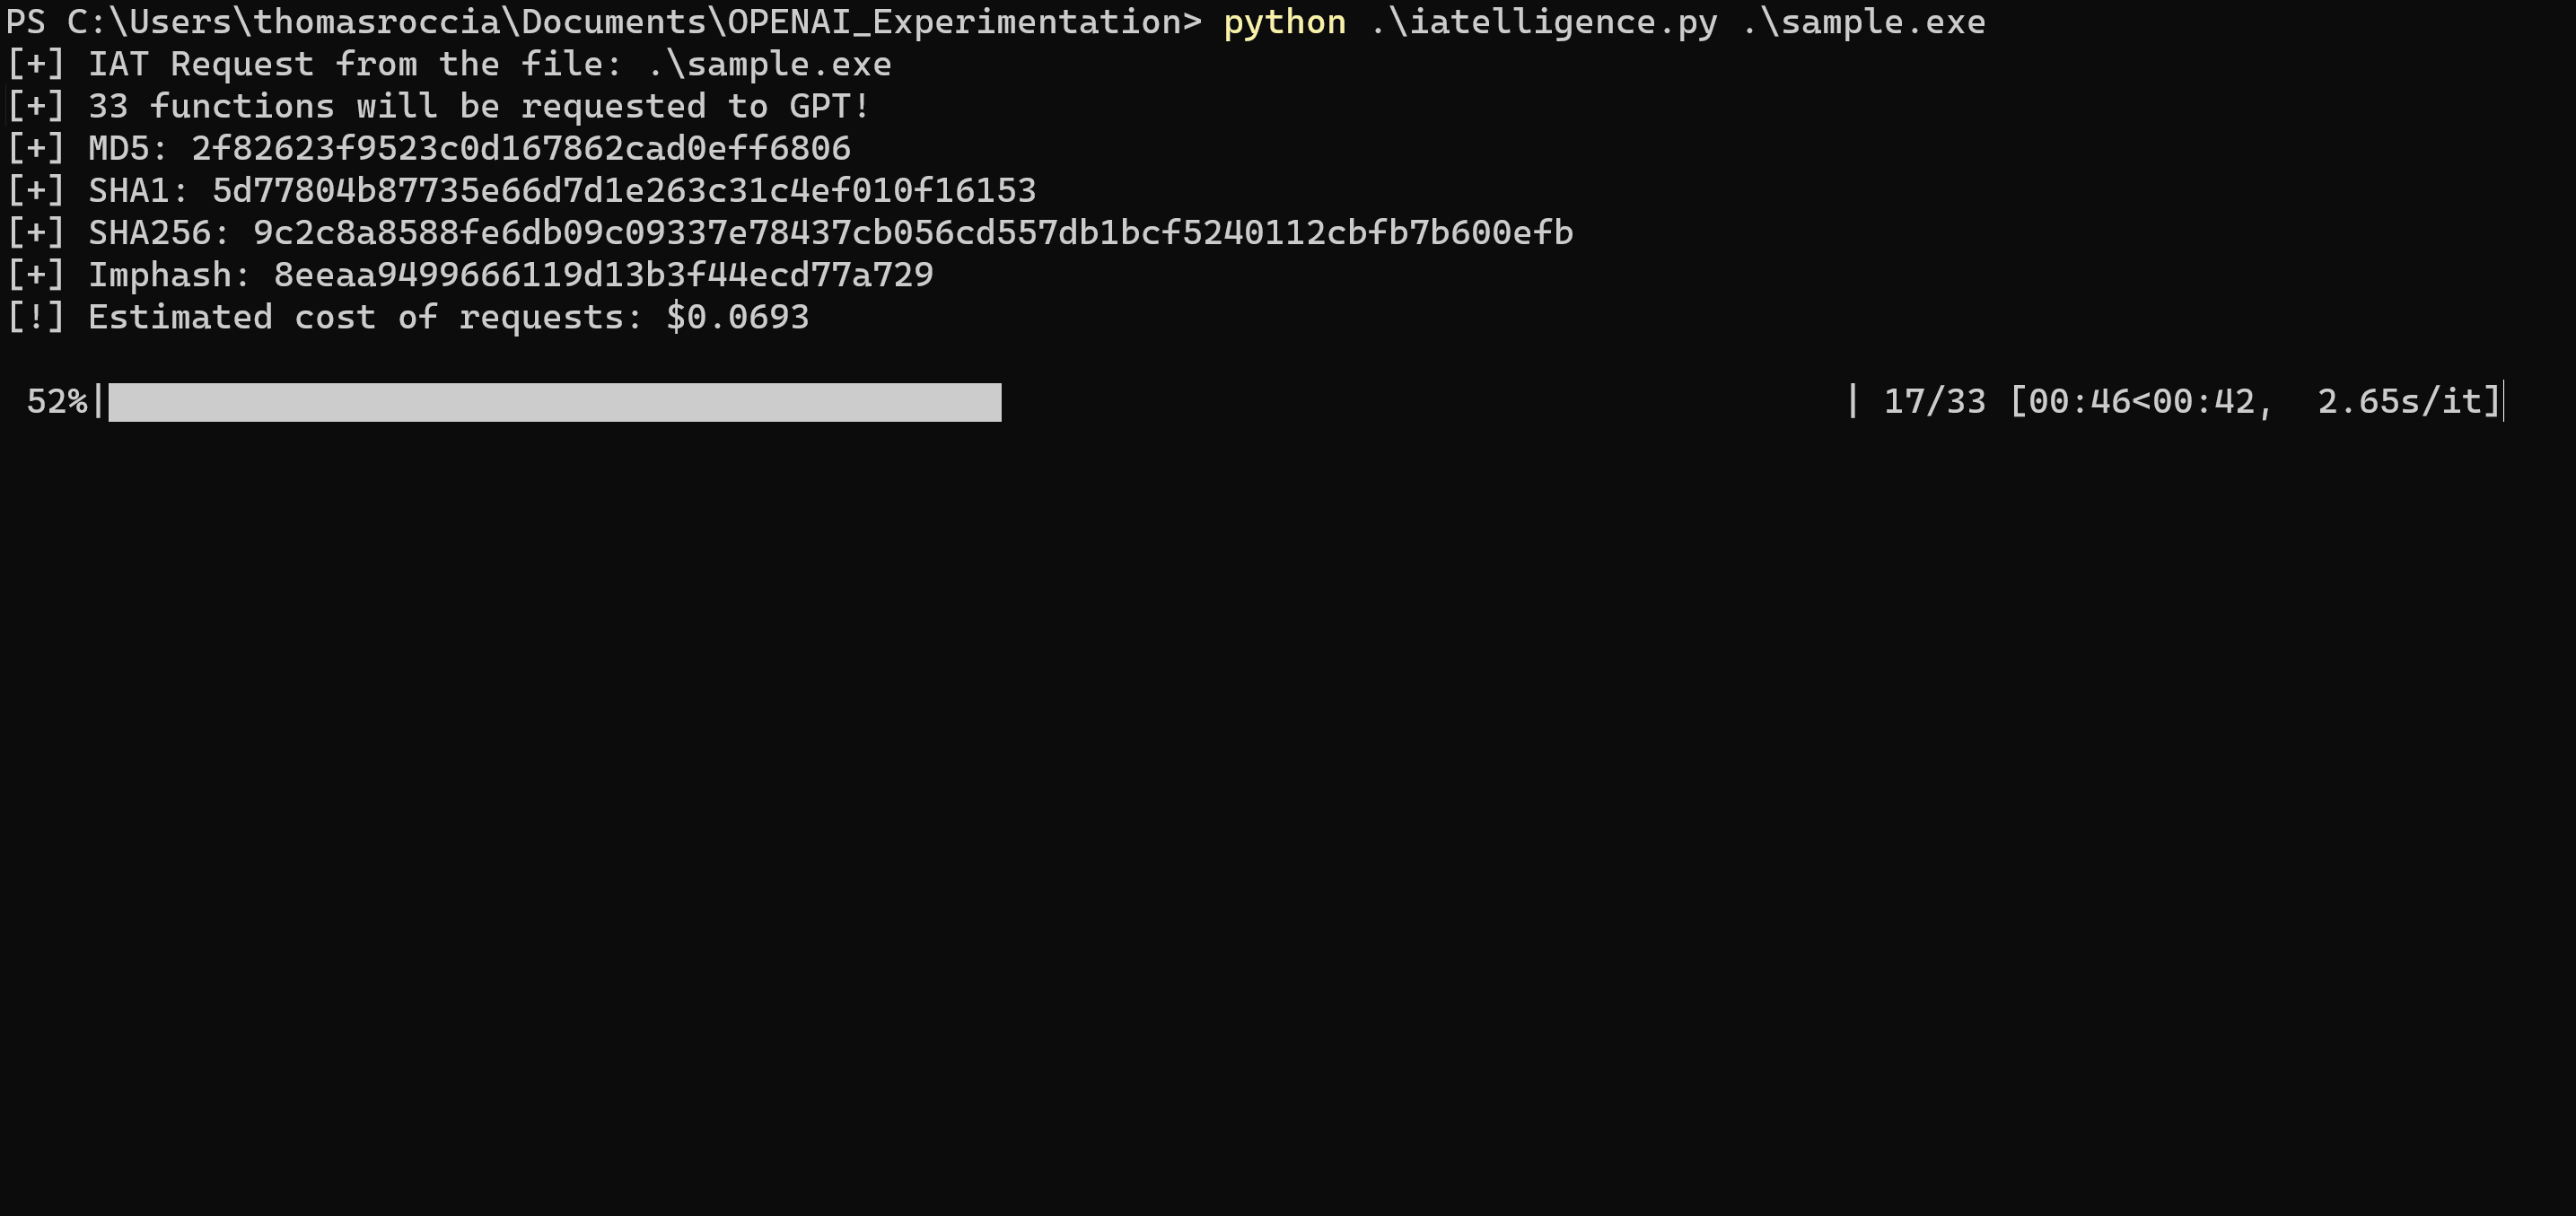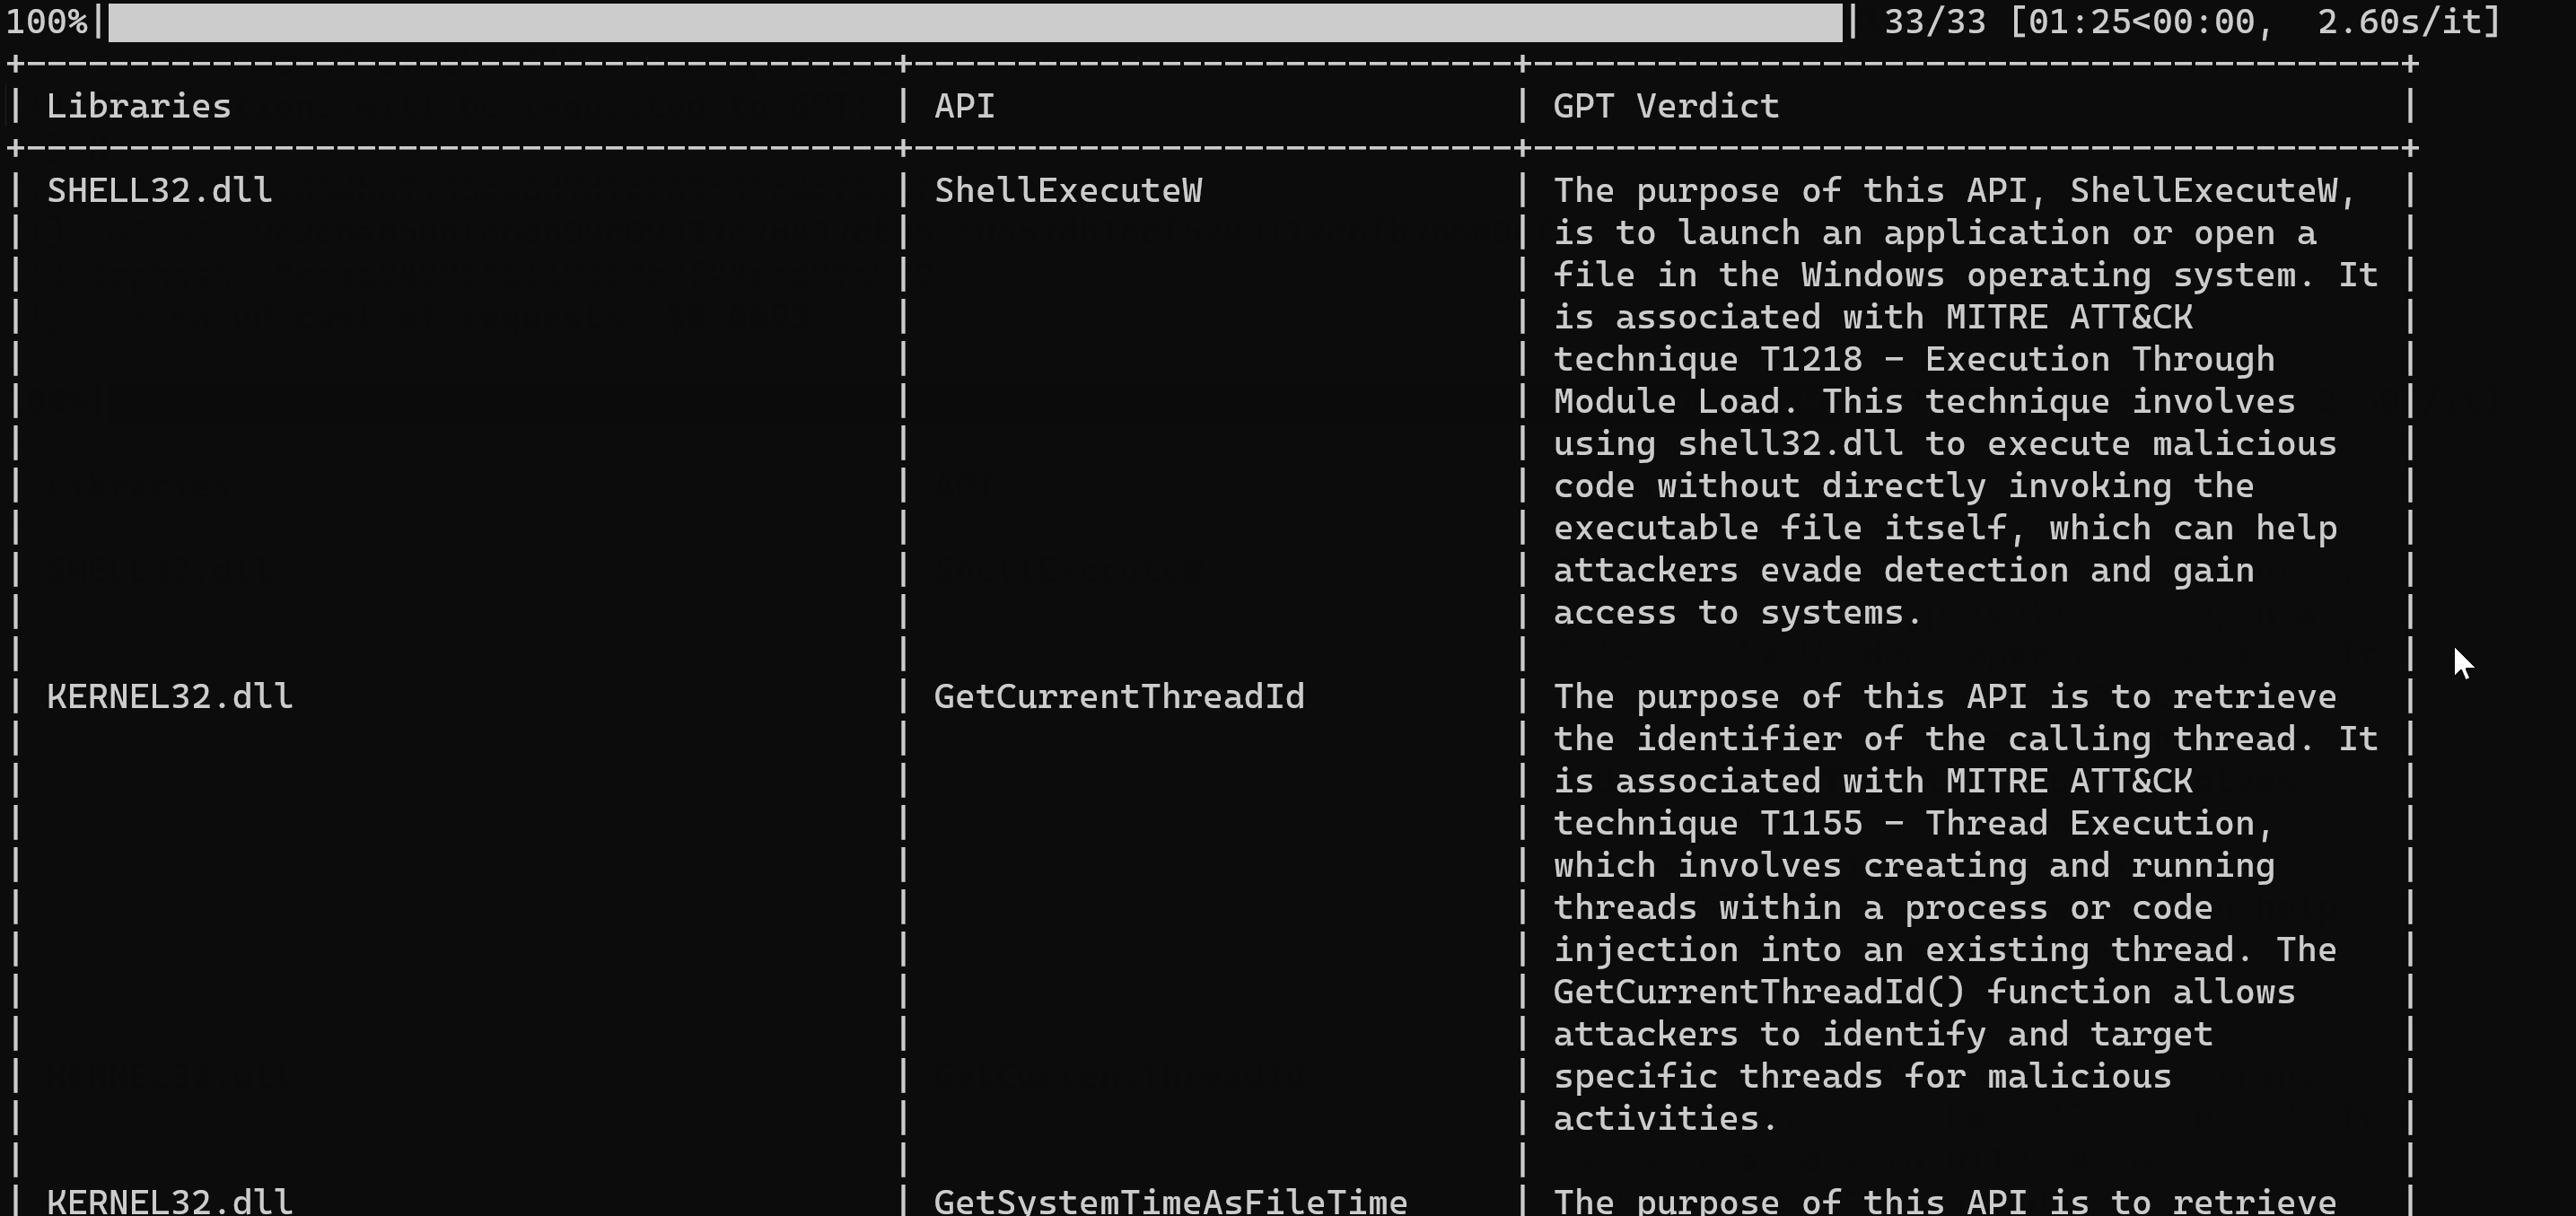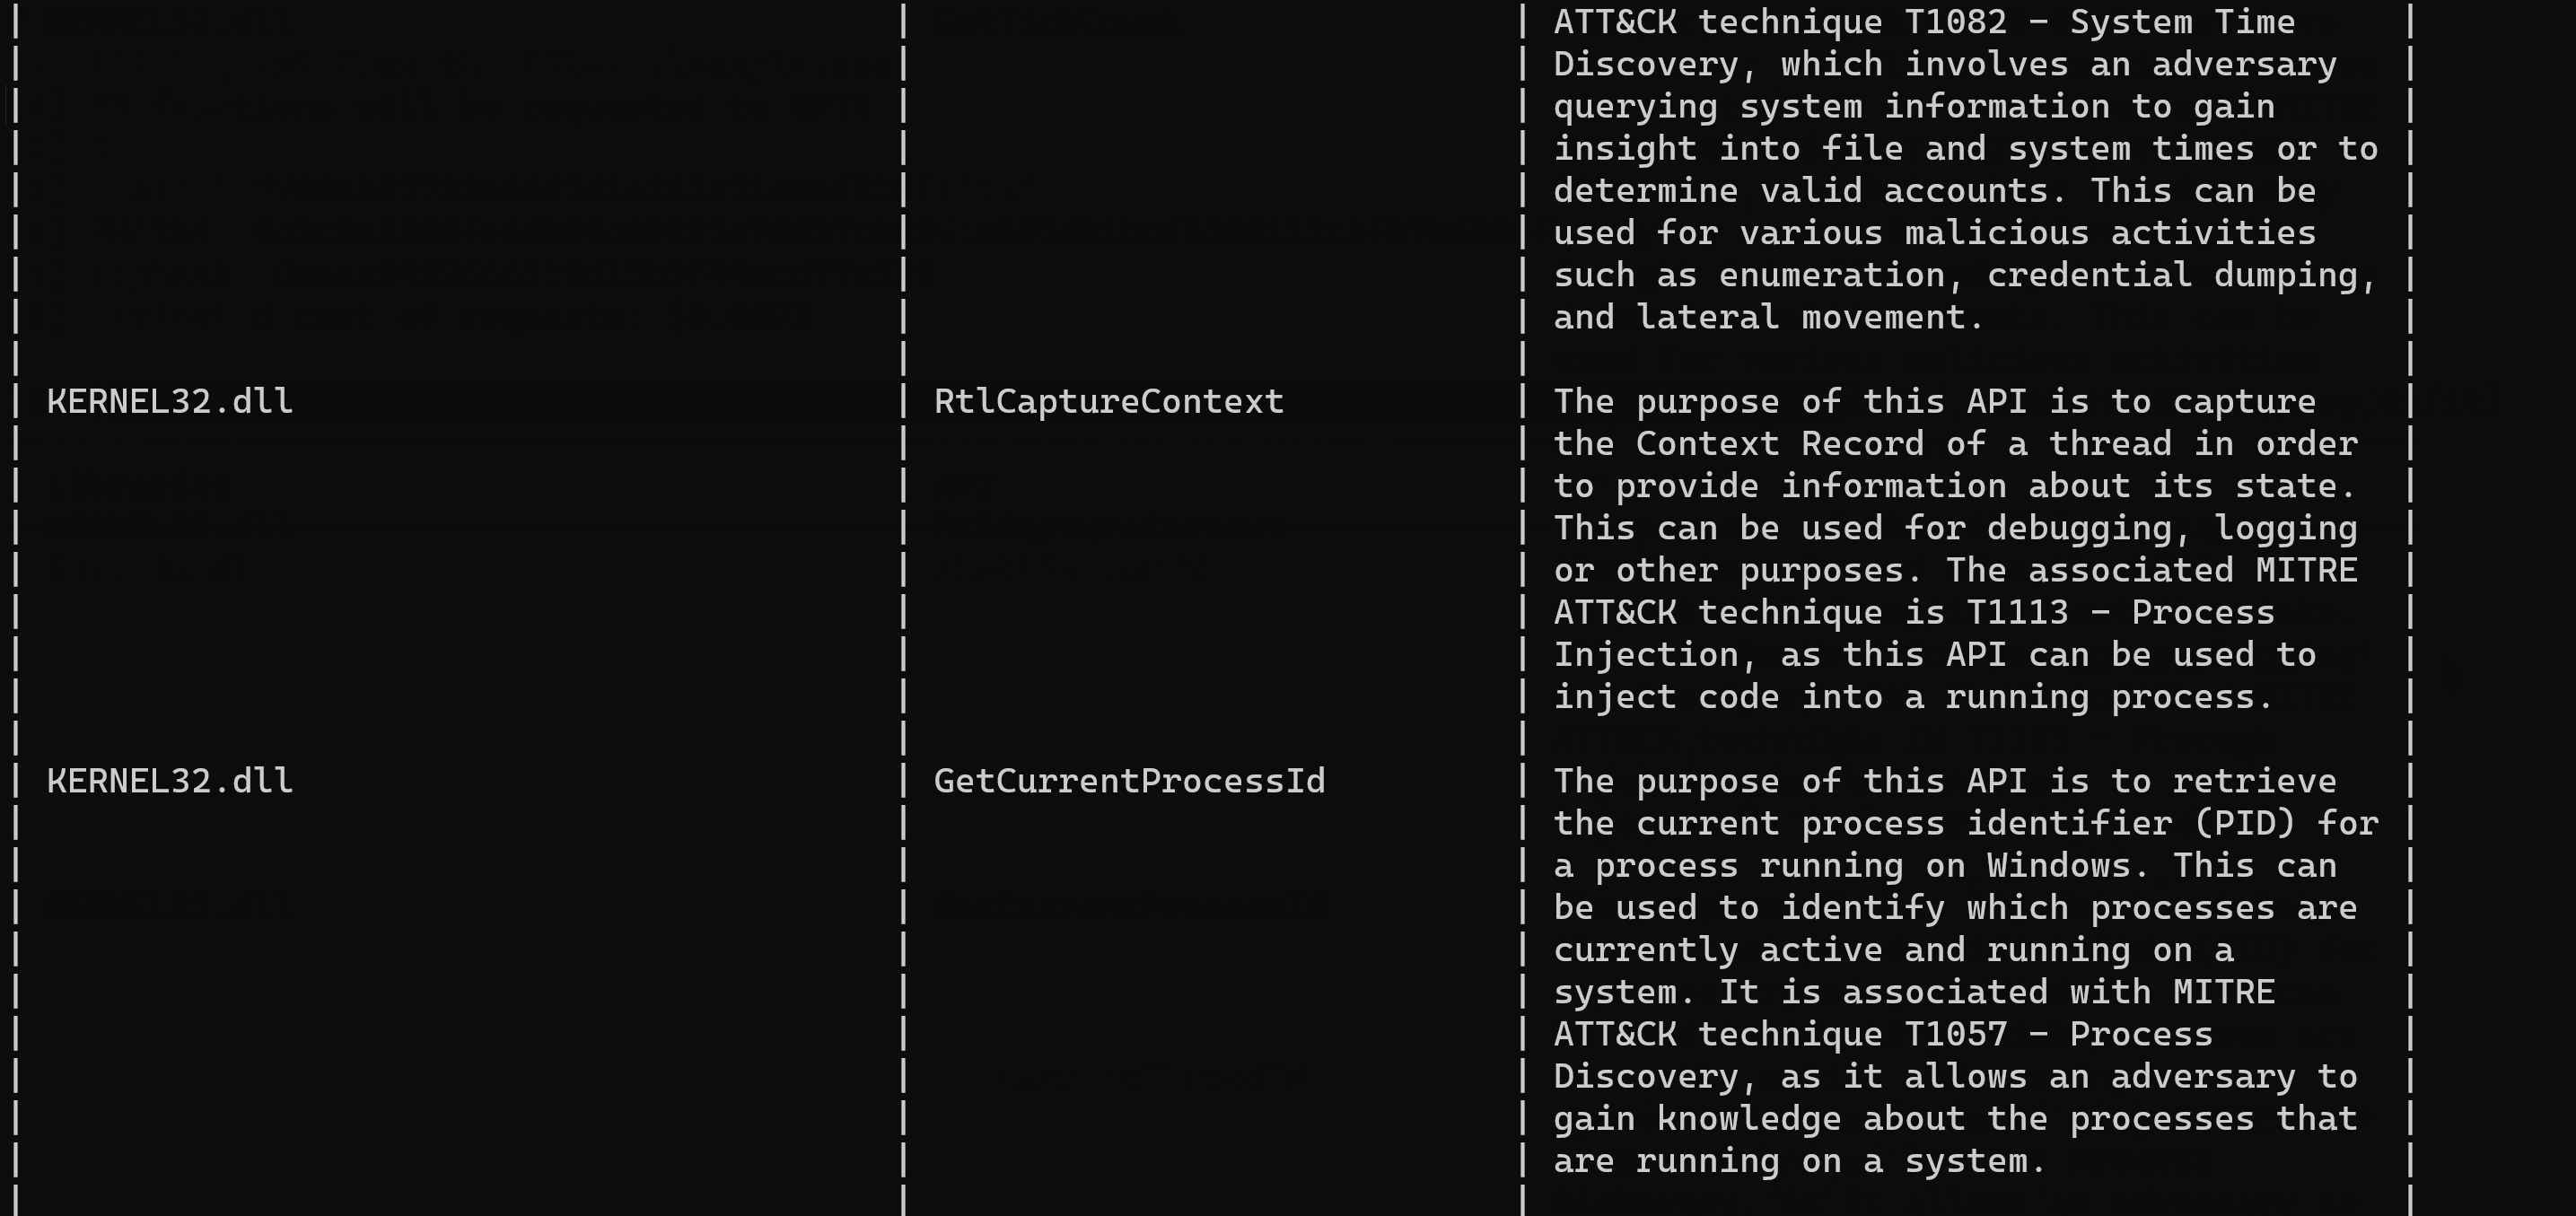
 fr0gger/iatelligence
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…
 nccgroup/susanrtti
Another RTTI Parsing IDA plugin
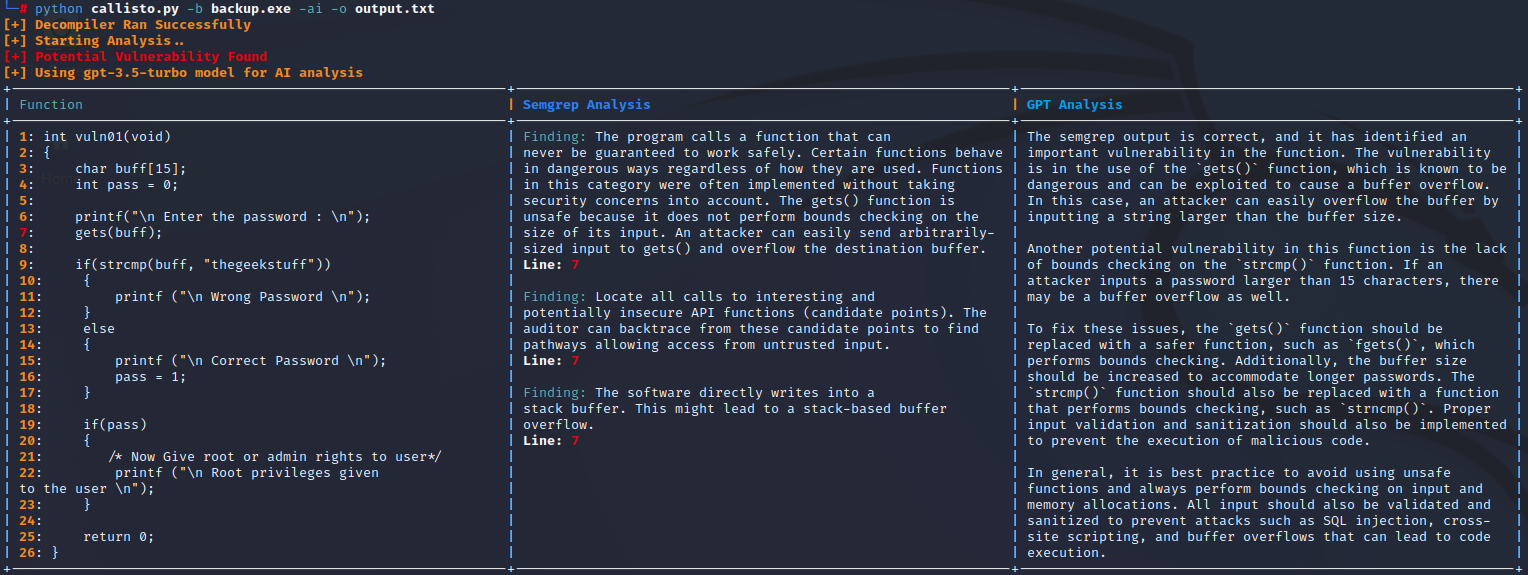 jetp1ane/callisto
Automated binary vulnerability analysis tool that decompiles executables via Ghidra, scans pseudo-C code with Semgrep, and validates findings using…
 mfthomps/resim
Reverse engineering software using a full system simulator
 fox-it/dissect.cobaltstrike
Python library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
 baptisterajaut/radmin-vpn-linux
Run Radmin VPN on Linux via Wine — custom driver, TAP bridge, zero packet loss
 antonin-deniau/cave_miner
Search for code cave in all binaries
 lepotekil/msfmania
Python AV Evasion Tools
 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
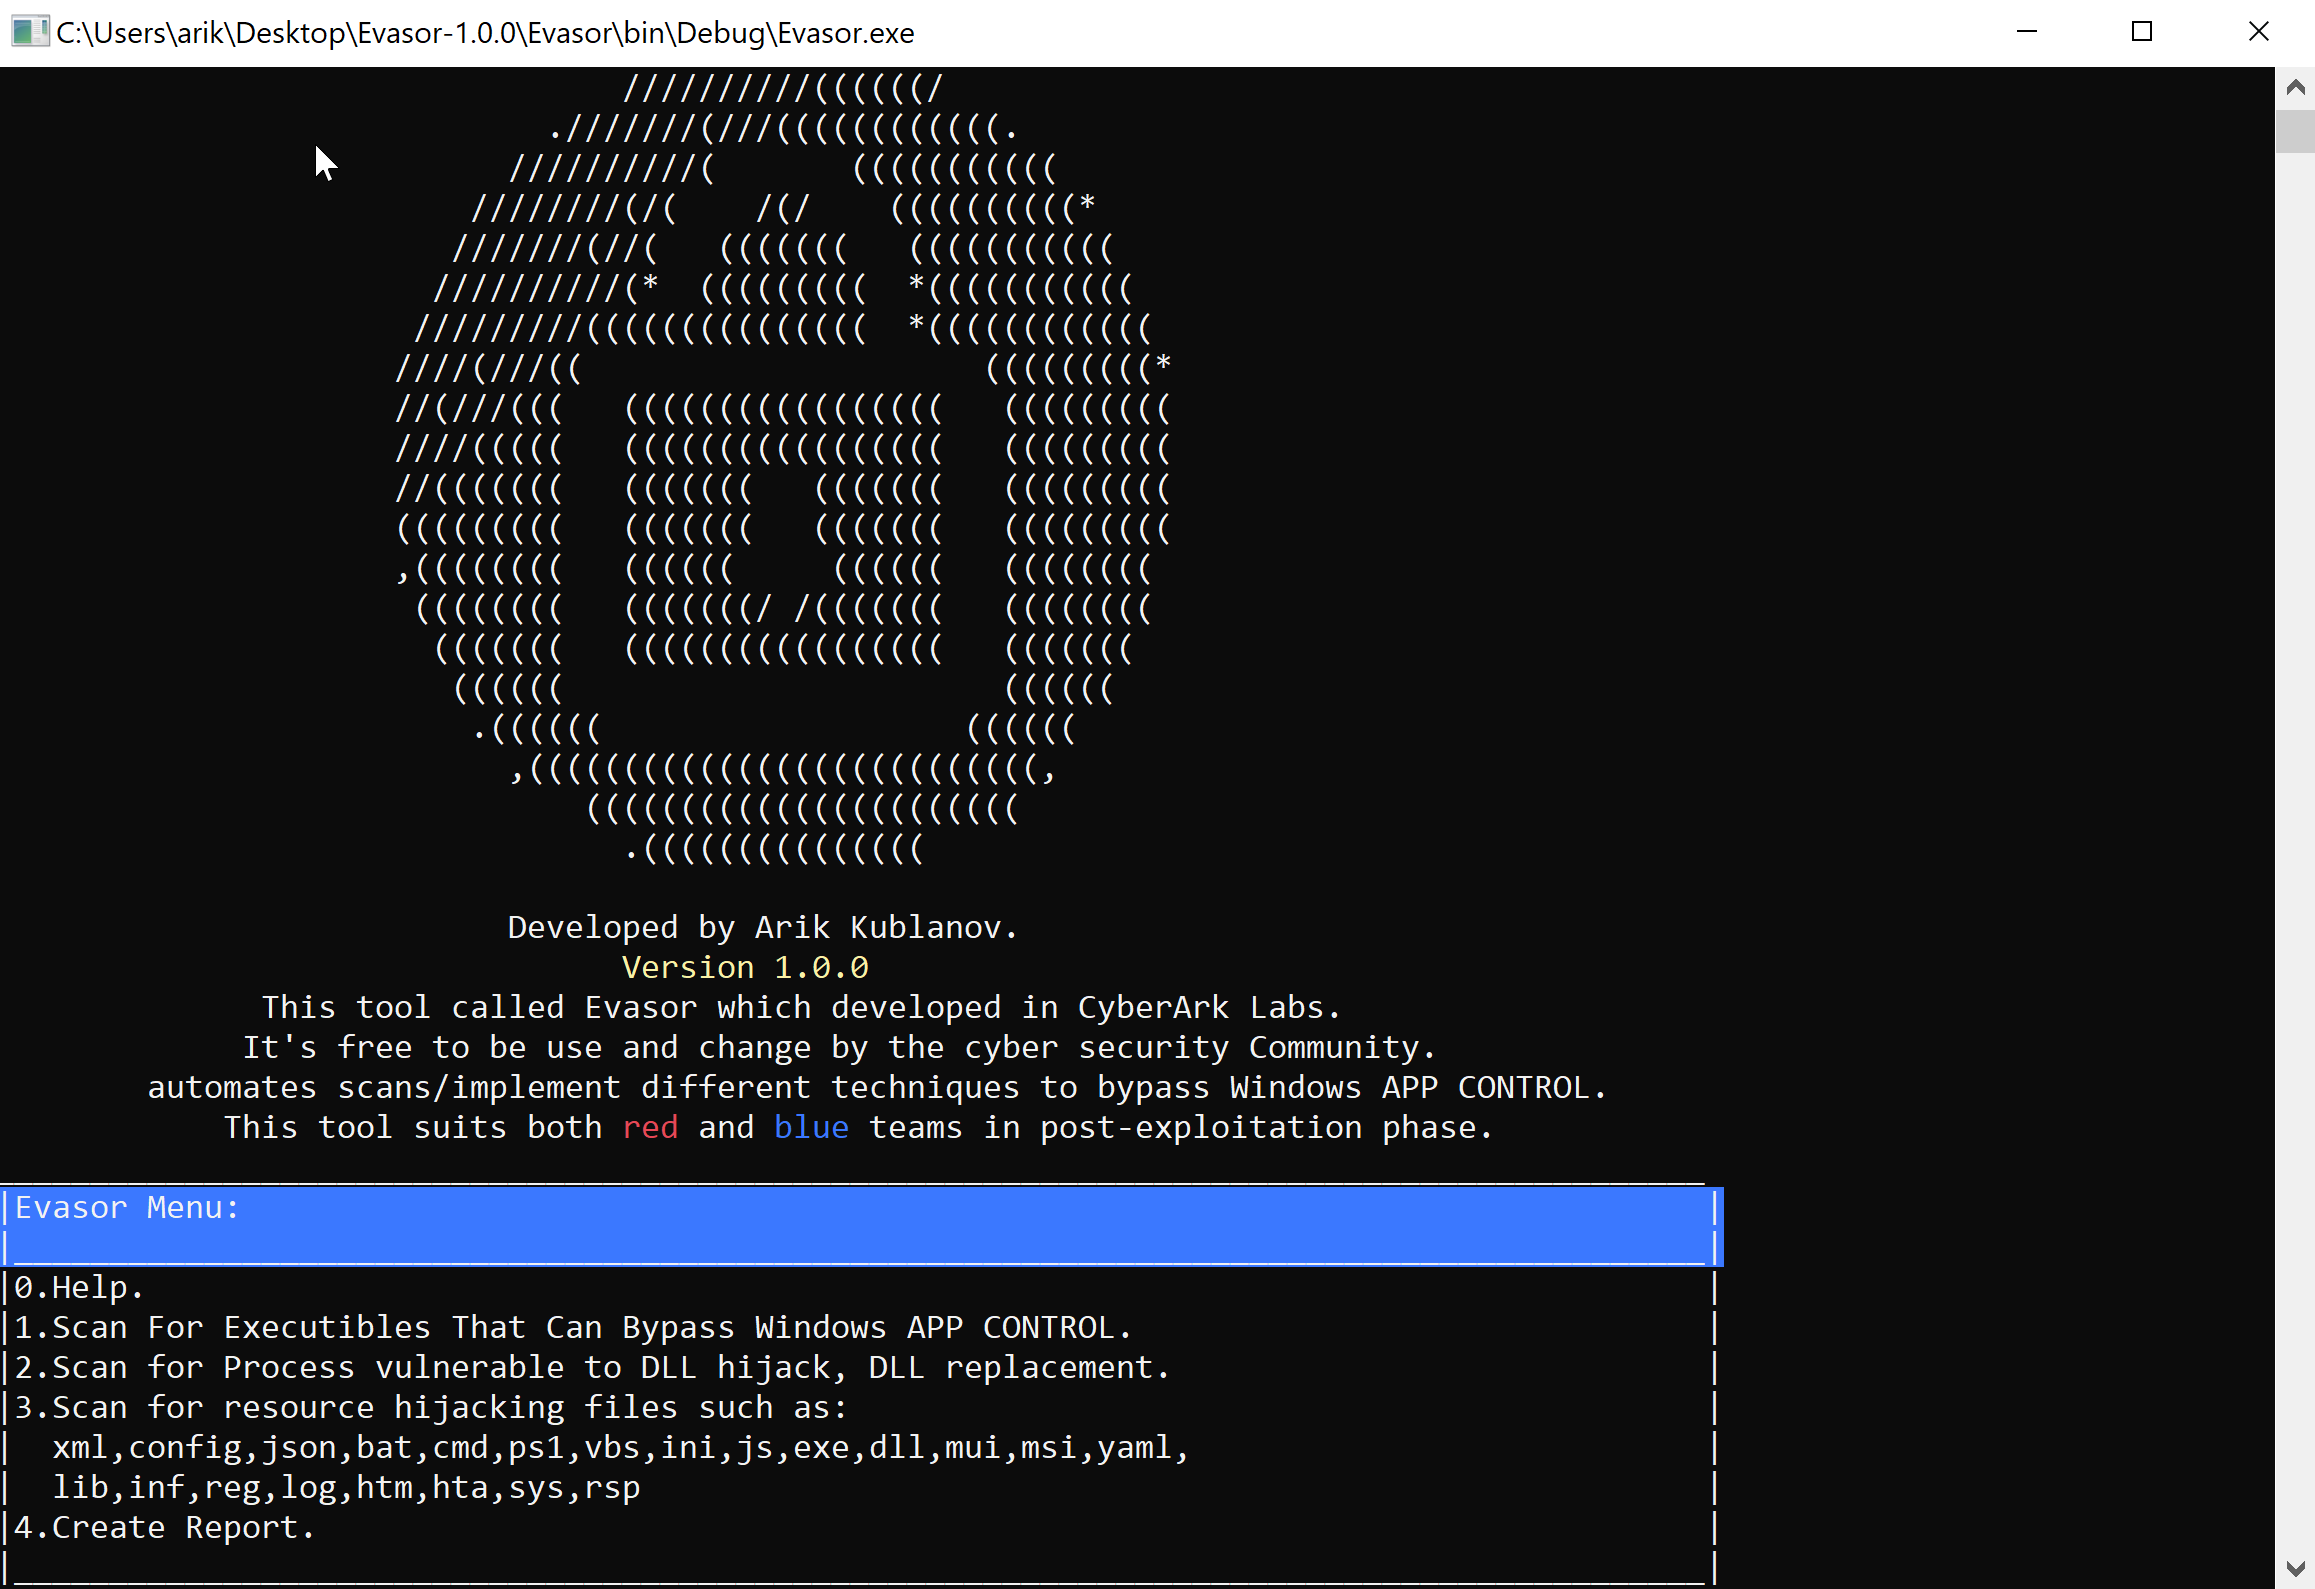 cyberark/evasor
A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies
 shack2/javaserializetools
Java反序列化漏洞利用工具V1.0 Java反序列化相关漏洞的检查工具,采用JDK 1.8+NetBeans8.2开发,软件运行必须安装JDK 1.8或者以上版本。 支持:weblogic xml反序列化漏洞…
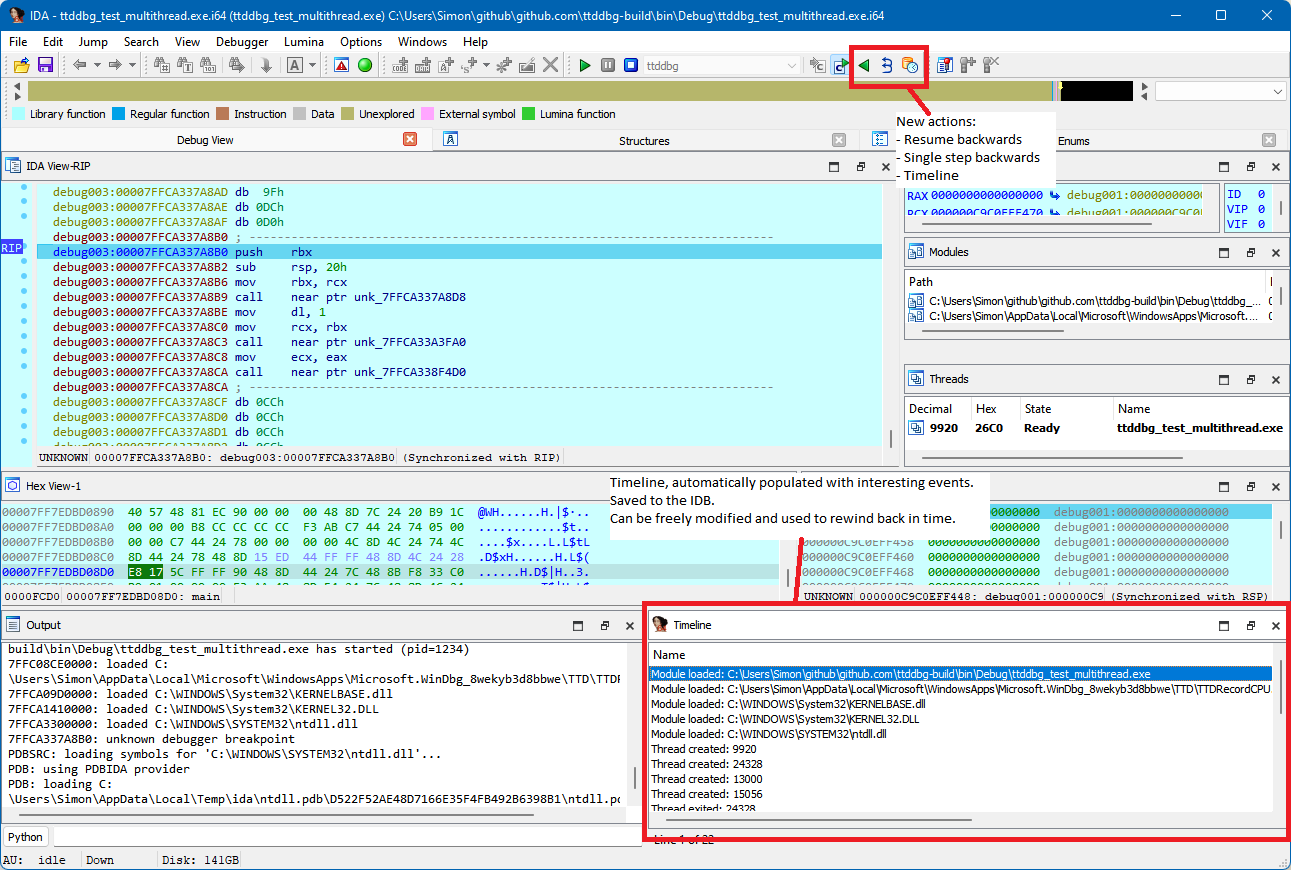 airbus-cert/ttddbg
Time Travel Debugging IDA plugin
 httpvoid/cve-reverse
Curated list of CVEs that have been reverse-engineered and analyzed, serving as a resource for vulnerability research, exploitation understanding,…
 angr/heaphopper
HeapHopper is a bounded model checking framework for Heap-implementations
 hfiref0x/wdextract
Extract Windows Defender database from vdm files and unpack it
 infobyte/cve-2022-27255
Automated firmware analysis and exploit toolkit for CVE-2022-27255, a Realtek eCos SDK SIP ALG buffer overflow affecting 30+ router models. Includes…
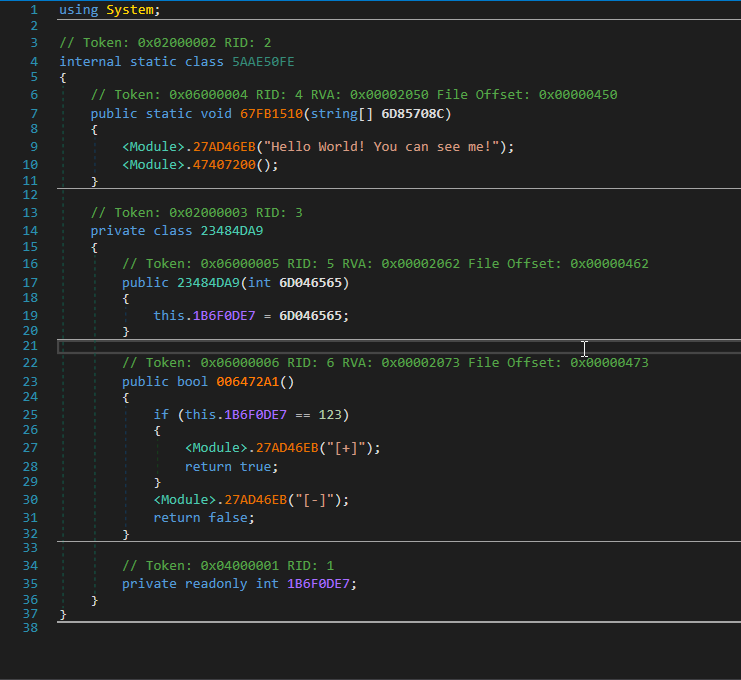 void-stack/vmunprotect.dumper
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.








