
 #1
Binary reverse engineering, disassembly, decompilation, and patching tools.
Kitploit recommended
 mandiant/flare-emu
Scriptable binary emulation framework integrating IDA Pro/Radare2 with Unicorn engine for automated malware analysis, string decryption, and code…
 cristianzsh/freki
Open-source malware analysis platform with static PE analysis, YARA pattern matching, VirusTotal integration, REST API, and Docker deployment for…
 nmatt0/moria
IoT firmware identification and extraction
 cristianzsh/forensictools
Collection of forensic tools
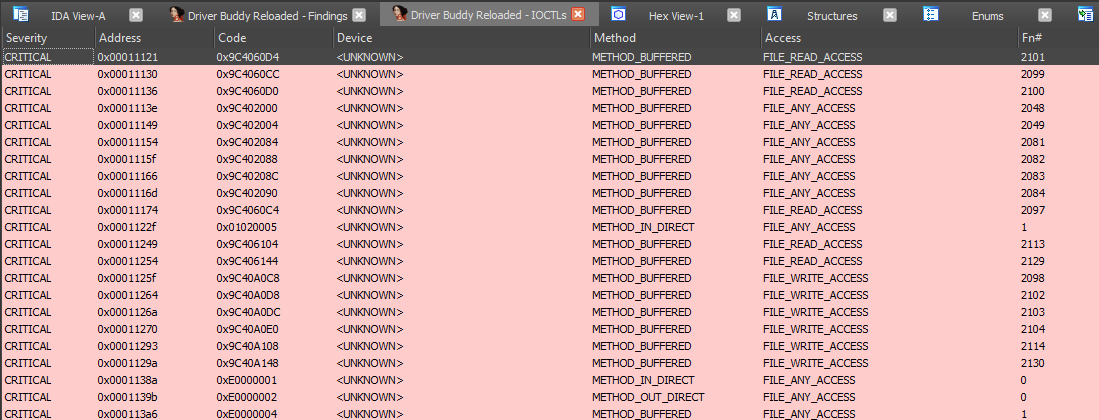 voidsec/driverbuddyreloaded
Driver Buddy Reloaded is an IDA Pro Python plugin that helps automate some tedious Windows Kernel Drivers reverse engineering tasks
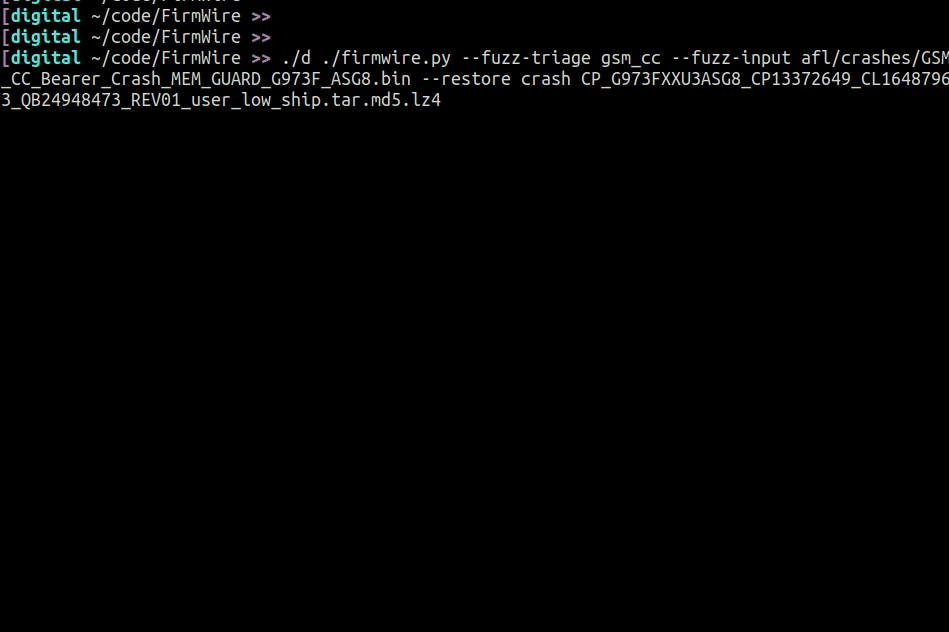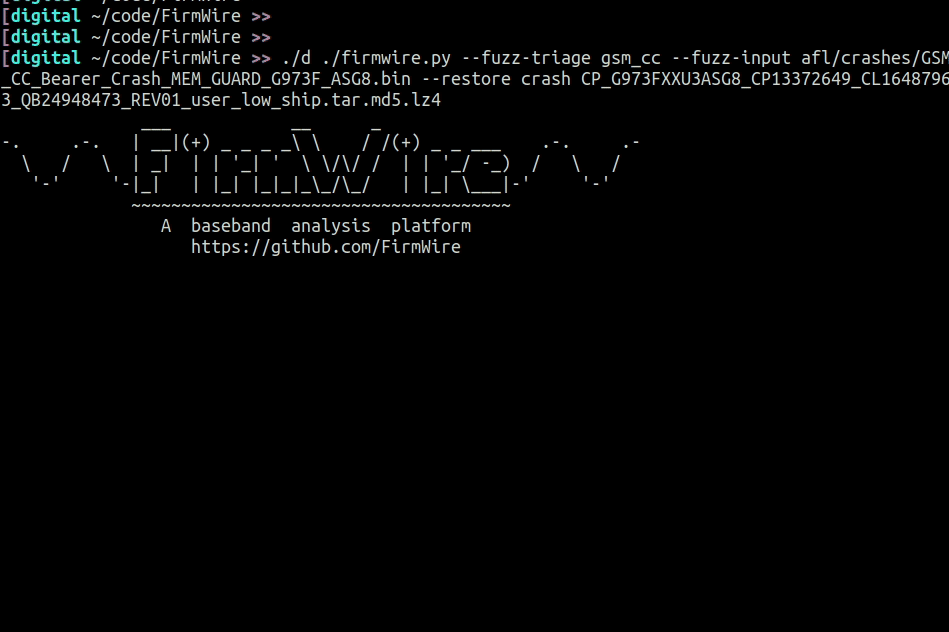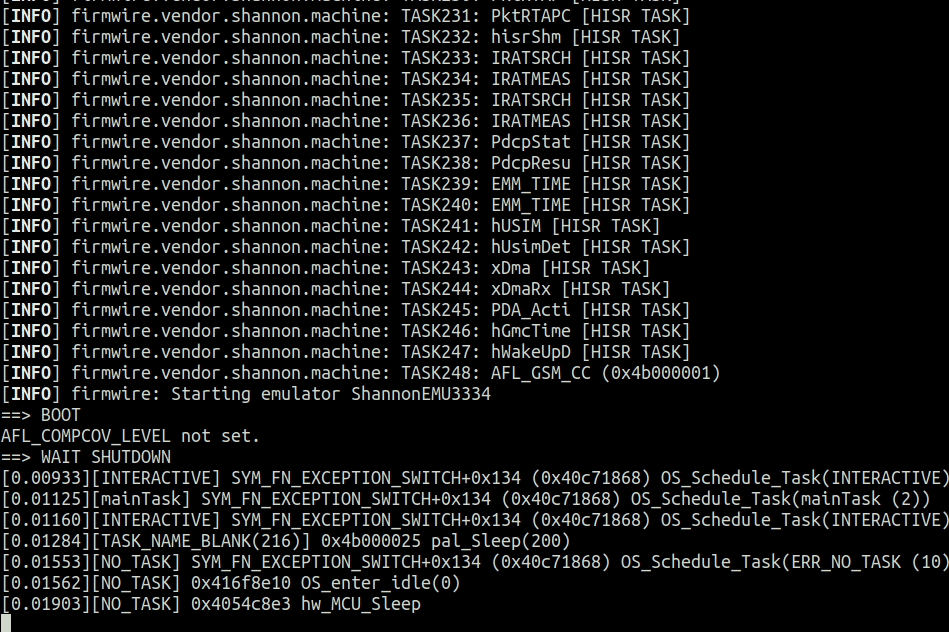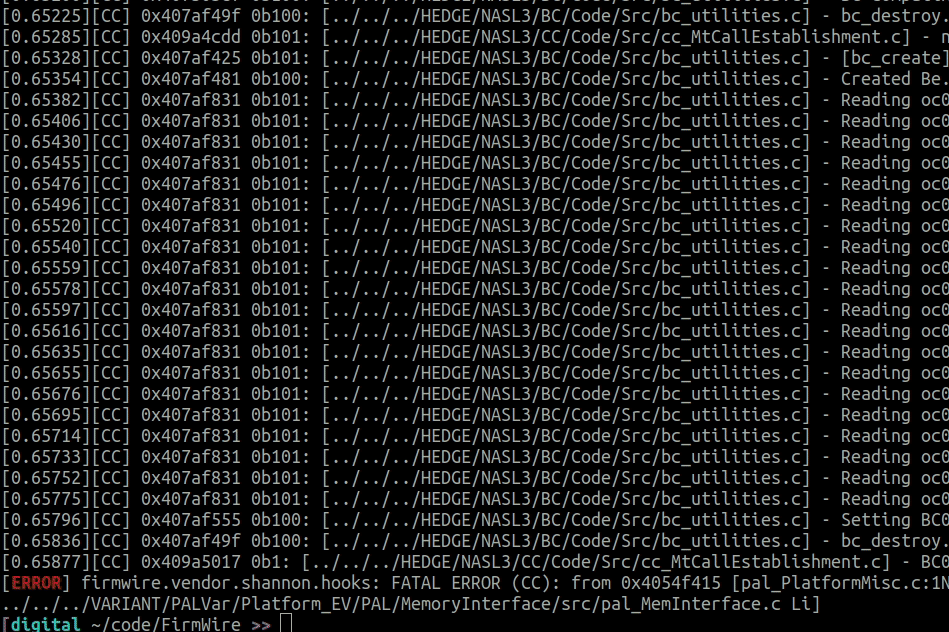 firmwire/firmwire
FirmWire is a full-system baseband firmware emulation platform for fuzzing, debugging, and root-cause analysis of smartphone baseband firmwares
 0xdea/ghidra-scripts
Curated Ghidra scripts to automate reverse engineering and vulnerability analysis: locate insecure functions, extract decompiler pseudocode, fix…
 isecpartners/introspy-ios
Security profiling for blackbox iOS
 sentinelabs/alphagolang
IDApython Scripts for Analyzing Golang Binaries
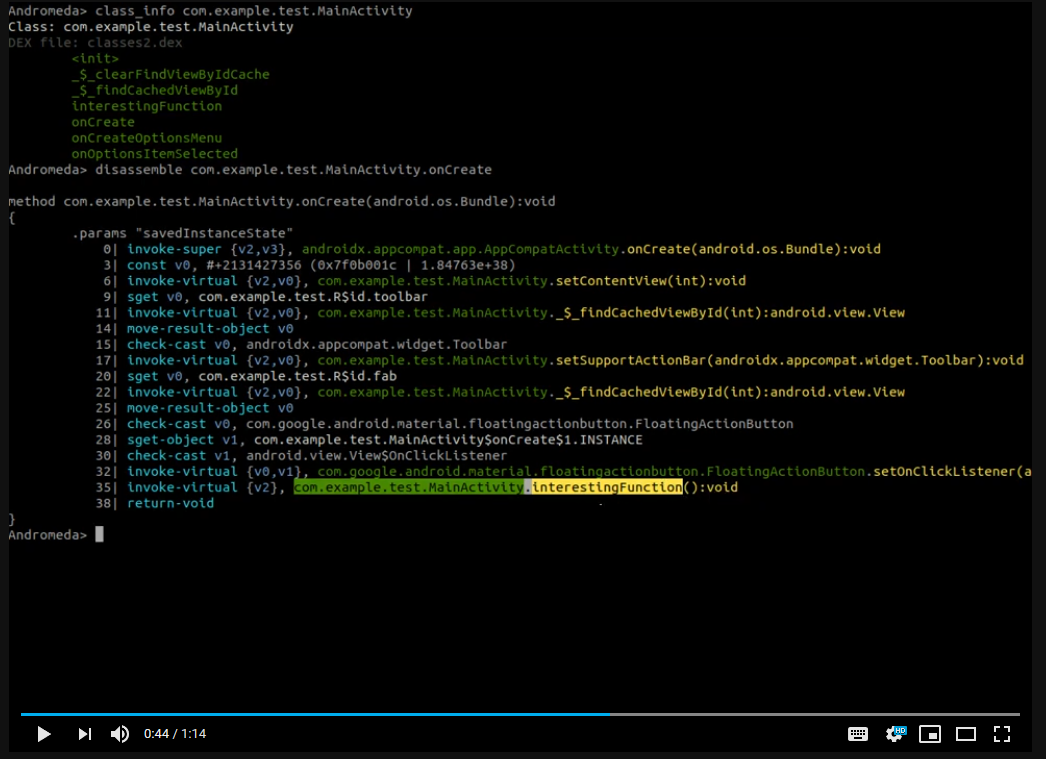 secrary/andromeda
C/C++ interactive reverse engineering tool for Android applications, enabling fast static analysis and binary inspection of APK files.
 raphaelsc/am-i-affected-by-meltdown
Meltdown Exploit / Proof-of-concept / checks whether system is affected by Variant 3: rogue data cache load (CVE-2017-5754), a.k.a MELTDOWN.
 suleram/view8
Decompiles serialized V8 bytecode (JSC files) into high-level readable JavaScript-like code, with support for multiple V8 versions, tree output, and…
 openrce/pydbg
A pure-python win32 debugger interface.
 checkpointsw/karta
IDA Python plugin for fast, location-driven matching of open-source library symbols in binaries, enabling efficient reverse engineering and…
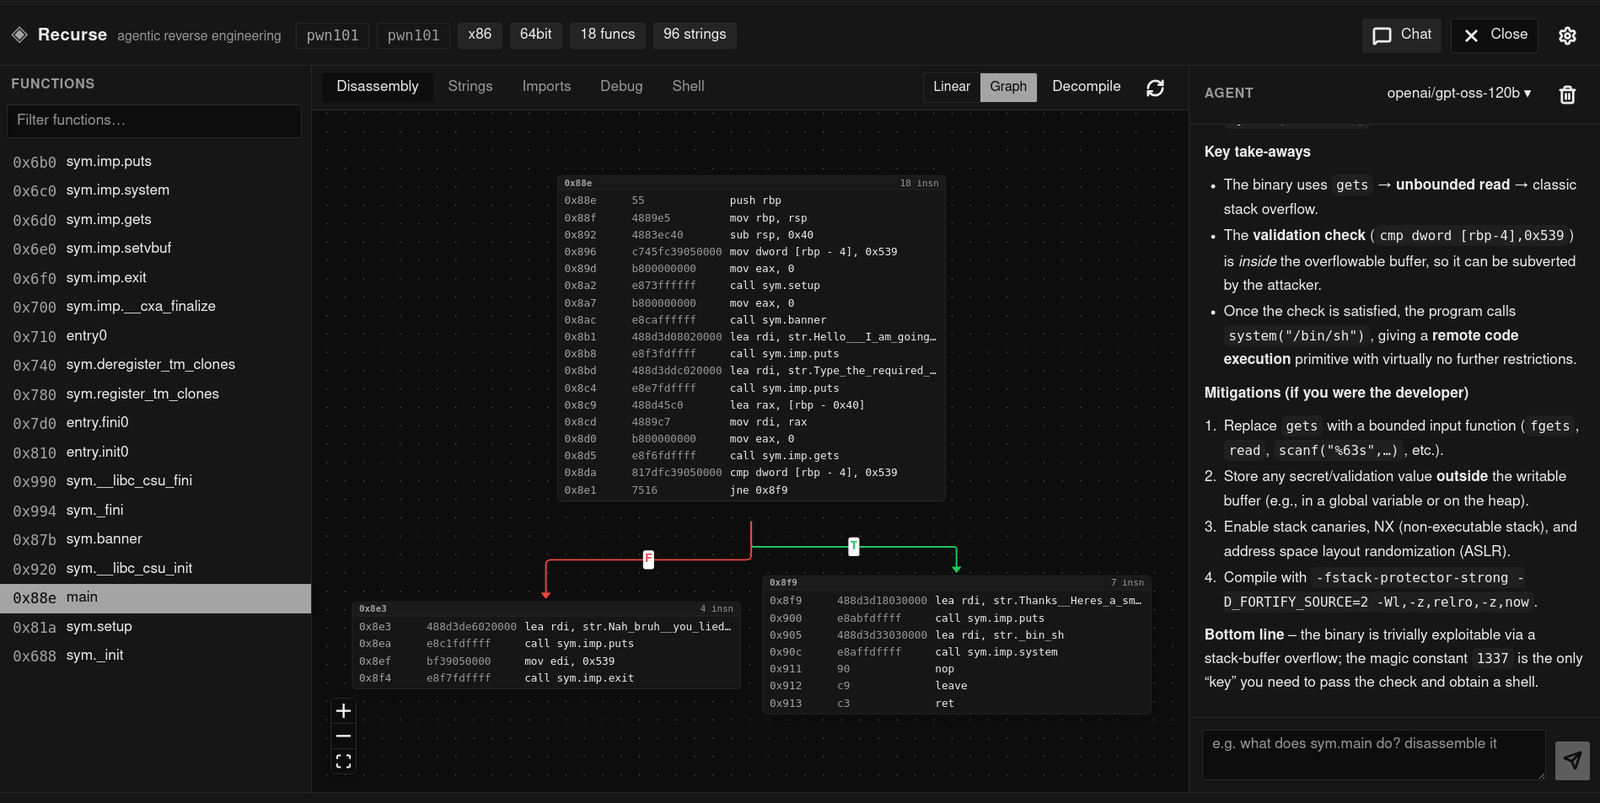 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
 mr-un1k0d3r/redteamccode
Red Team C code repo
 robertcprice/ncpu
Research runtime for differentiable neural computers, GPU-based CPU emulation, and program synthesis. Features neural ALU, constant-time crypto, JEPA…
 mildsunrise/protobuf-inspector
🕵️ Tool to reverse-engineer Protocol Buffers with unknown definition








