
 #1
Binary reverse engineering, disassembly, decompilation, and patching tools.
Kitploit recommended
 vitoplantamura/bugchecker
SoftICE-like kernel debugger for Windows 11
 loerting/threadtear
Multifunctional java deobfuscation tool suite
 nac-l/mergen
Deobfuscation via optimization with usage of LLVM IR and parsing assembly.
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
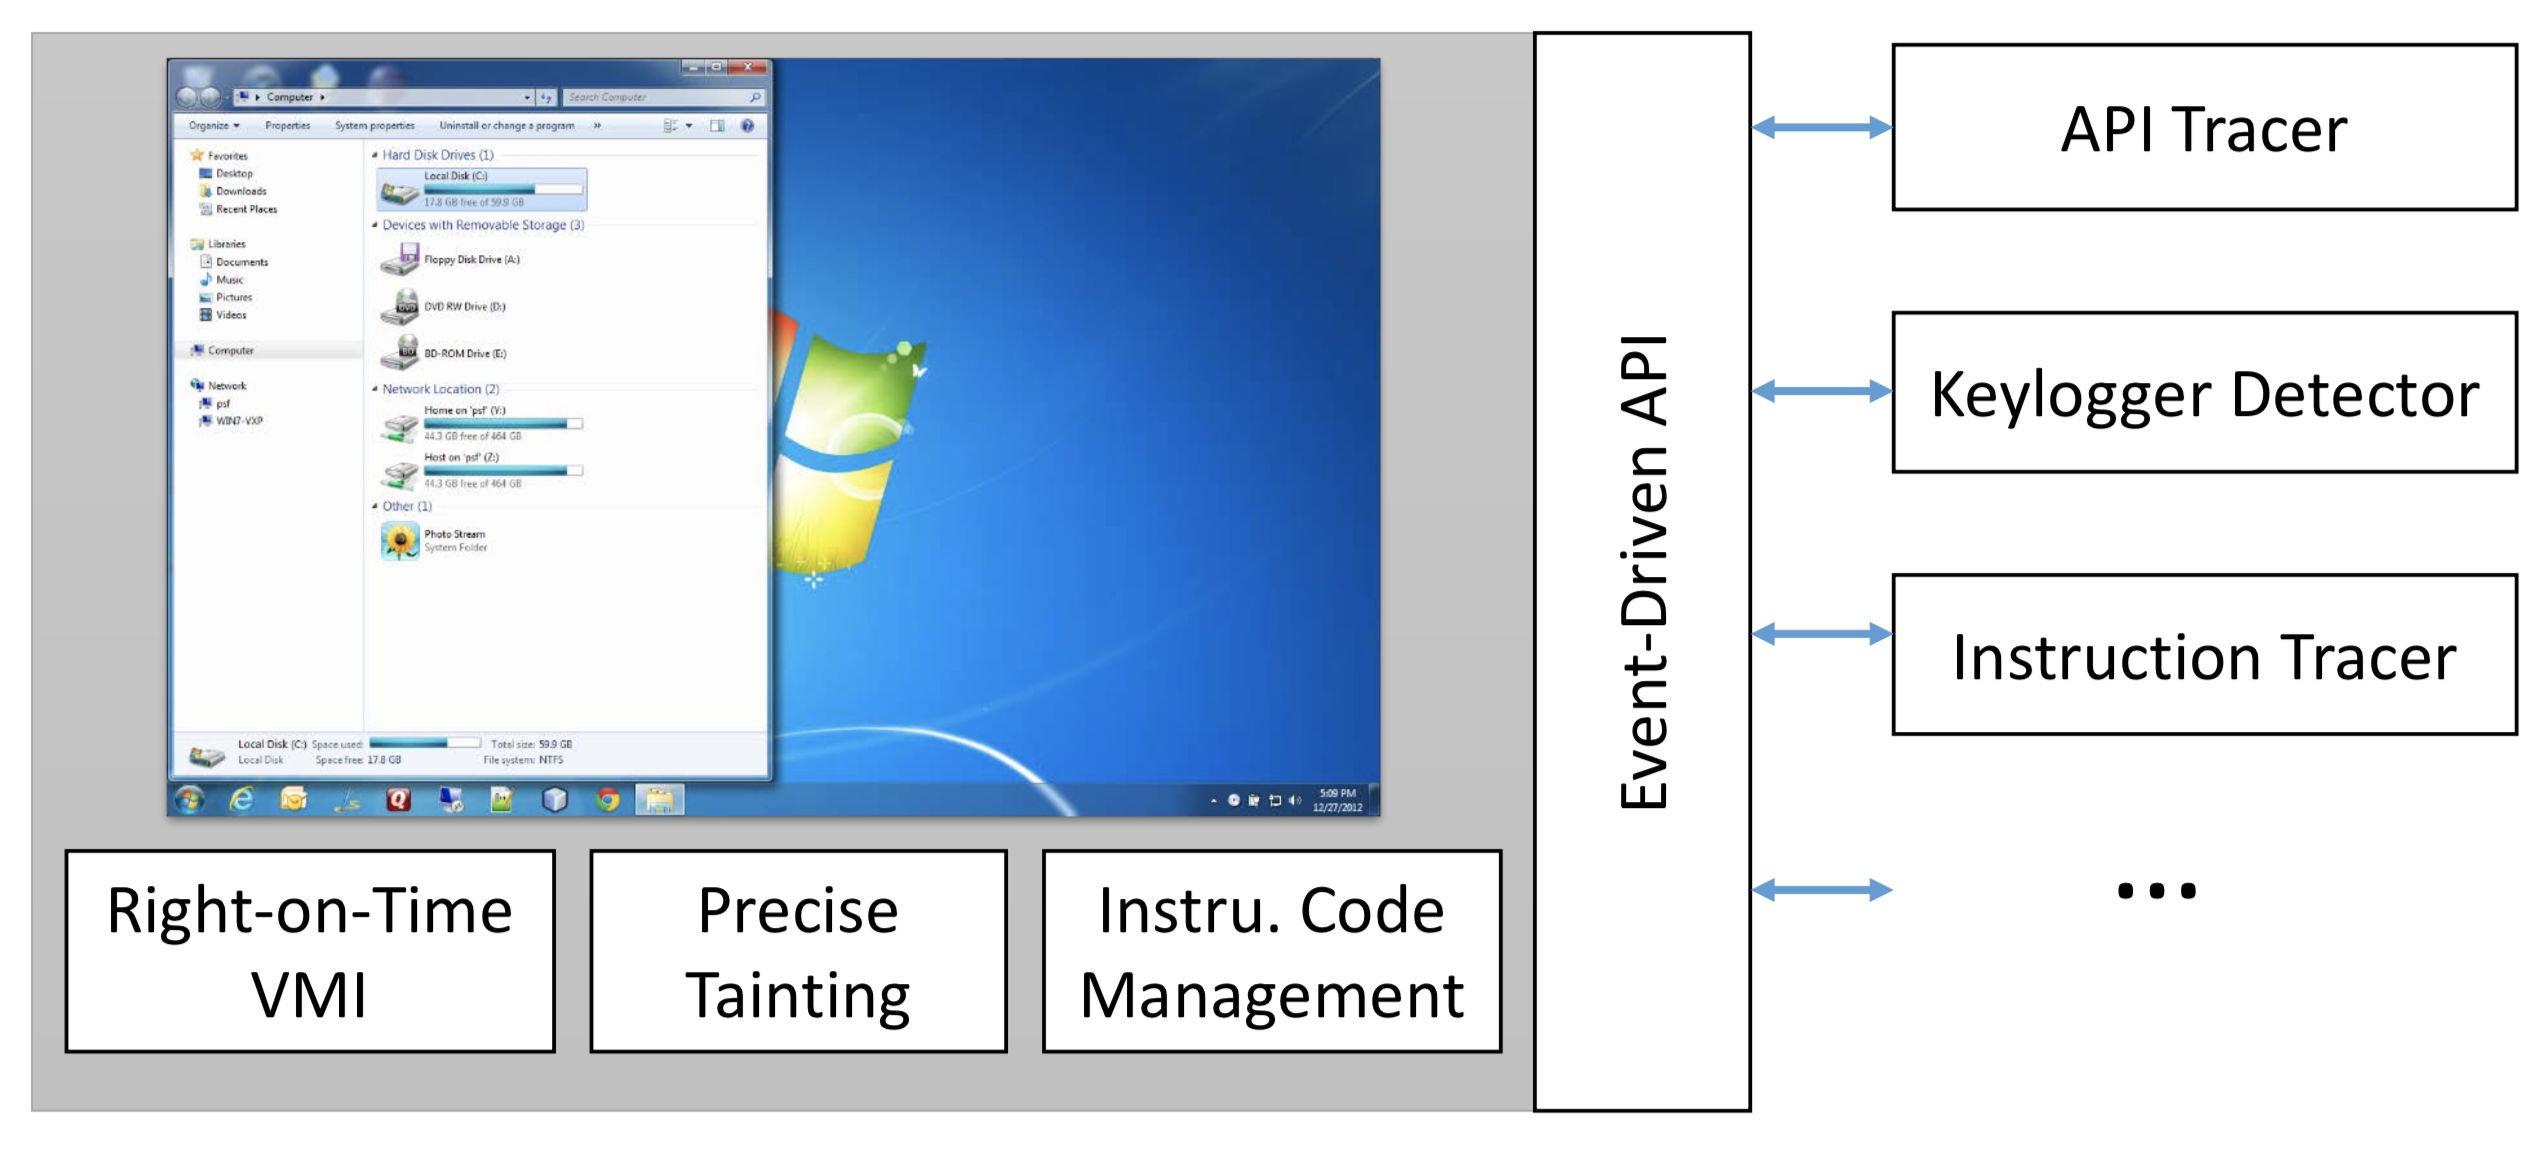 decaf-project/decaf
DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
 lunixbochs/patchkit
binary patching from Python
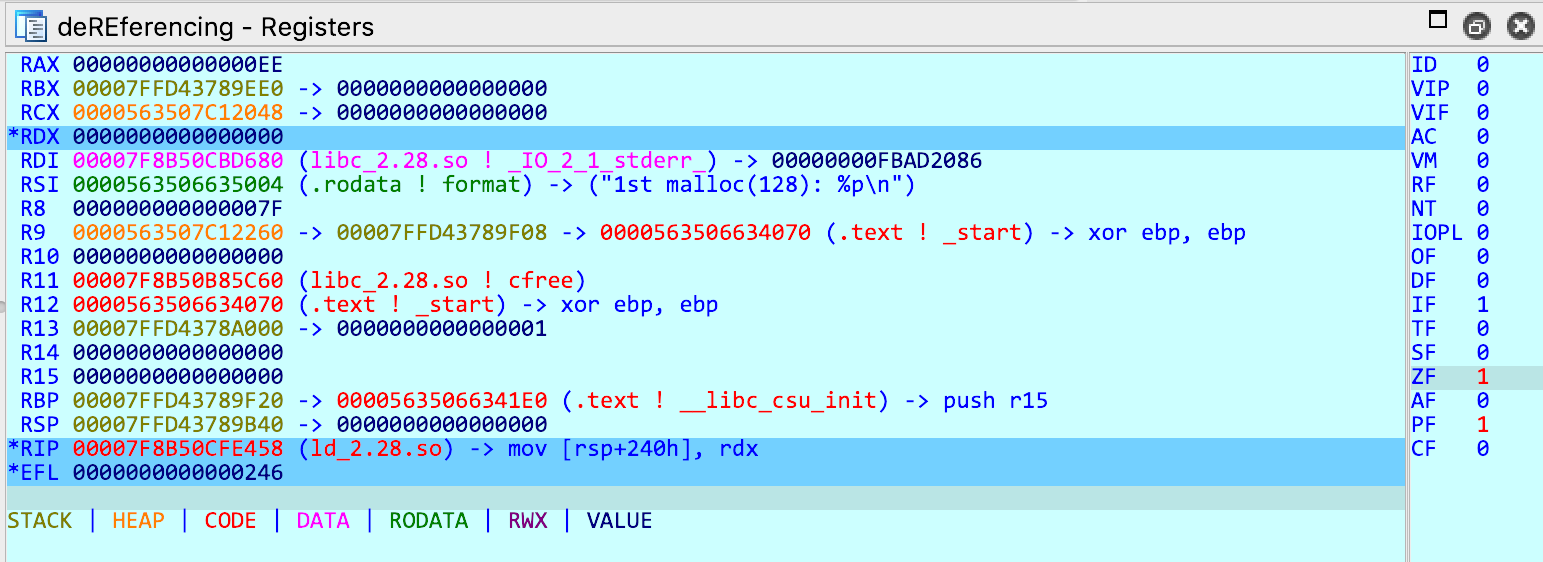 danigargu/dereferencing
IDA Pro plugin that implements more user-friendly register and stack views
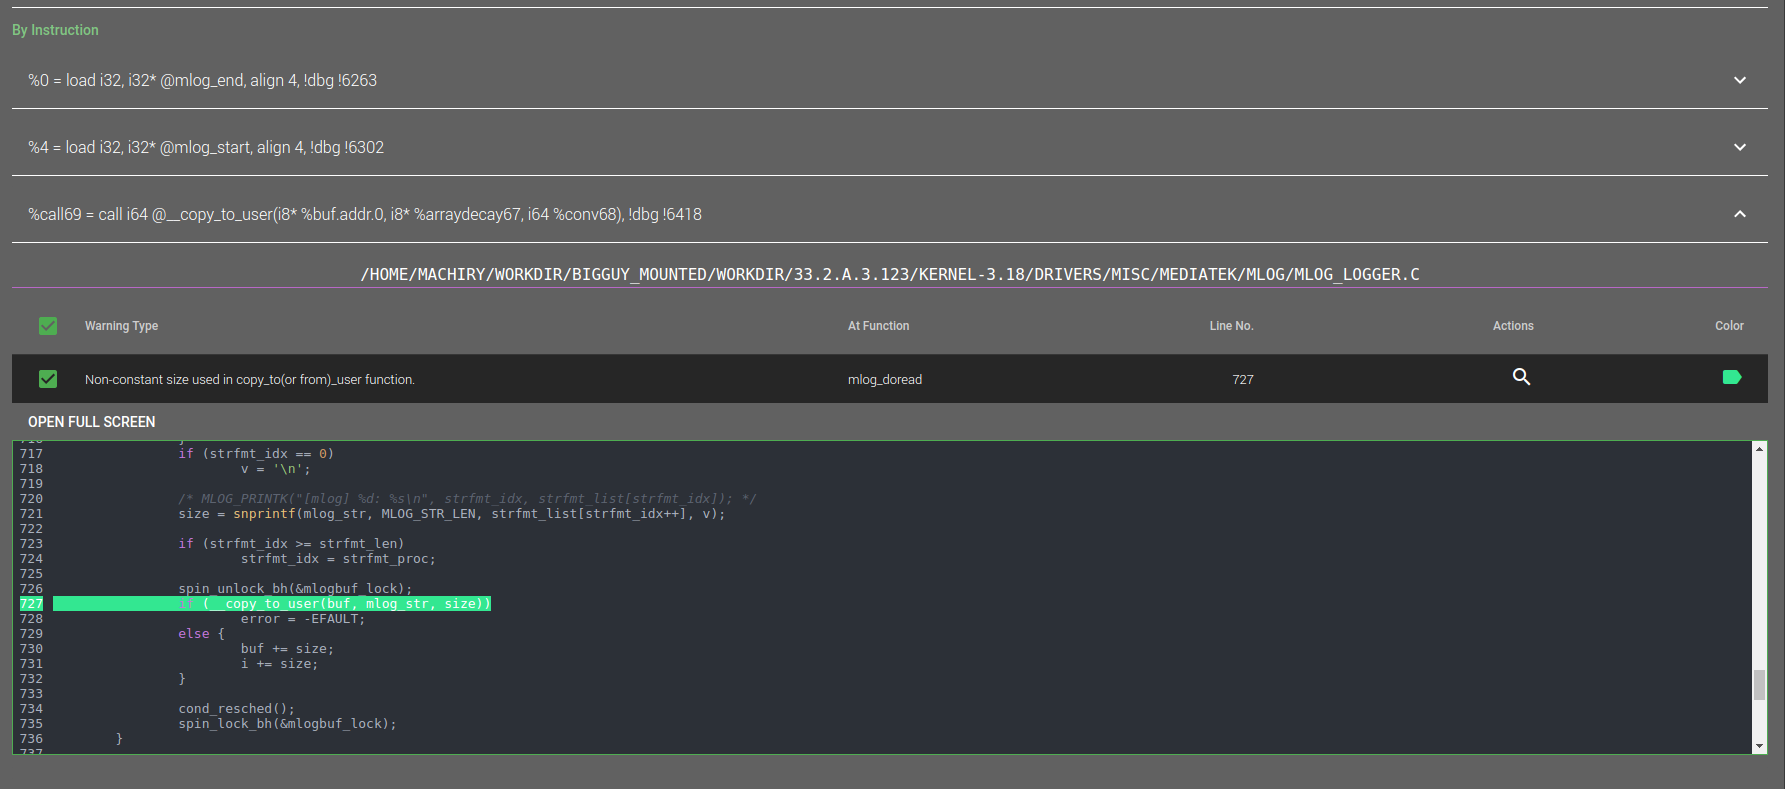 ucsb-seclab/dr_checker
DR.CHECKER : A Soundy Vulnerability Detection Tool for Linux Kernel Drivers
 panda-re/lava
LAVA: Large-scale Automated Vulnerability Addition
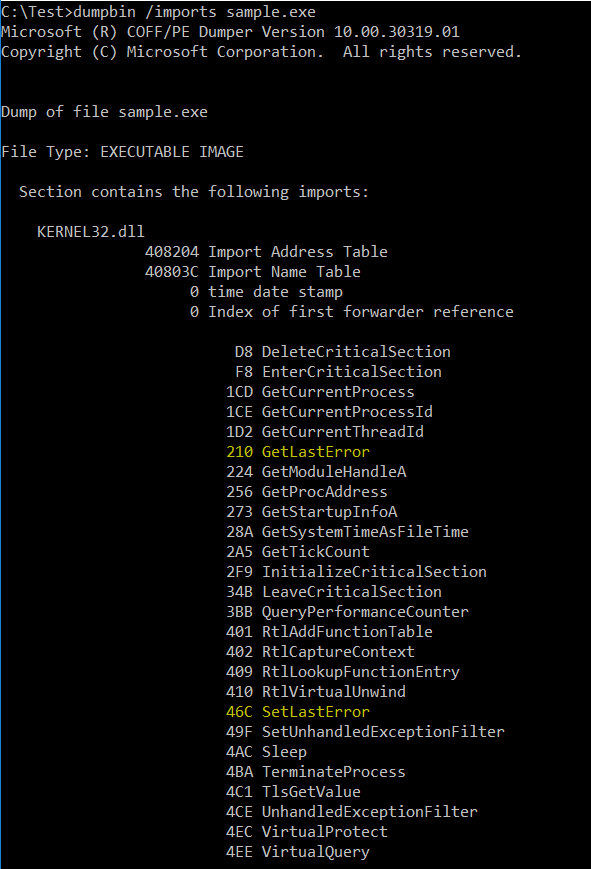 d35ha/callobfuscator
Obfuscate specific windows apis with different apis
 netzob/netzob
Open-source toolkit for reverse engineering, modeling, and fuzzing communication protocols. Infers message formats and state machines from network…
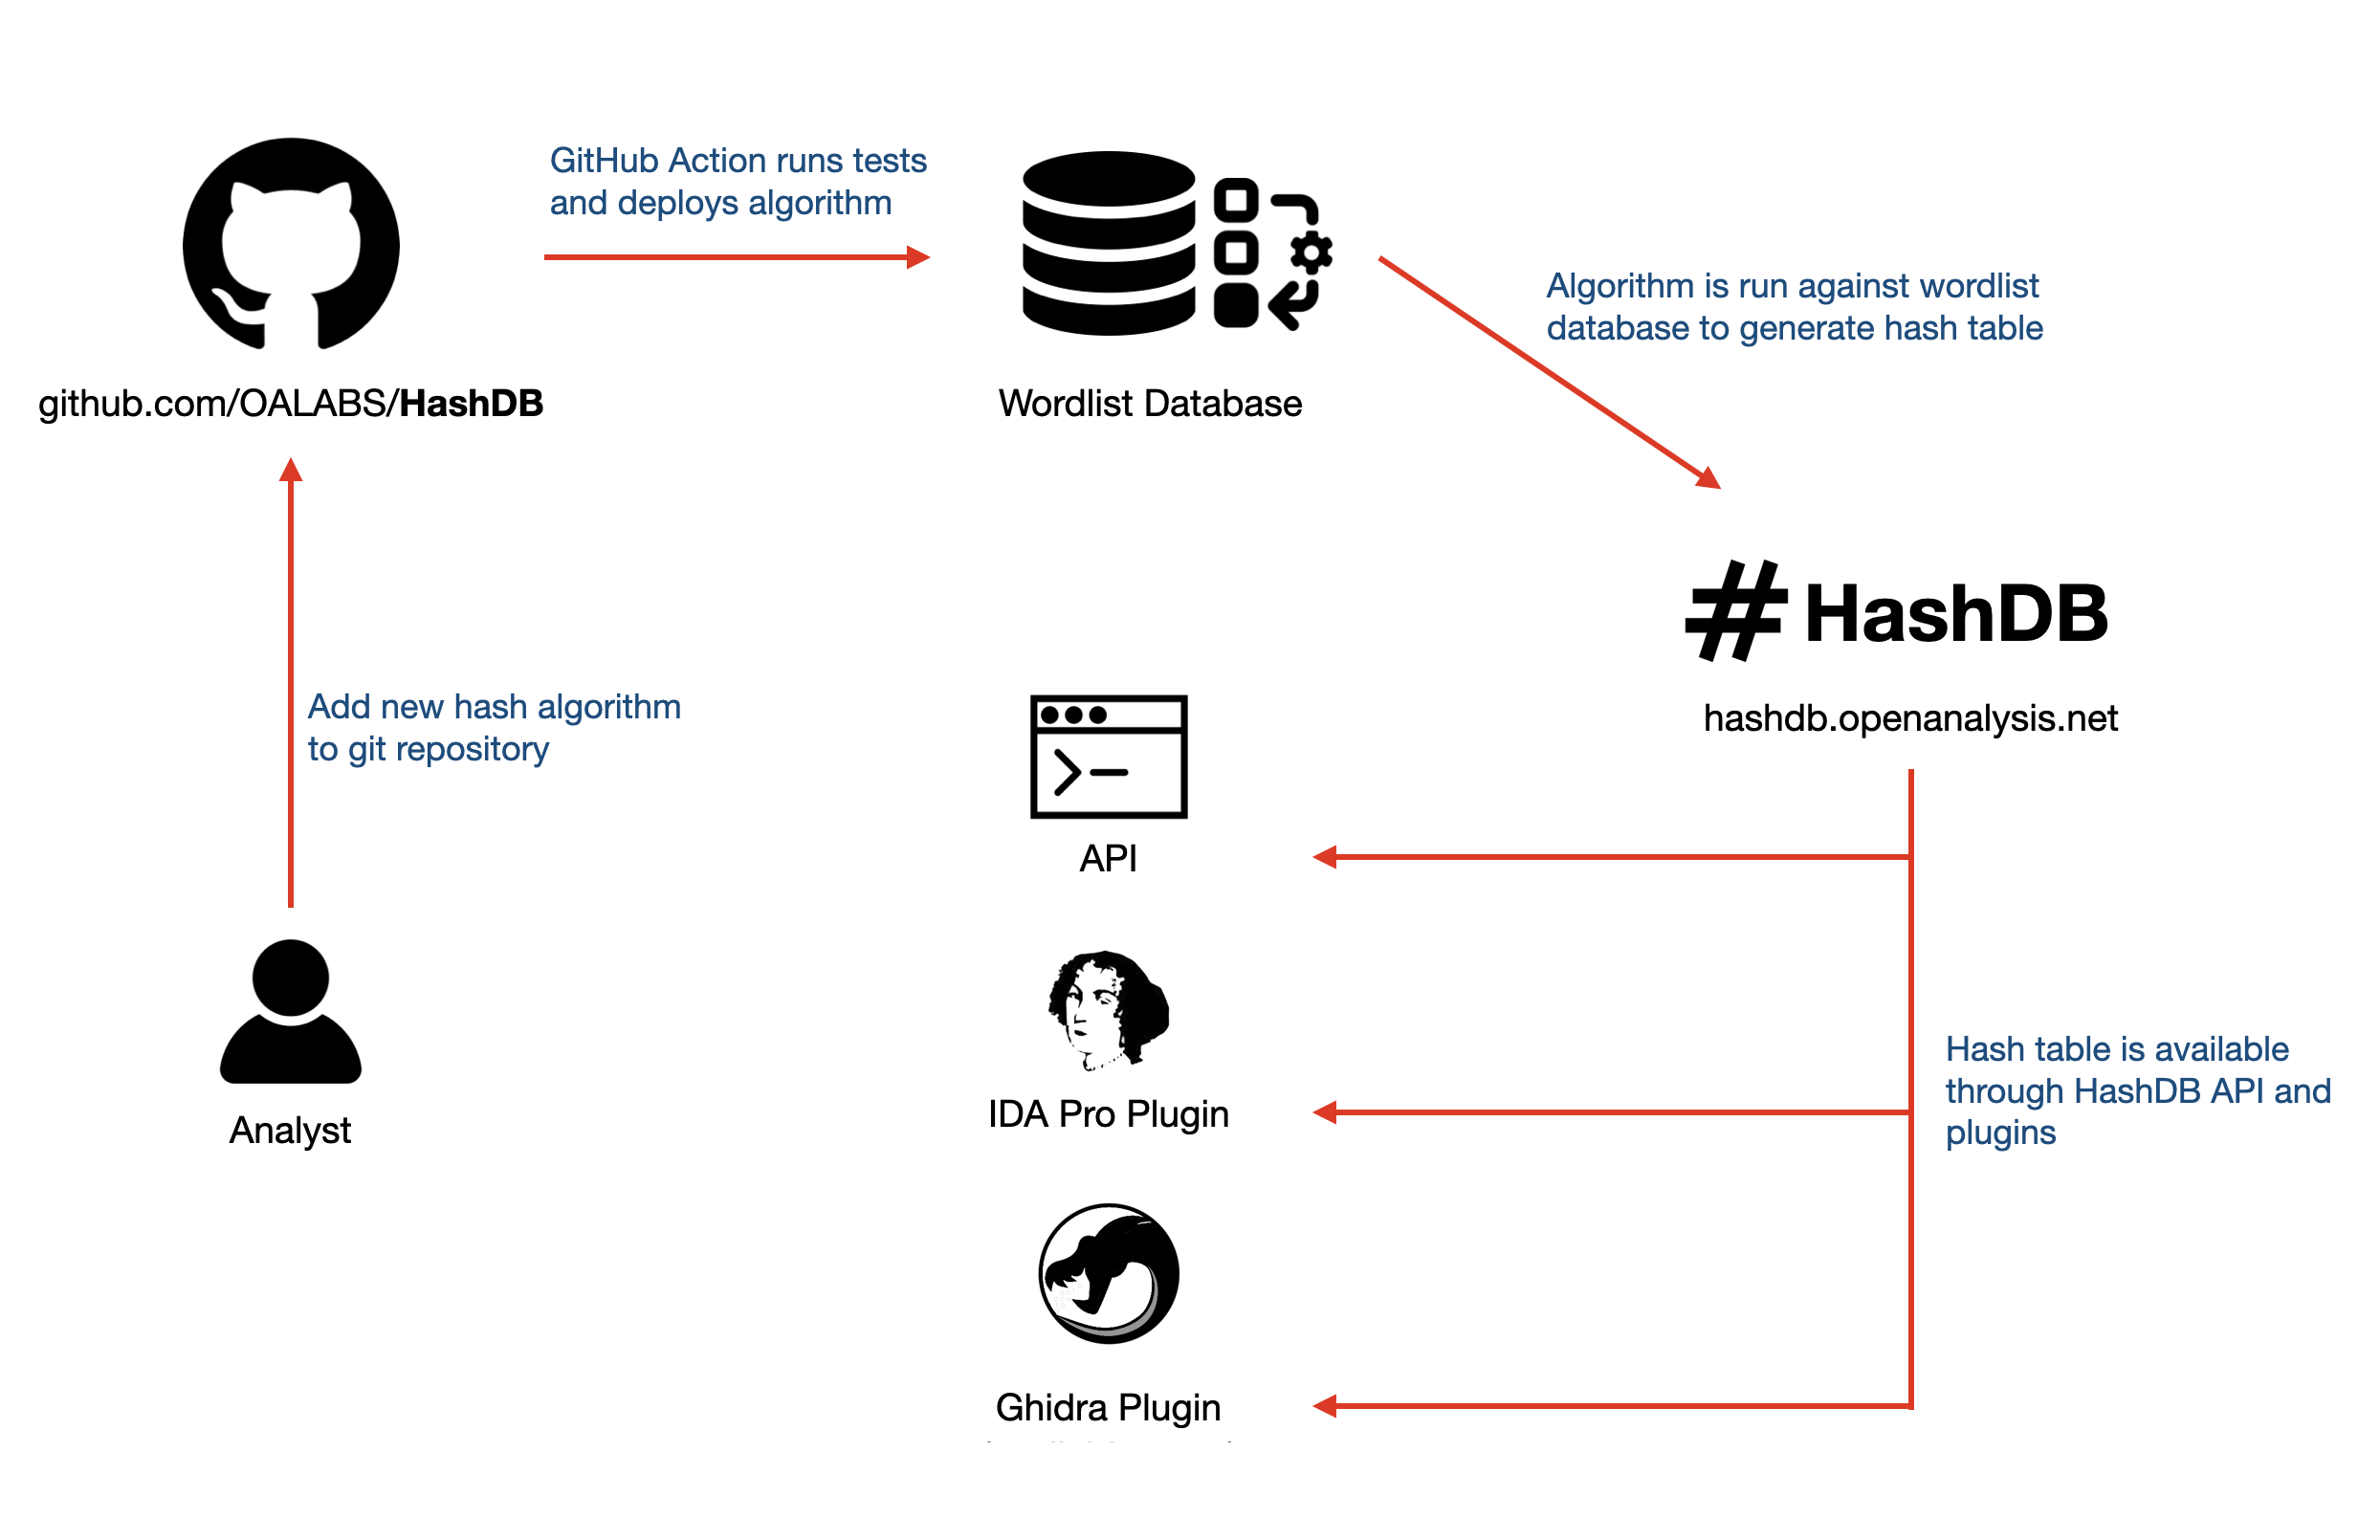 oalabs/hashdb
Assortment of hashing algorithms used in malware
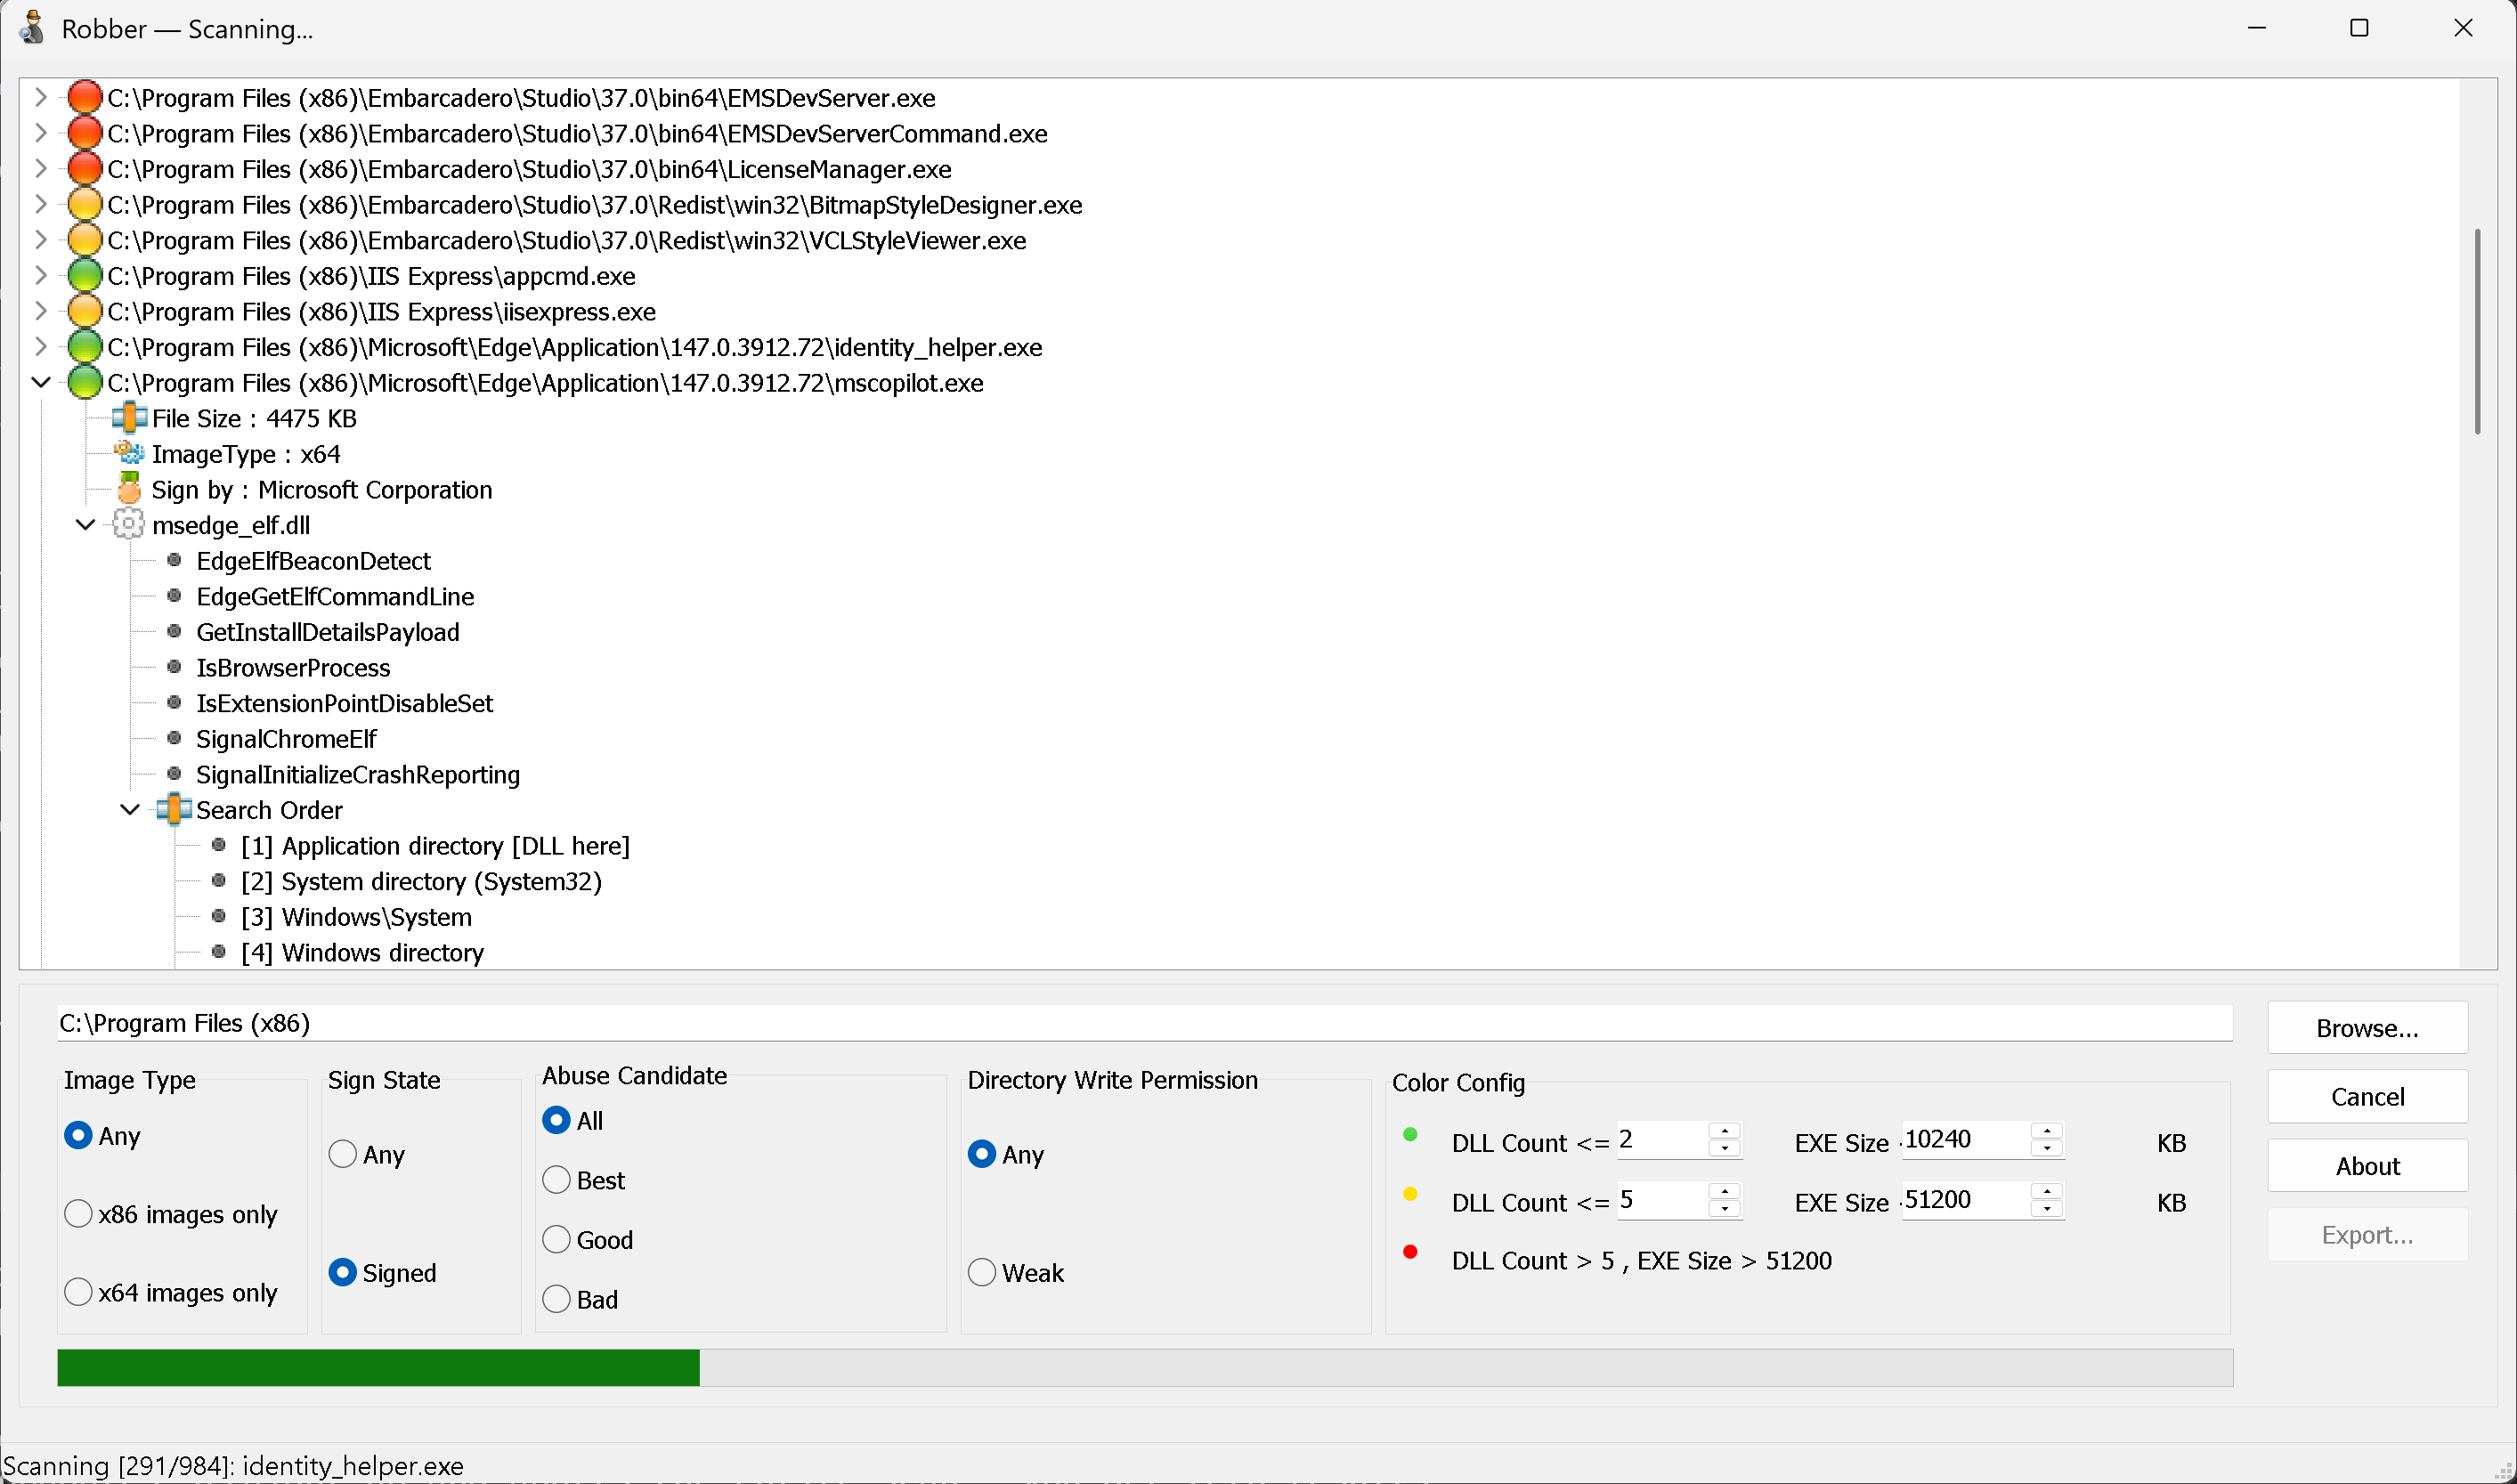 mojtabatajik/robber
Robber is open source tool for finding executables prone to DLL hijacking
 0sec-labs/0
Open-source AI security harness. Includes a web UI for code analysis, pentesting, vulnerability research, reverse engineering, verification, and…
 yadyvazifeh1oz92/ecdsa-private-key-recovery
Perform ECDSA and DSA nonce reuse private key recovery attacks to analyze signature vulnerabilities and recover private keys from blockchain…
 radareorg/r2ai
Radare2 AI plugin using local or remote LLMs for decompilation, function explanation, vulnerability detection, renaming, and scripted reverse…
 mandiant/flare-emu
Scriptable binary emulation framework integrating IDA Pro/Radare2 with Unicorn engine for automated malware analysis, string decryption, and code…








