
 #1
Binary reverse engineering, disassembly, decompilation, and patching tools.
Kitploit recommended
 ioncodes/idacode
An integration for IDA and VS Code which connects both to easily execute and debug IDAPython scripts.
 konatabrk/shellen
:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes
 theflink/hunt-sleeping-beacons
Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…
 zeze-zeze/ioctlance
A tool that is used to hunt vulnerabilities in x64 WDM drivers
 mandiant/stringsifter
A machine learning tool that ranks strings based on their relevance for malware analysis.
 al3xtjames/ghidra-firmware-utils
Ghidra extension for PC firmware reverse engineering, providing loaders for PCI option ROMs, Intel Flash Descriptor, coreboot CBFS, and UEFI firmware…
 trailofbits/trailmark
Build and query a graph database representation of source code
 mertdas/privkit
PrivKit is a simple beacon object file that detects privilege escalation vulnerabilities caused by misconfigurations on Windows OS.
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 seekbytes/ipa
GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…
 ejfkdev/ddc
Android DEX → Java decompiler in Rust, built for speed — full apps in seconds, queries in milliseconds. Progressive analysis, javac-verified output,…
 hasherezade/mal_unpack
Dynamic unpacker based on PE-sieve
 bishopfox/bfdecrypt
Utility to decrypt App Store apps on jailbroken iOS 11.x
 jfmaes/lazysign
Create fake certs for binaries using windows binaries and the power of bat files
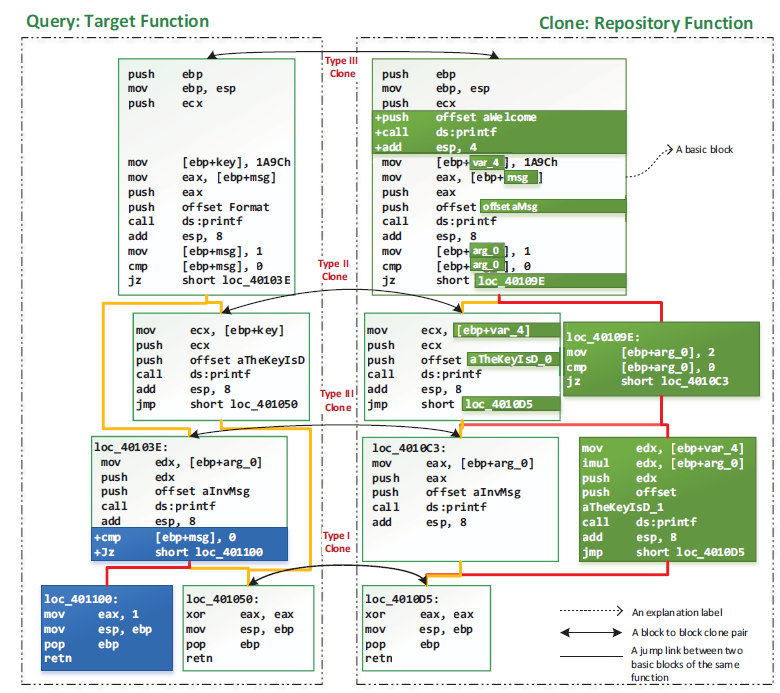 mcgill-dmas/kam1n0-community
Scalable assembly analysis platform for indexing, clone search, and executable classification using static, dynamic, and machine-learning techniques…
 oalabs/hashdb-ida
HashDB API hash lookup plugin for IDA Pro
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 therealsaumil/static-arm-bins
Statically compiled ARM binaries for debugging and runtime analysis








