
 #1
AI-powered decompilation, binary analysis, code summarization, and malware analysis tools.
Kitploit recommended

 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 martyx00/vulnfanatic-ng
BianryNinja plugin for identifying vulnerabilities in decompiled binaries with both programmatic scans and LLM support.
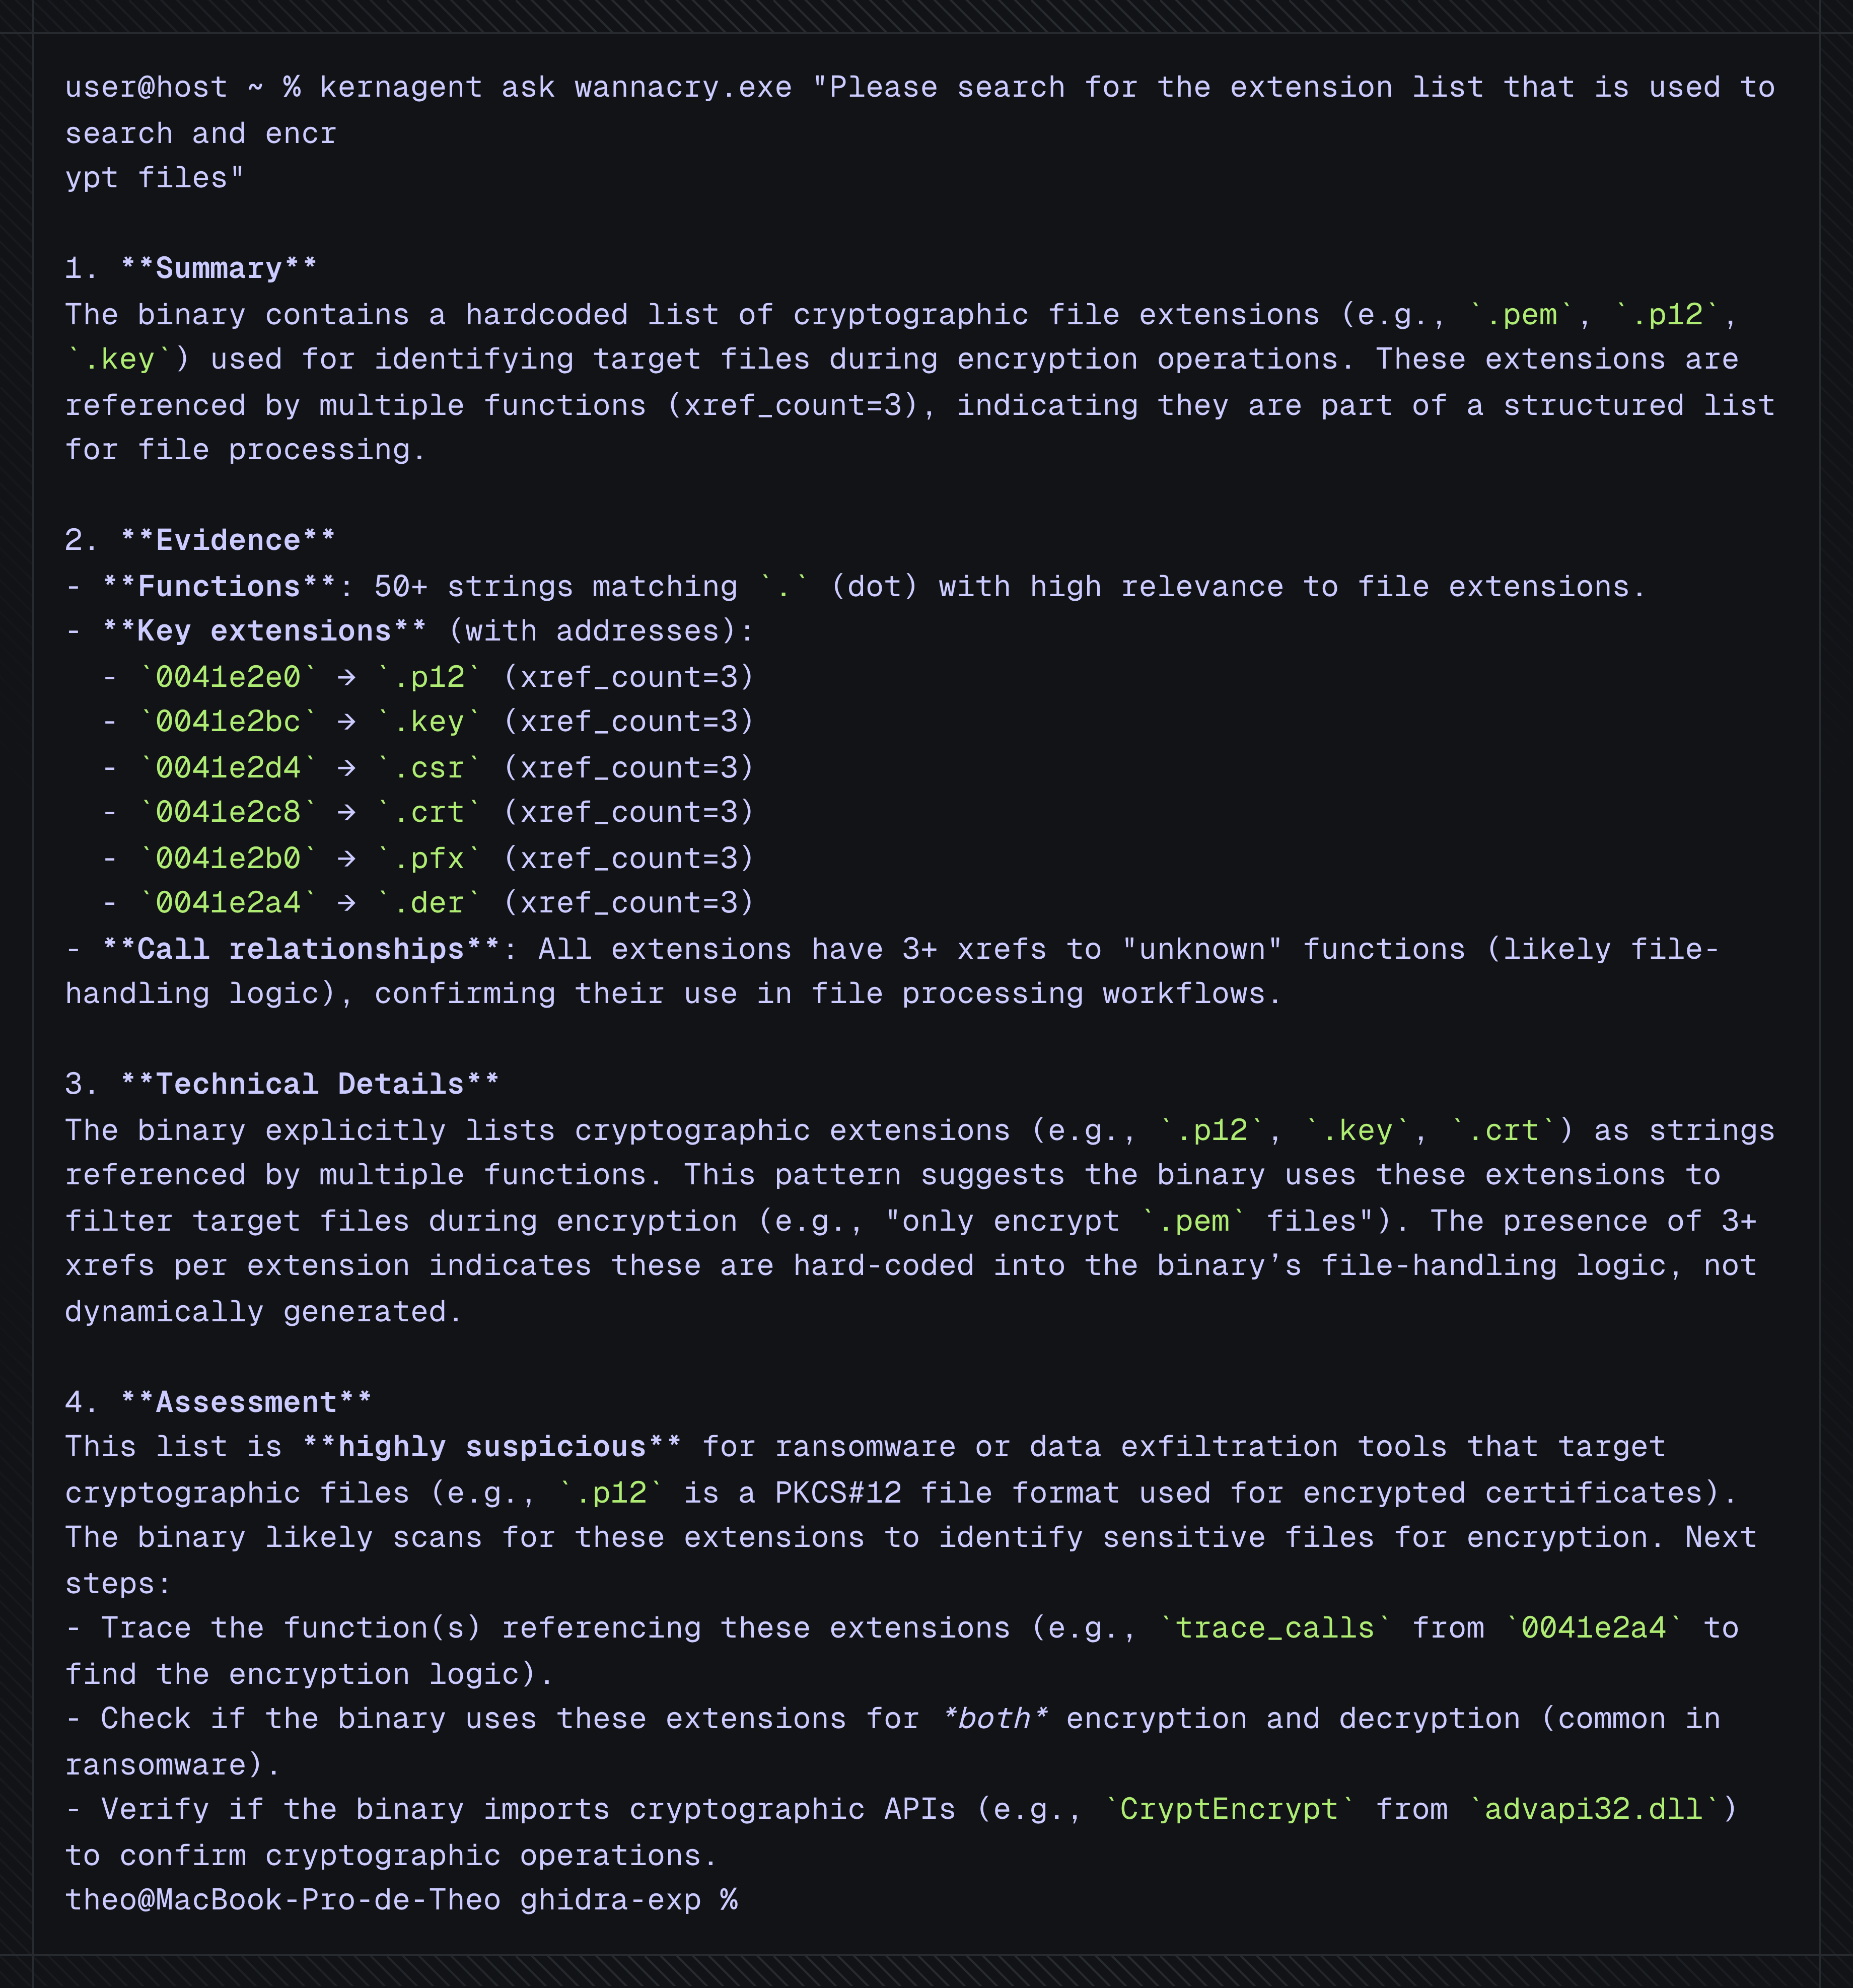 karib0u/kernagent
Headless AI agent for deterministic reverse engineering.
 akamai/cve-2025-60719-afd.sys
Proof-of-concept and root-cause analysis of CVE-2025-60719, a use-after-free vulnerability in Windows afd.sys leading to local privilege escalation,…
 knifeyspoony/ghidra-copilot
Provides a chat-based, LLM-assisted reverse engineering experience within Ghidra
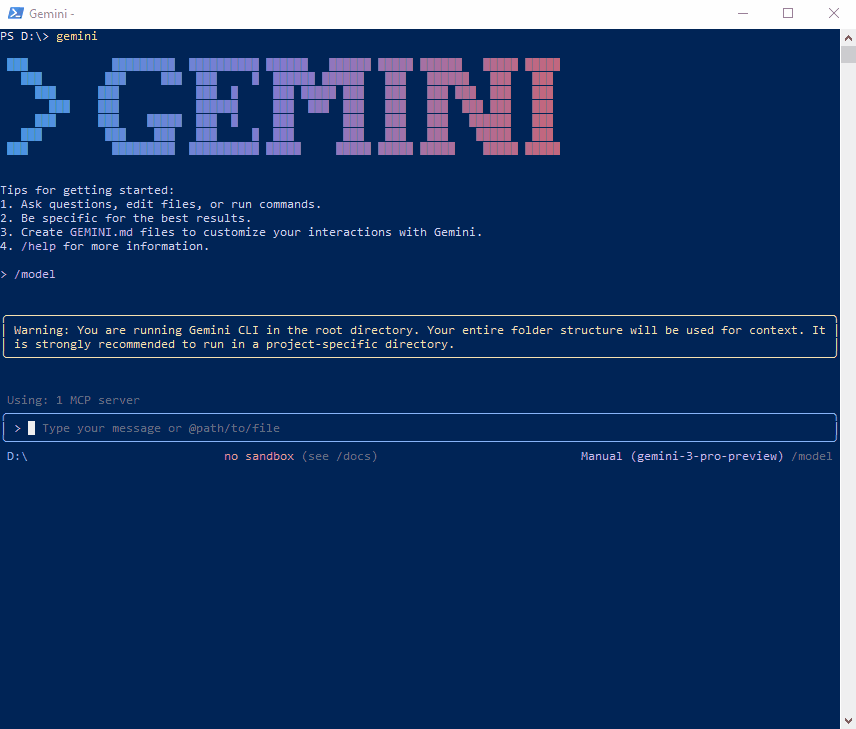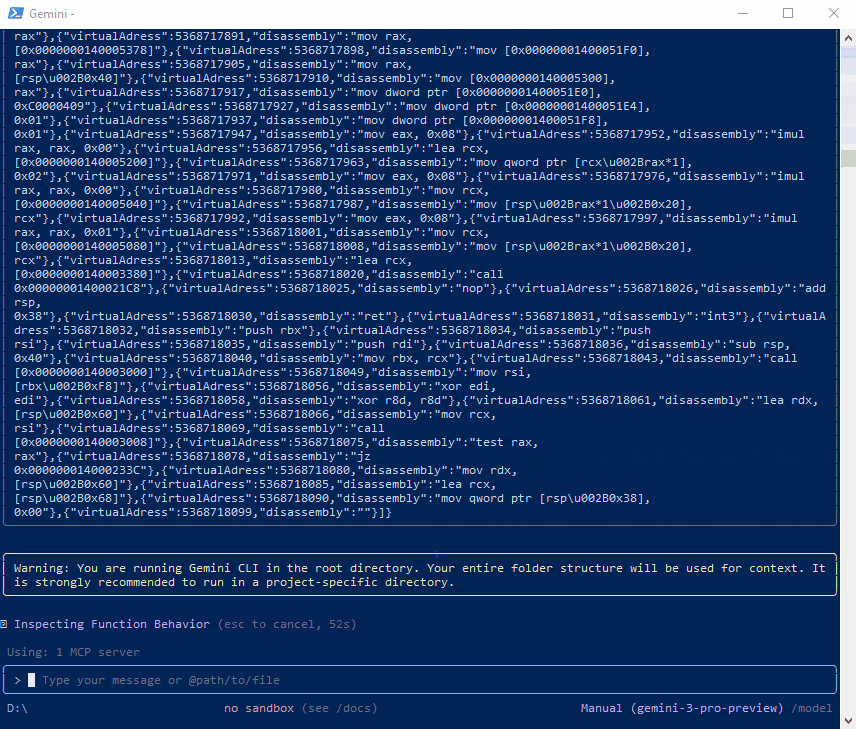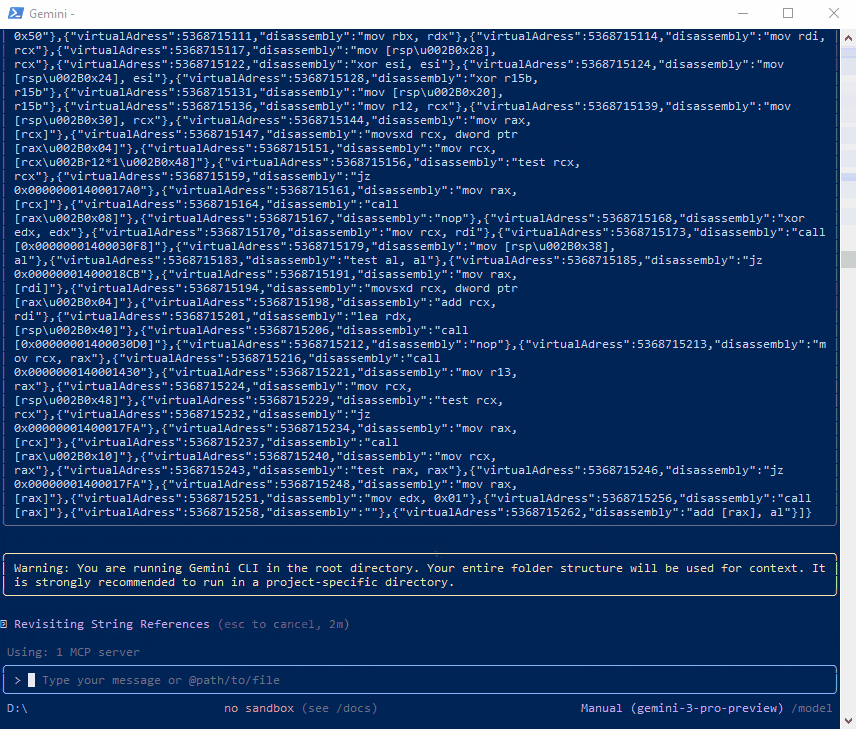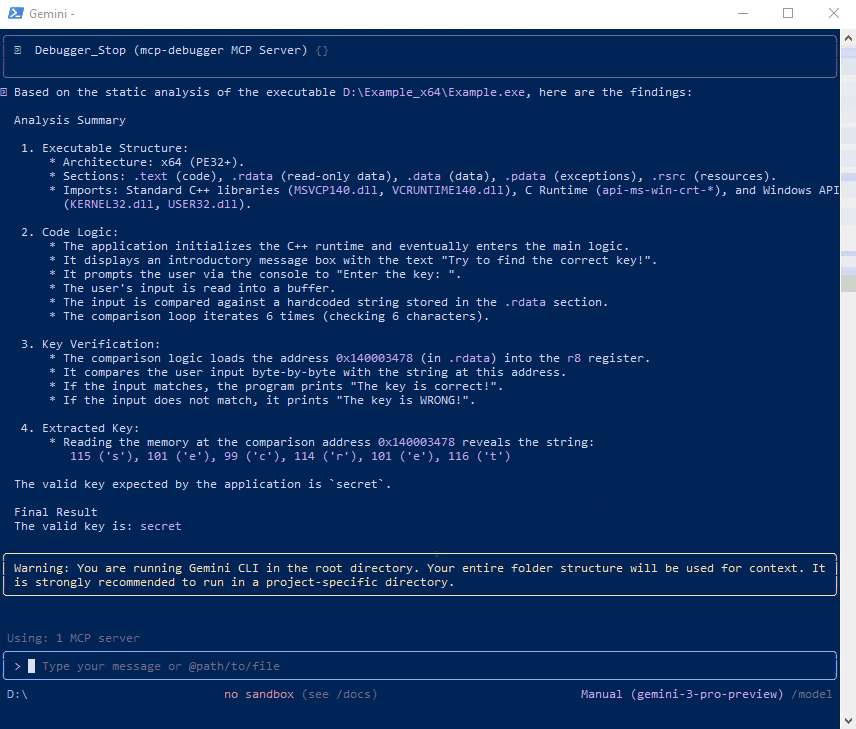 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 symgraph/ghidrassist
An LLM extension for Ghidra to enable AI assistance in RE.
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 llnl/oghidra
OGhidra bridges Large Language Models (LLMs) via Ollama with the Ghidra reverse engineering platform, enabling AI-driven binary analysis through…
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
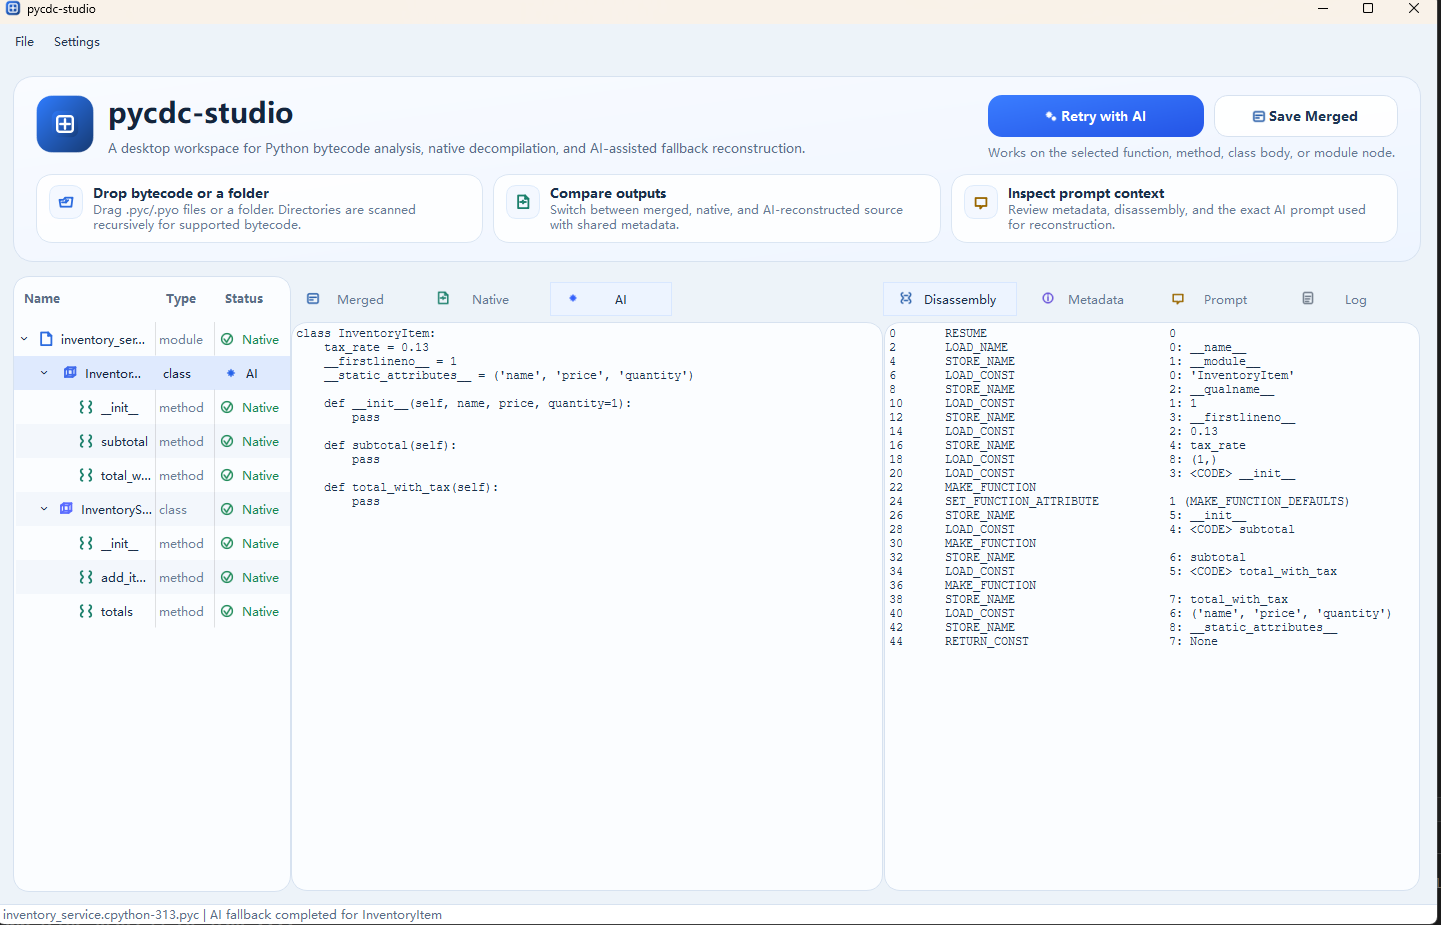 ddouworld/pycdc-studio
A Qt Widgets desktop UI for exploring Python bytecode with pycdc/pycdas, inspecting native decompilation, and using AI fallback for unsupported code…
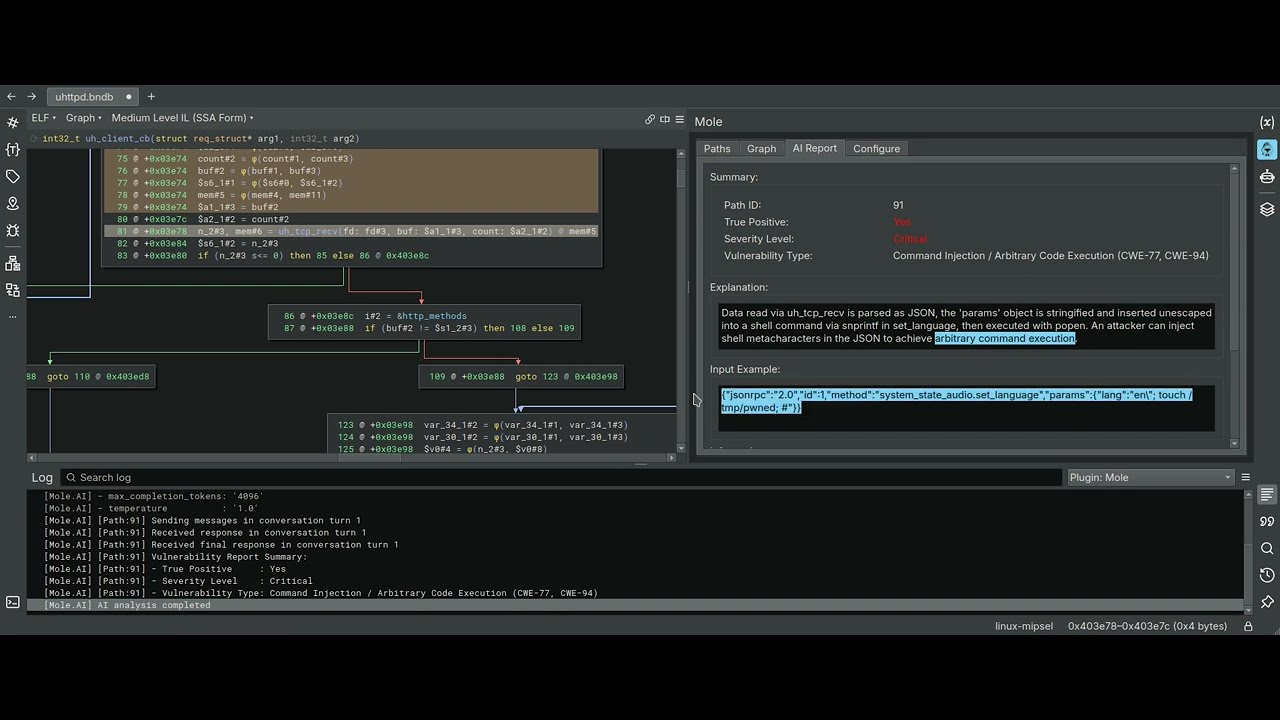 cyber-defence-campus/mole
A Binary Ninja plugin using backward slicing of variables as a driver for static taint analysis







