 #1
AI-powered decompilation, binary analysis, code summarization, and malware analysis tools.
Kitploit recommended
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 morluto/rea
Reverse engineer anything with agents, from app behavior down to native binaries.
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 storytold/craft-anything
Pure-Rust reverse-engineering engine with 314 CLI/MCP inspection tools (disassembly, decompilation, strings, call graphs) that studies any app, site…
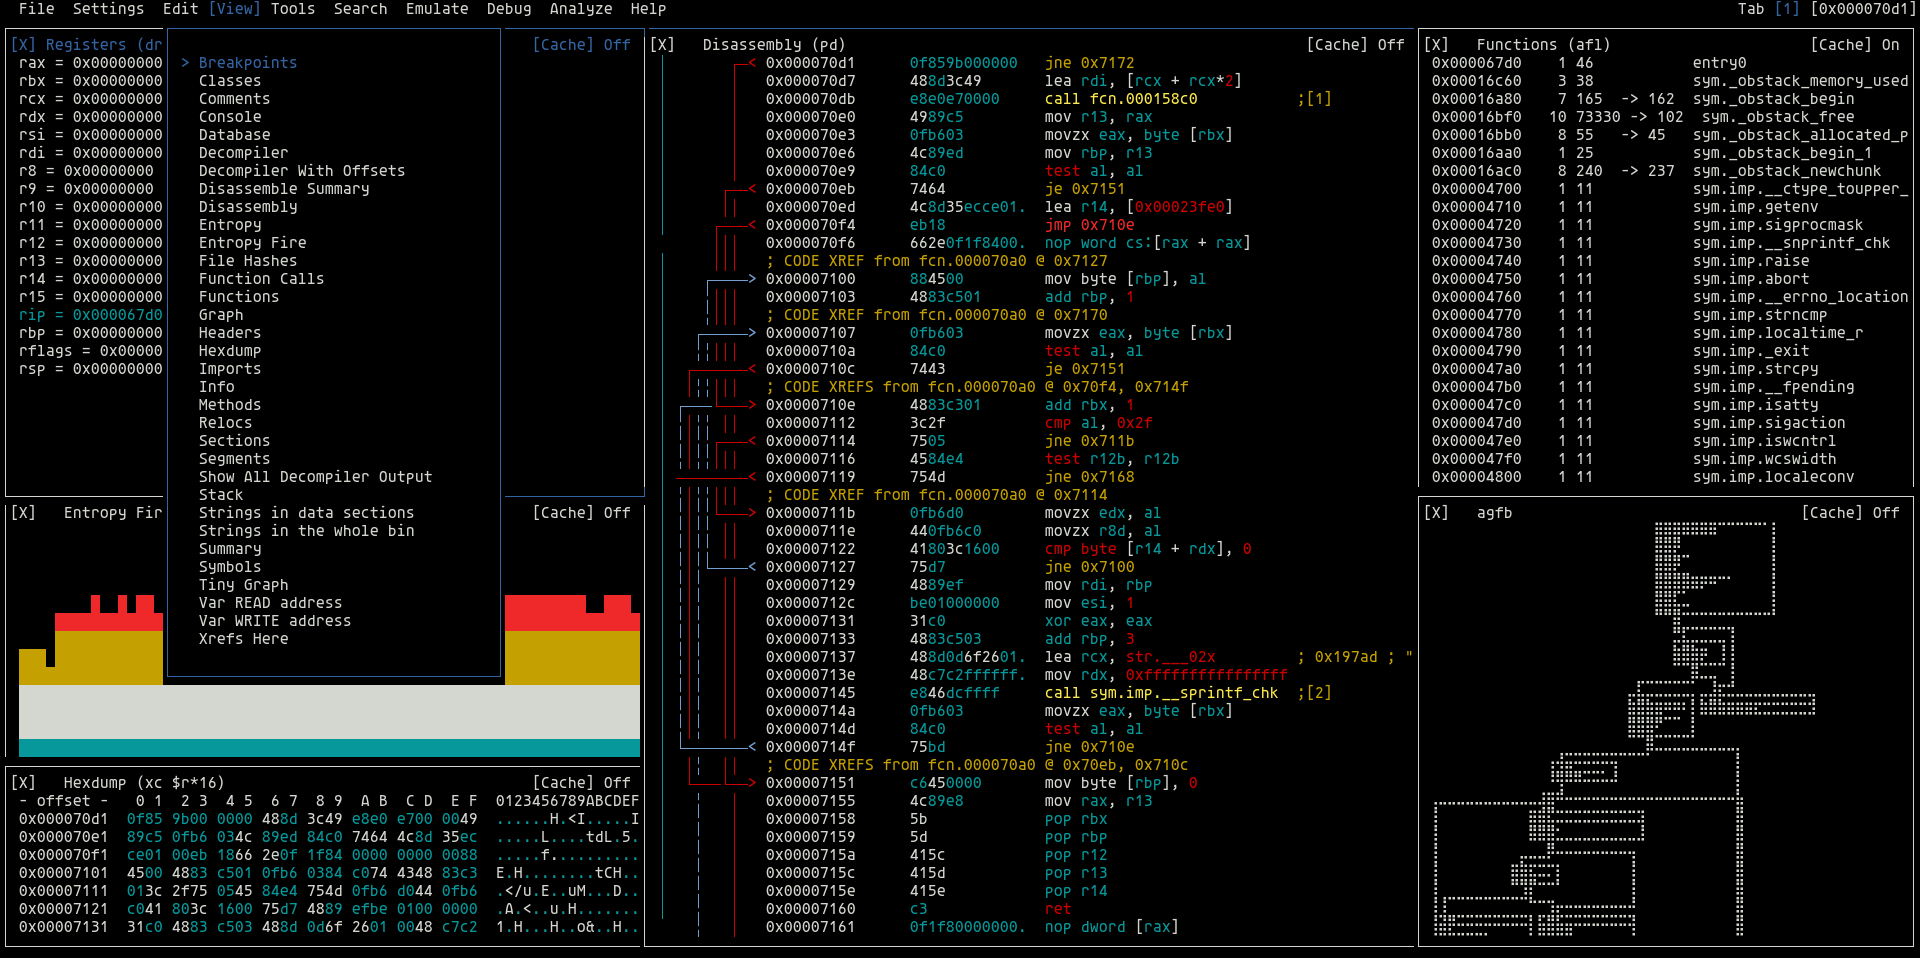 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
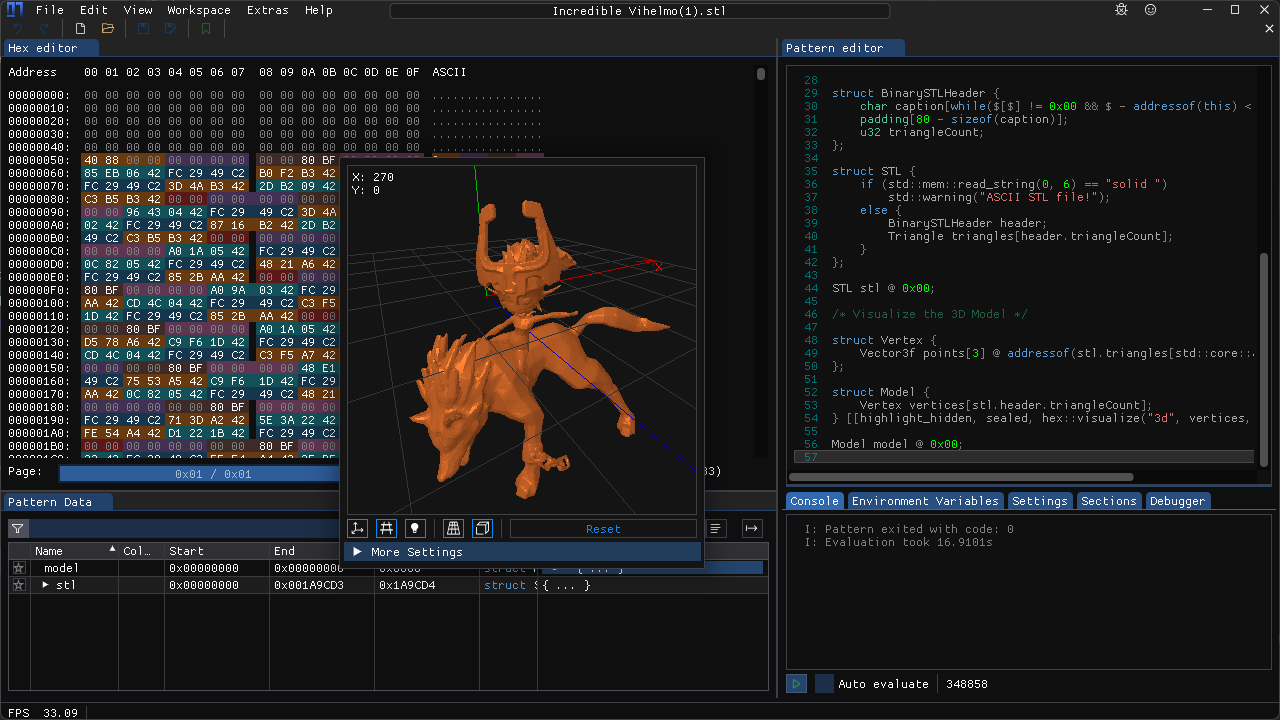 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 rizinorg/cutter
Free and Open Source Reverse Engineering Platform powered by rizin
 trailofbits/skills
Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows
mrexodia/ida-pro-mcpAI-powered reverse engineering assistant that bridges IDA Pro with language models through MCP.
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 angr/angr
A powerful and user-friendly binary analysis platform!
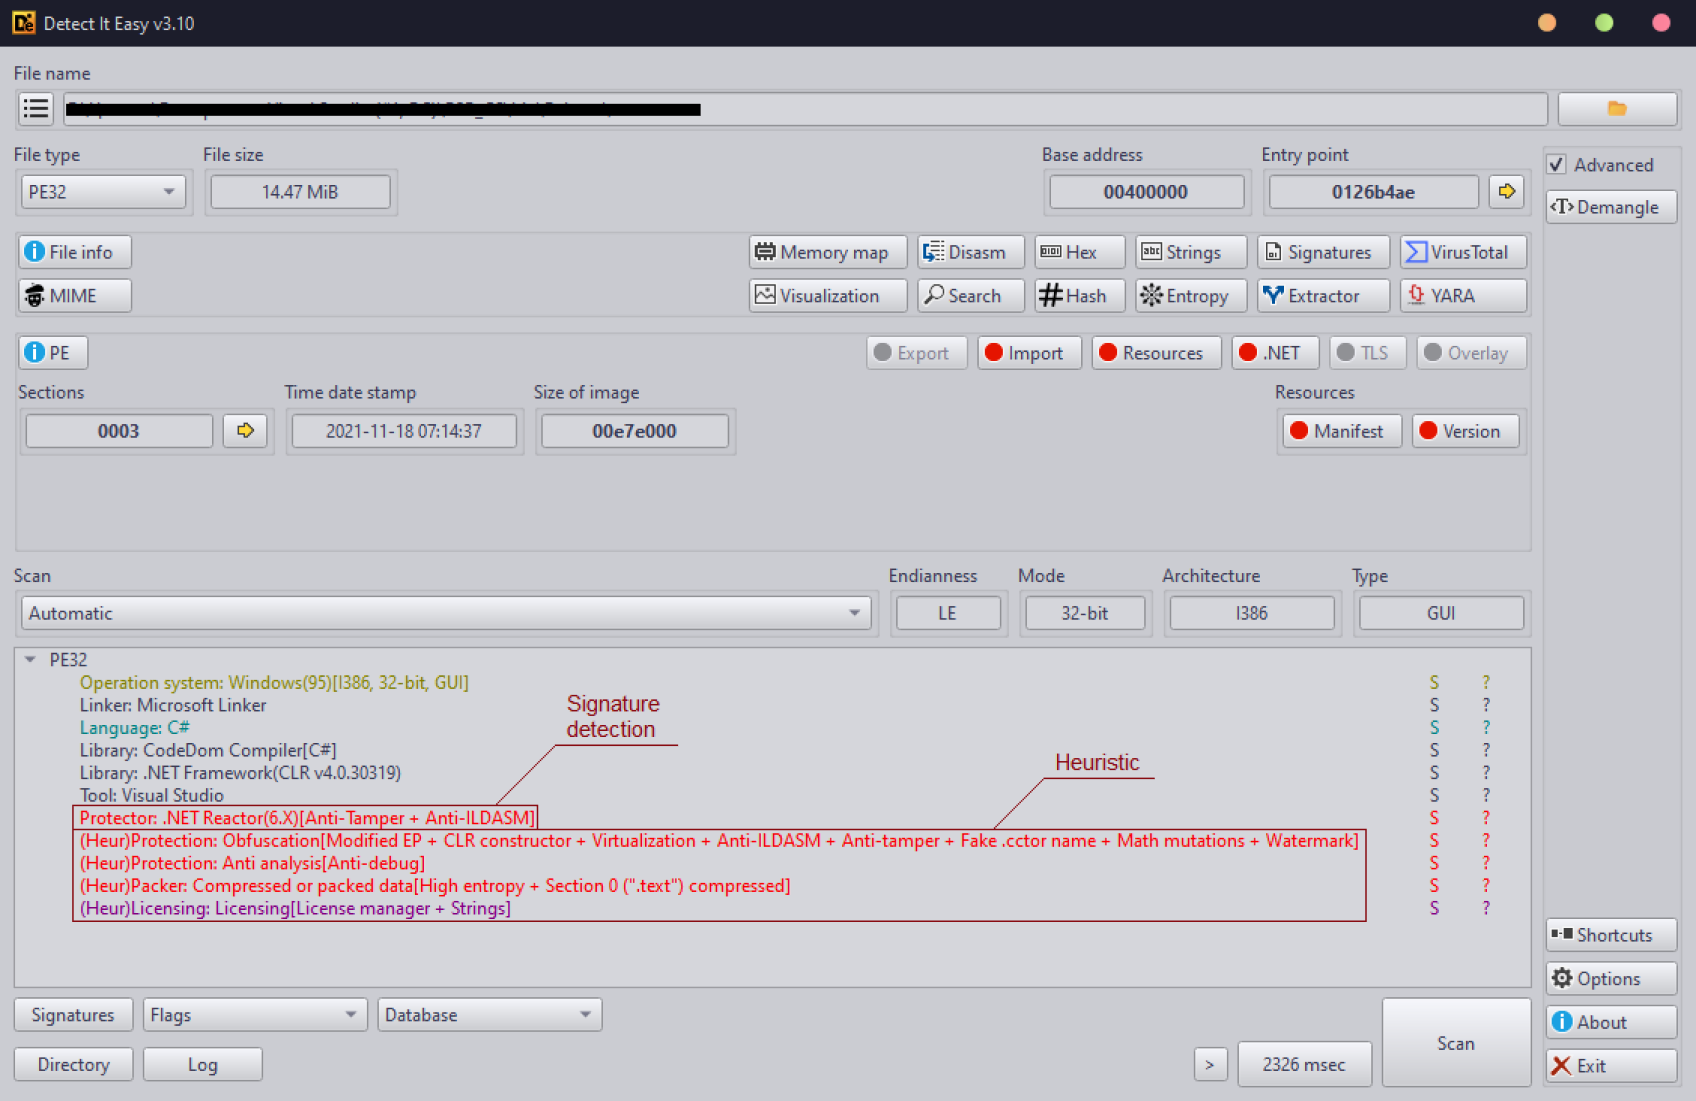 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
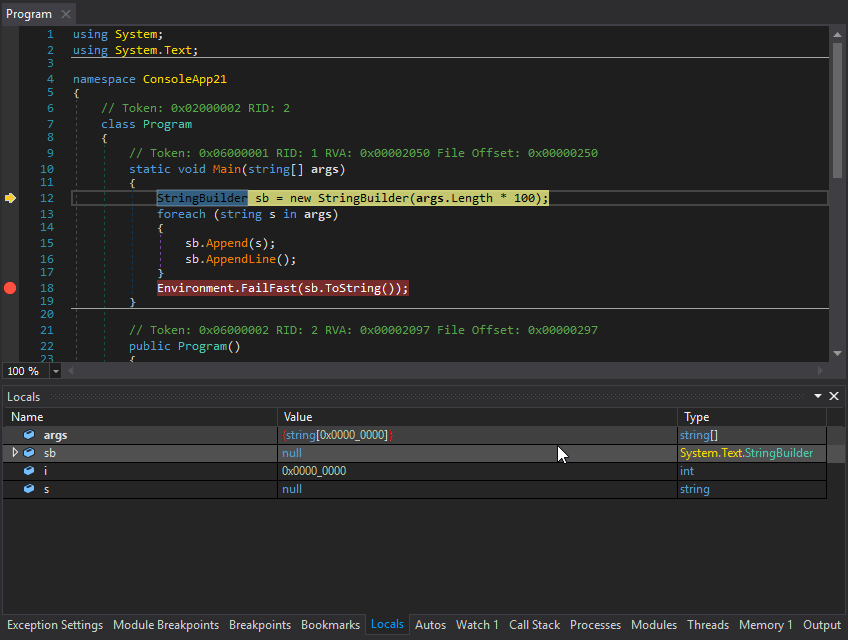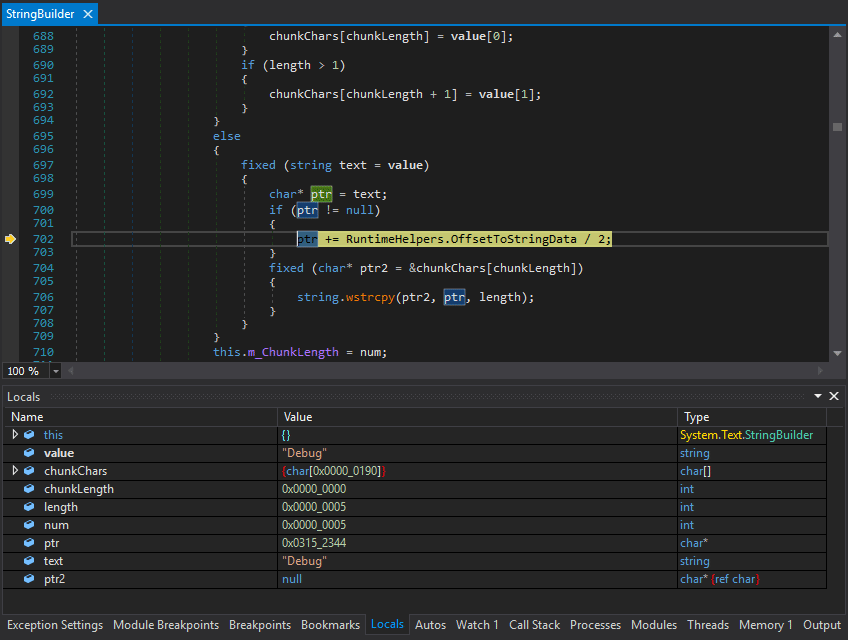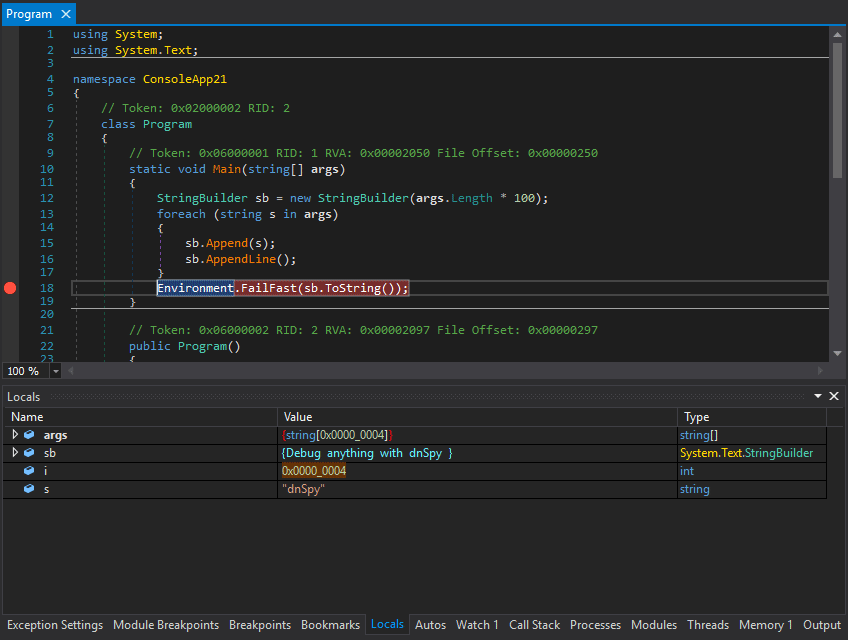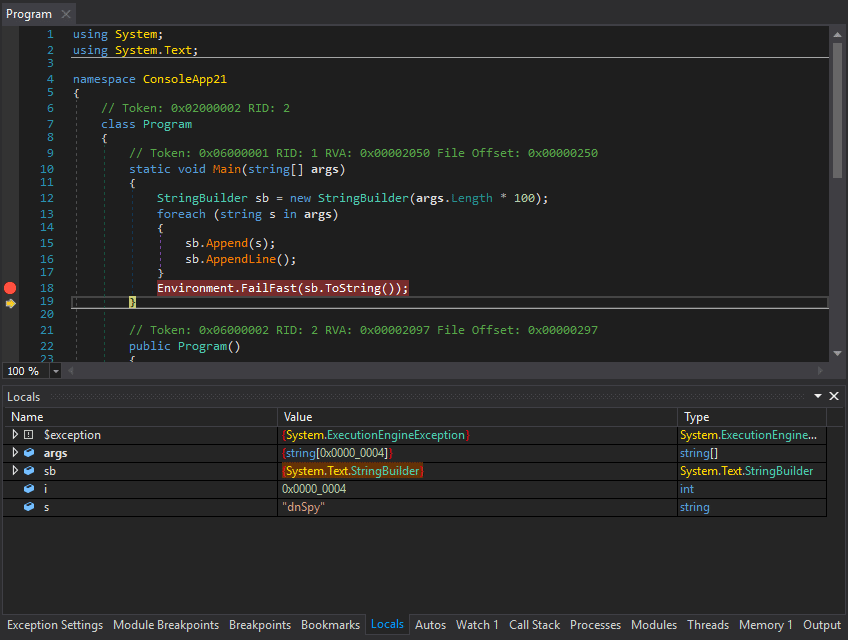 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 lauriewired/ghidramcp
MCP Server for Ghidra
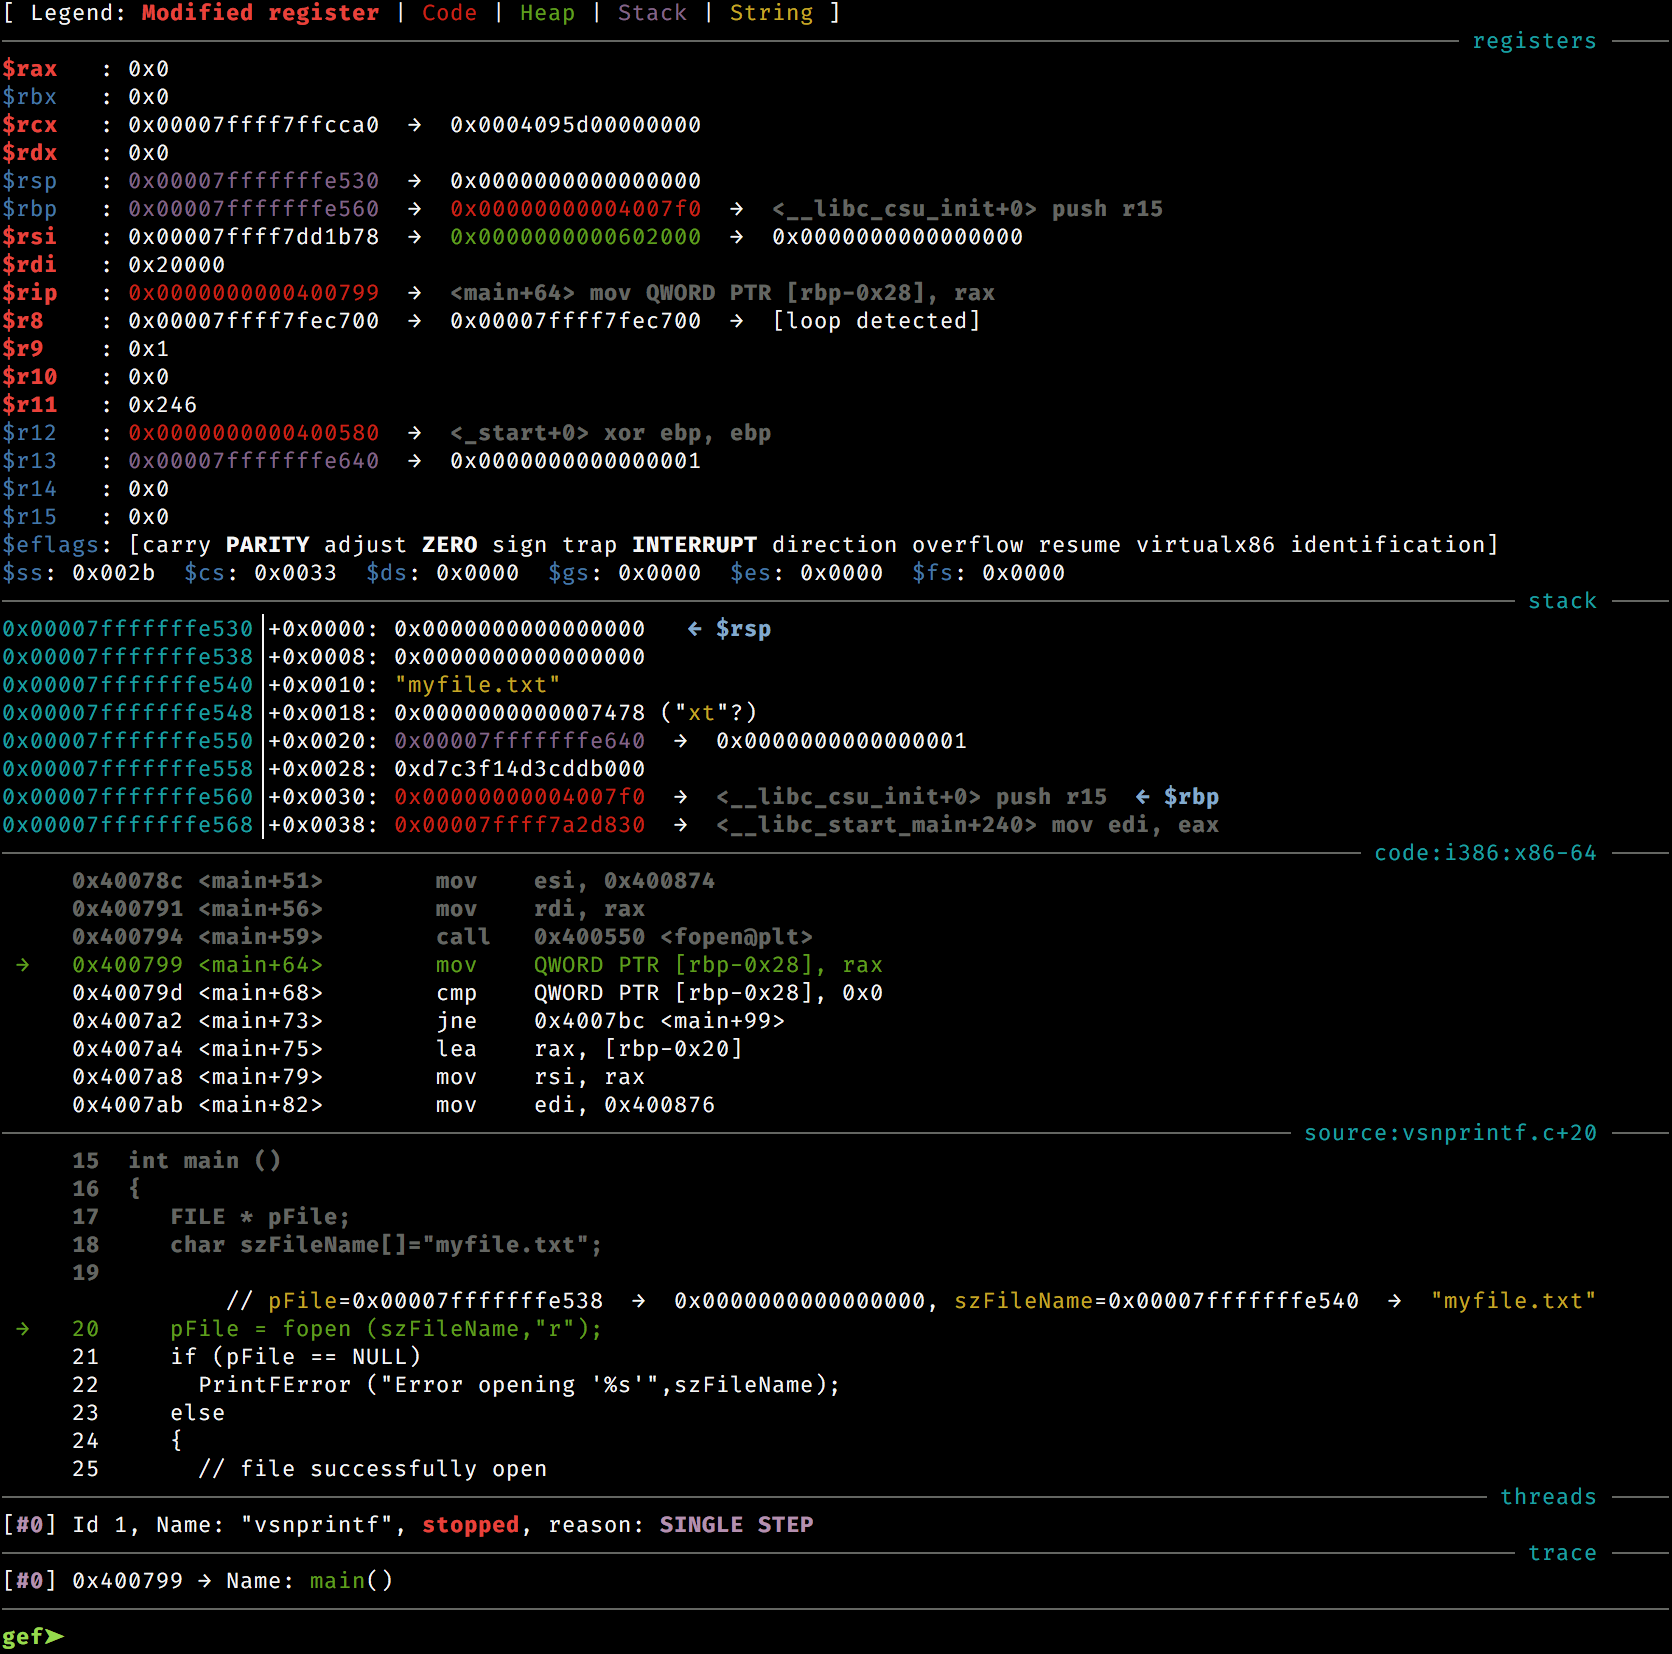 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
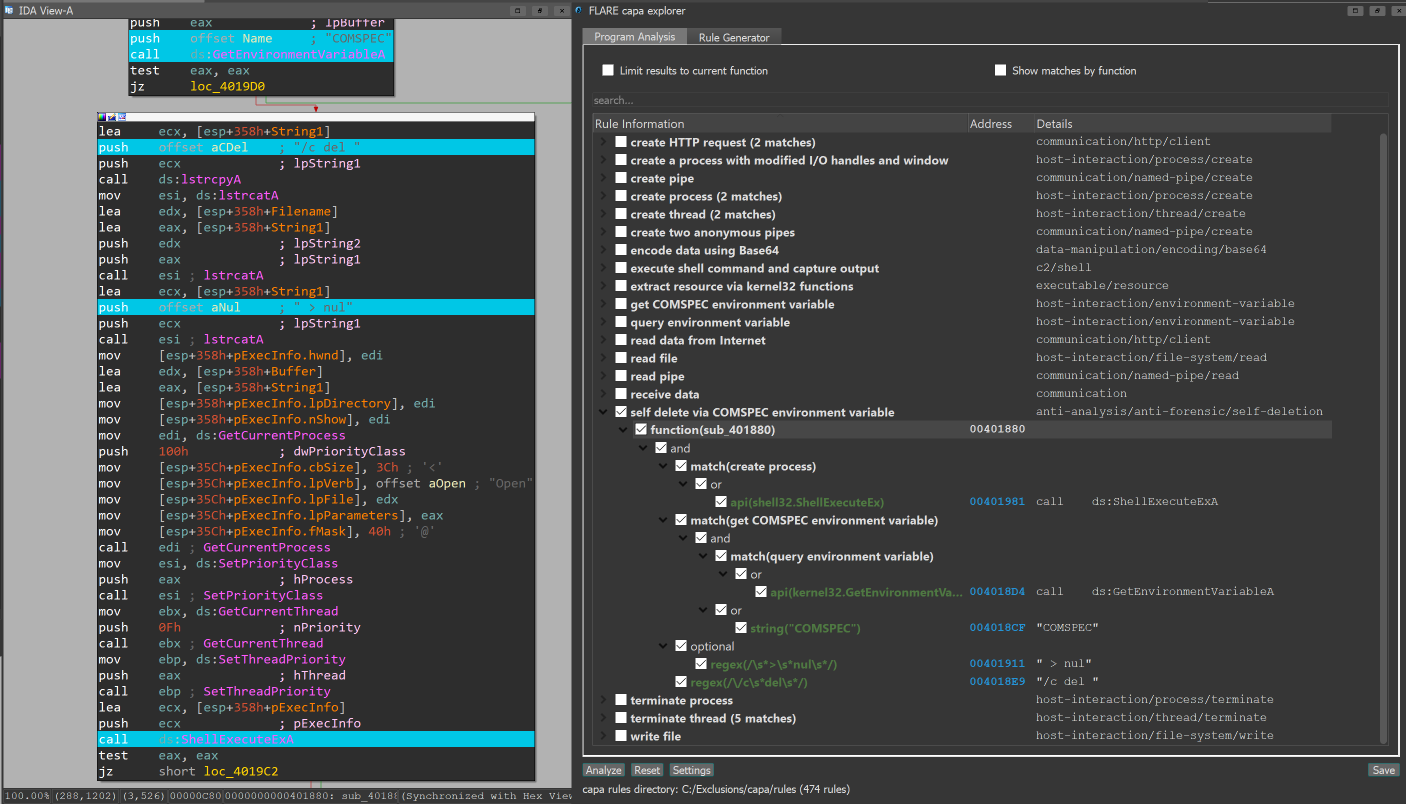 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
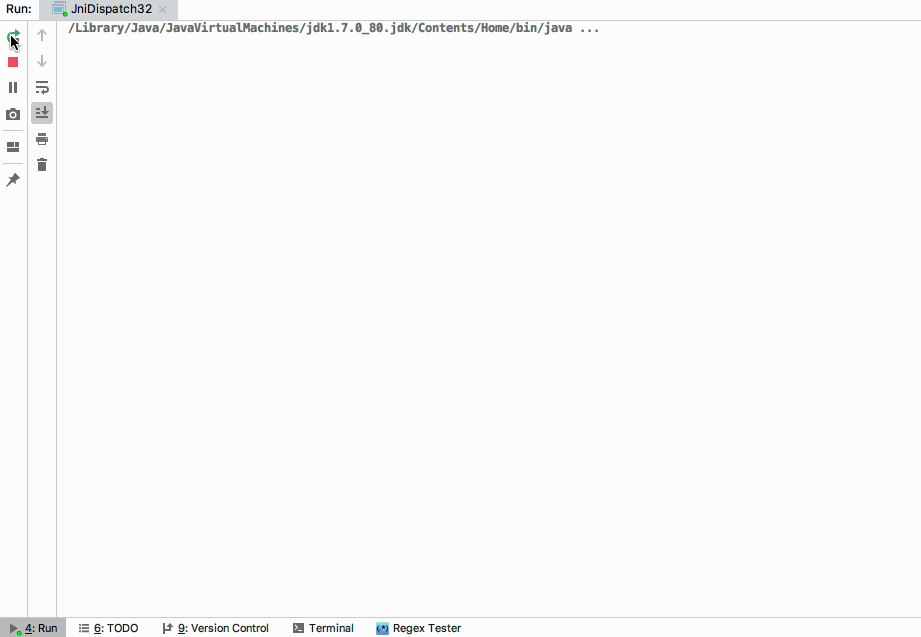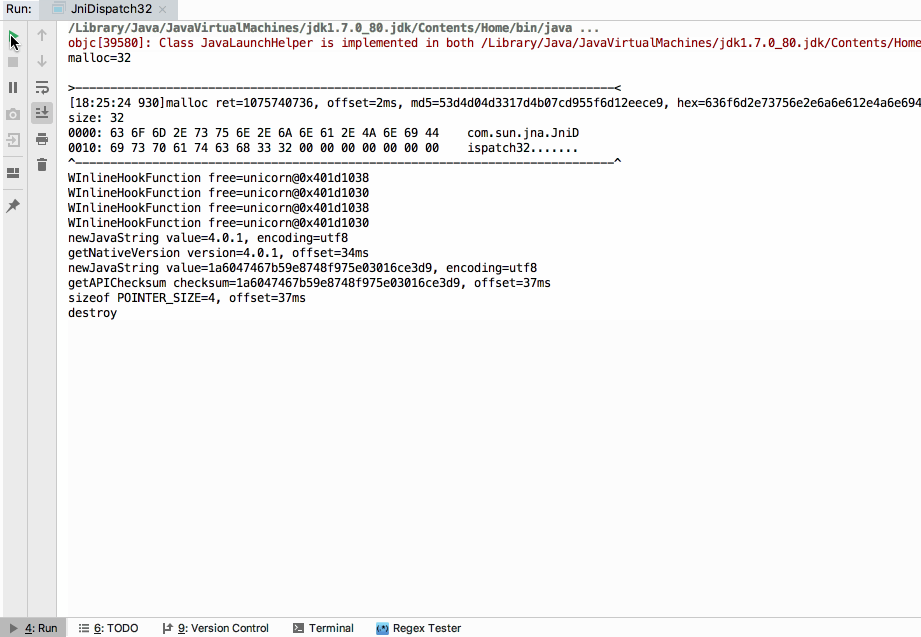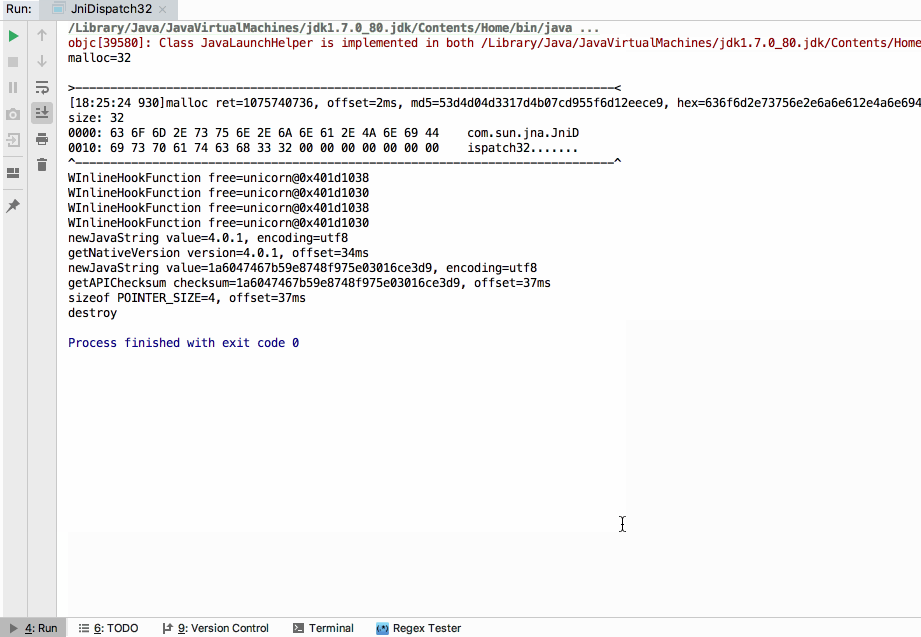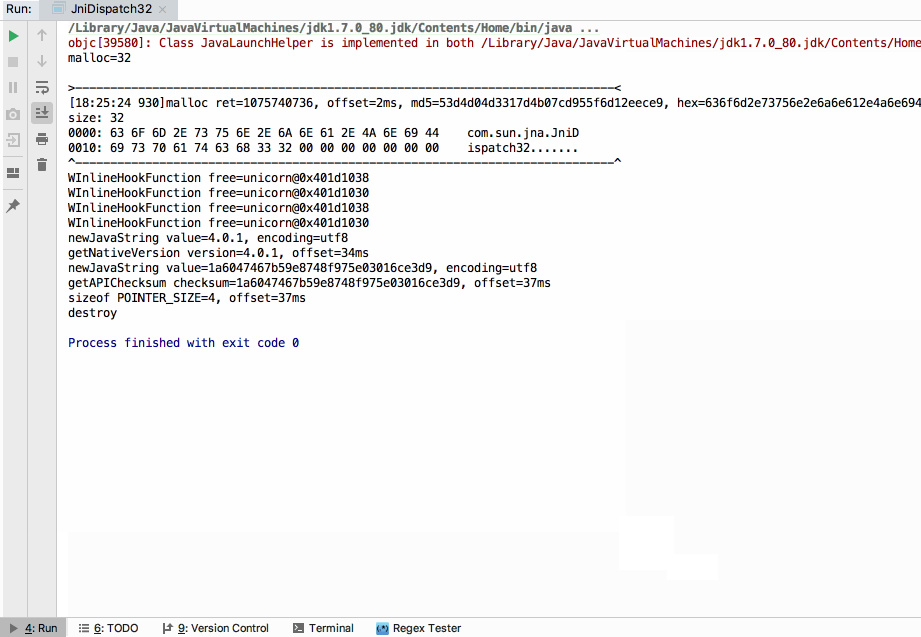 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation