
 #1
AI-powered decompilation, binary analysis, code summarization, and malware analysis tools.
Kitploit recommended

 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 mandiant/flare-floss
FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 blacktop/ipsw
iOS/macOS Research Swiss Army Knife
 zinja-coder/jadx-ai-mcp
Plugin for JADX to integrate MCP server
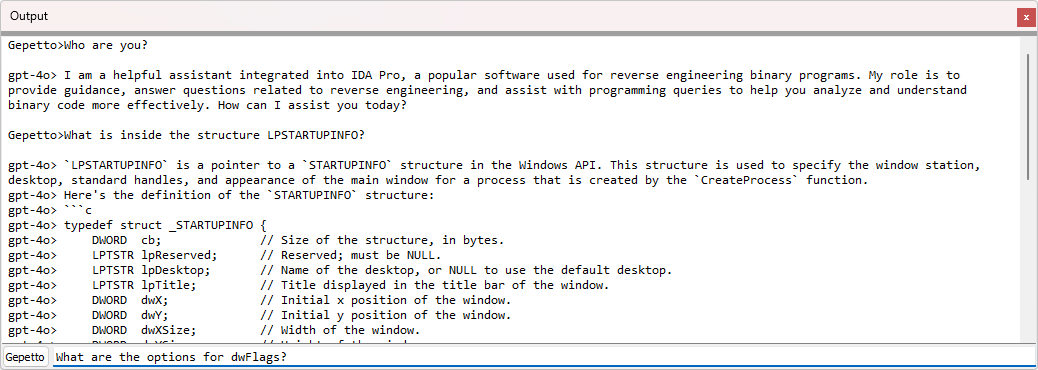 justicerage/gepetto
IDA plugin which queries language models to speed up reverse-engineering
 dryxio/auto-re-agent
Reconstruct and validate C/C++ code from compiled programs with AI.
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
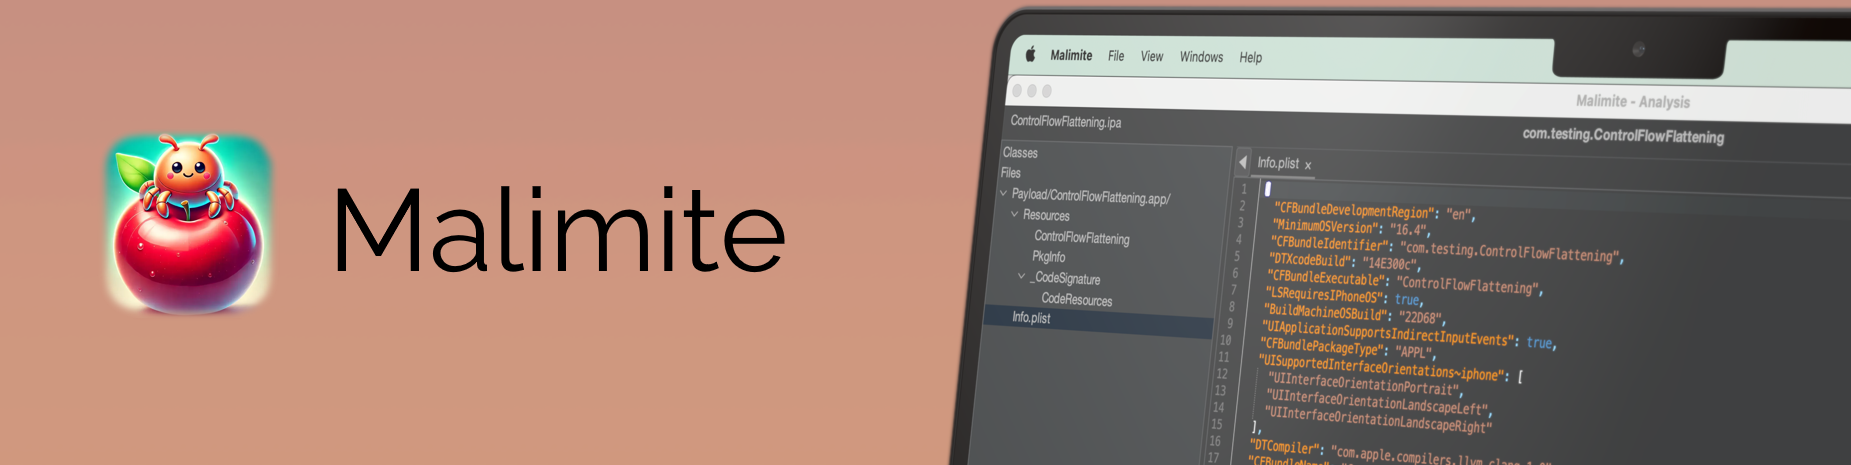 lauriewired/malimite
iOS and macOS Decompiler
 lkimuk/reark
An intelligent reverse engineering and AI-assisted analysis tool for HarmonyOS NEXT (HAP/APP/ABC), Android (APK/AAB), iOS (IPA), and native…
 symgraph/ghidrassist
An LLM extension for Ghidra to enable AI assistance in RE.
 nealbridges/vulnhunter
Agentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…
 fadi002/de4py
The ultimate AI-powered toolkit for python reverse engineering
 vulhunt-re/vulhunt
Vulnerability detection framework by Binarly's REsearch team
 ant4g0nist/lisa.py
LLDB MCP Integration + other helpful commands






