Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Einreichen
ToolsExploitsBlog
Einreichen

Hacking-, PenTest- und Cybersicherheits-Tools für Ihr Sicherheitsarsenal!

Kitploit ist ein Verzeichnis von Hacking-, Cybersicherheits- und Pentesting-Tools. Entdecken Sie die neuesten Projekt-Updates, um Schwachstellen zu finden, Systeme zu analysieren, Tests zu automatisieren und Ihre Sicherheit zu stärken.

FeedsKontaktDatenschutz© 2026 Kitploit

Tool-Verzeichnis

Kategorien

Alle Kategorien anzeigen
Loading categories
cyberbro — A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services. | Kitploit
Tools/GitHubGitHub/stanfrbd/cyberbro
Defensive ToolsIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Threat Feeds & AggregatorsVulnerability AnalysisHash AnalysisForensicsInformation GatheringThreat IntelligenceLearning & EducationIncident ResponseDNS Analysis
6777162vor 7h 21mVon Kitploit geprüft
GitHubstanfrbd/cyberbro

cyberbro

A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.
Repository anzeigenWebseite
Teilen
Inhalt in der angeforderten Sprache nicht verfügbar. Englische Version wird angezeigt.

Cyberbro


A simple application that extracts your IoCs from garbage input and checks their reputation using multiple services.
🌐 demo.cyberbro.net

GitHub stars Follow on X/Twitter Mastodon GitHub issues License build and test badge pre-commit validation badge Python


About

Inspired by Cybergordon and IntelOwl.

This project aims to provide a simple and efficient way to check the reputation of your observables using multiple services, without having to deploy a complex solution. Read the docs at https://docs.cyberbro.net/

[!TIP] To build custom reports, use Cyberbro with your favorite LLM (Claude, OpenAI gpt-5...) via MCP (Model Context Protocol)
Checkout Cyberbro MCP for more information.
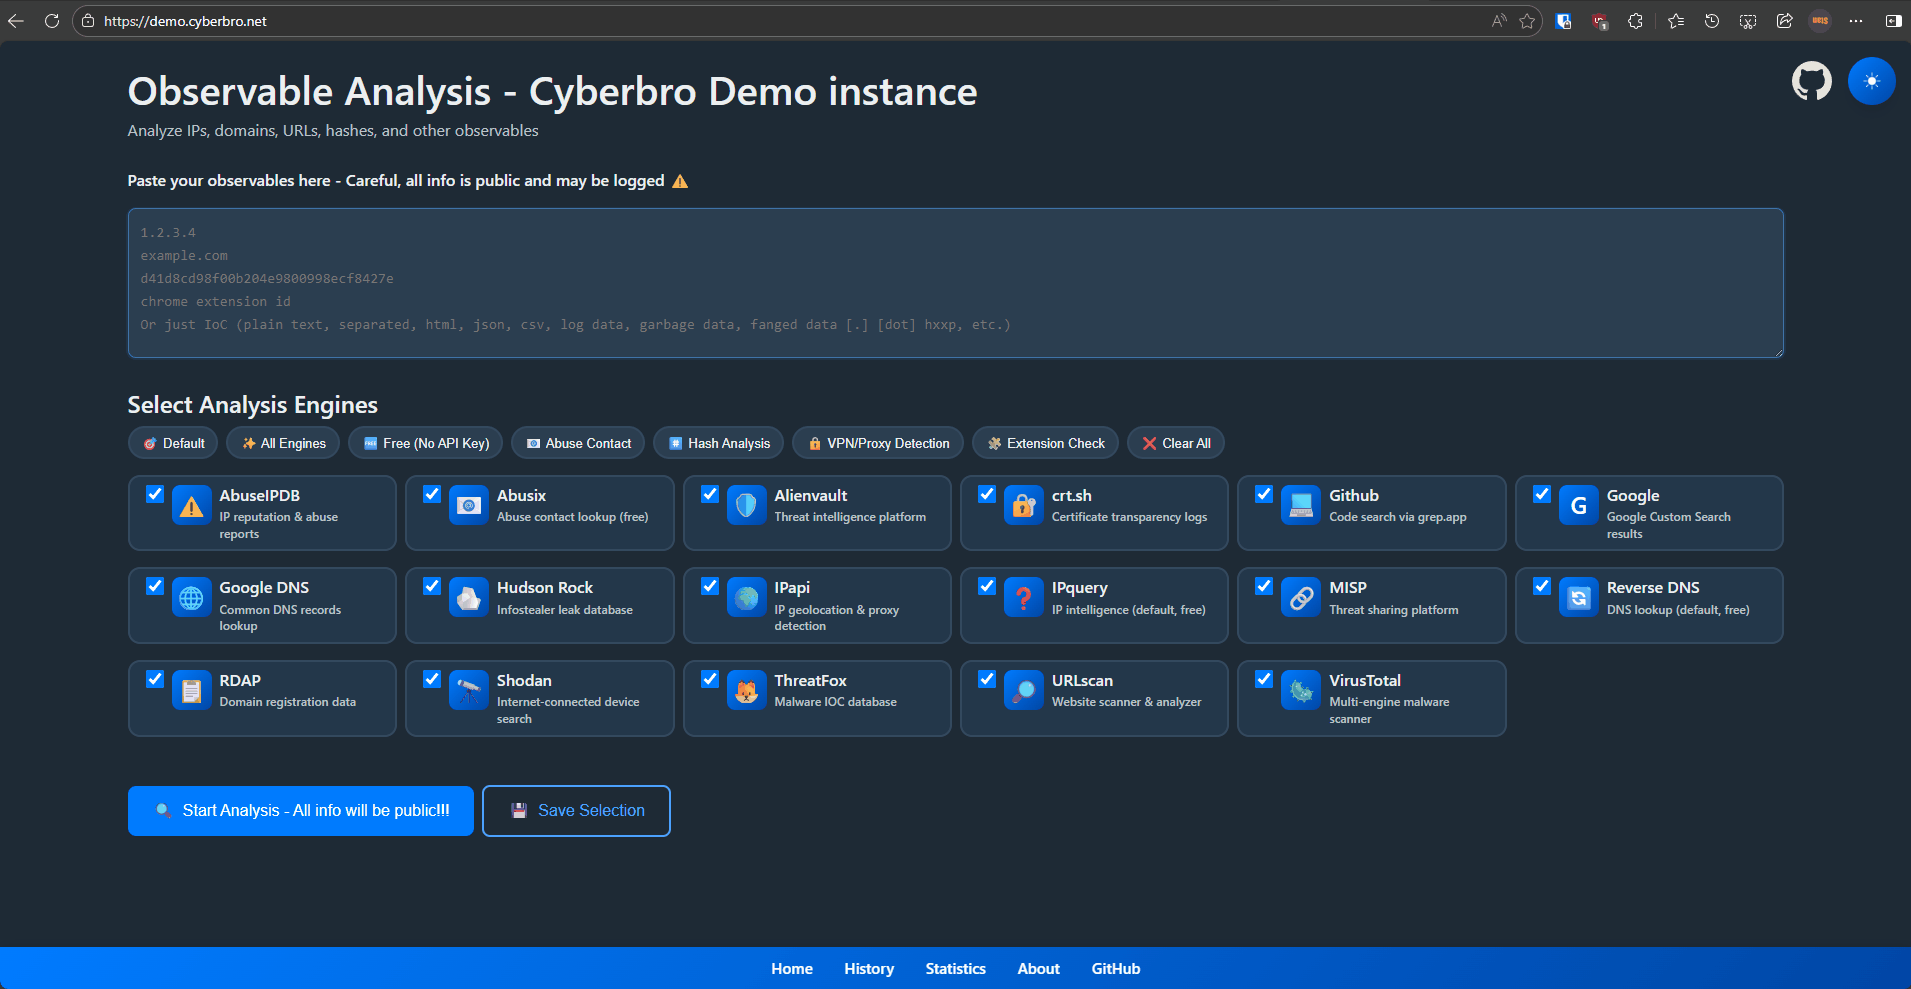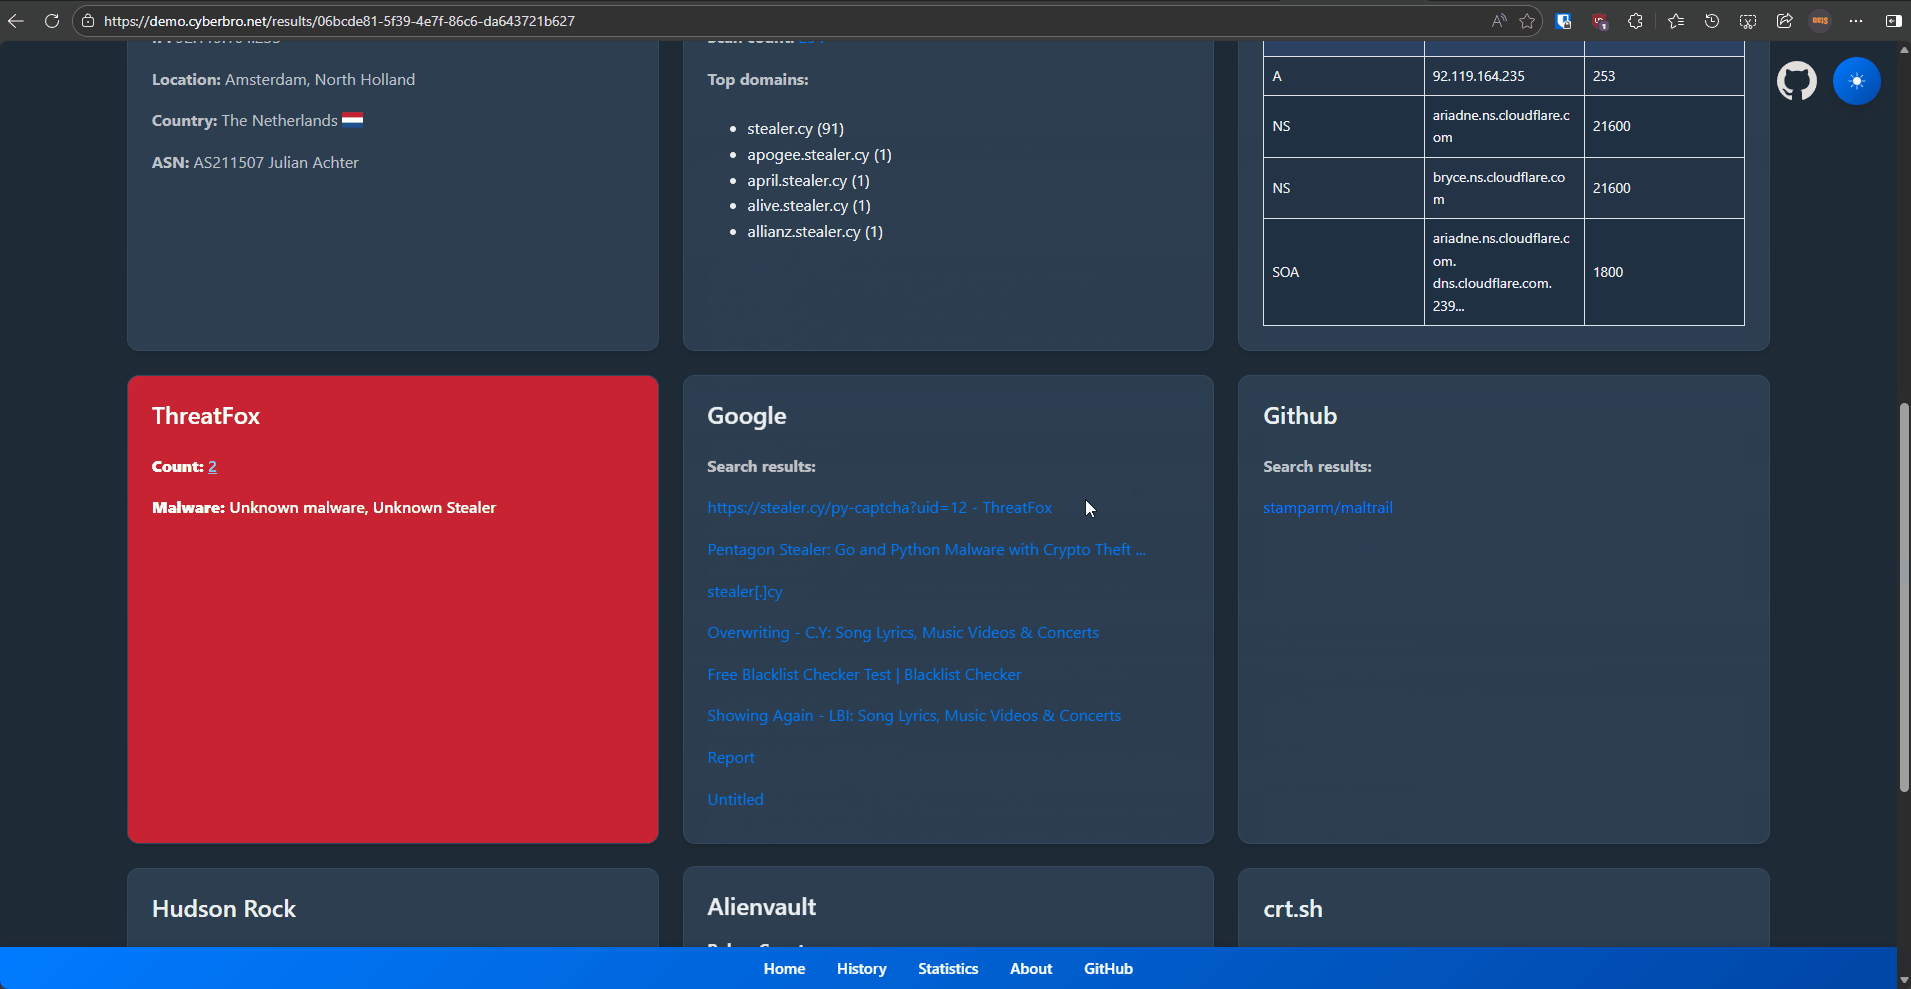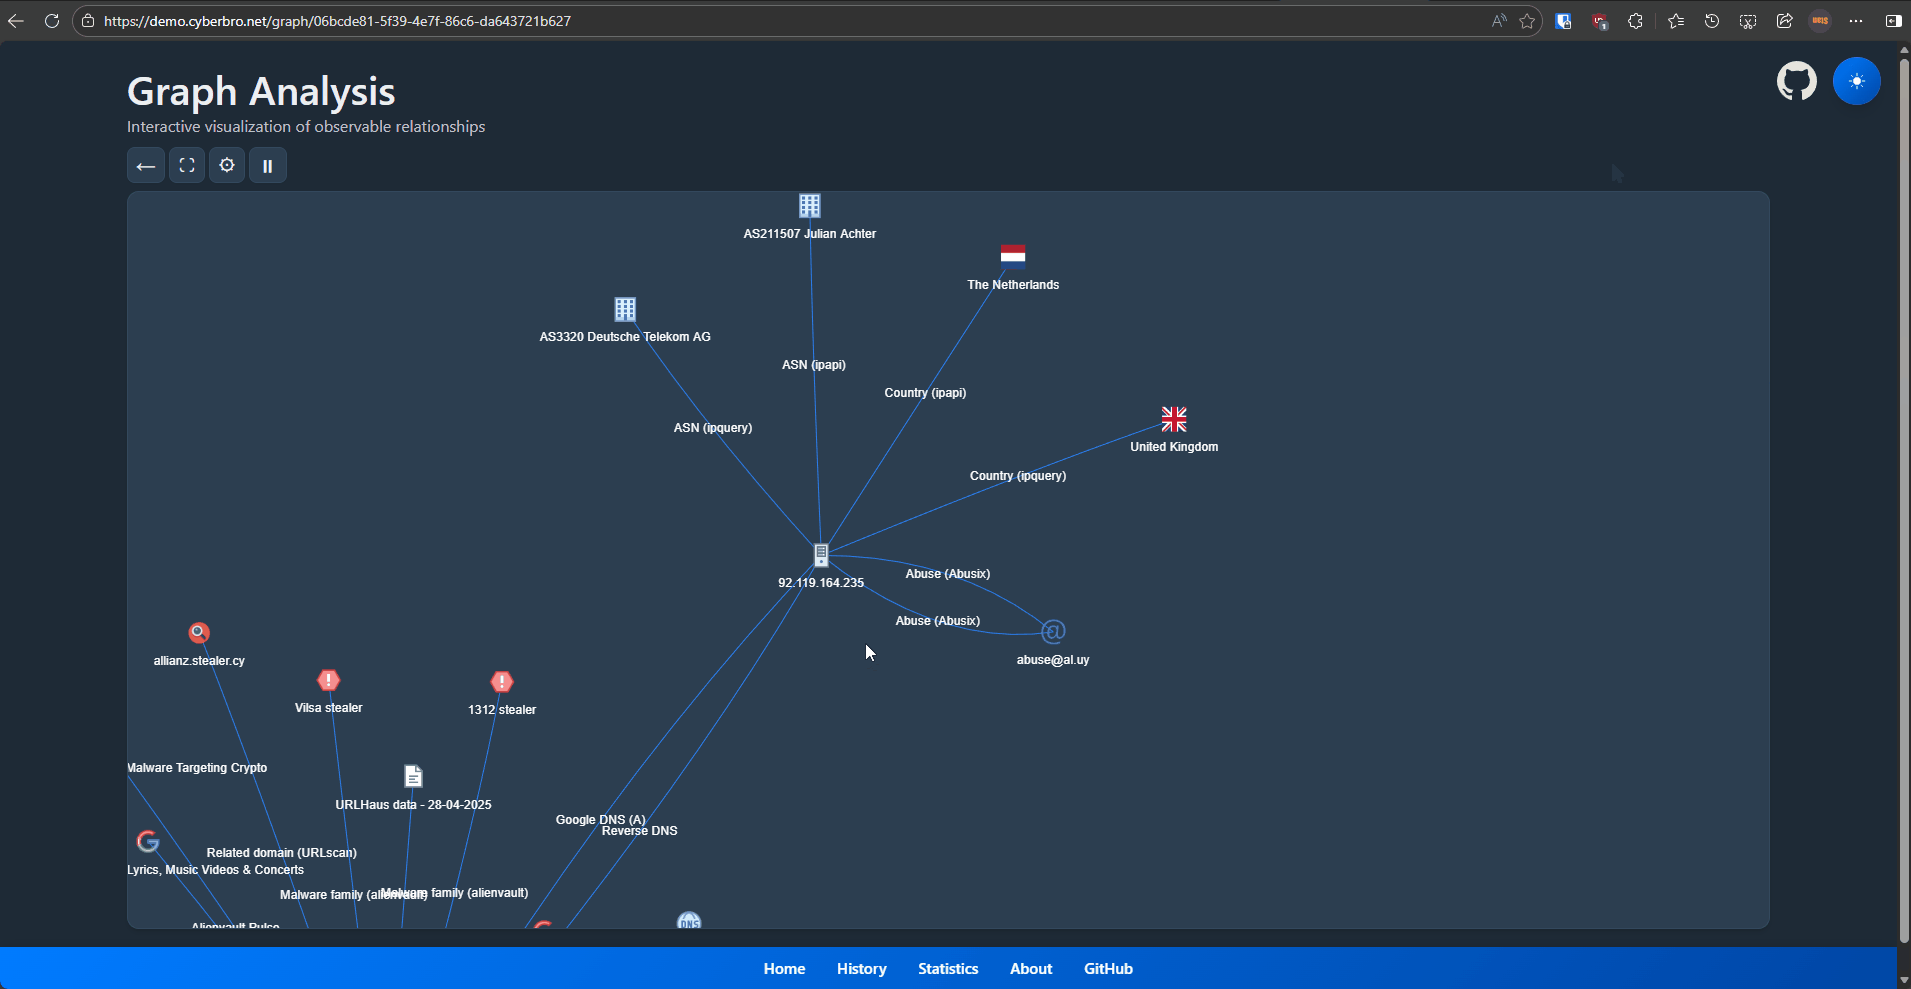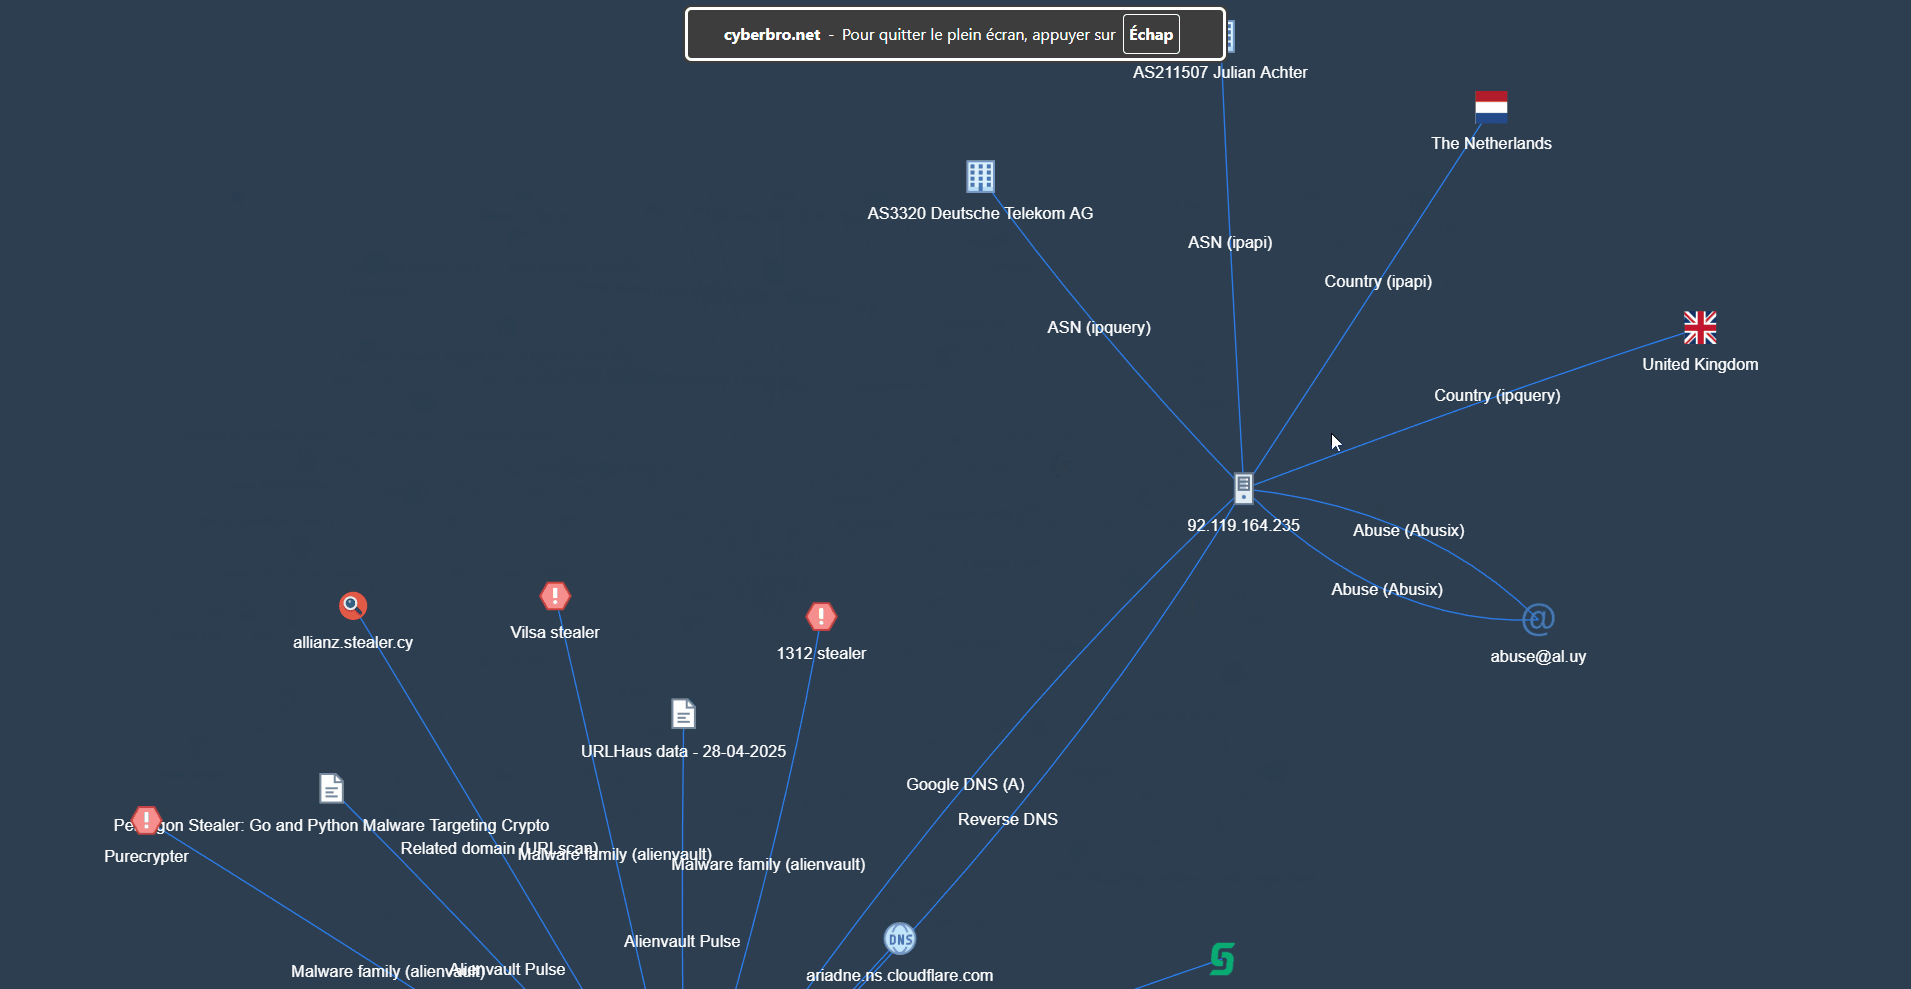
Demo

graph_demo

Features

  • Easy Input: Paste raw logs or IoCs-automatic parsing and extraction.
  • Multi-Service Checks: Reputation lookup for IPs, hashes, domains, URLs, and Chrome extension IDs across many threat intel services.
  • Comprehensive Reports: Advanced search, filtering, and export to CSV/Excel.
  • Fast Processing: Multithreaded for speed.
  • Automated Pivoting: Discover related domains, URLs, and IPs via reverse DNS and RDAP / Whois.
  • Accurate Domain & Abuse Info: RDAP / Whois and abuse contact lookups.
  • Integrations: Microsoft Defender for Endpoint, CrowdStrike, OpenCTI, Grep.App, Hudson Rock, and more.
  • Proxy & Storage: Proxy support and results stored in SQLite.
  • History & Graphs: Analysis history and experimental graph view.
  • Cache: Caching for faster repeat lookups (enabled at multi-engines level, not each engine).

What Makes Cyberbro Unique

  • Beginner-Friendly: Accessible for all skill levels.
  • Chrome Extension ID Lookup: Get extension names and CTI data from IDs.
  • Lightweight Deployment: Simple setup and use.
  • Advanced TLD Extraction: Accurate root domain detection for better lookups.
  • Pragmatic Data Gathering: Uses GitHub and Google to find overlooked IoCs.
  • CTI Report Integration: Fetches IoC-related reports from IoC.One.
  • EDR Integration: Checks observables against your own security tools (MDE, CrowdStrike).

Security and access control

[!WARNING] Cyberbro does not provide built-in authentication or authorization. This is an intentional design choice, and native authentication is not currently planned. Anyone who can reach the application may be able to launch analyses, access analysis history and results, and consume configured third-party API quotas. Do not expose Cyberbro directly to untrusted networks or the public Internet without external access controls.

For shared or remotely accessible deployments, protect all application routes (including API, history, results, and exports) using an established solution such as Cloudflare Access, an authentication-enabled reverse proxy, or a VPN. Restrict network access with firewall rules or IP allowlists where appropriate. A reverse proxy or WAF alone does not provide authentication.

Cyberbro is intended to remain a lightweight IOC enrichment tool rather than a multi-user threat intelligence platform. If you need integrated authentication and user management, consider a more comprehensive project such as IntelOwl.

See SECURITY.md for deployment expectations and vulnerability reporting.

Getting Started - TL;DR

[!TIP] If you are lazy, you need Docker.
Do a git clone ; copy .env.sample to .env ; docker compose up then go to localhost:5000. Yep, that's it!

Getting Started

  • To get started, clone the repository
git clone https://github.com/stanfrbd/cyberbro
cd cyberbro

Edit the config file (mandatory)

cp .env.sample .env

[!NOTE] Don't have API keys? No problem, just copy .env.sample to .env and leave optional values empty. Be careful if a proxy is used.
You will be able to use all free engines!

  • Fill values (including proxy if needed) in the .env file.

[!WARNING] .env contains sensitive secrets and must never be committed. For production/team deployments, use SOPS, Vault, or an equivalent secret manager workflow.

ABUSEIPDB=token_here
ALIENVAULT=token_here
CRIMINALIP_API_KEY=token_here
CROWDSTRIKE_CLIENT_ID=client_id_here
CROWDSTRIKE_CLIENT_SECRET=client_secret_here
DFIR_IRIS_API_KEY=token_here
DFIR_IRIS_URL=https://dfir-iris.local
DFIR_IRIS_SEARCH_NOTES=false
GOOGLE_CSE_CX=cx_here
GOOGLE_CSE_KEY=key_here
GOOGLE_CSE_URL=https://www.googleapis.com/customsearch/v1
GOOGLE_SAFE_BROWSING=token_here
HISTER_TOKEN=token_here
HISTER_BASE_URL=https://hister.example.com
IPAPI=token_here
IPINFO=token_here
MDE_CLIENT_ID=client_id_here
MDE_CLIENT_SECRET=client_secret_here
MDE_TENANT_ID=tenant_here
MISP_API_KEY=token_here
MISP_URL=https://misp.local
MISP_FEEDBACK_SERVER_URL=https://misp-feedback.local
MISP_FEEDBACK_TOKEN=token_here
OPENCTI_API_KEY=token_here
OPENCTI_URL=https://demo.opencti.io
PROXY_URL=
RANSOMWARE_LIVE_API_KEY=token_here
RL_ANALYZE_API_KEY=token_here
RL_ANALYZE_URL=https://spectra_analyse_url_here
ROSTI_API_KEY=token_here
SHODAN=token_here
SPUR_US=token_here
THREATFOX=token_here
VIRUSTOTAL=token_here
WEBSCOUT=token_here

[!IMPORTANT] Starting with version v0.13.0, Cyberbro no longer supports secrets.json and the /config page. Cf. discussion 165.
If you already have a legacy secrets.json, convert it to .env with: python3 scripts/secrets_json_to_env.py

See Advanced options for deployment in the docs.

Launch the app

Lazy and easy - use docker

[!WARNING] Make sure you install the compose plugin as docker compose and not docker-compose. In Docker, the app binds to 0.0.0.0 inside the container even if your local .env sets FLASK_HOST=127.0.0.1.

docker compose up # use -d to run in background and use --build to rebuild the image

Tool herunterladen

Beliebteste

Alle anzeigen →

Entdecken Sie die meistgenutzten Tools unserer Community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 Das ultimative OSINT-Toolkit: Untersuchungsgraph, Konfidenzbewertung, Alias-Familien, Karte, Zeitleiste und Berichte. 49 Module, 400+ Websites, keine API-Schlüssel erforderlich.

    668
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    496
  • 3

    ARTEX

    baarai/artex

    LLM-basierte Multi-Agenten-Plattform für autonome Penetrationstests mit Planer-/Worker-Agenten, Asset- und Explorationsgraphen, MITM-Verkehrsaufzeichnung und Schwachstellen-Retesting.

    394
  • 4

    redforge

    cybersecurity91/redforge

    Browser-seitiges Red-Team-Toolkit mit 102 Offline-Tools für Recon, Payload-Generierung, Credential-Angriffe, Krypto, Encoding und Engagement-Reporting.

    339
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    Das System der Handlung für KI-native Cybersicherheit – wo Absicht zu gesteuerter Ausführung wird, Beweise zu operativem Gedächtnis werden und jeder Einsatz den nächsten verbessert.

    258
  • 6

    antifox

    antifox-ai/antifox

    KI-Multi-Agenten-Plattform für autonome Penetrationstests, die Recon, Angriffsflächen-Erkennung, Exploit-Validierung und evidenzbasierte Berichtserstellung durchführt.

    254

Alle Tools erkunden

Durchsuchen Sie unsere Tool-Sammlung

Alle Tools anzeigen →