
 #1
Tools zur Erkennung von Netzwerktopologien, Geräten und Diensten.
Kitploit empfohlen
 pybluez/pybluez
Python-Erweiterungsmodul für den Bluetooth-Zugriff: Geräteabfrage, SDP-Dienstbrowsing, RFCOMM/L2CAP-Sockets sowie experimentelles BLE-Scanning und…
 qkaiser/broadcom-wps
Werkzeuge zur Fingerabdruck-Erkennung von WiFi-Access-Points, die das Broadcom SDK ausführen, sowie eine Liste bekannter betroffener Geräte.
 1n3/sn1per-mcp
MCP-Server, der KI-Assistenten eine selbst gehostete Sn1per-Installation steuern lässt, abgegrenzte, auditierte Scans ausführt und Ergebnisse, Ports,…
 yv1ing/secbox
Durchführung von Cybersicherheitstests mit dem pi-Agenten in einer vorkonfigurierten Sandbox-Umgebung.
 affolter-engineering/snmpen
SNMP-Enumerationstool, das SNMPv1/v2c-Hosts abfragt, um Systeminformationen, TCP-Verbindungen und Schreibzugriff für Penetrationstests und…
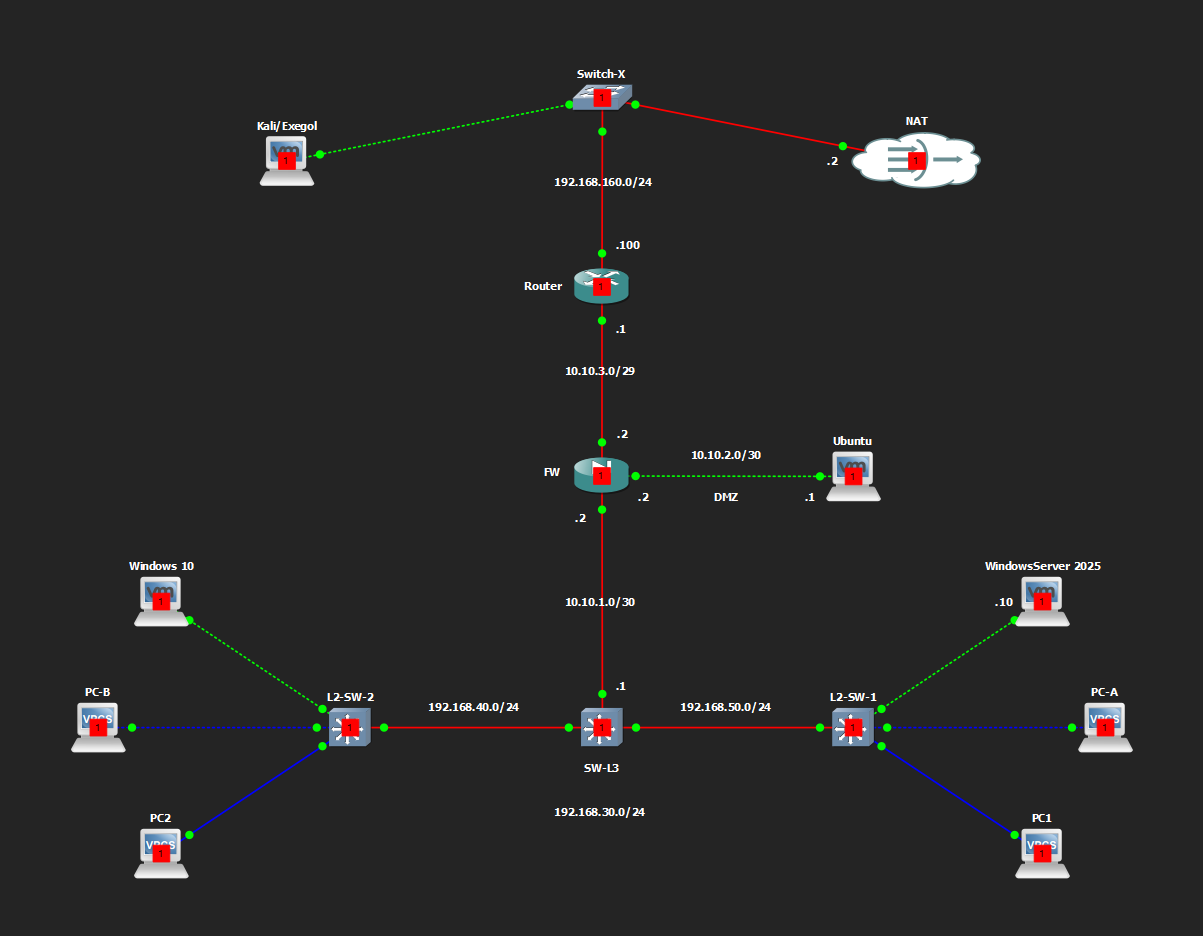 ko0ler/homelab
GNS3 home lab documenting a segmented network with Cisco ASAv firewall, L3 core, DMZ, and an Active Directory domain for practicing networking,…
 joda32/yowie
Finds the SaaS services an organisation subscribes to, using only externally observable data. Built for shadow IT discovery.
 hilmiazizi/oorecon
Terminal-UI für die Angriffsflächen-Erkundung: DNS-Recon, Subdomain-Enumeration, Port-Scanning, Reverse-IP, geleakte Login-URLs und…
 constantinefedorov/review.cve-2023-5612
Proof-of-Concept und Analyse für CVE-2023-5612, eine GitLab CE/EE Webhook-SSRF. Enthält curl-PoC-Schritte und benutzerdefinierte NSE-Skripte zum…
 sleepingbag945/dddd
Batch-Tool zur Asset-Erfassung und Schwachstellen-Scanning für Red Teams. Zieht Ziele von Hunter, Fofa und Quake, führt Fingerprinting,…
 cartography-cncf/cartography
Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…
 darkrx1/rxscan
Rust CLI for bounded network reconnaissance: TCP/UDP port discovery, service identification, DNS/TLS/HTTP evidence collection, and public-source…
 aixisstudio/snitch
Real-time network traffic visualizer — see every connection your computer makes. Privacy-first, 100% local. / Visualiseur de trafic réseau en temps…

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 qyvora/qyvora-anansi
Terminal-first attack surface intelligence engine. Built for speed, portability, and raw technical signal.
 trustedsec/spoonmap
Python wrapper around masscan and nmap for large-scale port discovery, host discovery, banner grabbing, and NSE-based vulnerability scanning across…
 vqkro/higernes
a passive OSINT toolkit in python and c++ usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 ankhcorp/nuke.sh
Bash-basiertes Skript für passive Reconnaissance und Attack-Surface-Mapping, das ausschließlich öffentliche APIs und Standard-Linux-Tools (curl, dig,…








