基于 frida-stalker 的 Windows(x64) 系统调用跟踪器。
[483]NtWaitForWorkViaWorkerFactory
test.exe!0x7ff91fbaf262
[35]NtQueryVirtualMemory
test.exe!0x7ff91fbaf262
[35]NtQueryVirtualMemory
test.exe!0x7ff91fbaf262
[35]NtQueryVirtualMemory
test.exe!0x7ff91fbb06d2
[199]NtCreateThreadEx
[+] Following thread 17876
test.exe!0x7ff91fbb06d2
[7]NtDeviceIoControlFile
[+] Unfollowing thread 17876
test.exe!0x7ff91fbaeee2
[7]NtDeviceIoControlFile
test.exe!0x7ff91fbaeee2
[7]NtDeviceIoControlFile
[+] Unfollowing thread 6344
[+] Unfollowing thread 6124
它还能准确识别那些掩盖系统调用的类型,例如下面这个项目。
https://github.com/passthehashbrowns/hiding-your-syscalls
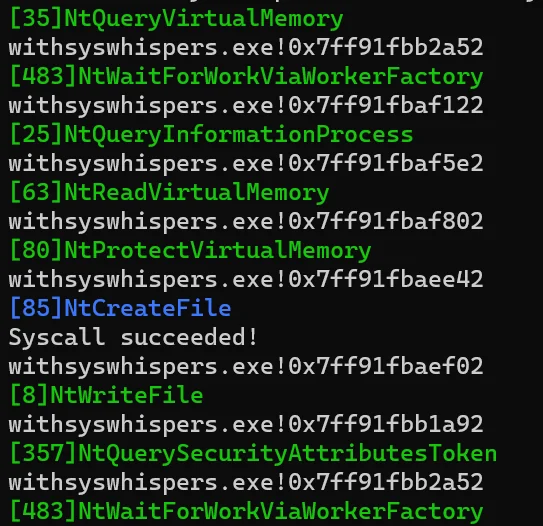
frida -l tracer.js app.exe
原始软件可在以下地址获取
https://github.com/sh1ma/iostrace。



