
 #1

 jamezx32/cve-2026-85046
V8 内联 Array.prototype.sort 元素类型混淆 - PoC + addrof(N-day 研究)
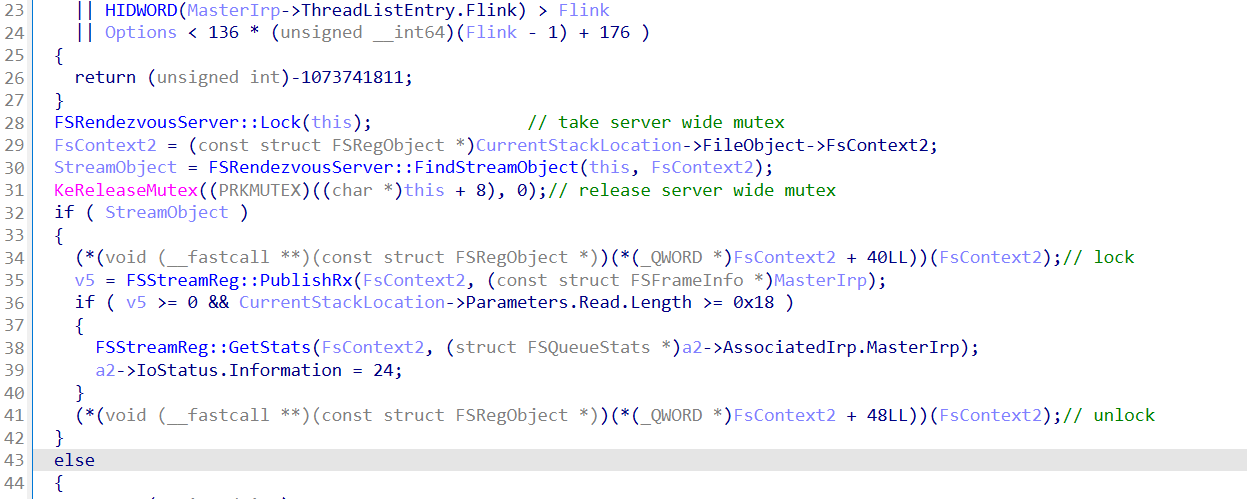 wkpwn/cve-2026-83834
对 FSRendezvousServer::PublishRx 和 ConsumeTx 中释放后使用竞态的分析,其中 Close() 可能在互斥锁释放与锁获取之间释放 FSStreamReg 对象。
 saretawa/cve-2026-77396
一个概念验证,通过构造恶意 AVI 文件在 PJSIP AVI 解析器中触发堆越界写入(CVE-2026-77396),并包含 ASan 验证与补丁分析。
 34zy/cve-2026-86950
针对 CVE-2026-86950(CoreGraphics 整数溢出漏洞)的利用框架:构造恶意 TrueType 字体和 PDF,提取 ASLR 泄漏,并构建 ARM64 ROP 链。
 0xsemizzz/cve-2026-86476
CVE-2026-86476 的概念验证:通过 unixfd 反序列化触发 GStreamer GstVideoMeta 堆越界读/写,包含 ASan 复现与 RCE 利用链。
 ylh440104/infinitycore-android-cve-2026-98260
ARM64 Android proof-of-concept for CVE-2026-98260, a POSIX timer UAF in the kernel Timer subsystem, with a full race, heap spray, and root escalation…
 01luyicheng/cve-2026-99999
Simulation-only proof of concept for CVE-2026-99999, a Linux kernel virtio-net IPv4 csum_start validation bug enabling guest-to-host heap memory…
 gandli/cve-2026-99999-pwnescape
Reproduction and analysis of the Linux IPv4 csum_start validation bug (CVE-2026-99999): header rewrite, 32-byte heap disclosure, leak oracle and…
 01luyicheng/cve-2026-99999-analysis
CVE-2026-99999 Educational Analysis — attack chain simulation of Linux kernel csum_start bug (CVSS 9.3). See also: CVE-2026-99999-exploit (Working…
 offline-ant/tcp2kaslr
CVE-2026-98432:一个普通的 IPv4 TCP 服务器存在漏洞,MPTCP 并非触发因素。漏洞触发、证据与分析。
 addxemmm/cve-2026-98260-pudding-android
Target-specific Android CVE-2026-98260 research port for Xiaomi 17 (pudding)
 janewas/cve-2026-98260-vivo-gki-research
Research notes: porting CVE-2026-98260 to vivo/iQOO GKI 6.6.127 (no exploit code; coordinated disclosure planned)
 jadedfella/lpe-study-notes
一次从零开始的缓慢讲解,深入剖析一个 Linux 内核提权漏洞(CVE-2026-98260)
 sganggs/cve-2026-98260-brm-an00
CVE-2026-98260 temporary root for HONOR Win2 BRM-AN00, handed to BakaSU. No flashing.
 yukonga/cve-2026-98260
Android kernel POSIX CPU timer use-after-free exploit for 6.12.69 that achieves uid=0 shell or KernelSU late-load via fake credentials.
 woshigenm/cve-2026-98260
Android kernel LPE research for CVE-2026-98260 (posix-cpu-timers UAF): trigger PoC, fake-cred and real-cred uid-0 shell chains, plus a…
 nanoturtle1145/cve-2026-98260-uaf
CVE-2026-98260 (posix-cpu-timers exec UAF) exploit research: S9280 Android 14 GKI 6.1 — UAF trigger + zero-write primitive + SELinux Permissive.…









