
 #1

 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 s3n4t0r-0x0/apts-adversary-simulation
This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…
 bigbodycobain/shadowbroker
Real-time geospatial OSINT platform aggregating 60+ public telemetry feeds (ADS-B, AIS, satellites, CCTV) into a unified map with server-side recon…
 goshs-labs/goshs
Feature-rich single-binary file server for red teamers and developers. HTTP/S · WebDAV · FTP/SFTP · SMB · LDAP/S · NTLM hash capture · DNS/SMTP…
 drb-ra/c2intelfeeds
自动生成的 C2 威胁情报源,包含 IP、域名、URL 路径和植入程序配置元数据,源自面向 SIEM、EDR 和威胁狩猎的互联网扫描。
 oyesanyf/oshoosiclaw
Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…
 sshuttle/sshuttle
透明代理服务器,可作为穷人的VPN使用。通过SSH转发。无需管理员权限。支持Linux和MacOS。支持DNS隧道。
 fortra/impacket
Python库,用于底层网络协议操作,包含SMB、MSRPC、Kerberos和WMI实现,提供认证攻击、哈希传递及Windows环境横向移动的工具。
 vulncheck-oss/go-exploit
基于Go的漏洞利用开发框架,内置了目标验证、版本扫描、利用和后门(C2)等多个阶段。支持多种载荷、协议助手,并与Metasploit等工具集成。
 onyks-os/transparenttorproxy
一个Linux命令行实用工具,通过nftables透明地将所有系统流量路由至Tor网络。它支持快速IP轮换,并可轻松切换全局代理设置,以满足隐私任务需求。
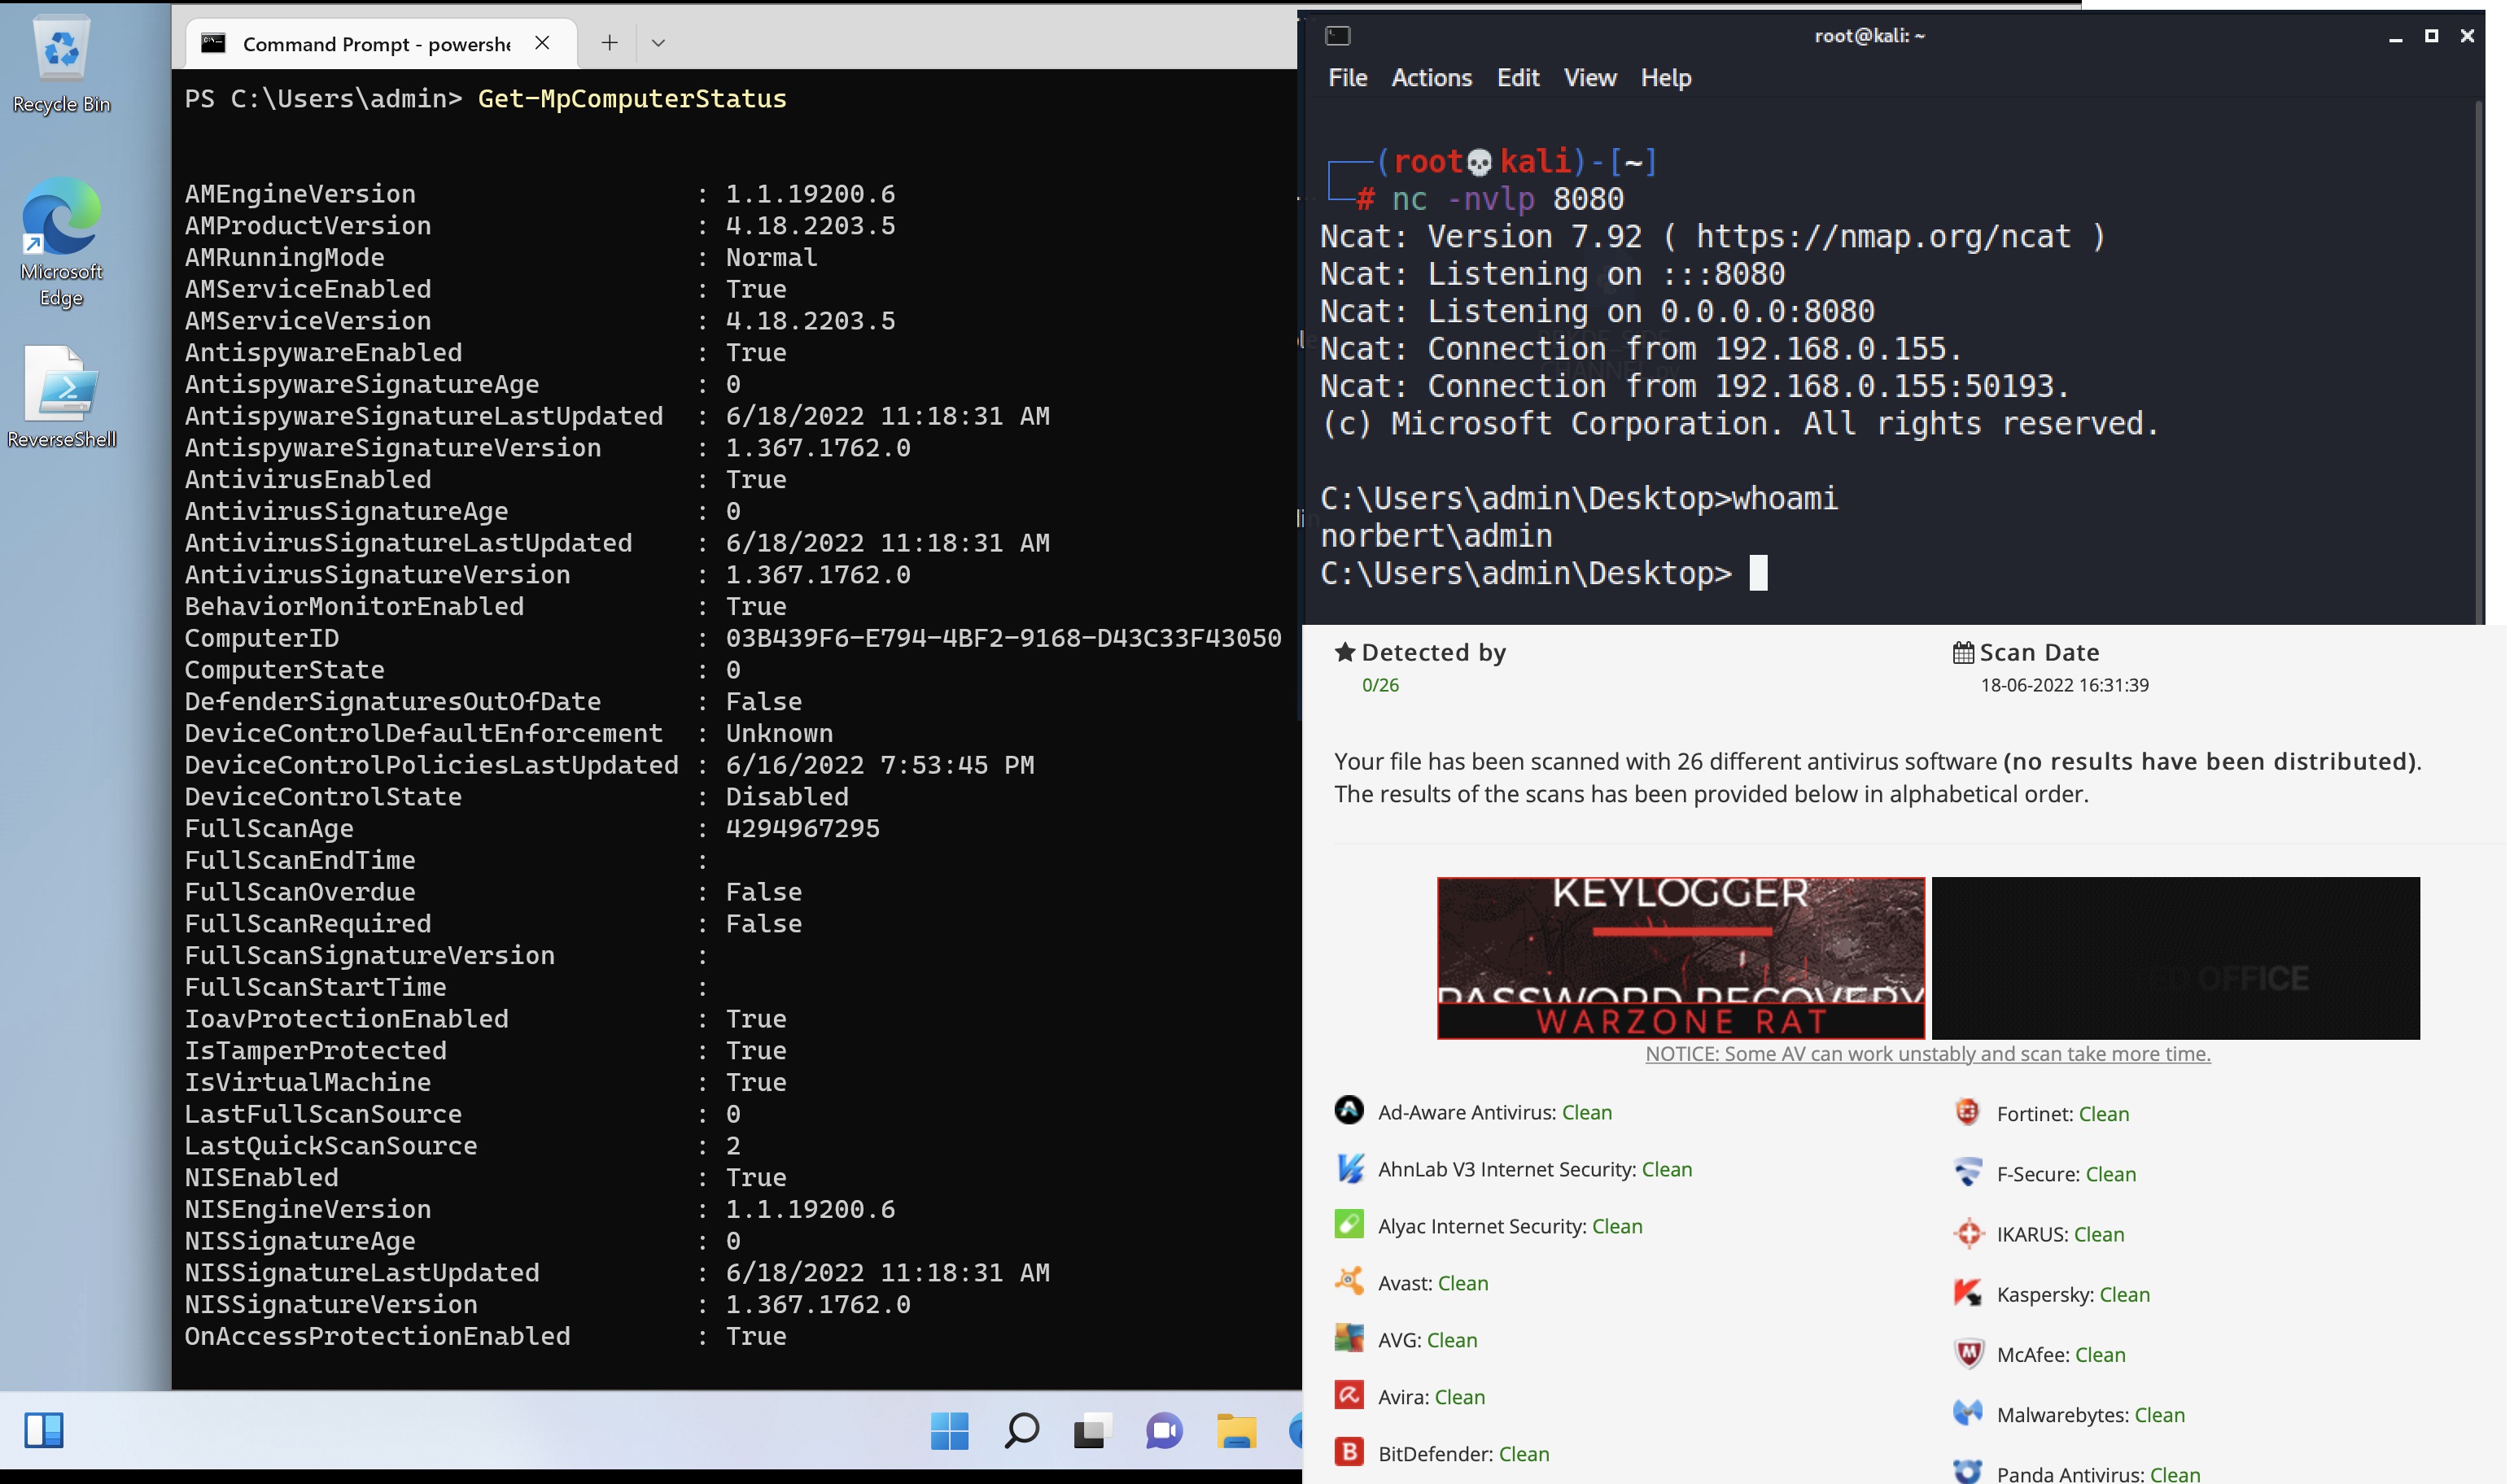 tihanyin/pssw100avb
一系列有用的 PowerShell 脚本,100% 免杀(在发布时)。

 node9-ai/node9-proxy
Access control for AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run,…

 yukibtc/redknife
A Swiss Army knife for offensive security.
 mafifrizi/ares
自主红队交战平台,具备 MITRE ATT&CK 模块编排、DAG 攻击路径求解、OPSEC 控制、加密凭据保险库以及多格式报告功能。
 threatexpert/gonc
具有自动NAT穿透、安全P2P以及用于shell访问、文件传输和网络代理的高级功能的Netcat。
 voidsecsoftwares/voidsyscall
跨平台系统调用驱动的植入程序与 C2 —— 直接系统调用(Windows)、原始系统调用(Linux)、HTTPS/DNS/ICMP 通道。无 winapi 层。








