#1

 pennyw0rth/netexec
后渗透框架,用于自动化的网络认证测试、凭证收集以及在Windows/AD环境中的横向移动,具有模块化协议支持。
 yarrick/iodine
Tunnel IPv4 data through DNS servers to bypass firewall restrictions and provide covert network access for penetration testing.
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
 rapid7/metasploit-payloads
Metasploit Framework 不同载荷的统一仓库
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 purpleailab/decepticon
Autonomous Hacking Agent for Red Team
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
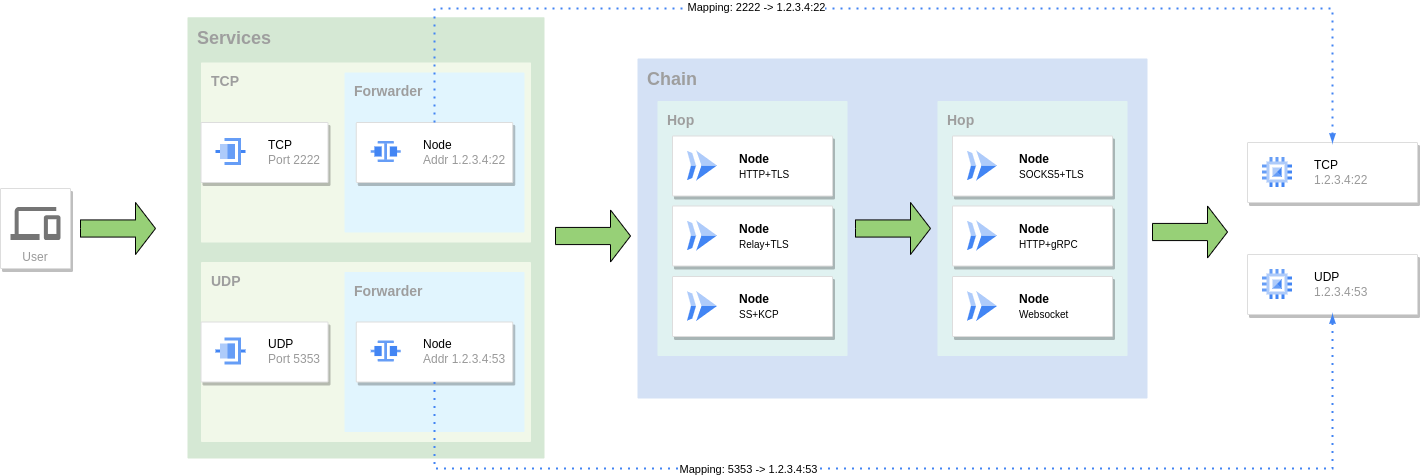 go-gost/gost
GO Simple Tunnel - a simple tunnel written in golang
 sia-iotechnology/kittysploit-framework
Python 漏洞利用框架、V8 引擎调试器、代理拦截器、市场、后渗透、后门生成器,……
 jm33-m0/emp3r0r
Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…
 yaklang/yakit
集MITM代理、Web模糊测试、反向连接处理程序和插件系统于一体的渗透测试平台,用于自动化安全测试与利用。
 rapid7/metasploit-framework
开源漏洞利用框架,具备模块化载荷、编码器和辅助系统,用于跨网络和应用的渗透测试、漏洞验证及安全研究。
 aipentest/cyberstrikeai
AI原生网络安全的行动系统——在这里,意图转化为受治理的执行,证据转化为运营记忆,每一次操作都让下一次更完善。
 ed1s0nz/cyberstrikeai
AI原生网络安全的行动系统——在这里,意图转化为受治理的执行,证据沉淀为运营记忆,每一次操作都让下一次更出色。