


Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
APTs-Adversary-Simulation — This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2 servers, backdoors, exploitation techniques, stagers, bootloaders, and other malicious artifacts that mirror those used in real world attacks . | Kitploit
工具/GitHubGitHub/s3n4t0r-0x0/apts-adversary-simulation
Privilege EscalationReconnaissancePersistence MechanismsExploitationLateral MovementPost-ExploitationPenetration TestingCommand and ControlLearning & EducationRed TeamingPayload DevelopmentAdversarial Attack
1.1k190497天前Kitploit 审核通过

关于

This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2 servers, backdoors, exploitation techniques, stagers, bootloaders, and other malicious artifacts that mirror those used in real world attacks .

分享
GitHubs3n4t0r-0x0/apts-adversary-simulation

APTs-Adversary-Simulation

查看仓库
内容在请求的语言中不可用。显示英文版本。

APTs Adversary Simulation


Comprehensive collection of simulated APT attacks based on real world TTPs used by state sponsored APT Groups from Russia, China, Iran, and North Korea
hollywood-Comp-02

[!CAUTION] Important Notice: This project is strictly for educational, research, and defensive security purposes only. Unauthorized use of these techniques may violate laws and result in serious legal consequences.

🧠 Overview

This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, command and control (C2) servers, backdoors, exploitation techniques, stagers, bootloaders, and other malicious artifacts that mirror those used in real world attacks. The simulations are based on extensive research from leading cybersecurity firms, including PaloAlto Unit42, Kaspersky, Microsoft, Cisco, Trellix, CrowdStrike, and WithSecure.

Learn More About the Importance and Outcomes of the Experience:

  • Why Adversary Simulation? - Understanding the strategic value of simulating advanced threats
  • Adversary Simulation VS Adversary Emulation - Key differences and when to use each approach
  • How do I simulate an APT - Adversary Simulation Is Not a Methodology It's the Outcome of Experience

🎯 Simulated APT Groups

Note: APT group names in this repository follow the naming conventions used by different security vendors. The same APT group may have different names depending on the vendor (e.g., Mandiant, CrowdStrike, Microsoft, Kaspersky, etc.).
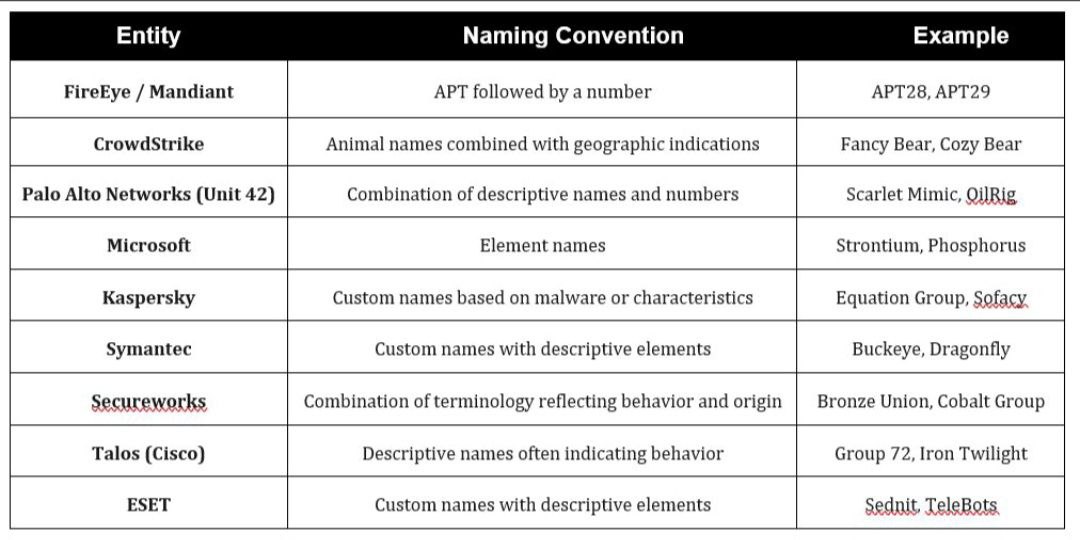
photo_2025-11-09_04-26-38

Below is the complete list of simulated APT Groups:

Country
of Origin
Russia 🇷🇺 China 🇨🇳 North Korea 🇰🇵 Iran 🇮🇷
APT Groups

Cozy Bear
Voodoo Bear
Fancy Bear
Energetic Bear
Berserk Bear
Gossamer Bear
Primitive Bear
Ember Bear
Venomous Bear

Mustang Panda
Wicked Panda
Goblin Panda
Deep Panda
Glacial Panda
Anchor Panda
Samurai Panda
Phantom Panda
Sunrise Panda
Ethereal Panda

Lazarus
Labyrinth Chollima
Velvet Chollima
Famous Chollima
Ricochet Chollima
Silent Chollima

Helix Kitten
Charming Kitten
Static Kitten
Muddy Water
Tracer Kitten
Pioneer Kitten
Nemesis Kitten
Clever Kitten
Pulsar Kitten
Remix Kitten
Haywire Kitten

🛠️ Adversary Framework

All adversary simulations are powered by BEAR-C2 a custom command and control framework designed for realistic threat simulation.
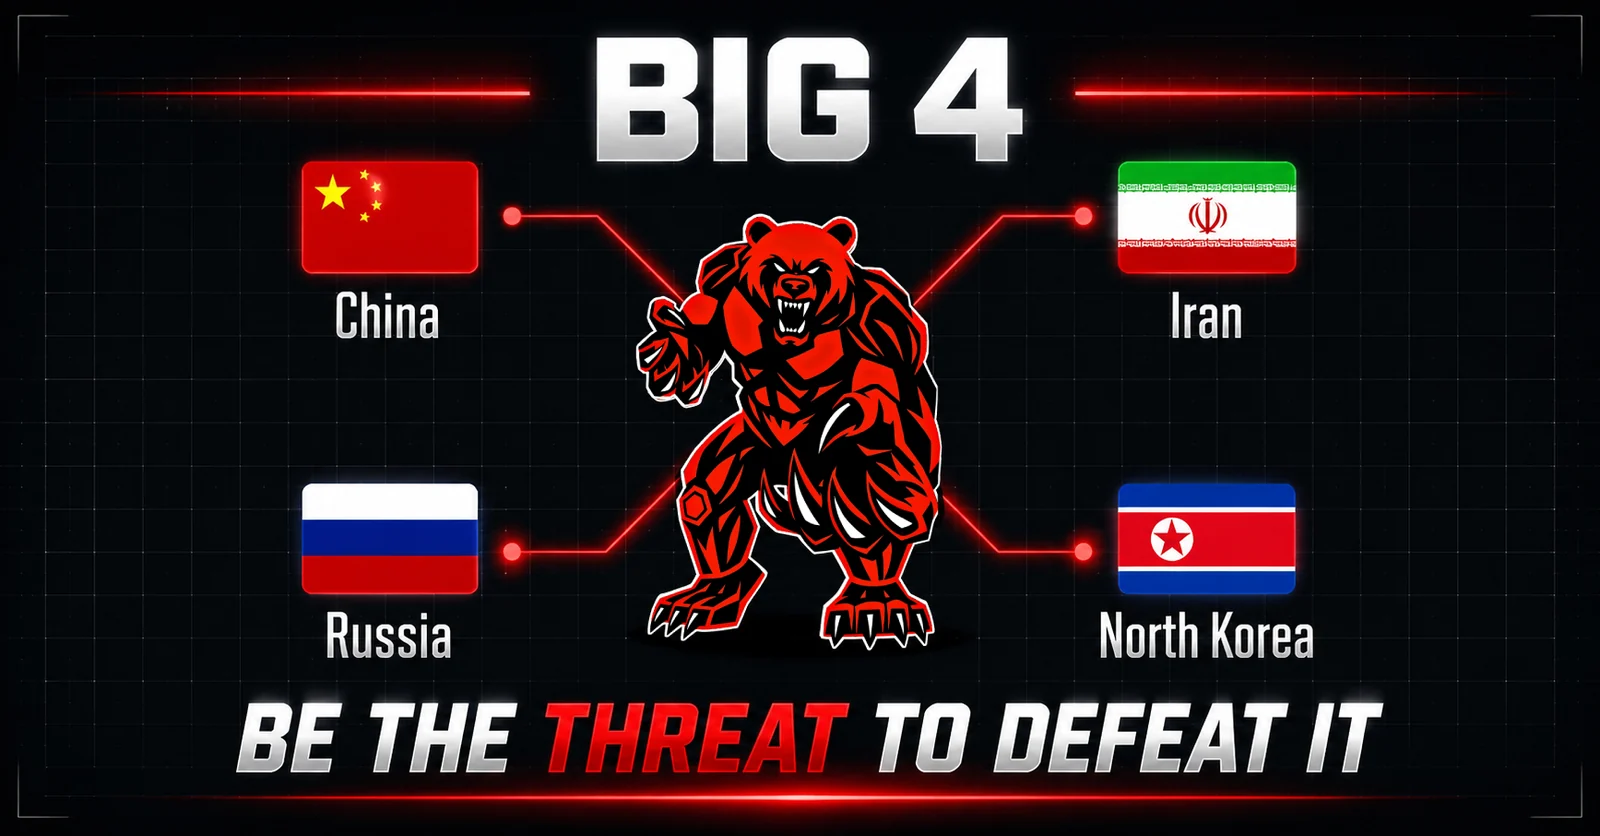
image psd(1)

📫 Contact

Telegram Twitter/X LinkedIn Reddit
下载工具

最受欢迎

查看全部 →

发现我们社区最常用的工具。

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 终极 OSINT 工具包:调查图谱、置信度评分、别名家族、地图、时间线和报告。49 个模块、400+ 个站点,无需 API 密钥。

    772
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock 一键执行应用(CVE-2026-43499)

    505
  • 3

    ARTEX

    baarai/artex

    基于LLM的多智能体自主渗透测试平台,具备规划器/执行器智能体、资产与探索图谱、MITM流量记录以及漏洞复测功能。

    420
  • 4

    redforge

    cybersecurity91/redforge

    浏览器端红队工具包,包含 102 个离线工具,用于侦察、载荷生成、凭据攻击、加密、编码和交战报告。

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    AI原生网络安全的行动系统——在这里,意图转化为受治理的执行,证据沉淀为运营记忆,每一次操作都让下一次更出色。

    260
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    251

探索所有工具

浏览我们的工具集合

查看所有工具 →






