 fr0gger/iatelligence
IATelligence é um script Python que extrai o IAT de um arquivo PE e solicita ao GPT mais informações sobre a API e a matriz ATT&CK relacionada.

IATelligence é um script Python que extrai a Tabela de Endereços de Importação (IAT) de um arquivo PE e usa o modelo GPT-3 da OpenAI para fornecer detalhes sobre cada API do Windows importada pelo arquivo. O script também pesquisa técnicas relacionadas do MITRE ATT&CK e explica como a API poderia ser usada por atacantes.
Ele também exibe os hashes do arquivo e estima o custo das solicitações ao GPT-3. IATelligence é uma prova de conceito para usar GPT-3 na análise de malware e avaliar rapidamente o comportamento de um malware com base em sua IAT.
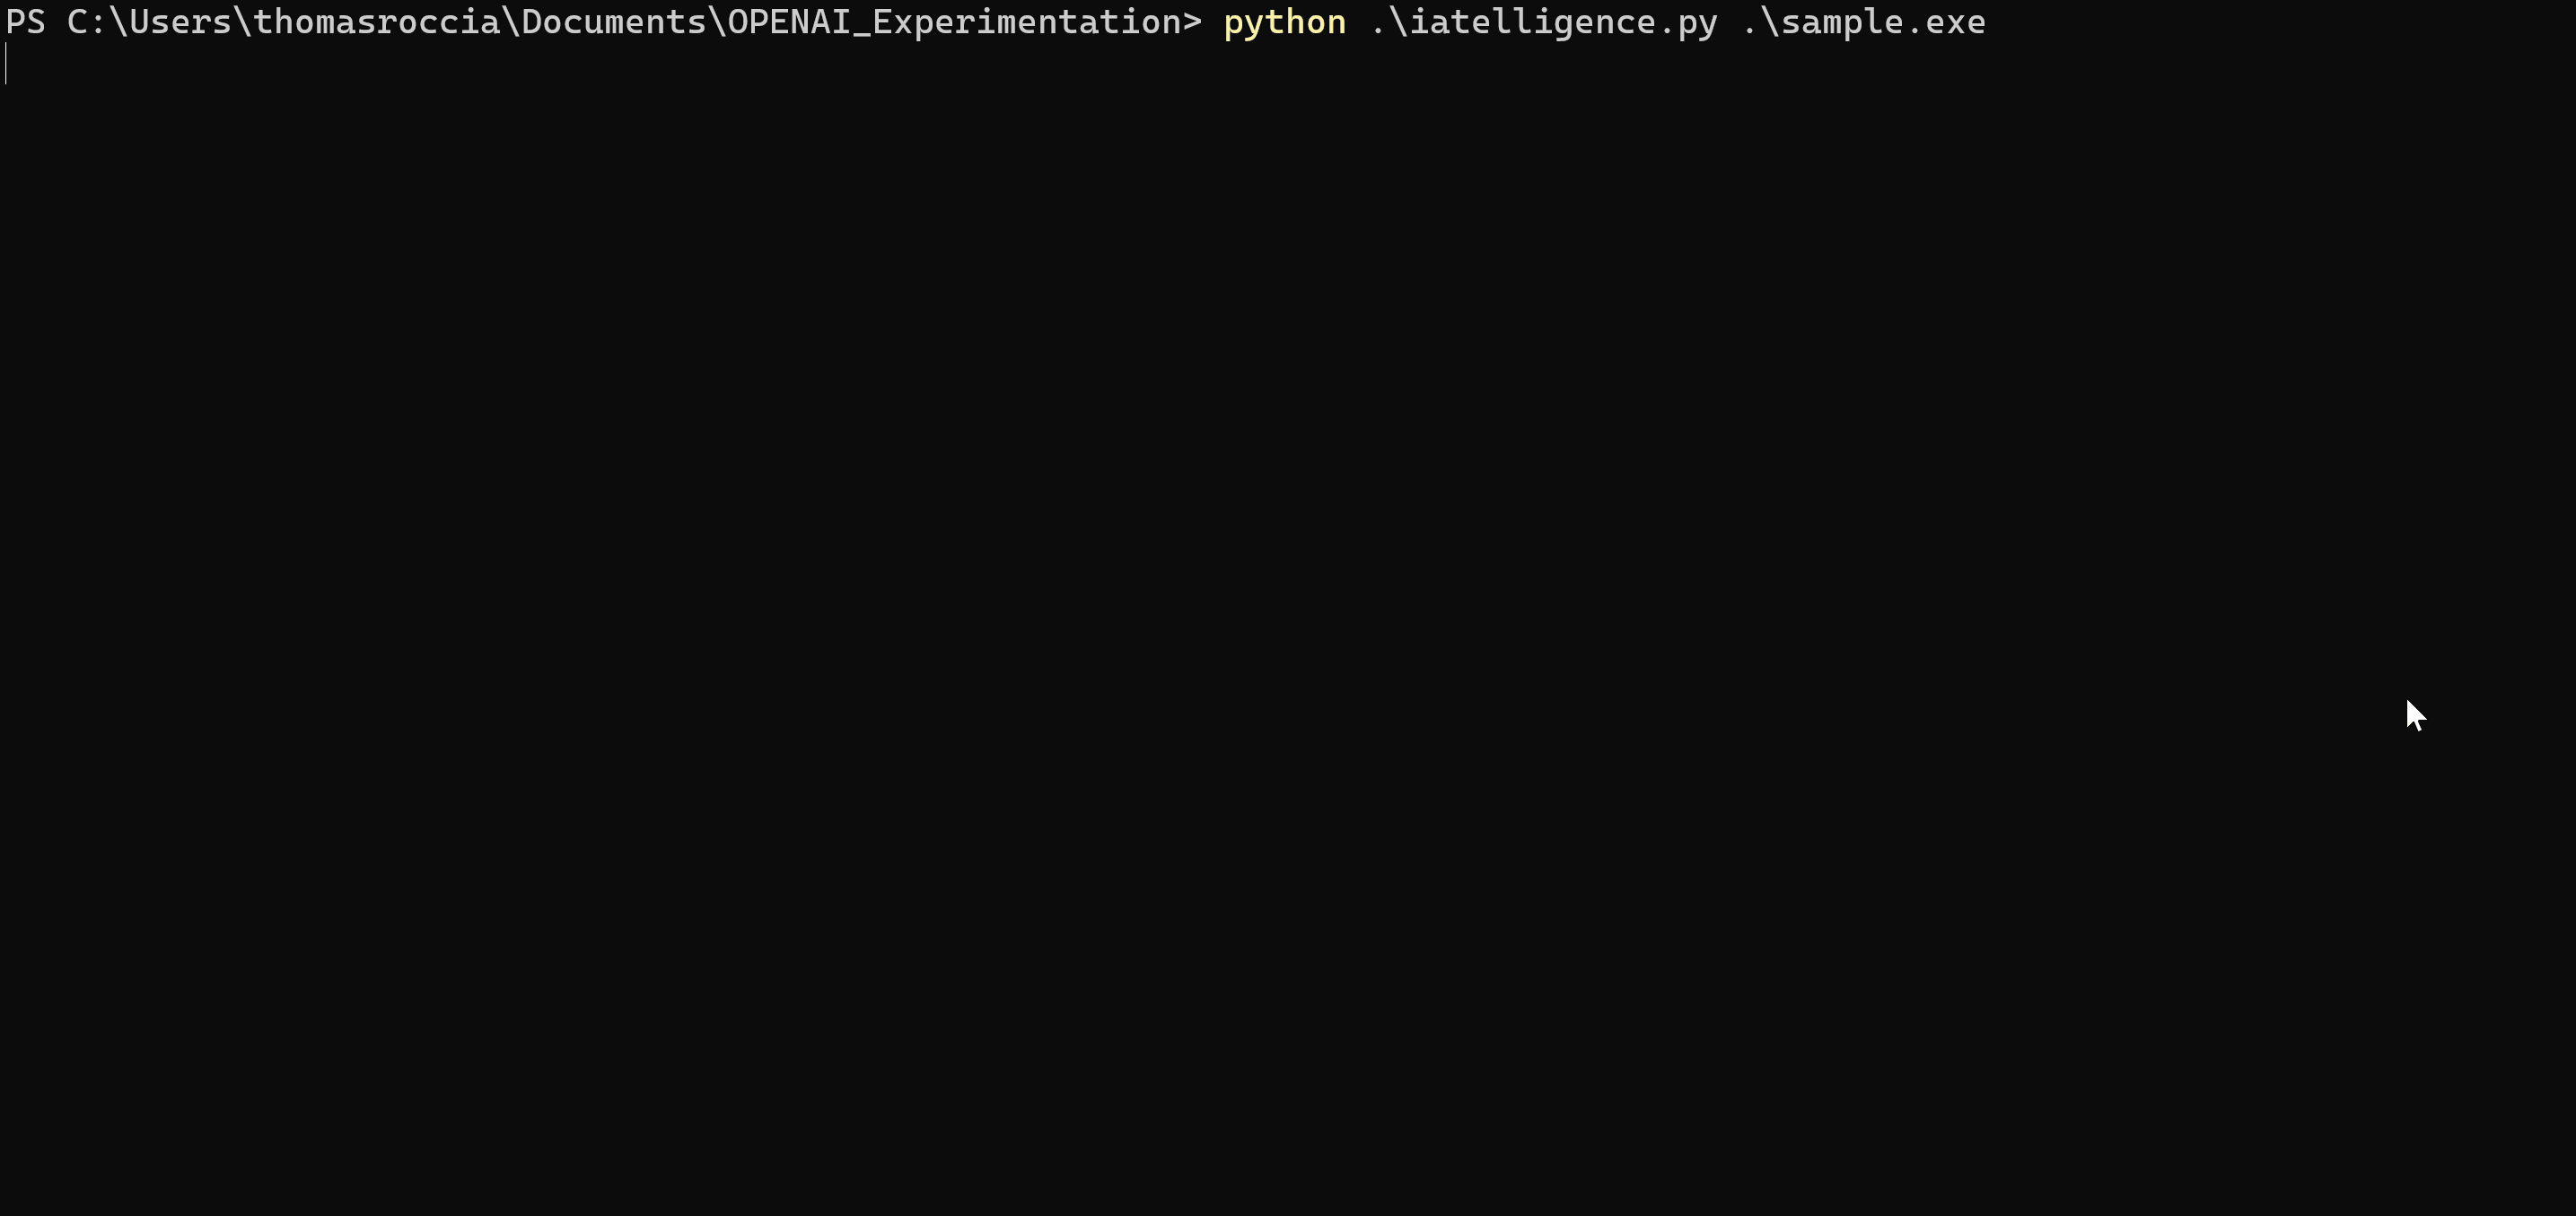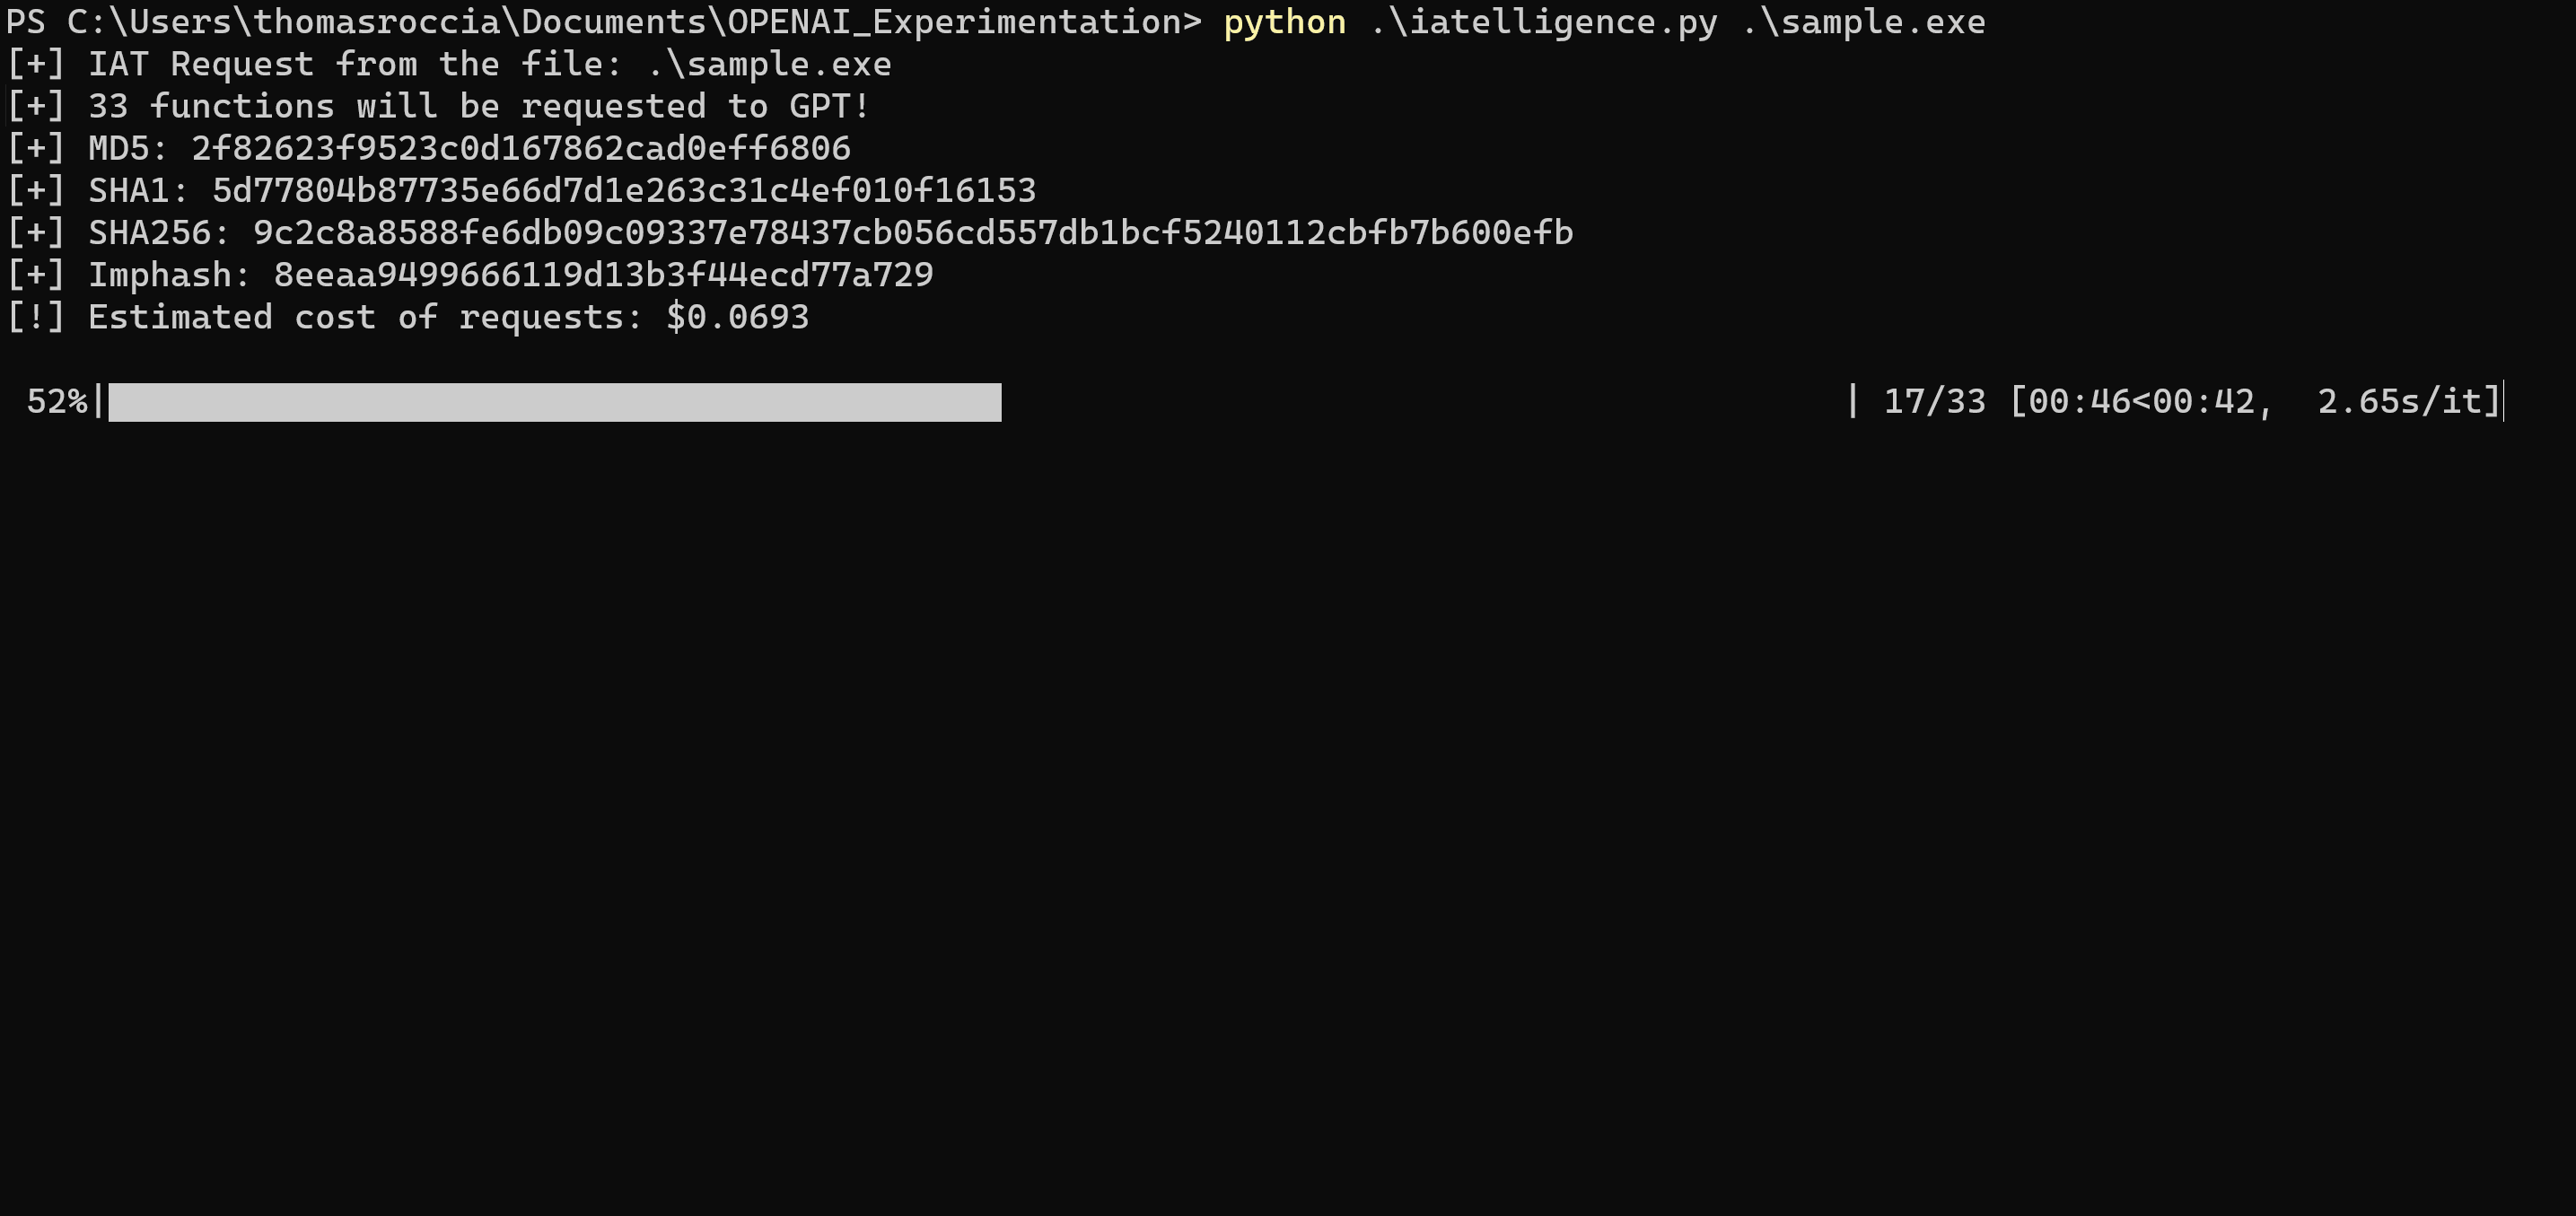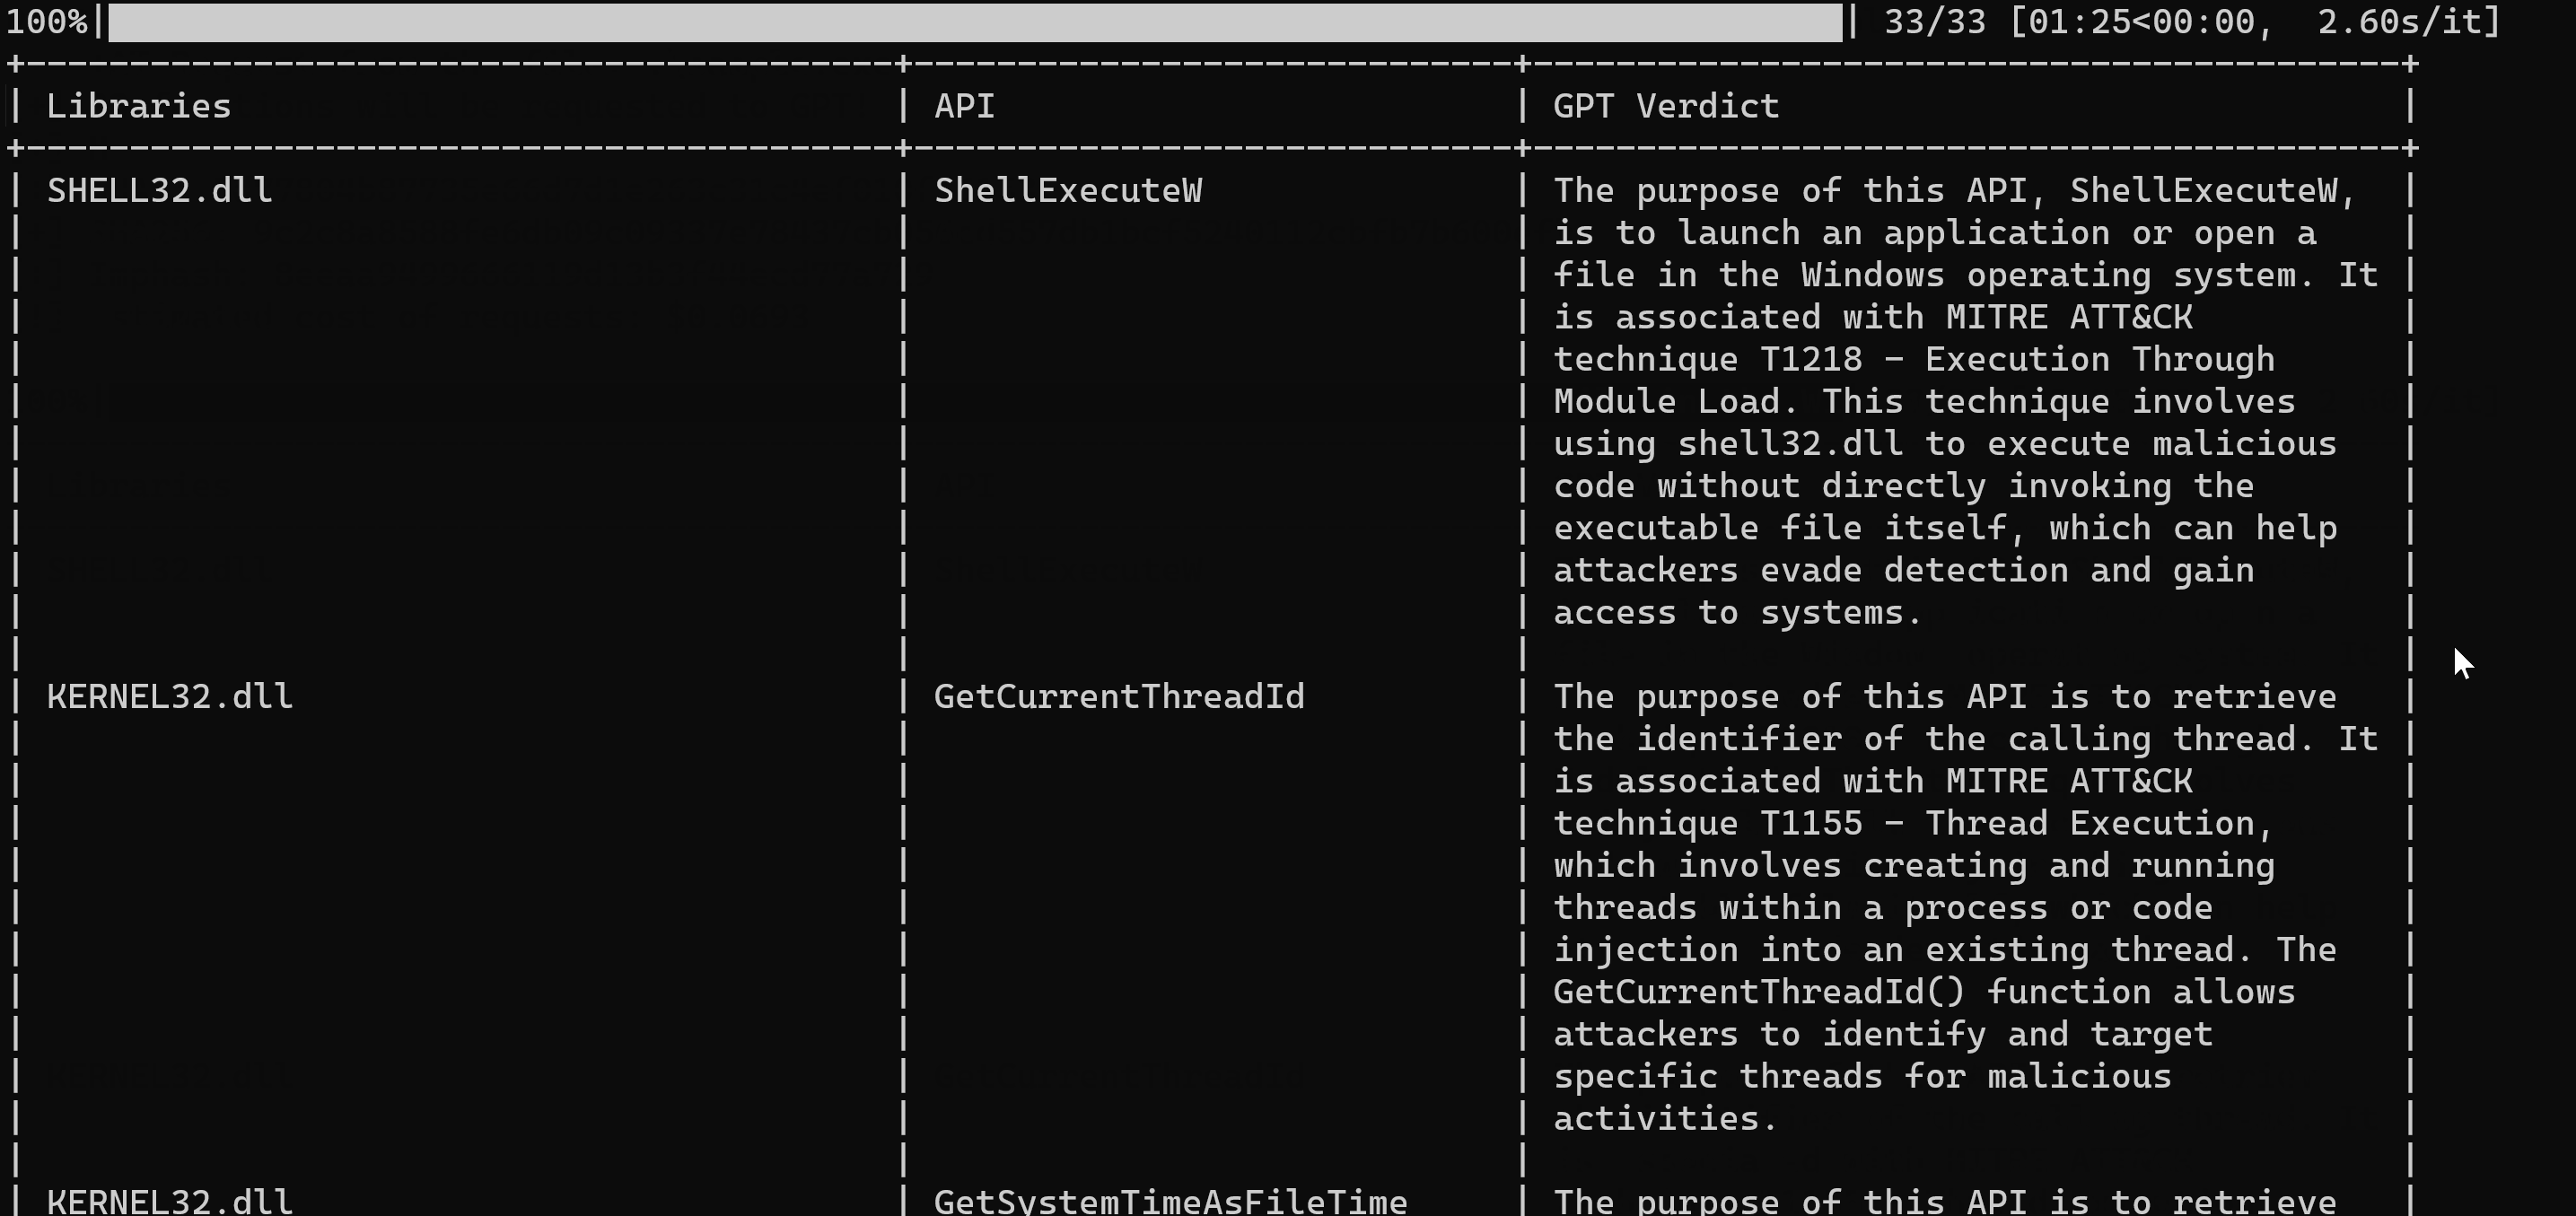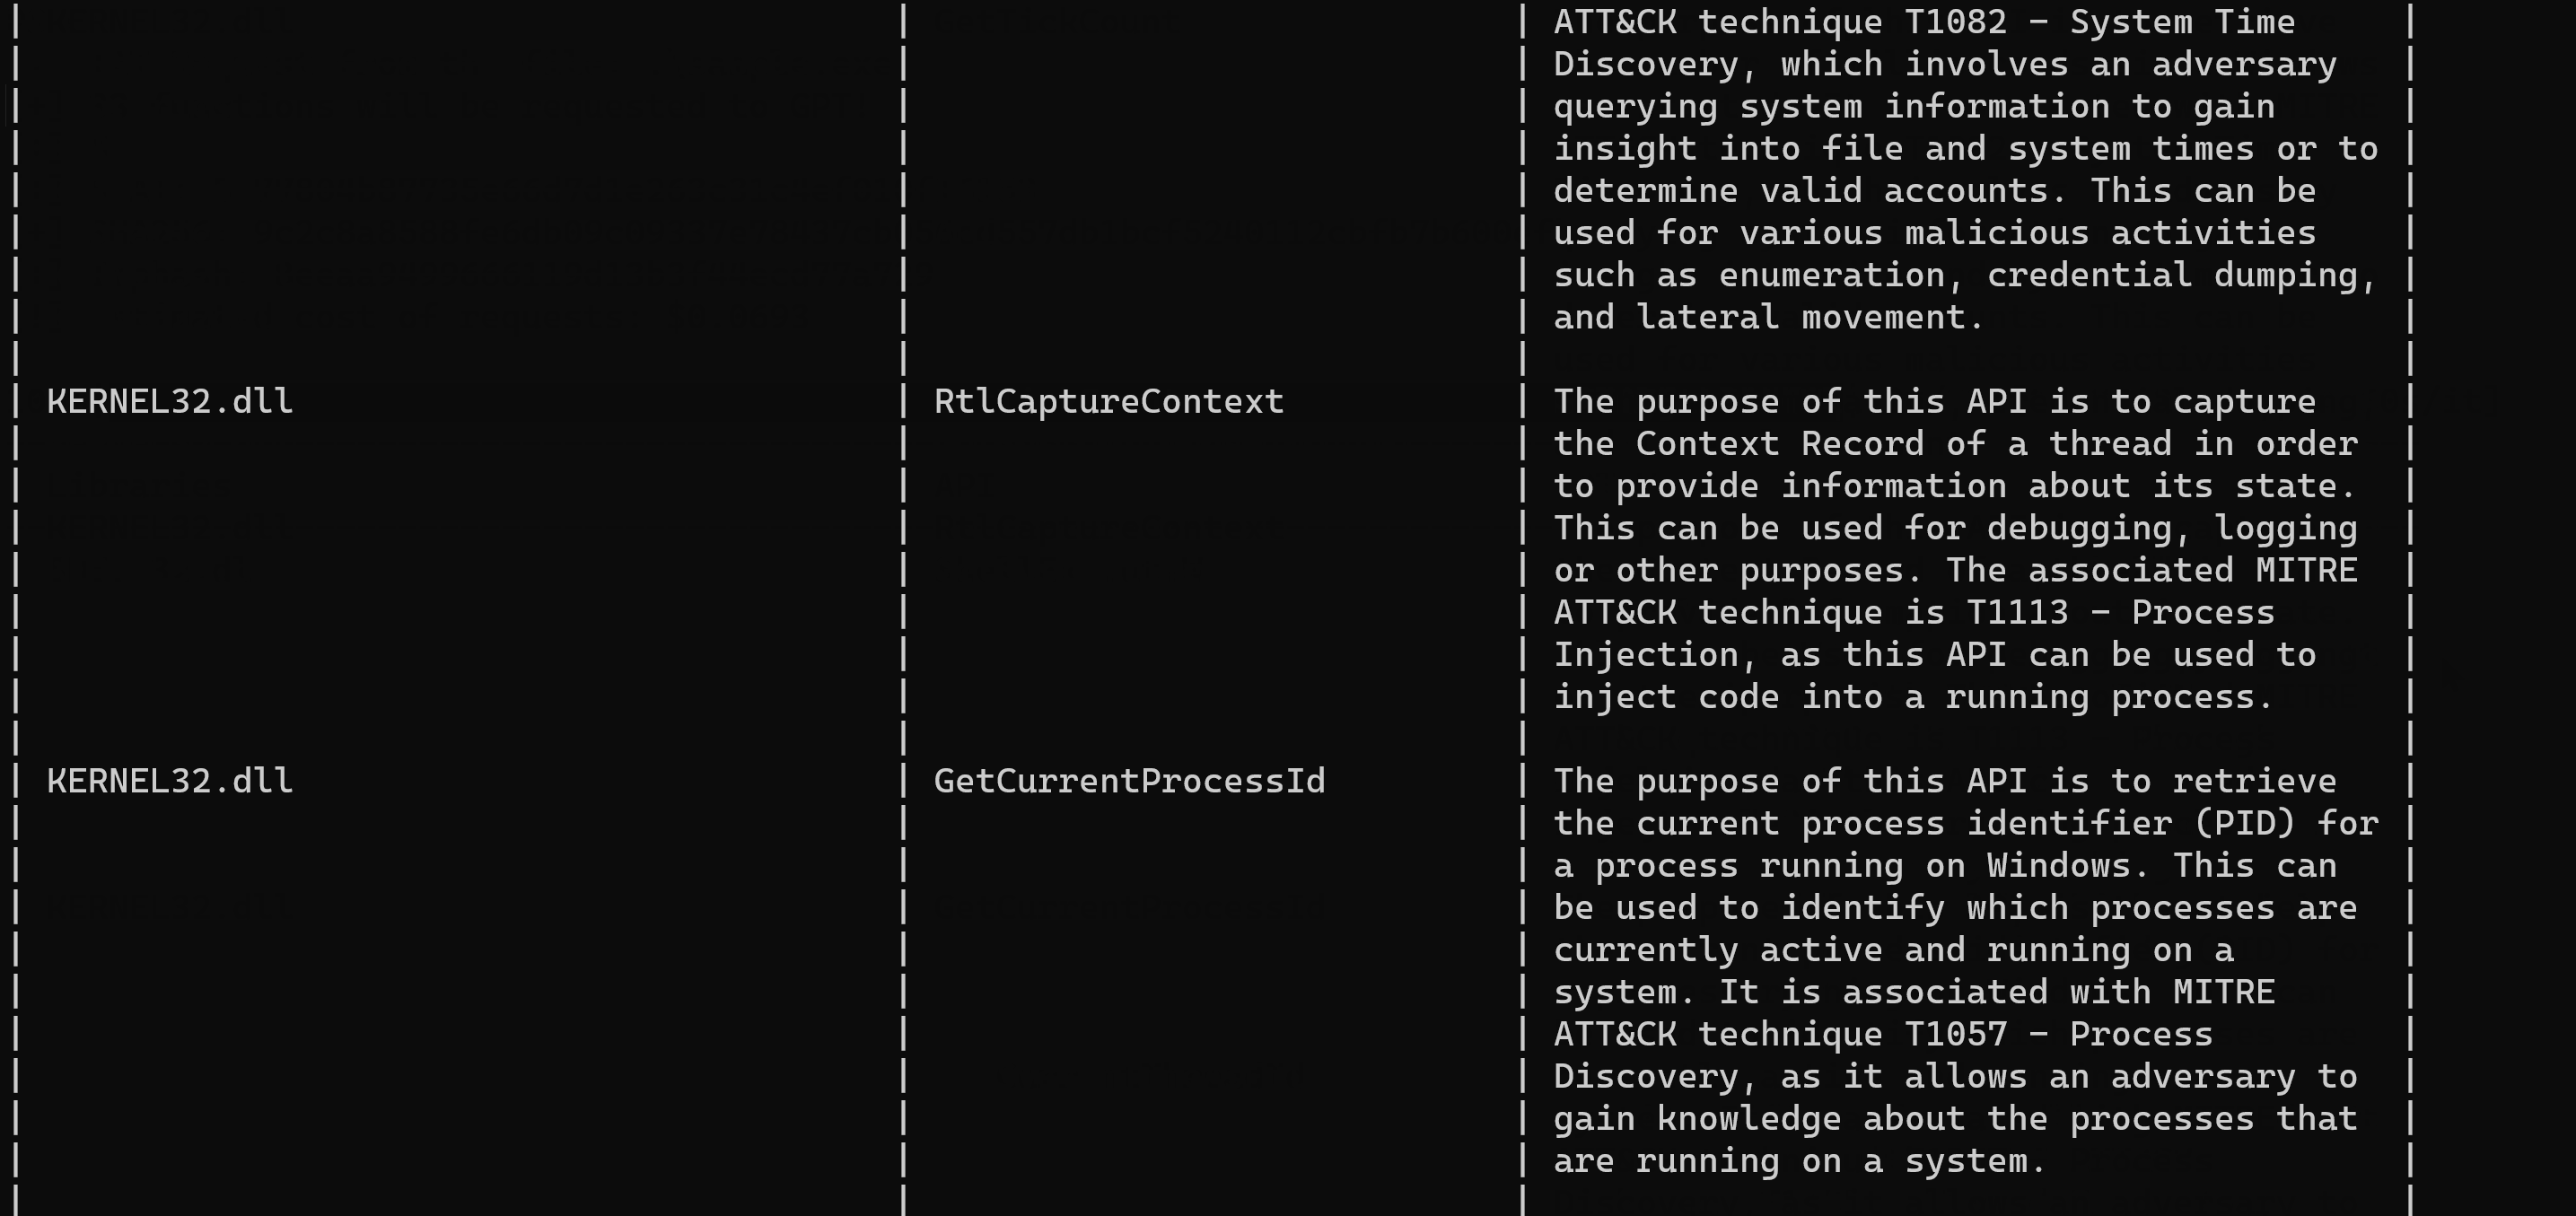
Abaixo está um exemplo rápido do resultado que você obterá. Observe que a solicitação pode demorar mais dependendo do tamanho da IAT.
Para executar esta ferramenta, você precisará de acesso à API OpenAI. Em seguida, você precisará modificar o script para adicionar sua própria chave de API.
# Authenticate with the OpenAI API
openai.api_key = ""
Você também precisará instalar os requisitos.
pip install -r requirements.txt
Para executar a ferramenta, basta especificar um arquivo PE como argumento para o script.
python iatelligence.py sample.exe
O script também calculará os hashes, bem como o custo estimado da solicitação.
[+] IAT Request from the file: .\sample.exe
[+] 33 functions will be requested to GPT!
[+] MD5: 2f82623f9523c0d167862cad0eff6806
[+] SHA1: 5d77804b87735e66d7d1e263c31c4ef010f16153
[+] SHA256: 9c2c8a8588fe6db09c09337e78437cb056cd557db1bcf5240112cbfb7b600efb
[+] Imphash: 8eeaa9499666119d13b3f44ecd77a729
[!] Estimated cost of requests: $0.0693
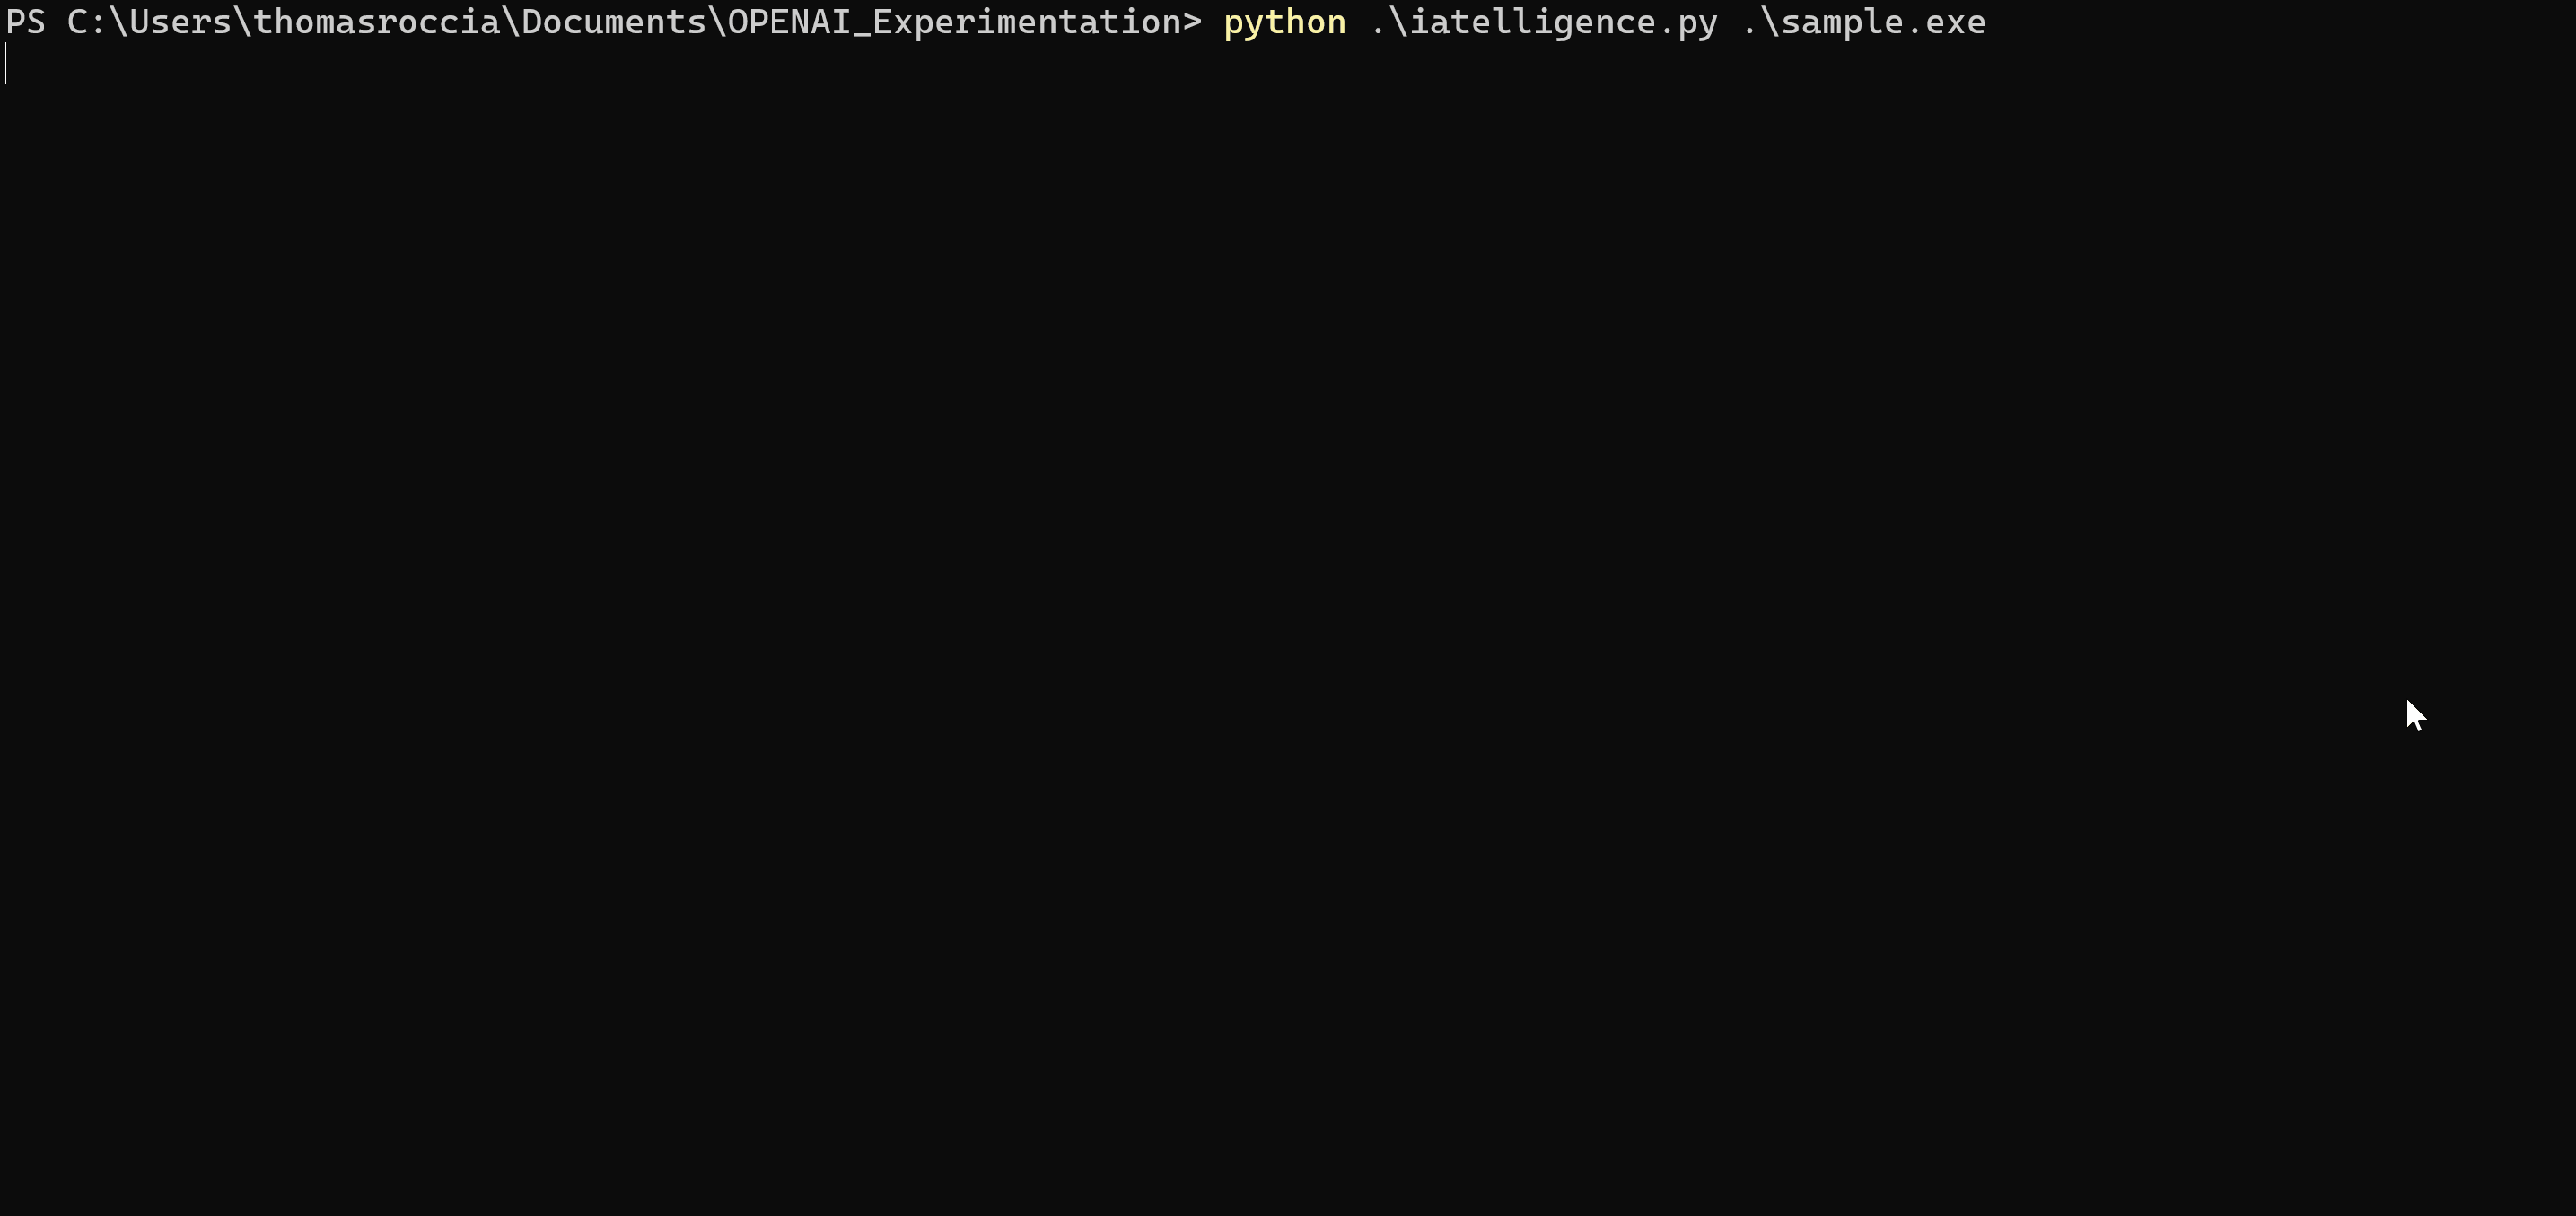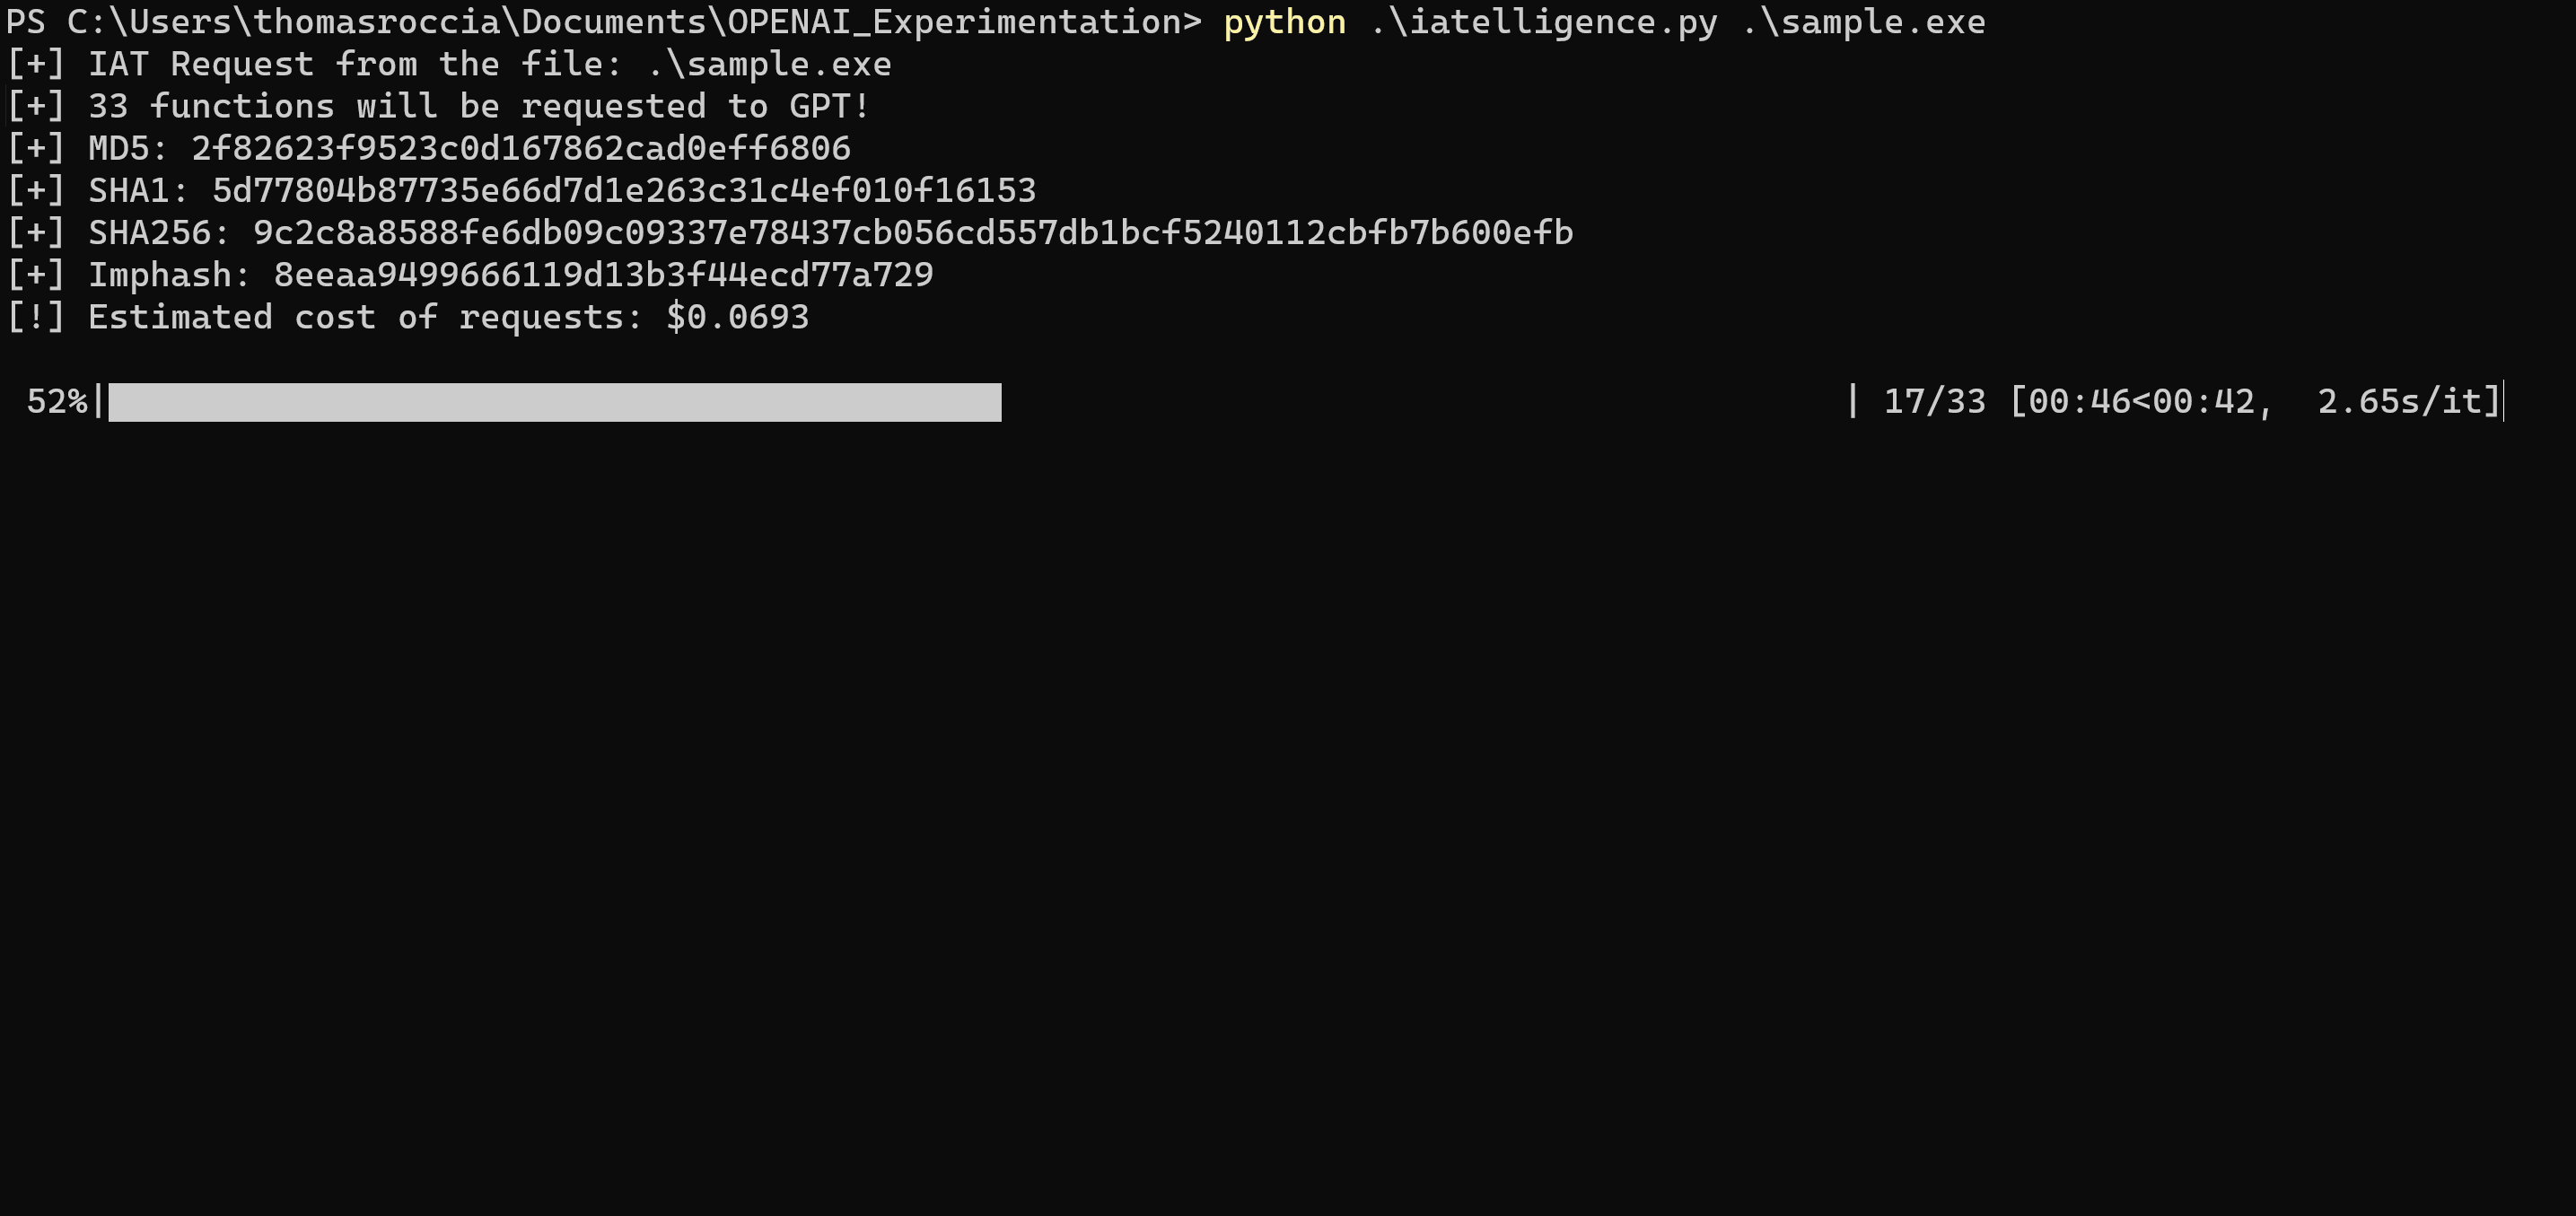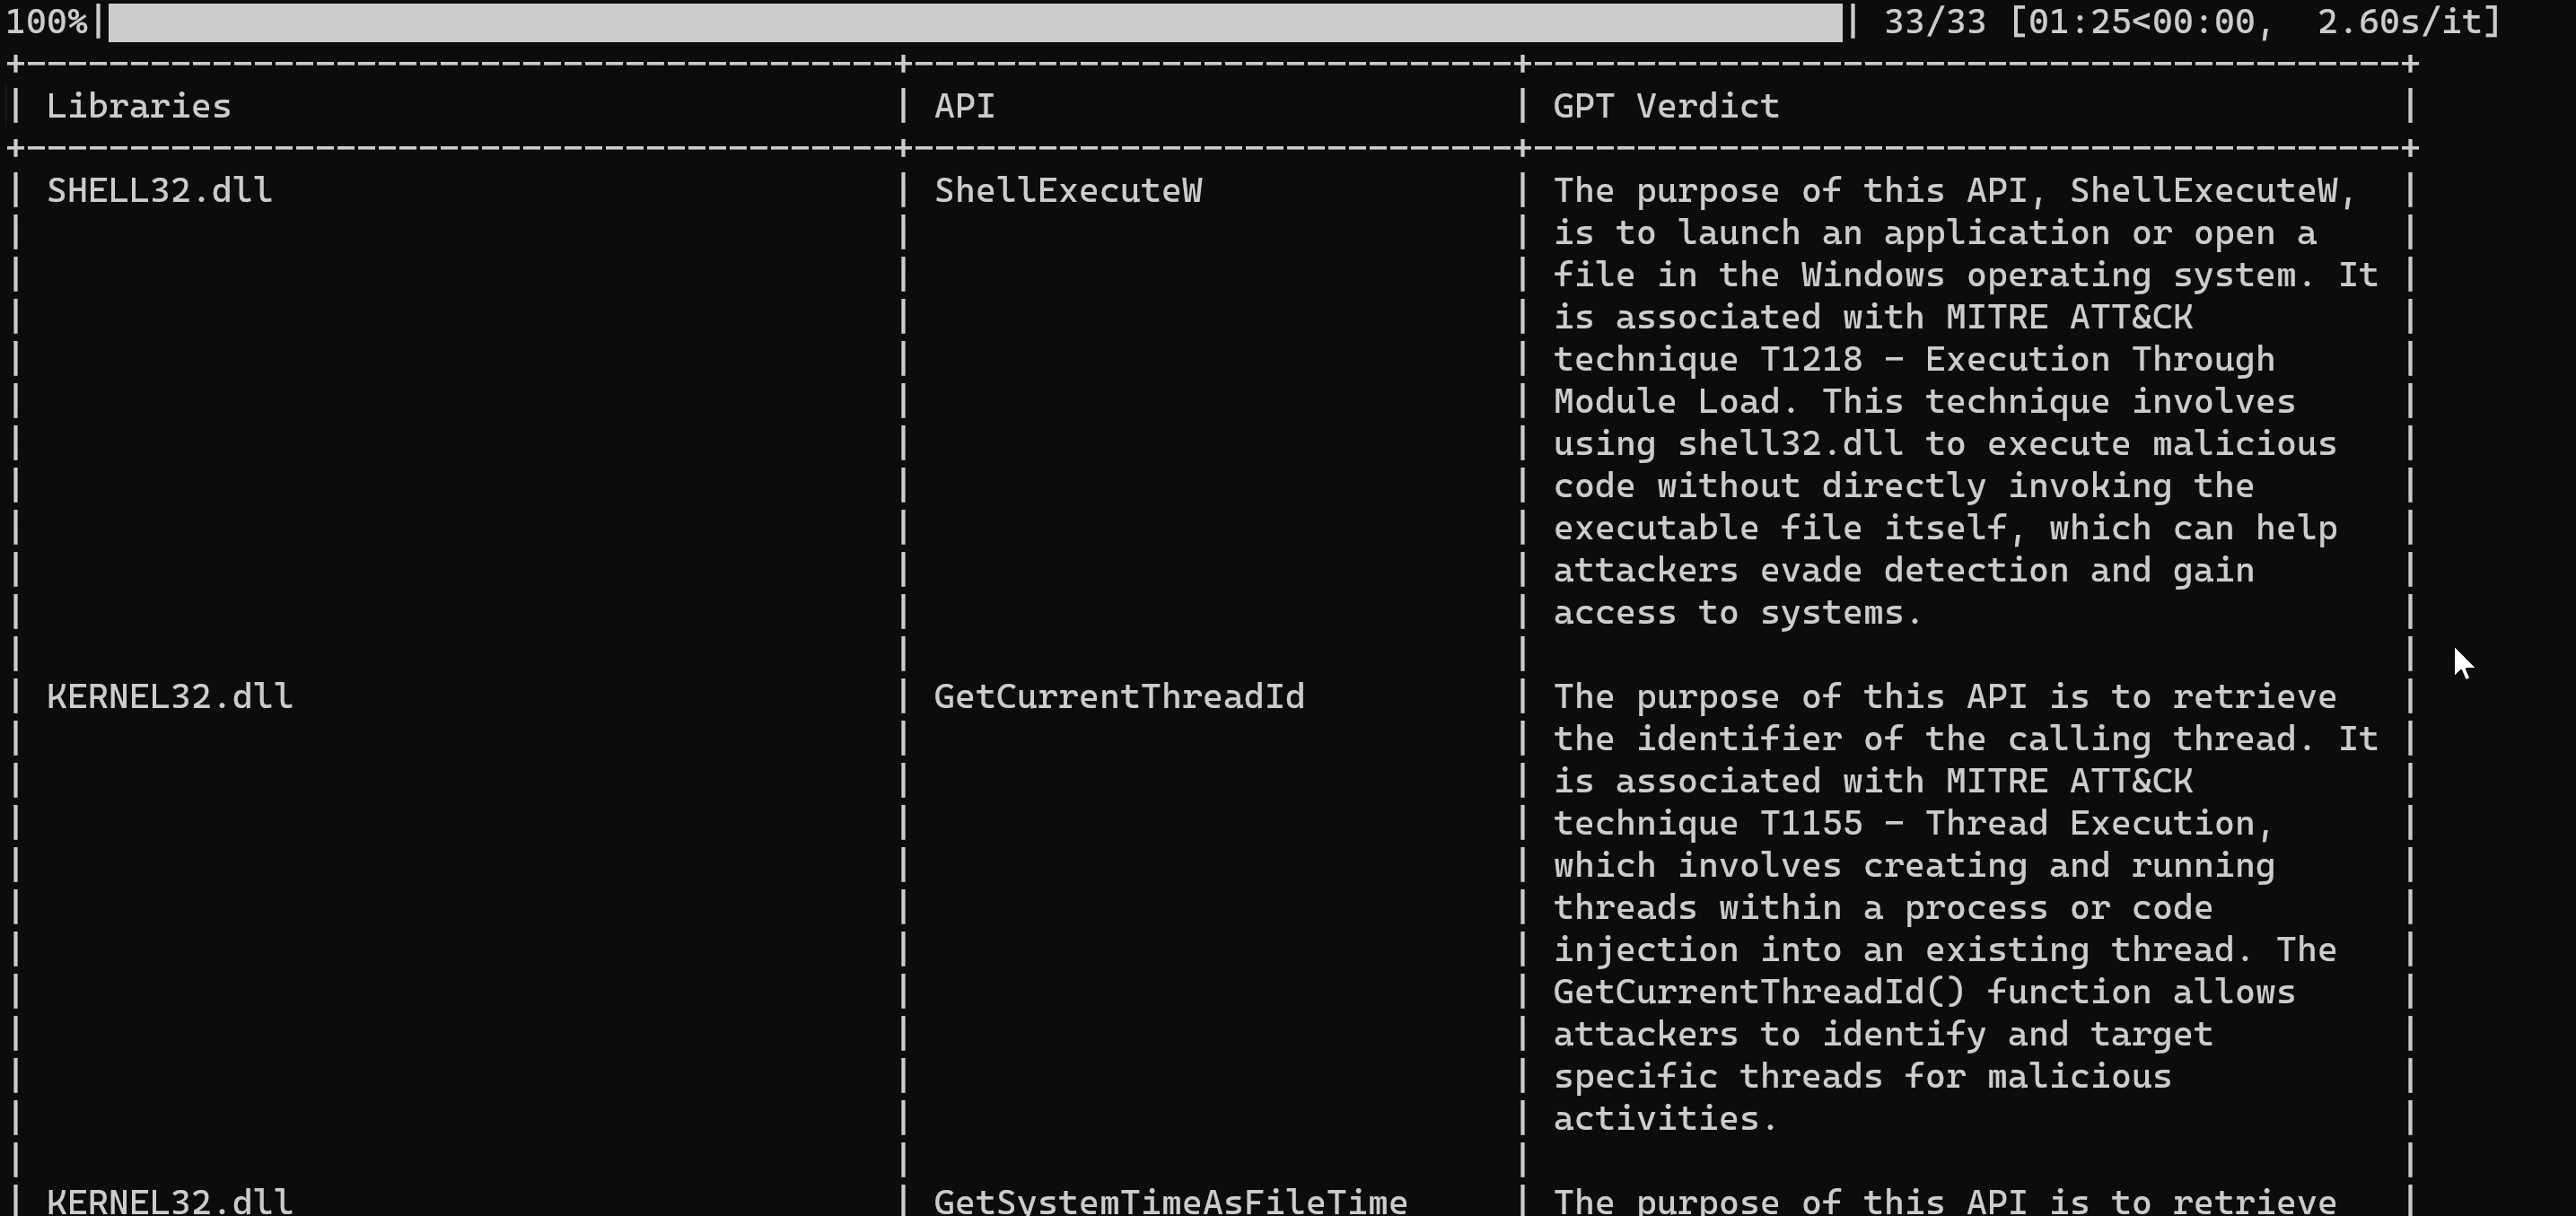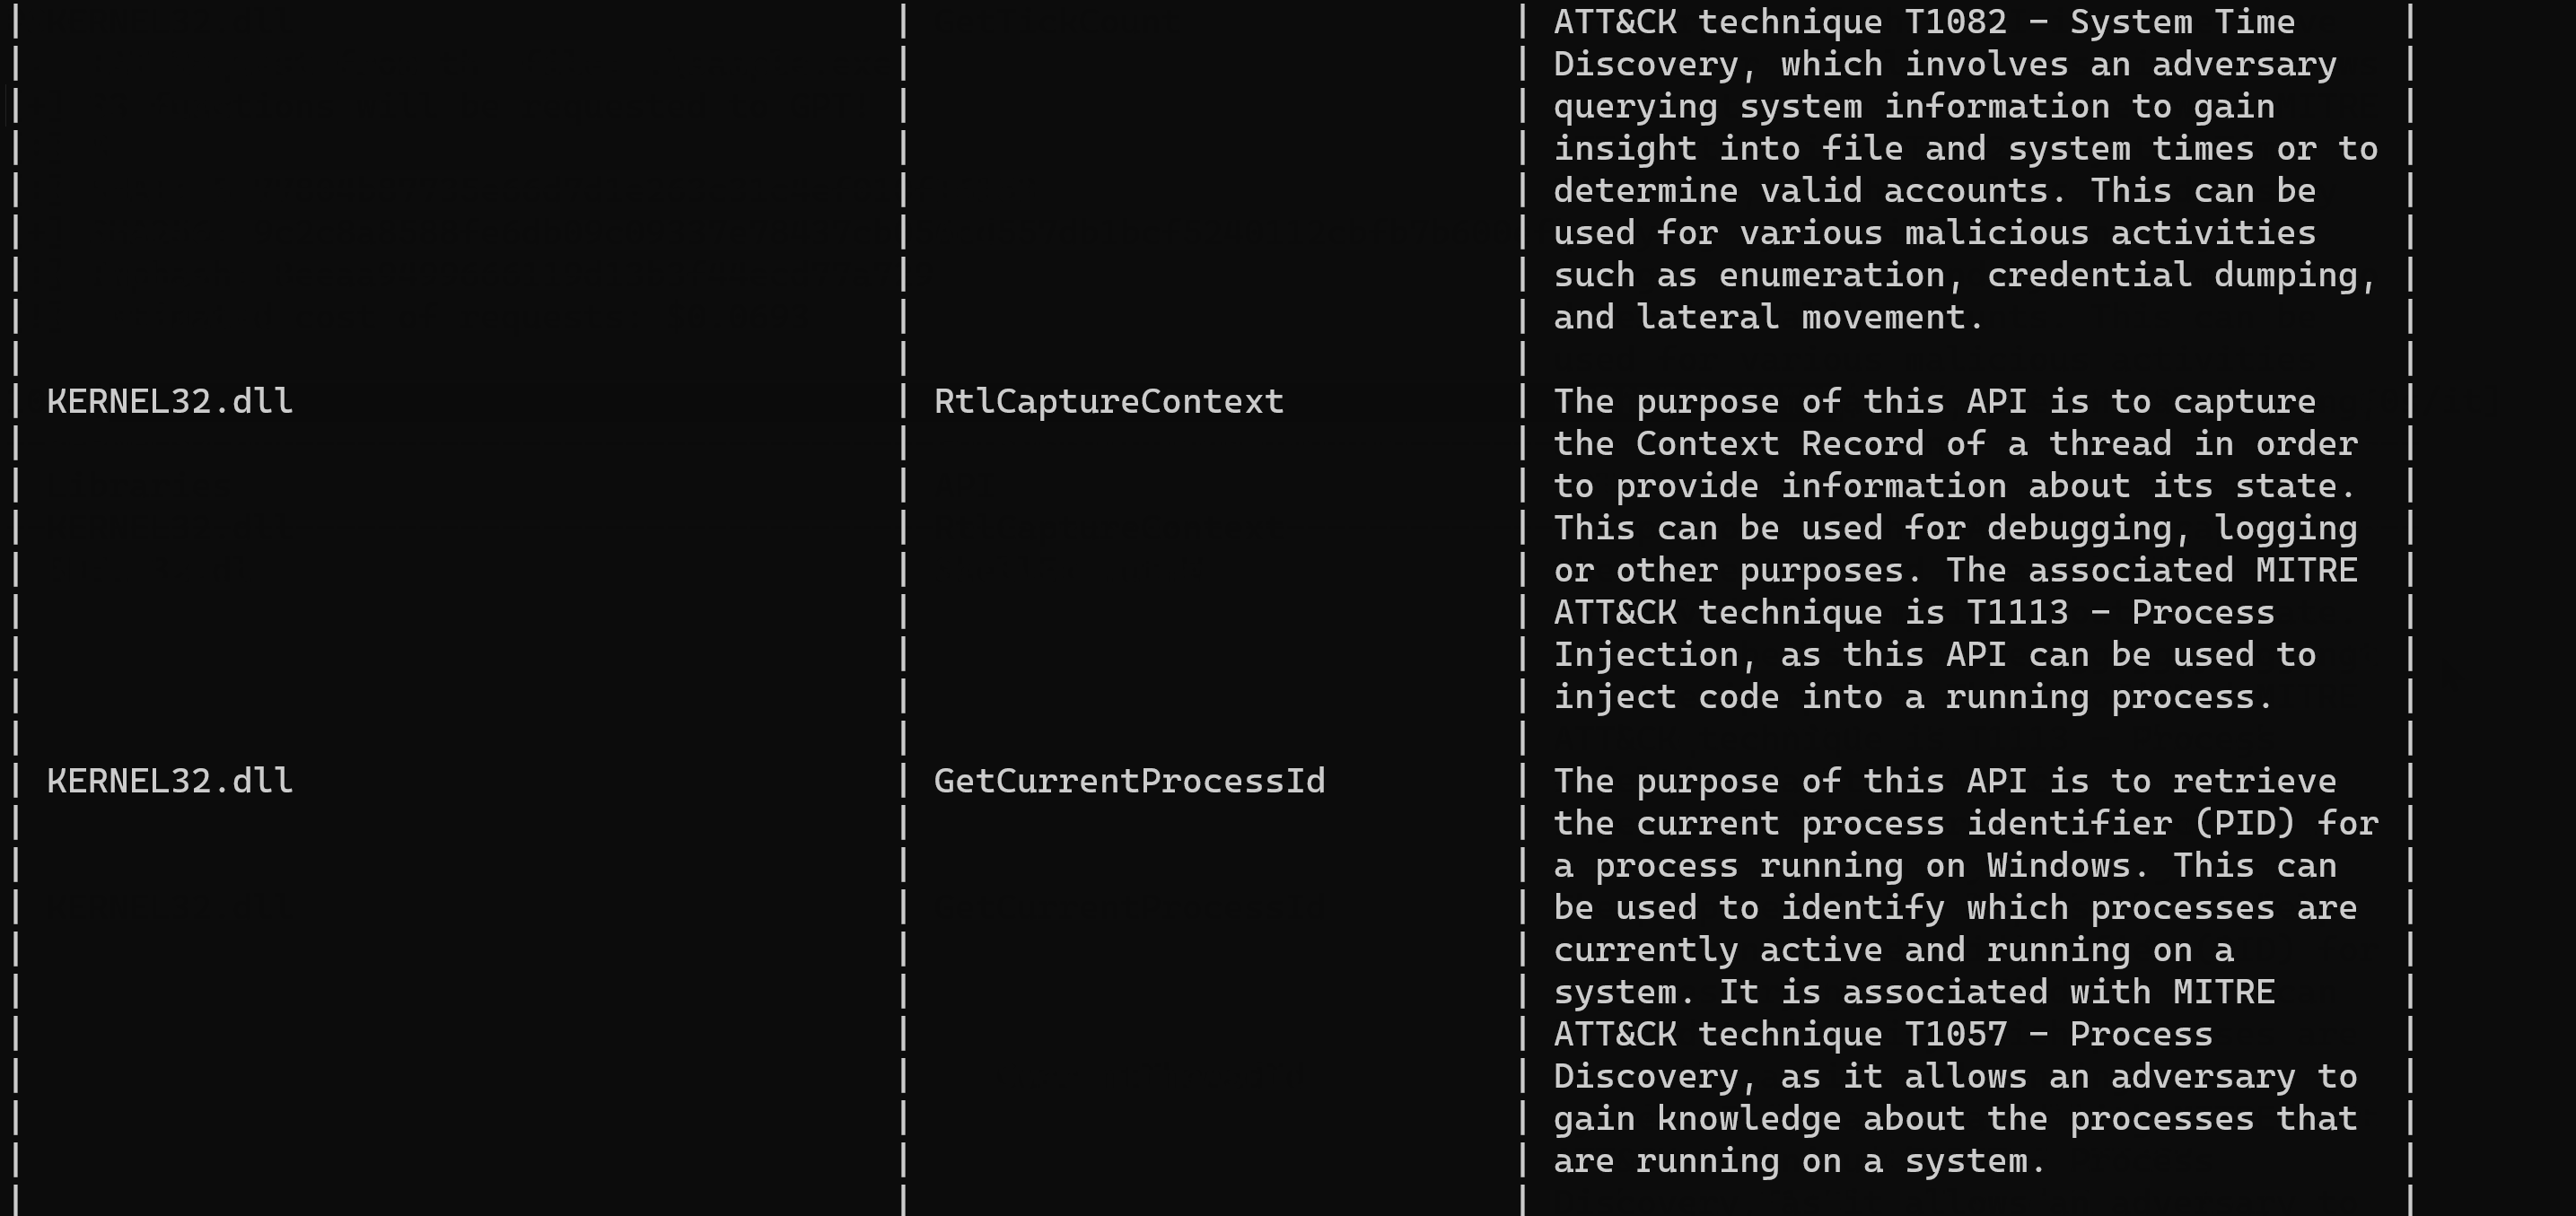
O resultado pode ser visualizado em uma tabela. Abaixo está um extrato truncado.
+------------------------------------------+-----------------------------+------------------------------------------+
| Libraries                                | API                         | GPT Verdict                              |
+------------------------------------------+-----------------------------+------------------------------------------+
| SHELL32.dll                              | ShellExecuteW               | The purpose of this API, ShellExecuteW,  |
|                                          |                             | is to launch an application or open a    |
|                                          |                             | file in the Windows operating system. It |
|                                          |                             | is associated with MITRE ATT&CK          |
|                                          |                             | technique T1218 - Execution Through      |
|                                          |                             | Module Load. This technique involves     |
|                                          |                             | using shell32.dll to execute malicious   |
|                                          |                             | code without directly invoking the       |
|                                          |                             | executable file itself, which can help   |
|                                          |                             | attackers evade detection and gain       |
|                                          |                             | access to systems.                       |
|                                          |                             |                                          |
| KERNEL32.dll                             | GetCurrentThreadId          | The purpose of this API is to retrieve   |
|                                          |                             | the identifier of the calling thread. It |
|                                          |                             | is associated with MITRE ATT&CK          |
|                                          |                             | technique T1155 - Thread Execution,      |
|                                          |                             | which involves creating and running      |
|                                          |                             | threads within a process or code         |
|                                          |                             | injection into an existing thread. The   |
|                                          |                             | GetCurrentThreadId() function allows     |
|                                          |                             | attackers to identify and target         |
|                                          |                             | specific threads for malicious           |
|                                          |                             | activities.                              |
|                                          |                             |                                          |
| KERNEL32.dll                             | GetSystemTimeAsFileTime     | The purpose of this API is to retrieve   |
|                                          |                             | the current system time as a file time   |
|                                          |                             | format. It is associated with the MITRE  |
|                                          |                             | ATT&CK technique T1124 - System Time     |
|                                          |                             | Discovery, which is used by adversaries  |
|                                          |                             | to gain insight into when certain        |
|                                          |                             | activities occurred or are scheduled to  |
|                                          |                             | occur. This allows them to perform       |
|                                          |                             | timing-based attacks and evade           |
|                                          |                             | detection.                               |
|                                          |                             |                                          |
| KERNEL32.dll                             | GetTickCount                | The purpose of this API is to retrieve   |
|                                          |                             | the number of milliseconds since Windows |
|                                          |                             | was started. It is associated with MITRE |
|                                          |                             | ATT&CK technique T1082 - System Time     |
|                                          |                             | Discovery, which involves an adversary   |
|                                          |                             | querying system information to gain      |
|                                          |                             | insight into file and system times or to |
|                                          |                             | determine valid accounts. This can be    |
|                                          |                             | used for various malicious activities    |
|                                          |                             | such as enumeration, credential dumping, |
|                                          |                             | and lateral movement.                    |
|                                          |                             |                                          |
| KERNEL32.dll                             | RtlCaptureContext           | The purpose of this API is to capture    |
