
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit 추천

 corazawaf/coraza
Go 기반의 ModSecurity SecLang 규칙 및 OWASP Core Rule Set v4와 호환되는 웹 애플리케이션 방화벽 라이브러리로, 웹 애플리케이션 및 API를 위한 실시간 HTTP 트래픽 검사 및 공격 차단 기능을 제공합니다.
 wpscanteam/wpscan
취약점을 탐지하고 플러그인/테마/사용자를 열거하며 약한 비밀번호를 점검하는 WordPress 보안 스캐너입니다. 실시간 취약점 데이터를 위해 WPScan API와 통합됩니다.
 projectdiscovery/katana
A next-generation crawling and spidering framework.
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 hahwul/dalfox
매개변수 분석, WAF 핑거프린팅, DOM/AST 검증을 갖춘 빠른 XSS 스캐너. CLI, 파이프라인 또는 REST API를 통해 반사형, 저장형, DOM 기반 XSS 탐지를 지원합니다.
 hahwul/gori
터미널을 위한 빠르고 키보드 중심의 HTTP 인터셉팅 프록시 및 해킹·펜테스팅 툴킷.
sqlmapproject/sqlmap자동 SQL 인젝션 및 데이터베이스 탈취 도구
 zaproxy/zaproxy
자동 취약점 탐지, 수동 침투 테스트, 그리고 프록시 기반 가로채기 엔진을 이용한 API 보안 테스트를 위한 오픈소스 웹 애플리케이션 보안 스캐너입니다.
 pig-tail/security-research
PoCs & write-ups for CVEs I reported (coordinated disclosure; published + patched only)
 nxploited/cve-2026-114509
Laravel TokenGuard의 비문자열 API 자격 증명을 통한 인증 우회
 mr-xn/penetration_testing_poc
침투 테스트와 관련된 POC, EXP, 스크립트, 권한 상승, 소형 도구 등---About penetration-testing python-script poc getshell csrf xss cms php-getshell domainmod-xss…
 projectdiscovery/nuclei
빠른 YAML 기반 취약점 스캐너로, 템플릿 기반 탐지 엔진을 통해 웹 애플리케이션, API, 네트워크, DNS, 클라우드 인프라 전반에 걸친 자동화된 보안 테스트를 수행합니다.
 keygraphhq/shannon
Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…
 commixproject/commix
Automated Αll-in-One OS command injection exploitation tool.
 ghosttroops/top
TOP All bugbounty pentesting CVE-2023- POC Exp RCE example payload Things
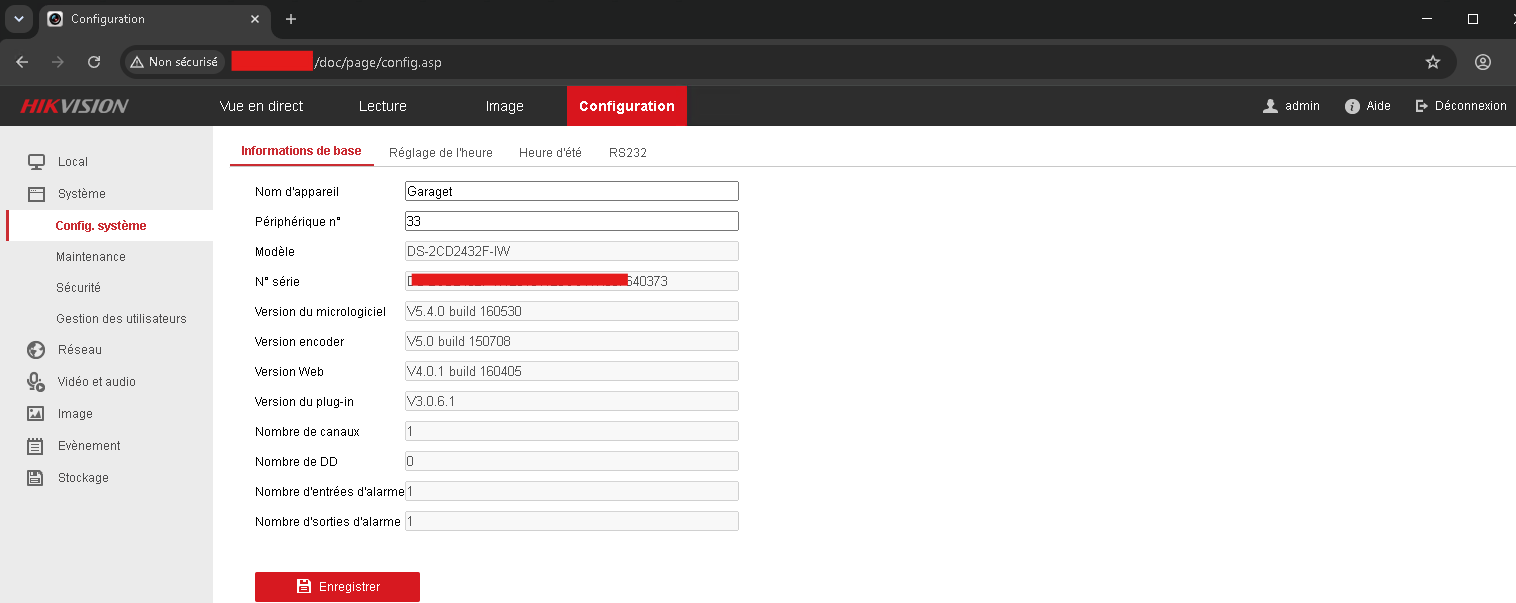 xjghnxhlh/hikihack
Hikvision CVE-2017-7921 해킹
 deathshotxd/cve-2025-52691-apt-poc
CVE-2025-52691(SmarterMail 임의 파일 업로드 RCE)에 대한 향상된 개념 증명(PoC) 익스플로잇으로, 스텔스 난독화, 지속성, 데이터 유출, 대화형 모드와 같은 APT급 기능을 포함합니다. 교육 및 승인된 테스트 용도로만 사용하십시오. 원본…





