Skip to content
KitploitKITPLOIT
StrumentiExploitsBlog
Log in
Invia
StrumentiExploitsBlog
Invia

Strumenti di Hacking, PenTest e Cybersecurity per il tuo Arsenale di Sicurezza!

Kitploit è una directory di strumenti di hacking, cybersecurity e pentesting. Scopri gli ultimi aggiornamenti dei progetti per trovare vulnerabilità, analizzare sistemi, automatizzare i test e rafforzare la tua sicurezza.

FeedContattoPrivacy© 2026 Kitploit

Directory degli strumenti

Categorie

Vedi tutte le categorie
Loading categories
kingfisher — Rileva i segreti. Convalidali in tempo reale. Mappa il raggio d'impatto. Revoca rapidamente. Esegui la CLI o integra in Rust, Python o Node.js. | Kitploit
Strumenti/GitHubGitHub/mongodb/kingfisher
Analisi StaticaScanner di VulnerabilitàSicurezza dei ContenitoriAnalisi Dinamica del Codice (DAST)Raccolta InformazioniSicurezza CloudDevSecOpsUtilità e FrameworkRilevamento SegretiSicurezza della Supply Chain
GitHubmongodb/kingfisher

kingfisher

Rileva i segreti. Convalidali in tempo reale. Mappa il raggio d'impatto. Revoca rapidamente. Esegui la CLI o integra in Rust, Python o Node.js.

Vedi RepositorySito web
1.3k1261783 giorni faRevisionato da Kitploit
Condividi
Contenuto non disponibile nella lingua richiesta. Visualizzazione della versione inglese.

Detect and Validate Secrets Anywhere. Map Access. Revoke Fast.

Kingfisher Logo
Apache 2.0 License Container downloads
GitHub downloads PyPI downloads

Find leaked secrets. Validate what’s live. Map the blast radius. Revoke fast.

Kingfisher is a fast, free, open-source secret scanner and credential response tool built in Rust. It detects leaked secrets with hundreds of built-in rules, validates which credentials are active, maps access for supported credential types, and revokes supported secrets—all in one Apache-2.0-licensed release:

Detect → Validate → Map → Triage → Revoke

  • scan source code, Git history, cloud storage, container images, archives, and developer platforms
  • validate which credentials are active
  • map a leaked secret's identity, permissions, and reachable resources
  • triage findings in a browser, or output as SARIF, JSON, TOON
  • send real-time alerts to Slack, Microsoft Teams, Discord, Mattermost, Google Chat, or any JSON webhook
  • revoke supported secrets

Defender workflow: Follow the end-to-end defender workflow for secret detection, validation, notifications, blast-radius mapping, and revocation.

Embed Kingfisher in Python, Node.js, or Rust

Add native secret detection, live credential validation, and explicit revocation to your Python, JavaScript/TypeScript (Node.js), or Rust application. The same Rust engine and rule catalog run in-process, with no CLI subprocess required. Kingfisher is an embeddable secret scanner that also runs as a standalone CLI.
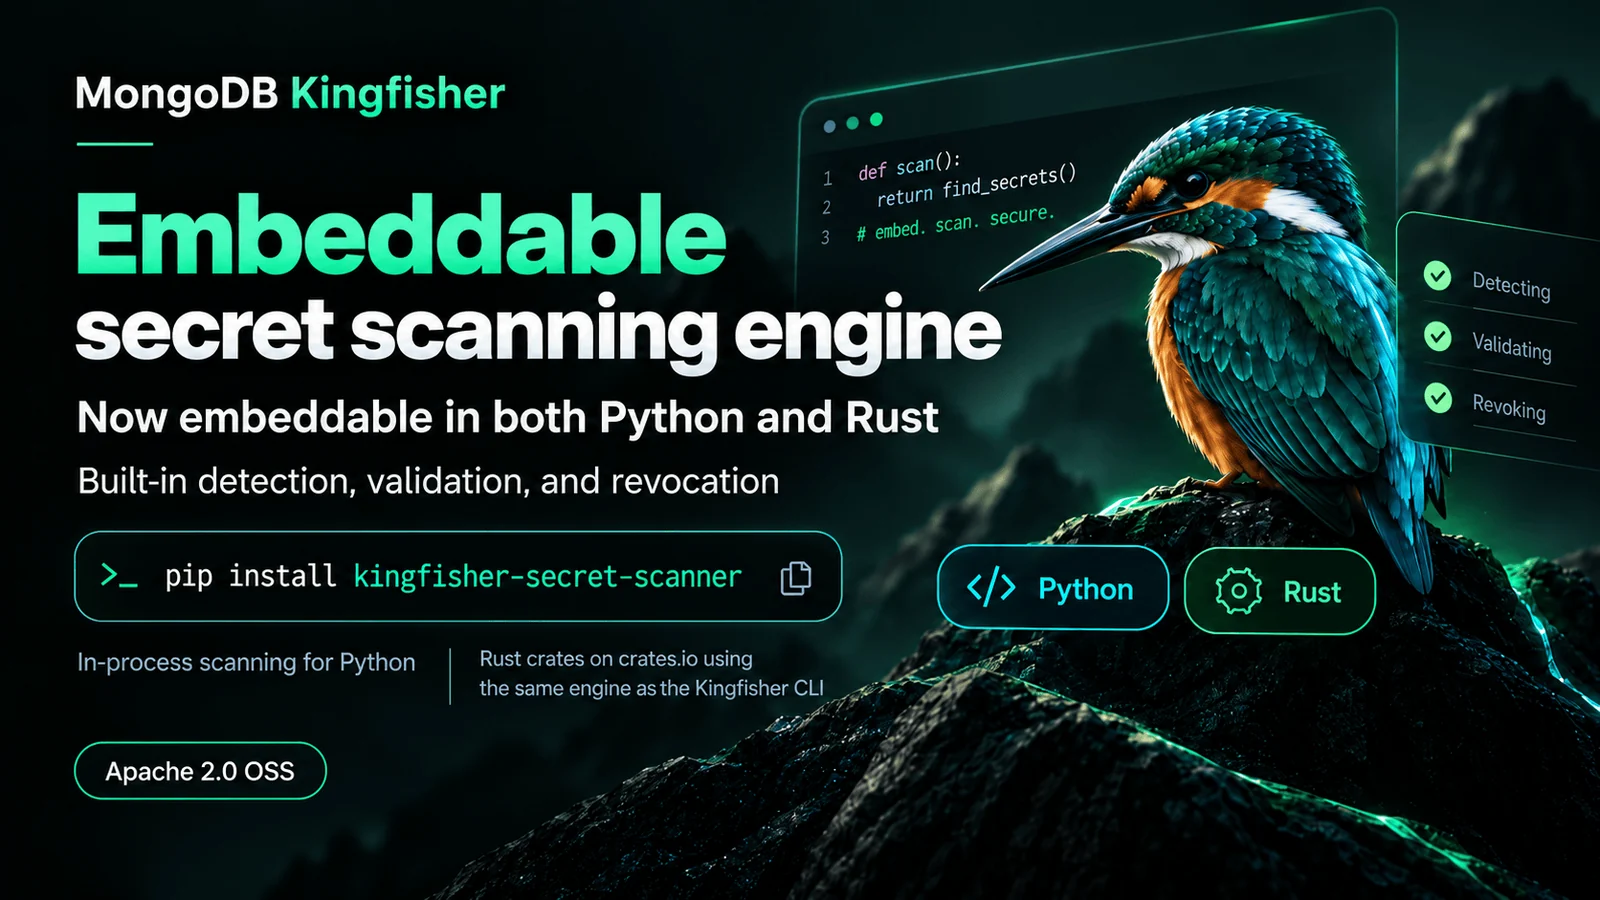
Kingfisher embeddable secret scanner: Detect Secrets → Validate → Map Blast Radius → Revoke. Native Python, Node.js/TypeScript and Rust SDK installs, plus CLI installation and HTML report commands.

Choose your language and add the SDK to your existing application:

  • Python:

    uv add kingfisher-secret-scanner
    

    Import kingfisher_sdk. See the Python SDK guide and runnable examples for scanning, validation, rule inspection, and explicit revocation.

  • Node.js / TypeScript:

    npm install kingfisher-secret-scanner
    

    The stable npm SDK 1.0.0 wraps the same Rust crates with napi-rs. See the Node SDK guide and source/examples. It targets Node.js, including VS Code workspace extensions, rather than browser/WASM runtimes. Explore Kingfisher Workbench, a commented showcase with live progress, Git-history scanning and a redacted HTML report, or start with the runnable recipe walkthrough; maintainers can follow the npm trusted-publishing setup.

  • Rust:

    cargo add kingfisher-scanner --features validation
    

    The validation feature enables live validation and revocation; omit --features validation for detection only. See the library guide, runnable examples, and revocation guide.

Or install the CLI, scan a codebase, and open the interactive HTML report:

uv tool install kingfisher-bin
kingfisher scan /path/to/code --view-report

Replace /path/to/code with your source directory. Scans validate credentials by default; add --no-validate for detection only. Add --blast-radius to map supported credentials' access when authorized. Revocation remains a separate, explicit action. See the CLI installation guide and usage guide for more options.

Scan Targets

Kingfisher handles local files and directories, Git repositories and history, compressed and office-document archives, SQLite databases, Python bytecode, Docker images, source-hosting organizations, cloud object storage, collaboration tools, and API-development platforms.

Files / DirsLocal GitGitHubGitLabAzure ReposBitbucketGiteaHugging Face
Files / Dirs
Files / Dirs
Local Git
Local Git
GitHub
GitHub
GitLab
GitLab
Azure Repos
Azure Repos
Bitbucket
Bitbucket
Gitea
Gitea
Hugging Face
Hugging Face
Scarica lo strumento

Più Popolari

Vedi tutti →

Scopri gli strumenti più utilizzati dalla nostra community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 Il toolkit OSINT definitivo: grafo di indagine, punteggio di affidabilità, famiglie di alias, mappa, timeline e report. 49 moduli, oltre 400 siti, nessuna chiave API richiesta.

    930
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # App di esecuzione con un tocco GhostLock (CVE-2026-43499)

    554
  • 3

    redforge

    cybersecurity91/redforge

    Toolkit red team lato browser con 102 strumenti offline per ricognizione, generazione di payload, attacchi alle credenziali, crittografia, codifica e reportistica dell'engagement.

    354
  • 4

    ARTEX

    baarai/artex

    Piattaforma di penetration testing autonoma multi-agente basata su LLM con agenti planner/worker, grafi di asset e di esplorazione, registrazione del traffico MITM e retesting delle vulnerabilità.

    349
  • 5

    looking-glass

    anonghosty/looking-glass

    Piattaforma CSIRT che importa i report di Shadowserver in MongoDB e li riproduce come mappe interattive, analisi, risultati, avvisi e dashboard executive.

    326
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    Il sistema d'azione per la cybersecurity nativa AI—dove l'intento diventa esecuzione governata, le evidenze diventano memoria operativa, e ogni operazione migliora la successiva.

    289

Esplora tutti gli strumenti

Sfoglia la nostra collezione di strumenti

Vedi tutti gli strumenti →