Skip to content
KitploitKITPLOIT
StrumentiExploitsBlog
Log in
Invia
StrumentiExploitsBlog
Invia

Strumenti di Hacking, PenTest e Cybersecurity per il tuo Arsenale di Sicurezza!

Kitploit è una directory di strumenti di hacking, cybersecurity e pentesting. Scopri gli ultimi aggiornamenti dei progetti per trovare vulnerabilità, analizzare sistemi, automatizzare i test e rafforzare la tua sicurezza.

FeedContattoPrivacy© 2026 Kitploit

Directory degli strumenti

Categorie

Vedi tutte le categorie
Loading categories
shannon — Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes real exploits to prove vulnerabilities before they reach production. | Kitploit
Strumenti/GitHubGitHub/keygraphhq/shannon
ReconnaissanceVulnerability ScannersCode AnalysisExploitationWeb Application ExploitationAPI Security TestingPenetration TestingAI Security
GitHubkeygraphhq/shannon

shannon

Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes real exploits to prove vulnerabilities before they reach production.

46.6k5.4k4626h 39m faRevisionato da Kitploit
Condividi
Vedi Repository
Sito web
Contenuto non disponibile nella lingua richiesta. Visualizzazione della versione inglese.

[!NOTE] Git worktrees, run limits and OpenAI cyber access checks: scan a worktree directly, tune scans for slow model endpoints, and catch missing OpenAI access before a scan starts.
Shannon, AI Pentester for Web Apps and APIs, by Keygraph

KeygraphHQ%2Fshannon | Trendshift

Shannon is an autonomous, AI pentester for web applications and APIs.

It analyzes your source code, identifies attack paths, and executes real exploits to prove vulnerabilities before they reach production. No exploit, no report.

This repository is Shannon: the full open-source agent, run locally from your command line.

Launch Shannon

npx @keygraph/shannon@latest

The interactive launcher will guide you through setup and your first pentest.

Join Discord      Visit Keygraph.io


[!TIP] AI agents and LLMs: start with llms.txt for a concise map of this repository, or use llms-full.txt for the README and docs combined into one file.

Table of Contents

  • Table of Contents
  • What is Shannon?
    • Why Shannon Exists
    • Why "Shannon"?
    • Not a replacement for human pentesters
  • Shannon in Action
  • Quick Start
    • Prerequisites
    • Run Shannon
  • Key Capabilities
  • CI/CD Integrations
    • GitHub Actions
  • Editions
  • Architecture
  • Documentation
  • Safety, Scope, and Limitations
  • License
  • Acknowledgements
  • About Keygraph
  • Community and Support
  • Common Questions
    • Can I self-host Shannon?
    • Does Shannon support bring your own key (BYOK)?
    • Does Shannon output SARIF?
    • Which AI providers does Shannon support?
    • Can I run Shannon on a local or self-hosted model?
    • Does Shannon actually exploit vulnerabilities, or just scan?

What is Shannon?

Shannon is an autonomous AI pentester developed by Keygraph. It performs security testing of web applications and their underlying APIs by combining source-code analysis with live exploitation.

Shannon analyzes your web application's source code to identify potential attack vectors, then uses browser automation and command-line tools to execute real exploits against the running application and its APIs. Only vulnerabilities with a working proof-of-concept are included in the final report.

Shannon is the agent. This repository is Shannon, the open-source pentester you run yourself. The same Shannon also powers Keygraph's commercial editions, Pro and Enterprise. See Editions for how Shannon compares with Pro, Enterprise, and the Community Program.

Why Shannon Exists

Thanks to tools like Claude Code and Cursor, your team ships code non-stop. But your penetration test? That happens once a year. This creates a massive security gap. For the other 364 days, you could be unknowingly shipping vulnerabilities to production.

Shannon closes that gap by providing on-demand, automated penetration testing that can run against every build or release.

Why "Shannon"?

It's named after Claude Shannon, the father of information theory. At its core, pentesting is an information problem: every probe reduces uncertainty about a system's state. The best tools maximize the signal gained from every request, turning those bits of knowledge into an exploit path.

Also, we wanted you to be able to say, "Hey Claude, run Shannon" to find all the security flaws in your vibe-coded app.

Not a replacement for human pentesters

Shannon is built to work alongside expert pentesters and red teamers, not replace them. Great pentesters understand the business, chain attacks in ways nobody anticipated, and bring years of judgment that current models can't match.

Shannon solves a different problem: there is far more software to test than security teams have time to cover. Critical systems get periodic expert assessments, while the long tail of internal apps, APIs, and fast-moving services rarely gets tested at all.

Shannon shifts pentesting left into the software development lifecycle (SDLC). Use it to run exploitation-backed tests against staging environments and releases at the cadence they actually ship, and save expert human time for the risks that need someone who knows the organization.
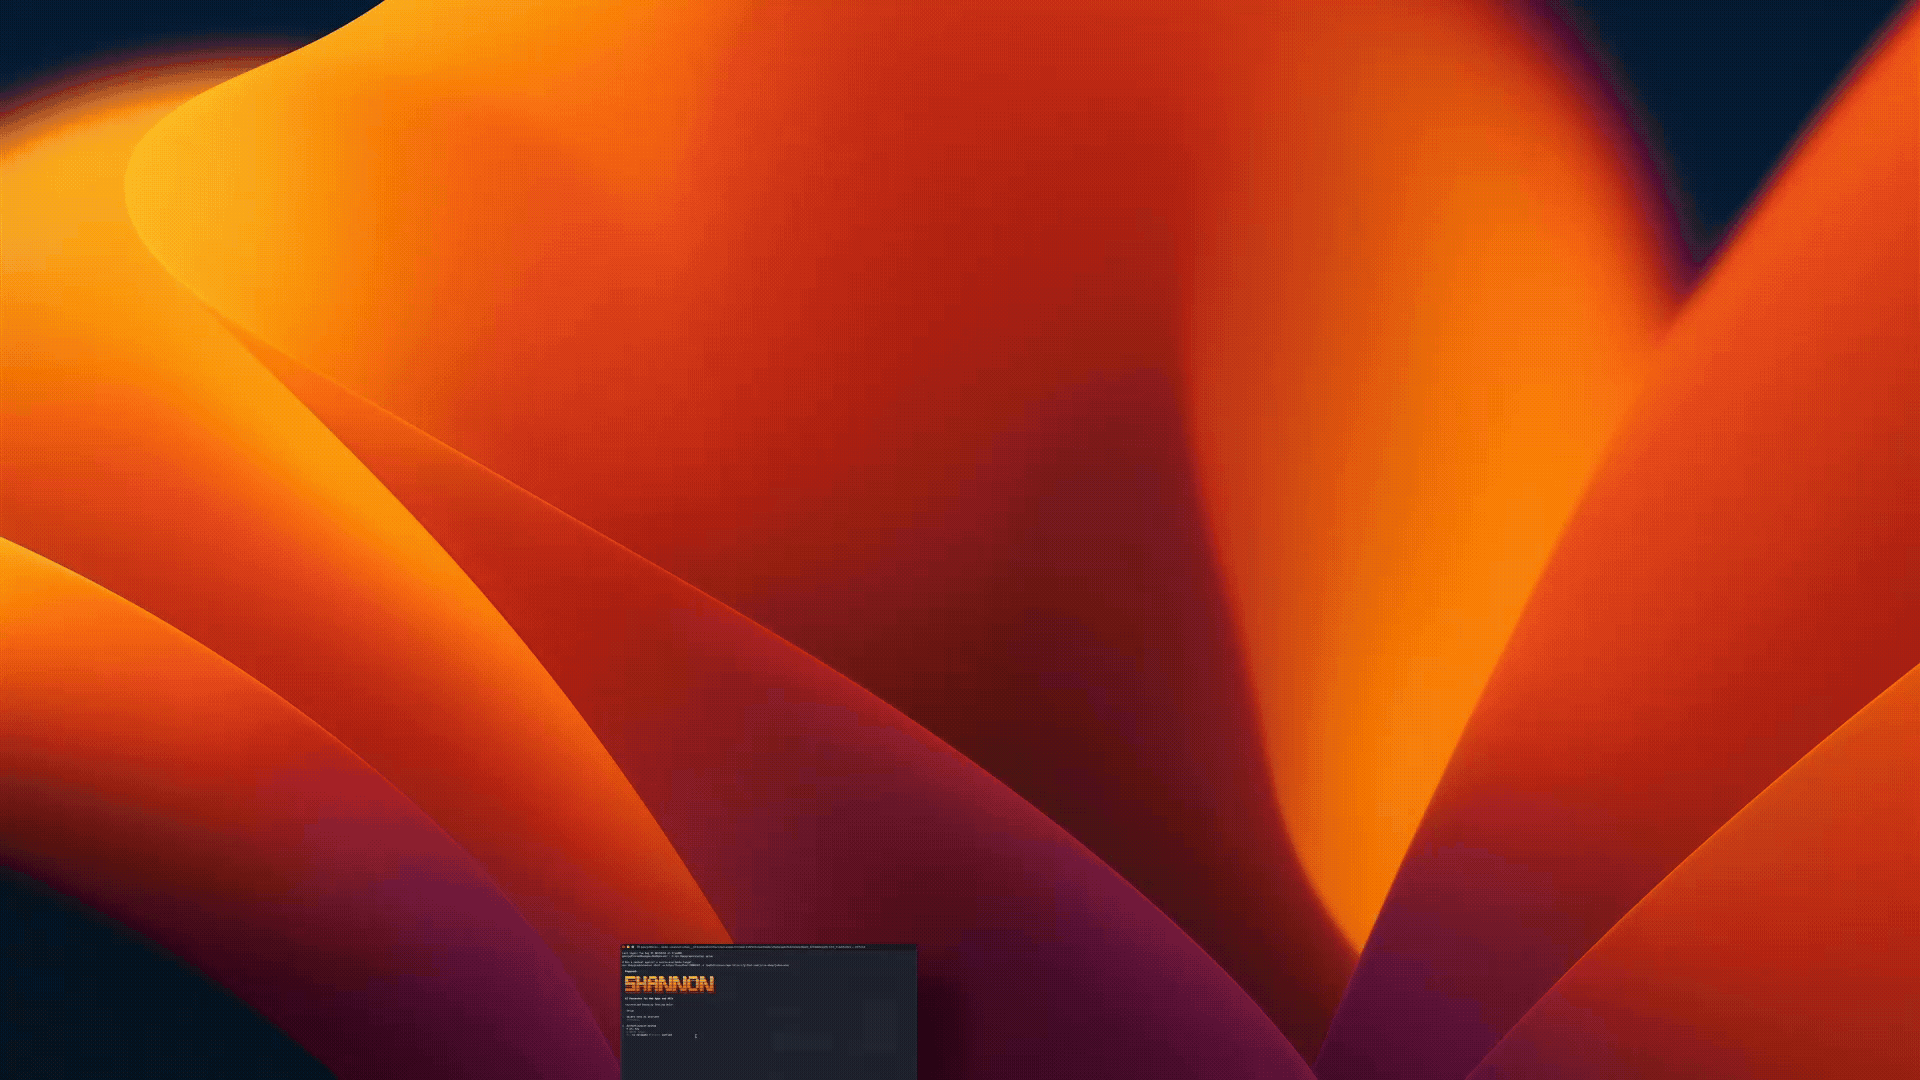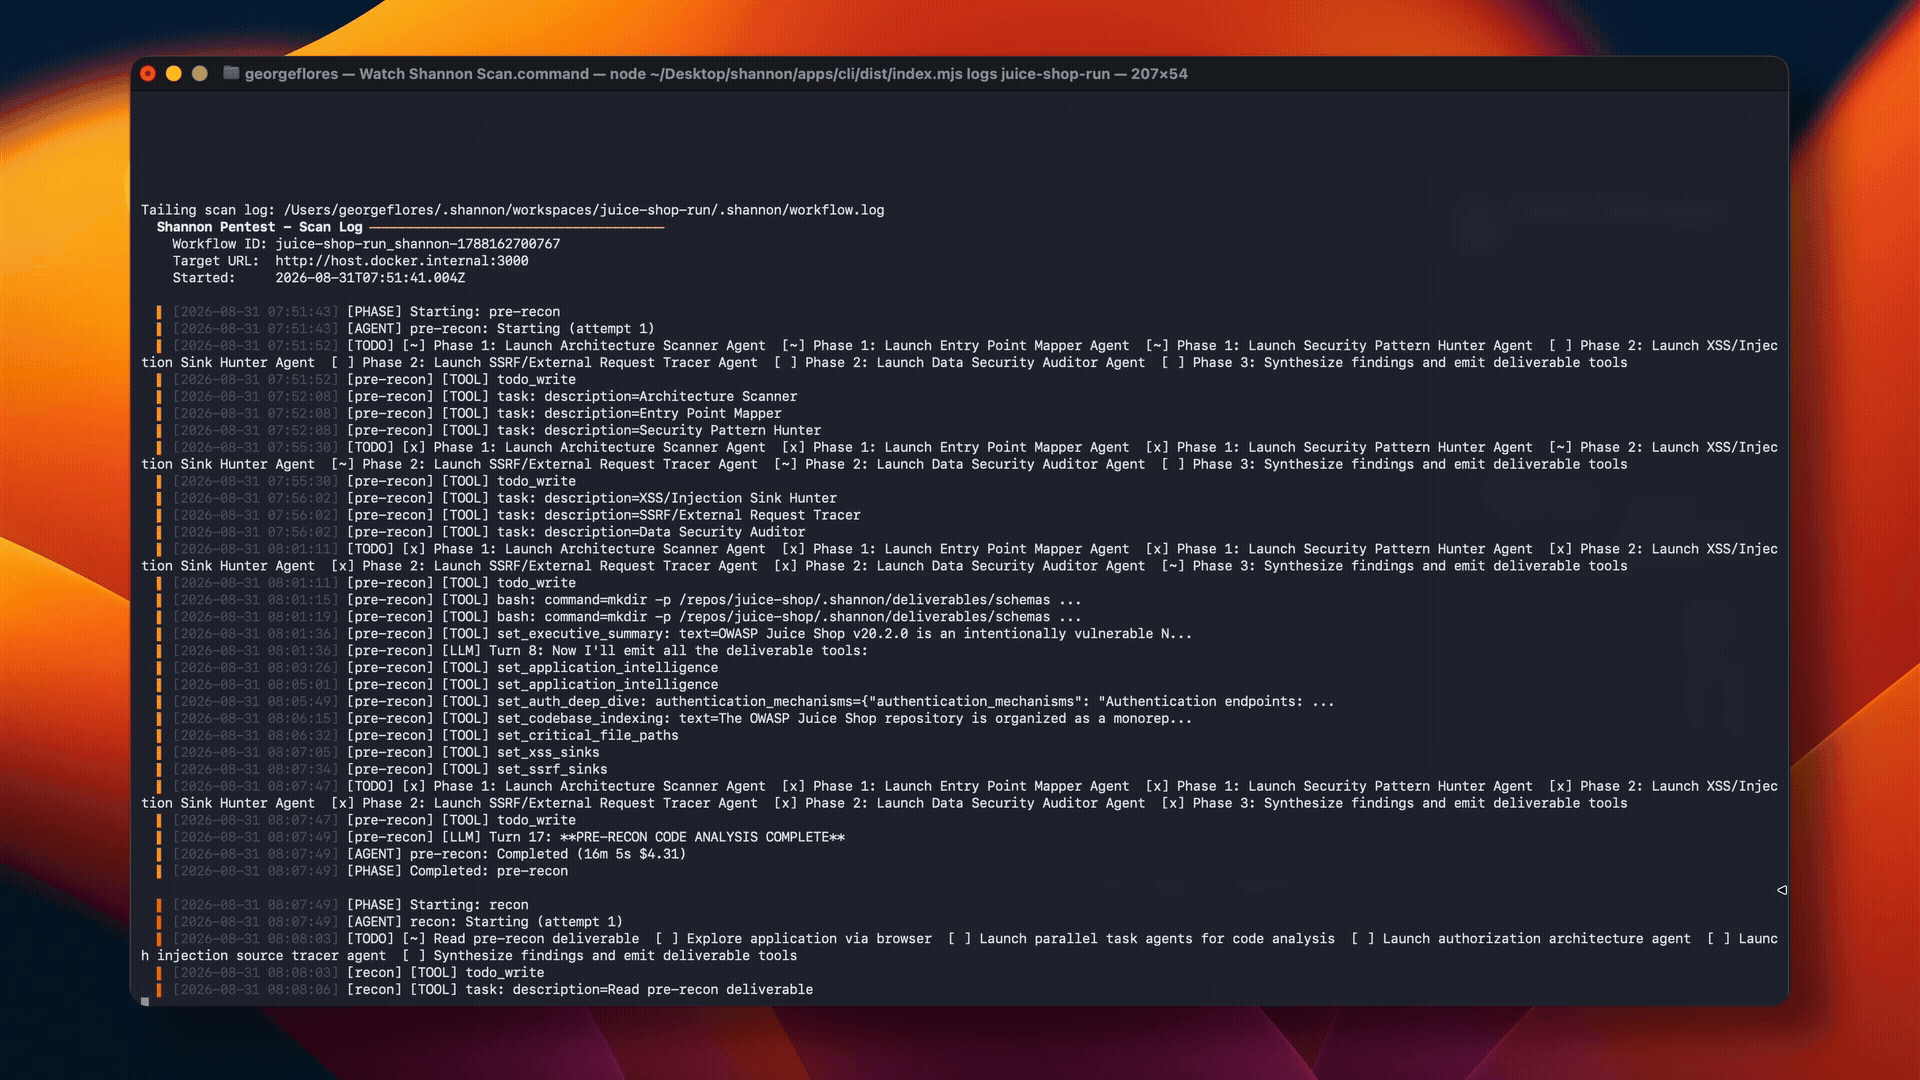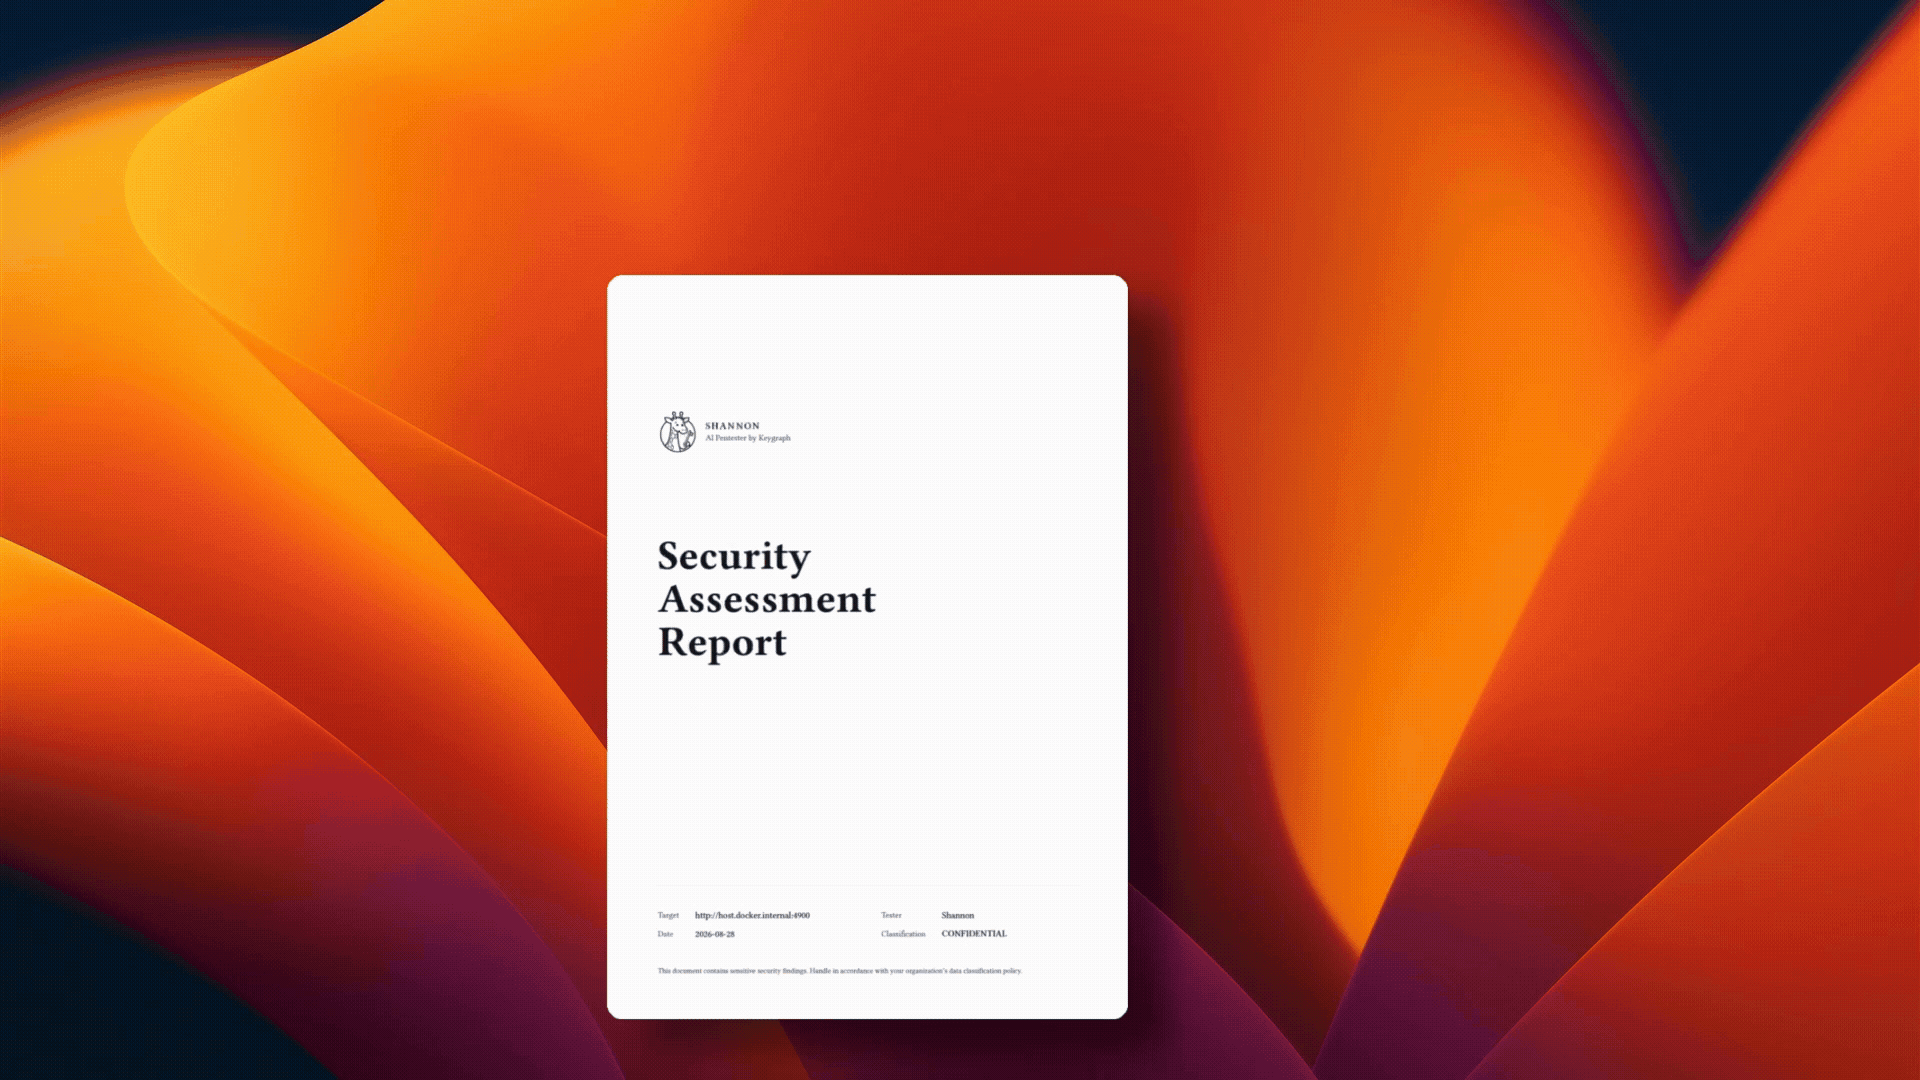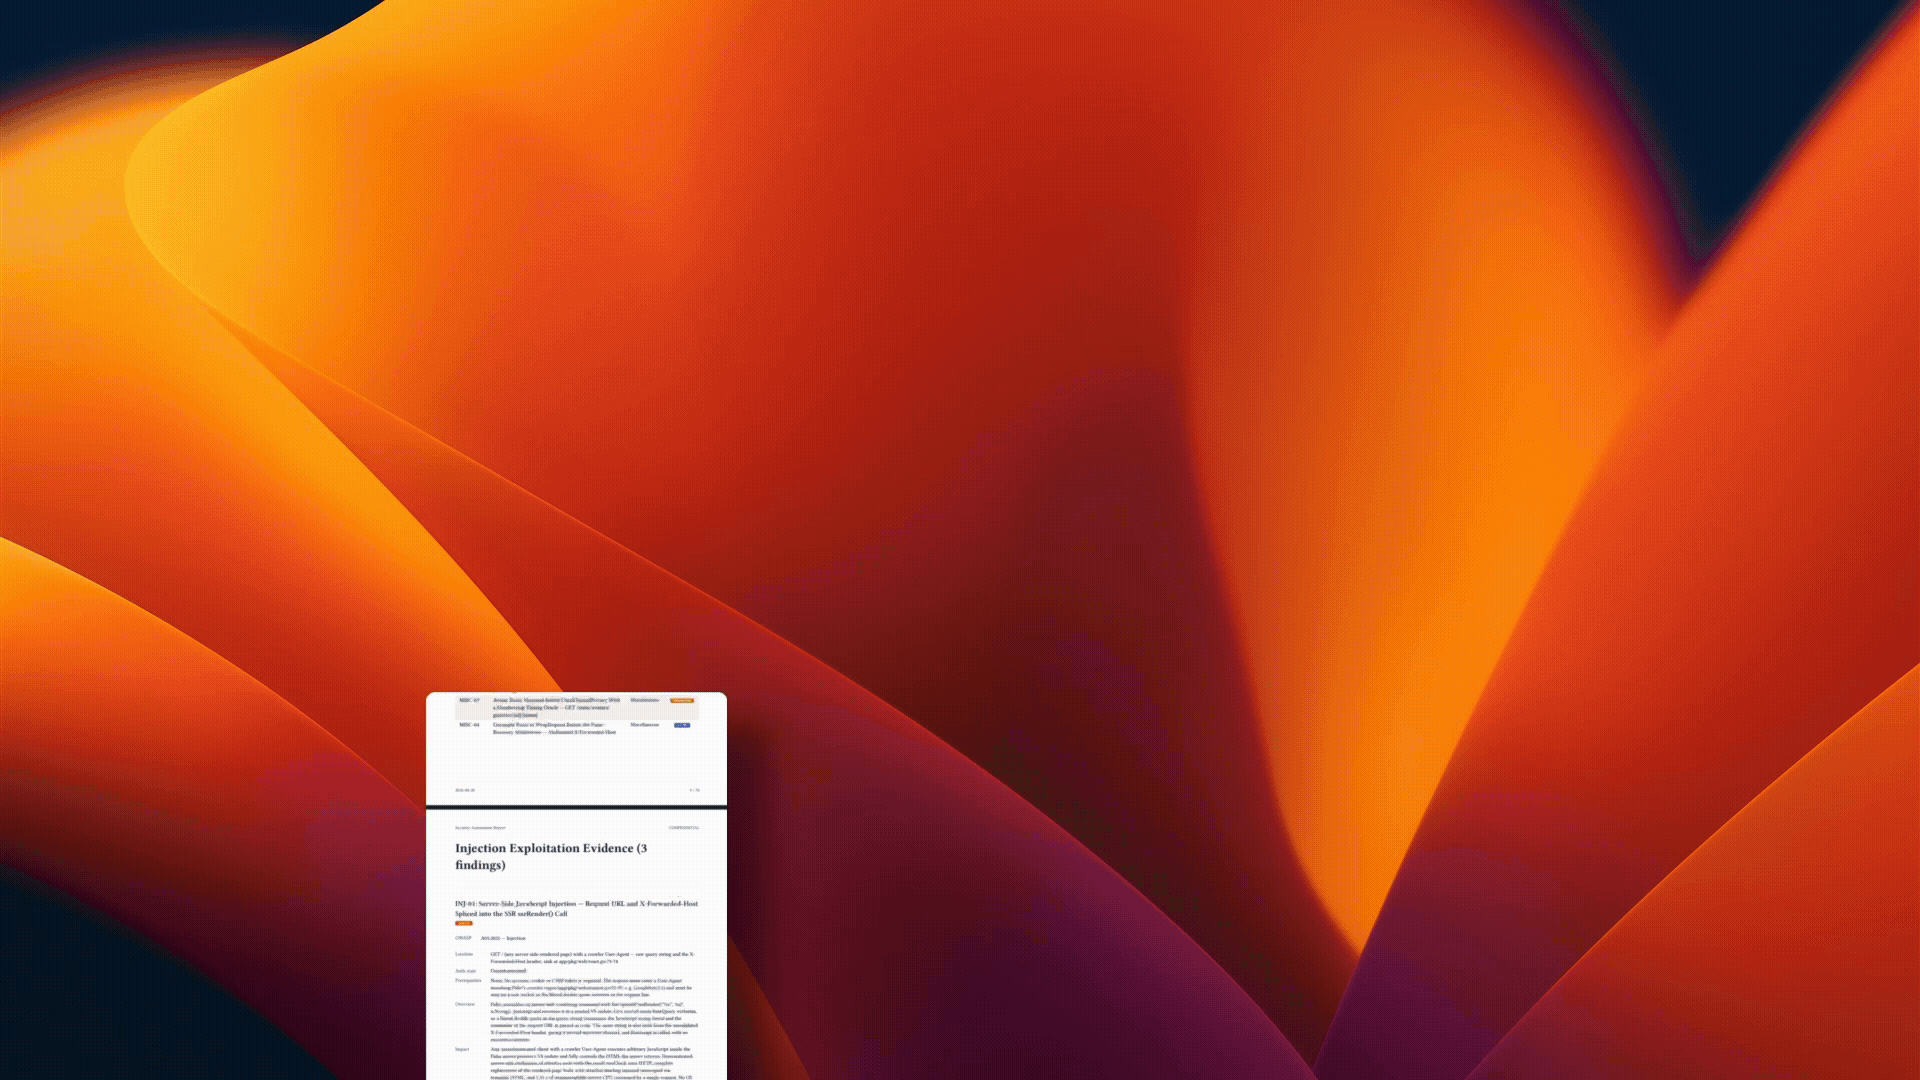
Shannon in Action

Shannon running an autonomous pentest

These reports are from Shannon OSS scans of Photoview 2.4.0, one of the applications in Doyensec's comparison of Aikido and XBOW. We ran Shannon against the same application version and evaluated its results separately. Read the Doyensec study and our Shannon follow-up comparison for the methodology, limitations, costs, and results.


Scarica lo strumento

Più Popolari

Vedi tutti →

Scopri gli strumenti più utilizzati dalla nostra community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 Il toolkit OSINT definitivo: grafo di indagine, punteggio di affidabilità, famiglie di alias, mappa, timeline e report. 49 moduli, oltre 400 siti, nessuna chiave API richiesta.

    1.1k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # App di esecuzione con un tocco GhostLock (CVE-2026-43499)

    603
  • 3

    looking-glass

    anonghosty/looking-glass

    Piattaforma CSIRT che importa i report di Shadowserver in MongoDB e li riproduce come mappe interattive, analisi, risultati, avvisi e dashboard executive.

    390
  • 4

    ARTEX

    baarai/artex

    Piattaforma di penetration testing autonoma multi-agente basata su LLM con agenti planner/worker, grafi di asset e di esplorazione, registrazione del traffico MITM e retesting delle vulnerabilità.

    321
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    Il sistema d'azione per la cybersecurity nativa AI—dove l'intento diventa esecuzione governata, le evidenze diventano memoria operativa, e ogni operazione migliora la successiva.

    301
  • 6

    redforge

    cybersecurity91/redforge

    Toolkit red team lato browser con 102 strumenti offline per ricognizione, generazione di payload, attacchi alle credenziali, crittografia, codifica e reportistica dell'engagement.

    263

Esplora tutti gli strumenti

Sfoglia la nostra collezione di strumenti

Vedi tutti gli strumenti →