gamehunterkaan/autopwn-suite
AutoPWN Suite è un progetto per la scansione delle vulnerabilità e lo sfruttamento automatico dei sistemi.

AutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.


|
|
Security Badges |
Install Nmap (needed for network scans, not for website-only dashboard scans) and AutoPWN Suite with pipx or uv. It needs Python 3.11.5 or newer. See Installation for standalone binaries, Docker and other options:
pipx install autopwn-suite
Scan a host or network that you are authorized to test:
autopwn-suite -t <target ip address>
Or start the web dashboard, then sign in with the admin account whose
random password is printed once in the terminal on first launch:
autopwn-suite --web
Use -h for all options. Report problems through support and
vulnerabilities privately through the security policy.
AutoPWN Suite is an operator-controlled scanner that runs with your privileges and stores integration credentials in plaintext JSON. Scan only systems you are authorized to test, do not expose the dashboard to the public internet, keep it behind HTTPS and trusted network controls, and verify releases before use. See the security policy for reporting, response times and deployment guidance.
The badges at the top show the status that OpenSSF Best Practices project 15518 reports for the Best Practices levels and the OpenSSF Baseline levels. They are updated by OpenSSF, not by this repository. The roadmap lists planned work and non-goals, and the continuity plan describes maintainer succession.
Project documentation: build from source, dependency management, architecture, interfaces, governance, changelog, release verification, and security policy, support lifecycle, threat model, secret management, and security checks, roadmap, access continuity, accessibility and internationalization.
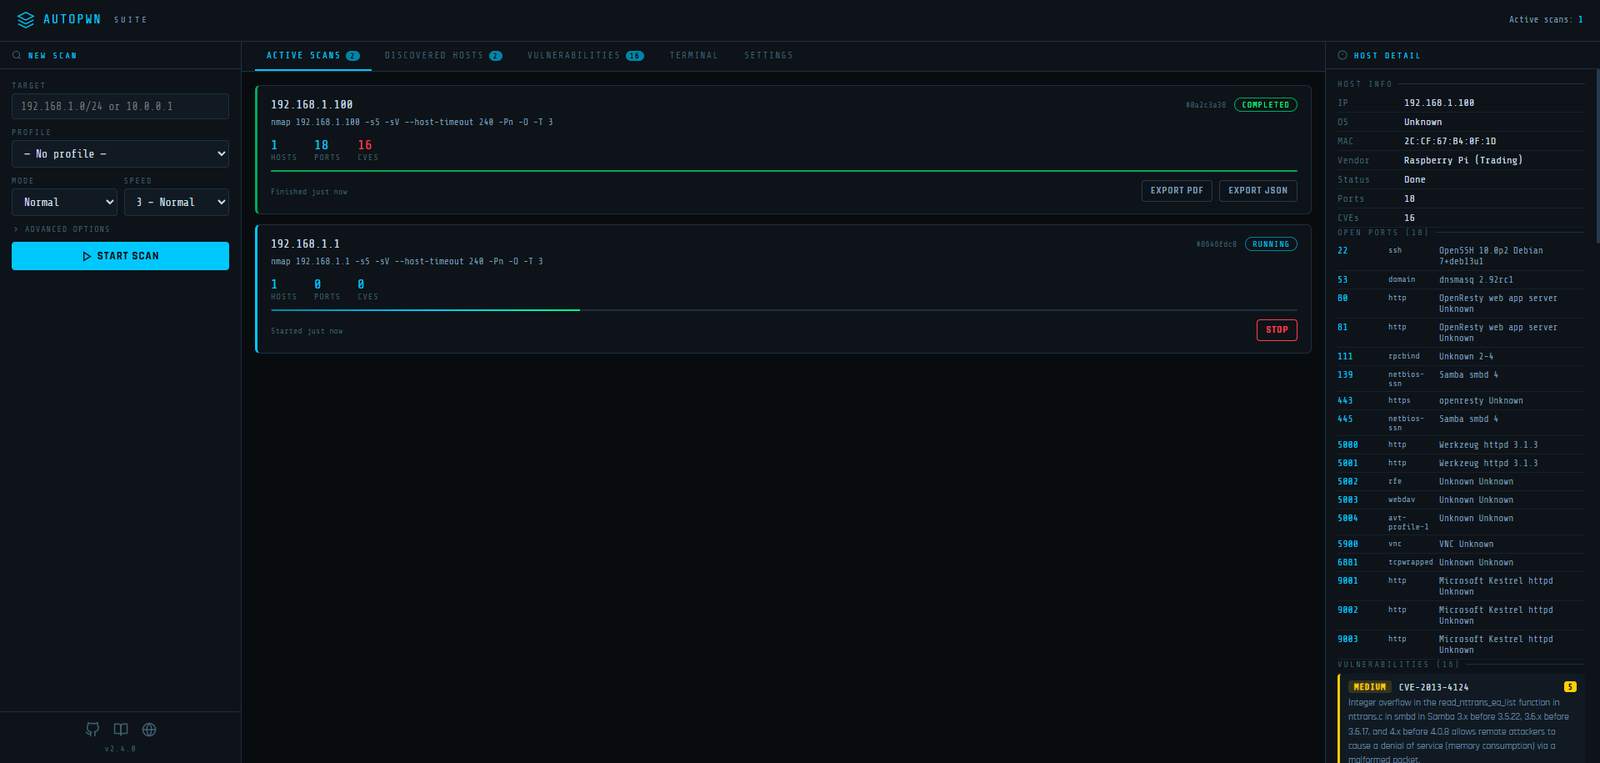
AutoPWN Suite includes a built-in web dashboard for managing scans from your browser.