 cappricio-securities/cve-2022-21500
Oracle E-Business Suite <=12.2 - Bypass dell'autenticazione




Installa Python3 e pip Istruzioni qui (Se non riesci a capirlo, non dovresti usare questo strumento)
pip install CVE-2022-21500
CVE-2022-21500 -hAbbiamo integrato l'API di Telegram per ricevere notifiche istantanee per il rilevamento delle vulnerabilità.
CVE-2022-21500 --chatid <YourTelegramChatID>
@CappricioSecuritiesTools_bot e clicca su startQuesto strumento ha molteplici casi d'uso.
CVE-2022-21500 -u http://example.com
CVE-2022-21500 -i urls.txt
CVE-2022-21500 -i urls.txt -o out.txt
CVE-2022-21500? Allora digita il comando qui sotto
CVE-2022-21500 -b
🚨 Dichiarazione di non responsabilità
Questo strumento è creato per l'identificazione e l'assistenza di bug di sicurezza; Cappricio Securities non è responsabile per qualsiasi uso illegale. Usalo responsabilmente entro i limiti legali ed etici. 🔐🛡️
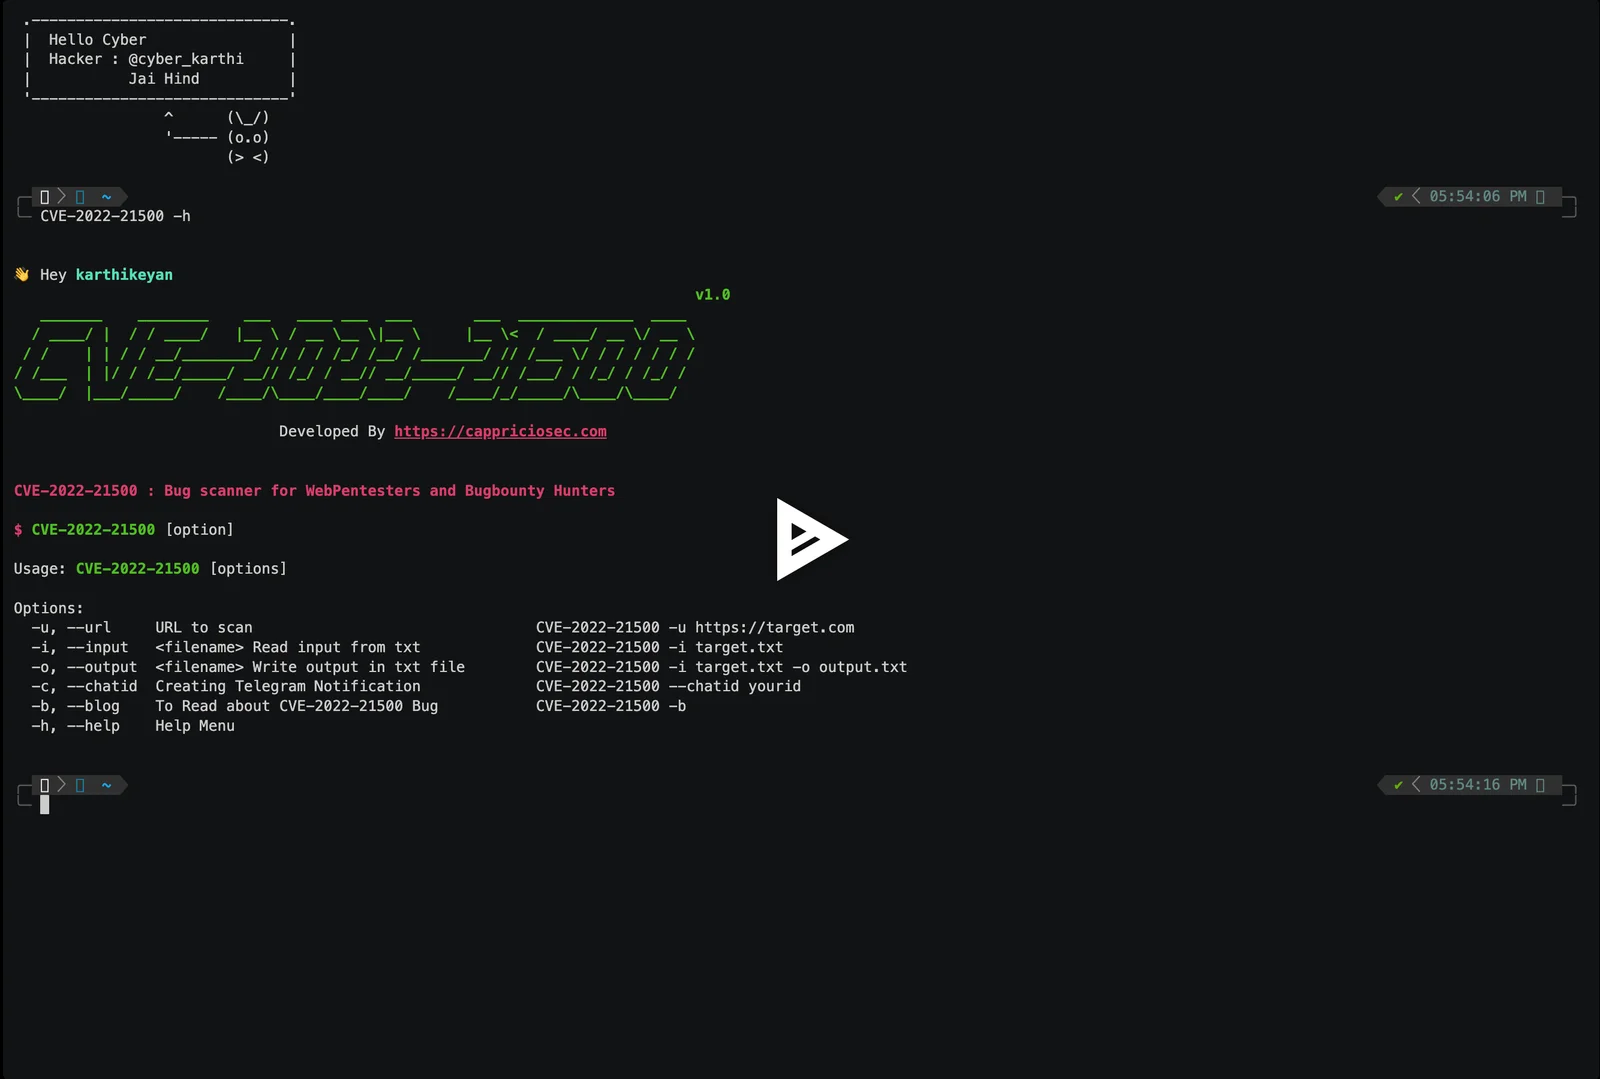
👋 Hey Hacker
                                                                             v1.0
   _______    ________    ___   ____ ___  ___       ___  _____________  ____
  / ____/ |  / / ____/   |__ \ / __ \__ \|__ \     |__ \<  / ____/ __ \/ __ \
 / /    | | / / __/________/ // / / /_/ /__/ /_______/ // /___ \/ / / / / / /
/ /___  | |/ / /__/_____/ __// /_/ / __// __/_____/ __// /___/ / /_/ / /_/ /
\____/  |___/_____/    /____/\____/____/____/    /____/_/_____/\____/\____/

                              Developed By https://cappriciosec.com


CVE-2022-21500 : Bug scanner for WebPentesters and Bugbounty Hunters

$ CVE-2022-21500 [option]

Usage: CVE-2022-21500 [options]
| Argomento | Tipo | Descrizione | Esempi |
|---|---|---|---|
-u | --url | URL da scansionare | CVE-2022-21500 -u https://target.com |
-i | --input | Leggi input da file txt | CVE-2022-21500 -i target.txt |
-o | --output | Scrivi output in file txt | CVE-2022-21500 -i target.txt -o output.txt |
-c | --chatid | Crea notifica Telegram | CVE-2022-21500 --chatid yourid |
-b | --blog | Per leggere informazioni sulla vulnerabilità CVE-2022-21500 | CVE-2022-21500 -b |
-h | --help | Menu di aiuto | CVE-2022-21500 -h |

Se hai qualsiasi feedback, contattaci a [email protected]