Red/blue team toolkit for CVE-2026-119977 WordPress core upgrade-window RCE: version triage, WAF origin discovery, race oracle, staged wp-config takeover and Bait MySQL proof.


Ethical Use Only – Authorized Tested
This repository provides tools for authorized security professionals, blue teams, and penetration testers only.
Unauthorized access to computer systems is illegal under CFAA (US), Computer Misuse Act (UK), TCK 243/244 (Turkey), and similar laws worldwide.
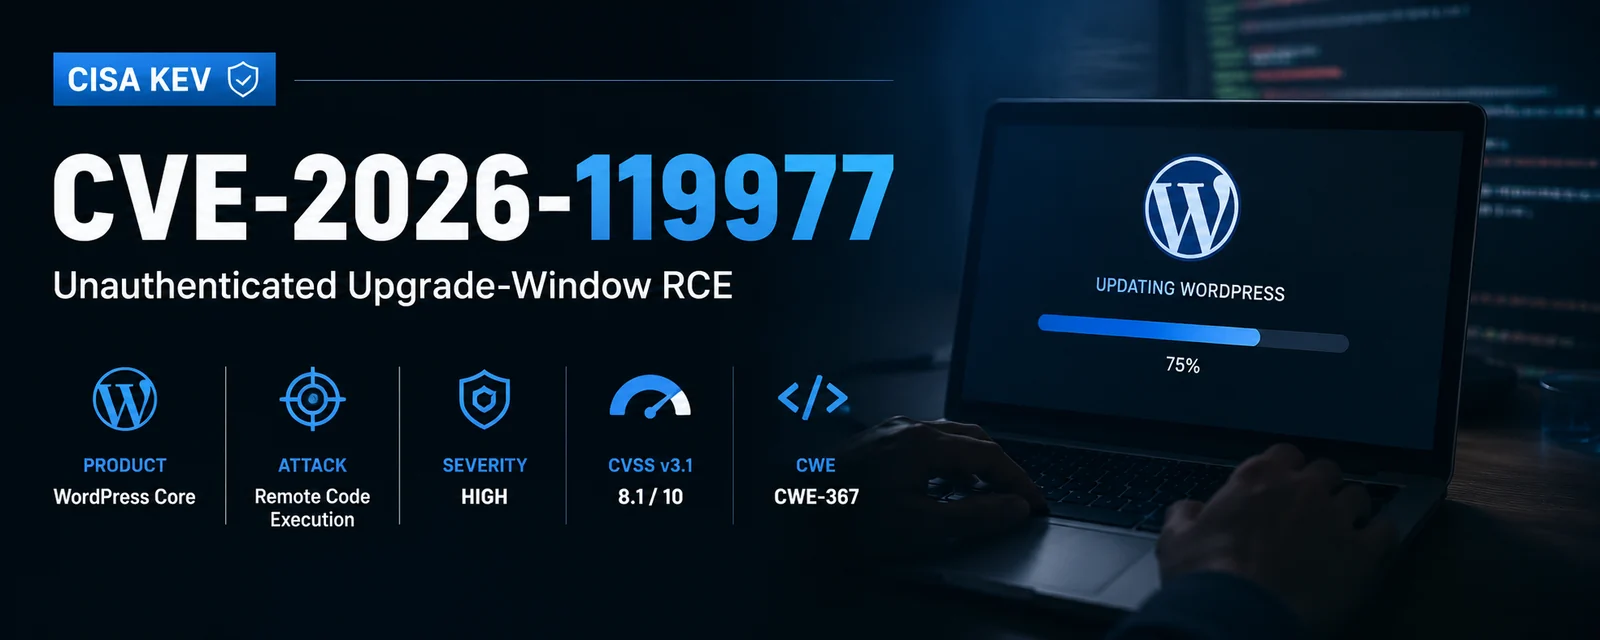
CVE-2026-119977 is a use-after-free in the Linux kernel's IPv4 TCP stack... no, wait. It is a TOCTOU race condition in WordPress Core versions 4.7.0 through 7.1.3. During a full-package core update, WordPress unpacks the new release into a predictable, web-accessible staging directory under wp-content/upgrade/. Because update_core() does not skip wp-config.php when copying the staged tree to the live root, an unauthenticated attacker who reaches the staged installer inside the update window can plant an attacker-controlled wp-config.php that replaces the live one.
WP_Upgrader::unpack_package() derives the working directory from the package basename, which is wordpress-<version>.wp-admin/setup-config.php, which runs without the live wp-config.php.setup-config.php?step=2 with database credentials they control. WordPress writes wp-config.php into the staged tree.update_core() copies the staged tree into ABSPATH. Before 7.1.4, wp-config.php was not in the skip list, so the attacker-written config replaces the live one.wp-config.php. Pointing DB_HOST at an endpoint the attacker owns yields full configuration takeover and code execution through the theme editor.The upstream fix is in WordPress 7.1.4 (backported to 4.7): the staging name includes a 16-char random suffix, wp-content/upgrade/index.php is written and preserved, and wp-config.php is added to the update_core() skip list. IPv6 is not related; that was the other CVE.
wp-content/upgrade/ at the web server.wp-content/upgrade/.| Tool | Purpose | Intended User |
|---|---|---|
exploit.py | Red team toolkit. Fingerprints WordPress, discovers origin behind CDNs, watches for the upgrade window, races the staged config write, proves promotion via a Bait MySQL server, optionally creates an admin account and deploys a mu-plugin shell. Includes SOCKS5 proxy pool, rate limiter, state file, and retry loop. | Red teams / authorized pentesters |
safecheck.py | Non-intrusive local triage. Grades a WordPress version against the fixed release for its branch. Reads wp-includes/version.php from a local install, a version file, or a JSON inventory. Never sends a network request. | Blue teams / security auditors |
| Feature | exploit.py | safecheck.py |
|---|---|---|
| WordPress version fingerprint | [+] | [+] |
| Local version triage | [-] | [+] |
| WAF detection | [+] | [-] |
| Origin discovery behind CDN | [+] | [-] |
| Upgrade-window race oracle | [+] | [-] |
| Staged config write | [+] | [-] |
| Bait MySQL promotion proof | [+] | [-] |
| Admin creation via attacker DB | [+] | [-] |
| mu-plugin shell deploy | [+] | [-] |
| Log cleanup | [+] | [-] |
| SOCKS5 proxy pool with circuit breaker | [+] | [-] |
| Rate limiter | [+] | [-] |
| State file for resume | [+] | [-] |
| Retry with backoff | [+] | [-] |
| HTTP/2 single-packet race | [+] | [-] |
| JSON inventory input | [-] | [+] |
| JSON / JSONL / CSV output | [+] | [+] |
| Async, zero-dependency runtime | [+] | [+] |
git clone https://github.com/tc4dy/CVE-2026-119977-PoC-Exploit
cd CVE-2026-119977-PoC-Exploit/tools/
pip install -r requirements.txt
requests

#optional
httpx
pymysql
passlib
h2spacex
Note: only httpx is required for the core exploit path. pymysql enables the real-database admin creation path. passlib produces a WordPress-compatible phpass hash. h2spacex enables the HTTP/2 single-packet race. The tool falls back gracefully when any of them is missing.
python exploit.py -t https://blog.example --authorized
Without flags, both tools print their help. exploit.py refuses to run without --authorized.
exploit.py flags| Flag | Description |
|---|---|
-t, --target | Target URL |
--authorized | Confirm authorized testing (required) |
--mode | check, watch, or exploit (default: exploit) |
--race-mode | httpx or single (HTTP/2 single-packet) |
--db-host | DB_HOST to plant in the staged config |
--db-port | DB port |
--db-name | Database name |
--db-user | Database user |
--db-pass | Database password |
--workers | Concurrent window pollers (default: 16) |
--threads | Concurrent race POSTs (default: 32) |
--timeout | HTTP timeout (default: 8.0) |
--rate | Requests per second (default: 20.0) |
--duration | Window watch duration (default: 3600) |
--retry | Retry attempts (default: 3) |
--path | Forced staging directory name |
--state-file | Resume state file |
--log-file | Debug log file |
--proxy-file | SOCKS5 proxy list |
--cleanup | Remove the created admin and wipe logs |
--bait-port | Bind a Bait MySQL server and wait for promotion |
--deploy-shell | Deploy a mu-plugin shell after login |
--versions | Candidate staging names |
--upgrade-path | Web path of the upgrade dir |
--distro-dir | Top-level directory inside the package |
--no-color | Disable ANSI colors |
safecheck.py flags| Flag | Description |
|---|---|
--version | WordPress version string |
--version-file | Path to wp-includes/version.php |
--wp-root | Path to a WordPress install |
--inventory-json | JSON list of site entries |
--upgrade-exposed | Mark wp-content/upgrade as web-accessible |
--upgrade-blocked | Mark wp-content/upgrade as blocked |
--auto-updates-off | Mark automatic updates as off |
--json | Machine-readable output |
--list | Print the fixed table |