DidierStevensSuite
Collection of Python scripts for malware analysis, file format parsing, hashing, and forensic triage, including PDF, OLE, and XOR analysis utilities.
Short editorial updates from published cybersecurity tools.

Collection of Python scripts for malware analysis, file format parsing, hashing, and forensic triage, including PDF, OLE, and XOR analysis utilities.

The agent that grows with you

Maliciousness scoring for Linux commands

Clean Indirect Syscalls with Syscall Tampering.

Audit only eBPF EDR for Linux 5.15+ LTS: 14 kernel hooks, 15 actions (13 MITRE techniques), process lineage, SIEM export, K8s/Docker ready.

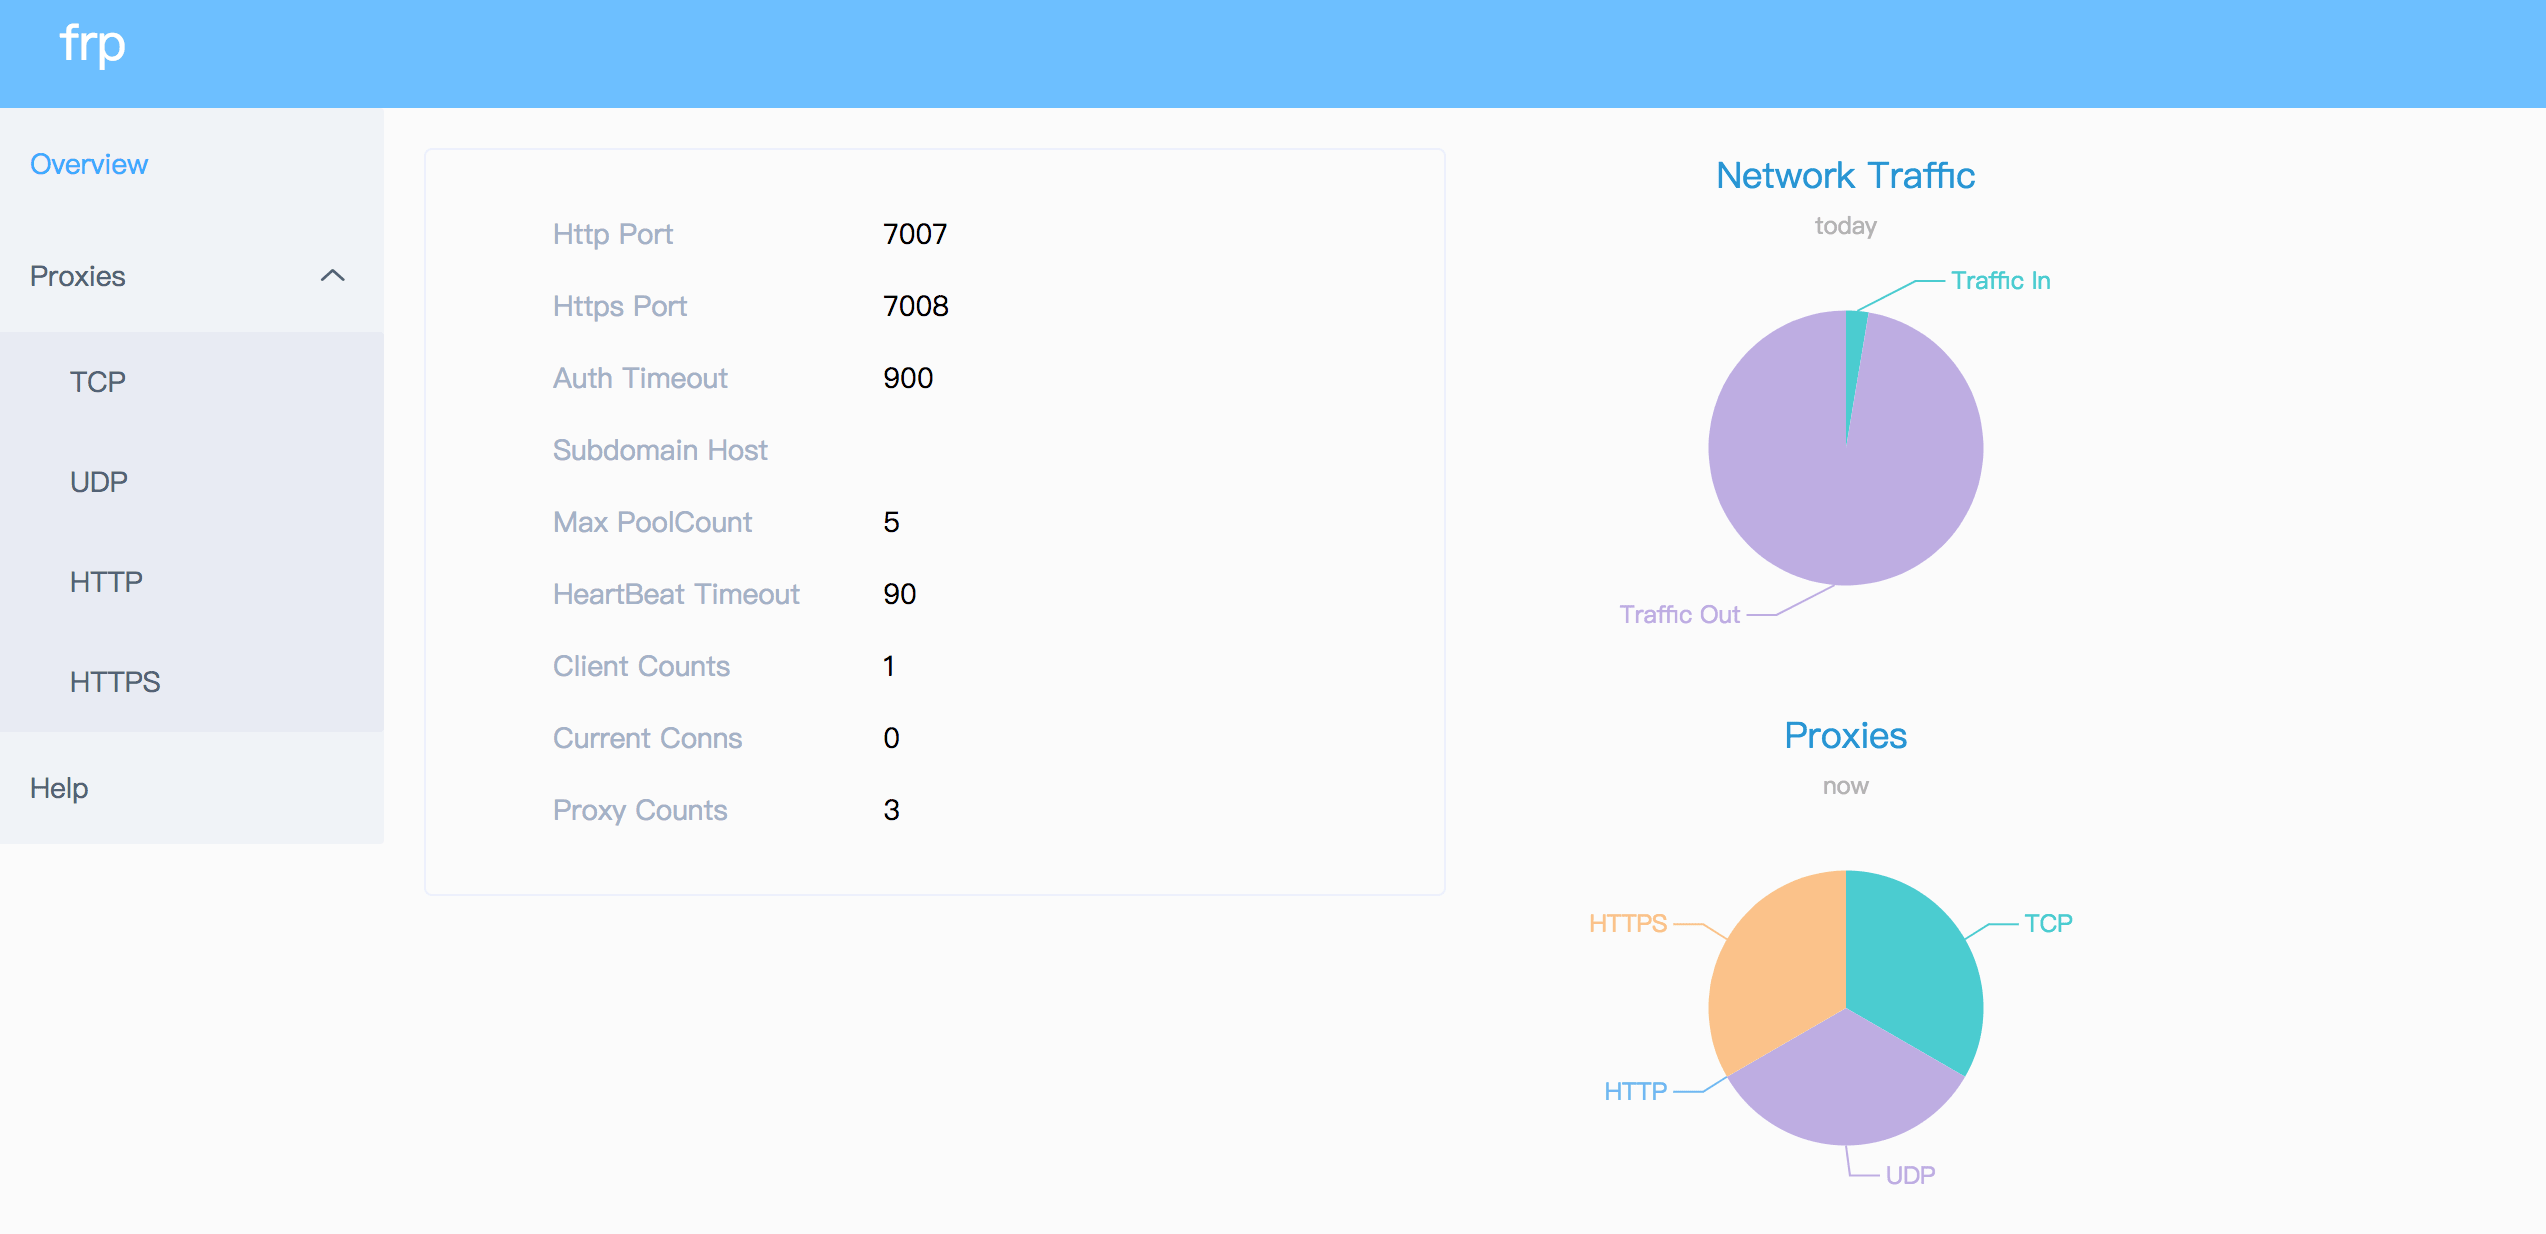
A fast reverse proxy to help you expose a local server behind a NAT or firewall to the internet.

Ring -4 to Ring 0: offense-defense firmware research platform. We build the bootkits, then we catch them. Closed-loop. Zero trust in silicon.

OSINT identity investigation tool. Pivot from an e-mail, username, phone or wallet across 46 sources into one profile and relationship graph.

Local static security scanner for Next.js, Supabase and Stripe apps: 24 AST-based checks for leaked keys, missing RLS and grants, unsafe webhooks.…

Read-only Windows host hardening auditor in PowerShell with optional AI analysis

Linux operating system for embedded devices with writable filesystem, package management, and build framework. Enables custom firmware creation for…

Read-only Active Directory & Microsoft Entra ID hygiene auditor in pure PowerShell. Collect once, analyze offline: deterministic findings, attack…