
 0xmfbk/ebpf-container-escape-framework
Audit only eBPF EDR for Linux 5.15+ LTS: 14 kernel hooks, 15 actions (13 MITRE techniques), process lineage, SIEM export, K8s/Docker ready.



Detection & audit only. Non-enforcing sensor. No BPF program returns
-EPERM; no syscall is blocked. This agent is a runtime observation plane, not a prevention plane. Seedocs/SECURITY.mdandTHREAT_MODEL.md.
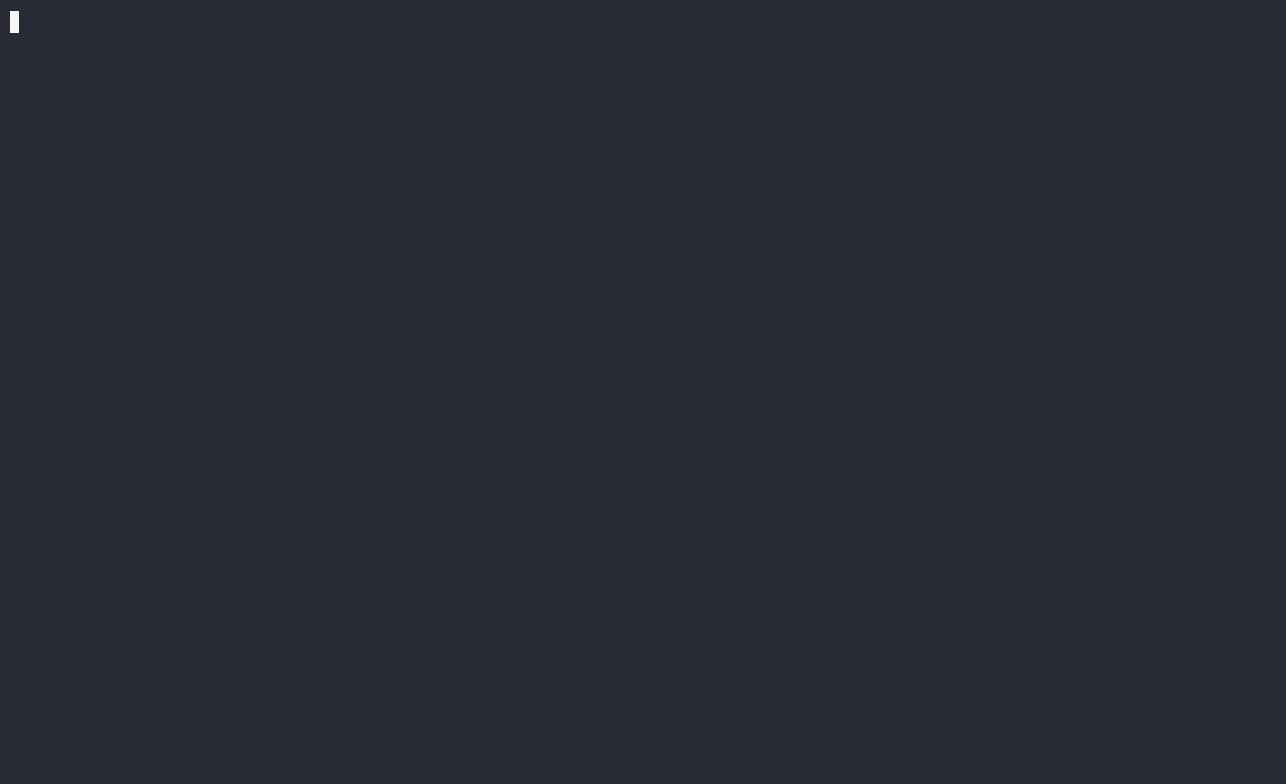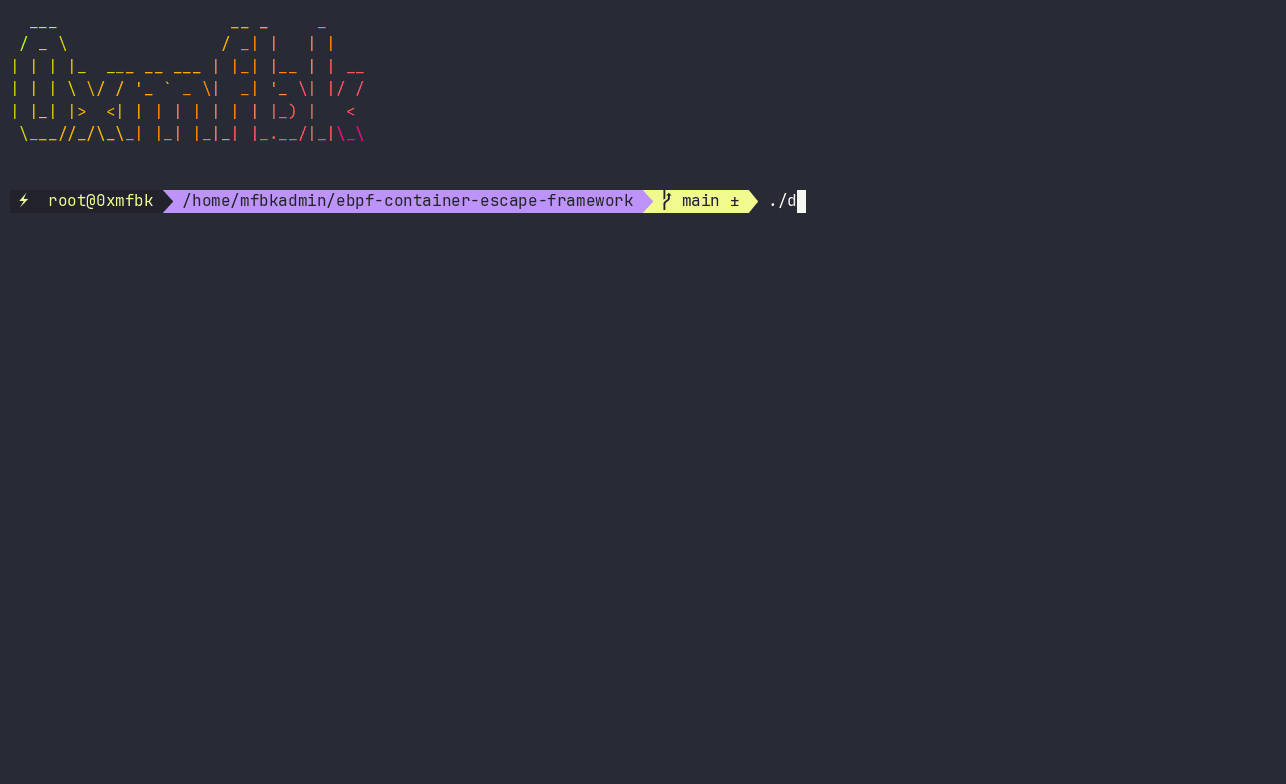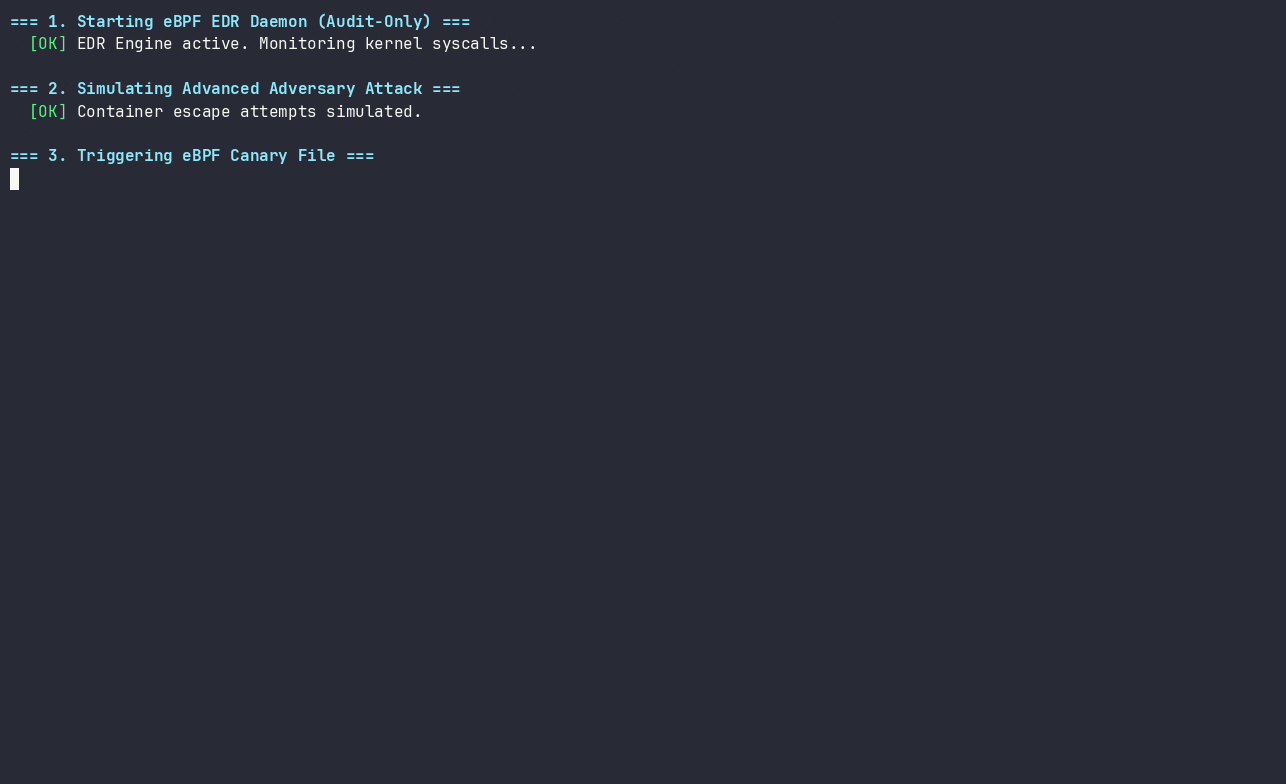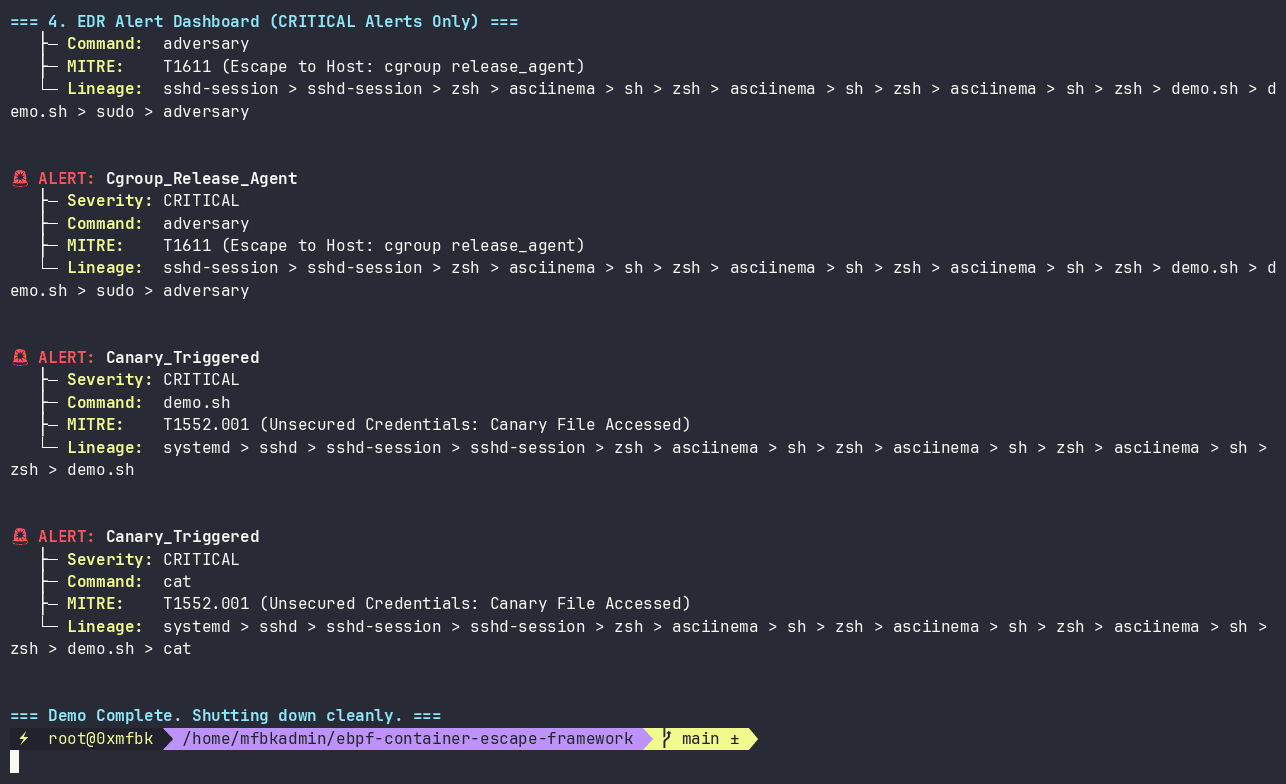
An ultra lightweight, audit only Linux EDR agent built with eBPF (C) and a high efficiency Go daemon. It targets Linux kernel 5.15 LTS and above, featuring a zero-allocation hot path, a sub-30MB memory footprint, and deep container/K8s context enrichment.
CRITICAL alert instantly.cgroup_id to Pod Name, Namespace, and ServiceAccount without inflating the 208-byte kernel wire format.0.40% idle CPU and 0 ringbuf drops under a 25,000 fork stress test.Status: Phase 2.7 complete. 13 MITRE ATT&CK techniques across 16 actions. Verified end to end on kernel 6.12.111 (82 PASS / 0 FAIL).
| # | Action | Severity | MITRE | Hook |
|---|---|---|---|---|
| 1 | Container_Namespace_Unshare | HIGH | T1611 | kprobe/__x64_sys_unshare |
| 2 | Container_Pivot_Root_Escape | CRITICAL | T1611 | kprobe/__x64_sys_pivot_root |
| 3 | Sensitive_File_Access | HIGH | T1003.008 | tracepoint/sys_enter_openat + open |
| 4 | Process_Execution | INFO/MEDIUM | T1059.004 | tracepoint/sys_enter_execve |
| 5 | Network_Connection | INFO/HIGH | T1071 | tracepoint/sys_enter_connect |
| 6 | Process_Injection | HIGH | T1055.008 | tracepoint/sys_enter_ptrace |
| 7 | Log_Tampering | HIGH | T1562.001 | tracepoint/sys_enter_unlinkat |
| 8 | Ebpf_Tampering | HIGH | T1562.001 | tracepoint/sys_enter_bpf |
| 9 | Perf_Event_Open | MEDIUM | T1562.001 | tracepoint/sys_enter_perf_event_open |
| 10 | Suspicious_Mount | HIGH | T1611 | tracepoint/sys_enter_mount |
| 11 | Namespace_Switch | HIGH | T1611 | tracepoint/sys_enter_setns |
| 12 | Chroot_Escape | HIGH | T1611 | tracepoint/sys_enter_chroot |
| 13 | Executable_Memory | MEDIUM | T1620 | tracepoint/sys_enter_mprotect |
| 14 | Core_Pattern_Modification | CRITICAL | T1611 | tracepoint/sys_enter_openat + open |
| 15 | Cgroup_Release_Agent | CRITICAL | T1611 | tracepoint/sys_enter_openat + open |
| 16 | Canary_Triggered | CRITICAL | T1552.001 | tracepoint/sys_enter_openat + open |
Actions 9 and 13 are attached but kernel side suppressed by default via
disabled_actions in config.toml.
Kernel hooks (14) feed a comm/cgroup filter, a canary_paths O(1) hash lookup, then an action_enabled lookup. Events are pushed to a 1 MiB ringbuf carrying 208 byte records. Userspace reads into a fixed pooled buffer, applies a per action token bucket, enriches with process lineage and cgroup path, and K8s Pod metadata from bounded LRU caches, and routes through an Encoder + Sink to any destination.
Full details: docs/ARCHITECTURE.md.
ebpf edr exports alerts to any SIEM via a format + transport layer.
[output]
format = "ecs"        # json | ecs | ocsf | cef | leef
target = "webhook"    # file | stdout | syslog | webhook

[output.webhook]
url         = "https://splunk.internal:8088/services/collector/event"
auth_header = "Splunk ${SPLUNK_HEC_TOKEN}"
splunk_hec  = true
Supported transports: file, stdout, syslog (UDP/TCP/TLS), HTTPS webhook. Supported formats: native JSON, ECS 8.11, OCSF 1.3.0, CEF, LEEF 2.0.
Recipes for Splunk, Elastic, Sentinel, QRadar, and generic syslog:
docs/SIEM_INTEGRATION.md.
Absent [output], behavior is byte identical to v1.x.
CONFIG_DEBUG_INFO_BTF=y (/sys/kernel/btf/vmlinux)docs/KERNEL_COMPATIBILITY.md for the full matrix.CAP_BPF CAP_PERFMON CAP_SYS_ADMINmake kernel # kernel/bpf_program.o
make userspace # userspace/ebpf_controller
make emulation # emulation/adversary
sudo -E make verify
Runs environment probe, build, C/Go struct layout assertion, BPF verifier dry-run, runtime smoke, adversary emulation, performance, config matrix, SIGHUP reload, idle CPU, lineage enrichment, cache bounds, new hooks, format matrix, and webhook delivery.
sudo ./install.sh --dry-run
sudo ./install.sh
sudo ./install.sh --uninstall
Installs /usr/local/sbin/ebpf-edr,
/usr/local/lib/ebpf-edr/bpf_program.o,
/etc/ebpf-edr/config.toml (existing preserved; new default at .new),
/etc/systemd/system/ebpf-edr.service,
/etc/logrotate.d/ebpf-edr.
TOML at /etc/ebpf-edr/config.toml. Precedence: CLI > env (EDR_*) > file > defaults.
mode = "audit"

disabled_actions = [
    "Perf_Event_Open",
    "Executable_Memory",
]

[log]
path        = "/var/log/ebpf_edr.json"
max_bytes   = 52428800
max_backups = 5
level       = "info"

[filter]
comm_allowlist   = []
cgroup_allowlist = []
canary_paths     = ["/var/run/secrets/kubernetes.io/serviceaccount/token"]

[k8s]
enrichment = true

[rates]
events_per_sec = 200
burst          = 400

[container]
cache_max_entries = 5000

[context]
lineage_max_depth  = 16
lineage_cache_size = 20000
cgroup_cache_size  = 5000
Reload: sudo systemctl reload ebpf-edr. mode = "enforce" is rejected;
this build is audit only.
{
  "timestamp": "2026-10-15T23:52:41Z",
  "pid": 1370, "ppid": 1369, "uid": 0,
  "start_time_ns": 180763002635,
  "command": "unix_chkpwd",
  "action": "Sensitive_File_Access",
  "target": "/etc/shadow",
  "severity": "HIGH",
  "mitre_id": "T1003.008",
  "mitre_technique": "OS Credential Dumping: /etc/shadow",
  "cgroup_id": 3874,
  "cgroup_path": "/user.slice/user-0.slice/session-3.scope",
  "runtime": "host",
  "lineage_summary": "systemd > sshd > bash > sudo > unix_chkpwd",
  "lineage": [
    {"pid": 1370, "ppid": 1369, "comm": "unix_chkpwd",
     "exe": "/usr/sbin/unix_chkpwd", "start_time_ns": 180763002635},
    {"pid": 1369, "ppid": 1368, "comm": "sudo",
     "exe": "/usr/bin/sudo", "start_time_ns": 180762998100}
  ]
}
Fields aux_u16, aux_u32, aux_u64 carry action specific context.
Health line every 60s:
