
CVE-2022-4510
 electr0sm0g/cve-2022-4510
Exploit for CVE-2022-4510 enabling remote command execution in Binwalk firmware analysis tool. Provides proof-of-concept code for security testing…
binary-analysisexploitationfirmware-analysis+2
9
electr0sm0g/cve-2022-4510Exploit for CVE-2022-4510 enabling remote command execution in Binwalk firmware analysis tool. Provides proof-of-concept code for security testing…

 ospg/binwalk
Firmware Analysis Tool
 ucsb-seclab/karonte
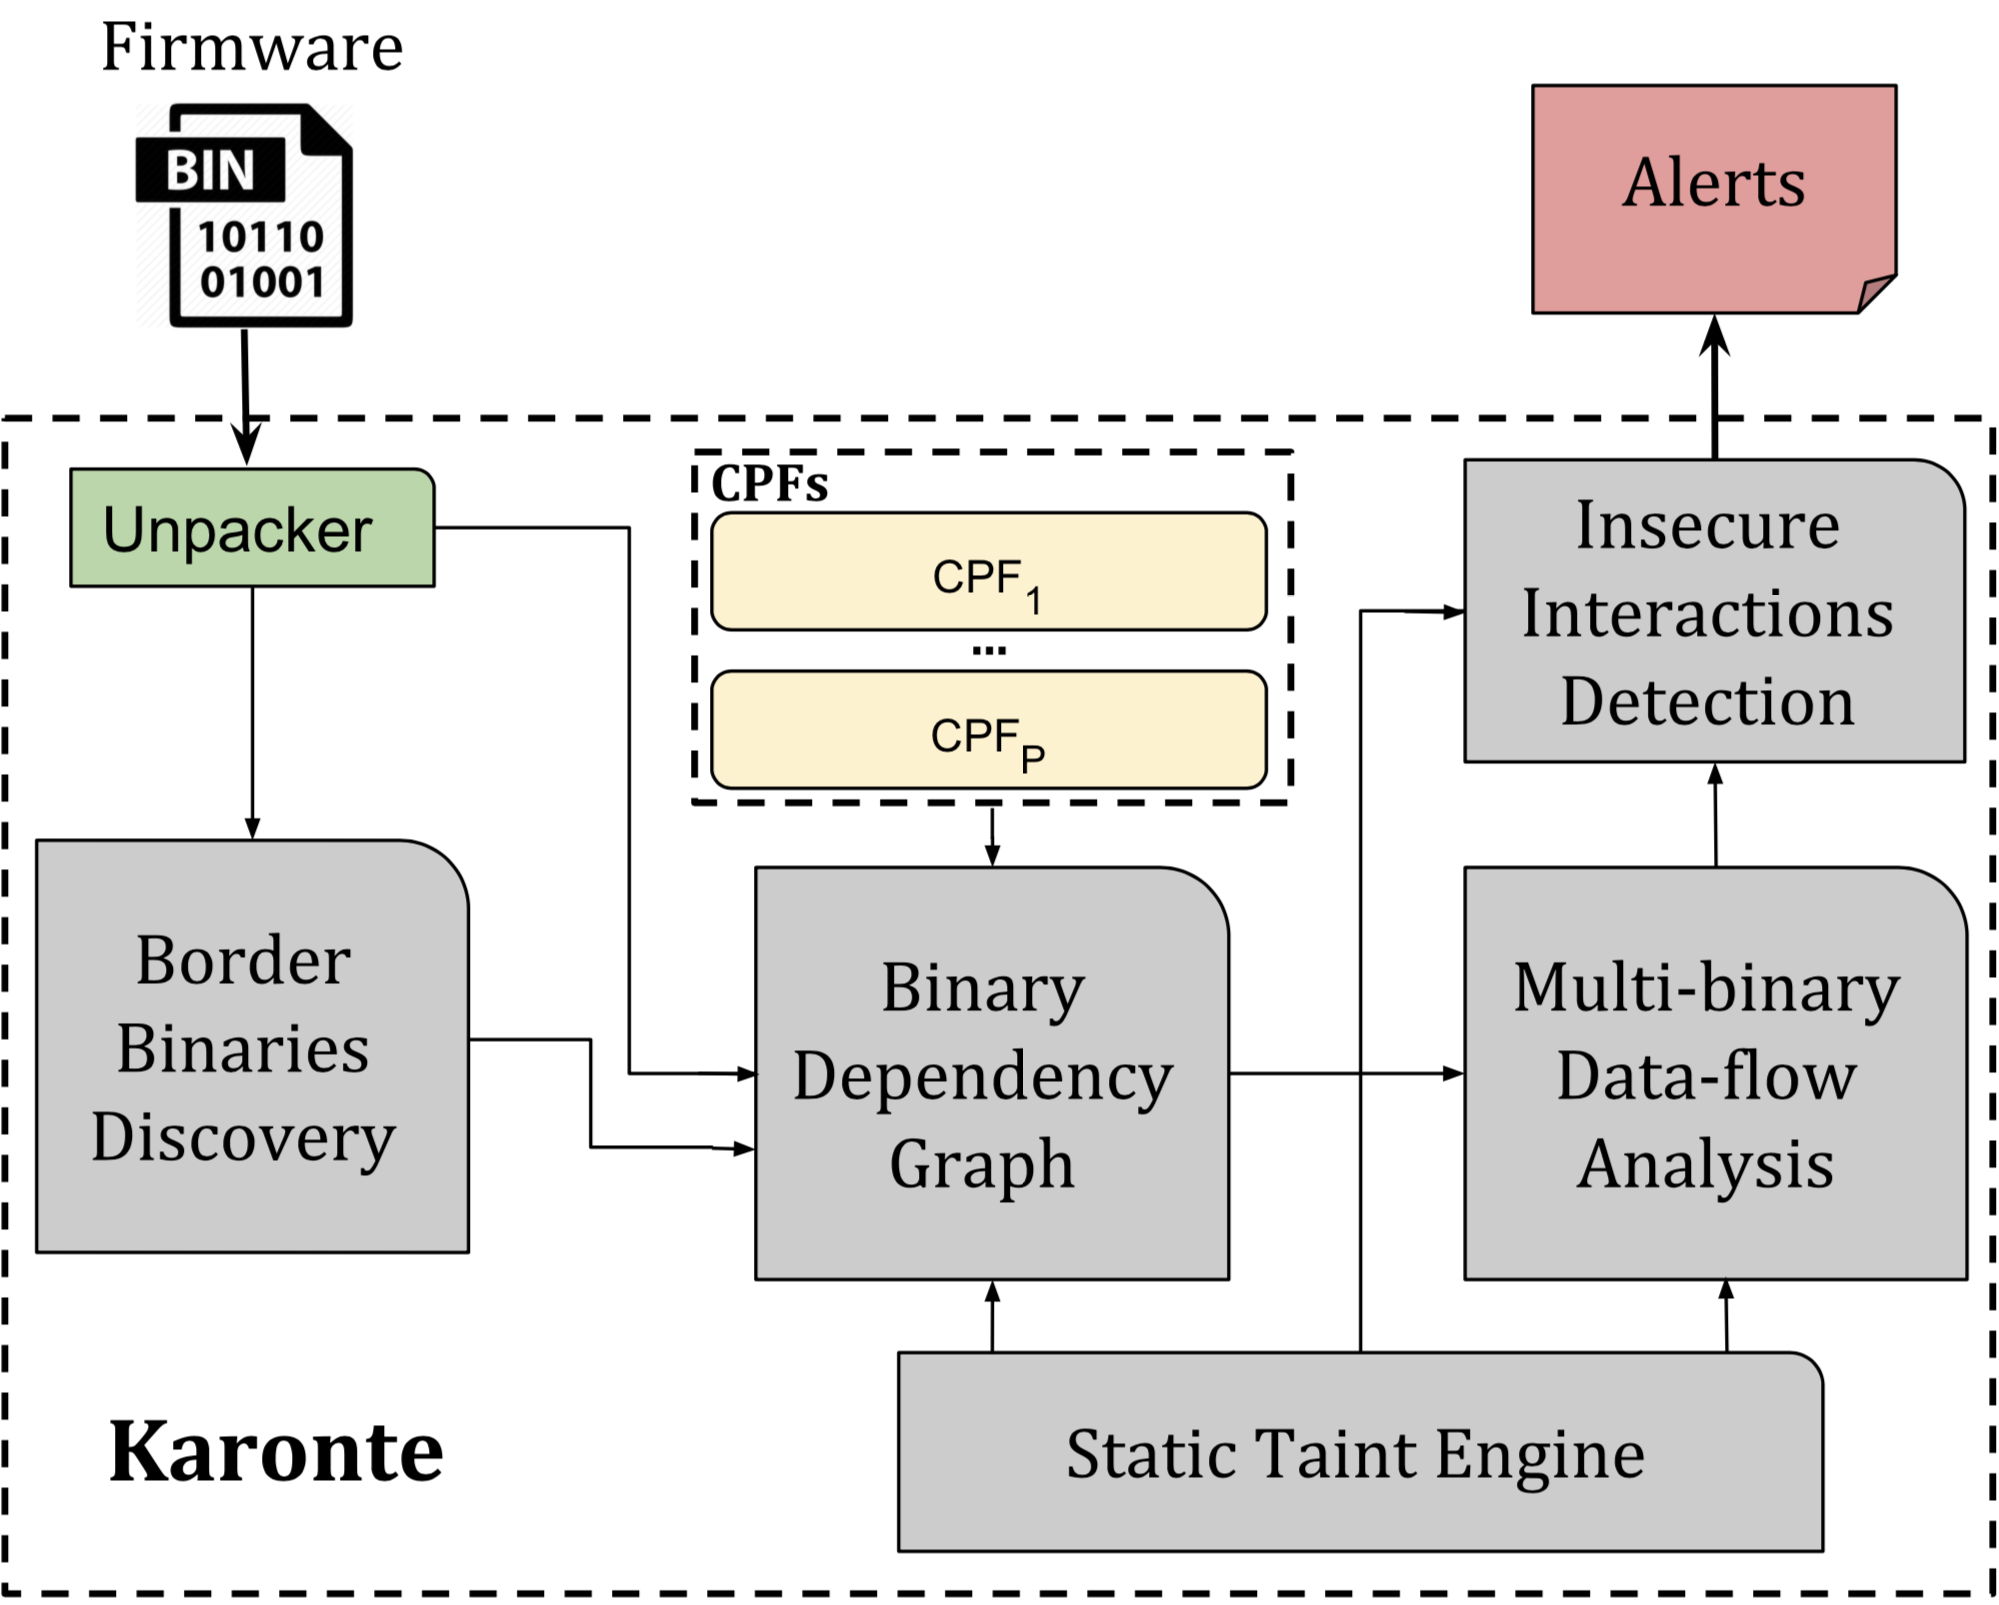
Karonte is a static analysis tool to detect multi-binary vulnerabilities in embedded firmware
 e-m-b-a/embark
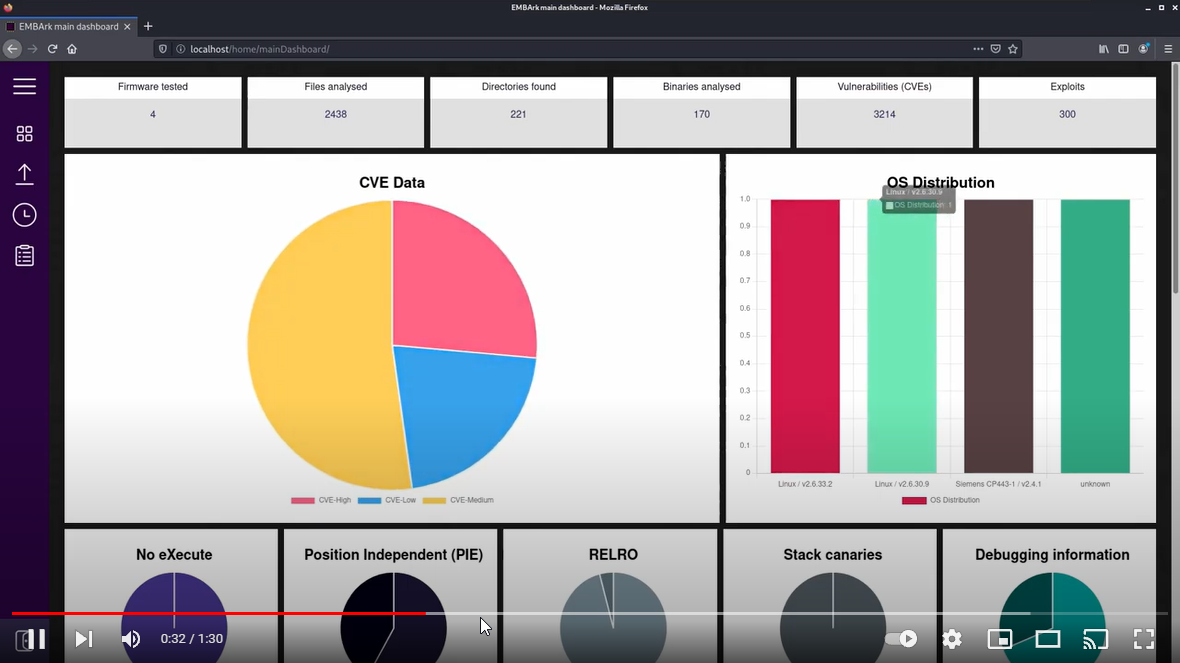
Centralized firmware scanning and reporting platform with a web UI, REST API, and automated analysis workflows for securing embedded/IoT devices.
 yeggor/uefi_retool
A tool for UEFI firmware reverse engineering
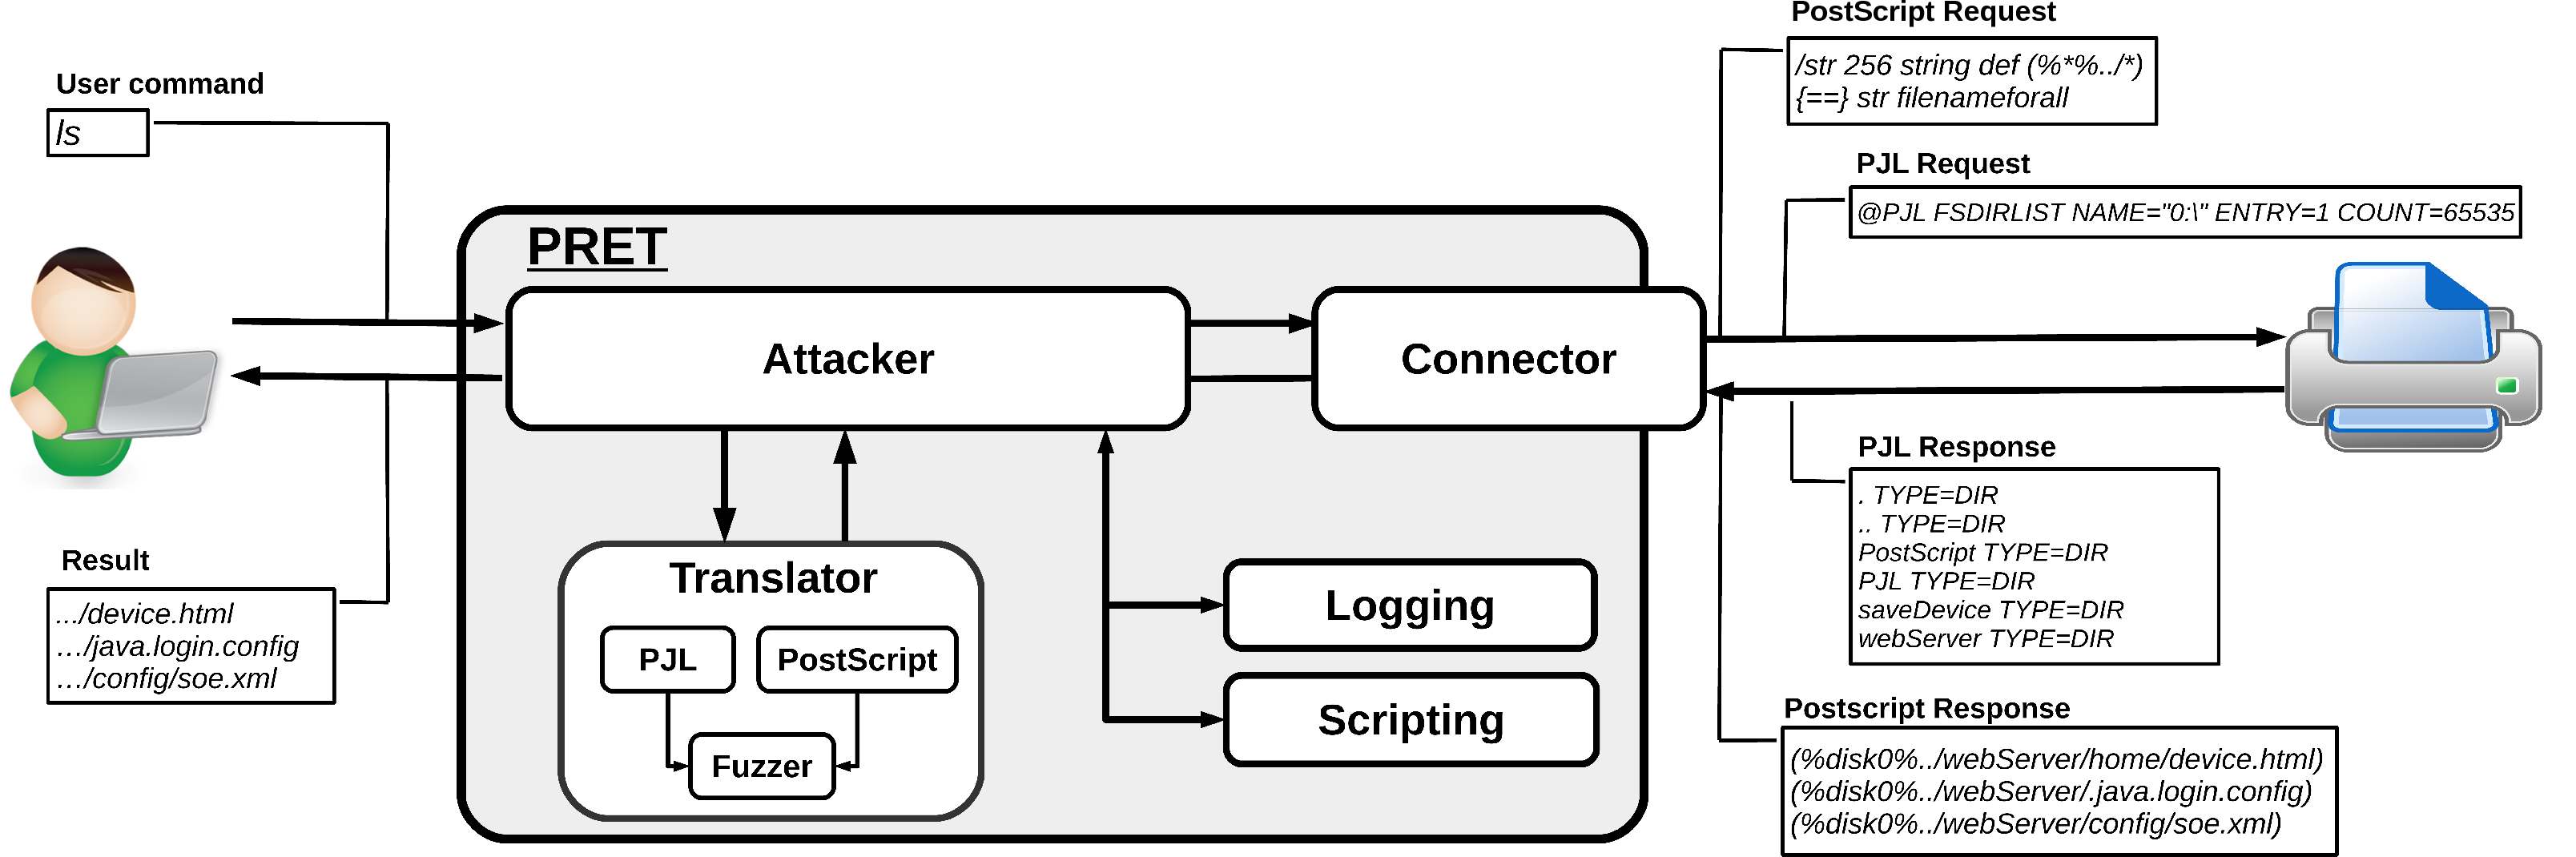 rub-nds/pret
Printer Exploitation Toolkit - The tool that made dumpster diving obsolete.
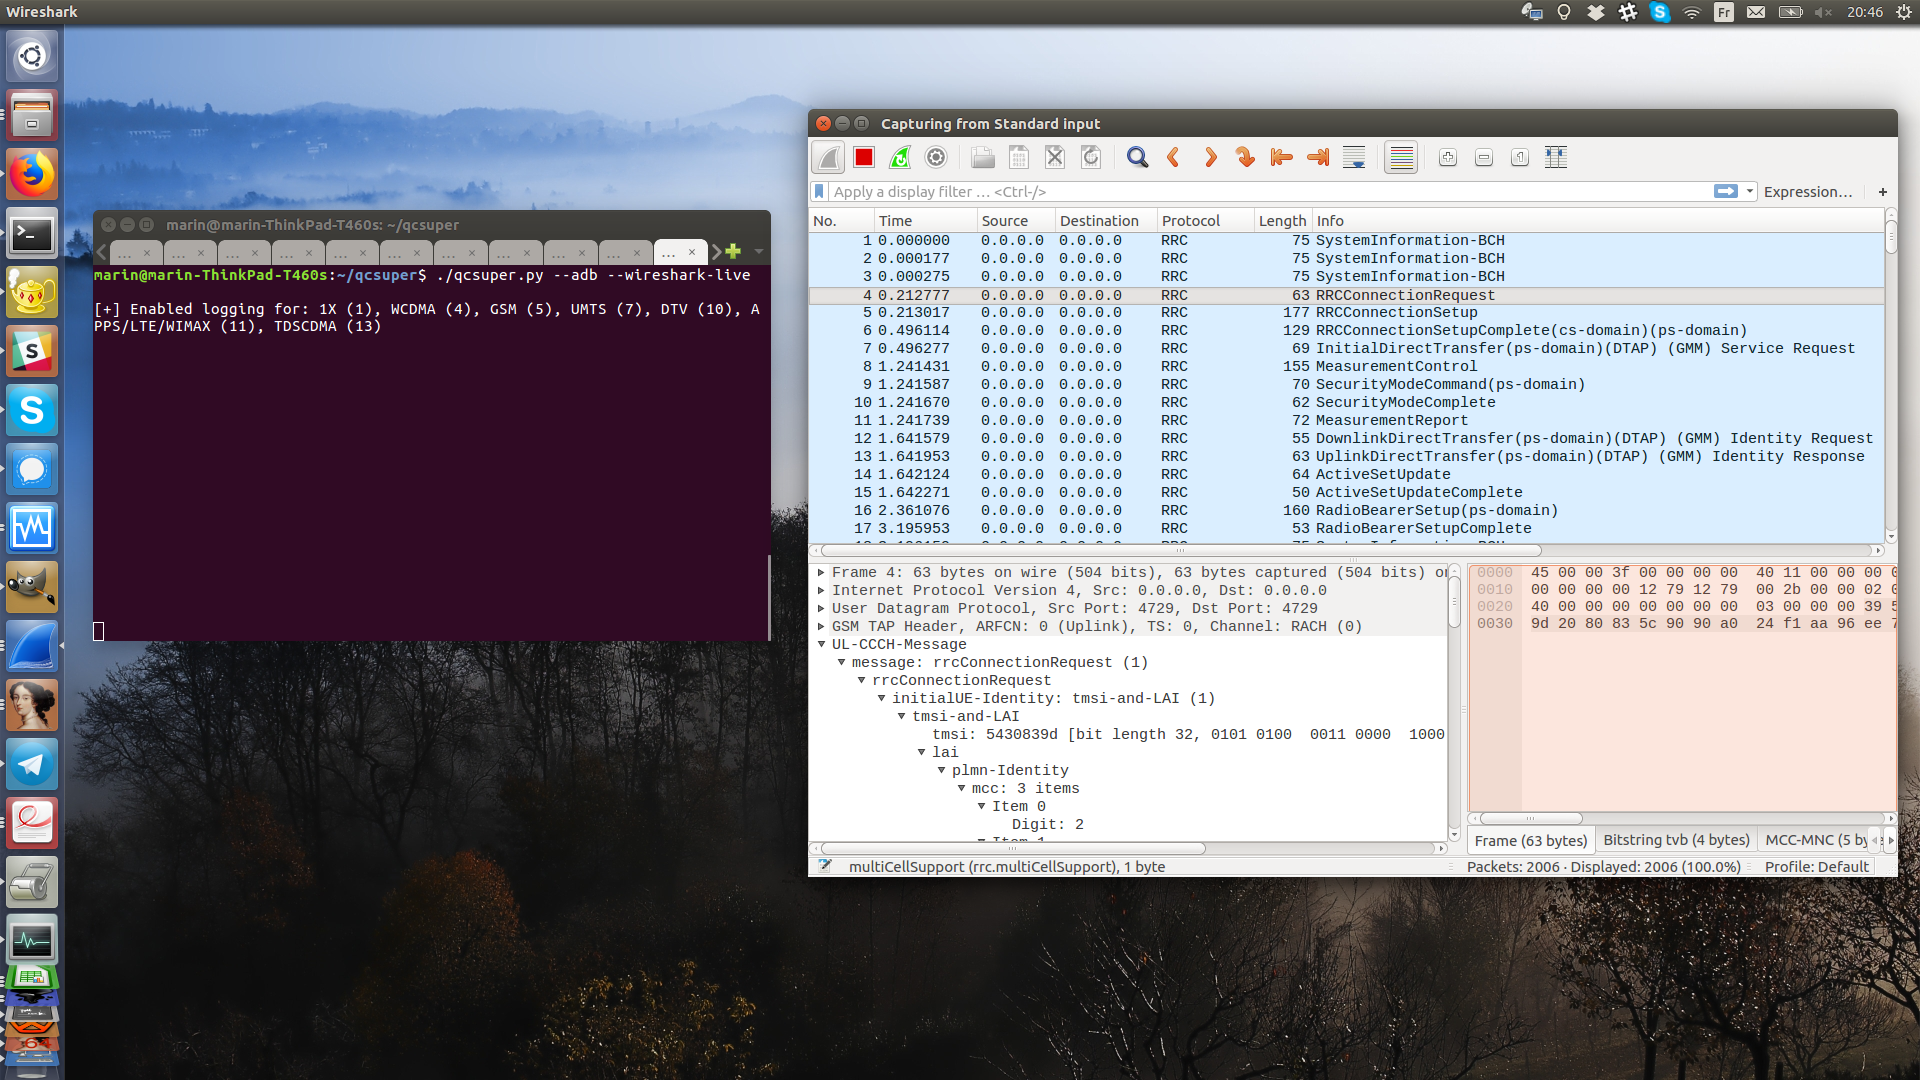 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 marin-m/vmlinux-to-elf
A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)
 rfidtool/esp-rfid-tool
A tool for logging data/testing devices with a Wiegand Interface. Can be used to create a portable RFID reader or installed directly into an existing…
 pagalaxylab/unifuzzer
A fuzzing tool for closed-source binaries based on Unicorn and LibFuzzer
 forescout/project-memoria-detector
Active fingerprinting tool that identifies 16 embedded TCP/IP stacks on network devices using ICMP, TCP, HTTP, SSH, and FTP probing techniques for…
 thewhiteh4t/killcast
Manipulate Chromecast Devices in your Network
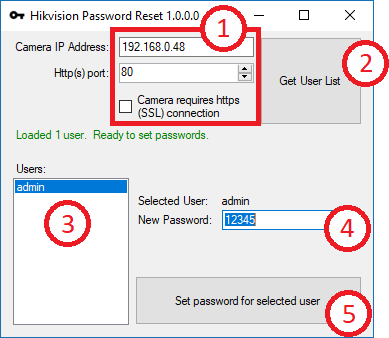 bp2008/hikpasswordhelper
A tool which exploits a backdoor in Hikvision camera firmwares circa 2014-2016 to help the owner change a forgotten password.
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
 kkamagui/napper-for-tpm
TPM vulnerability checking tool for CVE-2018-6622. This tool will be published at Black Hat Asia 2019 and Black Hat Europe 2019
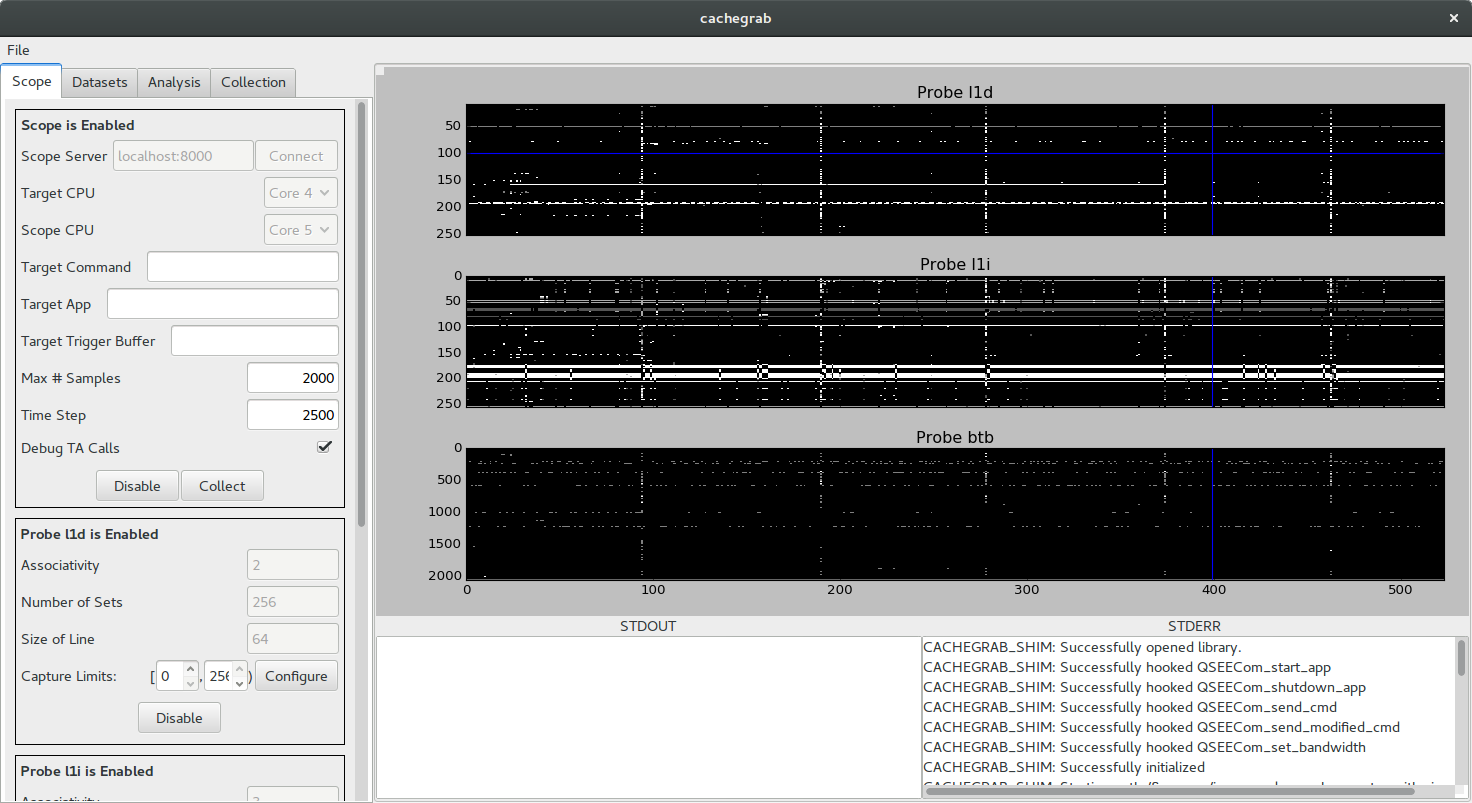 nccgroup/cachegrab
a tool designed to help perform and visualize trace-driven cache attacks against software in the secure world of TrustZone-enabled ARMv8 cores
 infobyte/draytek-arsenal
Reverse Engineering and Observability toolkit for Draytek firewalls