

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
karonte — Karonte is a static analysis tool to detect multi-binary vulnerabilities in embedded firmware | Kitploit
Tools/GitHubGitHub/ucsb-seclab/karonte
Embedded Systems SecurityStatic AnalysisVulnerability AnalysisBinary AnalysisFirmware Analysis
GitHubucsb-seclab/karonte

karonte

Karonte is a static analysis tool to detect multi-binary vulnerabilities in embedded firmware

View Repository
42963555 years agoReviewed by Kitploit
Share

Karonte

License

Karonte is a static analysis tool to detect multi-binary vulnerabilities in embedded firmware.

The master branch provides the latest version of Karonte, ported to python3. For the original implementation and experiments presented in our paper, please checkout the IEEE-SP-20 branch and have a look at our docker container.
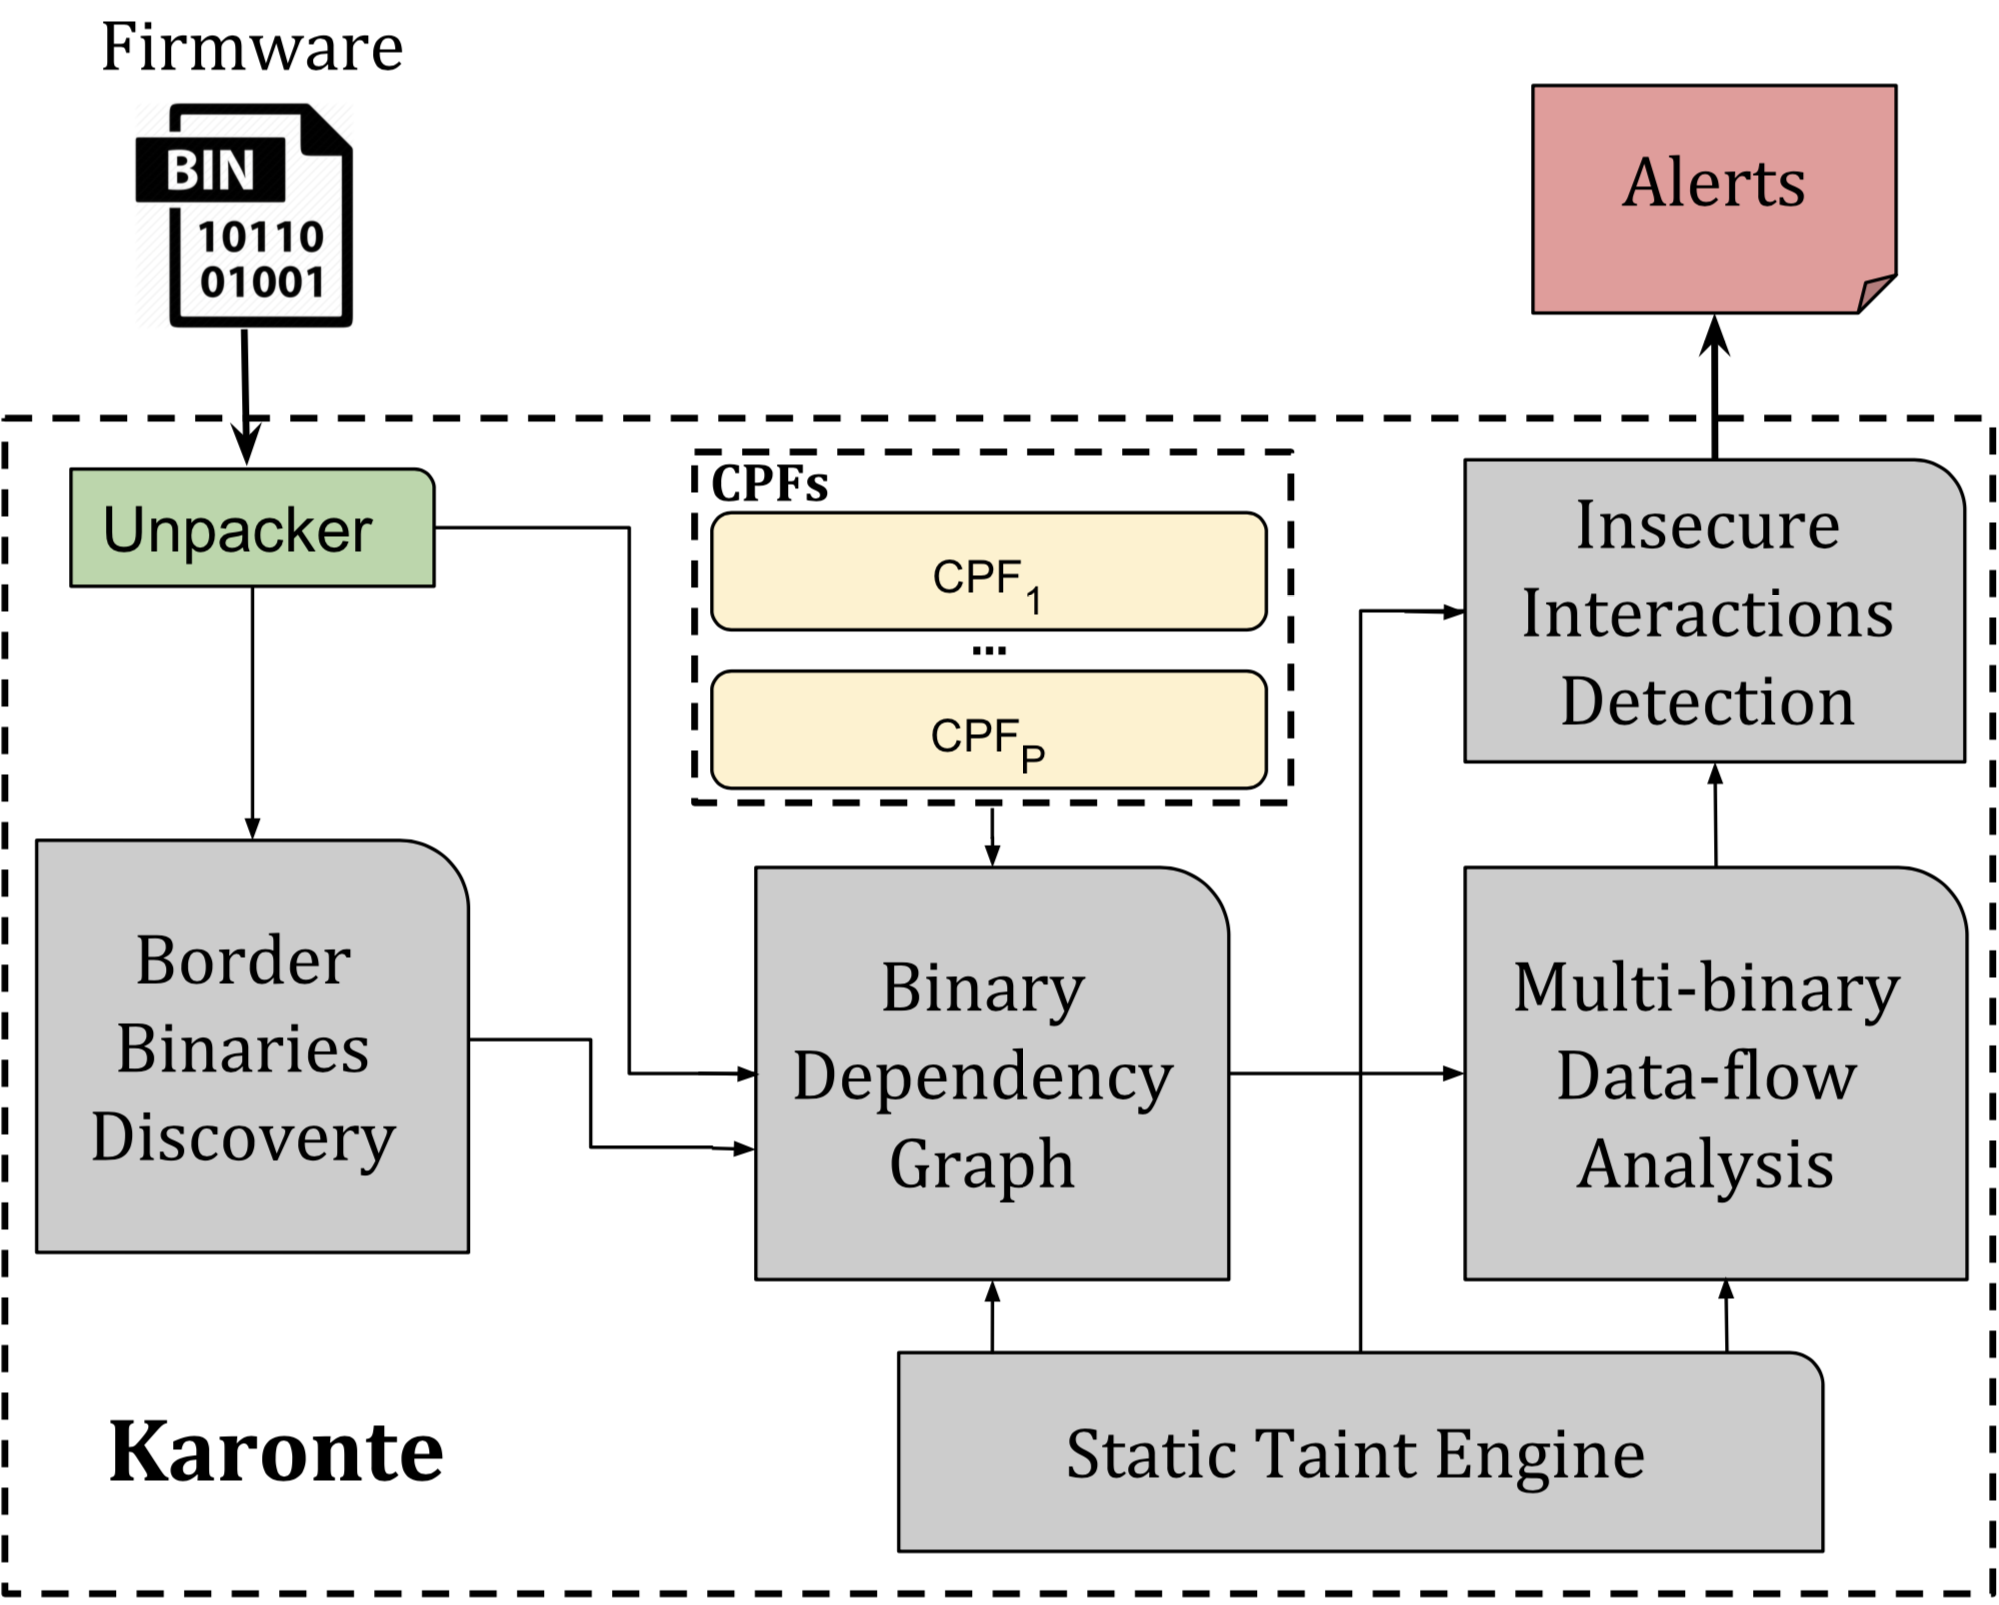
Overview

Research paper

We present our approach and the findings of this work in the following research paper:

KARONTE: Detecting Insecure Multi-binary Interactions in Embedded Firmware [PDF]
Nilo Redini, Aravind Machiry, Ruoyu Wang, Chad Spensky, Andrea Continella, Yan Shoshitaishvili, Christopher Kruegel, Giovanni Vigna.
In Proceedings of the IEEE Symposium on Security & Privacy (S&P), May 2020

If you use Karonte in a scientific publication, we would appreciate citations using this Bibtex entry:

@inproceedings{redini_karonte_20,
 author    = {Nilo Redini and Aravind Machiry and Ruoyu Wang and Chad Spensky and Andrea Continella and Yan Shoshitaishvili and Christopher Kruegel and Giovanni Vigna},
 booktitle = {In Proceedings of the IEEE Symposium on Security & Privacy (S&P)},
 month     = {May},
 title     = {KARONTE: Detecting Insecure Multi-binary Interactions in Embedded Firmware},
 year      = {2020}
}

Repository Structure

There are four main directories:

  • tool: Karonte python files
  • firmware: Karonte firmware dataset
  • configs: configuration files to analyze the firmware samples in the dataset
  • eval: scripts to run the various evaluations on Karonte
  • karonte-viz: script to visualize the results produced by Karonte

Run Karonte

To run karonte, from the root directory, just run

SYNOPSIS       python tool/karonte.py JSON_CONFIG_FILE [LOG_NAME]

DESCRIPTION      runs karonte on the firmware sample represented by the JSON_CONFIG_FILE, and save the results in LOG_NAME

EXAMPLE      python tool/karonte.py config/NETGEAR/r_7800.json      It runs karonte on the R7800 NETGEAR firmware

By default, results are saved in /tmp/ with the suffix Karonte.txt.

To inspect the generated alerts, just run:

      python tool/pretty_print.py LOG_NAME

Dataset

You can obtain the dataset that we used to evaluate Karonte at this link.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    772
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    505
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    260
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    251

Explore all tools

Browse our collection of tools

View all tools →





