
httplab
 qustavo/httplab
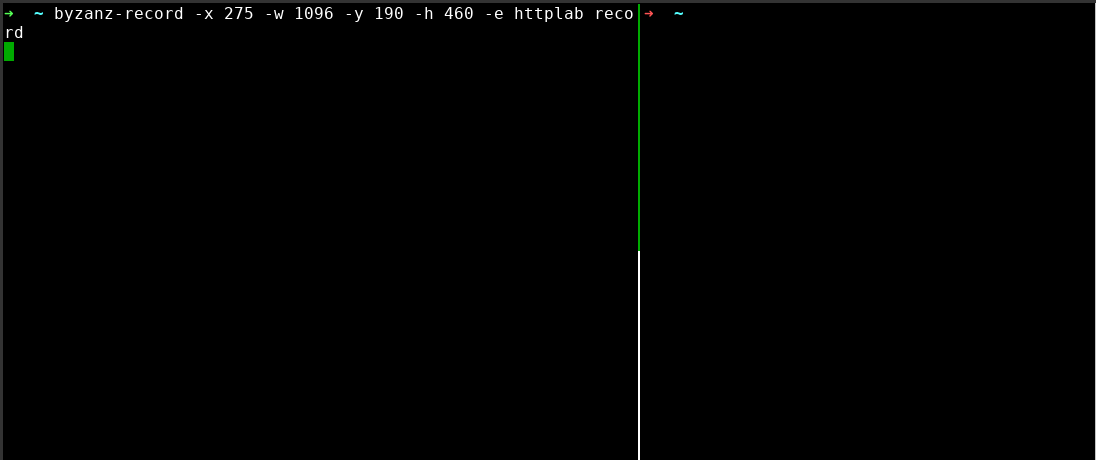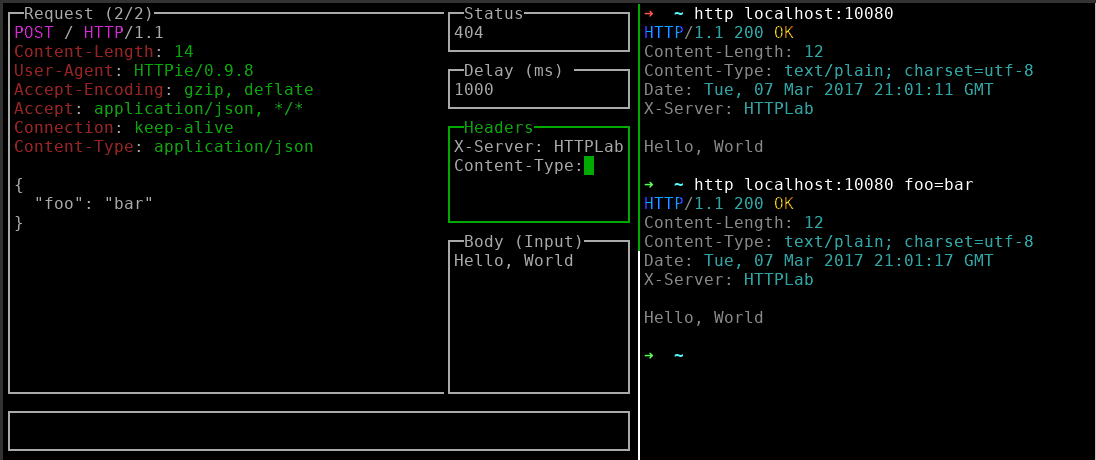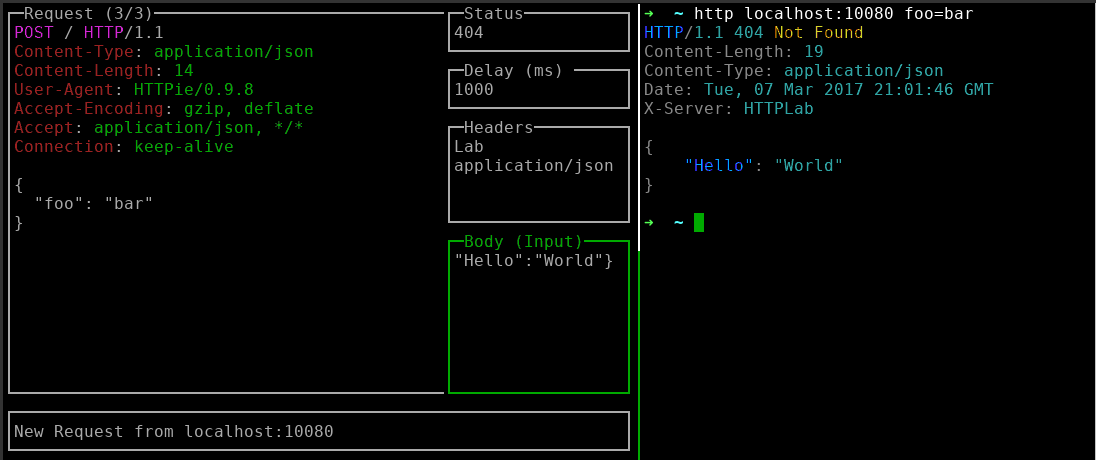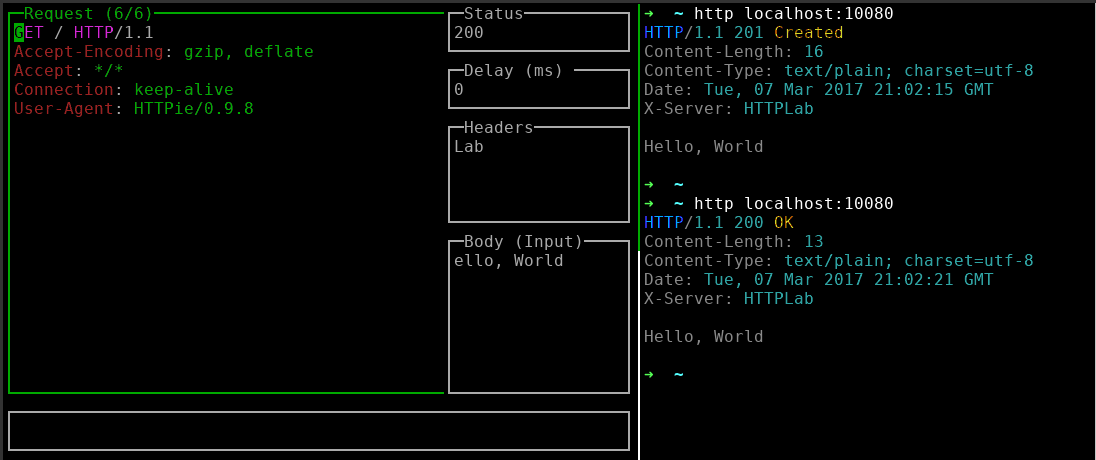
Interactive web server for inspecting HTTP requests and forging responses, with a terminal UI for real-time debugging and API testing.
api-security-testingdebuggersgeneral-purpose-utilities+1
4.2k
qustavo/httplabInteractive web server for inspecting HTTP requests and forging responses, with a terminal UI for real-time debugging and API testing.
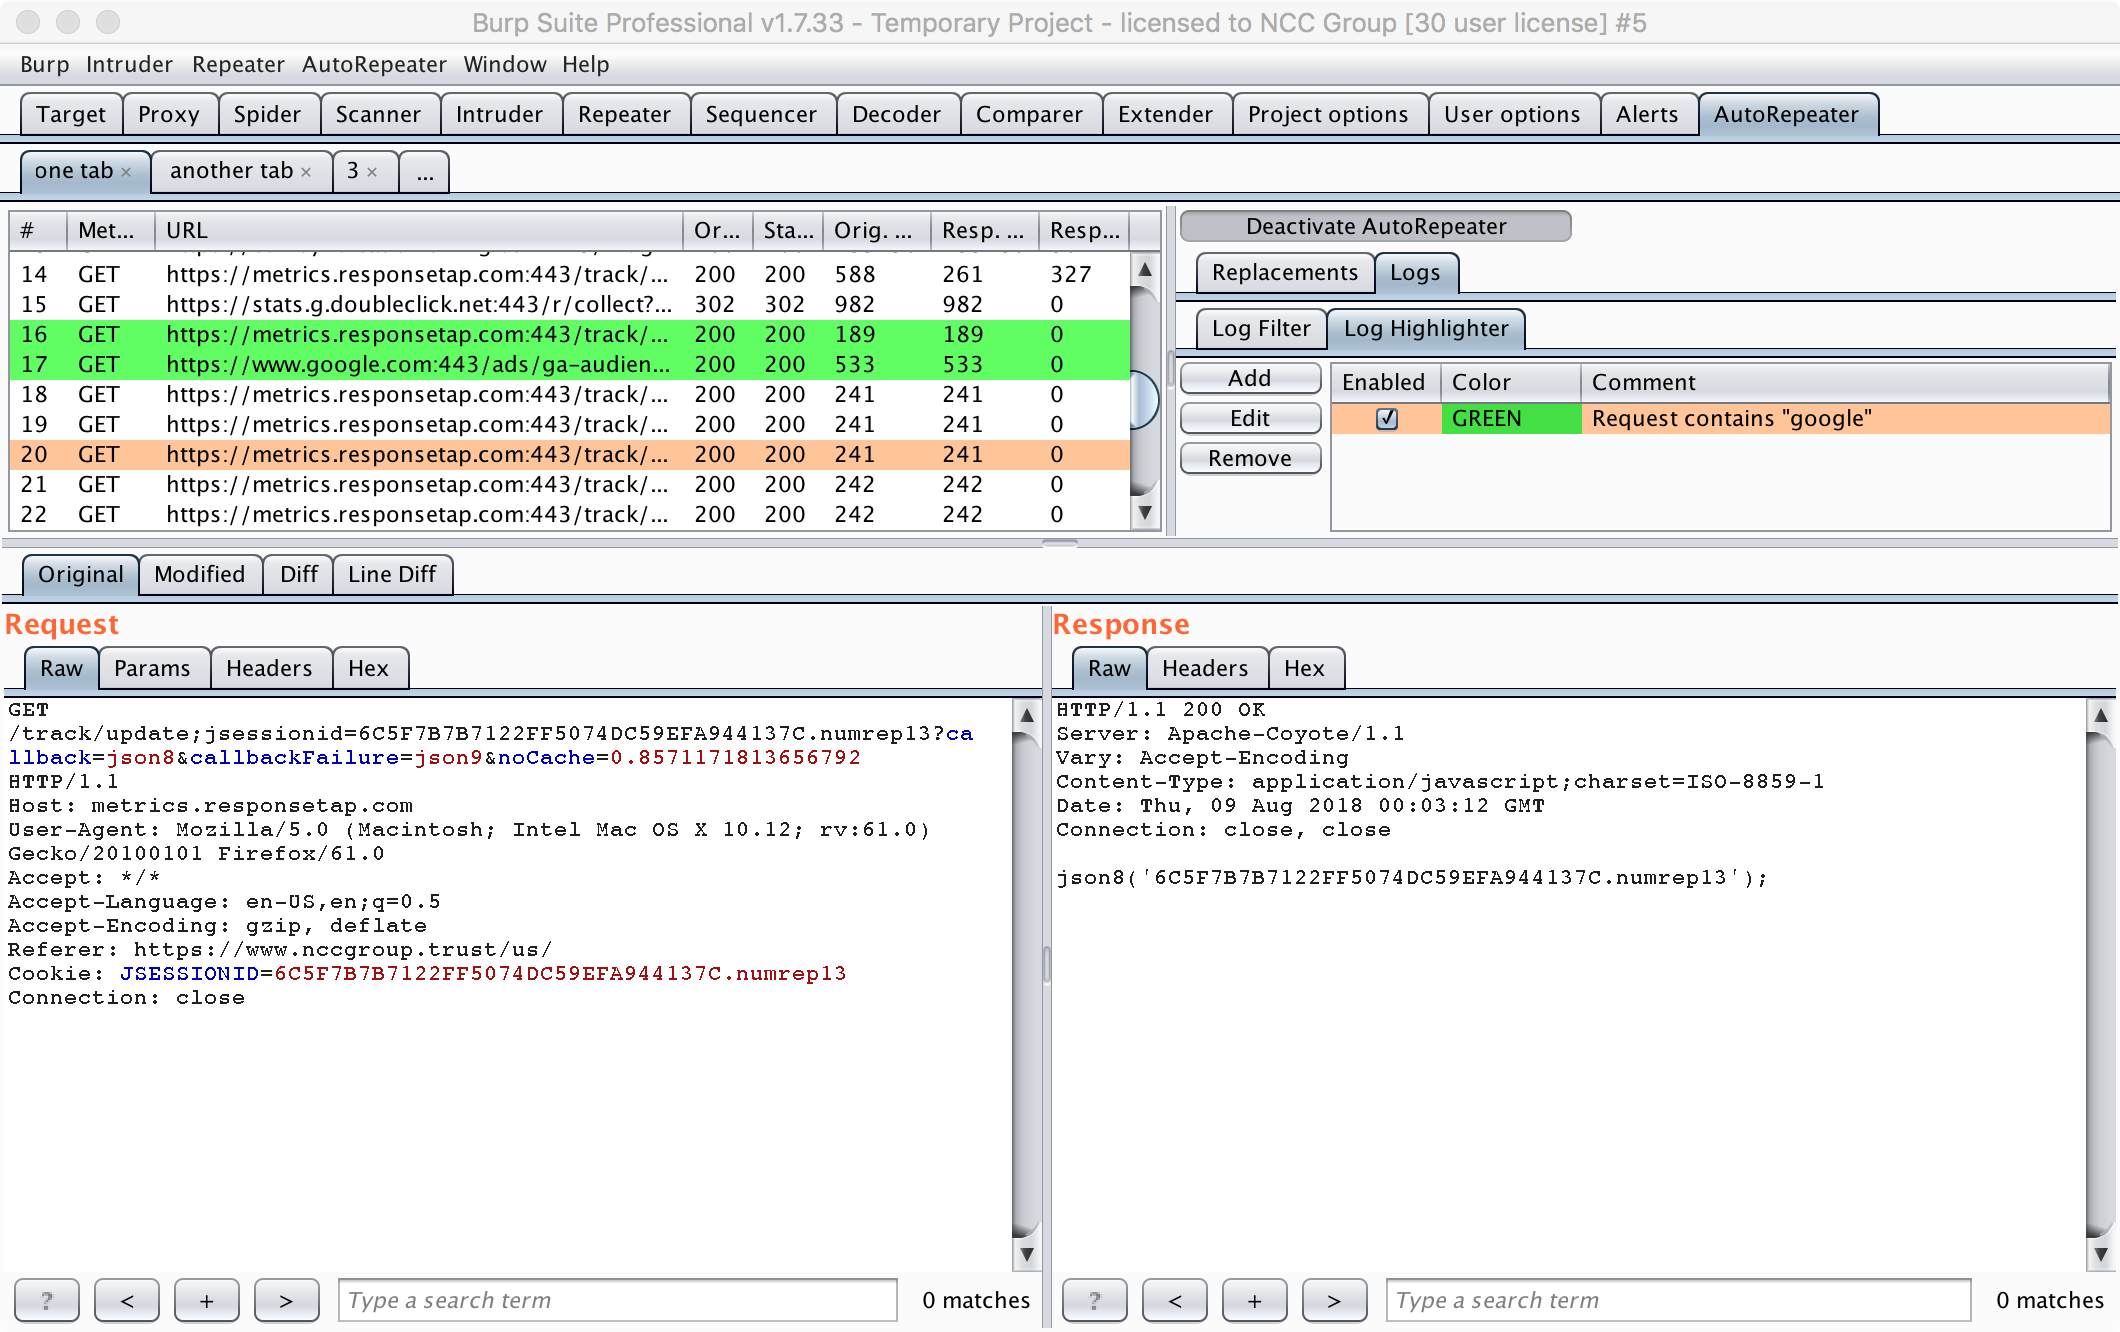 nccgroup/autorepeater
Automated HTTP Request Repeating With Burp Suite
 bifrost-proxy/bifrost
High-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and pentesting toolkit for the terminal built for humans and AI agents alike.
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 jas502n/burpsuite_pro_v1.7.37
Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…
 joanbono/gurp
Burp Commander written in Go
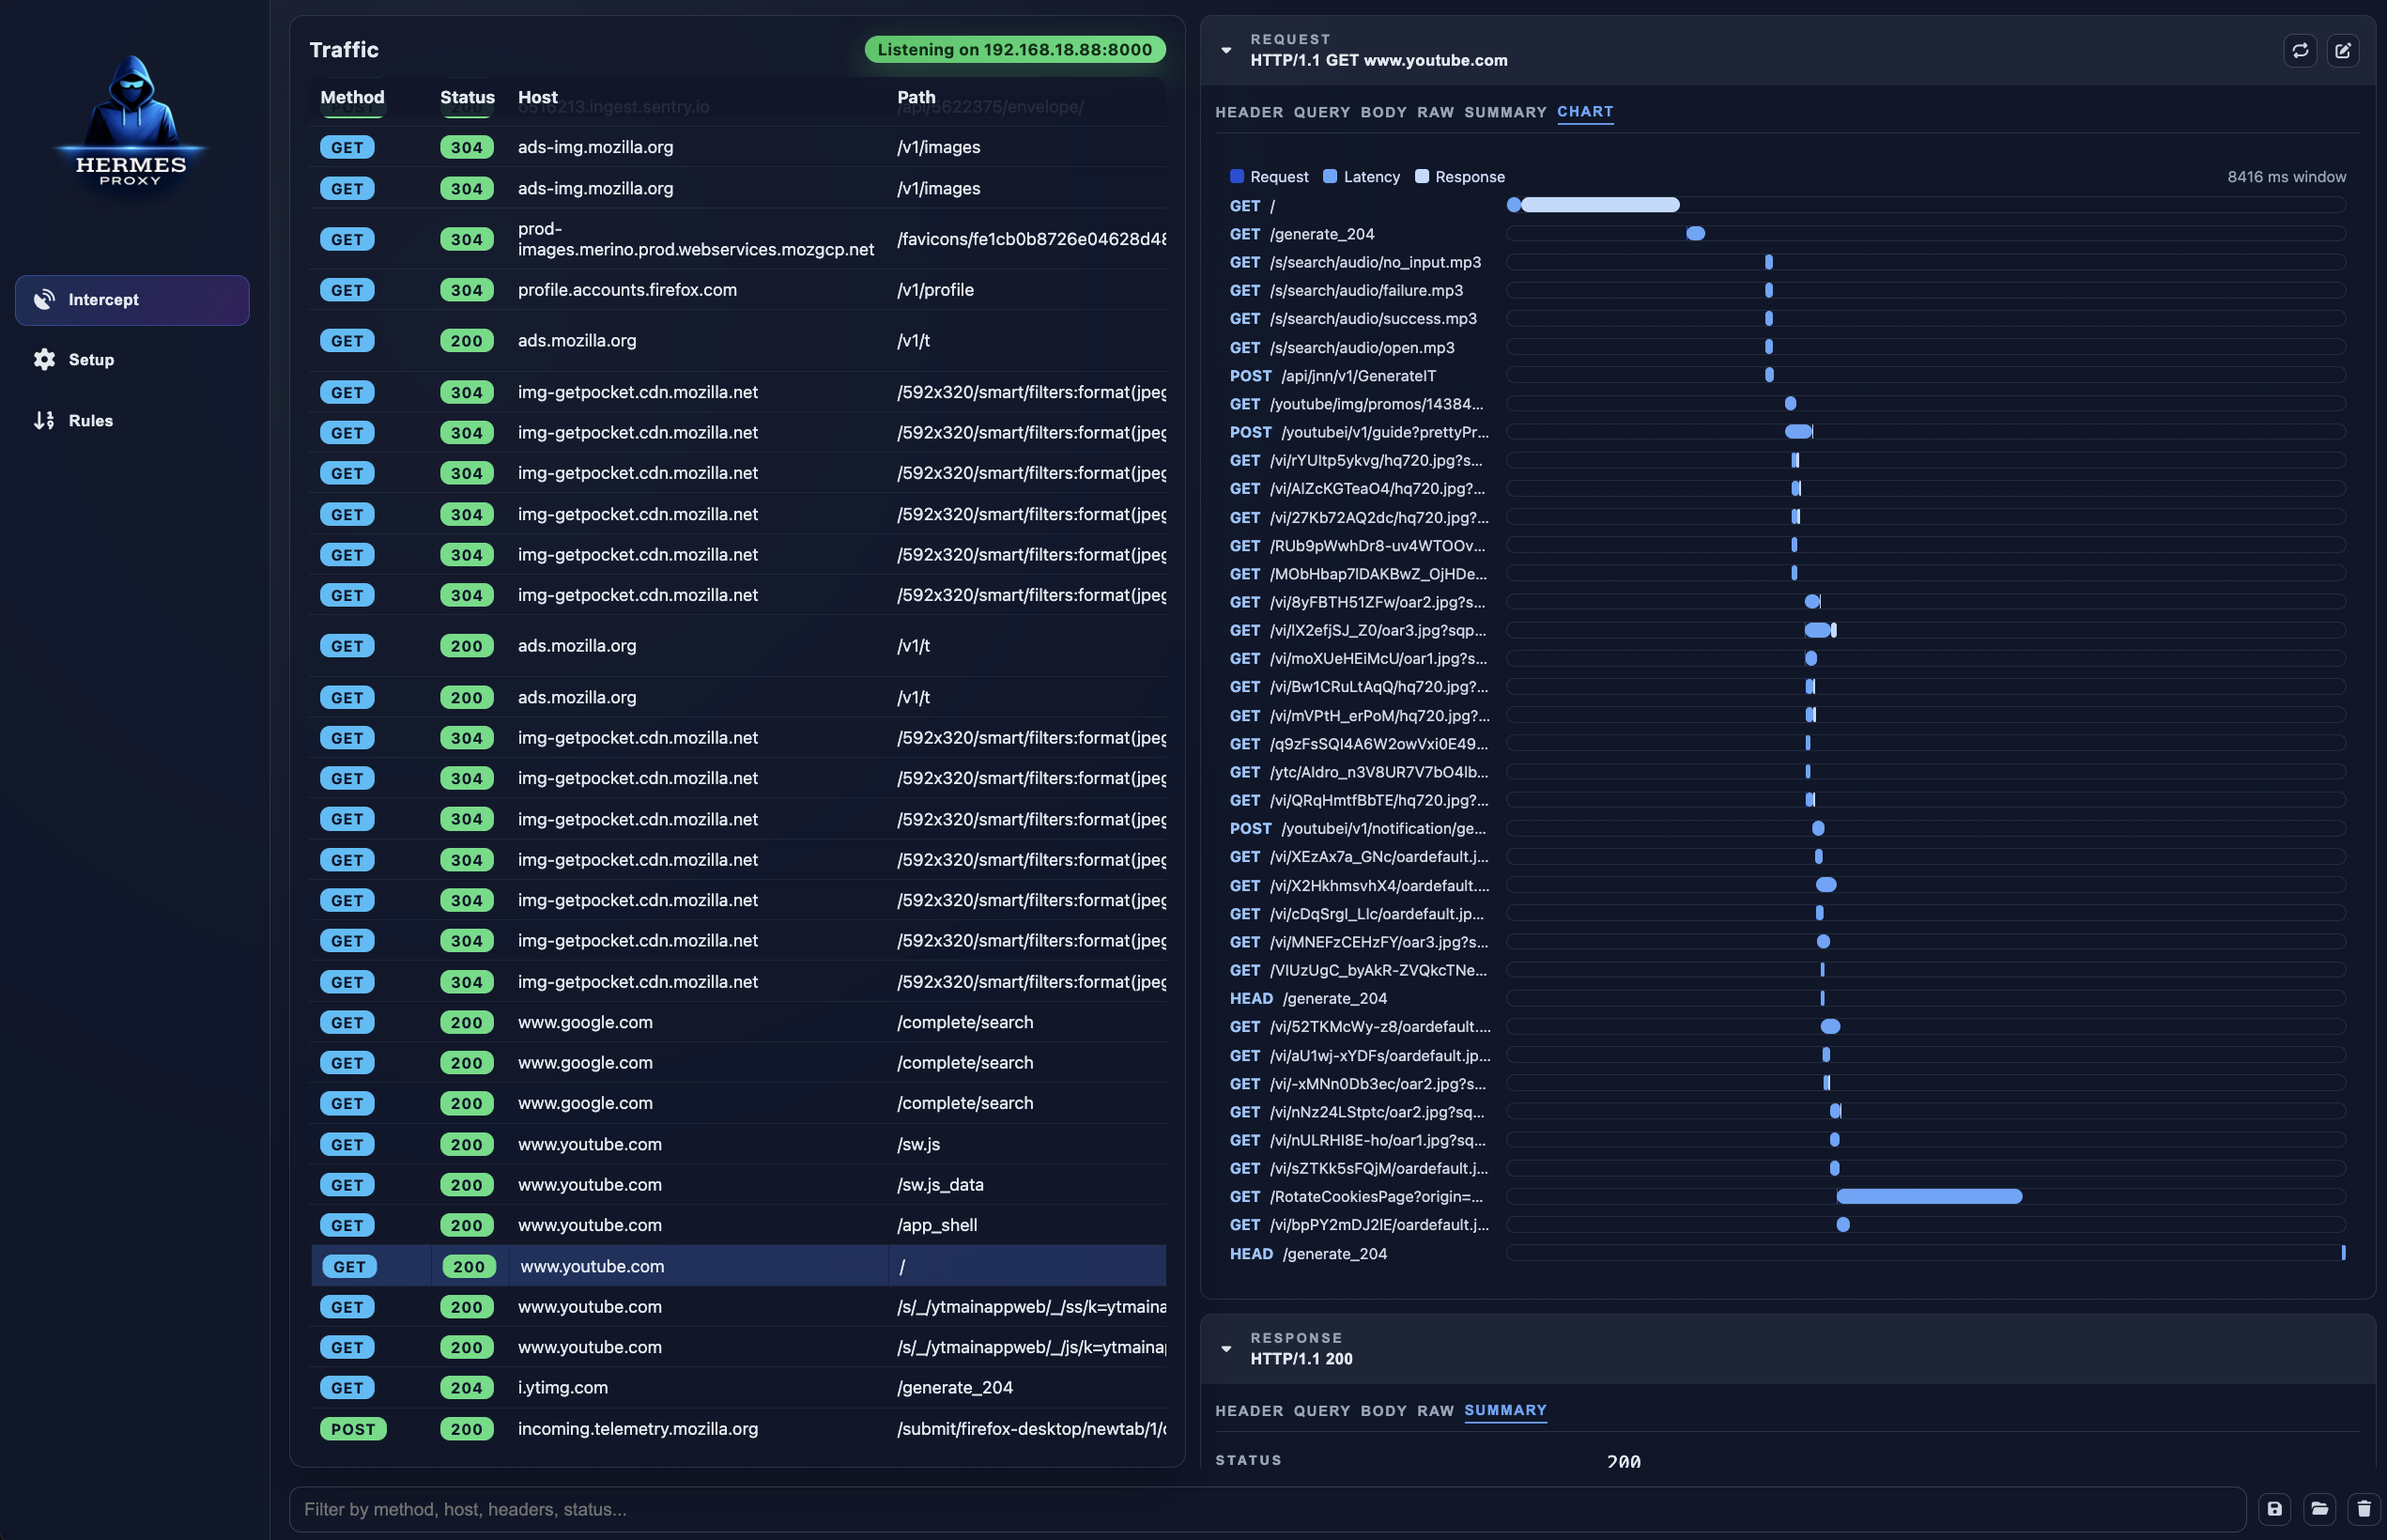 jp/hermes-proxy
Hermes Proxy - HTTP Traffic Analyzer
 nccgroup/wcfdser-ngng
A Burp Extender plugin, that will make binary soap objects readable and modifiable.
 projectdiscovery/collaborator
BurpSuite Standard/Private Collaborator Library
 emo-crab/slinger
An HTTP client specifically developed for security researchers
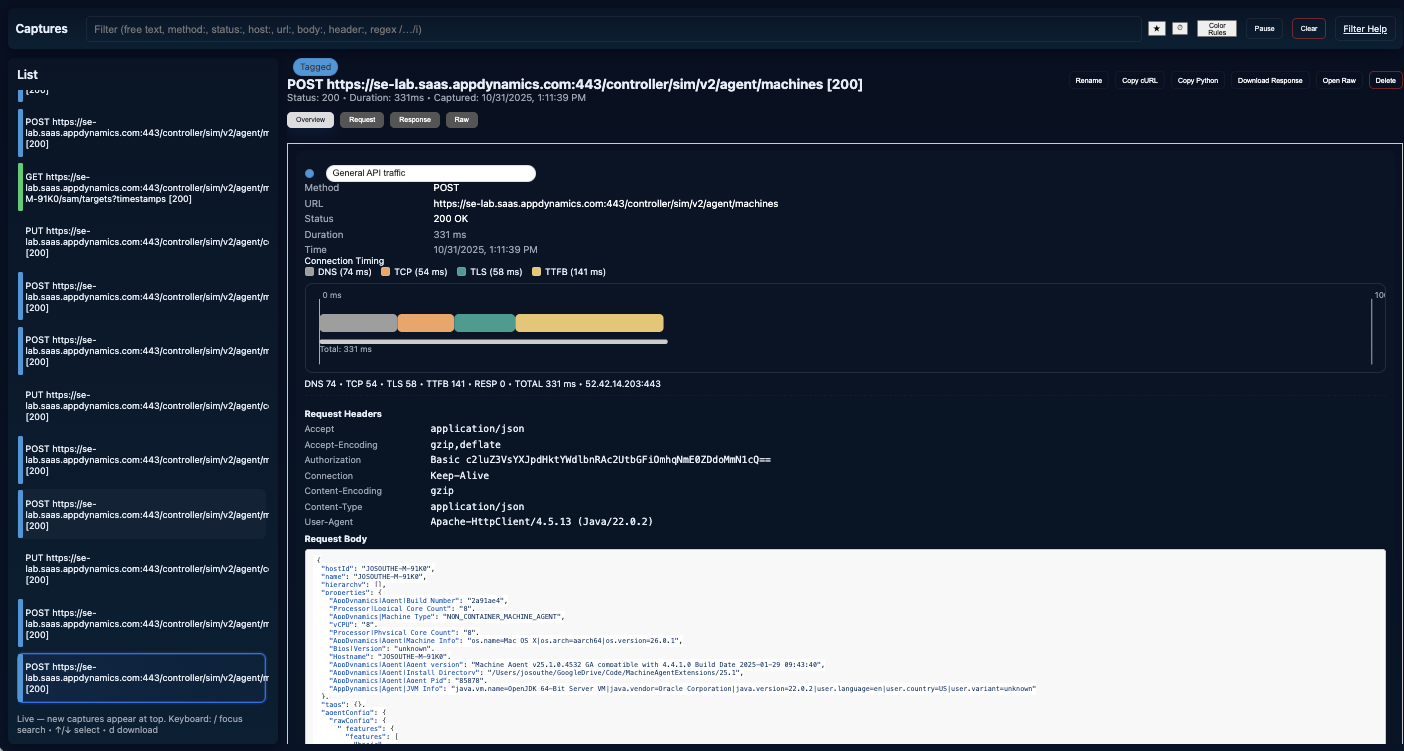 jbsouthe/http-breakout-proxy
HTTP Proxy Analysis for reverse engineering protocol communication
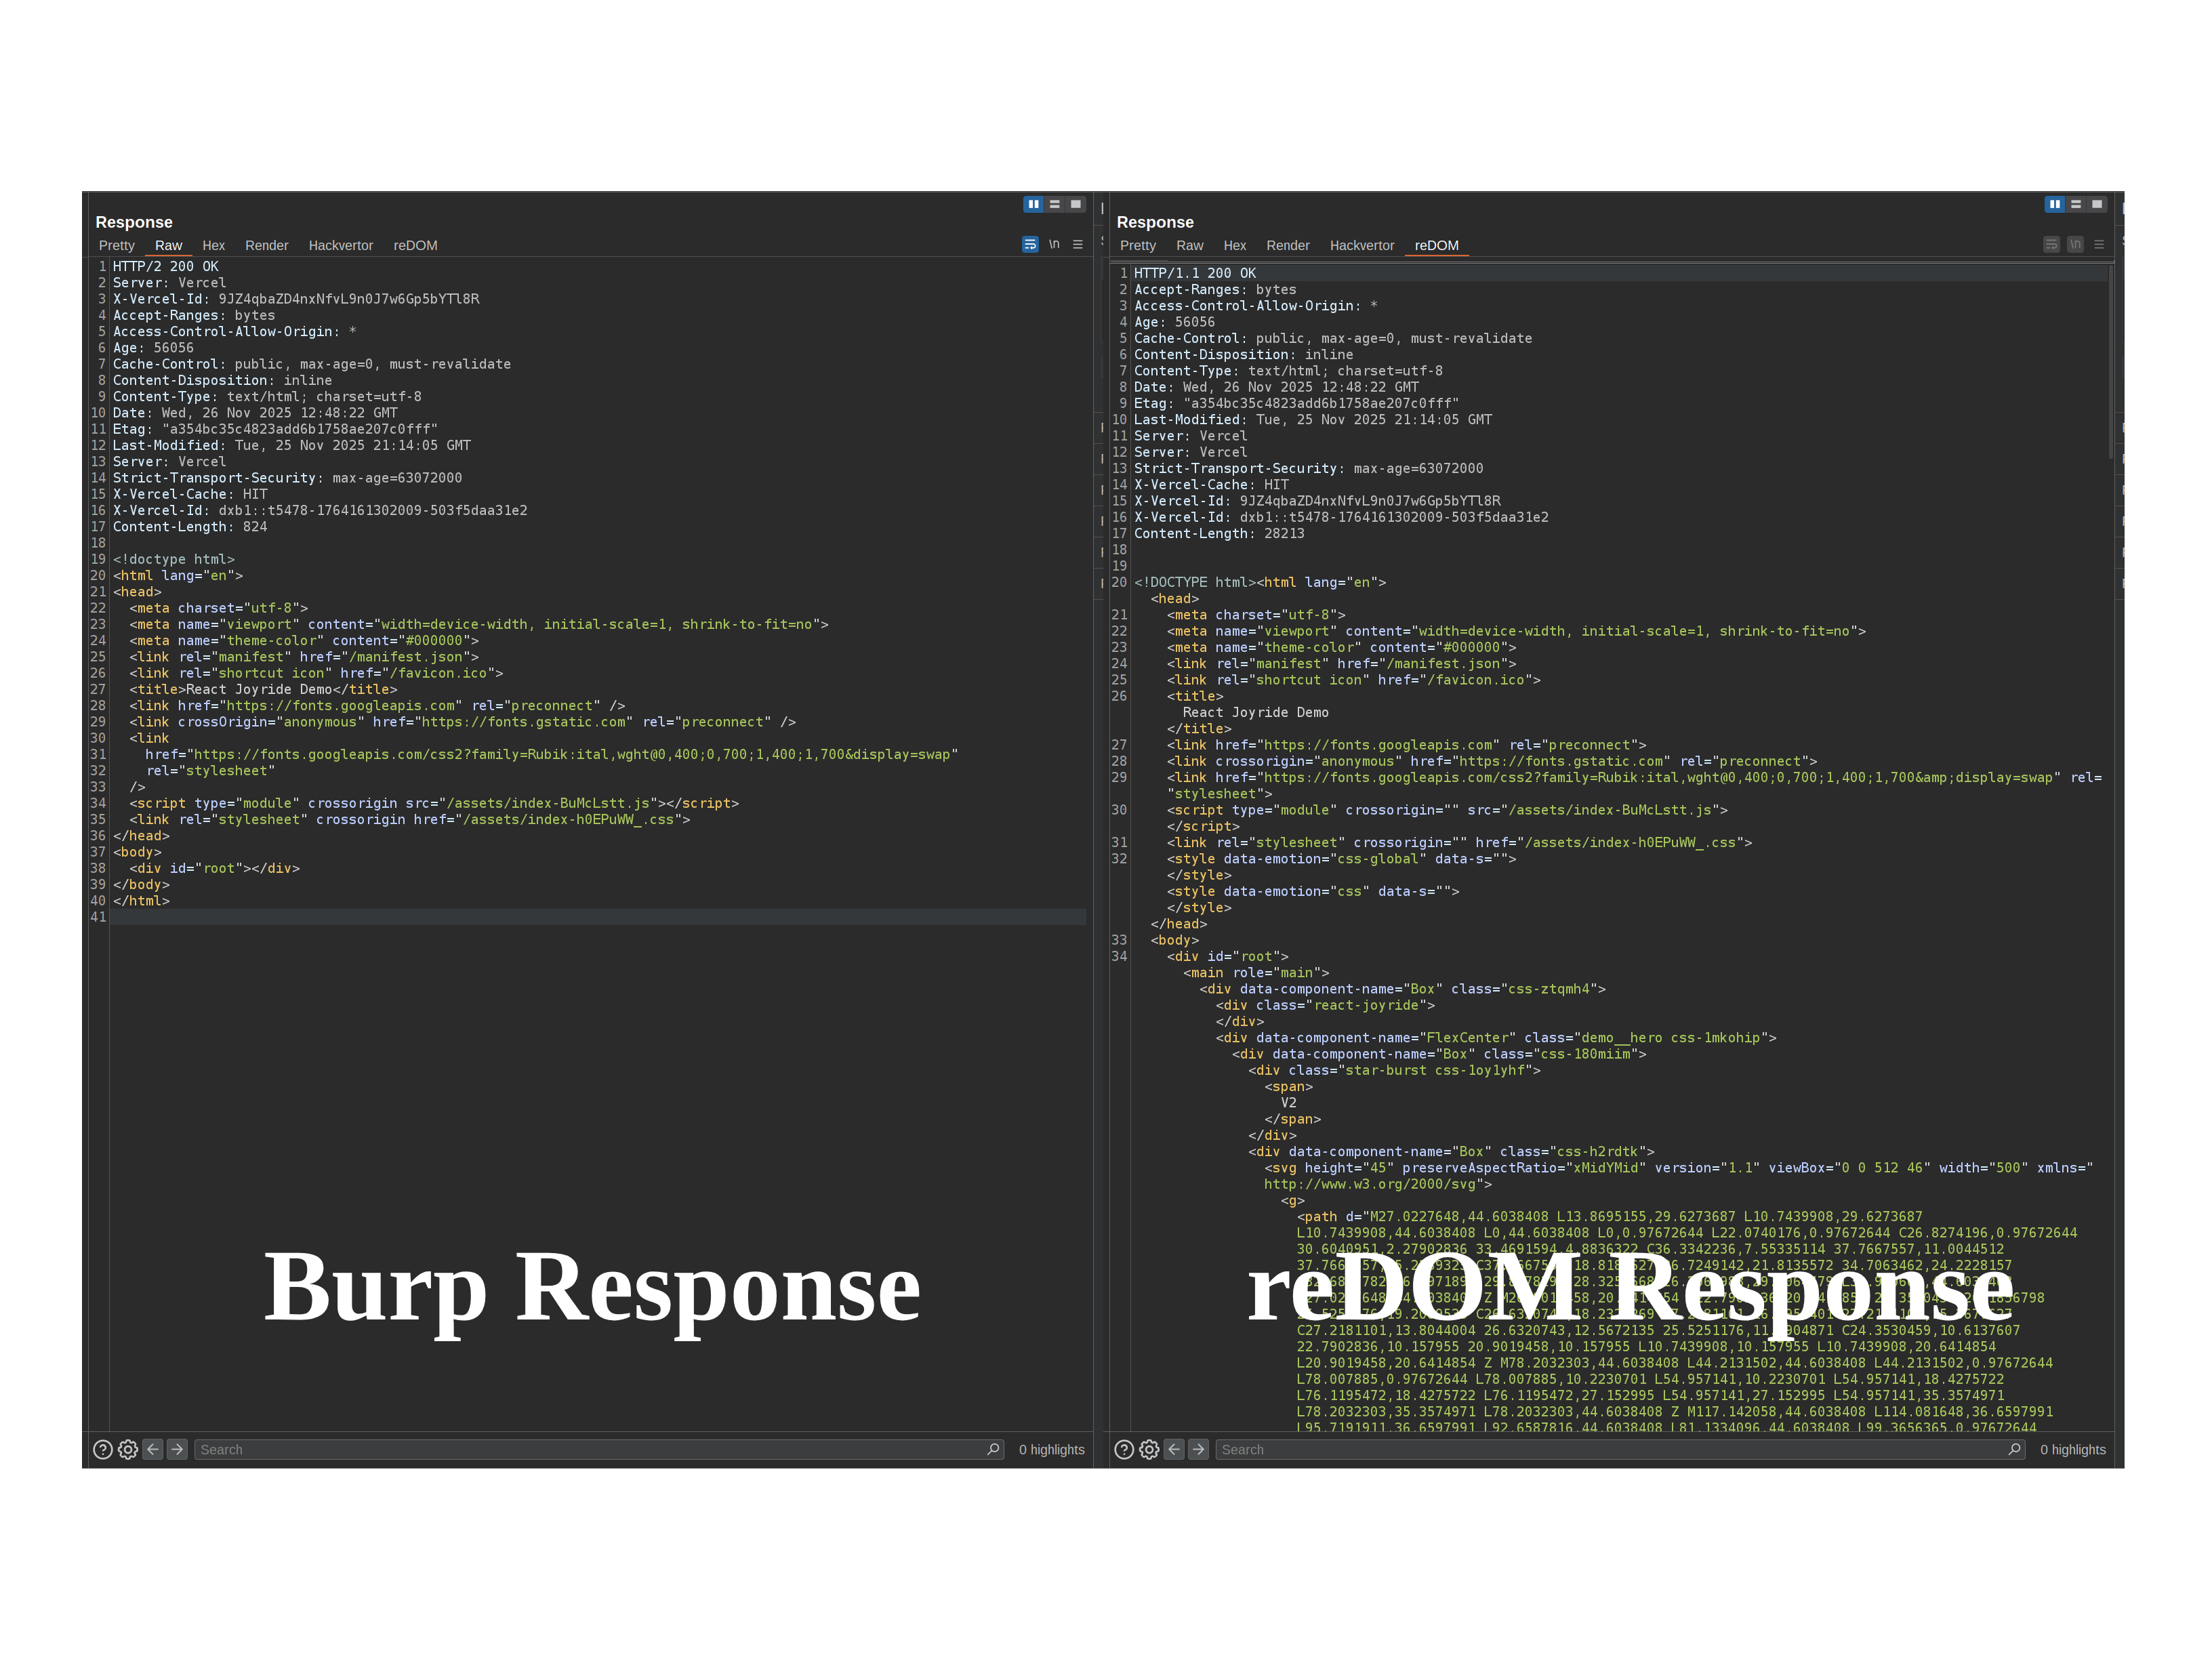 weirdmachine64/redom
A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy…
 vid4l-07/roxy
Terminal-based HTTP intercepting proxy with TUI for capturing, inspecting, and modifying requests in real time, plus a Repeater for resending and…
 t0xodile-swig/http3-adapter
Burp Suite extension that intercepts requests and sends them over HTTP/3, converting responses back for Burp, with support for kettled requests and…
 0xmarik/aresius
Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
 larrypeseckis/burp-cc-bridge
REST API automation for Burp Suite Community Edition. Drop-in Java extension exposing send/repeat/history endpoints over a local HTTP API.
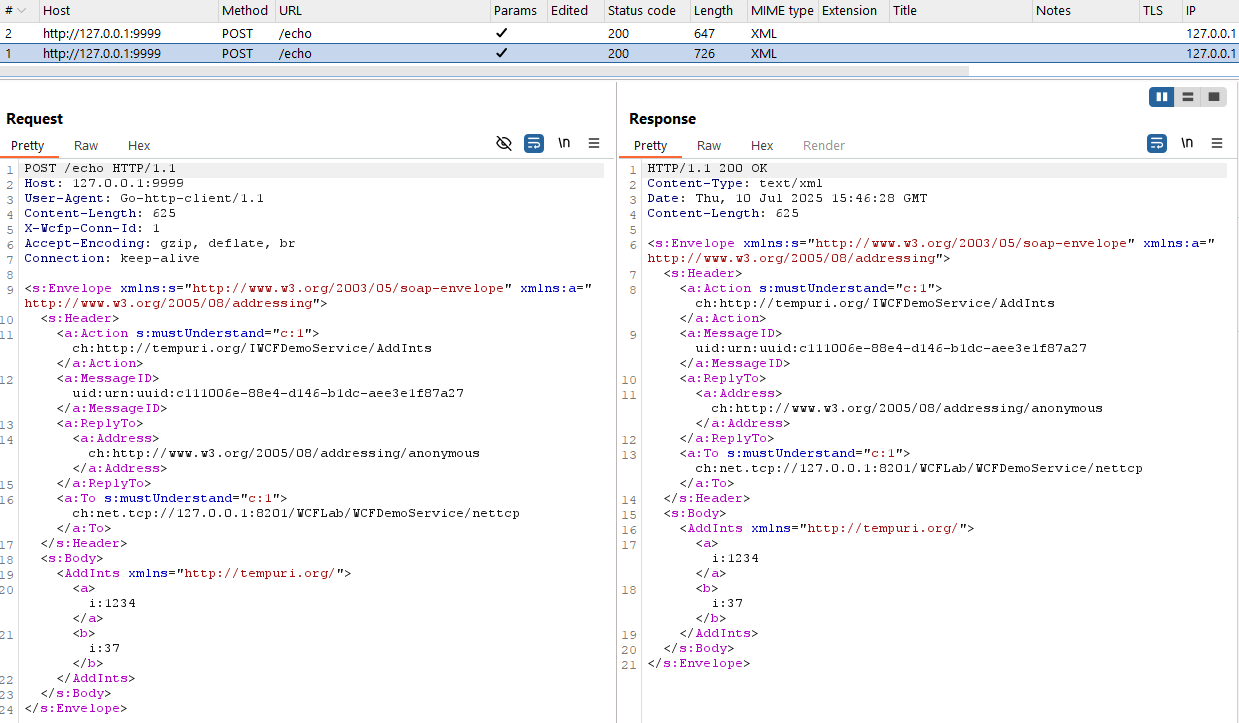 syss-research/wcfproxy
A proxy for net.tcp-based WCF traffic.