

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
httplab — Interactive web server for inspecting HTTP requests and forging responses, with a terminal UI for real-time debugging and API testing. | Kitploit
Tools/GitHubGitHub/qustavo/httplab
General Purpose UtilitiesWeb Proxies & InterceptionAPI Security TestingDebuggers
GitHubqustavo/httplab

httplab

Interactive web server for inspecting HTTP requests and forging responses, with a terminal UI for real-time debugging and API testing.

View Repository
4.2k122492 years agoReviewed by Kitploit
Share

HTTPLAB

Build Status Go Report Card PRs Welcome

The interactive web server.

HTTPLabs let you inspect HTTP requests and forge responses.
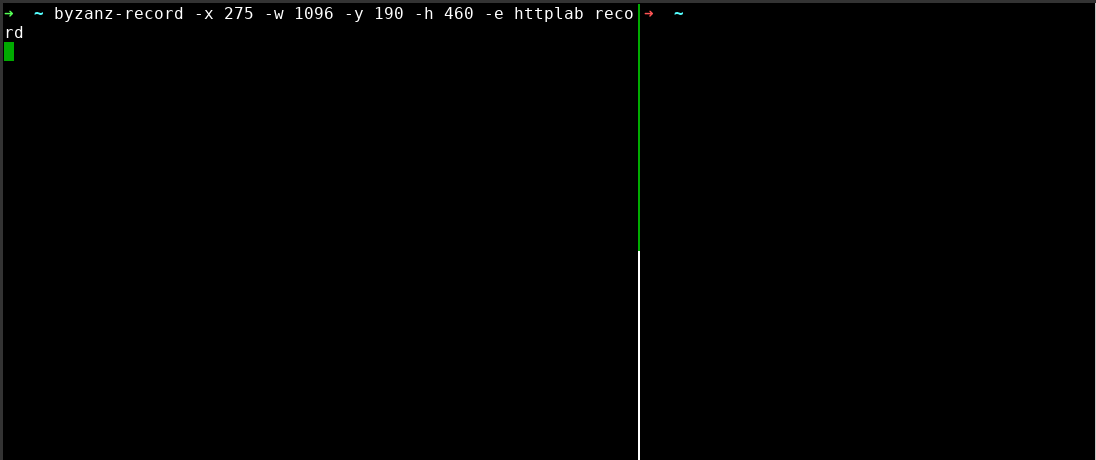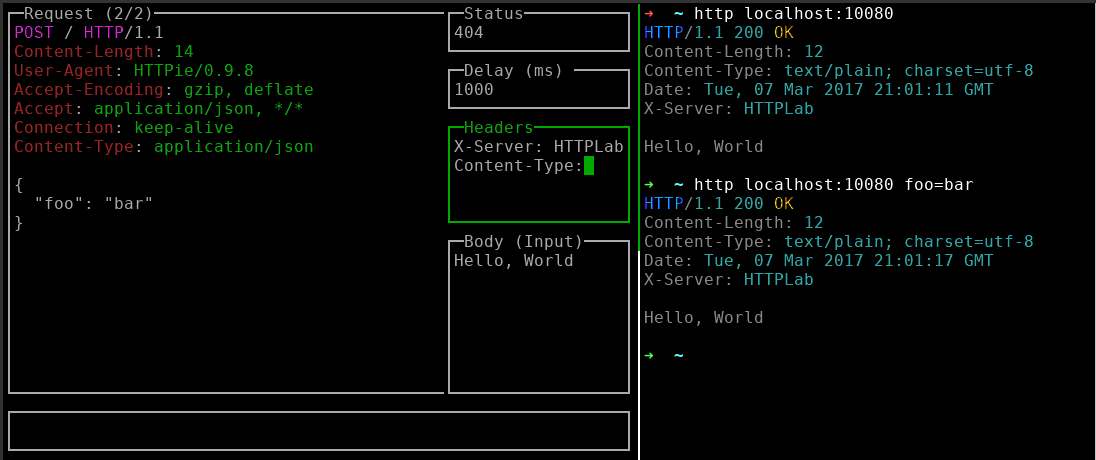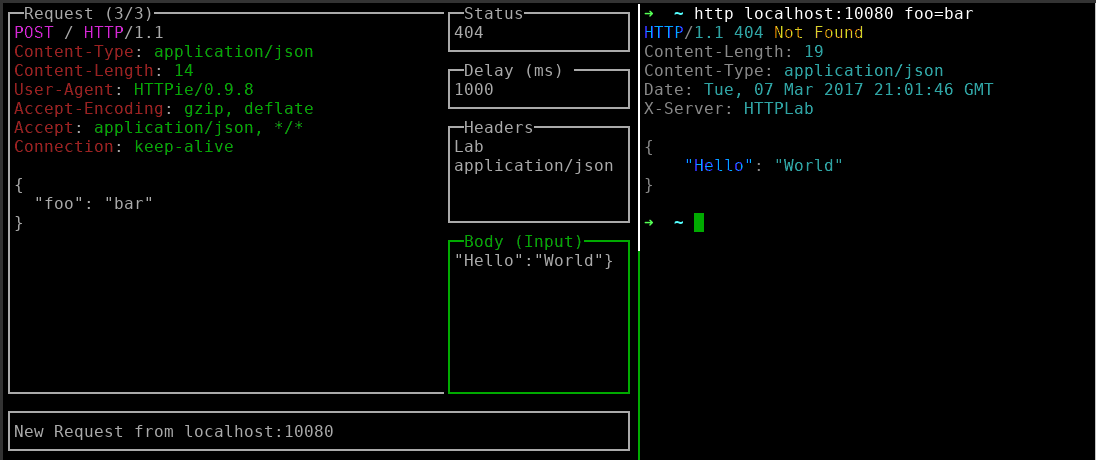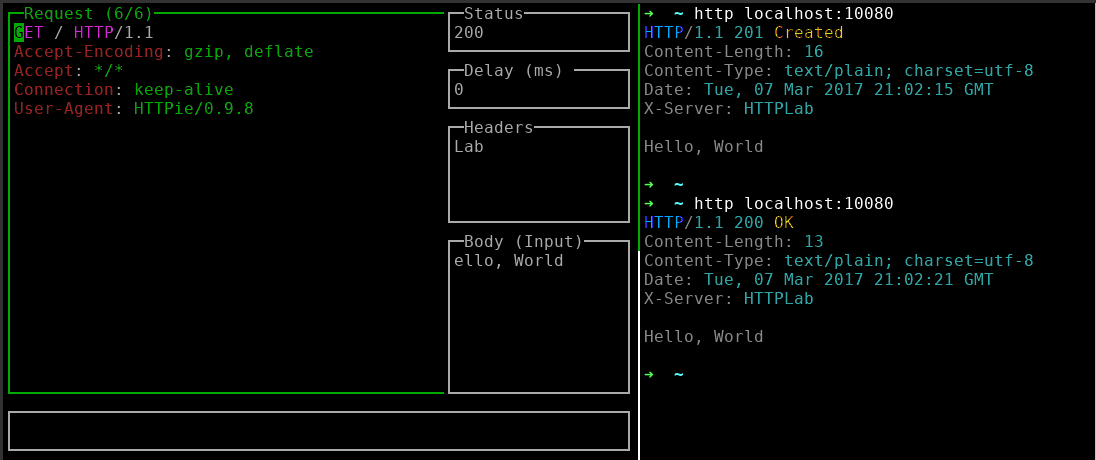

screencast

Install

Golang

go install github.com/gchaincl/httplab/cmd/httplab@latest

Archlinux

yaourt httplab

Snap FIXME

On systems where snap is supported:

snap install httplab

Binary distribution

Each release provides pre-built binaries for different architectures, you can download them here: https://github.com/gchaincl/httplab/releases/latest

Help

Usage of httplab:
  -a, --auto-update       Auto-updates response when fields change. (default true)
  -b, --body string       Specifies the inital response body. (default "Hello, World")
  -c, --config string     Specifies custom config path.
      --cors              Enable CORS.
      --cors-display      Display CORS requests. (default true)
  -d, --delay int         Specifies the initial response delay in ms.
  -H, --headers strings   Specifies the initial response headers. (default [X-Server:HTTPLab])
  -p, --port int          Specifies the port where HTTPLab will bind to. (default 10080)
  -s, --status string     Specifies the initial response status. (default "200")
  -v, --version           Prints current version.

Key Bindings

KeyDescription
TabNext Input
Shift+TabPrevious Input
Ctrl+aApply Response changes
Ctrl+rResets Request history
Ctrl+sSave Response as
Ctrl+fSave Request as
Ctrl+lToggle Responses list
Ctrl+tToggle Response builder
Ctrl+oOpen Body file
Ctrl+bSwitch Body mode
Ctrl+hToggle Help
Ctrl+wToggle line wrapping
qClose popup
PgUpPrevious Request
PgDownNext Request
Ctrl+cQuit

HTTPLab uses file to store pre-built responses, it will look for a file called .httplab on the current directory if not found it will fallback to $HOME. A sample file can be found here.

HTTPLab is heavily inspired by wuzz

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    516
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    476
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    355
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    315
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    303
  • 6

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    285

Explore all tools

Browse our collection of tools

View all tools →





