
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
reDOM — A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy applications built with frameworks like ReactJS, VueJS, Angular, and more. | Kitploit
Tools/GitHubGitHub/weirdmachine64/redom
Dynamic Analysis (Sandboxing)Vulnerability AnalysisWeb Proxies & InterceptionWeb Application ExploitationAPI Security TestingInformation GatheringWeb SecurityPenetration Testing
GitHubweirdmachine64/redom

reDOM

A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy applications built with frameworks like ReactJS, VueJS, Angular, and more.

153406 months agoNot yet reviewed
Share
View Repository

reDOM

  ██████╗ ███████╗██████╗  ██████╗ ███╗   ███╗
  ██╔══██╗██╔════╝██╔══██╗██╔═══██╗████╗ ████║
  ██████╔╝█████╗  ██║  ██║██║   ██║██╔████╔██║
  ██╔══██╗██╔══╝  ██║  ██║██║   ██║██║╚██╔╝██║
  ██║  ██║███████╗██████╔╝╚██████╔╝██║ ╚═╝ ██║
  ╚═╝  ╚═╝╚══════╝╚═════╝  ╚═════╝ ╚═╝     ╚═╝

A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy applications built with frameworks like ReactJS, VueJS, Angular, and more.
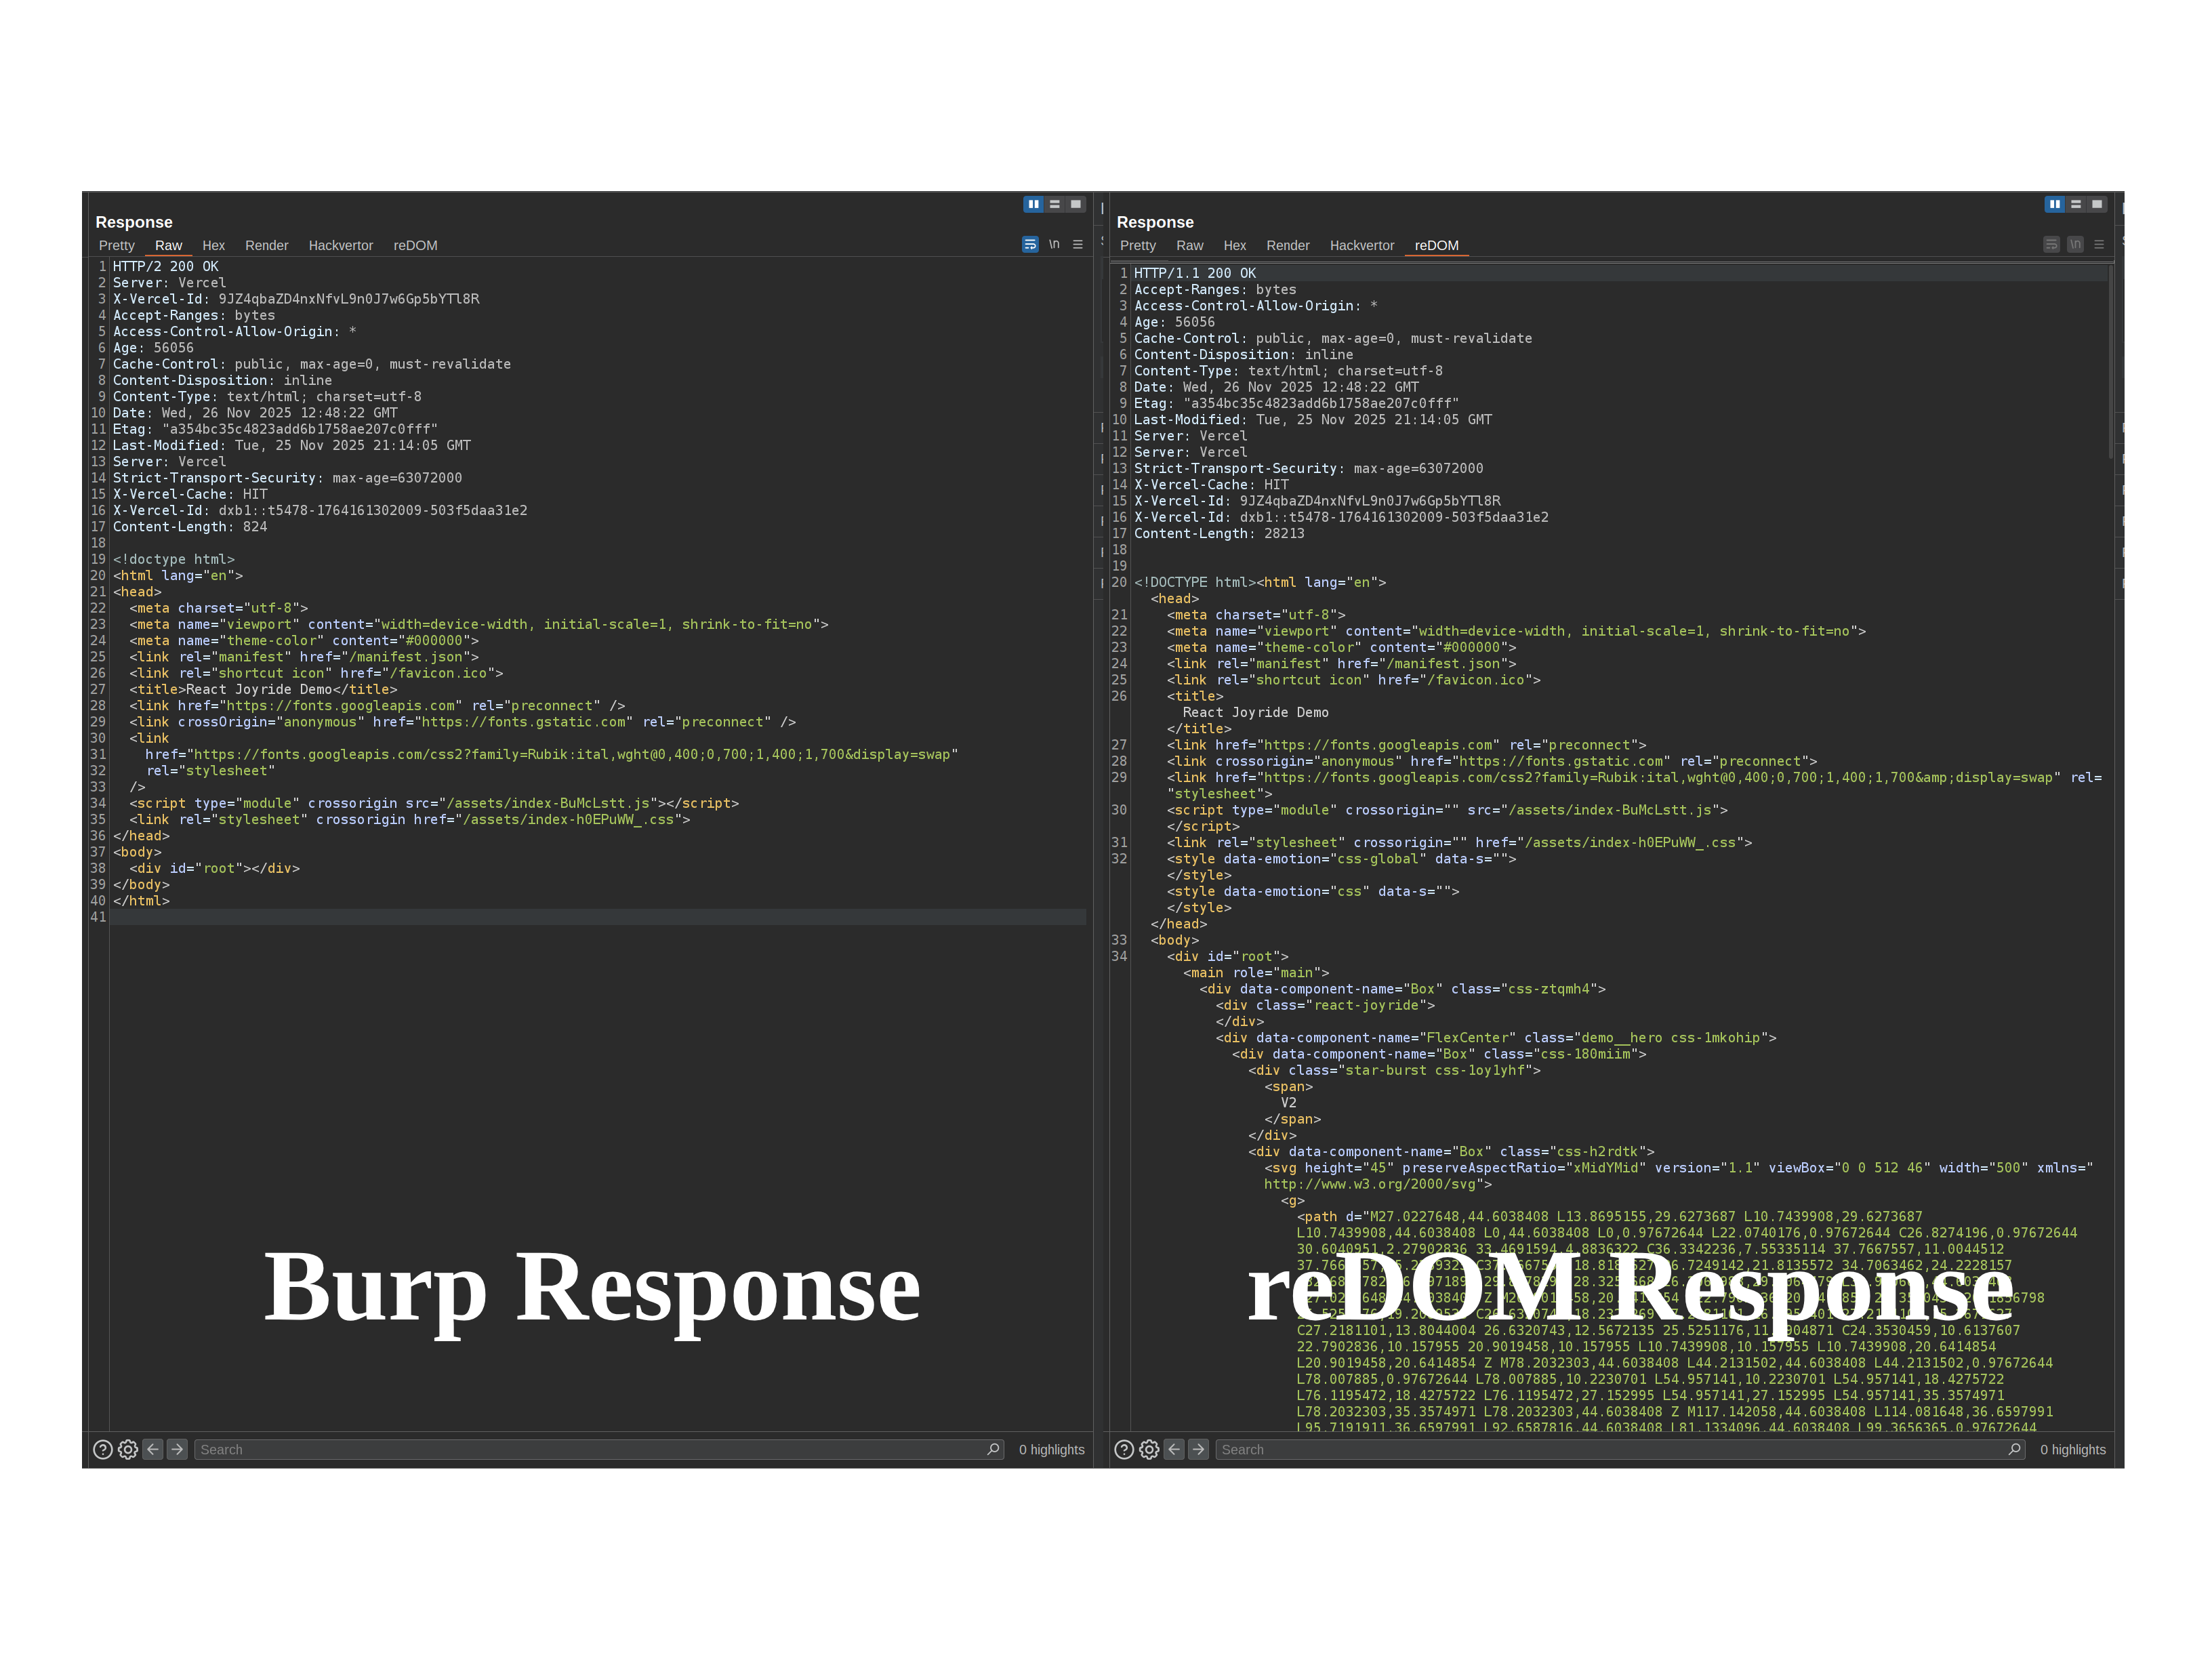
reDOM vs Native Burp Response

Features

  • Captures fully-rendered DOM after JavaScript execution
  • Analyzes Single Page Applications (SPAs) built with React, Vue.js, Angular, etc.
  • Integrates as a custom response tab in Burp Repeater
  • Launches and manages the browser directly from the extension
  • Configurable rendering and connection parameters

Requirements

  • Burp Suite Professional/Community
  • Chrome/Chromium browser

Installation

  1. Build the extension:

    mvn clean package
    
  2. Load target/reDOM.jar in Burp Suite (Extensions → Add)

Usage

  1. Load the extension — the settings panel opens automatically

  2. Configure browser path, upstream proxy, and profile directory as needed

  3. Click Launch & Connect to start the browser and connect

  4. Send a request to Repeater and switch to the DOM Render tab

Configuration

SettingDescriptionDefault
Browser pathPath to the Chromium executablechromium
Upstream proxyBurp proxy addresslocalhost:8080
Profile directoryBrowser profile to use/tmp/redom
Accept invalid certificatesTrust self-signed and invalid TLS certson
Launch browser on startupAutomatically launch browser when extension loadsoff
Host / PortRemote debugging addresslocalhost:9222
Command timeoutCDP command timeout30s
Post-load delayWait time after page load for JS to settle1000ms
Load timeoutMaximum time to wait for page load30s
Render on tab selectionRender automatically when the DOM Render tab is openedon
Pretty-print HTMLFormat the rendered HTML outputon

License

MIT License

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    916
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    558
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    370
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    317
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →






