
extloader
 synacktiv/extloader
A chromium extension exploitation toolkit
exploitationinformation-gatheringpenetration-testing+4
synacktiv/extloaderA chromium extension exploitation toolkit
 dxc-strikeforce/burp-log4j-hammertime
Burp Active Scan extension to identify Log4j vulnerabilities CVE-2021-44228 and CVE-2021-45046
 vulnbe/burpsuite-copy-as-xmlhttprequest
BurpSuite extension that converts HTTP requests into JavaScript XMLHttpRequest code for streamlined XSS proof-of-concept generation and web…
 portswigger/http-request-smuggler
Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…
 jackadamson/cve-2021-26700
Proof-of-concept for CVE-2021-26700: remote code execution in the VSCode npm-script extension via malicious workspace settings.json, with detailed…
 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…
 crynomore/cve-2024-34102
Burp Suite extension for detecting and testing CVE-2024-34102, a critical web vulnerability, enabling automated security assessment and exploitation…
 hoodoer/js-tap
JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
 shinthink/pbck-exploit
📤 Mass exploitation framework for CVE-2026-56290 — Page Builder CK Joomla unauthenticated file upload to RCE
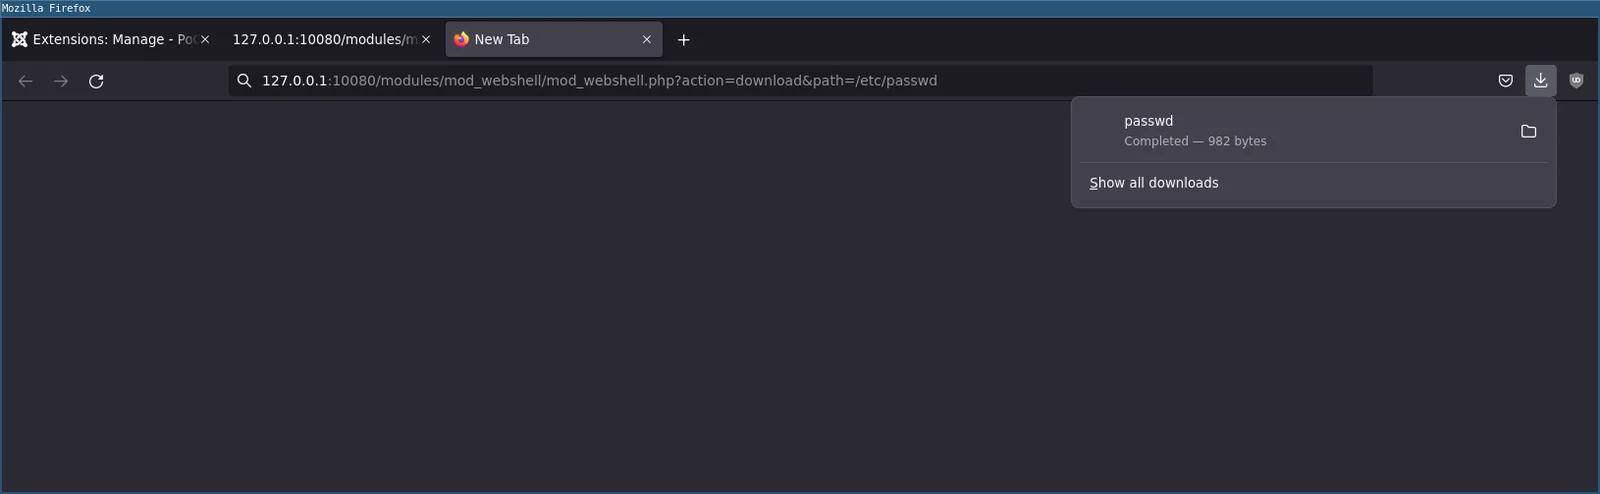 p0dalirius/joomla-webshell-plugin
A webshell plugin and interactive shell for pentesting a Joomla website.
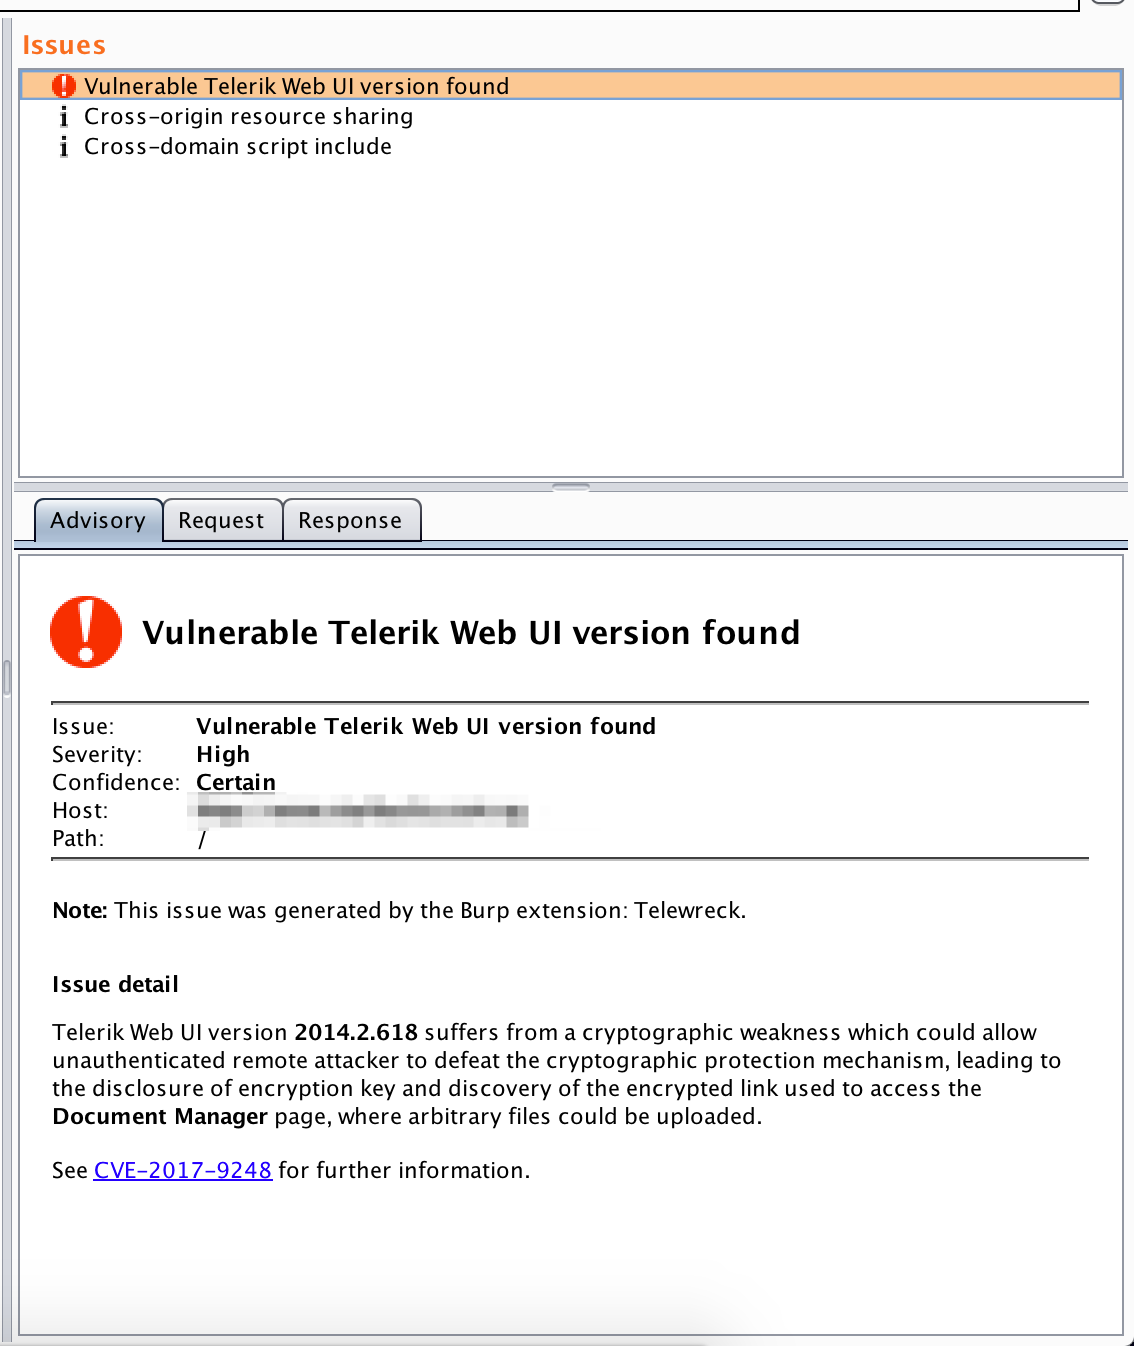 capt-meelo/telewreck
A Burp extension to detect and exploit versions of Telerik Web UI vulnerable to CVE-2017-9248.
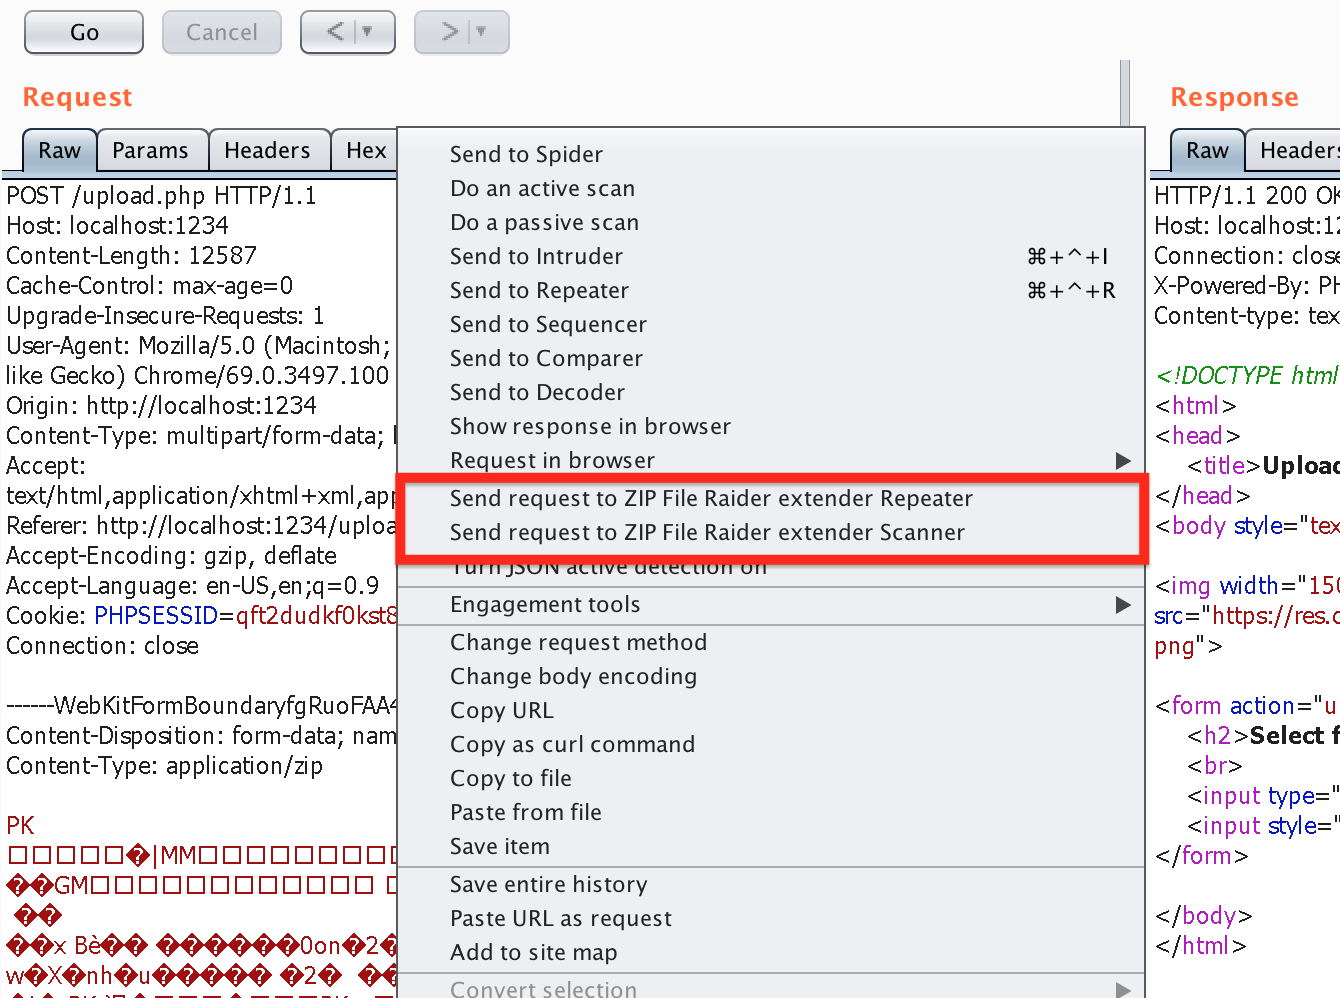 destine21/zipfileraider
ZIP File Raider - Burp Extension for ZIP File Payload Testing
 0xdexter0us/log4j-scanner
Burp extension to scan Log4Shell (CVE-2021-44228) vulnerability pre and post auth.
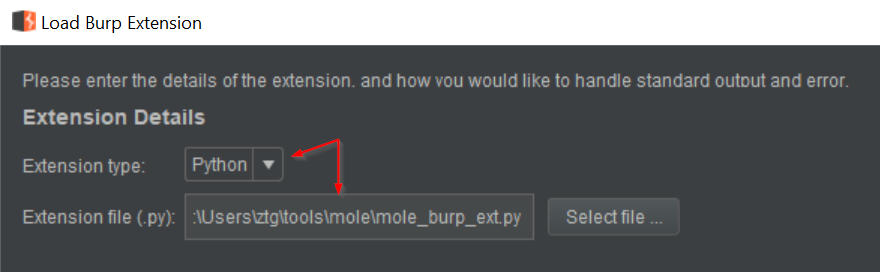 ztgrace/mole
Framework for identifying and exploiting out-of-band (OOB) application vulnerabilities with a custom DNS/token server, Burp Suite extension, and…
 t0xodile/crlf-powered-desync-scanner
Burp extension scanner for CRLF injection and HTTP desync attacks, using mutated probes, WAF false-positive checks, and optional…
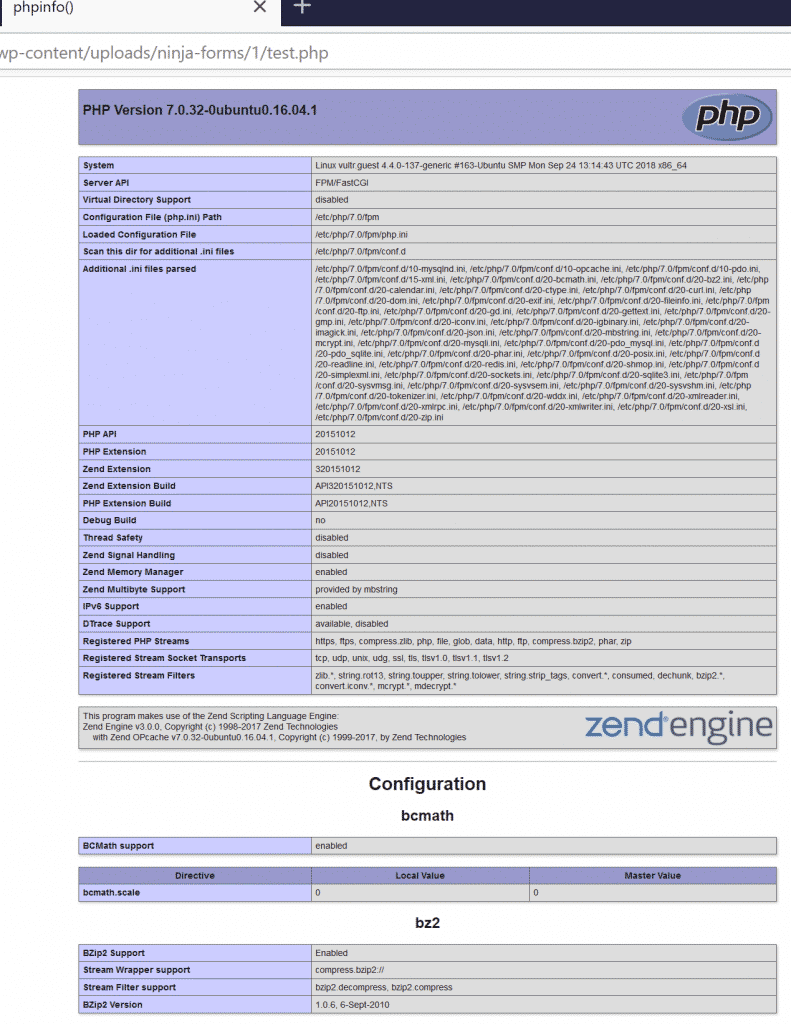 ktn1990/cve-2019-10869
(Wordpress) Ninja Forms File Uploads Extension <= 3.0.22 – Unauthenticated Arbitrary File Upload
 f0ng/text4shellburpscanner
Burp Suite extension for detecting CVE-2022-42889 (Text4Shell) vulnerability via passive scanning of HTTP requests and responses.
 r00tjunip3r1/poc-cve-2024-6778
Proof-of-concept exploit for CVE-2024-6778, a Chromium sandbox escape via a malicious browser extension, achieving code execution on privileged WebUI…