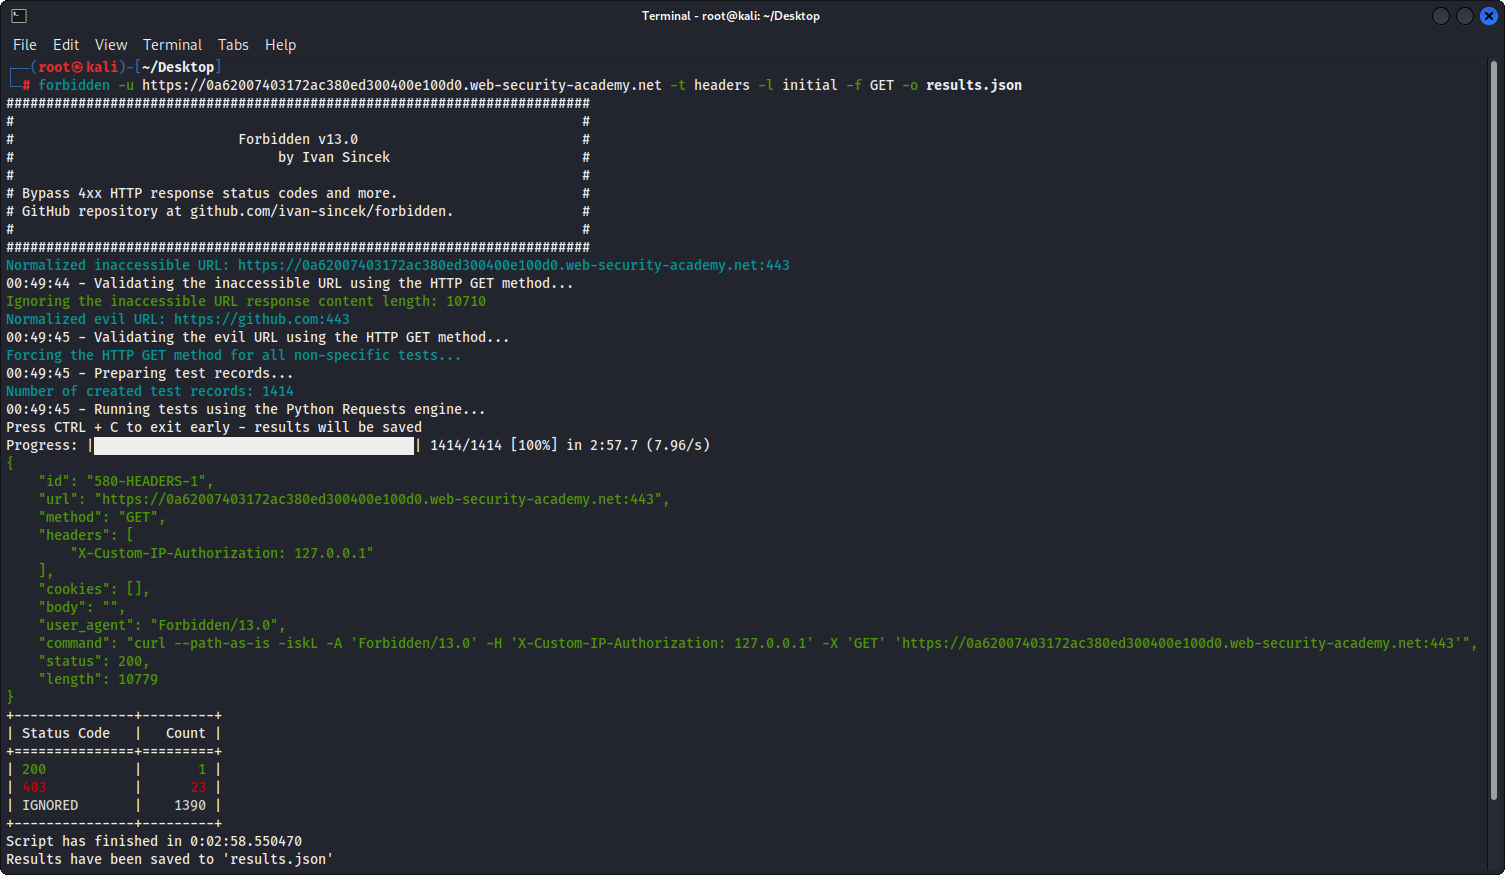
 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.

Bypass 4xx HTTP response status codes and more.
The tool is based on Python Requests, PycURL, and HTTP Client.
Tested on Kali Linux v2024.2 (64-bit).
Made for educational purposes. I hope it will help!
Future plans:
silent option to suppress console output.no color option to disable colored console output.hop-by-hop HTTP request headers.User-Agent HTTP request header.On Kali Linux, this should work without issues; otherwise, run:
apt-get -y install libcurl4-gnutls-dev librtmp-dev

pip3 install --upgrade pycurl
PycURL on Windows OS is not supported.
On macOS, run:
brew uninstall curl
brew uninstall openssl

brew install curl
brew install openssl

echo 'export PATH="/opt/homebrew/opt/curl/bin:$PATH"' >> ~/.zshrc
echo 'export PATH="/opt/homebrew/opt/openssl@3/bin:$PATH"' >> ~/.zshrc
source ~/.zshrc

export LDFLAGS="-L/opt/homebrew/opt/curl/lib"
export CPPFLAGS="-I/opt/homebrew/opt/curl/include"
export PYCURL_SSL_LIBRARY=openssl

pip3 install --no-cache-dir --compile --ignore-installed --config-setting="--with-openssl=" --config-setting="--openssl-dir=/opt/homebrew/opt/openssl@3" pycurl
Alternatively, install using Homebrew (not maintained by me):
brew install forbidden
pip3 install --upgrade forbidden
git clone https://github.com/ivan-sincek/forbidden && cd forbidden

python3 -m pip install --upgrade build

python3 -m build

python3 -m pip install dist/forbidden-13.4-py3-none-any.whl
Bypass 403 Forbidden HTTP response status code:
forbidden -u https://example.com/admin -t protocols,methods,uploads,overrides,headers,paths-ram,encodings -f GET -l initial,path -o forbidden_403_results.json
Bypass 403 Forbidden HTTP response status code with stress testing:
mkdir stresser_403_results

stresser -u https://example.com/admin -r 1000 -th 200 -f GET -l initial -dir stresser_403_results -o stresser_403_results.json
Bypass 401 Unauthorized HTTP response status code:
forbidden -u https://example.com/admin -t auths -f GET -l initial -o forbidden_401_results.json
Test for open redirects and broken URL parsers, i.e., test for out-of-band (OOB) interactions:
forbidden -u https://example.com/admin -t redirects,parsers -f GET -l initial -e xyz.interact.sh -o forbidden_oob_results.json
protocols
Host HTTP request header, using an IP address and domain name.methods
Content-Length: 0 HTTP request header.uploads
overrides
Host HTTP request headers.headers
values
paths
encodings
auths
redirects
parsers
If you're interested in more details, see:
Remarks:
unique filter is applied before anything is sent.Forbidden and Stresser use the Python Requests engine.Host HTTP request header is locked to the HTTP Client engine. Additionally, the provided cURL command will not work properly because cURL does not allow removing the Host HTTP request header.Host HTTP request headers is locked to the Python Requests engine. Additionally, the provided cURL command will not work properly because cURL does not allow using two Host HTTP request headers.PycURL engine.normalize URLs (e.g., when testing encodings), modify HTTP requests, or drop HTTP requests entirely.User-Agent HTTP request header.rate limiting and other similar anti-bot protections; take some time before running the tool again on the same domain.This is just a quick overview of what is used, but not how it is used.
ACL
ARBITRARY
BASELINE-CONTROL
BIND
CHECKIN
CHECKOUT
CONNECT
COPY
DELETE
GET
HEAD
INDEX
LABEL
LINK
LOCK
MERGE
MKACTIVITY
MKCALENDAR
MKCOL
MKREDIRECTREF
MKWORKSPACE
MOVE
OPTIONS
ORDERPATCH
PATCH
POST
PRI
PROPFIND
PROPPATCH
PUT
REBIND
REPORT
SEARCH
SHOWMETHOD
SPACEJUMP
TEXTSEARCH
TRACE
TRACK
UNBIND
UNCHECKOUT
UNLINK
UNLOCK
UPDATE
UPDATEREDIRECTREF
VERSION-CONTROL
This is just a quick overview of what is used, but not how it is used.
