

Bantam
An advanced PHP backdoor management tool, with a lightweight server footprint, multi-threaded communication, and an advanced payload generation and obfuscation tool. Features end to end encryption with request unique encryption keys, and payload streaming designed to bypass WAF, IDS, SIEM systems. It incorporates several
payload randomization and obfuscation techniques to help prevent detection when encryption is not possible. Bantam is an ideal tool for linux PHP post exploitation privesc making it a breeze to upload enumeration scripts. Bantam also has a plugin system making it easy to add scripts and features to the ui.
It is programmed in C# and runs on windows, and Linux using wine.
Features
End to end request & response encryption - encryption flow
- AES-256 bit encryption on request & response data using openssl or mcrypt
- Response encryption keys are newly generated and embedded into the request payload for every request making every response unique, preventing detection from WAF and IDS systems
- Request encryption keys can be embedded using a pre-shared key/iv, or use a pre-shared key with a randomly generated IV that is passed through a known request variable making every request signature unique
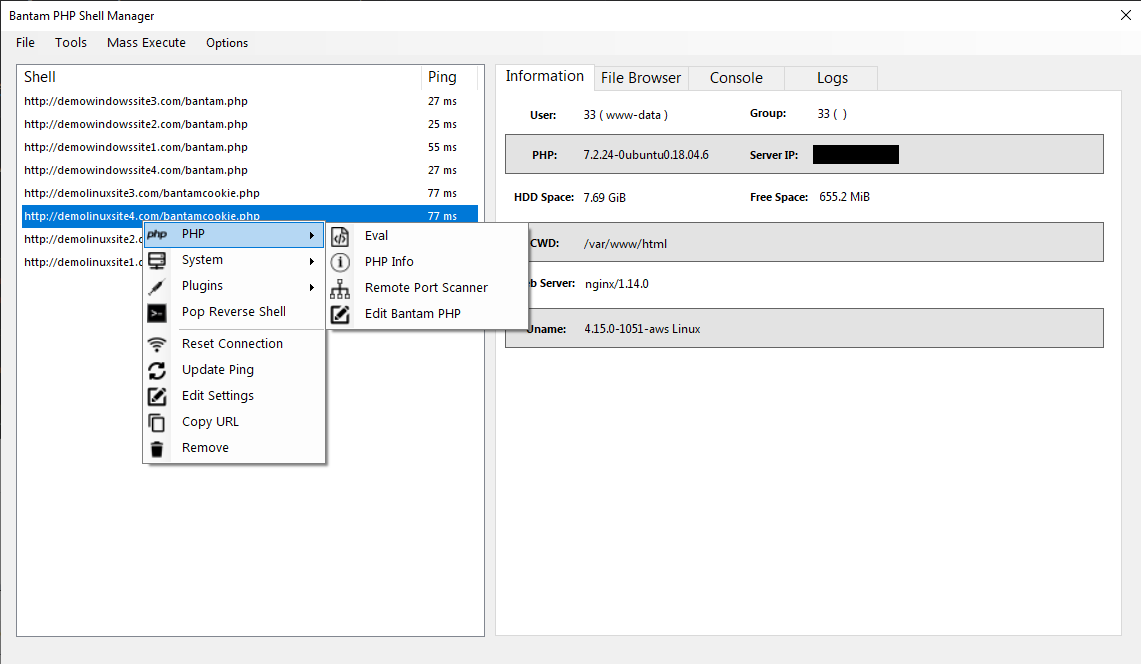
Main form - [img]
- Get Shell Information - [img]
- Add Shell - [img]
- Eval tool - Opens a text editor that will eval the input text as a php payload
- Remote port scanner - Uses the bantam server to scan remote ports
- PHPInfo viewer - Opens the phpinfo page in an html window
- Self Editor - Edit the Bantam code stored on the server
- Linux - Helpful cmds and files. Dynamically included from settings.xml (passwd, ps aux, ifconfig, ..etc)
- Wndows - Helpful cmds and files. Dynamically included from settings.xml (net user, hosts, ipconfig, ..etc)
- Windows Screenshot Grabber - Grabs a screenshot of the current screen
- Plugins - Dynamically include a php payload into the ui to be executed by setting up a plugin into the settings.xml
- Reset connection - Removes the current shell and session info from ui, re-adds the shell and tests the connection
- Update ping - Updates the ping to the selected shell
- Edit settings - Opens the current shell settings into the ui to modify
- Copy url - Copyies the shell url to the clipboard
- Remove - Removes the shell from the ui
- Save Shells to xml
- Open Saved Shells from XML
Reverse Shell - [img]
- Spawns a reverse shell to the indicated IP/Port
- Methods supported - perl, netcat, netcat with pipe, telnet with pipe, php, bash, python, barrage(all)
- Bypass disabled_functions & open_basedir with chankro
Backdoor generator - [img]
- Generates a php backdoor payload tailored for your settings
User Agent Switcher
- Randomize or customize the useragent used in requests
Proxy Settings
- Supports Socks and HTTP proxies
Mass Execute
- Executes php payloads on all servers
- Port Scanner - Distributed port scan that splits the work between selected servers and port scans a remote host - [img]
- Plugins - Dynamically include a custom payload from the settings.xml into the gui to be mass executed
File Browser - [img]
- Transverses file directories, and saves directory tree during current session
- Copy File
- Read File Content
- Delete file
- Rename File
- Upload File
- Send shell commands to the server using the vector selected in options form, saves history during current session
Logs
- Shows various logs and errors that could be generated by the application or server, adjustable verbosity in options form.
- Logging
- Log level - Determines which logs will be shown, higher level will show more logs
- Enable Global logs
- Request settings
- Max execution time - allows requests to run for max php execution time
- Disable error logs - disables error logging for requests
- Shell code vector - Shell code execution method (system/exec/shell_exec/passthru/popen/backticks)
- Timeout (milliseconds) - Default request timeout
- Max Post size (KiB) - Default max post size
- Max Cookie size (B) - Locked to 4096 bytes
- Request Obfuscation
- Inject Random Comments
- Injects comments with random text into the php payloads
- Comment frequency - Determines how many locations to inject comments into
- Max Length - Determines the max length of the comments
- Randomize PHP Var Names
- Randomizes variable names in php payloads, Always on
- Max length - Determines the max length of the random php varnames
Credits
- Socks Sharp - Socks proxy handler for HttpClient
- Chankro - Disabled functions / Open Base Dir bypass

 gellin/bantam










