
 warflop/cloudbunny
CloudBunny is a tool to capture the real IP of the server that uses a WAF as a proxy or protection. In this tool we used three search engines to search domain information: Shodan, Censys and Zoomeye.

CloudBunny is a tool to capture the origin server that uses a WAF as a proxy or protection.
You can read more about the tool here: https://tinyurl.com/y8p48wb3
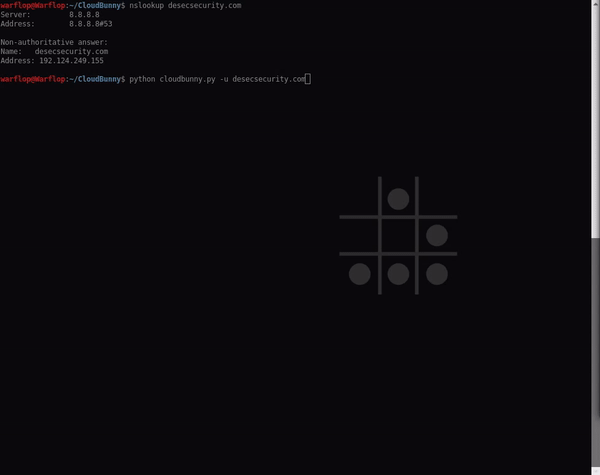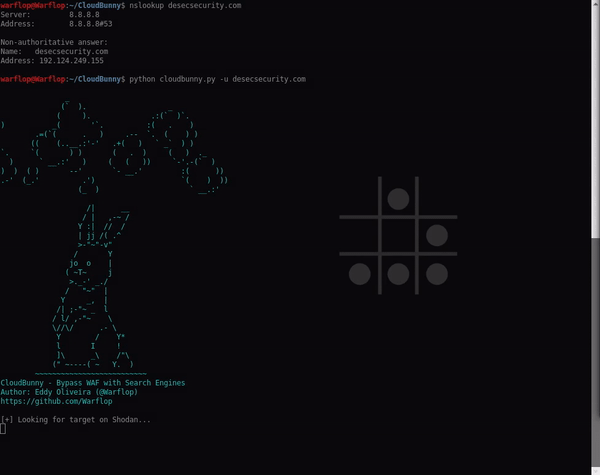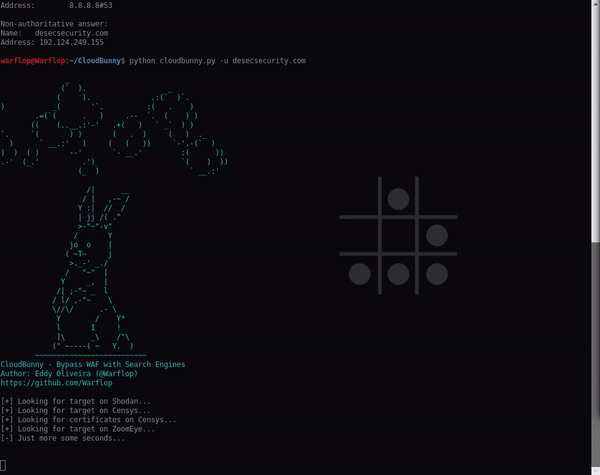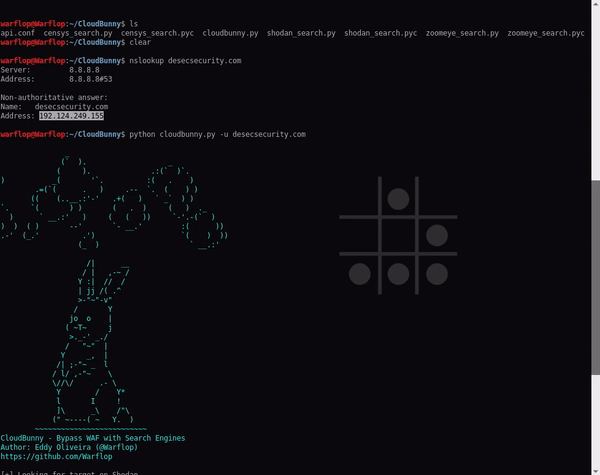
In this tool we used three search engines to search domain information: Shodan, Censys and Zoomeye. To use the tools you need the API Keys, you can pick up the following links:
Shodan - https://account.shodan.io/
Censys - https://censys.io/account/api
ZoomEye - https://www.zoomeye.org/profile
NOTE: In Zoomeye you need to enter the login and password, it generates a dynamic api key and I already do this work for you. Just enter your login and password.
After that you need to put the credentials in the api.conf file.
Install the requirements:
$ pip3 install -r requirements.txt
By default the tool searches on all search engines (you can set this up by arguments), but you need to put the credentials as stated above. After you have loaded the credentials and installed the requirements, execute:
$ python3 cloudbunny.py -u securityattack.com.br
Check our help area:
$ python3 cloudbunny.py -h
Change securityattack.com.br for the domain of your choice.
$ python3 cloudbunny.py -u site_example.com.br

	            /|      __
	           / |   ,-~ /
	          Y :|  //  /
	          | jj /( .^
	          >-"~"-v"
	         /       Y
	        jo  o    |
	       ( ~T~     j
	        >._-' _./
	       /   "~"  |
	      Y     _,  |
	     /| ;-"~ _  l
	    / l/ ,-"~    \
	    \//\/      .- \
	     Y        /    Y*
	     l       I     !
	     ]\      _\    /"\
	    (" ~----( ~   Y.  )
	~~~~~~~~~~~~~~~~~~~~~~~~~~
CloudBunny - Bypass WAF with Search Engines
Author: Eddy Oliveira (@Warflop)
https://github.com/Warflop

[+] Looking for target on Shodan...
[+] Looking for target on Censys...
[+] Looking for certificates on Censys...
[+] Looking for target on ZoomEye...
[-] Just more some seconds...


+---------------+------------+-----------+----------------------------+
|   IP Address  |    ISP     |   Ports   |        Last Update         |
+---------------+------------+-----------+----------------------------+
|  55.14.232.4  | Amazon.com | [80, 443] | 2018-11-02T16:02:51.074543 |
| 54.222.146.40 | Amazon.com |    [80]   | 2018-11-02T10:16:38.166829 |
| 18.235.52.237 | Amazon.com | [443, 80] | 2018-11-08T01:22:11.323980 |
| 54.237.93.127 | Amazon.com | [443, 80] | 2018-11-05T15:54:40.248599 |
| 53.222.94.157 | Amazon.com | [443, 80] | 2018-11-06T08:46:03.377082 |
+---------------+------------+-----------+----------------------------+
    We may have some false positives :)






