apache-vulnerability-testing

Apache HTTP Server Vulnerability Testing Tool | PoC for CVE-2024-38472 , CVE-2024-39573 , CVE-2024-38477 , CVE-2024-38476 , CVE-2024-38475 ,…

Apache HTTP Server Vulnerability Testing Tool | PoC for CVE-2024-38472 , CVE-2024-39573 , CVE-2024-38477 , CVE-2024-38476 , CVE-2024-38475 ,…

C-based proof-of-concept exploit for VirtualBox CVE-2018-2844, demonstrating a heap overflow vulnerability in the hypervisor's network driver for…

Proof-of-concept exploit for CVE-2022-23808, a stored XSS vulnerability in phpMyAdmin 5.1.1 setup script, with payload and reproduction steps for…

Java RMI security testing tool for detecting, enumerating, and exploiting insecure RMI services using ysoserial deserialization gadgets to achieve…

Collection of Python-based exploit scripts for penetration testing, covering multiple vulnerability types and exploitation techniques.

Modular web vulnerability scanner with template-driven detection engine for automated testing of XSS, SQLi, LFI, RFI, and sensitive file/directory…

Proof-of-concept exploit for CVE-2024-26218, demonstrating a specific vulnerability for security research and testing.

Proof-of-concept exploit for CVE-2025-5419, demonstrating a critical vulnerability with a JavaScript-based implementation for security testing and…

Tool for testing mitigations and exposure to Rapid Reset DDoS (CVE-2023-44487)

Proof-of-concept exploit for CVE-2024-21345, demonstrating a specific vulnerability with functional code for security testing and validation.

JavaScript exploit targeting CVE-2023-2033 for proof-of-concept testing and vulnerability validation in web applications.

C++ exploit for CVE-2021-1732 targeting Windows privilege escalation on Win10 1803-20H2 and Server 2019/2004. Provides kernel-level elevation of…

Proof-of-concept exploit for CVE-2019-1253, a Windows privilege escalation vulnerability. Demonstrates exploitation technique for security research…

Framework for identifying and exploiting out-of-band (OOB) application vulnerabilities with a custom DNS/token server, Burp Suite extension, and…

Modular credential validation framework with active and passive (regex-based) checking modes for penetration testers. Supports multiple services via…

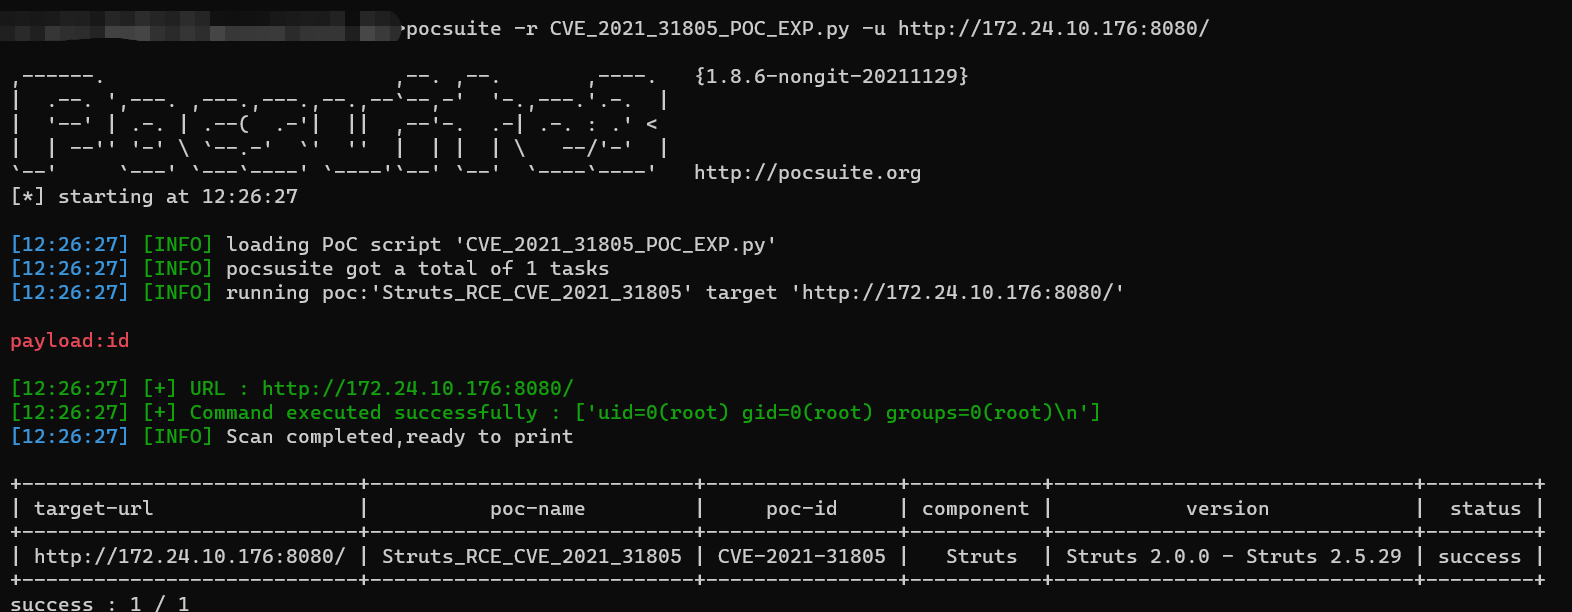
Python-based proof-of-concept and exploit for Apache Struts2 RCE (CVE-2021-31805), enabling command execution via OGNL injection. Includes POC and…

C# proof-of-concept exploit for CVE-2023-29357 targeting SharePoint, with YARA detection rules and detailed usage instructions for security testing.

Proof-of-concept exploit code targeting CVE-2026-40369, demonstrating the vulnerability for research and authorized security testing.