 zerodayevil/cve-2026-40369-exploit
Proof-of-concept exploit code targeting CVE-2026-40369, demonstrating the vulnerability for research and authorized security testing.

🛡️ AI Security Tool Module
CVE-2026-40369: NtQuerySystemInformation Class 253 Kernel Address Increment LPE
Official Security Audit & Exploitation Module for AI Security Tool Ecosystem





🌐 Web Demo • 📚 Project Website • 💬 Community Chat
Website Navigation: Home • Updates • Downloads • Modules
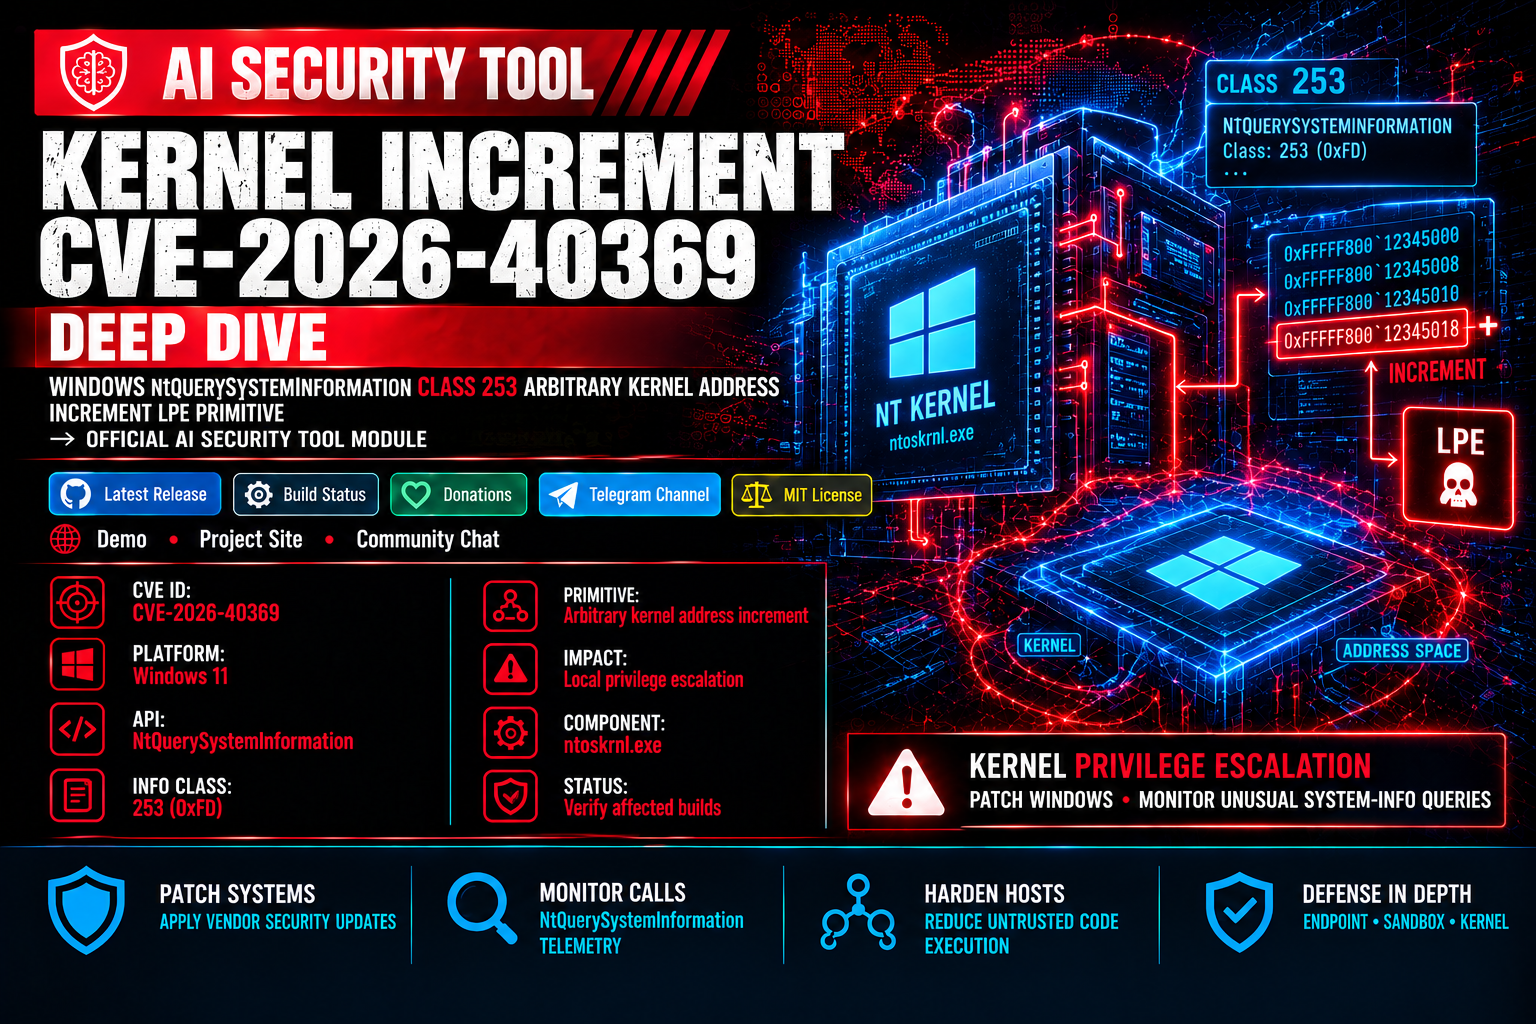
This module provides diagnostic tools and deep technical analysis for CVE-2026-40369, an arbitrary kernel address increment (write primitive) vulnerability in Windows ntoskrnl.exe via NtQuerySystemInformation (Class 253 / SystemProcessInformationExtension).
Because NtQuerySystemInformation is reachable from restricted contexts (including the Chrome browser sandbox), this vulnerability provides an unprivileged local user with a deterministic, 100% reliable privilege escalation primitive.



| Specification | Assigned Value | Notes |
|---|---|---|
| CVE Identifier | CVE-2026-40369 |
Arbitrary Kernel Address Increment via NtQuerySystemInformation |
| Component | Windows Kernel (ntoskrnl.exe) |
ExpGetProcessInformation |
| Trigger Vector | NtQuerySystemInformation(SystemProcessInformationExtension, kernelAddr, 0, &needed) |
Length=0 bypasses ProbeForWrite |
| Windows Versions | Windows 11 24H2–25H2 | Reachable from Chrome sandbox |
| Impact & Vector | Arbitrary kernel address increment (Write Primitive) | Deterministic privilege escalation building block |
| Auth Required | None (Unprivileged local user / Sandboxed) | No special tokens or privileges needed |
ExpGetProcessInformation is called by ExpQuerySystemInformation for info classes 5, 0x39, 0x94, 0xFC, and 0xFD (253 = SystemProcessInformationExtension). When handling class 253, variable v95 is initialized directly from the buffer pointer without sanitization or NULL checks.
__int64 ExpGetProcessInformation(unsigned int *buffer, unsigned int length, ..., int infoClass)
{
    v91 = buffer; // = NULL (when probing length=0)
    if (infoClass == 253) {
        v95 = v91; // BUG: sanitization for kernel address check missing!
        goto LABEL_11;
    }
    // ...
LABEL_11:
    while (NextProcess) {
        if (infoClass == 253) {
            ++*v95;          // CRASH / WRITE: Increments DWORD at target address
            v95[1] += ...;   // Adds thread count
            v95[2] += ...;   // Adds handle count
        }
    }
}
ExpQuerySystemInformation invokes ProbeForWrite(buffer, Length, alignment) prior to dispatching. However, ProbeForWrite with Length=0 is a complete NO-OP as it is gated by an internal if (Length) check. Passing an arbitrary kernel address with Length=0 successfully passes unvalidated pointers straight into the process iteration loop.
For each process on the system, the kernel performs triple arithmetic increments on the target memory address:
[target+0] += 1 per process (total system process count)[target+4] += cumulative active thread count[target+8] += cumulative active handle count
Monitor for anomalous calls to NtQuerySystemInformation referencing Class 253 with zero-length output buffers or unusual address ranges. Apply latest vendor updates and endpoint telemetry controls.
⚠️ IMPORTANT: This module is built specifically for safe execution and diagnostics within the AI Security Tool ecosystem. Always use verified modules sourced from official repositories.
To execute the monitoring and diagnostic scripts, ensure the AI Security Tool core engine is installed either via pre-built binaries or by building from source:
