

coraza
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
api-securityapi-security-testingdefensive-tools+7
3.8k
corazawaf/corazaGo-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
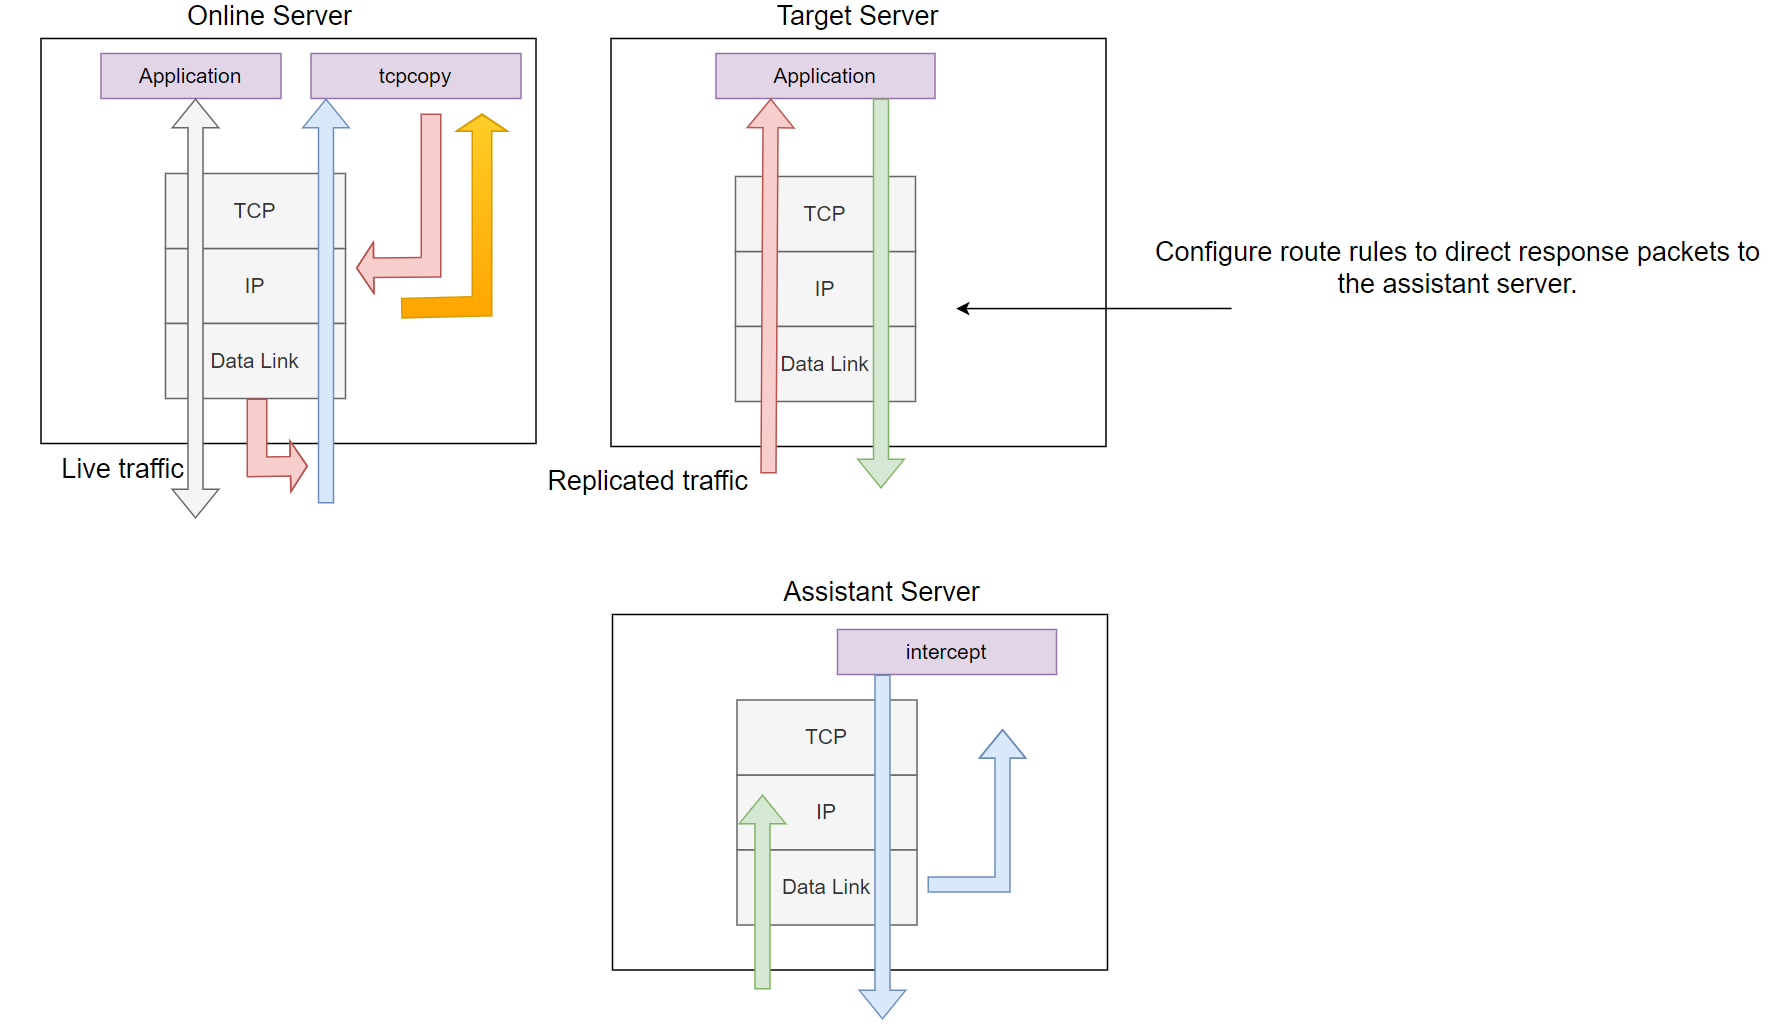 session-replay-tools/tcpcopy
An online request replication and TCP stream replay tool, ideal for real testing, performance testing, stability testing, stress testing, load…
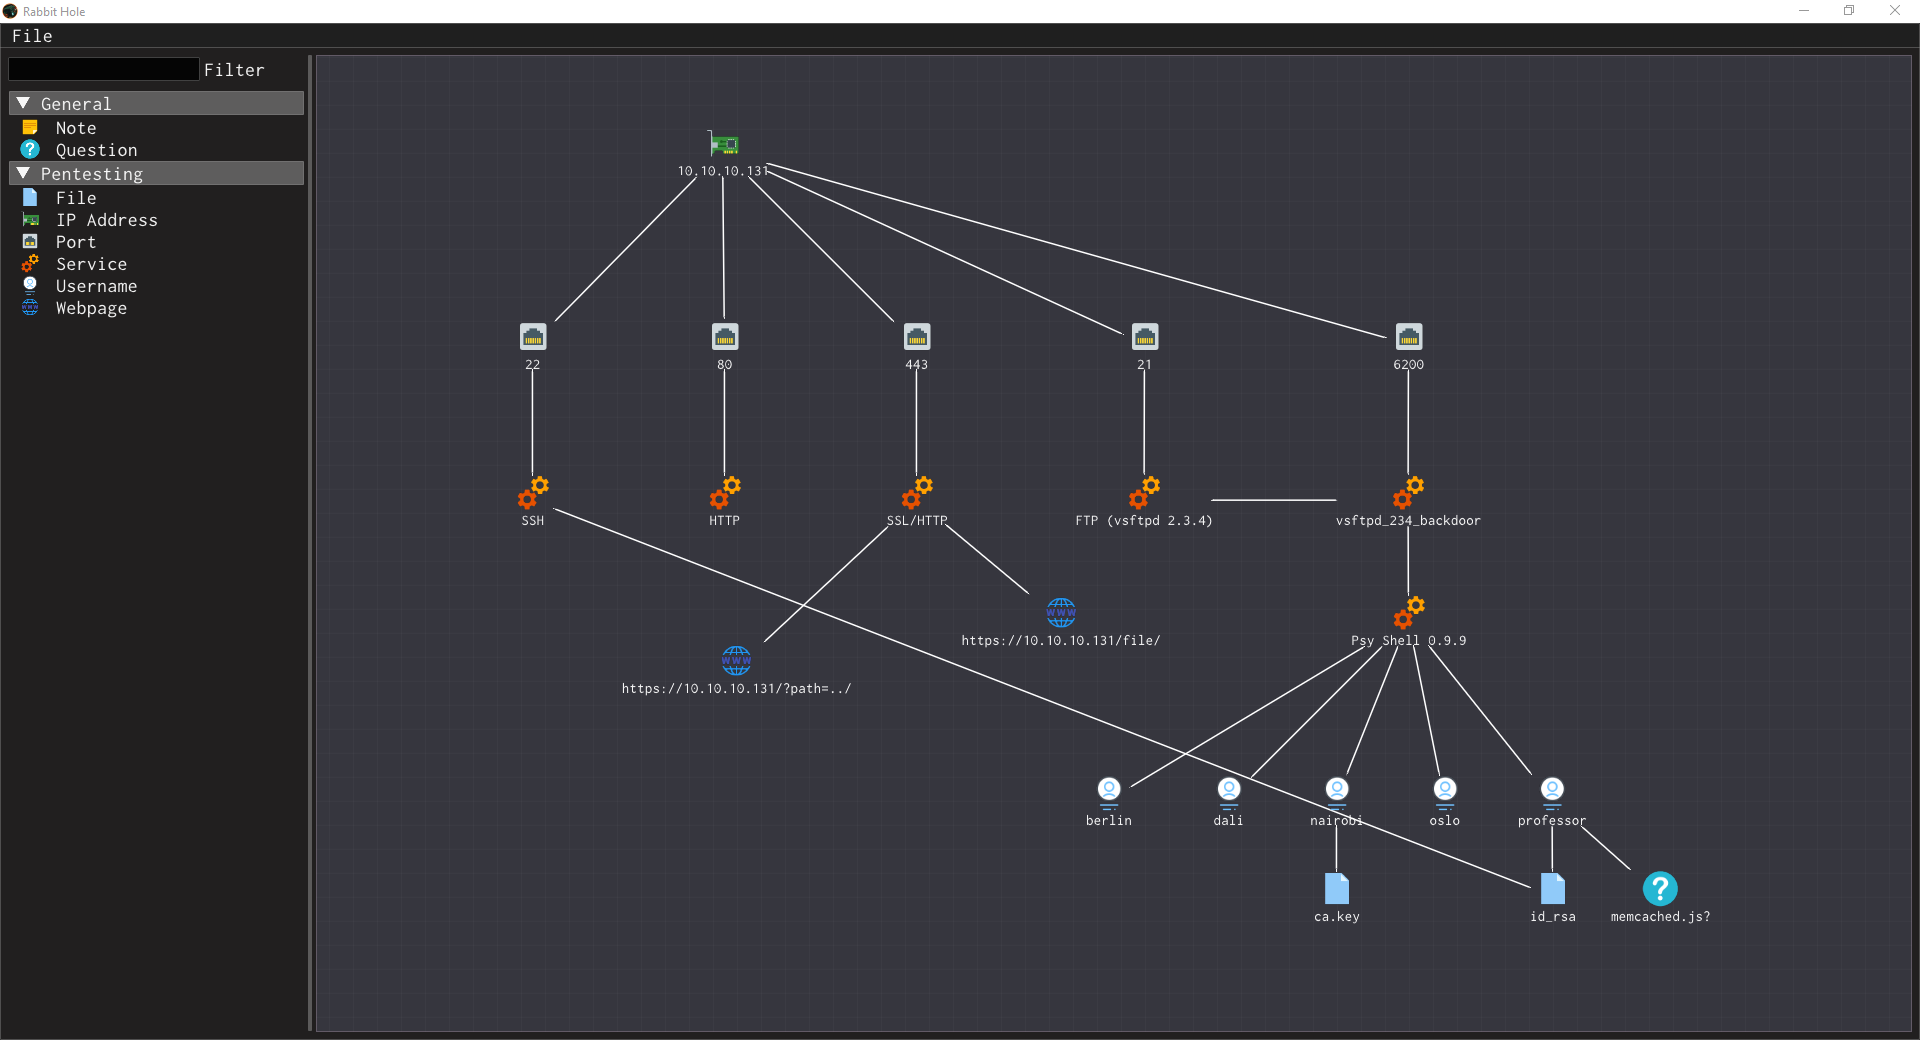
 hostile.node/rabbithole
Lightweight graph-based tool for organizing penetration testing data into visual node-link diagrams of IPs, ports, services, and findings, inspired…
 kkhackinglearning/cve-2025-55184_testing
Python script for Testing CVE-2025-55184
 s_r_e_e_r_a_j/reconhound
ReconHound is a Python-based web reconnaissance tool designed for penetration testers, bug bounty hunters, and ethical hackers. It supports directory…
 s_r_e_e_r_a_j/sshbuster
SSHBuster is a powerful command-line SSH brute-forcing tool designed for ethical hacking and penetration testing. It performs dictionary-based…
 s_r_e_e_r_a_j/php-reverse-shell
This is a powerful and stealthy PHP reverse shell designed for ethical hacking and penetration testing. It establishes a reliable and quiet…
 streaak/keyhacks
Curated collection of commands to validate leaked API keys from bug bounty programs and penetration tests, covering 80+ services including AWS,…
 testssl/testssl.sh
Testing TLS/SSL encryption anywhere on any port
 xmendez/wfuzz
Modular web fuzzer for automated security testing. Injects payloads into any HTTP request field to discover vulnerabilities, brute-force parameters,…
 andresriancho/w3af
Open-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
 bugcrowd/hunt
Flags parameters commonly associated with injection, SSRF, path traversal, IDOR, and SSTI, via passive Burp/ZAP scanning; also organizes manual…
 syslifters/sysreptor
A customizable and powerful penetration testing reporting platform for offensive security professionals. Simplify, customize, and automate your…
 r4j0x00/exploits
Proof-of-concept exploit collection targeting Linux kernel LPE, sudo heap overflow, and Chrome V8 OOB write vulnerabilities for penetration testing.
 cravaterouge/bloodyad
LDAP-based Active Directory privilege escalation framework supporting pass-the-hash, pass-the-ticket, and certificate authentication for automated…
 kevin-robertson/inveigh
.NET IPv4/IPv6 machine-in-the-middle tool for penetration testers
 defparam/smuggler
Python-based HTTP request smuggling and desync testing tool that detects CL.TE and TE.CL vulnerabilities using configurable mutation payloads and…
 powershellempire/powertools
Collection of offensive PowerShell projects for reconnaissance, privilege escalation, and post-exploitation during penetration testing engagements.